
The Deceptive Nature of Digital Infiltration
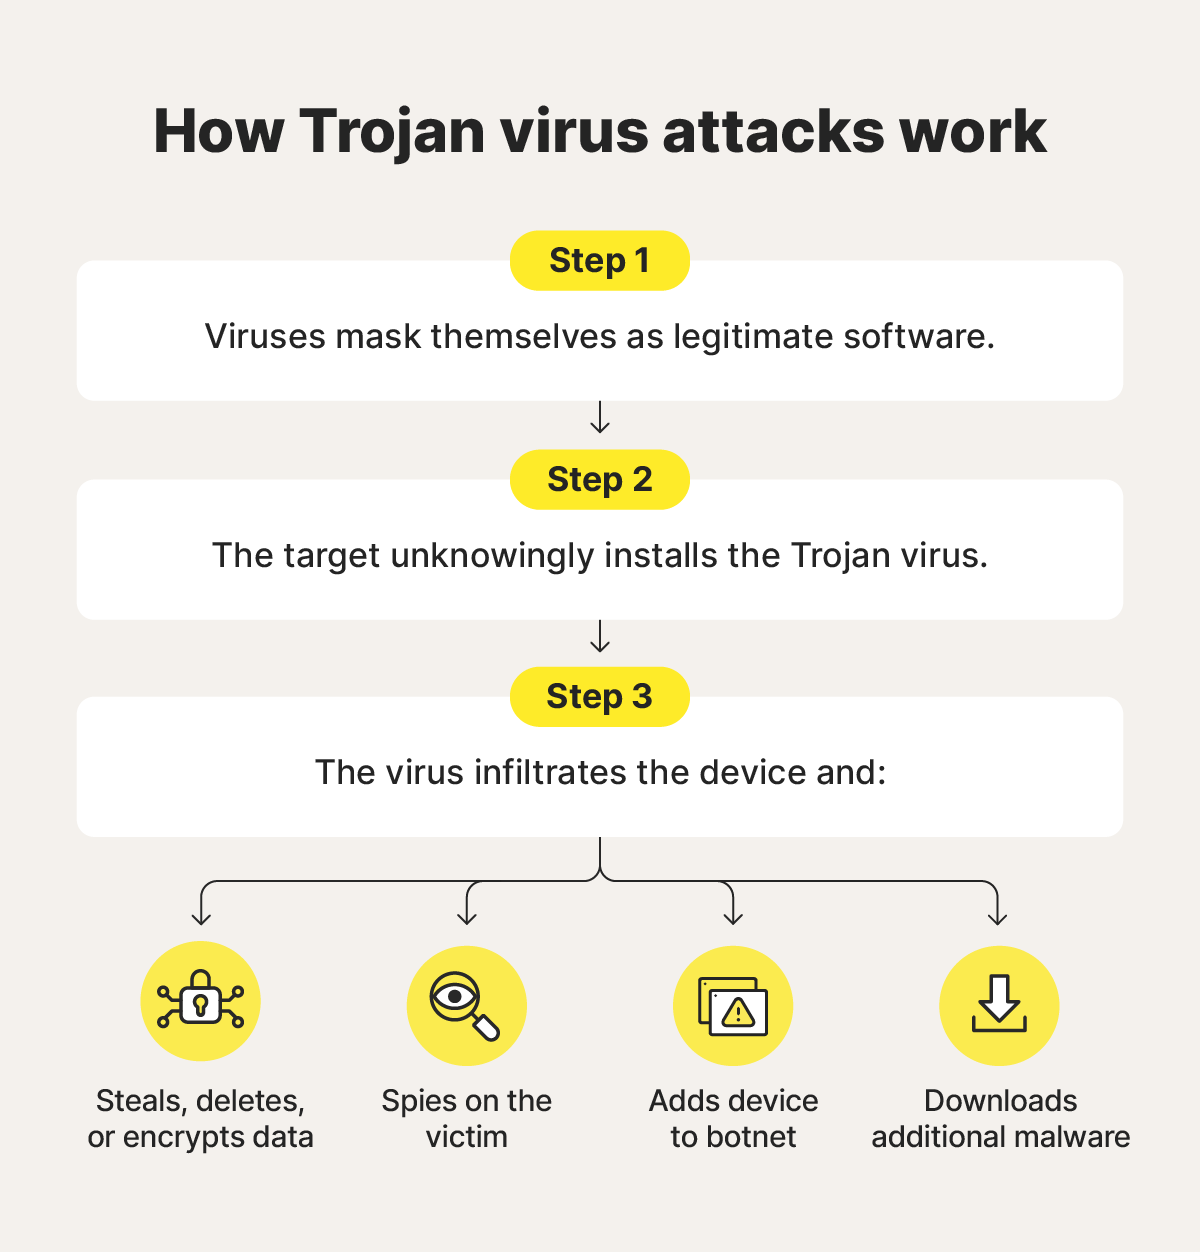
In the intricate landscape of modern technology, where innovation propels us forward at an unprecedented pace, understanding fundamental threats to digital integrity becomes paramount. Among the most pervasive and insidious forms of malicious software is the Trojan virus, or more accurately, the Trojan horse program. Unlike a virus that self-replicates, a Trojan masquerades as legitimate or beneficial software, gaining access to systems through deception. Its namesake originates from the ancient Greek tale, where a seemingly innocuous gift concealed warriors destined to breach a city’s defenses. In the digital realm, a Trojan operates with the same principle, presenting itself as a benign application, file, or utility, only to harbor destructive capabilities or create backdoors once executed. This deceptive entry mechanism makes Trojans a potent threat, particularly for the advanced, interconnected systems that define contemporary tech.
Mimicry and Concealment
Trojans excel at blending in. They can appear as free software downloads, game patches, pirated media, or even seemingly legitimate updates from trusted vendors. In an era of constant software iteration and feature enhancements, users are accustomed to frequent updates and new application installations, creating fertile ground for Trojan propagation. The malicious code is often embedded within what appears to be a fully functional program, making initial detection by an unsuspecting user incredibly difficult. This mimicry extends to their behavior post-installation; a Trojan may allow the intended program to function normally while secretly executing its payload in the background, minimizing suspicion and prolonging its undetected presence within a system. This sophisticated form of concealment is a key differentiator from more overt malware, allowing Trojans to persist within complex technology stacks for extended periods.
Beyond Simple Malware
Distinguishing a Trojan from other forms of malware is crucial for comprehending its unique threat profile. While viruses replicate and worms spread across networks independently, a Trojan relies on user interaction and deception to establish its foothold. It doesn’t inherently seek to spread itself; rather, its primary objective is to gain unauthorized access, exfiltrate data, or execute commands on the compromised system. This distinction is particularly relevant in high-tech environments where data integrity, intellectual property, and operational continuity are critical. Trojans represent a targeted entry point, often preceding more significant breaches or acting as the initial stage for ransomware, espionage, or sabotage campaigns against advanced technological assets. Their utility as a stealthy gateway makes them a favored tool for state-sponsored actors, industrial spies, and sophisticated cybercriminals targeting innovative enterprises.
Modus Operandi: How Trojans Compromise Modern Systems
The lifecycle of a Trojan involves several stages, each designed to ensure successful infiltration, persistence, and payload execution. Understanding these operational tactics is essential for developing robust cybersecurity postures for cutting-edge technologies.
Initial Entry Vectors
Trojans exploit various channels to gain entry into digital environments. One common method is phishing, where attackers craft convincing emails or messages that trick users into downloading and executing malicious attachments or clicking on links leading to compromised websites. These sites might then auto-download the Trojan, often bundled with seemingly legitimate software. Another significant vector is drive-by downloads, where visiting a compromised website can silently install malware without explicit user consent, often leveraging vulnerabilities in web browsers or plugins. In enterprise environments, Trojans might spread through internal networks via social engineering, where an employee is persuaded to install a seemingly helpful tool that, unbeknownst to them, contains a Trojan. For advanced technology firms, securing supply chains is also critical, as Trojans can be injected into legitimate software builds or hardware firmware during manufacturing or distribution, making them incredibly difficult to detect before deployment.
Establishing Persistent Presence
Once executed, a Trojan’s primary goal is to establish a persistent presence, ensuring it can survive system reboots and evade basic detection mechanisms. This often involves modifying system registries, creating scheduled tasks, or embedding itself within legitimate system processes. Many Trojans utilize rootkit functionalities to conceal their files, processes, and network connections from operating system tools and security software. By maintaining stealth, they can operate undetected for extended periods, continuously monitoring user activity, capturing sensitive data, or awaiting commands from a remote attacker (Command and Control, or C2 server). In the context of AI-driven systems or remote sensing platforms, such persistence could mean a Trojan continuously siphoning off proprietary algorithms, confidential mapping data, or sensor readings without immediate indicators of compromise.
Diverse Malicious Payloads
The “payload” is the ultimate destructive or malicious action a Trojan is designed to perform. Trojans are highly versatile, capable of carrying a wide array of payloads tailored to specific objectives:
- Backdoor Trojans: These create a secret entry point into the compromised system, allowing remote attackers to gain full control, execute commands, modify files, and install additional malware. This is particularly dangerous for autonomous systems, as it could allow unauthorized manipulation of control parameters.
- Downloader Trojans: Designed to download and install other malicious programs, such as ransomware, spyware, or additional Trojans. They act as initial beachheads for multi-stage attacks.
- Fake AV Trojans: Masquerade as legitimate antivirus software, often displaying fake security alerts to trick users into purchasing rogue software or revealing personal information.
- Game-Thief Trojans: Target online gaming accounts to steal credentials or in-game assets.
- Infostealer Trojans: Specifically designed to steal sensitive information such as login credentials, bank account details, and personal files. This poses a severe threat to data integrity and intellectual property within innovative companies.
- Mailfinder Trojans: Harvest email addresses from a victim’s computer for spamming or phishing campaigns.
- Ransom Trojans: Encrypt files on the victim’s computer and demand a ransom payment for their decryption. This can cripple operations reliant on critical data, such as mapping or remote sensing databases.
- Remote Access Trojans (RATs): Provide attackers with comprehensive remote control over a compromised system, often including webcam access, keylogging, and file transfer capabilities. RATs are sophisticated tools for espionage.
- SMS Trojans: Target mobile devices, sending costly SMS messages to premium-rate numbers without the user’s consent.
The Peril for Advanced Tech & Innovation
In the domain of “Tech & Innovation,” where cutting-edge solutions like AI follow mode, autonomous flight, mapping, and remote sensing are rapidly evolving, the threat posed by Trojans is particularly acute. The integrity, security, and confidentiality of these advanced systems are constantly under siege.
Data Integrity and Remote Sensing
Innovative remote sensing technologies generate vast amounts of critical data, from environmental monitoring to geospatial intelligence for urban planning or agricultural optimization. A Trojan designed to exfiltrate or corrupt this data could have catastrophic consequences. Imagine a scenario where a Trojan silently alters sensor calibration data, introducing subtle inaccuracies into mapping information, or siphoning off proprietary algorithms used for data processing. Such an attack could undermine the reliability of entire datasets, compromise strategic decisions, and erode trust in the technology itself. The intellectual property embedded in these data pipelines and processing techniques is immensely valuable, making it a prime target for state-sponsored or corporate espionage facilitated by Trojan infiltration.
Autonomous Systems and AI
Autonomous systems, whether in robotics, logistics, or transportation, rely heavily on AI and precise operational parameters. The introduction of a Trojan into the control systems or AI algorithms of such an autonomous entity could have profound and dangerous implications. A Trojan could subtly manipulate navigation instructions, alter decision-making logic, or disrupt communication protocols. For instance, a Trojan might introduce biases into an AI’s learning model or compromise the integrity of its input data, leading to unpredictable or malicious behavior. In a mission-critical context, this could result in operational failures, safety hazards, or even intentional sabotage, directly threatening the reliability and safety promised by autonomous innovation. Maintaining the integrity of the software stack that governs autonomous functions is paramount.
Intellectual Property and Competitive Advantage
The heart of tech innovation lies in novel ideas, proprietary algorithms, and unique system designs. Trojans are frequently employed by adversaries to steal intellectual property (IP), ranging from source code and design blueprints to business strategies and research findings. A well-placed Trojan can act as a long-term spy, quietly transmitting confidential documents and communications to a competitor or foreign entity. This theft of IP can severely undermine a company’s competitive advantage, allowing rivals to replicate innovative features or accelerate their own development cycles at a fraction of the cost. Protecting the digital assets that embody innovation from such stealthy infiltration is a continuous and complex challenge requiring advanced security measures.
Proactive Defense in an Innovative Landscape
Combating Trojans in an era of rapid technological advancement requires a multi-faceted and adaptive security strategy that goes beyond traditional antivirus solutions.
Multi-Layered Security Architectures
Effective defense against Trojans demands a comprehensive, layered security architecture. This includes robust firewalls, intrusion detection and prevention systems (IDPS), and endpoint detection and response (EDR) solutions that can monitor for anomalous behavior indicative of Trojan activity. Advanced threat intelligence platforms, often leveraging machine learning and AI, can identify emerging Trojan variants and attack patterns. Network segmentation, principle of least privilege, and application whitelisting are critical architectural controls that limit a Trojan’s ability to spread laterally or execute unauthorized code, even if it manages initial infiltration. For critical infrastructure or proprietary systems, hardware-level security, such as Trusted Platform Modules (TPMs) and secure boot processes, adds another layer of defense by verifying system integrity from the boot-up sequence.
Human-Centric Security Practices
Despite technological advancements, the human element remains a primary vulnerability for Trojan infections. Continuous security awareness training for employees is vital. This includes educating users on how to identify phishing attempts, the dangers of downloading unverified software, and the importance of strong, unique passwords and multi-factor authentication (MFA). Implementing stringent software update policies ensures that systems are patched against known vulnerabilities that Trojans often exploit. Regular security audits and penetration testing can uncover weaknesses in both technological infrastructure and human practices, allowing organizations to proactively address potential entry points for Trojans before they are exploited.
The Evolving Role of AI in Threat Detection
Ironically, just as AI and autonomous systems are targets for Trojans, they also offer powerful new tools for defense. AI-driven security solutions can analyze vast amounts of network traffic, system logs, and behavioral patterns in real-time to detect the subtle indicators of Trojan activity that might evade traditional signature-based detection. Machine learning algorithms can identify anomalous process executions, unusual network connections to C2 servers, or unauthorized data exfiltration attempts. Furthermore, AI can contribute to predictive threat intelligence, anticipating new Trojan attack vectors and adapting defenses dynamically. As technology continues to innovate, so too must the methods of defense, leveraging the very intelligence that adversaries seek to compromise.