
The Genesis of Digital Vulnerability in Autonomous Flight Systems
The question “what was the first virus?” typically evokes images of early biological pathogens or foundational pieces of malicious computer code like the Creeper program or the Morris Worm. However, when we consider this question through the lens of modern “Tech & Innovation,” particularly in the context of autonomous flight and drone technology, the answer transcends a singular, identifiable entity. Instead, it points to the earliest recognized vulnerabilities and disruptive anomalies within complex, interconnected systems that laid the groundwork for understanding present-day threats to unmanned aerial vehicles (UAVs). The “first virus” in this domain wasn’t necessarily a specific piece of malware targeting a drone, but rather the fundamental realization that sophisticated machinery, reliant on computation and communication, was inherently susceptible to unintended behavior, external manipulation, and systemic breakdown – a kind of conceptual “infection” that could compromise integrity and function.

Early Seeds of System Integrity Concerns
Long before drones became ubiquitous, the precursors to autonomous flight systems were emerging in military avionics, industrial control systems, and early networked computers. These foundational technologies, though rudimentary by today’s standards, introduced the critical concept of system integrity. Engineers grappled with ensuring that complex machines would perform as intended, free from errors, interference, or malicious intent. The “first virus” in this nascent era might be considered the initial discovery of a bug, a logic flaw, or an unanticipated interaction within a control system that led to an undesired outcome. These early vulnerabilities, whether accidental or theoretical, highlighted the imperative for robust design, redundancy, and secure communication protocols, principles that are paramount in contemporary drone development. The very act of linking distinct computational elements introduced points of failure, each a potential entry vector for a “viral” disruption.
From Industrial Control to Airborne Autonomy
The evolution from simple electromechanical systems to digitally controlled aircraft brought with it new layers of complexity and, consequently, new avenues for potential “infection.” Early industrial control systems (ICS) and supervisory control and data acquisition (SCADA) systems, for instance, were among the first truly interconnected networks to manage critical infrastructure. Their vulnerabilities, which often stemmed from a lack of inherent security in their design (prioritizing functionality over cyber resilience), provided a blueprint for understanding how digital disruptions could cascade through a network and impact physical operations. As autonomous flight technology advanced, borrowing heavily from these established engineering paradigms, the lessons learned about securing ground-based industrial systems became increasingly relevant for airborne platforms. The “first virus” then morphs into the first instance where a digital exploit or systemic flaw in such an interconnected environment demonstrated the potential to cause real-world, kinetic effects – a direct parallel to the concerns surrounding drone security today.
Tracing the Ancestry of Autonomous System Threats
While no definitive “first virus” directly targeting a drone can be named from the early days, the lineage of threats that inform drone cybersecurity can be traced through the history of computer science and network security. The principles behind disruptive software and external interference have long been subjects of study, and their application to autonomous vehicles represents a modern iteration of these enduring challenges.
The Echoes of Foundational Digital Breaches
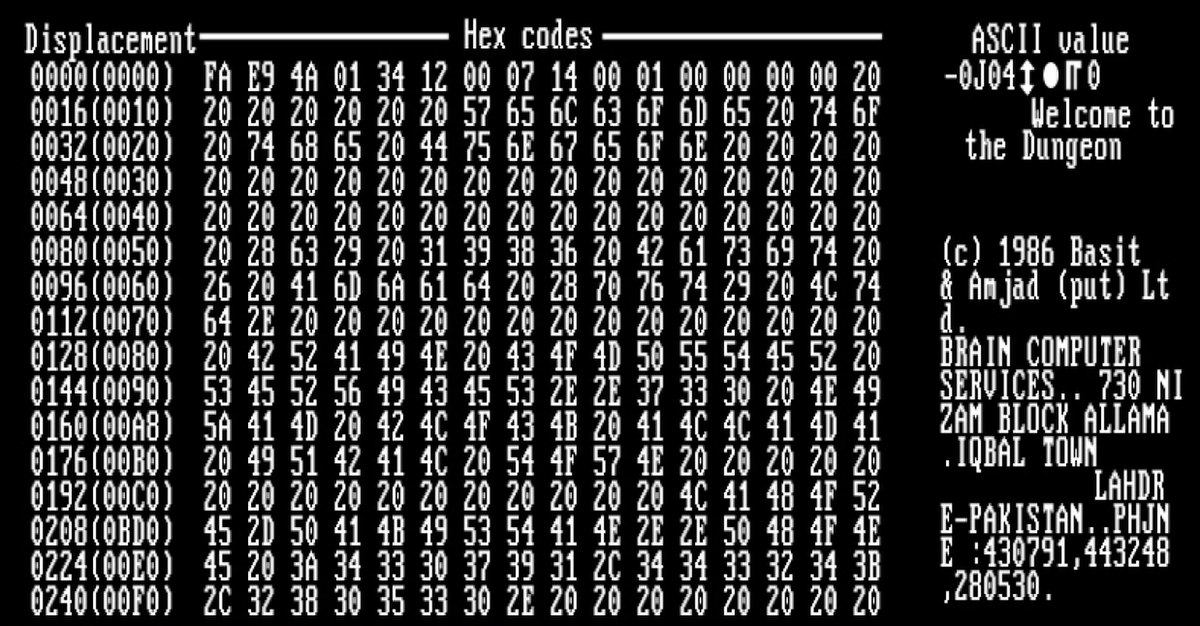
The seminal computer viruses and worms of the 1970s and 80s, such as the Creeper program, Elk Cloner, and the Morris Worm, were instrumental in illustrating the power of self-replicating code and network exploitation. While these early viruses were not designed for airborne systems, they proved that digital entities could spread autonomously, consume resources, and alter system behavior. The lessons from these foundational breaches—the importance of robust authentication, secure coding practices, and network segmentation—are directly applicable to the development of drone operating systems and communication channels. The “first virus” in this context is not a single piece of code, but the demonstration that complex digital systems are inherently vulnerable to unseen, self-propagating threats that leverage design flaws and network connectivity. This understanding served as an early warning for all future networked autonomous systems.
Beyond Code: Environmental “Viruses” and Early Disruptions
The concept of a “virus” impacting autonomous flight systems extends beyond malicious code to include environmental and external disruptions that mimic the effect of a digital infection. Early forms of interference, such as radio frequency (RF) jamming or electromagnetic interference (EMI), could effectively “infect” a drone’s communication links, rendering it unresponsive or causing loss of control. GPS spoofing, a technique to deceive a receiver about its actual location, represents another early, non-code-based “viral” threat that could severely compromise a drone’s navigation and mission integrity. These forms of attack, though not traditional software viruses, demonstrate a similar disruptive pattern: they interfere with critical system functions, propagate undesired behavior (like a drone flying off course), and require robust countermeasures to mitigate. The “first virus” might thus be interpreted as the first successful instance of such an environmental attack, revealing a fundamental vulnerability in autonomous operation.
The Evolving Landscape of Drone-Specific Vulnerabilities
As drone technology matured, so did the sophistication of potential threats. The proliferation of commercial and consumer drones, combined with their increasing autonomy and connectivity, created new vectors for attack, transforming theoretical vulnerabilities into tangible risks.
Firmware, Communications, and Supply Chain Exposures
Modern drones rely heavily on complex firmware, which is often developed by various third-party vendors. A “virus” can exist as a hidden vulnerability within this firmware, whether introduced intentionally or accidentally during the development or manufacturing process. Exploits can range from backdoor access to malicious code that compromises flight stability or data integrity. Communication links, particularly the command-and-control (C2) channels and data downlinks, remain critical targets. Interception, jamming, or spoofing of these signals can lead to unauthorized control, data exfiltration, or denial of service. Furthermore, the global supply chain for drone components—from microcontrollers to sensors—introduces numerous points of potential compromise, where hardware or software can be subtly altered, creating a “supply chain virus” that is incredibly difficult to detect before deployment.
The Human Element and Social Engineering as a “Virus”
Beyond technical vulnerabilities, the “first virus” for a drone system could also be attributed to the human element. Social engineering attacks, phishing campaigns, or insider threats leverage human psychology to gain unauthorized access or introduce malware. A seemingly innocuous email, a manipulated software update, or an exploited human trust can act as a “virus,” allowing adversaries to compromise drone networks, control systems, or steal sensitive data. Training and awareness are critical components of cybersecurity, as the most robust technical defenses can be bypassed if the human operators are not adequately protected against these insidious “viral” forms of attack.
Pioneering Countermeasures: Innovation in Drone Cybersecurity
Recognizing the multifaceted nature of these “viral” threats, the drone industry and cybersecurity experts have continuously innovated to develop robust countermeasures. The goal is to build resilience and redundancy into every layer of autonomous flight systems, from hardware to software and network protocols.
Architectural Resilience and Redundancy
A primary defense against digital and environmental “viruses” is the implementation of resilient drone architecture. This includes redundant flight control systems, multiple communication channels, and fail-safe mechanisms that allow a drone to return home or land safely even if critical systems are compromised. Hardware security modules (HSMs) and trusted execution environments (TEEs) are being integrated to protect cryptographic keys and ensure the integrity of critical processes. Diversification of sensor inputs and the use of sensor fusion algorithms also contribute to resilience, making it harder for a single point of failure or a single type of spoofing attack to completely destabilize the drone’s operation.
Leveraging AI and Machine Learning for Threat Detection
Artificial intelligence and machine learning (AI/ML) are at the forefront of identifying and mitigating novel “viral” threats. These technologies can analyze vast amounts of flight data, network traffic, and system logs to detect anomalies that signify an attack or a system compromise. AI algorithms can learn normal operational behavior and flag deviations in real-time, whether it’s an unusual flight path, an unrecognized command, or a deviation in power consumption. This proactive anomaly detection acts as an immune system for drones, identifying “infections” before they can cause significant damage. Machine learning models can also be trained to recognize patterns associated with known jamming, spoofing, or malware signatures, providing an adaptive defense mechanism.
Secure Protocols and Blockchain Integration
The development and adoption of secure communication protocols are fundamental to preventing digital “viruses” from exploiting data transmission channels. End-to-end encryption, mutual authentication between drones and ground control stations, and secure over-the-air updates ensure that commands are legitimate and data remains confidential. Emerging technologies like blockchain are also being explored for drone security. By creating immutable ledgers for flight logs, maintenance records, and supply chain provenance, blockchain can enhance trust and verifiability, making it exceedingly difficult for malicious actors to introduce “viral” changes or tamper with critical historical data. Decentralized identity management for drones can also prevent unauthorized access and ensure that only authenticated entities can interact with the aircraft.
The Perpetual Challenge: Safeguarding the Future of Autonomous Flight
The fight against “viruses” in autonomous flight systems is a continuous and evolving battle. As drone technology advances and its applications broaden, so too will the ingenuity of those seeking to exploit its vulnerabilities. The “first virus” may have been a theoretical concept or a foundational flaw, but the future promises an ever-increasing sophistication of threats.
Proactive Threat Intelligence and Ethical Hacking
Maintaining a secure drone ecosystem requires a proactive approach centered on threat intelligence and ethical hacking. Cybersecurity professionals actively monitor the threat landscape, identify emerging vulnerabilities, and develop defensive strategies before attacks occur. Ethical hackers (or “white hats”) conduct penetration testing and vulnerability assessments on drone systems, simulating real-world attacks to uncover weaknesses that could be exploited by malicious actors. This continuous cycle of identification, testing, and remediation is crucial for staying ahead of potential “viral” outbreaks.

International Collaboration and Regulatory Frameworks
Given the global nature of drone operations and the interconnectedness of supply chains, international collaboration is essential for establishing common security standards and sharing threat intelligence. Regulatory bodies are increasingly focusing on drone cybersecurity, developing frameworks that mandate secure design principles, data protection, and incident response protocols. These frameworks aim to create a baseline of security across the industry, ensuring that all drones, from consumer models to sophisticated military UAVs, are resilient against the myriad forms of “viruses” that could seek to compromise their integrity and mission. The lessons learned from the “first virus” – the realization of inherent vulnerability in complex systems – continue to drive innovation in protecting the skies.