
In the rapidly evolving landscape of enterprise technology, the traditional network perimeter has all but dissolved. Organizations grapple with a dispersed workforce, applications residing in diverse cloud environments, and an ever-increasing sophistication of cyber threats. Amidst this complexity, the Zscaler Client Connector emerges as a pivotal piece of the modern security puzzle, acting as the intelligent conduit that securely connects users to applications and data, regardless of location or device. It is a critical component of Zscaler’s Zero Trust Exchange platform, embodying a fundamental shift from network-centric security to an identity-centric, user-to-app approach.
Navigating the Evolving Cyber Landscape
The advent of cloud computing and the seismic shift towards remote and hybrid work models have fundamentally reshaped how businesses operate and secure their digital assets. This transformation has rendered legacy security architectures largely ineffective, paving the way for innovative solutions that can adapt to a borderless enterprise.

The Demise of the Traditional Network Perimeter
For decades, cybersecurity strategies revolved around a “castle-and-moat” defense, where all corporate resources were housed within a well-defined network perimeter, protected by firewalls, VPNs, and intrusion detection systems. Users inside the perimeter were implicitly trusted, while those outside faced stringent checks to gain access. However, this model faltered as applications migrated to the cloud (SaaS, IaaS), users accessed resources from home offices or public Wi-Fi, and mobile devices became primary workstations. The perimeter fragmented, creating numerous entry points for attackers and significant blind spots for security teams. Trying to backhaul all traffic to a central data center for security inspection became a bottleneck, impacting performance and user experience.
Rise of Cloud and Remote Work
The imperative for businesses to leverage cloud agility and support a distributed workforce accelerated the need for a new security paradigm. Cloud applications offer scalability and flexibility, but they bypass the traditional corporate network. Remote workers require secure, direct access to these cloud resources and internal applications without compromising security or suffering from latency. The challenge became how to provide secure access to any user, from any device, to any application, anywhere, without exposing the corporate network to unnecessary risk. This is where the concept of Zero Trust gained prominence, advocating for a “never trust, always verify” principle, where every access request is authenticated and authorized, regardless of its origin. Zscaler Client Connector is a cornerstone of implementing this Zero Trust model.
Zscaler Client Connector: A Deep Dive into its Mechanics
At its core, Zscaler Client Connector is a lightweight software agent installed on an end-user device—laptops, desktops, or mobile devices. Its primary function is to steer all user traffic securely to the Zscaler Zero Trust Exchange platform, a globally distributed cloud security service. This fundamental redirection allows Zscaler to enforce security policies and provide direct, secure access to applications without placing users on the corporate network.
Identity-Centric, Zero Trust Access
Unlike traditional VPNs that grant network access, Zscaler Client Connector enables identity-centric access to specific applications. When a user authenticates, the Client Connector establishes an encrypted micro-tunnel to the nearest Zscaler data center. This tunnel authenticates the user and device against identity providers (like Okta, Azure AD) and then applies granular access policies defined by the organization. Instead of connecting the user to the network, it connects the user to the application. This prevents lateral movement within the network, as users are never truly “on” the network; they only see the applications they are authorized to access. This significantly reduces the attack surface and minimizes the impact of potential breaches.
Securely Connecting Users to Applications
The Client Connector intelligently intercepts user traffic at the device level. Based on configured policies, it directs internet-bound traffic to Zscaler’s Cloud Security Platform (ZIA – Zscaler Internet Access) for full security inspection—including threat protection, data loss prevention (DLP), and cloud access security broker (CASB) services. Simultaneously, it directs private application traffic to Zscaler Private Access (ZPA), which establishes an outbound, encrypted tunnel from the Zscaler cloud to the private application. This innovative architecture means:
- No Inbound Connections: Private applications are never directly exposed to the internet. ZPA brokers connections without requiring inbound firewall rules.
- Direct-to-App: Users connect directly to applications, not the network, reducing latency and improving performance.
- Always-On Security: Whether users are on the corporate network or a public Wi-Fi, their traffic is always routed through Zscaler for consistent policy enforcement and threat protection.
The Role of Zscaler’s Cloud Security Platform
The Client Connector is the on-ramp, but the Zscaler Zero Trust Exchange is the superhighway. This global cloud platform consists of hundreds of data centers, providing a massive, distributed security infrastructure. When traffic is steered to Zscaler via the Client Connector, it undergoes comprehensive scrutiny:
- Threat Protection: Advanced firewalls, intrusion prevention systems, sandbox analysis, and anti-malware engines scrutinize all web and cloud traffic.
- Data Loss Prevention (DLP): Prevents sensitive data from leaving the organization’s control, whether intentionally or accidentally.
- Cloud Access Security Broker (CASB): Provides visibility and control over SaaS applications, preventing shadow IT and enforcing compliance.
- Bandwidth Control and QoS: Optimizes network performance by prioritizing critical applications and de-duplicating traffic.
All these services are delivered in the cloud, at the edge, closer to the user, ensuring a fast, secure, and seamless experience.

Transformative Benefits for Modern Enterprises
Implementing Zscaler Client Connector as part of a broader Zero Trust strategy brings a multitude of benefits that extend beyond mere security, impacting operational efficiency and user productivity.
Enhanced Security Posture
The primary advantage is a dramatically improved security posture. By eliminating implicit trust, reducing the attack surface, and enforcing granular, identity-based policies, organizations can significantly mitigate the risk of data breaches, ransomware attacks, and insider threats. Lateral movement by attackers is largely prevented, as users only connect directly to specific applications. The cloud-delivered security functions ensure that all traffic is inspected, even encrypted SSL/TLS traffic, catching threats that often bypass traditional perimeter defenses. Furthermore, the inherent isolation of private applications from the internet removes a major vulnerability point.
Simplified Network Operations
Zscaler Client Connector streamlines network operations by collapsing multiple point products (VPNs, firewalls, proxies) into a single, integrated cloud platform. This simplifies management, reduces infrastructure costs, and eliminates the need to backhaul traffic to a central data center. IT teams can provision access quickly and consistently, managing policies from a unified console. The global scale of the Zscaler platform means organizations can expand their footprint without deploying additional hardware or complex network configurations, making it an ideal solution for agile, cloud-first enterprises. Troubleshooting becomes easier as traffic flows through a standardized, secure path.
Improved User Experience and Productivity
By routing traffic directly to the nearest Zscaler data center and then directly to the application, Zscaler Client Connector dramatically reduces latency and improves application performance compared to traditional VPNs that route all traffic back to a corporate data center. Users experience faster access to cloud applications, internet resources, and private applications, leading to higher productivity and satisfaction. The “always-on” nature of the Client Connector means users are consistently protected and have seamless access, whether they are at home, in the office, or traveling, without the friction often associated with manually connecting to a VPN. This reliability is crucial for maintaining business continuity in a hybrid work environment.
Implementation and Strategic Considerations
Deploying Zscaler Client Connector involves strategic planning and integration, yet it is designed for ease of management and global scalability.
Integration with Existing Infrastructure
The Client Connector integrates seamlessly with existing identity providers (IdPs) like Azure Active Directory, Okta, Ping Identity, and others, leveraging an organization’s existing user authentication mechanisms. This ensures a consistent identity experience and simplifies user provisioning. It also coexists effectively with endpoint security solutions, offering complementary protection without conflict. For private application access, Zscaler Private Access (ZPA) Connectors are deployed in data centers or cloud environments where applications reside. These lightweight virtual machines establish outbound tunnels to the Zscaler cloud, enabling the secure, brokered access for users.
Scalability and Global Reach
One of Zscaler’s most compelling features is its inherent scalability and global presence. With hundreds of data centers strategically located worldwide, the Zscaler Zero Trust Exchange offers consistent performance and security to users anywhere on the globe. As an organization grows or expands into new regions, the Zscaler Client Connector automatically connects users to the nearest Zscaler data center, ensuring low latency and high availability without requiring additional infrastructure investment. This global footprint is critical for multinational corporations and businesses with highly distributed workforces, providing a unified security experience across all geographies.
Beyond Basic Connectivity: Advanced Features
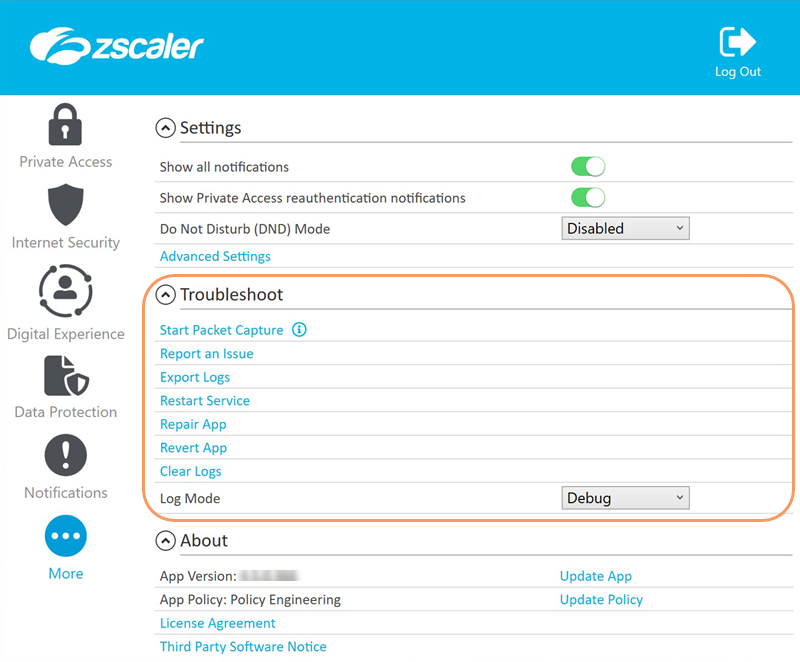
The Zscaler Client Connector is not just about routing traffic; it’s a feature-rich endpoint agent that enhances endpoint posture and user experience. It can gather telemetry for security analytics, enforce device posture checks (e.g., ensuring endpoint security software is running, OS is up to date), and even provide granular control over application access based on device health. Its integration with Zscaler Digital Experience (ZDX) offers deep visibility into user application performance, helping IT troubleshoot issues proactively and optimize the digital experience for employees. This comprehensive approach means Zscaler Client Connector acts as a key enabler for a secure, productive, and future-proof enterprise environment.
In essence, Zscaler Client Connector represents a paradigm shift in how organizations approach network security. By providing an intelligent, always-on, and identity-centric gateway to the Zero Trust Exchange, it empowers businesses to embrace cloud transformation and remote work securely and efficiently, future-proofing their operations against an ever-evolving threat landscape.