
The Foundation of Wireless Security for Modern Tech
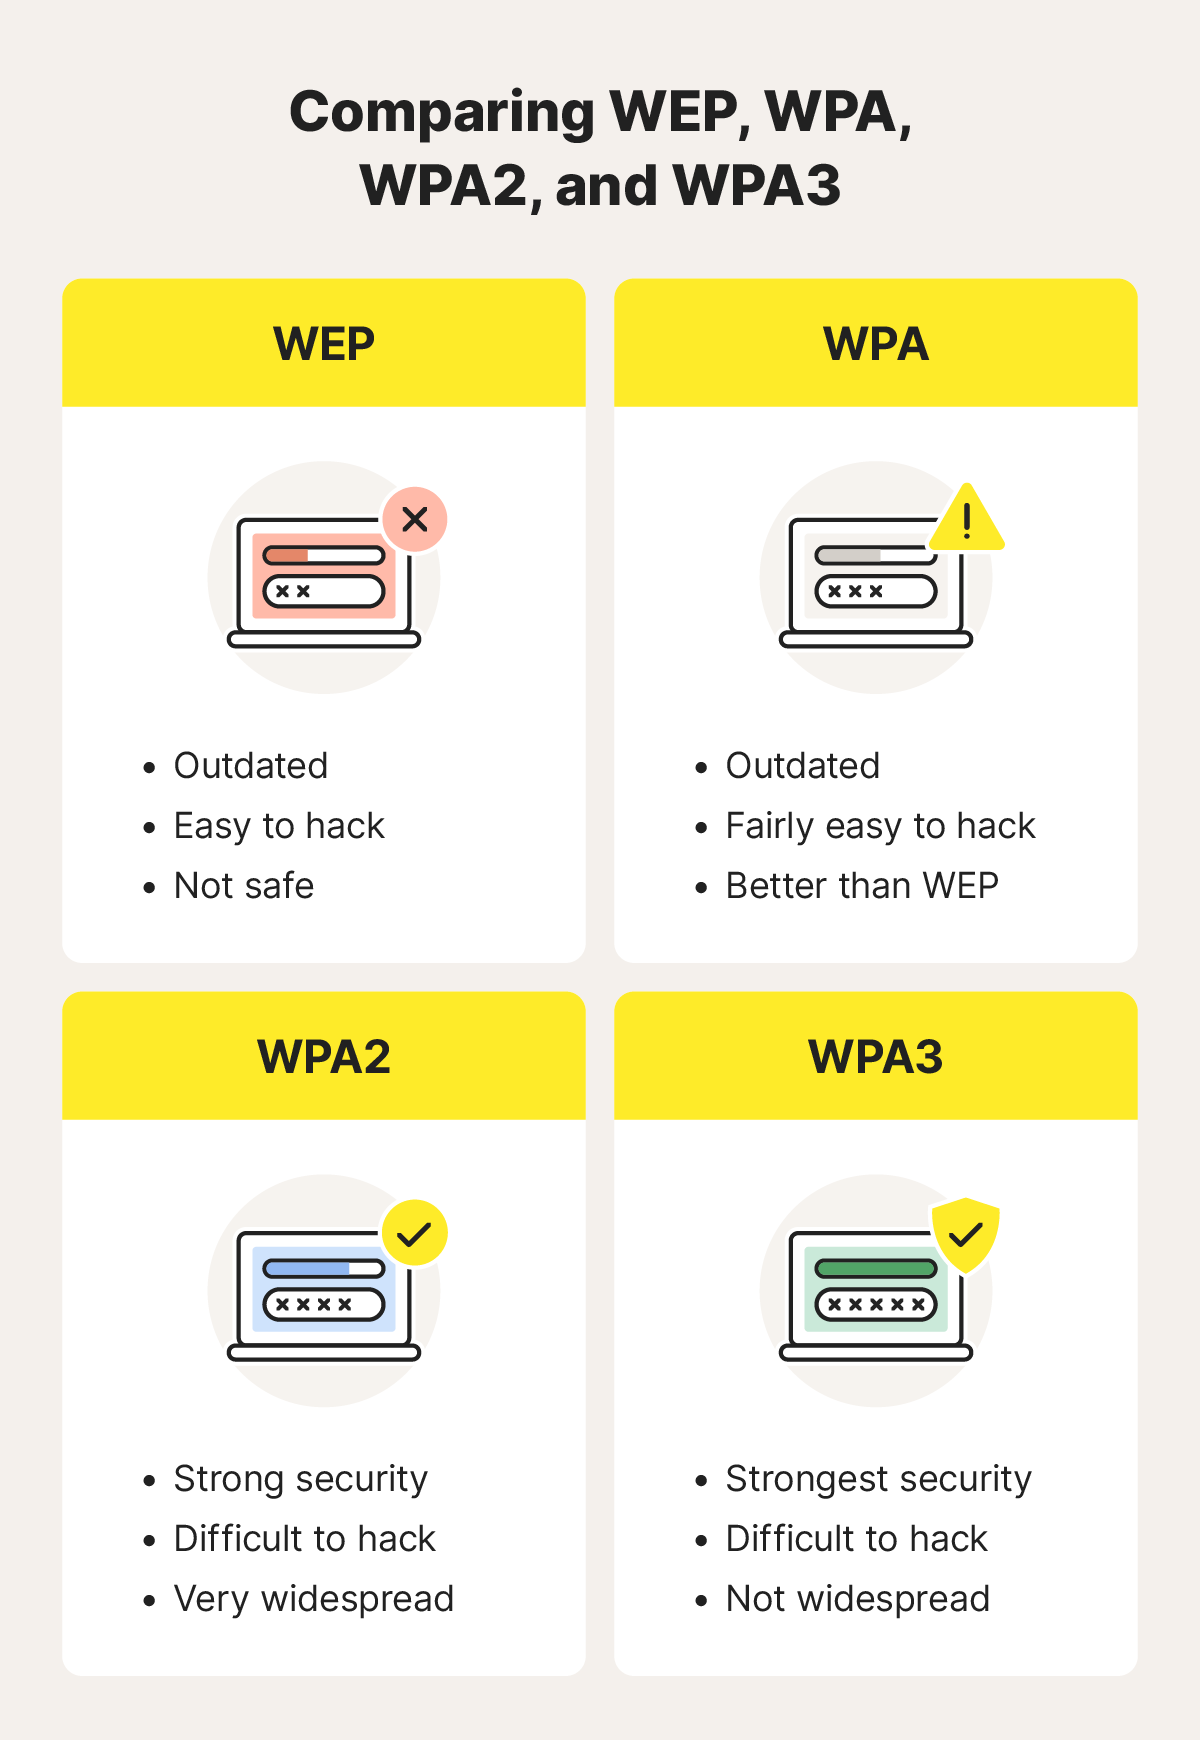
In an era increasingly defined by pervasive wireless connectivity, understanding the underlying security protocols that protect our digital interactions is paramount. For advanced technological systems, particularly within the burgeoning field of drone innovation, secure wireless communication is not merely a convenience but a critical operational necessity. WPA (Wi-Fi Protected Access) and WEP (Wired Equivalent Privacy) represent two key milestones in the evolution of Wi-Fi security standards, foundational to how data is safeguarded over wireless networks. While WEP is largely obsolete due to severe vulnerabilities, WPA, and its subsequent iterations (WPA2 and WPA3), form the bedrock of secure wireless networking today, directly impacting the integrity and reliability of numerous tech applications, including those vital to drone operations. From securing telemetry data and high-resolution video feeds to protecting mission-critical command and control links, these protocols are integral to the trusted deployment of modern autonomous and remotely operated systems.

WEP: A Legacy of Vulnerabilities
Wired Equivalent Privacy (WEP) was the first security algorithm included in the 802.11 wireless standard, ratified in 1999. Its primary objective was to provide wireless networks with a level of security comparable to that of traditional wired networks. WEP aimed to achieve this through confidentiality, preventing unauthorized parties from eavesdropping on data, and integrity, ensuring data packets weren’t tampered with during transmission.
At its core, WEP employed the RC4 stream cipher for encryption. This cipher, while initially considered robust, was implemented in WEP in a way that introduced critical flaws. A major weakness stemmed from the use of a relatively short Initialization Vector (IV), typically 24 bits, concatenated with a static WEP key. Because the IV was transmitted in plain text with each packet and reset frequently, the same key stream would inevitably be reused, especially on busy networks. This reuse, combined with mathematical vulnerabilities in the RC4 algorithm itself when used with weak key scheduling, allowed attackers to collect enough data packets to deduce the WEP key relatively quickly using statistical analysis.
The consequence of WEP’s inherent design flaws was a severely compromised security posture. By the early 2000s, easily accessible tools could crack WEP keys in minutes, rendering it ineffective against even moderately skilled attackers. For drone technology, a WEP-secured network would pose an unacceptable risk. Imagine a drone transmitting sensitive mapping data or performing critical infrastructure inspection over a WEP-protected Wi-Fi link; any malicious actor could intercept and potentially alter the data, compromise the drone’s command signals, or gain unauthorized access to its network. This rapid exposure of WEP’s vulnerabilities underscored the urgent need for more robust wireless security protocols, especially as wireless technology began its rapid expansion into mission-critical applications.
WPA: An Urgent Interim Solution
The glaring deficiencies of WEP necessitated a swift response from the Wi-Fi Alliance. Recognizing the need for an immediate upgrade while a more comprehensive solution (WPA2) was being developed, they introduced Wi-Fi Protected Access (WPA) in 2003. WPA was designed as an interim standard, primarily to address the most critical vulnerabilities of WEP without requiring entirely new hardware. This allowed device manufacturers to release firmware updates for existing WEP-compatible equipment, facilitating a quicker transition to enhanced security.
WPA significantly improved upon WEP by introducing two key enhancements: the Temporal Key Integrity Protocol (TKIP) and Message Integrity Code (MIC). TKIP was a stopgap measure that still used the RC4 stream cipher, but it fundamentally changed how encryption keys were handled. Instead of a static key, TKIP dynamically generated a new 128-bit per-packet key, incorporating a longer 48-bit IV, the station’s MAC address, and a master key. This dynamic key generation and per-packet key mixing largely mitigated the key reuse attacks that plagued WEP. Furthermore, TKIP implemented a key re-keying mechanism, where the master key would be refreshed at regular intervals, further complicating cryptanalysis.
The second major enhancement, MIC, addressed WEP’s lack of strong data integrity protection. MIC, also known as Michael, added a cryptographically strong integrity check to each packet. If a packet’s MIC was invalid (indicating tampering), the receiving station would drop the packet and potentially disconnect the client, preventing various injection attacks. While WPA was a significant leap forward from WEP, improving protection against both eavesdropping and data manipulation, it was still based on the RC4 cipher, which inherently carried some risks. TKIP itself was found to have some theoretical vulnerabilities, though much harder to exploit than WEP’s. Nevertheless, WPA served its purpose effectively as a bridge to a truly robust security standard, proving that quick, iterative security enhancements are vital in rapidly evolving tech landscapes like that of drone development and deployment.
WPA2: The Industry Standard for Secure Connectivity
Following WPA’s interim deployment, the full IEEE 802.11i standard was ratified in 2004, leading to the widespread adoption of WPA2 by 2006. WPA2 was not an incremental update but a complete overhaul, designed from the ground up to provide enterprise-grade security for all Wi-Fi networks. It became the mandatory certification for all Wi-Fi enabled products, solidifying its status as the de facto industry standard for secure wireless communication for over a decade. Its robustness and widespread implementation have been crucial for the secure evolution of numerous technologies, including the sophisticated wireless systems employed in modern drone operations.
Robust Protection with AES and CCMP
The cornerstone of WPA2’s superior security is its reliance on the Advanced Encryption Standard (AES) cipher. Unlike WEP and WPA, which used the less secure RC4, AES is a symmetric block cipher widely adopted by governments and security agencies worldwide for its strength and efficiency. WPA2 pairs AES with the Counter Mode with Cipher Block Chaining Message Authentication Code Protocol (CCMP), forming a highly secure and reliable encryption and integrity solution.
CCMP combines AES for data confidentiality with a strong Message Authentication Code (MAC) for data integrity and authentication. It effectively ensures that data transmitted over a WPA2 network remains confidential and untampered with. The CCMP protocol utilizes a 128-bit key size for AES encryption, providing significantly higher cryptographic strength compared to its predecessors. This robust encryption prevents unauthorized interception and decryption of data, making it virtually impossible for attackers to read wireless traffic. The integrity component ensures that if any part of a packet is altered during transmission, the receiving device will detect the change and discard the packet, protecting against data manipulation and injection attacks.
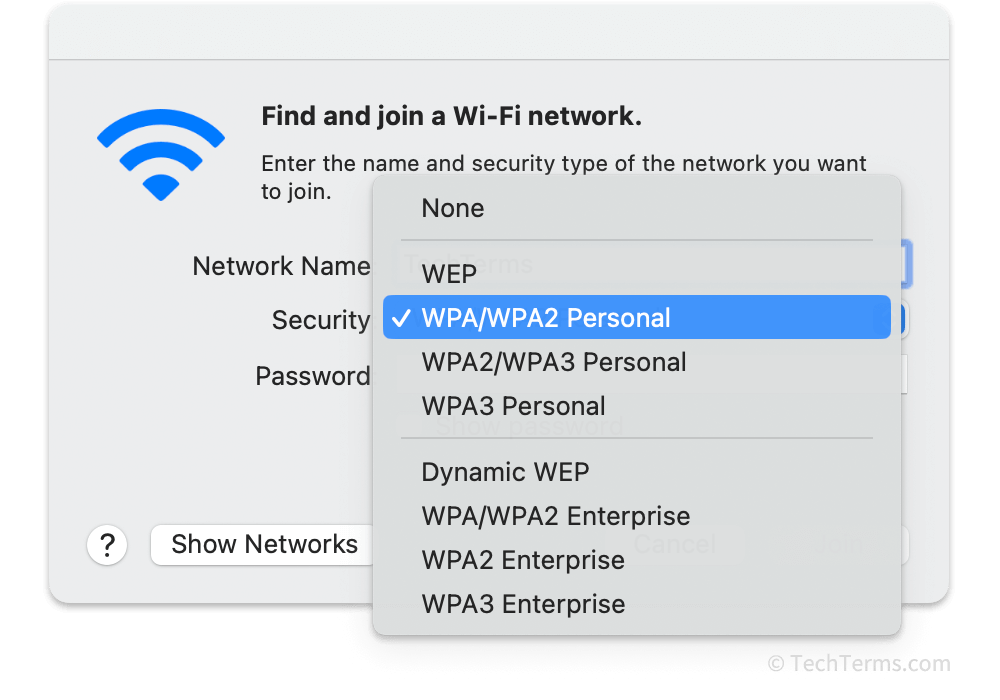
WPA2 offers two primary modes of operation: WPA2-Personal (often referred to as WPA2-PSK for Pre-Shared Key) and WPA2-Enterprise. WPA2-Personal is designed for home and small office networks, relying on a single shared passphrase that all devices use to connect. While effective, the security of WPA2-PSK largely depends on the strength of this passphrase. WPA2-Enterprise, on the other hand, provides a much higher level of security suitable for larger organizations and mission-critical applications. It uses 802.1X authentication, which integrates with a RADIUS (Remote Authentication Dial-In User Service) server to provide individual, dynamic authentication for each user or device. This means each connection gets its own unique encryption key, preventing a compromised single key from affecting the entire network and offering granular control over network access.
Relevance for Drone Operations and Data Integrity
For the evolving landscape of drone technology and innovation, WPA2’s robust security features are indispensable. Modern drones are increasingly networked devices, relying on wireless communication for a multitude of functions.
Firstly, control links and telemetry often utilize Wi-Fi or similar radio technologies, especially for ground control stations interfacing with the drone. Securing these links with WPA2-Enterprise is crucial to prevent unauthorized access to the drone’s controls, protecting against hijacking or interference. In situations where drones operate beyond visual line of sight (BVLOS) or in critical infrastructure inspections, the integrity of these links is paramount.
Secondly, payload data transmission is a significant aspect of advanced drone applications. Drones equipped with high-resolution cameras, thermal imagers, LiDAR sensors, or other remote sensing equipment generate vast amounts of sensitive data. Transmitting 4K video streams, detailed mapping data, or confidential inspection reports wirelessly requires strong encryption. WPA2 ensures that this data remains confidential during transit to ground stations or cloud services, protecting proprietary information, privacy of individuals, and sensitive infrastructure details.
Thirdly, the integration of drones into broader networked ecosystems necessitates WPA2. As drones become more autonomous and communicate with each other (drone swarms), with ground infrastructure, or with centralized management systems, securing these interconnected layers is vital. WPA2 provides the baseline for trusted communication within these complex networks, ensuring that data exchanged for collaborative missions, real-time analytics, or AI-driven decision-making is authentic and uncompromised. The integrity of collected data for mapping and remote sensing applications, upon which critical decisions are made, relies heavily on the secure transmission enabled by WPA2. Without such robust protection, the accuracy and trustworthiness of drone-derived insights could be severely undermined, posing significant risks to operational efficiency, safety, and regulatory compliance.
WPA3: The Next Frontier in Wireless Security
Despite WPA2’s enduring strength, the relentless evolution of cyber threats and the proliferation of internet-connected devices, including drones, demanded further advancements in wireless security. In 2018, the Wi-Fi Alliance introduced WPA3, representing the latest generation of Wi-Fi security protocols. WPA3 not only addresses some of WPA2’s theoretical vulnerabilities but also introduces new features designed to enhance security for personal, enterprise, and public Wi-Fi networks in an increasingly connected world. For the sophisticated and sensitive operations inherent in modern drone ecosystems, WPA3 promises a new level of assurance and resilience.
Enhanced Security Features
WPA3 brings several significant improvements over WPA2, particularly in areas like authentication, protection against dictionary attacks, and enhanced security for public Wi-Fi.
One of the most impactful changes in WPA3-Personal is the replacement of the Pre-Shared Key (PSK) handshake with Simultaneous Authentication of Equals (SAE), based on the Dragonfly key exchange. SAE provides much stronger protection against offline dictionary attacks, which are common against WPA2-PSK networks. Even if an attacker intercepts encrypted Wi-Fi traffic, SAE makes it significantly harder to guess the network password by trying countless combinations offline. This forward secrecy means that even if the network password is later compromised, past traffic cannot be decrypted, a critical feature for protecting long-term data transmissions from drones.
For open, unencrypted Wi-Fi networks (like those in public spaces), WPA3 introduces Opportunistic Wireless Encryption (OWE), also known as Wi-Fi Enhanced Open. OWE automatically encrypts traffic between the client and the access point, even without a password. While it doesn’t provide authentication or protect against malicious hotspots, it prevents passive eavesdropping, offering a basic layer of privacy that was entirely absent in previous open Wi-Fi connections. This feature is particularly relevant for drone operators who might need to transmit data over less secure public networks in certain scenarios, adding a crucial layer of confidentiality.
WPA3-Enterprise further enhances security with 192-bit cryptographic strength, aligning with the Commercial National Security Algorithm (CNSA) Suite requirements set by the U.S. National Security Agency. This provides an even higher level of protection for sensitive networks and data, employing stronger encryption algorithms (AES-256) and more robust key derivation methods. This level of security is essential for government, military, and critical infrastructure drone operations where data integrity and confidentiality are paramount.
Implications for Advanced Drone Ecosystems
The introduction of WPA3 holds profound implications for the future of advanced drone technology and innovation. As drone applications become more complex, encompassing autonomous flight, swarming capabilities, and deep integration with cloud-based AI and IoT platforms, the need for cutting-edge wireless security becomes increasingly urgent.
For autonomous drone swarms and collaborative missions, WPA3’s SAE provides a stronger foundation for inter-drone communication. Securing these communication channels with SAE can prevent sophisticated adversaries from compromising individual drone nodes or injecting malicious commands into the swarm, which could lead to mission failure or even physical harm.
In drone-as-a-service (DaaS) models and scenarios involving sensitive data, such as real-time surveillance, critical infrastructure monitoring, or delivery services, WPA3’s enhanced protection against dictionary attacks and forward secrecy ensures the long-term confidentiality of collected data. This is crucial for maintaining trust and regulatory compliance when handling sensitive information.
Furthermore, the increasing reliance on cloud integration and remote control centers for managing drone fleets means that securing the wireless links from drones to ground control stations and onward to cloud platforms is non-negotiable. WPA3’s 192-bit cryptographic strength in Enterprise mode provides the necessary assurances for highly regulated environments, protecting command and control links, telemetry, and payload data from sophisticated state-sponsored threats. WPA3 solidifies the security posture of the entire drone ecosystem, from the air to the ground and into the cloud, ensuring that the innovative potential of drones is realized with the highest levels of trust and resilience.
Securing Drone Communications: Beyond WPA/WEP/WPA2/WPA3
While WPA, WPA2, and WPA3 are specifically Wi-Fi security protocols, their principles—confidentiality, integrity, and authentication—are fundamental to the broader field of securing drone communications across various wireless technologies. Drones often utilize a mix of wireless standards, including custom radio links, cellular (4G/5G), and satellite communications, in addition to Wi-Fi. The core lessons learned from the evolution of Wi-Fi security are universally applicable and continually drive innovation in drone cybersecurity.
The continuous development of drone technology, including AI follow modes, autonomous flight, mapping, and remote sensing, hinges on the ability to transmit and receive data securely. This necessitates a comprehensive approach to cybersecurity that extends beyond just the choice of Wi-Fi security protocol. It includes, for instance, securing the custom radio links used for primary command and control, which often employ proprietary encryption and frequency hopping techniques to resist jamming and interception. Similarly, cellular data links, leveraging 4G or 5G networks, rely on their own robust cryptographic standards to protect drone communication over long distances.
Crucially, the focus on “Tech & Innovation” in drones demands an end-to-end security mindset. This means:
- Secure Boot and Firmware Integrity: Ensuring that the drone’s operating system and critical software are authentic and haven’t been tampered with from the moment the drone powers on.
- Hardware-Based Security: Incorporating trusted platform modules (TPMs) or secure enclaves within drone hardware to protect cryptographic keys and sensitive data.
- Application-Layer Encryption: Encrypting data at the application level before it’s transmitted, providing an additional layer of security independent of the underlying wireless protocol. This is particularly important for safeguarding sensitive payload data, such as high-resolution imagery or sensor readings.
- Threat Detection and Incident Response: Implementing systems capable of detecting anomalies in drone communication or behavior, and having established protocols for responding to security incidents.
- Regular Security Audits and Updates: The threat landscape is constantly evolving. Drones, like any advanced tech, require continuous monitoring, vulnerability assessments, and timely security patches to protect against emerging threats.
The trajectory from the vulnerabilities of WEP to the advanced protections of WPA3 illustrates a crucial principle in technological innovation: security is an ongoing process, not a static feature. For drone technology, where safety, privacy, and operational integrity are paramount, embracing and continually advancing these security paradigms across all communication channels is essential for realizing the full potential of this transformative technology. As drones become more integrated into critical infrastructure and everyday life, the sophistication of their communication security will be a defining factor in their trustworthiness and societal acceptance.