
The Imperative of Enhanced Digital Security
In an increasingly interconnected digital world, the bedrock of personal and operational security—the traditional password—has shown its vulnerabilities. As our lives, businesses, and critical technologies like drones become more reliant on digital systems, the integrity of account access is paramount. The landscape of cyber threats is continuously evolving, with sophisticated phishing attacks, brute-force attempts, and credential stuffing becoming commonplace. A single compromised password can lead to a cascade of security breaches, exposing sensitive personal information, proprietary business data, or even granting unauthorized control over advanced technological assets. For instance, in the realm of drone technology, a compromised account could mean unauthorized access to flight plans, sensitive mapping data, remote sensing information, or even the direct control interface of a sophisticated UAV. The intellectual property embedded in flight algorithms, collected data, and operational strategies represents significant value, making robust security measures not just advisable, but essential. Two-step verification (2SV) emerges as a critical defense mechanism, adding a vital layer of protection that goes beyond the singular reliance on a password to safeguard digital identities and assets.
Deconstructing Two-Step Verification (2SV)
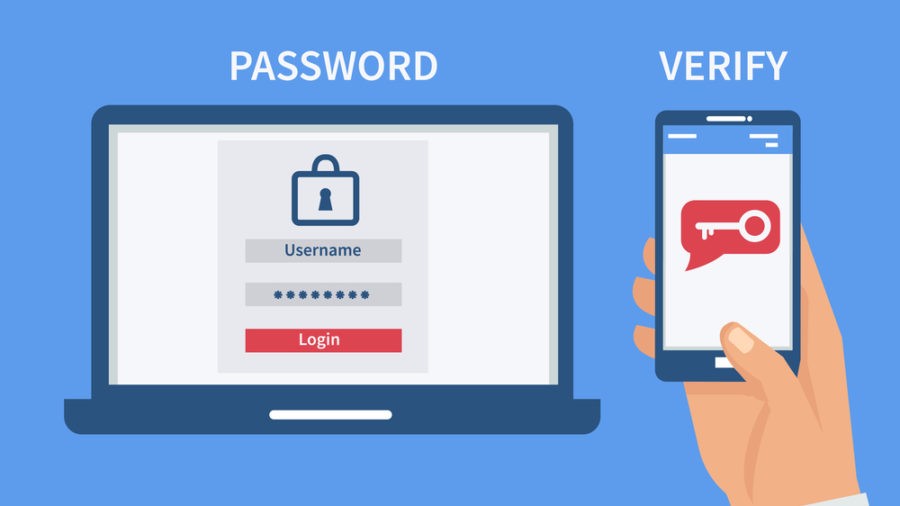
Two-step verification, often interchangeably referred to as two-factor authentication (2FA) in common parlance, is a security process that requires two distinct forms of identification before granting access to an account or system. Its fundamental principle is built upon validating a user’s identity using a combination of two independent verification methods, typically drawn from different categories. This multi-layered approach significantly enhances security by making it exponentially harder for unauthorized individuals to gain entry, even if they manage to acquire one of the authentication factors.
The Core Concept: Something You Know, Something You Have, Something You Are
The strength of 2SV lies in its requirement for proof from at least two of three distinct categories:
- Something you know: This is typically your password, PIN, or a secret question—information that only you should possess. It’s the primary layer of defense.
- Something you have: This refers to a physical item in your possession, such as a smartphone, a hardware security key, or a smart card. The system sends a code or prompt to this device, or the device itself generates a unique code.
- Something you are: This involves biometrics, unique physical attributes of your body, like a fingerprint, facial scan, or retina scan.
For 2SV to function, an attacker would need to compromise not just your password (something you know), but also gain access to your physical device (something you have) or replicate your unique biological markers (something you are). This dual requirement forms a formidable barrier.
Common Second Factor Types
The second factor, the crucial additional layer, can manifest in several forms, each offering varying degrees of convenience and security:
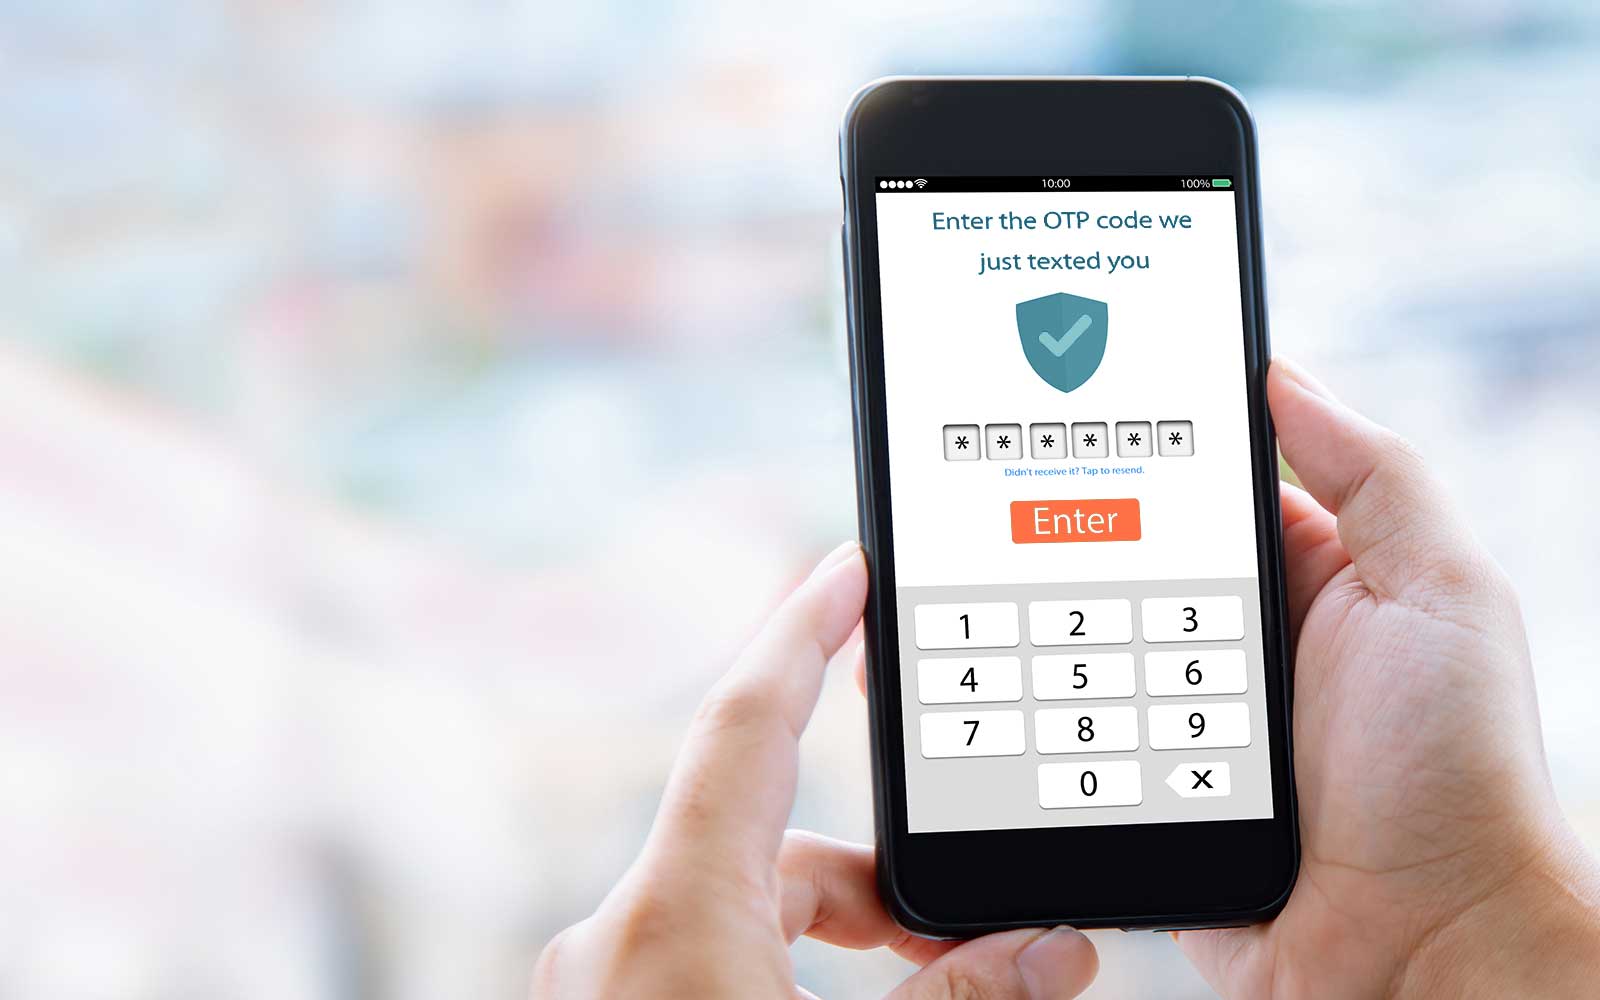
- SMS/Text Codes: One of the most common and user-friendly methods, where a unique, time-sensitive code is sent to your registered mobile phone via SMS after you enter your password. While convenient, this method can be susceptible to SIM swap attacks, where attackers trick carriers into porting your phone number to a device they control.
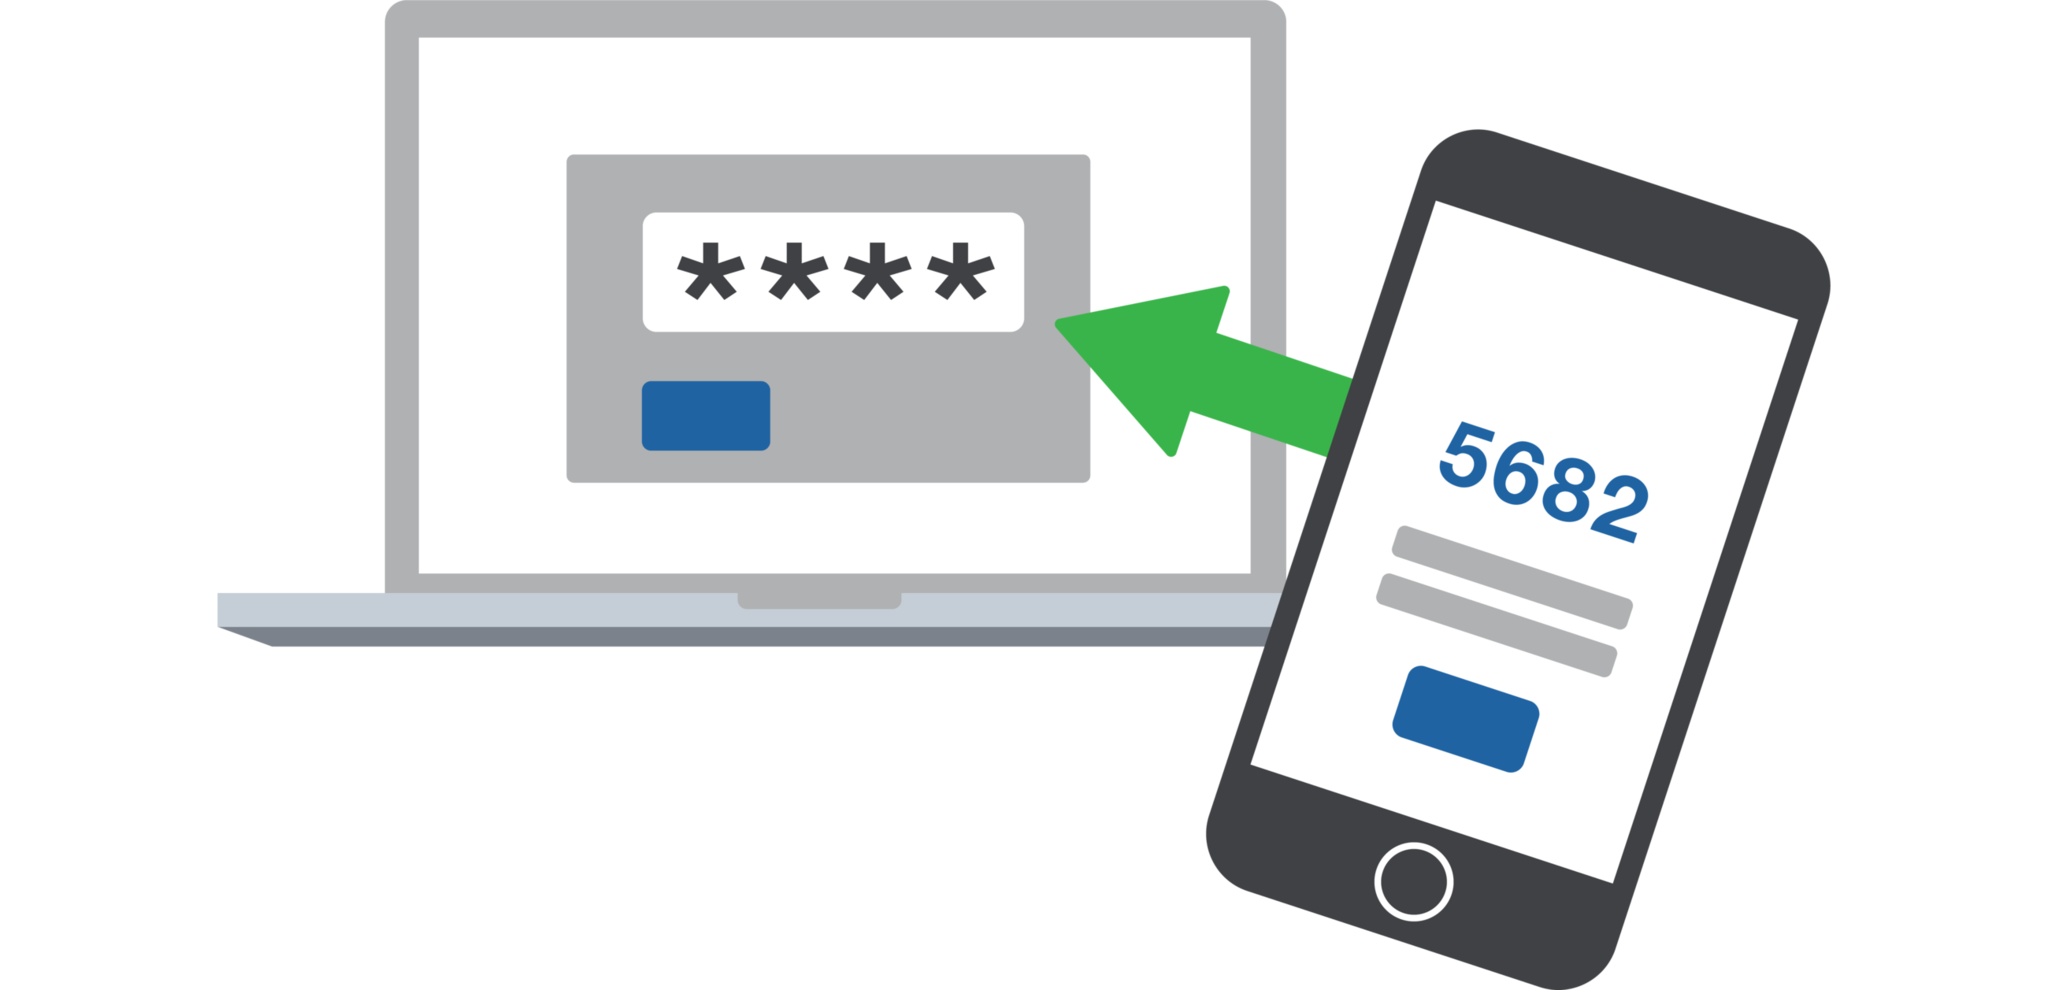
- Authenticator Apps: Applications like Google Authenticator, Microsoft Authenticator, or Authy generate time-based one-time passwords (TOTP) directly on your smartphone, even without an internet connection. These codes refresh every 30-60 seconds. They are generally more secure than SMS codes as they are not reliant on cellular network security.
- Hardware Security Keys: Devices like YubiKey or Google Titan Security Key are physical USB or NFC tokens that plug into or interact with your device. When prompted, you simply tap or press the key. These are considered among the most secure 2SV methods as they are highly resistant to phishing and man-in-the-middle attacks, relying on strong cryptographic protocols.
- Biometrics: Increasingly integrated into modern devices, biometric authentication uses unique biological identifiers such as fingerprints, facial recognition (e.g., Face ID), or iris scans. This method offers high convenience and a strong level of security, as biometrics are exceptionally difficult to forge.
- Email Codes: Similar to SMS codes, a unique code is sent to a registered email address. While better than no 2SV, it is generally considered less secure than other methods because if an attacker gains access to your primary email, they might bypass this second factor.
How 2SV Works in Practice
The process of 2SV is designed to be straightforward for the legitimate user:
- Initiation: You attempt to log into an account or service (e.g., a drone flight management platform, a cloud storage service for aerial footage, or an app controlling a UAV).
- First Factor: You provide your username and password (the “something you know”).
- Second Factor Prompt: The system verifies your password and, if correct, immediately prompts you for the second factor.
- Second Factor Input: You then provide the second factor, whether it’s entering a code from an authenticator app, tapping a security key, confirming a prompt on your phone, or scanning your fingerprint.
- Access Granted: If both factors are correctly provided, the system grants you access to your account.
This sequential validation ensures that even if an attacker manages to steal your password, they are still locked out without the second, independent piece of information.
The Benefits Beyond Basic Protection
The implementation of two-step verification offers a multitude of advantages that extend far beyond simply having a longer or more complex password. It fundamentally alters the security posture of an individual or an organization, particularly critical in technologically advanced fields.
Robust Defense Against Credential Theft
The primary and most significant benefit of 2SV is its unparalleled ability to thwart credential theft. In scenarios where a password has been compromised through phishing, malware, or data breaches, 2SV acts as a crucial safety net. An attacker possessing only your password would still be unable to log in, as they lack the second factor—be it your physical phone, security key, or biometric signature. This renders a vast majority of password-based attacks ineffective, protecting accounts from unauthorized access even when basic security measures have failed. For drone operators, this means the sensitive data collected during missions—thermal imagery for inspections, high-resolution maps for agriculture, or even flight paths for delivery routes—remains secure against opportunistic attackers who might gain access to login credentials through less sophisticated means.
Safeguarding Sensitive Data and Operations
In sectors heavily reliant on technology and innovation, such as drone operations and aerial mapping, the data generated is often highly sensitive, valuable, or critical for decision-making. 2SV ensures that access to platforms managing this data, such as cloud repositories for aerial imagery, mission planning software, or sophisticated AI analytics dashboards, is restricted to authorized personnel only. Consider the implications for a commercial drone enterprise:
- Flight Logs and Mission Plans: Detailed records of flight paths, operational parameters, and target areas could be exploited by competitors or malicious actors. 2SV protects these records.
- Proprietary Mapping Data: High-resolution photogrammetry or LiDAR data, often containing details of infrastructure, land use, or private properties, requires stringent access controls.
- Remote Sensing Information: Data derived from agricultural surveys, environmental monitoring, or construction progress tracking can have significant financial and strategic value, necessitating robust protection.
- Drone Control Apps: While direct real-time drone control often uses separate secure links, many advanced functionalities and post-flight data analysis are managed through web or mobile applications. Securing these ensures operational integrity.
By enforcing 2SV, organizations can maintain the confidentiality and integrity of their digital assets, preventing data breaches that could lead to financial losses, reputational damage, or compromise of operational security.
Compliance and Trust
Implementing 2SV is also a significant step towards meeting various industry regulations and data protection standards. Many compliance frameworks (e.g., GDPR, HIPAA, NIST) either recommend or mandate multi-factor authentication for accessing sensitive data. By adopting 2SV, businesses demonstrate a proactive commitment to data security, fostering trust among clients, partners, and regulators. This commitment is particularly important in burgeoning fields like drone technology, where public perception and regulatory scrutiny are high. Users are more likely to trust platforms and services that visibly prioritize their security, enhancing the overall credibility and adoption of innovative tech solutions.
Implementing and Managing 2SV in the Modern Tech Landscape
Successfully integrating two-step verification into a digital ecosystem requires careful consideration of security needs, user experience, and ongoing management. For developers of drone-related software and services, as well as for end-users, understanding best practices is crucial.
Choosing the Right 2SV Method
The selection of a 2SV method should be a thoughtful balance between the level of security required and the convenience offered to users.
- For General Users/Lower Risk Accounts: SMS-based verification can be a good starting point due to its ease of setup and familiarity for most users. However, it’s important to educate users about SIM swap risks.
- For Moderate Risk Accounts/Tech-Savvy Users: Authenticator apps provide a stronger level of security, are not reliant on cellular networks, and are generally user-friendly once set up. These are often recommended for accessing cloud services, social media, and personal email.
- For High-Value Accounts/Critical Infrastructure: Hardware security keys offer the highest level of protection against phishing and sophisticated attacks. They are ideal for administrators, developers, and individuals managing highly sensitive data, such as the core systems of a drone fleet or critical mapping infrastructure.
- For Mobile-First Experiences: Biometrics (fingerprint, facial recognition) offer unparalleled convenience and strong security, making them excellent choices for mobile applications, including drone control and mission planning apps, where quick and secure access is essential.
Developers of drone software should aim to offer multiple 2SV options to cater to diverse user needs and security preferences, guiding users towards the most secure options for their specific use cases.
Best Practices for Users
For 2SV to be truly effective, users must embrace and properly manage it:
- Activate 2SV Everywhere Possible: The more accounts protected by 2SV, the smaller the attack surface for cybercriminals. Users should make it a default habit to enable this feature on all supported services, especially those linked to drone operations or sensitive data.
- Protect Recovery Codes: Most 2SV systems provide recovery codes in case you lose access to your second factor (e.g., a lost phone). These codes are essentially backup keys to your account and should be stored securely offline, away from your primary devices.
- Be Wary of Social Engineering: Phishing attacks can sometimes trick users into revealing their 2SV codes. Always verify the legitimacy of any request for your second factor and never enter codes onto unfamiliar or suspicious websites. Legitimate services typically don’t ask for your code directly via email or text.
- Keep Software Updated: Ensure that operating systems, authenticator apps, and drone-related applications are always updated to their latest versions to benefit from the newest security patches and features.
Implications for Developers and Platform Providers
Integrating 2SV is not just a feature; it’s a commitment to user security and trust.
- Seamless Integration: Developers building drone control apps, data analytics platforms, or cloud services for aerial data must ensure that 2SV integration is smooth and intuitive, minimizing friction for the end-user while maximizing security. A cumbersome 2SV process can lead to user frustration and disengagement.
- User Education: Platforms should actively educate users on the importance of 2SV, how to enable it, and how to choose the most appropriate method. Clear, concise guides and in-app prompts can significantly boost adoption rates.
- Robust Backend Support: The underlying infrastructure supporting 2SV must be secure, scalable, and reliable to handle authentication requests efficiently and prevent service interruptions. This includes secure generation and delivery of one-time codes and robust handling of hardware key protocols.
The Future of Authentication: Beyond 2SV
While two-step verification represents a significant leap forward in digital security, the innovation in authentication methods continues to evolve. The future aims for even more seamless, robust, and user-friendly security paradigms, building upon the principles established by 2SV.
Multi-Factor Authentication (MFA) vs. 2SV
It’s important to note the nuanced difference between 2SV and Multi-Factor Authentication (MFA). While often used interchangeably, 2SV is a specific instance of MFA, requiring precisely two factors. MFA is a broader term that encompasses any authentication system requiring two or more distinct factors. This distinction becomes relevant as security needs intensify, where some critical systems might demand three or more factors for access, further fortifying protection for highly sensitive drone operations or mission-critical data.
Passwordless Authentication and Adaptive Security
The ultimate goal in authentication is often cited as “passwordless” access—eliminating the need for passwords altogether, which are inherently vulnerable. Technologies like the FIDO (Fast IDentify Online) Alliance standards are paving the way for passwordless authentication using cryptographic security keys (both hardware and software-based) combined with biometrics. This approach shifts the burden of security from user-remembered secrets to device-bound credentials, dramatically reducing phishing risks and improving user experience.
Beyond passwordless systems, the concept of adaptive or contextual security is gaining traction. This involves authentication systems that dynamically adjust the level of security required based on various contextual cues:
- Location: Is the user logging in from a familiar location or a suspicious new one?
- Device: Is the device typically used by the user, or is it an unfamiliar one?
- Time of Day: Is the access attempt occurring outside normal operating hours?
- Behavioral Biometrics: Analyzing patterns of typing, mouse movements, or how a user interacts with a touch screen to continuously verify identity without explicit prompts.
For advanced tech sectors like drone technology, adaptive security holds immense promise. Imagine a drone control system that automatically requests an additional biometric scan if a pilot attempts to initiate a flight from an unusual geographic location, or if the system detects anomalous behavioral patterns. These innovations will further secure the intricate operations of autonomous drones, AI-driven analytics platforms, and the vast networks that support remote sensing and mapping, ensuring that only trusted users with verified intent can interact with and control these powerful technologies. The journey of digital security is continuous, with 2SV serving as a vital, present-day benchmark for protecting our increasingly digital world.