
The rapidly evolving landscape of drone technology, encompassing everything from autonomous flight and sophisticated mapping to remote sensing and AI-powered operations, has ushered in an era of unprecedented capabilities. Yet, with great power comes the paramount need for robust security. As drones become integral tools across industries, from agriculture and construction to defense and public safety, the digital ecosystems supporting them – flight planning software, cloud storage for data, remote control applications, and user accounts – become attractive targets for malicious actors. In this environment, traditional password-based security is increasingly insufficient. This is where Two-Factor Authorization (2FA), a cornerstone of modern cybersecurity, emerges as an indispensable layer of defense for securing access to sensitive drone technology and the valuable data it generates.
The Evolving Landscape of Digital Security in Drone Technology
The drone industry, a vibrant hub of innovation under the broader umbrella of Tech & Innovation, constantly pushes the boundaries of what is possible. Autonomous flight systems leverage advanced algorithms for self-navigation and decision-making. High-resolution sensors capture intricate details for 3D mapping and infrastructure inspection. Remote sensing applications analyze vast tracts of land for environmental monitoring or precision agriculture. Each of these advancements relies heavily on interconnected digital systems – from the user interfaces on a remote controller or a smartphone app, to cloud-based processing platforms, and the drone’s onboard firmware.
The sheer volume and sensitivity of the data collected by modern drones, combined with the potential for direct operational interference, elevate the importance of digital security. A compromised drone account could lead to unauthorized access to flight plans, theft of proprietary mapping data, or even the hijacking of a drone itself. Furthermore, compliance with data protection regulations, such as GDPR or industry-specific security standards, necessitates proactive measures to safeguard information. Relying solely on a username and password, which can be vulnerable to brute-force attacks, phishing, or credential stuffing, is no longer a viable strategy for protecting these critical assets. The imperative is to move beyond single-factor authentication towards more resilient mechanisms that incorporate multiple, distinct layers of verification.
Deconstructing Two-Factor Authorization (2FA)
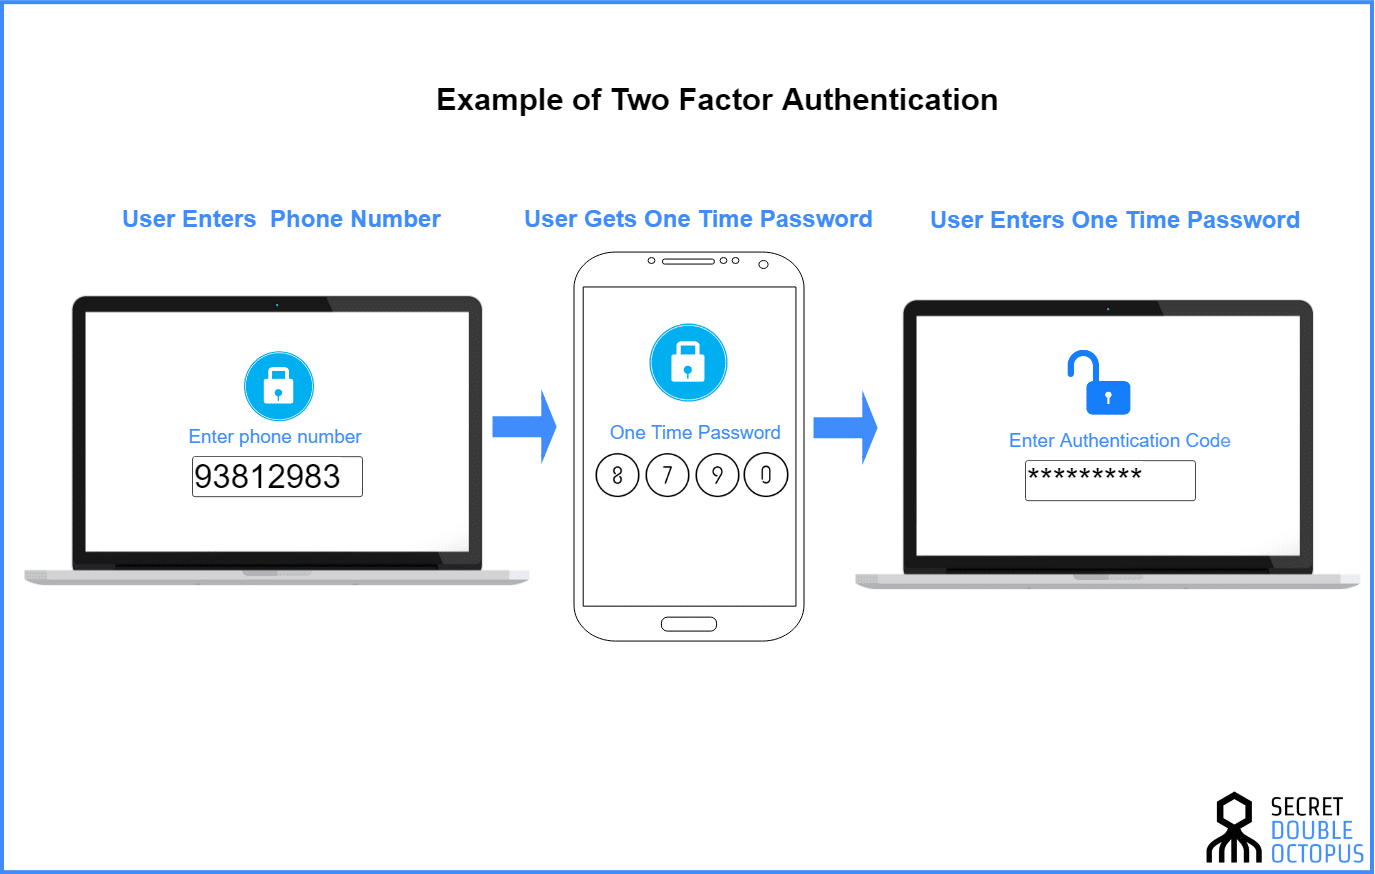
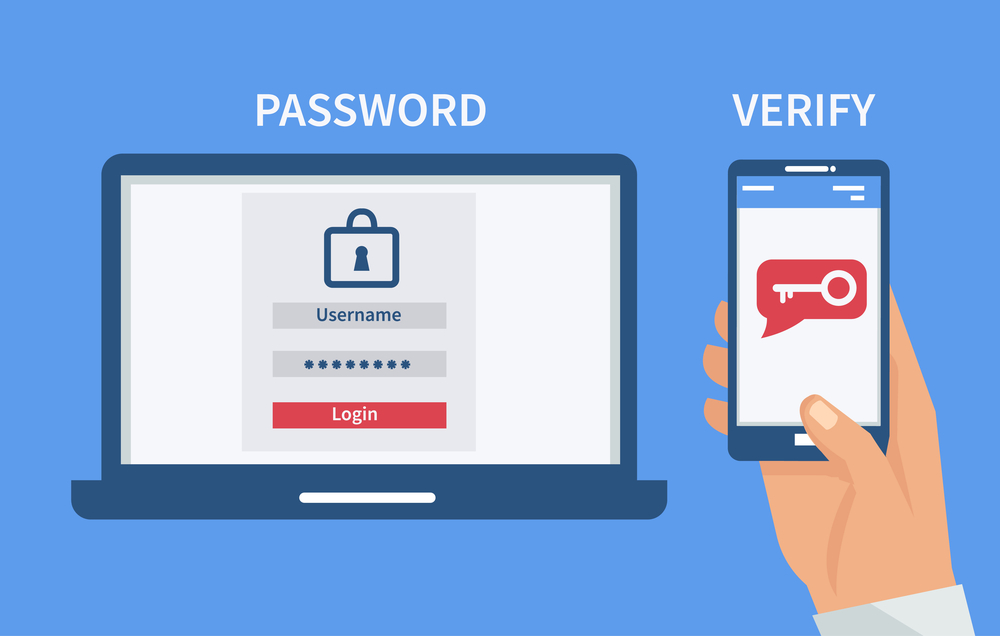
At its core, Two-Factor Authorization (2FA) is a security process where users provide two different authentication factors to verify their identity. It’s designed to provide a significantly higher level of security than a simple password because compromising one factor typically isn’t enough to gain access. Even if a cybercriminal obtains your password, they would still need the second factor to breach the account.
The Core Principle: Something You Know, Have, or Are
The foundation of 2FA lies in combining distinct categories of authentication factors. These are traditionally categorized as:
- Something You Know (Knowledge Factor): This is the most common factor, typically a password, PIN, or a secret question answer. It relies on information that only the legitimate user is supposed to know.
- Something You Have (Possession Factor): This refers to a physical item or device that the legitimate user possesses. Examples include a smartphone, a hardware security token, or a smart card. The device generates a code, receives an SMS, or presents a biometric prompt.
- Something You Are (Inherence Factor): This involves unique biological attributes of the user, commonly referred to as biometrics. Examples include fingerprints, facial recognition, iris scans, or voice recognition.
For an authentication system to be considered “two-factor,” it must combine at least two distinct types of these factors. For instance, combining a password (something you know) with a code sent to your smartphone (something you have) constitutes 2FA. Combining a password with a fingerprint scan is also 2FA. However, requiring two passwords or two PINs is not 2FA, as both fall under the “something you know” category.
Common Implementations of 2FA in Tech
The practical application of 2FA manifests in various forms, each with its own advantages and levels of convenience:
- SMS-based Codes: One of the most widespread methods, where a one-time passcode (OTP) is sent via SMS to a registered mobile number. While convenient, it’s susceptible to “SIM swapping” attacks where an attacker transfers the victim’s phone number to a new SIM card under their control.
- Authenticator Apps (Time-based One-Time Passwords – TOTP): Apps like Google Authenticator, Authy, or Microsoft Authenticator generate a new six-digit code every 30-60 seconds. These codes are generated algorithmically and don’t require network connectivity once set up, making them generally more secure than SMS codes.
- Biometrics: Increasingly common on modern devices, biometrics like fingerprint readers and facial recognition (e.g., Apple’s Face ID) offer a seamless and highly secure second factor, leveraging the “something you are” category.
- Hardware Security Keys: Physical devices (e.g., YubiKey) that plug into a USB port or connect wirelessly. They use cryptographic protocols to verify identity and are considered among the most secure forms of 2FA, as they are resistant to phishing.
- Email-based Codes: Similar to SMS, a one-time code is sent to a registered email address. This method’s security depends heavily on the security of the email account itself.
Why 2FA is Critical for Drone Operations and Data Integrity
The unique characteristics of drone technology – ranging from mission-critical applications to the collection of highly sensitive data – make the implementation of 2FA not just a best practice, but an essential security requirement.
Protecting Drone Control Systems and Platforms
Drone operations are managed through a complex web of software and online platforms. This includes manufacturer portals for registering drones and accessing firmware updates, flight planning applications that map out mission parameters, and cloud-based services for storing flight logs and processing data. Unauthorized access to any of these systems poses significant risks:
- Compromised Flight Operations: If a malicious actor gains access to a flight planning account, they could potentially alter mission parameters, inject false data, or even take control of a drone if the platform allows for direct remote operation. This could lead to mission failure, property damage, or in worst-case scenarios, endanger public safety.
- Disruption of Services: Unauthorized access could lead to the disabling of accounts, deletion of critical flight records, or denial of service, causing significant operational downtime and financial losses for businesses reliant on drone fleets.
- Intellectual Property Theft: Flight paths, operational methodologies, and custom configurations stored in these platforms represent valuable intellectual property. Securing access ensures these proprietary details remain confidential.
By enabling 2FA on all user accounts associated with drone management platforms, operators significantly reduce the risk of unauthorized takeovers, ensuring that only verified personnel can access and manage these critical systems.
Safeguarding Sensitive Data
Drones are powerful data collection instruments. Whether it’s high-resolution imagery for detailed mapping, thermal data for industrial inspections, or multispectral data for agricultural analysis, the information gathered can be highly sensitive, proprietary, or even classified.
- Proprietary Business Data: For companies using drones for infrastructure inspection, resource management, or construction progress monitoring, the data collected is often proprietary and forms the basis of critical business decisions. A breach could expose trade secrets or give competitors an unfair advantage.
- Personal Identifiable Information (PII): Drones can inadvertently or intentionally collect PII, especially in urban environments. Protecting this data is a legal and ethical imperative.
- Defense and Security Applications: In sensitive fields like national security or law enforcement, drone-collected intelligence can be paramount. The integrity and confidentiality of this data are non-negotiable, often requiring the highest levels of authentication.
- Cloud Storage Security: Much of the data collected by drones is uploaded to cloud storage for processing, analysis, and archiving. Implementing 2FA on these cloud accounts is crucial to prevent unauthorized access to massive datasets, which could lead to data breaches, compliance violations, and reputational damage.
2FA acts as a critical barrier, ensuring that only authorized individuals can access, download, or manipulate these valuable and often sensitive datasets, thereby upholding data integrity and confidentiality.
Ensuring Operational Continuity and Compliance
Beyond direct security threats, the adoption of 2FA plays a vital role in maintaining operational continuity and meeting regulatory compliance demands within the drone industry.
- Mitigating Downtime: Security breaches can lead to significant operational disruptions, including system shutdowns, data recovery efforts, and forensic investigations. By preventing unauthorized access, 2FA minimizes the likelihood of such events, ensuring that drone operations can proceed without interruption.
- Meeting Regulatory Requirements: Many industries operate under stringent data security regulations (e.g., HIPAA for healthcare data, GDPR for personal data in the EU, various governmental and defense standards). Incorporating 2FA into data management protocols for drone-collected information helps organizations demonstrate due diligence and comply with these legal frameworks, avoiding hefty fines and legal repercussions.
- Building Trust: For service providers offering drone-based solutions, demonstrating a commitment to robust security, including 2FA, builds trust with clients, partners, and regulators, enhancing their market credibility.
Implementing 2FA in Your Drone Ecosystem
The widespread adoption of 2FA across the drone ecosystem is a proactive step towards a more secure future for autonomous systems and data.
Best Practices for Adoption
For drone operators, businesses, and platform developers, several best practices ensure effective 2FA implementation:
- Mandate 2FA for All Critical Accounts: Ensure that all user accounts related to drone manufacturers’ platforms, flight planning software, cloud storage services, and any custom applications are protected with 2FA. Make it a non-negotiable security policy.
- Prioritize Strong Secondary Factors: While SMS-based 2FA is better than none, encourage or mandate the use of more secure options like authenticator apps (TOTP) or hardware security keys, which are less susceptible to common attack vectors.
- Educate Users: Provide clear instructions and training to all personnel on how to enable and use 2FA. Emphasize the “why” behind it – the risks it mitigates and the benefits it provides.
- Secure Recovery Options: Establish secure procedures for account recovery in cases where a user loses their secondary authentication device. These procedures should be robust enough to prevent unauthorized recovery but flexible enough to be usable by legitimate users.
- Regular Security Audits: Periodically review and audit the security protocols of all drone-related platforms and applications to ensure 2FA is consistently applied and remains effective against evolving threats.
The Future of Authentication in Autonomous Systems
As drone technology advances, so too will the methods for securing it. The future of authentication in autonomous systems is likely to move beyond static 2FA to more dynamic and adaptive approaches:
- Continuous Authentication: Instead of a single authentication event at login, continuous authentication systems will monitor user behavior (e.g., typing patterns, mouse movements, location, device characteristics) throughout a session. Any deviation from the norm could trigger a re-authentication prompt or flag suspicious activity.
- AI and Machine Learning Integration: AI will play an increasingly significant role in identifying anomalous behavior patterns, predicting potential threats, and adapting security measures in real-time, making authentication more intelligent and proactive.
- Hardware-Level Security: Advanced drones may integrate more sophisticated hardware-level security features, such as trusted platform modules (TPMs) or secure enclaves, which can store cryptographic keys and perform authentication processes in isolation from the main operating system, making them highly resistant to software-based attacks.
- Decentralized Identity: Blockchain and decentralized identity solutions could offer new paradigms for managing user identities and access controls, potentially enhancing security and privacy for drone operators interacting with multiple platforms.
Challenges and Considerations
While 2FA significantly bolsters security, its implementation is not without challenges. One primary consideration is the balance between enhanced security and user convenience. Adding an extra step to the login process can sometimes be perceived as cumbersome, leading to user resistance. Organizations must clearly communicate the benefits and streamline the process as much as possible.
Another crucial aspect is planning for recovery scenarios. What happens if a user loses their phone (the “something you have” factor) or forgets their authenticator app’s backup codes? Robust, yet secure, account recovery mechanisms are essential to prevent legitimate users from being locked out, without creating new vulnerabilities for attackers.
Finally, while 2FA protects against many common attacks, it’s not a silver bullet. Sophisticated phishing techniques can sometimes trick users into revealing their second factor, or “man-in-the-middle” attacks can intercept authentication codes. Therefore, ongoing user education and cybersecurity awareness training remain vital. Drone operators must understand the importance of vigilance against social engineering tactics and continuously update their knowledge on evolving cyber threats.
In conclusion, as drones continue to revolutionize various sectors and integrate deeply into our technological infrastructure, safeguarding their operational integrity and the vast amounts of data they generate is paramount. Two-Factor Authorization stands as a fundamental pillar in this defense strategy, offering a pragmatic and highly effective means to protect against unauthorized access, ensuring the security, reliability, and trustworthiness of the burgeoning drone ecosystem.