
The Domain Name System (DNS) is an indispensable backbone of the internet, a foundational technology that underpins virtually every networked interaction. For those exploring the cutting edge of tech and innovation, from autonomous drones to sophisticated remote sensing platforms, understanding DNS—and specifically its designated ports—is critical. DNS acts as the internet’s phonebook, translating human-readable domain names (like example.com) into machine-readable IP addresses (like 192.0.2.1). This seemingly simple function is what allows devices, whether a smartphone or an advanced drone, to locate and communicate with servers and services across the globe.
The Core Function of DNS in Modern Tech
At its heart, DNS solves a fundamental problem: while humans remember names, computers operate on numerical addresses. Without DNS, users would need to memorize the IP address for every website, cloud service, or remote server they wished to access, an impractical and unwieldy task. For sophisticated tech, particularly in the realm of autonomous systems and connected devices, DNS is even more crucial.
Consider a drone operating with AI follow mode. This feature often relies on cloud-based processing or real-time communication with a ground control station. To connect to these remote services, the drone’s internal systems first perform a DNS lookup to resolve the hostname of the cloud server or ground control platform into an IP address. Similarly, for remote sensing platforms uploading vast quantities of data to designated data centers, DNS ensures these systems can reliably find and establish connections with their intended destinations. Firmware updates, mapping data synchronization, and even remote diagnostics all depend on this invisible layer of name resolution. Therefore, DNS isn’t merely a convenience; it’s a critical component enabling the connectivity and functionality that define modern tech innovation. Its reliability and efficiency directly impact the performance and capabilities of any internet-enabled device or system.
Understanding DNS Ports: UDP 53 and TCP 53
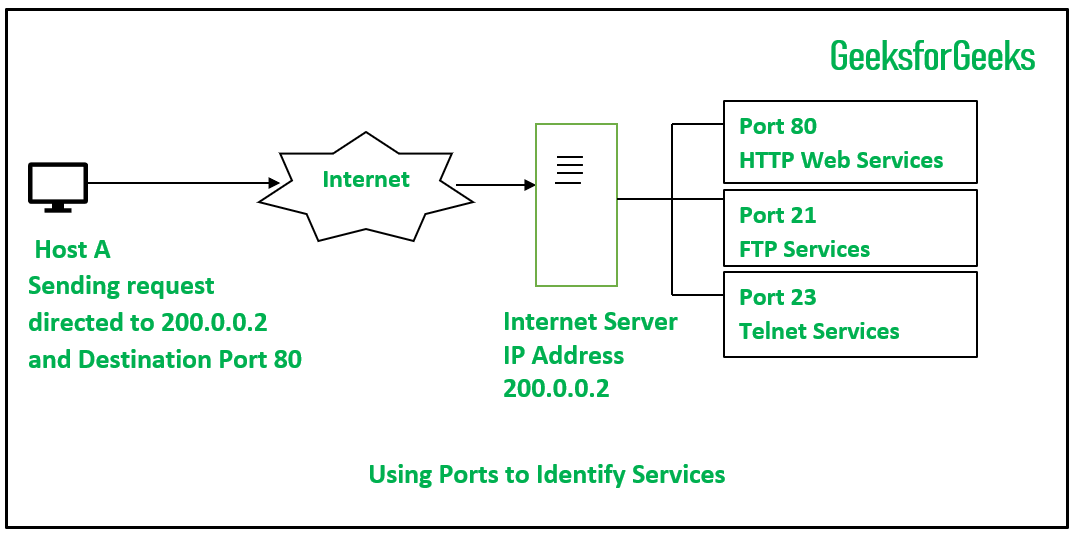
While DNS’s function is relatively straightforward, its implementation involves specific communication protocols and designated ports to ensure efficient and reliable operation. DNS primarily utilizes two distinct ports, both numbered 53, but differentiated by their underlying transport protocols: User Datagram Protocol (UDP) and Transmission Control Protocol (TCP).
UDP Port 53: The Workhorse for Queries
UDP Port 53 is the primary port used for standard DNS queries. When a client (be it a computer, a drone’s onboard system, or a sensor array) needs to resolve a domain name, it typically sends a DNS query packet to a DNS server using UDP Port 53. UDP is a connectionless protocol, meaning it doesn’t establish a persistent connection before sending data. This makes it fast and efficient, which is ideal for the small, quick requests and responses characteristic of most DNS lookups.
The process is asynchronous: the client sends a query and awaits a response. If a response isn’t received within a certain timeframe, the client might retransmit the query or try another DNS server. This efficiency is paramount for devices requiring rapid access to remote resources, such as drones performing real-time data streaming or AI services that need quick lookups for cloud-based inference engines. The lightweight nature of UDP minimizes overhead, conserving bandwidth and processing power, which can be critical for devices with limited resources, like many IoT devices and autonomous systems.
TCP Port 53: Ensuring Reliability for Larger Data Transfers
While UDP 53 handles the bulk of day-to-day DNS queries, TCP Port 53 plays a vital role in more specialized DNS operations, primarily DNS zone transfers. A DNS zone transfer is the process by which a secondary DNS server requests and receives a complete copy of a DNS zone’s database from a primary DNS server. This ensures that all authoritative DNS servers for a given domain have consistent and up-to-date information.
TCP (Transmission Control Protocol) is a connection-oriented protocol, meaning it establishes a reliable, ordered, and error-checked connection between two endpoints before data transmission. This reliability is crucial for zone transfers, where the integrity and completeness of the data are paramount. If a single record were corrupted or lost during a transfer, it could lead to widespread resolution failures for that domain. TCP’s built-in mechanisms for retransmission and flow control prevent such issues, making it the preferred choice for these larger, more critical data exchanges. Additionally, TCP Port 53 is sometimes used for DNS queries when the response size exceeds the typical UDP packet limits (around 512 bytes, though extensions allow for larger UDP packets). For instance, responses involving DNS Security Extensions (DNSSEC) often exceed these limits, prompting the client and server to switch to TCP. In the context of large-scale tech deployments, such as a fleet of autonomous vehicles or a network of distributed sensors, the reliable synchronization of DNS records via TCP 53 ensures consistent access to critical services and resources across the entire ecosystem.
DNS in the Ecosystem of Connected Drones and Autonomous Systems
The capabilities of modern drones and autonomous systems extend far beyond simple flight. They are increasingly integrated into complex digital ecosystems, relying heavily on network connectivity, cloud computing, and real-time data exchange. DNS acts as an invisible but vital enabler for many of these advanced functionalities.
Cloud Connectivity and Remote Operations
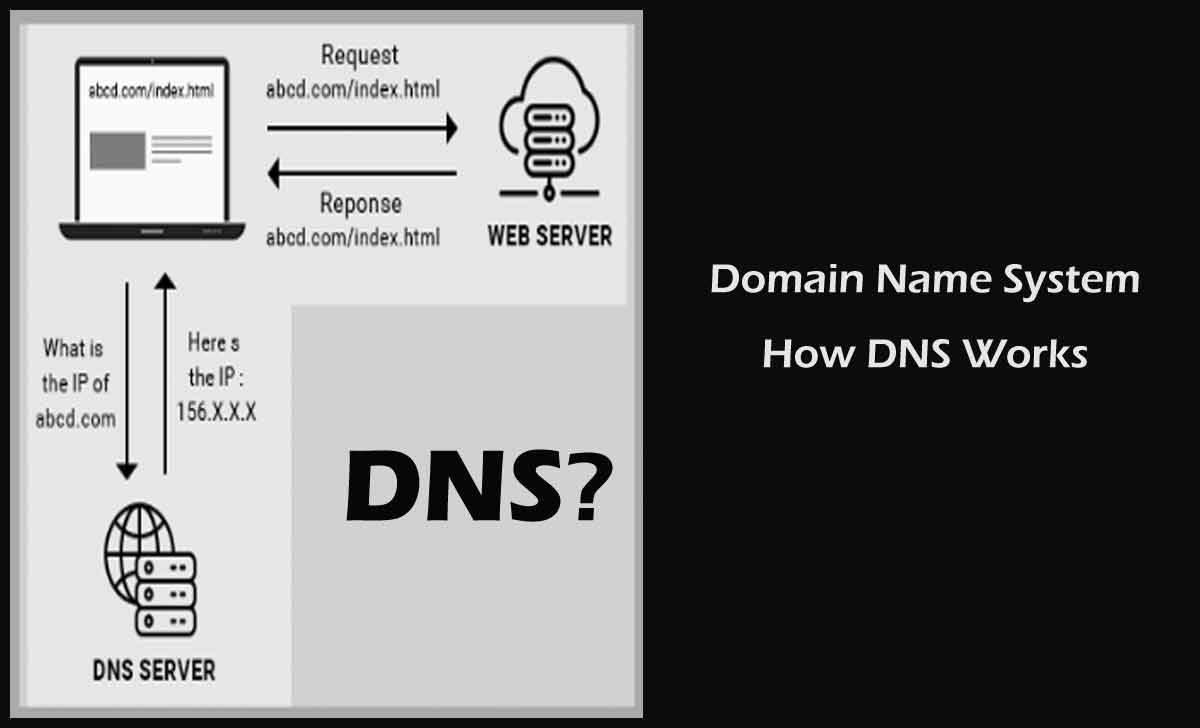
Autonomous drones frequently connect to cloud platforms for a myriad of reasons, including mission planning, data processing, AI model updates, and remote command and control. For instance, a drone programmed for infrastructure inspection might upload high-resolution imagery to a cloud-based analytics engine, which then uses AI to identify anomalies. To initiate this connection, the drone’s onboard software performs a DNS lookup to resolve the cloud service’s domain name (e.g., analytics.cloudprovider.com) into an IP address. This step is fundamental for establishing secure communication channels, allowing ground operators to manage fleets from a centralized dashboard or enabling autonomous systems to access distributed computing resources. Without reliable DNS resolution, these critical cloud connections would fail, severely limiting the operational scope and intelligence of autonomous fleets.
Firmware Updates and Software-Defined Features
The rapid evolution of drone technology means frequent firmware updates and the introduction of new software-defined features. These updates often deliver performance enhancements, bug fixes, security patches, or entirely new capabilities like advanced obstacle avoidance algorithms or enhanced camera controls. When a drone checks for available updates, its internal systems typically query an update server hosted by the manufacturer. This process begins with a DNS lookup to find the IP address of the update server (e.g., updates.dronecorp.com). Ensuring robust and reliable DNS resolution for these update servers is paramount, as it directly impacts the security, functionality, and longevity of the drone. Furthermore, many modern drones leverage software-defined capabilities that can be enabled or enhanced via remote configurations pulled from cloud services, again relying on DNS to locate these configuration endpoints.
Mapping, Remote Sensing, and Data Synchronization
Drones are invaluable tools for mapping, remote sensing, and environmental monitoring, generating vast amounts of georeferenced data, aerial imagery, and sensor readings. This data often needs to be synchronized with ground control stations, specialized mapping software, or cloud storage solutions for processing, analysis, and archiving. For example, a drone conducting a photogrammetry mission will capture thousands of images that must be uploaded to a processing server to create 3D models. The drone’s system uses DNS to locate the specific IP addresses of these data repositories (e.g., storage.mapping-service.com). Efficient and accurate DNS resolution is critical for timely data transfer, especially for time-sensitive applications like disaster response or precision agriculture, where delays in data availability can have significant consequences.
Enhancing Autonomous Capabilities
The cutting edge of autonomous flight, including features like AI follow mode, intelligent path planning, and advanced object recognition, frequently relies on distributed computing and cloud-based AI services. While some AI processing occurs onboard, complex computations or the use of regularly updated machine learning models often necessitates communication with remote servers. For example, an AI follow mode might use cloud processing to refine its target tracking algorithms based on real-time environmental data. Here, DNS plays its part by enabling the drone to locate the appropriate AI inference engines or data sources hosted in the cloud. This reliable access to remote intelligence is what empowers many of the sophisticated autonomous behaviors that define next-generation drone technology, allowing for continuous improvement and adaptability without requiring constant physical updates to the drone itself.
Security and Performance Implications of DNS in Tech Innovation
The foundational role of DNS in connecting advanced tech systems to the internet also introduces critical considerations regarding security and performance. For innovative applications like autonomous drone operations and remote sensing, the integrity and responsiveness of DNS directly impact mission success and data security.
DNS Security Challenges
Given its ubiquity, DNS is a frequent target for malicious attacks, which can have severe consequences for connected technologies. DNS spoofing (or cache poisoning) involves an attacker injecting false DNS records into a DNS resolver’s cache, redirecting legitimate traffic to malicious servers. Imagine an autonomous drone attempting to connect to its cloud mission planning server, only to be unknowingly redirected to an attacker-controlled server that feeds it erroneous flight commands or steals sensitive operational data. Distributed Denial of Service (DDoS) attacks against DNS servers can overwhelm them, preventing legitimate queries from being resolved. If a drone fleet cannot resolve the domain names of its command-and-control servers or data upload endpoints, its operations can be crippled, leading to mission failure or critical data loss. To counter these threats, technologies like DNS Security Extensions (DNSSEC) provide a layer of cryptographic authentication to DNS data, verifying the origin and integrity of DNS responses. Implementing and enforcing DNSSEC within the infrastructure supporting autonomous systems is crucial for maintaining trust and operational security.
Optimizing DNS for Performance
Beyond security, the performance of DNS resolution is paramount for time-sensitive applications prevalent in tech innovation. For real-time data streaming from a drone or rapid command execution in an autonomous vehicle, even small delays in DNS lookups can accumulate into noticeable latency, potentially affecting responsiveness or data quality. Slow DNS resolution can delay the establishment of connections to cloud services, impact the speed of firmware updates, or cause lags in data synchronization.
Organizations operating extensive networks of connected devices, such as drone service providers or remote sensing companies, often implement strategies to optimize DNS performance. This includes configuring devices to use high-performance, geographically close DNS resolvers, leveraging DNS caching at various points in the network (e.g., on local routers or gateways), and employing content delivery networks (CDNs) which use DNS to direct clients to the closest server. Furthermore, monitoring DNS query response times and ensuring redundancy in DNS infrastructure are essential practices to guarantee consistent and low-latency connectivity, critical for maintaining the efficiency and effectiveness of advanced technological deployments.
The Future of DNS and Decentralized Tech
As technology continues to evolve, so too does the landscape of network infrastructure. The traditional, hierarchical structure of DNS, while robust, is being explored for new paradigms, particularly with the rise of decentralized technologies. Concepts like blockchain-based DNS or other forms of distributed naming systems offer potential alternatives that could enhance resilience, censorship resistance, and security.
For autonomous systems, which are increasingly distributed and operate in diverse environments, decentralized DNS could offer advantages. Imagine a swarm of drones in a remote location operating with peer-to-peer communication and needing to resolve names within their ad-hoc network without relying on a central authority. Such systems could potentially benefit from naming resolutions that are more resilient to single points of failure and less susceptible to centralized control or attack. While these decentralized alternatives are still maturing, their exploration represents a significant frontier in “Tech & Innovation,” promising new ways to secure and manage the digital identities of devices and services within future autonomous and distributed networks. The evolution of DNS, therefore, remains a key area of development that will continue to shape how innovative technologies connect, communicate, and operate.