
The digital infrastructure powering modern drone technology is a complex tapestry of hardware and software, where efficiency and reliability are paramount. Within this intricate ecosystem, various communication protocols play foundational roles, often operating behind the scenes. Among these is the Trivial File Transfer Protocol (TFTP), a deceptively simple yet remarkably effective mechanism for moving files across networks. While its name might suggest a rudimentary function, TFTP’s lightweight nature makes it an invaluable tool in specific contexts, particularly within the specialized domain of drone tech and innovation where resource constraints and rapid deployment are key considerations.
Unpacking the Trivial File Transfer Protocol
At its core, TFTP is a protocol designed for the straightforward transfer of files between two network devices. Developed in the early days of networking, it predates many of the more robust and feature-rich file transfer solutions we use today, such as the File Transfer Protocol (FTP) or Secure File Transfer Protocol (SFTP). This historical context is vital to understanding its inherent design philosophy: simplicity over complexity, speed over advanced features.
A Simpler Approach to File Transfer
The “trivial” in TFTP is not an insult but a descriptor of its minimalist design. Unlike FTP, which offers a rich set of features including directory listings, user authentication, and multiple data connection modes, TFTP deliberately omits these complexities. This pared-down functionality results in a protocol that is exceptionally lightweight in terms of both network overhead and computational resources required for its implementation. For embedded systems, IoT devices, and increasingly, components within drone architectures where every byte of memory and every clock cycle matters, this efficiency is a significant advantage. The protocol is typically used for basic tasks like booting computers from a network (PXE boot), transferring configuration files to network devices, or, as we’ll explore, pushing firmware updates to drone components.
The UDP Foundation
A defining characteristic of TFTP is its reliance on the User Datagram Protocol (UDP) as its transport layer, rather than the more commonly used Transmission Control Protocol (TCP). This choice has profound implications for how TFTP operates. UDP is a connectionless protocol, meaning it does not establish a persistent connection between the client and server before data transfer begins. Each packet is sent independently, and UDP itself does not guarantee delivery, order, or duplication prevention.
To compensate for UDP’s inherent unreliability, TFTP incorporates its own rudimentary mechanisms for reliability. Each data packet sent by the server must be acknowledged by the client before the next packet is sent. If an acknowledgment is not received within a certain timeout period, the data packet is retransmitted. This stop-and-wait acknowledgment system provides a basic level of reliability without incurring the higher overhead associated with TCP’s complex connection management, flow control, and congestion avoidance algorithms. While this makes TFTP faster for small transfers over reliable networks, it can become inefficient or fail entirely over lossy or high-latency connections.
The Mechanics of TFTP: How it Operates
Understanding the operational flow of TFTP reveals its elegant simplicity. It’s a request-response protocol where a client initiates an action, and a server responds accordingly.
Client-Server Interaction
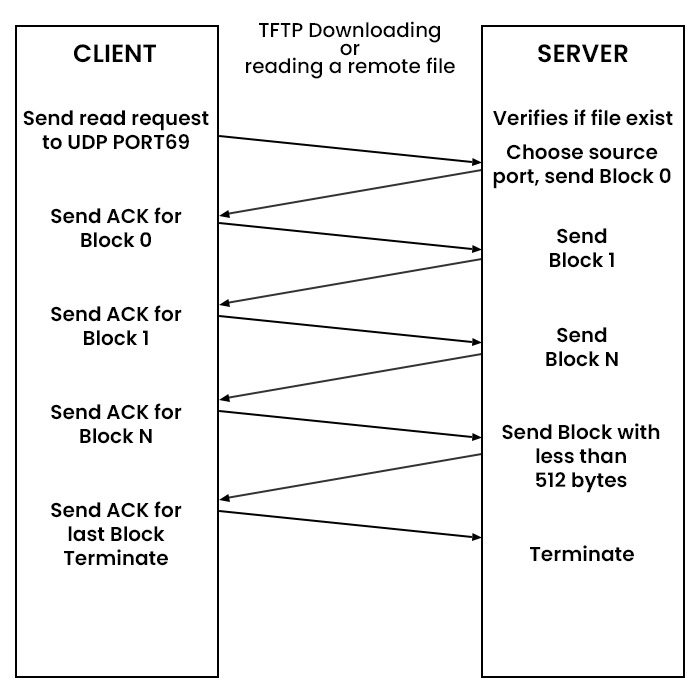
The TFTP process begins with a client sending a request to a TFTP server. This request can be one of two primary types: a Read Request (RRQ) to download a file, or a Write Request (WRQ) to upload a file. The server listens on UDP port 69 for these incoming requests.
Once a request is received, the server allocates a new, ephemeral UDP port for that specific transfer session. All subsequent data packets and acknowledgments for that transfer will use this new port, allowing the main port 69 to remain free for new incoming requests. This mechanism enables the TFTP server to handle multiple concurrent file transfers efficiently.
Request and Transfer Modes
TFTP defines five distinct types of packets, each serving a specific purpose in the file transfer process:
- Read Request (RRQ): Sent by the client to request a file from the server.
- Write Request (WRQ): Sent by the client to request writing a file to the server.
- Data (DATA): Carries the actual file data, typically in blocks of 512 bytes.
- Acknowledgment (ACK): Sent by the receiver (client or server) to confirm successful receipt of a DATA packet.
- Error (ERROR): Sent when an error condition occurs during the transfer.
The file transfer sequence is straightforward. For a download (RRQ), the client sends an RRQ packet specifying the filename and transfer mode (e.g., “octet” for binary). The server then responds with the first DATA packet. The client acknowledges this packet, and upon receiving the ACK, the server sends the next DATA packet. This continues until the entire file has been transferred, indicated by a DATA packet containing less than 512 bytes (the last block). The process is reversed for an upload (WRQ), with the client sending DATA packets and the server sending ACKs.
Absence of Authentication and Directory Listing
A critical aspect of TFTP’s “trivial” nature is its complete lack of built-in security features. There is no user authentication mechanism; any client that can reach the TFTP server can attempt to read or write files. Similarly, there are no commands for listing directory contents or navigating the file system. A TFTP client must know the exact filename it wishes to access. This design choice dramatically reduces complexity but, as will be discussed, introduces significant security vulnerabilities if TFTP is not deployed with careful consideration and proper network segmentation.
Why TFTP Matters in Drone Tech & Innovation
While seemingly simplistic, TFTP’s core characteristics—lightweightness, efficiency, and directness—make it surprisingly relevant for specific applications within the rapidly evolving landscape of drone technology and innovation. It thrives in environments where resources are constrained, and precise, targeted file transfers are required.
Lightweight Efficiency for Embedded Systems
Modern drones are essentially flying embedded systems, integrating numerous specialized microcontrollers, processors, and sensors, each often running its own dedicated firmware. Components such as flight controllers, electronic speed controllers (ESCs), GPS modules, remote sensing payloads, and companion computers are often resource-constrained devices with limited processing power, memory, and storage. In such environments, the overhead associated with more complex protocols like FTP or HTTP can be prohibitive, consuming valuable CPU cycles and memory that are better dedicated to critical flight operations or data processing.
TFTP’s minimal footprint is a perfect match for these embedded systems. Its simple packet structure and UDP-based operation mean less code to implement, less memory to consume, and fewer processing steps per transaction. This efficiency is paramount for ensuring that essential functions like firmware updates or configuration changes can occur quickly and reliably without overburdening the drone’s critical control systems.
Facilitating Firmware Updates and Configuration
One of the most crucial applications of TFTP in drone technology is for managing firmware and configuration files. Drones, particularly those in commercial or industrial use, frequently receive updates to improve performance, add new features, fix bugs, or enhance security. TFTP can be used to push new firmware images to various drone components:
- Flight Controllers: Updating the core operating system or flight control algorithms that dictate the drone’s stability and maneuverability.
- ESCs: Providing updated firmware for motor control, optimizing efficiency or responsiveness.
- GPS Modules: Loading new satellite almanac data or improving positioning algorithms.
- Specialized Payloads: Updating the software on thermal cameras, LiDAR sensors, or custom AI processing units attached to the drone.
Beyond firmware, TFTP is also ideal for transferring configuration files. This could include mission profiles for autonomous flights, pre-defined waypoints, sensor calibration data, or network settings for onboard communication modules. The ability to rapidly deploy these small, critical files ensures that drones can be quickly adapted for new tasks or optimized for specific environmental conditions.
Bootstrapping and Network Device Initialization
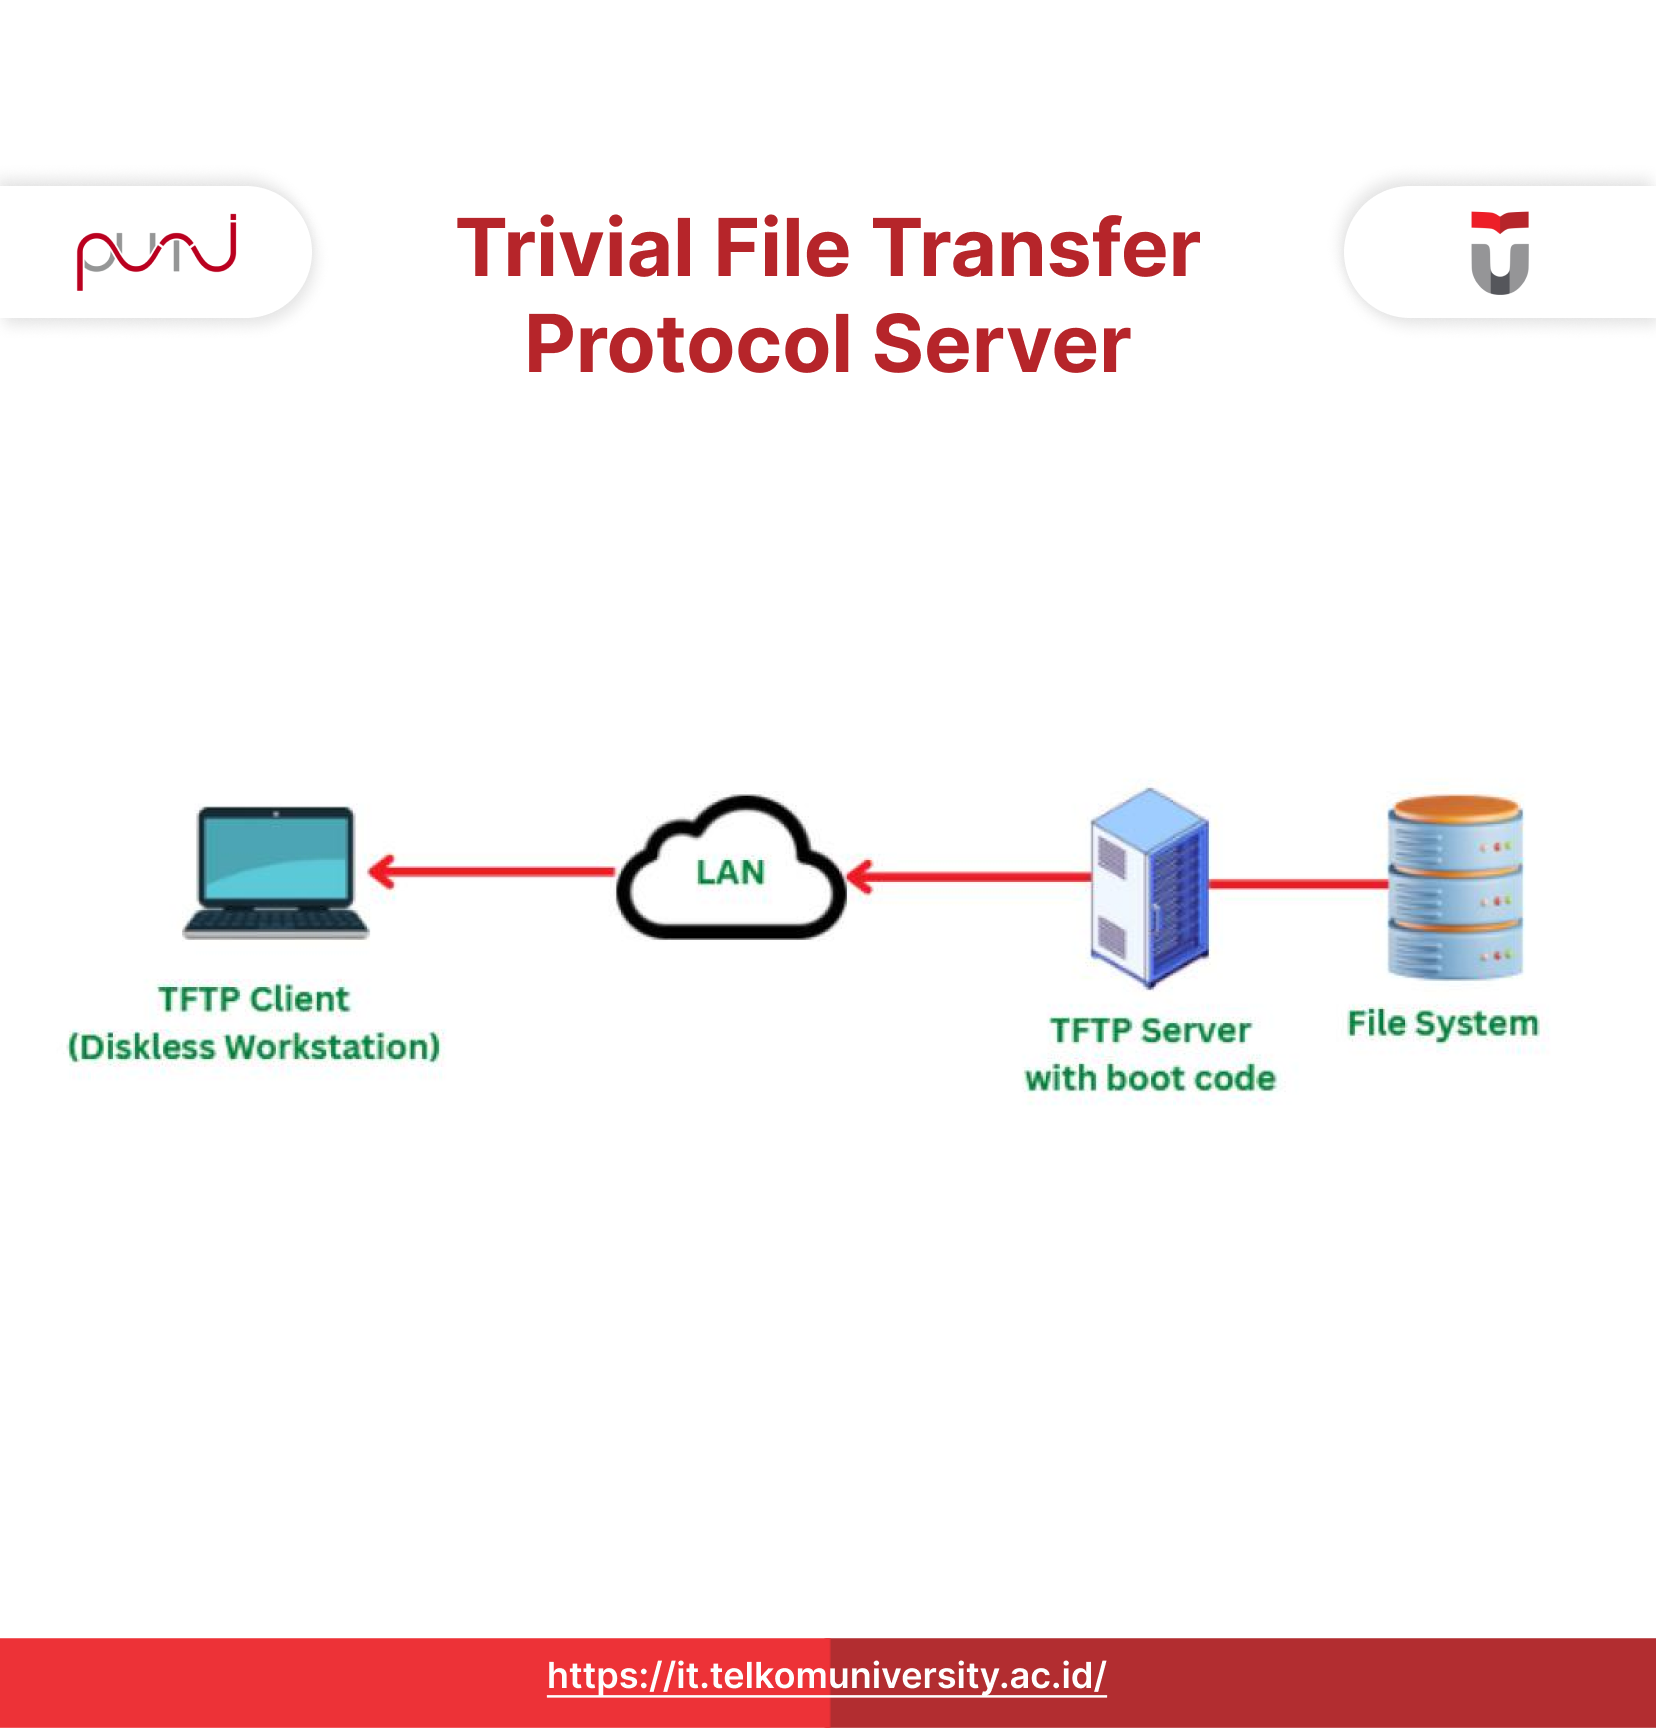
For more advanced drone platforms that incorporate full-fledged operating systems on companion computers (e.g., Linux-based systems for AI processing, advanced navigation, or mission planning), TFTP can play a vital role in the bootstrapping process. In scenarios where a drone component needs to load its operating system or a configuration file directly from the network upon startup, TFTP provides a lightweight and efficient method. This is analogous to how traditional network devices use TFTP for PXE (Preboot Execution Environment) booting. A drone’s companion computer, lacking local storage or needing to load a very specific, frequently updated image, can use TFTP to pull its boot image from a central server. This enables rapid deployment, centralized management of images, and quick recovery from system failures, all critical for fleet operations and experimental drone platforms.
Practical Applications and Emerging Trends in Drone Ecosystems
The integration of TFTP, while often hidden, underpins several important functionalities and trends in drone innovation, particularly in areas requiring robust remote management and automation.
Remote Management of Autonomous Systems
As drone autonomy advances, the ability to remotely manage and update entire fleets becomes increasingly important. While TFTP is not a complete remote management solution on its own, it serves as a critical underlying component. For instance, a ground control station (GCS) or a fleet management system might use more sophisticated protocols for high-level command and control. However, when a drone in the field needs a new autonomous flight algorithm, an updated AI model for object detection, or a revised set of environmental parameters, TFTP can be the rapid, low-resource method for pushing these specific files to the drone’s onboard computer. This is particularly relevant for drones operating in remote areas with limited bandwidth, where the efficiency of TFTP reduces transfer times and overhead.
Data Handling in Specialized Drone Payloads
While TFTP is generally not suitable for large-scale data offloading (e.g., high-resolution imagery or video streams), it finds niche applications in managing specialized drone payloads. For example, a scientific sensor payload might generate small diagnostic logs, error reports, or acquire tiny snippets of metadata that need to be retrieved periodically. Using TFTP, these small files can be quickly pulled from the payload’s embedded controller, allowing for rapid assessment of sensor health or data quality without interrupting ongoing missions or requiring more complex communication channels.
Integration with Ground Control Stations (GCS) and Fleet Management Software
Modern drone operations often rely on sophisticated Ground Control Stations and comprehensive fleet management software. These systems are designed to monitor, control, and manage multiple drones simultaneously. Within this architecture, TFTP can be strategically employed by the GCS to push essential files to connected drones. Whether it’s updating the “no-fly zone” database, deploying a new set of flight restrictions, or synchronizing specific configuration parameters across an entire fleet, TFTP offers a reliable and efficient backend mechanism. This enables administrators to maintain consistent operational parameters and ensure all drones are running the latest, approved software and configurations, which is vital for safety, compliance, and mission success in regulated airspace.
Security Considerations and Best Practices for Drone Implementations
Despite its utility, TFTP’s inherent lack of security features presents significant challenges that must be addressed, especially when used in the sensitive context of drone operations. Unsecured TFTP implementations can become a critical vulnerability.
Inherent Vulnerabilities
The absence of authentication means any client can request or attempt to write files to a TFTP server. This opens the door to:
- Unauthorized File Access: Malicious actors could potentially download sensitive configuration files, mission plans, or even proprietary firmware images from a drone component if they can access the TFTP server.
- Malicious Firmware Injection: Perhaps the most dangerous threat is the possibility of uploading corrupted or malicious firmware to a drone’s flight controller or other critical components. This could lead to loss of control, erratic flight behavior, or complete system compromise.
- Denial-of-Service (DoS) Attacks: Because TFTP uses UDP, it is susceptible to various DoS attacks that could flood the server with requests or forged packets, preventing legitimate transfers.
Mitigating Risks in Drone Deployments
Given these risks, deploying TFTP in any drone-related system requires a stringent security posture. Best practices include:
- Strict Network Segmentation: Isolate TFTP services on dedicated, firewalled subnets (VLANs). Access to these networks should be highly restricted to only authorized management systems or known IP addresses. Never expose a TFTP server directly to the public internet or an untrusted network.
- Firewall Rules: Implement granular firewall rules to limit incoming TFTP requests (UDP port 69) to specific source IP addresses or network ranges. Further restrict outbound connections from the drone components if TFTP is used for uploading.
- Principle of Least Privilege: Configure TFTP servers to allow access only to specific directories and specific file types. Deny write access to critical system directories. Only allow transfers during controlled maintenance windows.
- Secure Boot and Firmware Signatures: For firmware updates, TFTP should ideally be used in conjunction with a secure boot process and cryptographic verification of firmware images. This ensures that even if a malicious actor manages to upload a file, the drone’s system will reject it if it’s not cryptographically signed by a trusted authority. This is a critical line of defense.
- Use for Non-Sensitive Data Only: Whenever possible, use TFTP only for non-sensitive data or in highly controlled, air-gapped environments. For sensitive data, configuration, or firmware, prioritize more secure protocols like SFTP or HTTPS with robust authentication and encryption.
- Regular Security Audits: Continuously monitor and audit network traffic related to TFTP services. Implement intrusion detection systems (IDS) to flag suspicious activity or unauthorized access attempts.
In conclusion, TFTP remains a niche but valuable protocol within the broad spectrum of drone tech and innovation. Its efficiency and simplicity make it an ideal choice for specific tasks like firmware distribution and component bootstrapping in resource-constrained drone architectures. However, its inherent lack of security necessitates a meticulous approach to network design and operational procedures to ensure that the advantages of its lightweight nature are not overshadowed by preventable vulnerabilities. As drones continue to evolve in complexity and autonomy, the judicious and secure application of foundational network technologies like TFTP will continue to play an unseen, yet vital, role in their ongoing advancement.