
Understanding Server-Side Request Forgery (SSRF): A Core Cybersecurity Challenge
In the rapidly evolving landscape of technology and innovation, where interconnected systems and cloud-based services form the backbone of new advancements, cybersecurity vulnerabilities pose a significant threat. Among these, Server-Side Request Forgery (SSRF) stands out as a particularly insidious vulnerability, often underestimated despite its potential for devastating impact. At its core, SSRF describes a flaw in a web application that allows an attacker to induce the server-side application to make HTTP requests to an arbitrary domain of the attacker’s choosing. This seemingly straightforward concept masks a complex array of exploitation scenarios, enabling attackers to bypass security controls, access sensitive internal resources, and potentially compromise entire systems.
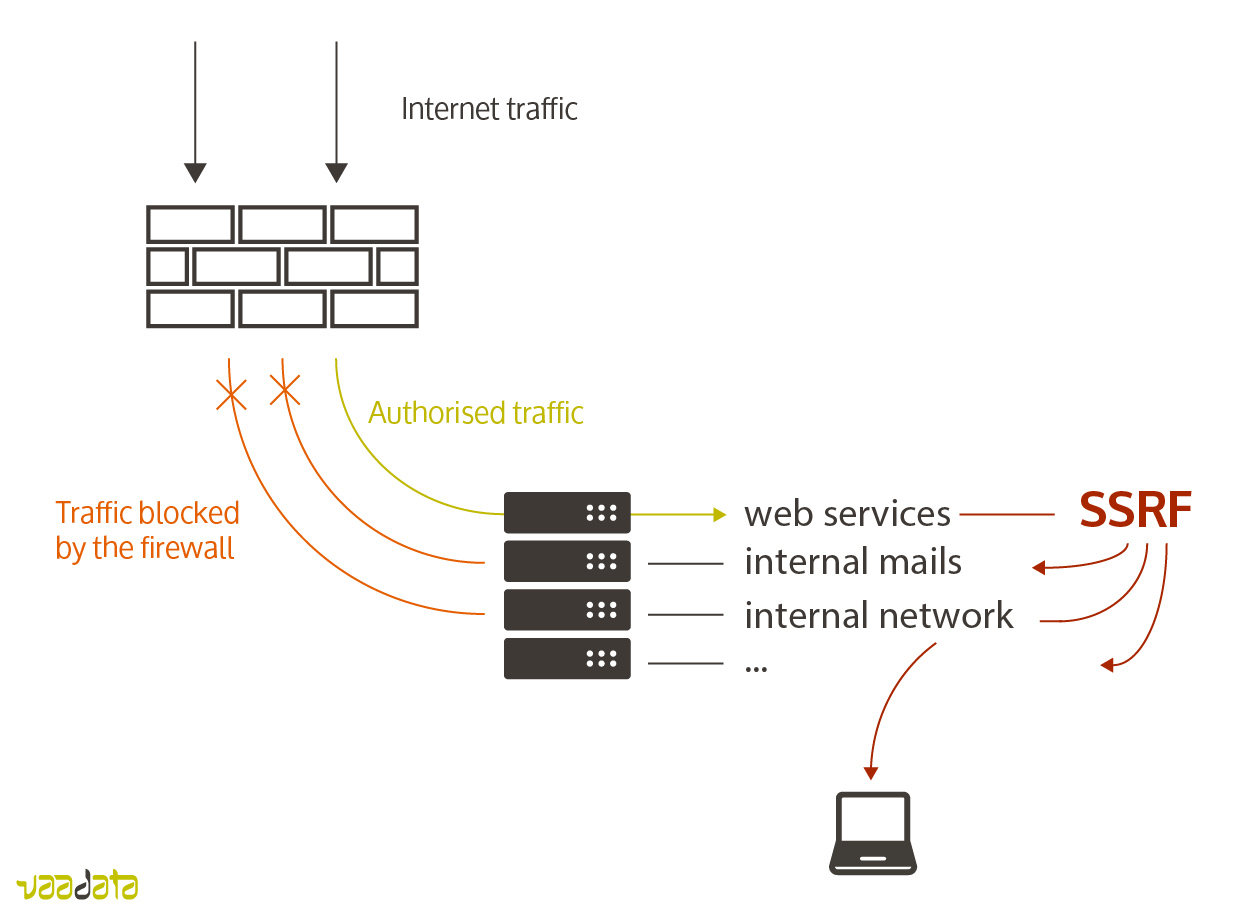
The essence of SSRF lies in the server’s trust. Many modern applications need to fetch resources from other URLs, whether for displaying remote images, integrating with third-party APIs, or performing background tasks. When an application accepts a URL as input and then fetches content from that URL without proper validation, it creates an opening for an attacker. Instead of providing a legitimate external URL, an attacker can supply an internal IP address or a URL pointing to a service within the organization’s private network. The vulnerable server, acting on behalf of the attacker, then makes a request to this internal resource. Since the request originates from within the trusted network perimeter, firewalls and other external security measures that would typically block such access are bypassed. This effectively turns the legitimate server into a proxy for the attacker, granting them unprecedented access to internal systems that were never intended to be exposed directly to the public internet. The criticality of understanding and addressing SSRF vulnerabilities is paramount for any organization striving to secure its innovative technologies and data infrastructure against sophisticated cyber threats.
The Mechanics of an SSRF Attack: Exploiting Trust and Connectivity
The success of an SSRF attack hinges on the application’s functionality that allows it to retrieve data from a user-supplied URL. This functionality is common across a wide range of web applications, including those found in cloud platforms, IoT management systems, and advanced analytics engines – all pillars of modern tech innovation. Understanding the various vectors and scenarios through which an SSRF attack can be executed is crucial for robust defense.
Common SSRF Vectors and Scenarios
- Image or File Fetching Services: Many applications offer features to import images or data from a URL (e.g., profile pictures, document attachments). If this feature doesn’t validate the URL properly, an attacker can inject an internal IP address (e.g.,
http://127.0.0.1/admin) or a local hostname (e.g.,http://localhost/metrics). The server then attempts to fetch this “image” or “file,” inadvertently sending a request to an internal service. - Webhooks and Callback URLs: Services that integrate with external systems often use webhooks or allow users to specify callback URLs. For instance, an innovative AI service might notify a user’s system upon completion of a task by sending a POST request to a user-defined URL. If this URL is not properly sanitized, an attacker can specify an internal endpoint, turning the notification mechanism into an SSRF vector.
- URL Shorteners and Proxy Services: Applications designed to shorten URLs or act as content proxies can be exploited. If the shortening or proxy service does not sufficiently restrict the target URLs, an attacker can submit an internal URL. When another user or the system itself accesses the shortened URL, the server makes a request to the internal resource.
- Data Aggregation and API Integrations: Modern applications often aggregate data from multiple sources or integrate with various internal and external APIs. If the endpoint for an API call or data retrieval is dynamically constructed using user input, an attacker can manipulate this input to point to internal API endpoints or databases.
- Cloud Metadata Services: A particularly potent form of SSRF often targets cloud environments. Cloud providers (like AWS, Azure, GCP) expose metadata services at specific, well-known internal IP addresses (e.g.,
http://169.254.169.254for AWS EC2 instances). These services provide sensitive information about the running instance, including IAM roles, temporary credentials, and network configuration. An SSRF vulnerability can allow an attacker to query these metadata services and gain access to highly privileged credentials, leading to full compromise of cloud resources.
Out-of-Band SSRF (Blind SSRF)
Sometimes, the server’s response to an SSRF request isn’t directly returned to the attacker. This is known as blind SSRF or out-of-band SSRF. Even without a direct response, an attacker can still confirm the vulnerability and exfiltrate data by using techniques like:
- DNS Resolution: Monitoring DNS queries on a controlled domain. If the vulnerable server attempts to resolve a domain supplied by the attacker, it confirms connectivity.
- Time-Based Delays: Inducing delays by requesting a resource that is known to take time to respond, thereby observing the overall application’s response time.
- Error Messages: Subtle differences in error messages or application behavior that indicate an attempt to connect to an internal resource.
The ability to exploit trust boundaries, leverage existing application functionality, and operate in both visible and blind modes makes SSRF a versatile and dangerous tool in an attacker’s arsenal, necessitating robust security measures for all innovative digital platforms.
The Far-Reaching Impact of SSRF Vulnerabilities on Modern Innovation
The consequences of a successful SSRF attack extend far beyond simple data exposure. In the context of cutting-edge technology and innovation, where systems are increasingly distributed, interconnected, and rely heavily on cloud infrastructure, the impact can be catastrophic. SSRF vulnerabilities represent a critical blind spot that can undermine the security and integrity of advanced applications and services.
Escalation of Privileges and Data Exfiltration

One of the most immediate impacts is the ability to bypass network segmentation and access internal resources. This can lead to:
- Access to Internal APIs and Admin Panels: Attackers can interact with internal APIs that are not exposed to the public internet, potentially executing administrative functions, retrieving sensitive data, or altering system configurations. They can also access internal administrative interfaces, gaining full control over an application or system.
- Database Access: Many databases are configured to only accept connections from within the internal network. SSRF can allow an attacker to trick the vulnerable server into making requests to these databases, potentially extracting vast amounts of sensitive customer data, intellectual property, or operational secrets.
- Cloud Instance Compromise: As highlighted, SSRF can be used to query cloud metadata services, leading to the theft of temporary credentials. These credentials often possess significant permissions, allowing an attacker to enumerate, modify, or even delete cloud resources, leading to service disruption, data loss, or the deployment of malicious infrastructure. For innovative solutions built entirely on cloud-native architectures, this is an existential threat.
Service Disruption and System Control
Beyond data theft, SSRF can facilitate direct control over system behavior or lead to service outages:
- Port Scanning and Network Reconnaissance: An attacker can use SSRF to scan internal ports and identify active services running on other machines within the internal network. This reconnaissance provides a detailed map of the internal infrastructure, making subsequent, more targeted attacks easier to plan.
- Denial of Service (DoS): By repeatedly requesting computationally intensive internal resources or triggering unintended operations, an attacker can cause internal services to crash or become unresponsive, leading to a denial of service for legitimate users.
- Bypassing IP Whitelisting: If a service relies on IP whitelisting for access control, an SSRF vulnerability can effectively bypass this protection. Since the request originates from the trusted server’s IP address, the whitelisting mechanism is circumvented, allowing unauthorized access. This is particularly dangerous for critical services or proprietary technologies where access is meant to be highly restricted.
The integration of AI, machine learning, IoT devices, and autonomous systems into enterprise and consumer applications means that the attack surface for SSRF is expanding. A compromised system due to SSRF could lead to: manipulated AI models, unauthorized control over IoT devices, disruption of autonomous operations, or exfiltration of proprietary algorithms and data sets that drive innovation. Therefore, understanding and mitigating SSRF is not just a matter of compliance; it is fundamental to safeguarding the future of technological progress.
Identifying and Mitigating SSRF Risks: Best Practices for Secure Development
Addressing SSRF vulnerabilities requires a multi-layered approach that integrates security considerations throughout the entire software development lifecycle, from design to deployment and ongoing operations. For organizations pushing the boundaries of technology and innovation, embedding these practices is not optional but essential for maintaining trust and securing valuable assets.
Proactive Identification and Prevention Strategies
The most effective defense against SSRF is proactive prevention through rigorous input validation and secure architectural design.
- Whitelisting is Key: Instead of blacklisting malicious inputs (which is notoriously difficult to maintain comprehensively), implement a strict whitelist of allowed domains, IP addresses, and URL schemes that the application is permitted to access. Any request to a URL not on this whitelist should be explicitly rejected. This is the strongest defense.
- Input Validation and Sanitization: All user-supplied URLs and parameters used in URL construction must be meticulously validated and sanitized. This includes checking the protocol, hostname, port, and path. Regular expressions can be used, but they must be robust enough to handle various encoding schemes and bypass techniques.
- Disable Unused URL Schemes: If the application only needs to fetch HTTP/HTTPS resources, disable support for other URL schemes (e.g.,
file://,ftp://,gopher://). These can often be exploited for local file access or to interact with other network services. - Implement Network Segmentation: Employ strong network segmentation to isolate sensitive internal services. Even if an SSRF attack occurs, proper segmentation can limit the attacker’s lateral movement and reduce the scope of compromise. Critical databases, administration panels, and cloud metadata services should reside in highly restricted network zones.
- Use URL Parsers Carefully: When parsing URLs, rely on robust, well-tested URL parsing libraries rather than attempting to parse URLs manually. Be aware of how different parsers handle redirects, subdomains, and various encoding methods, as inconsistencies can lead to bypasses.
- User-Supplied Hostnames and IP Addresses: Never allow user input to directly specify a hostname or IP address without strict validation against an allowed list. Ensure that any resolution of hostnames to IP addresses happens on the server-side after initial validation, and verify that the resolved IP address is not an internal or reserved IP range (e.g.,
127.0.0.1/8,10.0.0.0/8,172.16.0.0/12,192.168.0.0/16). - Isolate Functionality: If certain functionality absolutely requires fetching resources from arbitrary URLs (e.g., a web scraping service), consider isolating this functionality to a separate, highly sandboxed environment with minimal privileges and no access to internal networks.

Detection and Response
Even with the best preventive measures, constant vigilance is required.
- Logging and Monitoring: Implement comprehensive logging for all outbound requests made by the server. Monitor these logs for suspicious patterns, unusual destinations (especially internal IP ranges), or requests to services that are not typically accessed. Integrate these logs with security information and event management (SIEM) systems for real-time alerting.
- Web Application Firewalls (WAFs): While WAFs can provide an additional layer of defense by filtering malicious inputs, they should not be considered a primary defense against SSRF. Attackers often find ways to bypass WAF rules. They are best used as a complementary control.
- Regular Security Audits and Penetration Testing: Conduct periodic security audits, code reviews, and penetration tests specifically targeting SSRF vulnerabilities. Ethical hackers can often uncover complex bypasses that automated tools might miss.
By integrating these best practices, organizations can significantly reduce their exposure to SSRF attacks, ensuring that their innovative products and services remain secure, reliable, and trustworthy in an increasingly interconnected digital world. The journey of technological innovation must always be accompanied by a steadfast commitment to robust cybersecurity.