
Security in cloud computing represents the collective measures, technologies, and best practices designed to protect cloud-based data, applications, and infrastructure from threats, vulnerabilities, and attacks. It’s a multifaceted domain that blends traditional cybersecurity principles with the unique characteristics of distributed, virtualized, and on-demand cloud environments. As organizations increasingly migrate their critical operations to public, private, and hybrid clouds, understanding and implementing robust cloud security becomes paramount for maintaining business continuity, protecting sensitive information, and ensuring compliance. This isn’t merely about erecting digital firewalls; it’s about a comprehensive strategy that spans infrastructure, platforms, and applications, continuously adapting to an evolving threat landscape.
The Foundational Principles of Cloud Security
At its core, cloud security is built upon established cybersecurity tenets but re-contextualized for the cloud’s distinct operational model. A clear understanding of these foundational principles is essential for any effective cloud security strategy.
The Shared Responsibility Model
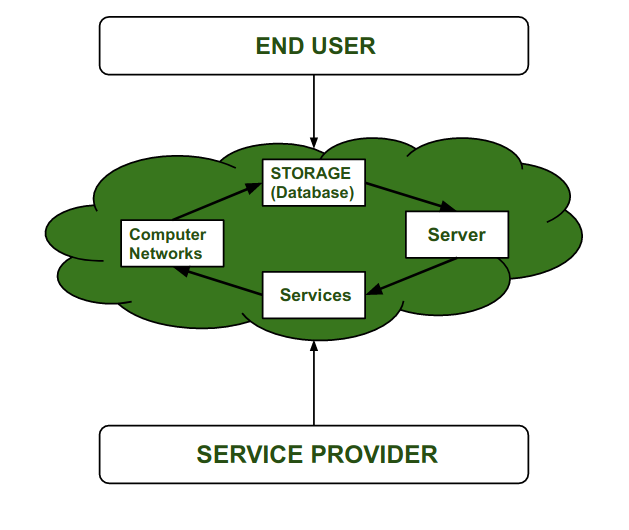
Perhaps the most critical concept in cloud security is the Shared Responsibility Model. Unlike traditional on-premise environments where an organization is solely responsible for all layers of security, the cloud model divides these responsibilities between the Cloud Service Provider (CSP) and the customer.
- Cloud Service Provider (CSP) Responsibility: The CSP is responsible for the “security of the cloud.” This typically includes the physical infrastructure (data centers, servers, networking hardware), virtualization layers, and global network infrastructure. For IaaS (Infrastructure as a Service), the CSP secures the underlying infrastructure. For PaaS (Platform as a Service), they secure the platform and infrastructure. For SaaS (Software as a Service), they secure the entire application stack, though customer configuration remains crucial.
- Customer Responsibility: The customer is responsible for “security in the cloud.” This encompasses data (content, classification, encryption), platforms (operating systems, applications, network configuration), identity and access management, and configurations of cloud services. For IaaS, customers secure their operating systems, applications, network configurations, and data. For PaaS, they secure their applications and data. For SaaS, their primary responsibility lies in user access management and configuration settings within the application.
Misunderstanding this model is a leading cause of cloud security breaches, as organizations may mistakenly assume the CSP covers areas for which they are accountable.
Pillars of Cloud Security
Cloud security efforts are typically anchored around core pillars, ensuring a holistic approach to protection:
- Confidentiality: Ensuring that sensitive data is accessible only to authorized individuals or systems. This involves encryption, access controls, and data segregation.
- Integrity: Guaranteeing the accuracy and completeness of data, preventing unauthorized modification or corruption. This is achieved through hashing, digital signatures, and strict change management processes.
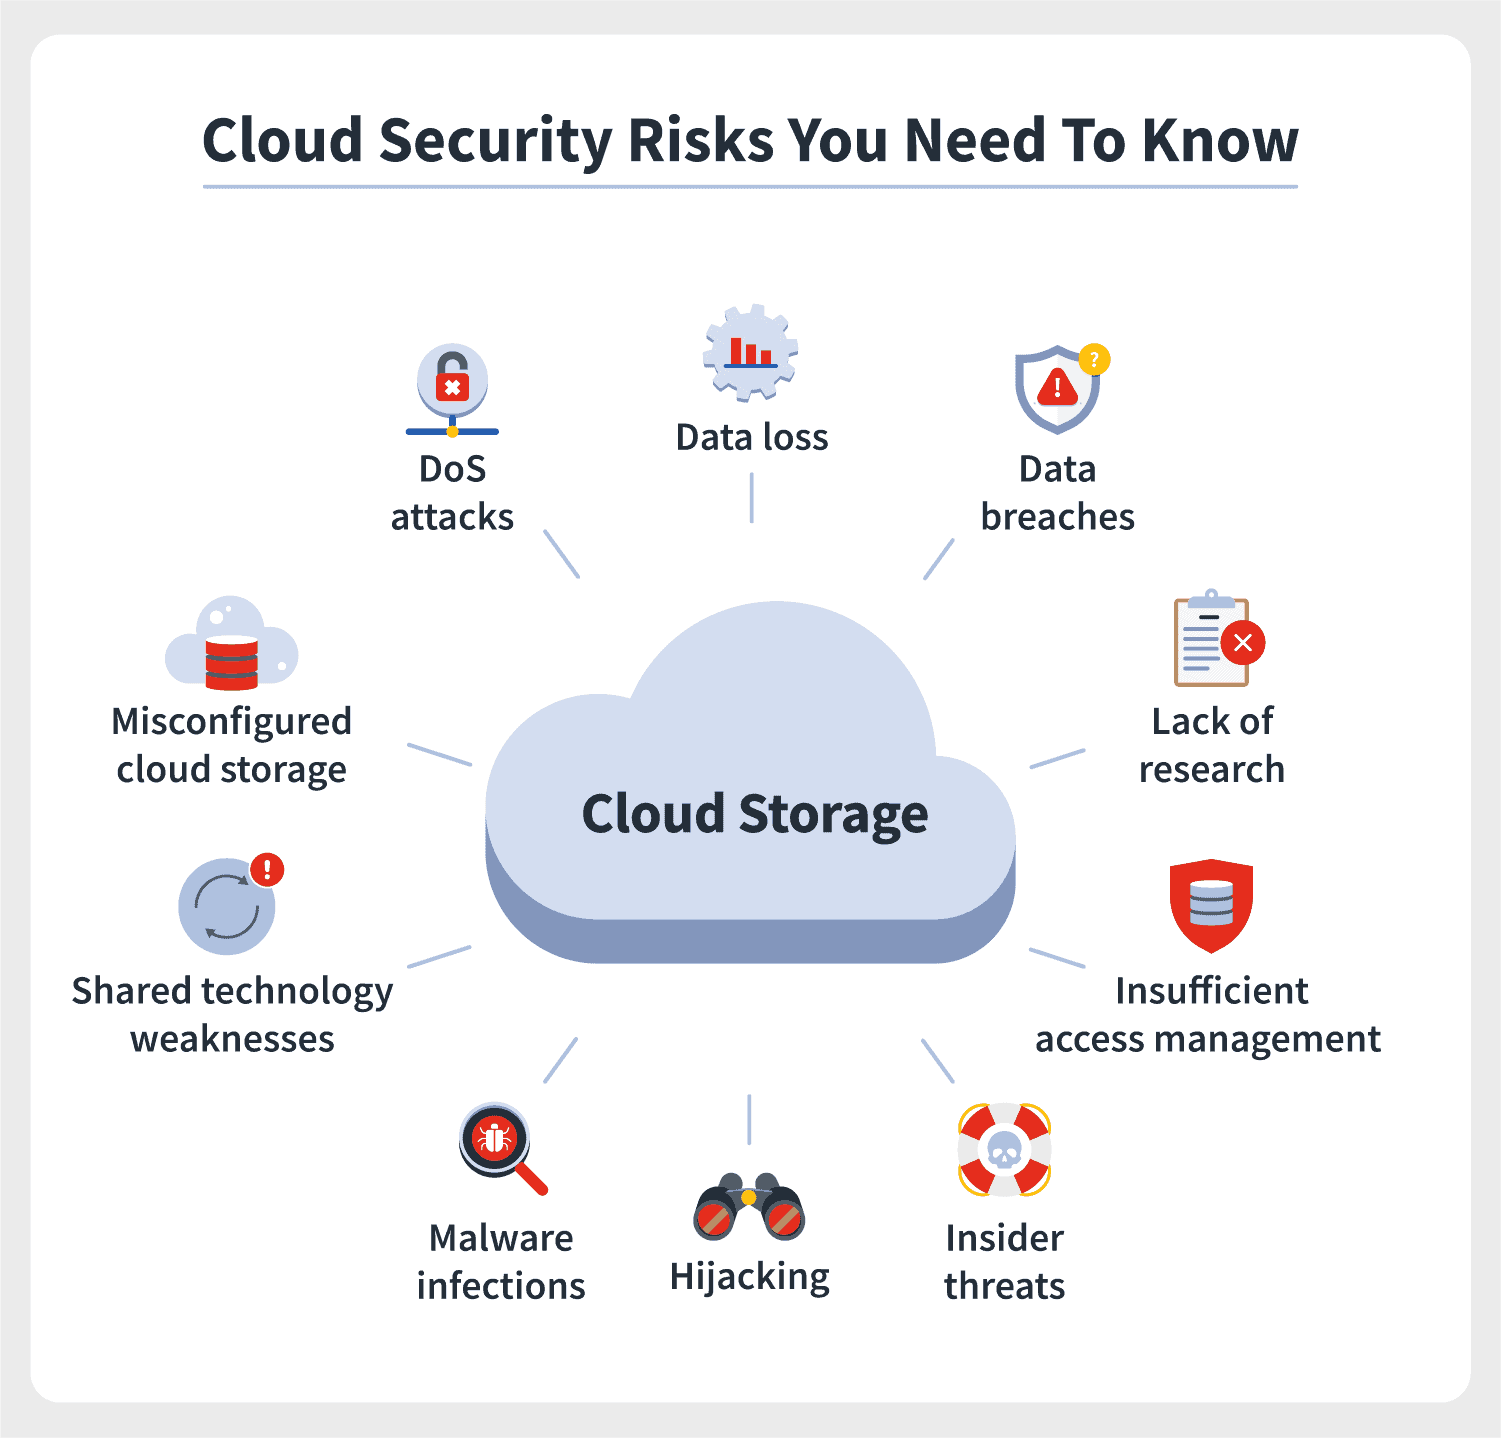
- Availability: Ensuring that authorized users can access data and resources whenever needed. This involves redundancy, disaster recovery planning, and protection against denial-of-service (DoS) attacks.
- Authentication: Verifying the identity of users or systems attempting to access cloud resources. Strong authentication mechanisms, such as multi-factor authentication (MFA), are crucial.
- Authorization: Granting specific permissions to authenticated users based on their roles and responsibilities, ensuring they can only perform actions they are allowed to.
- Non-Repudiation: Providing irrefutable proof that a specific action or event occurred, linking it to a particular user or system, which is vital for auditing and accountability.
Key Challenges and Threat Vectors in the Cloud
While the cloud offers immense benefits, it also introduces a unique set of security challenges and exposes organizations to evolving threat vectors. Addressing these requires specialized knowledge and proactive strategies.
Data Breaches and Confidentiality Risks
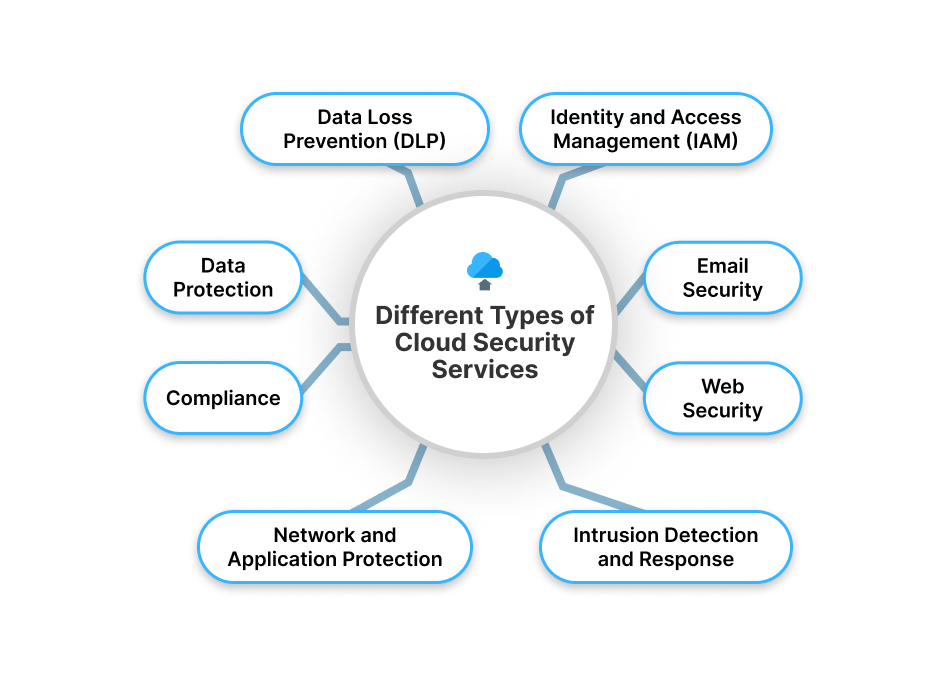
Cloud environments consolidate vast amounts of data, making them attractive targets for malicious actors. Data breaches can occur due to misconfigured storage buckets, insecure APIs, weak access controls, or insider threats. The distributed nature of the cloud can also complicate data visibility and control, increasing the risk of sensitive information being exposed or exfiltrated. Encryption, both at rest and in transit, alongside robust data classification and data loss prevention (DLP) strategies, are critical to mitigate these risks.
Identity and Access Management (IAM) Complexities
Managing identities and controlling access in the cloud is notoriously complex. Organizations often struggle with granting appropriate permissions (least privilege principle), managing ephemeral identities, integrating cloud IAM with on-premises directories, and enforcing strong authentication. Over-privileged accounts, compromised credentials, and insufficient audit trails for access events are common vulnerabilities that attackers exploit to gain unauthorized access to cloud resources. Centralized IAM solutions, multi-factor authentication, and continuous monitoring of access patterns are essential.
Vulnerabilities in Cloud Native Architectures
The rapid adoption of cloud-native technologies like containers (e.g., Docker, Kubernetes), serverless functions, and microservices introduces new attack surfaces. Misconfigurations in container registries, unpatched images, insecure APIs between microservices, and vulnerabilities within serverless function code can all be exploited. The dynamic and transient nature of these environments makes traditional perimeter-based security less effective, necessitating a focus on securing individual components and inter-service communication.
Compliance and Governance Overhead
Organizations operating in regulated industries face the challenge of extending their compliance obligations (e.g., GDPR, HIPAA, PCI-DSS, ISO 27001) to the cloud. While CSPs offer compliance certifications for their infrastructure, customers remain responsible for their own data and applications. Demonstrating compliance requires meticulous configuration, continuous auditing, and transparent reporting, often across multiple cloud services and regions. Automated compliance tools and Cloud Security Posture Management (CSPM) solutions help manage this complexity.
Strategic Security Controls and Best Practices
Building a secure cloud environment necessitates the implementation of strategic controls and adherence to best practices that go beyond basic protections.
Robust Data Protection Mechanisms
Data protection is paramount. This includes implementing comprehensive encryption strategies, ensuring data is encrypted both when stored (at rest) and when transmitted across networks (in transit). Key management systems (KMS) are crucial for securely managing encryption keys. Data loss prevention (DLP) tools monitor and prevent sensitive data from leaving the organization’s control. Regular data backups and robust disaster recovery plans are also essential for data resilience and availability.
Network Security and Segmentation
Even in a virtualized cloud environment, network security remains a cornerstone. This involves configuring virtual private clouds (VPCs) with appropriate subnets, routing tables, and network access control lists (NACLs). Cloud-native firewalls and security groups filter traffic at various layers. Micro-segmentation, which involves creating granular security zones around individual workloads or applications, dramatically limits the lateral movement of attackers within a cloud network, even if a perimeter defense is breached.
Proactive Threat Detection and Response
Effective cloud security requires continuous vigilance. Security Information and Event Management (SIEM) systems aggregate and analyze security logs from various cloud services, providing a centralized view of security events. Cloud Security Posture Management (CSPM) tools continuously assess cloud configurations against best practices and compliance benchmarks, identifying misconfigurations and vulnerabilities. Endpoint Detection and Response (EDR) solutions extend protection to cloud-based virtual machines and containers. Automated incident response playbooks help rapidly detect, contain, and remediate security incidents.
Secure Configuration and Infrastructure as Code
Misconfigurations are a leading cause of cloud breaches. Adopting Infrastructure as Code (IaC) principles, where cloud infrastructure is defined and provisioned via code (e.g., Terraform, CloudFormation), allows for automated security checks and consistent deployments. Security policies can be embedded directly into IaC templates. Continuous scanning of configurations, automated policy enforcement, and the principle of “immutable infrastructure” (where infrastructure is never modified after deployment, only replaced) significantly reduce configuration drift and human error.
The Horizon of Cloud Security Innovation
Cloud security is a rapidly evolving field, continually leveraging cutting-edge technologies and methodologies to stay ahead of sophisticated threats. Innovation is not just an advantage; it’s a necessity.
Integrating AI and Machine Learning for Threat Intelligence
Artificial Intelligence (AI) and Machine Learning (ML) are transforming cloud security by enhancing threat detection and response capabilities. AI-powered systems can analyze vast quantities of security data to identify anomalous behavior, predict potential threats, and automate the identification of sophisticated attack patterns that might evade traditional signature-based detection. This includes user and entity behavior analytics (UEBA) for detecting insider threats or compromised accounts, and leveraging ML for faster vulnerability scanning and patch management prioritization.
Embracing Zero Trust Architecture
The traditional perimeter-based security model is increasingly insufficient for dynamic cloud environments. Zero Trust Architecture (ZTA) fundamentally shifts the security paradigm from “trust but verify” to “never trust, always verify.” Every user, device, and application attempting to access resources, regardless of their location (inside or outside the corporate network), must be authenticated, authorized, and continuously validated. Implementing ZTA in the cloud involves micro-segmentation, granular access controls, strong identity verification, and continuous monitoring of all interactions.
DevSecOps: Security as a Continuous Process
DevSecOps integrates security practices into every stage of the software development lifecycle (SDLC), from initial design to deployment and operations. It champions a “shift left” approach, embedding security into the CI/CD pipeline rather than treating it as an afterthought. This means automated security testing (SAST, DAST, SCA) in code repositories, vulnerability scanning of container images, and security policy enforcement during deployment. By making security an integral part of development and operations, organizations can identify and remediate vulnerabilities earlier, reducing cost and risk.
The Role of Serverless and Container Security
As organizations embrace serverless computing and container orchestration platforms like Kubernetes, security strategies must adapt. Serverless security focuses on securing the function code itself, managing API gateways, and ensuring proper IAM roles for functions. Container security involves securing the container images (scanning for vulnerabilities), runtime protection of containers, and securing the orchestration platform (e.g., Kubernetes hardening). Tools for container image scanning, runtime security monitoring, and network policy enforcement specific to these ephemeral environments are critical for maintaining integrity and preventing exploits.
In conclusion, security in cloud computing is not a static state but an ongoing journey of adaptation, vigilance, and strategic implementation. It demands a sophisticated understanding of both foundational cybersecurity principles and the nuances of cloud platforms, continuously evolving with technological advancements and the ever-changing threat landscape.