
A Remote Access Trojan (RAT) represents a particularly insidious class of malware designed to grant an unauthorized third party comprehensive, covert control over a victim’s computer or network. Unlike some forms of malware that might simply steal data or disrupt operations, a RAT aims to establish persistent, remote access, effectively turning the compromised machine into a proxy for the attacker. This sophisticated piece of technology has evolved significantly, becoming a staple in the arsenals of cybercriminals, state-sponsored actors, and even industrial espionage rings, embodying a malicious form of innovation in the realm of covert digital control.

The Core Concept of a Remote Access Trojan
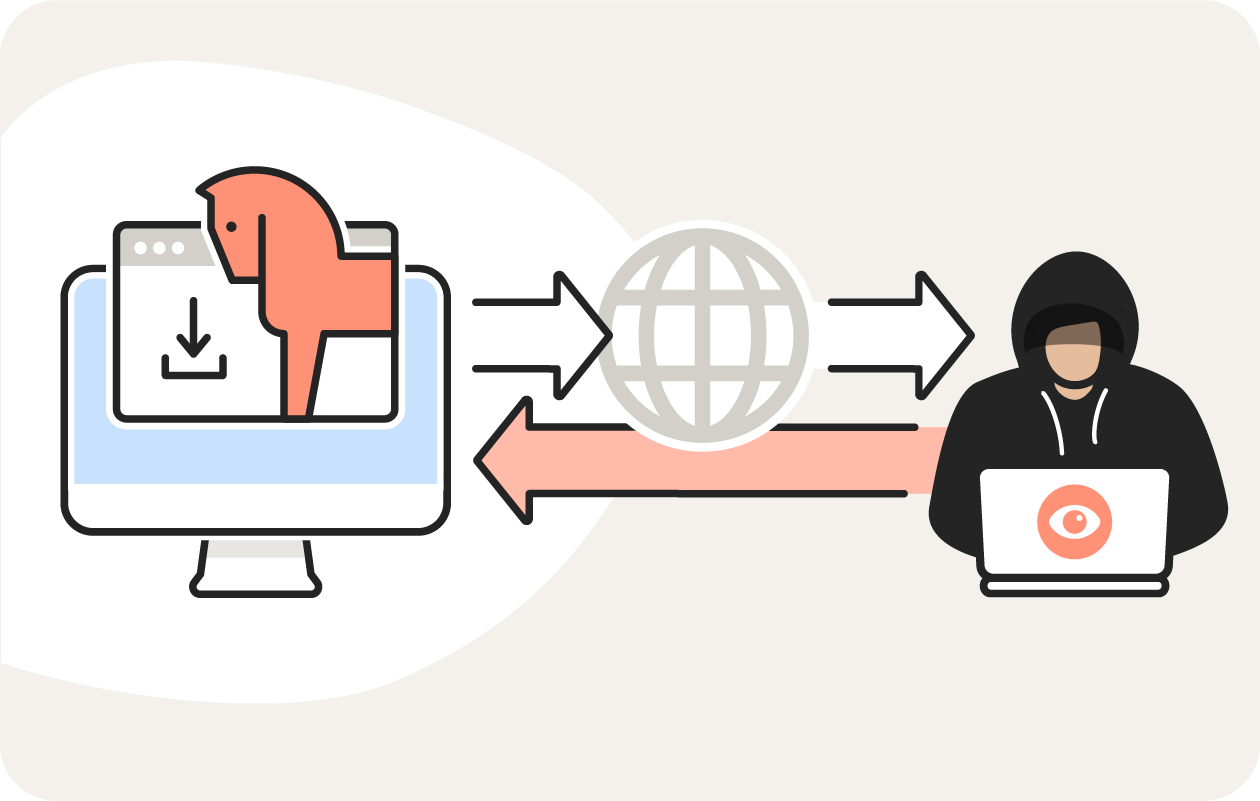
At its heart, a Remote Access Trojan is a program that masquerades as legitimate software or is embedded within it, deceiving users into executing it. Once activated, it silently installs itself on the system, creating a backdoor that allows an attacker to connect to the machine from a remote location. This remote connection grants the attacker capabilities ranging from file manipulation and system monitoring to complete administrative control, all without the victim’s knowledge or consent.
Defining Malicious Remote Control
The defining characteristic of a RAT is its ability to facilitate malicious remote control. While legitimate remote access tools (like TeamViewer or AnyDesk) require explicit user consent and are transparent in their operation, a RAT operates surreptitiously. It bypasses security measures, hides its presence, and establishes a communication channel to a command-and-control (C2) server operated by the attacker. This covert channel then becomes the conduit for issuing commands and receiving stolen data, fundamentally subverting the user’s ownership and control of their own device.
Components and Architecture
A typical RAT architecture involves several key components working in concert:
- The Dropper/Client: This is the initial malicious file that the victim executes. It contains the payload – the actual RAT software – and is responsible for installing it onto the system. Droppers are often disguised as benign files (e.g., PDFs, executables, media files) or embedded within legitimate applications.
- The Server/Agent: Once dropped, this component is the core of the RAT. It installs itself on the victim’s machine, establishes persistence (ensuring it runs after reboots), and opens a communication port. It then attempts to connect back to the attacker’s C2 server.
- The Command-and-Control (C2) Server: This is a system controlled by the attacker that listens for connections from compromised machines. It acts as the central hub for managing multiple infected clients, issuing commands, and collecting data.
- The Attacker’s Console/Controller: This is the software interface used by the attacker to interact with the C2 server and, by extension, the compromised victim machines. It provides a user-friendly way to browse files, execute commands, and view data from afar.
The sophistication of these components can vary wildly, from basic scripts to highly engineered, modular systems capable of dynamic updates and complex evasion.
Mechanisms of Operation and Infiltration
The effectiveness of a RAT hinges on its ability to infiltrate a system without detection and maintain its presence for extended periods. This involves a multi-stage process of initial compromise, establishing persistence, and covert communication.
Initial Compromise Vectors
RATs employ a diverse array of initial compromise vectors, often leveraging social engineering tactics to trick users:
- Phishing and Spear Phishing: Emails containing malicious attachments (e.g., weaponized documents, executables disguised as invoices or critical updates) or links to infected websites are common.
- Malvertising and Drive-by Downloads: Malicious advertisements on legitimate websites can redirect users to exploit kits that automatically download and install RATs without user interaction, leveraging vulnerabilities in browsers or plugins.
- Software Bundling: RATs can be bundled with legitimate freeware or pirated software, installing alongside the desired application without the user’s knowledge.
- Exploiting Vulnerabilities: Attackers may exploit known or zero-day vulnerabilities in operating systems, applications, or network services to directly install the RAT.
- Removable Media: Infected USB drives or other removable media can spread RATs when plugged into target systems.
Establishing Persistence
Once on a system, a RAT strives to ensure its continued operation even after system reboots or user logoffs. This “persistence” is crucial for long-term compromise and involves modifying system configurations:
- Registry Entries: Adding entries to the Windows Registry’s Run keys (e.g.,
HKEY_CURRENT_USERSoftwareMicrosoftWindowsCurrentVersionRun) ensures the RAT launches automatically at startup. - Startup Folders: Placing the RAT’s executable or a shortcut to it in the system’s startup folder.
- Scheduled Tasks: Creating a scheduled task that executes the RAT at specific intervals or system events.
- Services: Installing the RAT as a legitimate-looking system service, making it harder to detect and terminate.
- DLL Sideloading/Hijacking: Exploiting legitimate applications to load a malicious DLL instead of the intended one, thereby executing the RAT code.
Covert Communication Channels
To maintain remote control, the RAT must communicate with its C2 server without raising suspicion. This often involves:
- Standard Protocols: Using common internet protocols like HTTP, HTTPS, or DNS, often blending in with normal network traffic. HTTPS traffic, in particular, can be encrypted, making it harder to inspect.
- Obfuscation and Encryption: Encrypting the data exchanged between the RAT and C2 server to prevent eavesdropping and make detection by network security tools more difficult.
- Dynamic DNS and Fast Flux: Employing dynamic DNS services or fast flux techniques to rapidly change the IP address of the C2 server, making it harder to block or trace.
- Proxy Chains and Tor: Routing communications through multiple proxy servers or the Tor network to anonymize the attacker’s location.
Capabilities and Modus Operandi
The versatility of RATs makes them a potent tool for a wide range of malicious activities. Their capabilities extend far beyond simple data theft, allowing for deep system intrusion and manipulation.
Data Exfiltration and Espionage
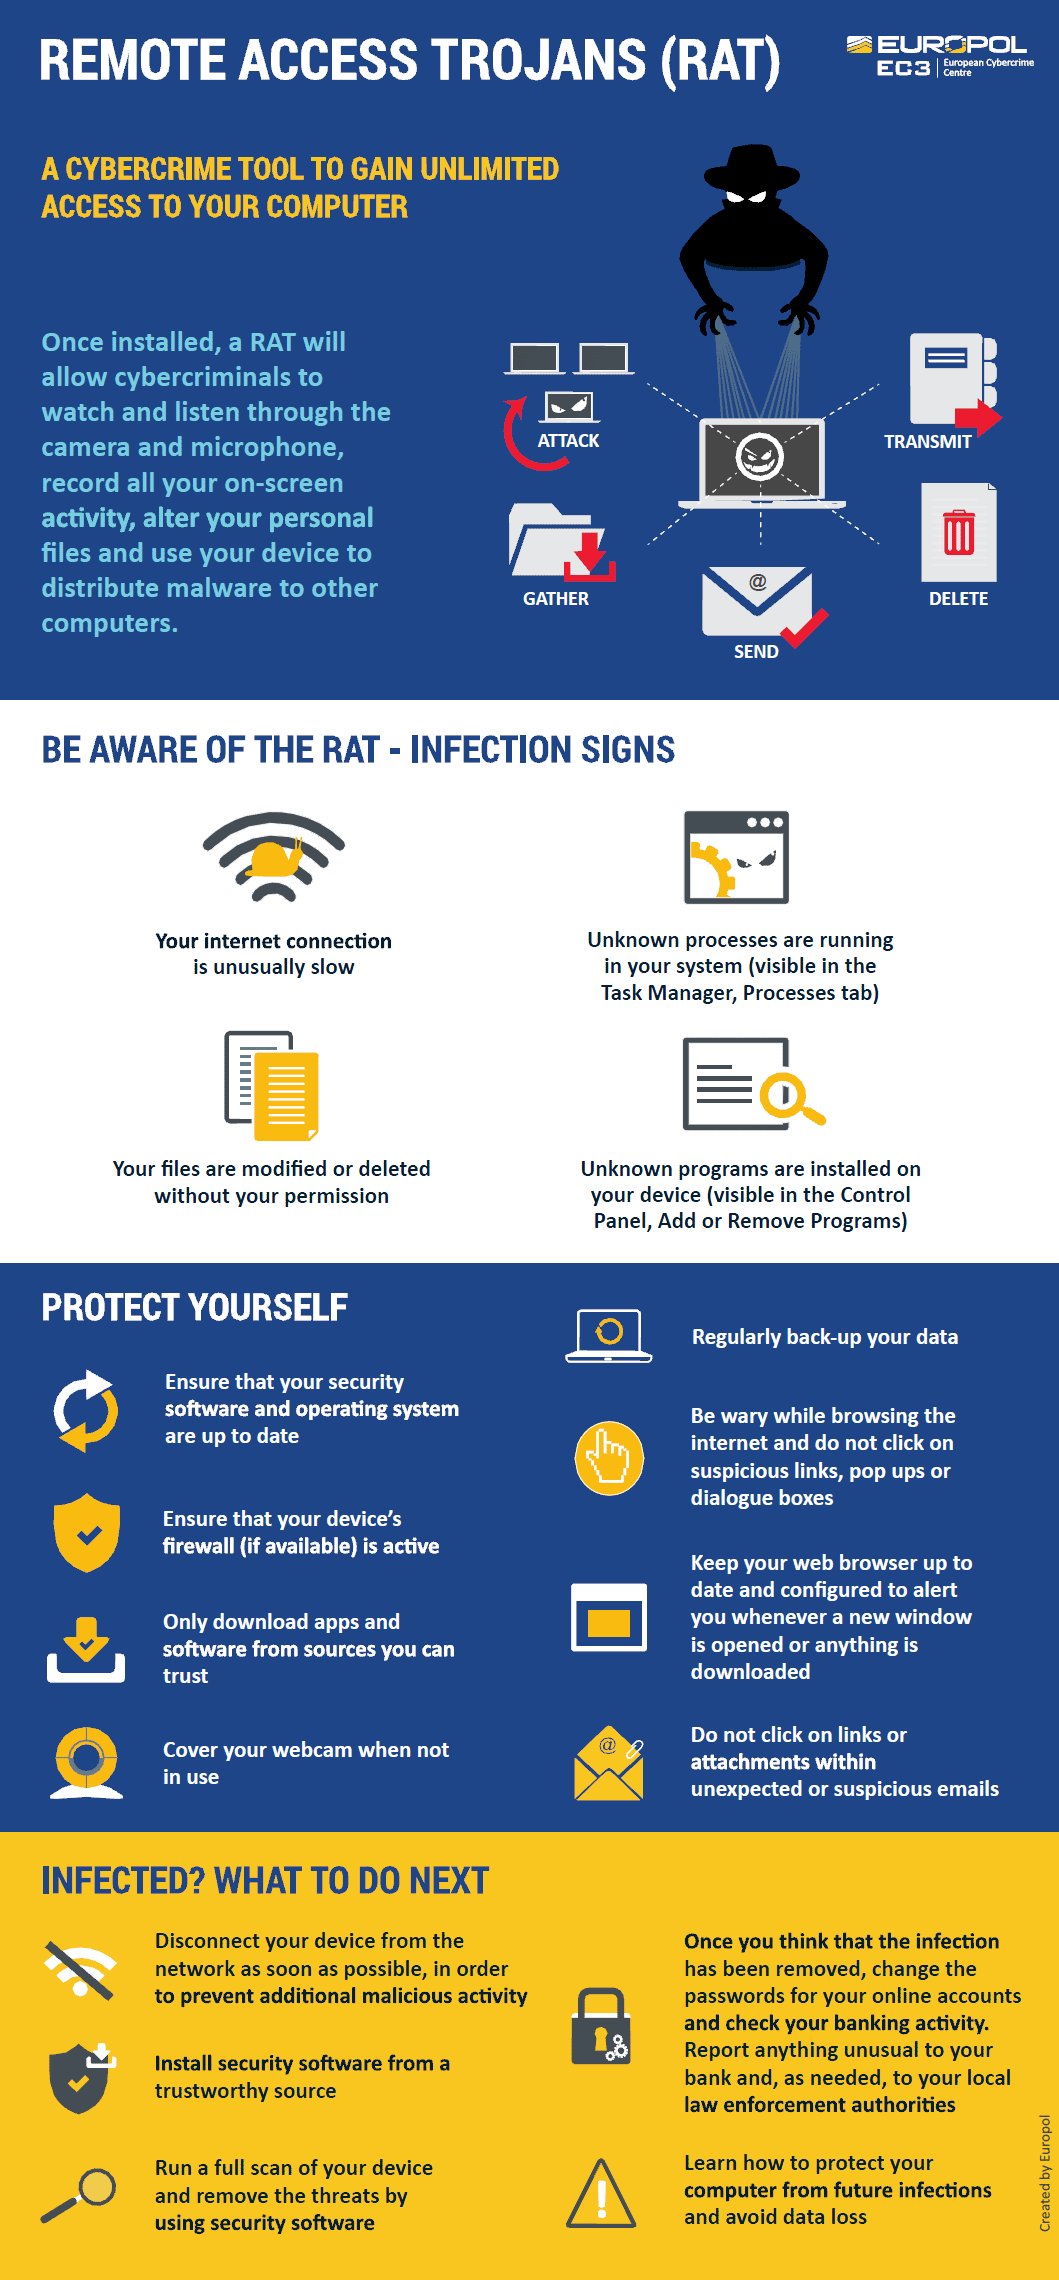
A primary objective of many RAT operations is data exfiltration and espionage. Attackers can:
- Steal Files: Browse, locate, and download sensitive documents, intellectual property, financial records, or personal identifiable information (PII).
- Keylogging: Record every keystroke made by the user, capturing passwords, credit card numbers, and private communications.
- Screen Capturing and Webcam Access: Take screenshots of the victim’s desktop or secretly activate their webcam and microphone to record audio and video, facilitating visual and auditory surveillance.
- Clipboard Monitoring: Capture data copied to the clipboard, which often includes sensitive information.
- Browser History and Cookie Theft: Access browsing history, stored credentials, and session cookies to hijack user accounts.
System Manipulation and Damage
Beyond data theft, RATs enable attackers to directly manipulate the compromised system, sometimes leading to significant damage:
- Remote File Execution: Execute arbitrary commands or install additional malware (e.g., ransomware, cryptocurrency miners) on the victim’s machine.
- System Configuration Changes: Modify system settings, disable security software, or alter firewall rules to facilitate further compromise or cover their tracks.
- Process Management: Start, stop, or kill running processes, potentially disrupting legitimate applications or services.
- Network Scanning: Use the compromised machine as a pivot point to scan internal networks for other vulnerable systems, expanding the attack surface.
- Denial of Service (DoS) Attacks: Enlist the compromised machine into a botnet to participate in large-scale distributed denial of service (DDoS) attacks.
Stealth and Evasion Techniques
Modern RATs are highly sophisticated, incorporating various techniques to remain undetected by security software:
- Polymorphism and Metamorphism: Constantly changing their code signatures to evade signature-based antivirus detection.
- Anti-VM and Anti-Sandbox: Detecting if they are running within a virtual machine or sandbox environment (often used by security researchers) and altering their behavior or refusing to execute.
- Code Obfuscation: Making their code difficult to read and analyze, hindering reverse engineering efforts.
- Rootkit Functionality: Employing rootkit techniques to hide their files, processes, and network connections from the operating system and security tools.
- Process Hollowing/Injection: Injecting malicious code into legitimate running processes to disguise their activity.
The Evolution of RATs: A Malicious Innovation
The trajectory of RAT development showcases a continuous arms race between attackers and defenders, embodying a malicious form of technological innovation. From rudimentary tools to advanced persistent threat (APT) capabilities, RATs have become increasingly sophisticated.
From Simple Keyloggers to Sophisticated APT Tools
Early forms of RATs were relatively basic, often focused on keylogging or simple file transfer. However, over time, they integrated more advanced features, evolving into comprehensive espionage platforms. Today’s state-of-the-art RATs are modular, allowing attackers to load specific plugins for different tasks (e.g., VoIP recording, specific software exploitation). They are often bespoke creations used in targeted attacks against high-value targets, known as Advanced Persistent Threats (APTs). These APT RATs are designed for long-term, covert operations, featuring sophisticated evasion techniques and custom-tailored exploits.
AI and Automation in RAT Development
The integration of artificial intelligence and automation is the next frontier for RATs. While not fully autonomous, elements of AI can be seen in:
- Automated Reconnaissance: AI algorithms can analyze target systems for vulnerabilities, suggesting the most effective exploit paths.
- Adaptive Evasion: Machine learning models can help RATs adapt their behavior to evade new detection signatures or sandbox environments in real-time.
- Intelligent Data Filtering: AI could prioritize and filter stolen data, sending only the most valuable information back to the C2 server, reducing network footprint.
- Self-Healing Mechanisms: Future RATs might use AI to detect attempts to remove them and automatically reinstall or repair their components, increasing persistence.
This evolution signifies a shift towards more intelligent, resilient, and autonomous malware, posing unprecedented challenges to cybersecurity.
The Arms Race in Cybersecurity
The continuous innovation in RAT technology directly fuels the cybersecurity arms race. As new detection and prevention mechanisms are developed, attackers respond with more advanced RATs that circumvent these defenses. This iterative process drives both sides to push the boundaries of technological capability, highlighting the critical importance of continuous research, development, and adaptation in defensive security strategies. The very existence and evolution of RATs exemplify a significant, albeit negative, aspect of technological advancement, demonstrating how innovation can be weaponized for illicit gain and control.
Mitigation and Defensive Strategies
Protecting against Remote Access Trojans requires a multi-layered security approach, combining proactive measures, robust detection capabilities, and continuous user education.
Proactive Security Measures
Preventing initial infection is paramount:
- Robust Endpoint Protection: Deploying next-generation antivirus (NGAV) and endpoint detection and response (EDR) solutions that use behavioral analysis and machine learning to detect unknown threats.
- Firewalls and Intrusion Prevention Systems (IPS): Configuring network firewalls to block suspicious outbound connections and deploying IPS to detect and prevent exploitation attempts.
- Patch Management: Regularly updating operating systems, applications, and firmware to patch known vulnerabilities that RATs could exploit.
- Email Security Gateways: Implementing advanced email filtering to detect and block phishing attempts and malicious attachments.
- Application Whitelisting: Restricting the execution of unauthorized applications, only allowing approved software to run.
Detection and Response
Even with proactive measures, some RATs may slip through. Effective detection and rapid response are crucial:
- Network Monitoring: Continuously monitoring network traffic for unusual patterns, suspicious C2 communications, or data exfiltration attempts.
- Behavioral Analysis: Using security information and event management (SIEM) systems to analyze system and network logs for anomalous behaviors indicative of RAT activity.
- Regular Audits and Scans: Conducting periodic vulnerability assessments and penetration tests to identify weaknesses.
- Incident Response Plan: Having a well-defined incident response plan to quickly identify, contain, eradicate, and recover from RAT infections.
User Awareness and Best Practices
The human element remains a critical vulnerability. Educating users is a vital defense:
- Security Awareness Training: Training employees to recognize phishing attempts, identify suspicious links, and understand the risks associated with downloading untrusted software.
- Strong Password Policies and Multi-Factor Authentication (MFA): Enforcing strong, unique passwords and using MFA to protect accounts, even if credentials are stolen by a keylogger.
- Principle of Least Privilege: Granting users only the necessary permissions to perform their job functions, limiting the potential damage of a compromised account.
- Data Backup: Regularly backing up critical data to ensure recovery in case of system compromise or data encryption.
By understanding the technical intricacies, evolving capabilities, and prevalent threat vectors of Remote Access Trojans, organizations and individuals can implement more effective defenses, mitigating the significant risks posed by this sophisticated form of malicious technological innovation.