
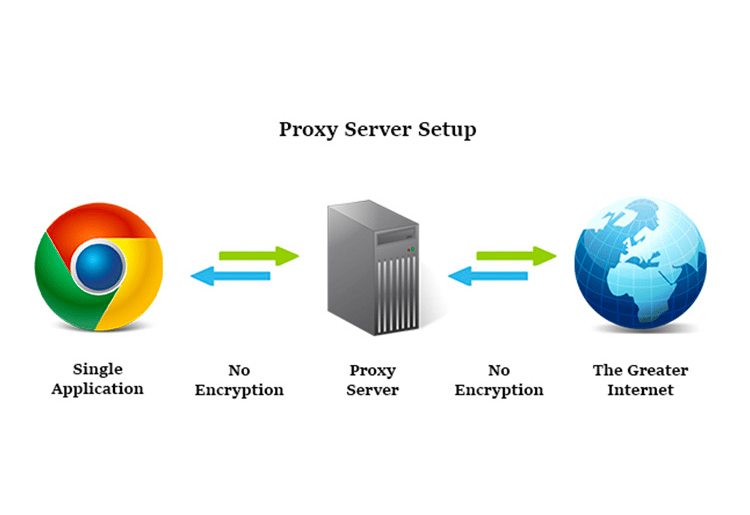
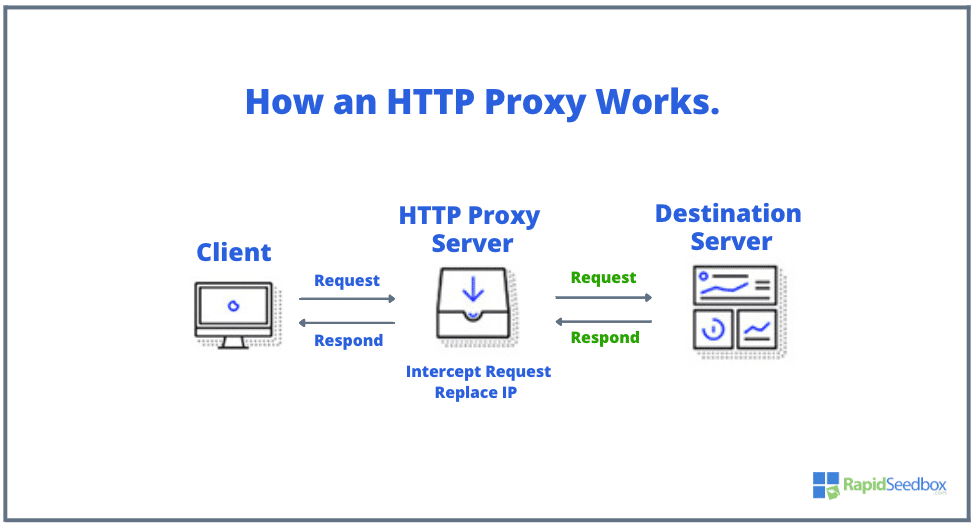
HTTP proxies stand as fundamental components within the architecture of modern internet communication, acting as intermediaries for web requests. At its core, an HTTP proxy server positions itself between a client, such as a web browser or an application, and a destination server, like a website host. Rather than the client connecting directly to the destination, it sends its request to the proxy server. The proxy then processes this request, forwarding it to the target server, and subsequently receives the response, which it then relays back to the original client. This seemingly simple redirection introduces a profound layer of control, security, and performance optimization that has become indispensable in today’s interconnected digital landscape.
The evolution of HTTP proxies mirrors the growth of the internet itself. Initially conceived to enhance network performance through caching and to facilitate access control, their roles have expanded dramatically. Today, proxies are integral to enterprise network security, privacy-enhancing solutions for individual users, content delivery networks (CDNs), and even advanced web scraping and data aggregation efforts. Understanding the mechanisms and myriad applications of HTTP proxies is crucial for anyone navigating or developing within the complex ecosystem of the internet.
Understanding the Core Concept of an HTTP Proxy
The operational essence of an HTTP proxy lies in its intermediary function. When a client initiates an HTTP request (e.g., accessing a webpage), instead of resolving the domain name and connecting directly to the web server, it is configured to send this request to a proxy server. The proxy server, upon receiving the request, analyzes it, and based on its internal rules and configurations, decides whether to forward it, block it, or serve it from its cache.
This process involves several key steps:
- Client Request: The client, unaware of the destination server’s actual IP address, directs its HTTP request (e.g., GET /index.html HTTP/1.1 Host: example.com) to the proxy server.
- Proxy Processing: The proxy receives the request. It extracts the intended destination (e.g., example.com) and any other relevant headers.
- Proxy Forwarding: The proxy establishes its own connection to the destination server (example.com) and forwards the client’s request.
- Server Response: The destination server processes the request and sends its HTTP response back to the proxy.
- Proxy Relay: The proxy receives the server’s response and relays it back to the original client.
This intermediary role allows the proxy to inspect, modify, log, and even cache the traffic flowing through it. By abstracting the direct connection between client and server, proxies offer a versatile point of control and optimization, enabling a range of functionalities from bolstering security to improving network efficiency.
Types of HTTP Proxies and Their Distinct Functions
The broad category of HTTP proxies encompasses several distinct types, each designed for specific purposes and offering different levels of functionality and anonymity.
Forward Proxies
A forward proxy is the most common type, typically deployed within a private network (like an office or a home network) to provide access to the public internet for clients within that network. Clients are explicitly configured to use the forward proxy.
- Purpose: To control outbound traffic, cache frequently accessed content, enforce internet usage policies, and provide a single point of exit to the internet for multiple clients.
- Example: An organization might use a forward proxy to filter malicious websites, block social media access during work hours, or anonymize its employees’ web traffic to some degree by presenting the proxy’s IP address instead of individual client IPs.
Reverse Proxies
Unlike forward proxies, which sit in front of clients, a reverse proxy sits in front of one or more web servers. It intercepts requests from the internet before they reach the actual web servers.
- Purpose: To provide load balancing across multiple servers, enhance security by obscuring the true identity of backend servers, serve cached content, perform SSL/TLS termination, and protect against certain types of attacks.
- Example: A popular e-commerce website might use a reverse proxy to distribute incoming customer requests across several web servers, preventing any single server from becoming overwhelmed and ensuring high availability. It can also handle SSL encryption/decryption, offloading this computational task from the backend servers.
Transparent Proxies
A transparent proxy is one that clients are not aware they are using. Network configurations (e.g., router settings) redirect traffic through the proxy without requiring explicit client-side configuration.
- Purpose: Often used by ISPs or public Wi-Fi providers to implement content filtering, caching, or to log user activity without user interaction.
- Drawback: Lacks user consent and can be perceived as an invasion of privacy if not used responsibly and disclosed.
Anonymous Proxies
Anonymous proxies aim to conceal the client’s original IP address from the destination server. There are different levels of anonymity:
- Anonymous (Level 2): Hides the client’s IP address but identifies itself as a proxy in HTTP headers (e.g., via
X-Forwarded-Forheader with a false IP, orViaheader). - Distorting (Level 3): Provides a false IP address for the client while still identifying itself as a proxy.
- High-Anonymity / Elite (Level 1): Conceals the client’s IP address and does not reveal that it is a proxy, making the client appear to be directly connected to the server. These are highly sought after for privacy-sensitive tasks.
Key Benefits and Applications of HTTP Proxies
The widespread adoption of HTTP proxies across various technological domains stems from the significant benefits they offer in terms of security, performance, and operational flexibility.
Enhanced Security and Privacy
Proxies act as a vital line of defense, shielding internal networks and individual users from direct exposure to potential online threats.
- Anonymity: By masking the client’s original IP address, proxies make it harder for websites to track user behavior, gather personal data, or identify the user’s geographic location. This is particularly valuable for privacy-conscious individuals and organizations engaged in sensitive research or data collection.
- Access Control and Filtering: Organizations use forward proxies to enforce internet usage policies, blocking access to malicious websites, inappropriate content, or time-wasting platforms. Reverse proxies protect backend servers from direct internet exposure, acting as a firewall and mitigating DDoS attacks by absorbing initial traffic.
- SSL/TLS Offloading: Reverse proxies can handle the computationally intensive task of encrypting and decrypting SSL/TLS traffic, freeing up backend servers to focus on serving content.
Improved Performance and Efficiency
Proxies can significantly boost network performance and reduce bandwidth consumption.
- Caching: Proxies can store copies of frequently requested web pages, images, and other resources. When a client requests content already in the proxy’s cache, the proxy serves it directly without needing to fetch it from the origin server. This dramatically reduces latency and network traffic.
- Load Balancing: Reverse proxies are critical for distributing incoming network traffic across multiple backend servers. This ensures that no single server becomes overloaded, improving the availability and responsiveness of web services, especially during peak traffic.
- Content Compression: Some proxies can compress content before sending it to the client, especially for slower connections, further enhancing perceived performance.
Overcoming Geo-restrictions and Access Barriers
For users facing geographical content restrictions or censorship, proxies offer a crucial workaround.
- Bypassing Geo-blocks: By routing traffic through a proxy server located in a different region, users can appear to be accessing content from that region, thereby bypassing geographical restrictions imposed by streaming services or websites.
- Circumventing Censorship: In regions with strict internet censorship, proxies can enable access to blocked websites and services, providing a gateway to unfiltered information.
Operational Flexibility and Logging
Proxies provide powerful tools for network administrators and developers.
- Traffic Monitoring and Logging: Proxies can log all requests and responses passing through them, providing valuable data for auditing, debugging, security analysis, and understanding network usage patterns.
- Protocol Conversion: While primarily for HTTP, some proxies can facilitate communication between different network protocols or apply transformations to data.
- API Gateway: In modern microservices architectures, reverse proxies often serve as API gateways, routing requests to appropriate backend services, handling authentication, and rate limiting.
Challenges and Considerations When Using Proxies
While HTTP proxies offer numerous advantages, their implementation and usage are not without complexities and potential drawbacks that require careful consideration.
Performance Overhead
Introducing an intermediary server inevitably adds a step to the communication path, which can, under certain circumstances, introduce latency. While caching often mitigates this, poorly configured or overloaded proxy servers can become bottlenecks, slowing down web access rather than speeding it up. The processing required for security checks, content filtering, or complex routing rules also consumes resources, which must be factored into deployment planning.
Security and Trust Implications
The very nature of a proxy, as an intermediary that can inspect and modify traffic, raises significant security and trust concerns.
- Interception Risk: If a proxy server itself is compromised, it could be used to intercept sensitive user data, inject malicious content, or redirect users to phishing sites. This is especially true for third-party proxy services where the level of trust in the provider’s security practices is paramount.
- Man-in-the-Middle (MitM) Attacks: While proxies can defend against external threats, a malicious proxy can itself facilitate a MitM attack, eavesdropping on encrypted traffic if it terminates SSL/TLS connections without proper authentication.
- Misconfiguration: Improperly configured proxies can inadvertently expose internal network details, create open relays, or otherwise weaken security postures.
Complexity and Management
Deploying and managing proxy servers, especially in large-scale environments or with advanced configurations, can be complex.
- Setup and Maintenance: Configuring client applications or network infrastructure to correctly route traffic through proxies, managing proxy rules, and keeping the proxy software updated requires technical expertise.
- Troubleshooting: Diagnosing network issues can be more challenging with a proxy in the middle, as it adds another layer where problems can occur.
- Scalability: Ensuring a proxy infrastructure can handle increasing traffic demands without becoming a bottleneck requires careful planning for hardware, software, and network capacity.
Legal and Ethical Considerations
The use of proxies, particularly for anonymity or bypassing restrictions, ventures into complex legal and ethical territory.
- Terms of Service Violations: Using proxies to circumvent geo-restrictions for copyrighted content (e.g., streaming services) often violates the terms of service of those platforms and could lead to account suspension.
- Illegal Activities: While proxies offer legitimate privacy benefits, they can also be exploited by malicious actors for illegal activities, such as cybercrime or content distribution that violates intellectual property rights. Users must be aware of the legal implications of their activities when using proxies.
- Data Privacy Regulations: Organizations operating proxies must comply with data privacy regulations (e.g., GDPR, CCPA) regarding the logging and handling of user traffic data, especially for transparent proxies.
The Evolving Role of Proxies in Modern Networks
The landscape of internet infrastructure is constantly evolving, and HTTP proxies are adapting to meet new challenges and integrate with emerging technologies. Their role is becoming more specialized and deeply embedded within complex systems.
Integration with Content Delivery Networks (CDNs)
CDNs heavily leverage the principles of reverse proxying and caching. They consist of globally distributed proxy servers that store copies of website content closer to end-users. When a user requests content, the CDN directs the request to the nearest proxy server, which then delivers the cached content, dramatically reducing latency and improving content delivery speed. This integration highlights the continued importance of caching and distributed proxy architectures for global content distribution.
Microservices and API Gateways
In modern application development, especially with microservices architectures, reverse proxies are frequently used as API gateways. These gateways act as the single entry point for all client requests, routing them to the appropriate backend microservice. They also handle cross-cutting concerns such as authentication, authorization, rate limiting, and logging, abstracting the complexity of the microservices from the client. This pattern simplifies client-side development and enhances the manageability and security of distributed applications.
Security at the Edge
As cyber threats become more sophisticated, proxies are increasingly crucial for “security at the edge.” Next-generation firewalls, Web Application Firewalls (WAFs), and advanced threat protection systems often incorporate proxy functionalities. They inspect traffic for anomalies, known attack patterns, and malicious payloads before allowing it to reach internal resources. This proactive defense mechanism is vital in protecting critical infrastructure and sensitive data from external attacks.

IoT and Edge Computing
The proliferation of Internet of Things (IoT) devices and the rise of edge computing present new frontiers for proxy technology. Proxies at the edge can facilitate communication between IoT devices and cloud services, perform local data aggregation and filtering, and enforce security policies closer to the data source. This reduces bandwidth requirements, lowers latency for critical operations, and enhances the overall security posture of IoT deployments.
HTTP proxies, once primarily a tool for caching and access control, have evolved into indispensable components of the modern internet. Their diverse types and sophisticated applications underscore their foundational importance in enhancing security, boosting performance, and enabling flexible network architectures. As technology continues to advance, the principles and functionalities of HTTP proxies will undoubtedly remain central to building robust, secure, and efficient digital ecosystems.