
In an increasingly interconnected world driven by innovation, understanding the fundamental mechanics of network communication is paramount. One such critical concept, often encountered when deploying specialized systems or custom applications, is port forwarding on a router. At its core, port forwarding is a network configuration that directs incoming external requests from the internet to a specific device or service within a local private network. It acts as a bridge, allowing external entities to initiate connections with internal systems that would otherwise be inaccessible due to network security measures.
The Fundamentals of Network Address Translation (NAT)
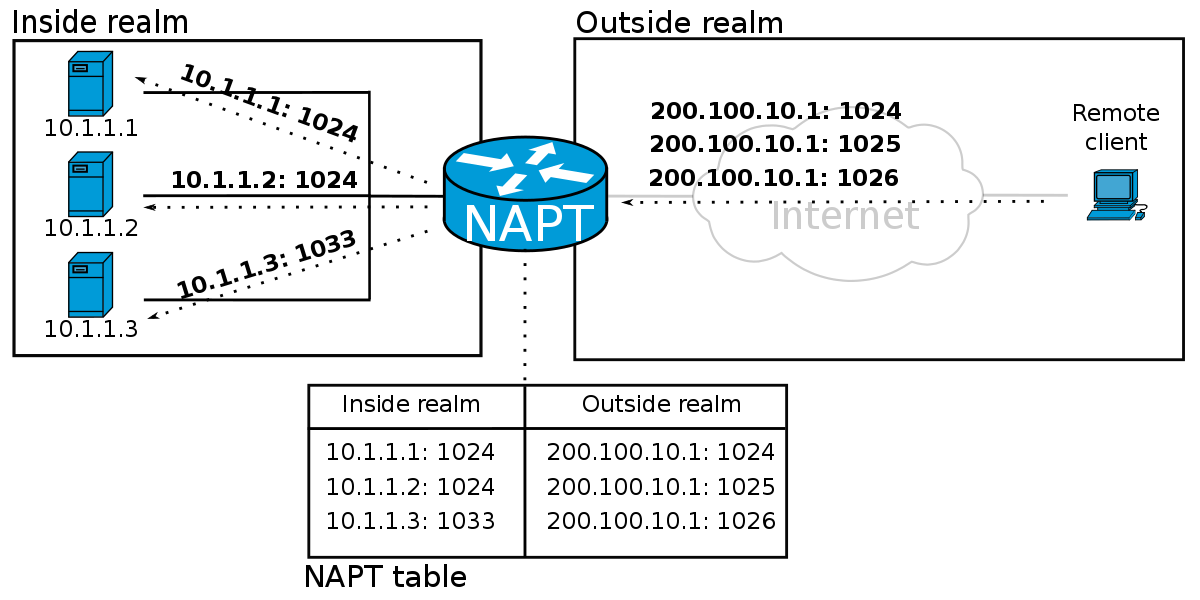
To truly grasp port forwarding, one must first understand the role of Network Address Translation (NAT) within modern networks. Most homes and businesses operate behind a router, which serves as the primary gateway to the internet. This router performs NAT, a process that allows multiple devices on a private network to share a single public IP address assigned by an Internet Service Provider (ISP).
The Role of Public and Private IPs
Every device connected to the internet requires an IP address to communicate. These addresses come in two main types: public and private. A public IP address is unique across the entire internet and is assigned to your router by your ISP. This is the address that the rest of the internet sees and uses to communicate with your network.
Conversely, private IP addresses are used within a local area network (LAN) and are not routable on the internet. Devices within your home or office (computers, smart devices, servers) are assigned private IP addresses, typically in ranges like 192.168.x.x, 172.16.x.x, or 10.x.x.x. These addresses are unique within your private network but can be duplicated in other private networks globally.
How NAT Acts as a Gateway
NAT operates by translating private IP addresses and port numbers into the router’s public IP address and a corresponding public port number when outgoing traffic leaves the local network. When a device inside your network requests data from the internet, the router modifies the packet’s source address to its own public IP before sending it out. When the response returns, the router uses a stored mapping to identify the original internal device and forwards the data accordingly.
This system provides a crucial layer of security, as external entities cannot directly initiate connections with devices inside your private network. They can only see and interact with the router’s public IP address. While excellent for general browsing and outgoing connections, this design inherently blocks unsolicited incoming connections, which are often necessary for specialized applications or services that need to be accessible from outside the local network.
Demystifying Port Forwarding
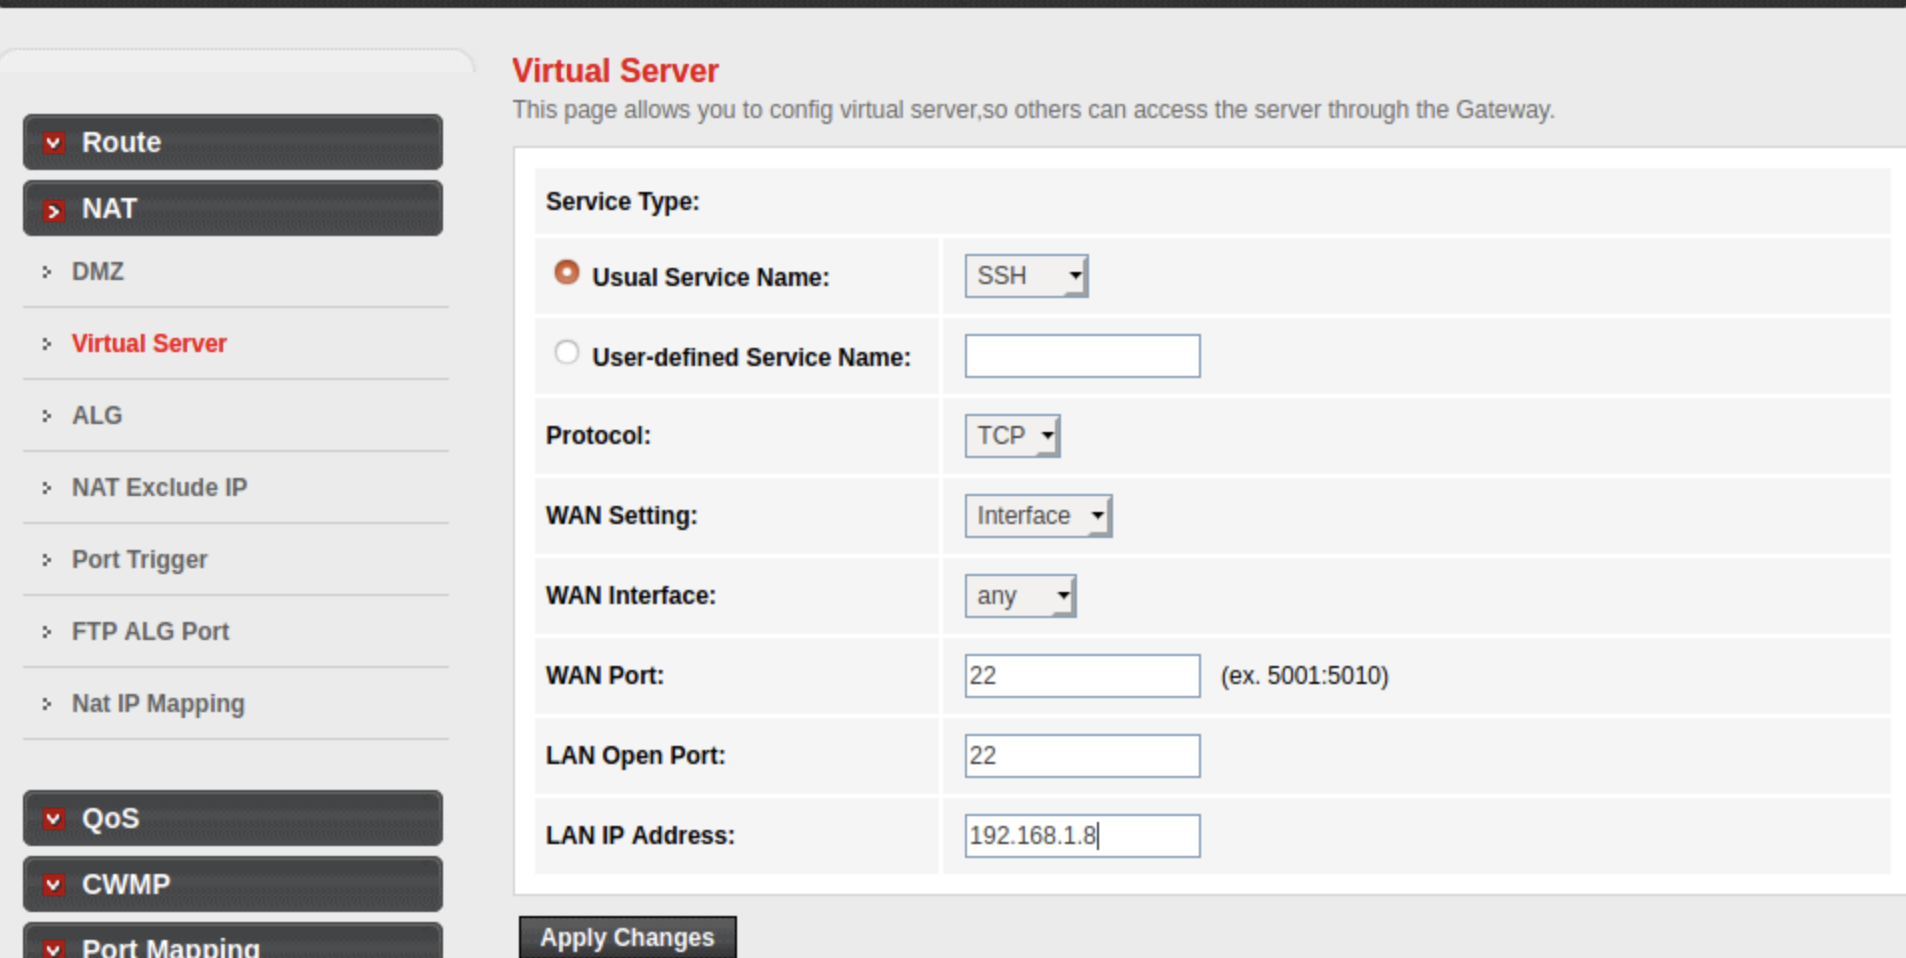
Port forwarding bypasses the default NAT behavior for specific types of incoming traffic. It creates a static, predefined rule that tells the router: “When an external connection attempt arrives on a particular public port, always direct it to a specific private IP address and port within the local network.”
The Concept of Ports and Services
In networking, a “port” is a numerical label (from 1 to 65535) that identifies a specific application or service running on a device. When data is sent over a network, it’s not just addressed to an IP address; it’s also addressed to a specific port on that IP address. For instance, web traffic typically uses port 80 (HTTP) or 443 (HTTPS), while email might use port 25 (SMTP) or 993 (IMAPS).
Directing External Traffic Inward
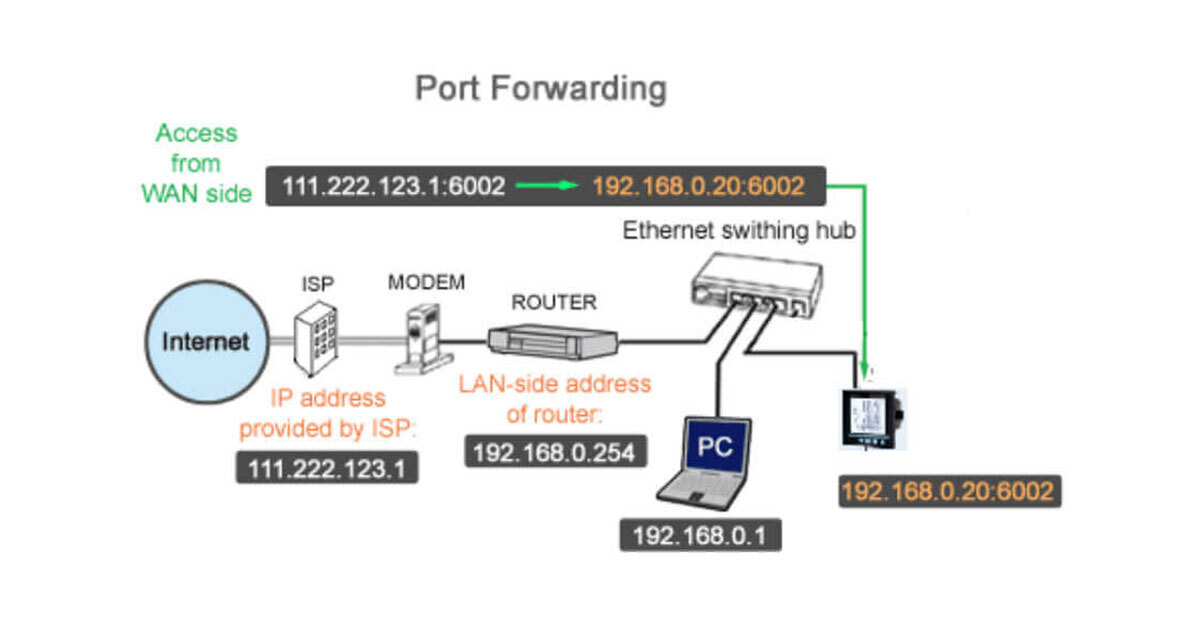
Without port forwarding, if an external user tries to connect to your router’s public IP address on, say, port 8080, the router won’t know which internal device or service to send that request to and will typically block it. Port forwarding solves this by mapping the public IP and a chosen public port to a specific private IP and port.
For example, if you’re running a custom application server on a device with a private IP of 192.168.1.100, listening on port 8080, you would configure port forwarding on your router to say: “Any incoming traffic to my public IP on public port 8080 should be forwarded to 192.168.1.100 on private port 8080.” This effectively opens a dedicated “door” through your router’s firewall directly to that specific internal service.
Static IP Addresses and Dynamic DNS
For port forwarding to be reliable, the internal device to which traffic is being forwarded ideally needs a static private IP address. If the device’s private IP changes (which can happen with DHCP, where IPs are dynamically assigned), the port forwarding rule will break, as it will be pointing to the wrong internal address. Most routers allow you to reserve a static IP for a specific device based on its MAC address.
Furthermore, since most residential and small business public IP addresses are dynamic (meaning they can change periodically), accessing a forwarded service from outside can be challenging. This is where Dynamic DNS (DDNS) services become invaluable. A DDNS service automatically updates a registered domain name (e.g., mycustomserver.ddns.net) with your router’s current dynamic public IP address. This allows external users to connect to your custom services using an easy-to-remember domain name, even if your public IP changes.
Practical Applications in Modern Tech & Innovation
Port forwarding is a cornerstone for numerous innovative technological applications, enabling remote access, specialized data handling, and custom service deployments that would otherwise be impossible.
Enabling Remote Access to Internal Systems
For professionals and enthusiasts working with advanced systems, port forwarding is crucial for managing internal servers, network-attached storage (NAS), or specialized workstations remotely. This allows for off-site administration, data retrieval, or collaborative work without needing to be physically present on the local network. For instance, a developer might forward a port to access a local code repository or a test server from anywhere with an internet connection.
Facilitating IoT and Smart Device Communication
The proliferation of Internet of Things (IoT) devices often relies on cloud services for remote interaction. However, for specialized or custom IoT deployments, particularly those involving sensitive data or requiring ultra-low latency, port forwarding can enable direct communication. This allows custom controllers or monitoring applications outside the local network to directly interface with specific smart sensors, actuators, or local automation hubs, fostering more localized and private smart environments. This is particularly relevant for industrial IoT or bespoke home automation systems where direct, secure access is preferred over third-party cloud intermediaries.
Hosting Specialized Servers and Custom Applications
Many cutting-edge projects and niche applications require hosting custom servers. This could involve hosting a private data processing unit, a dedicated server for a specialized simulation, a custom voice or video communication server, or a unique web application for internal use. Port forwarding makes these local servers accessible to external users or other internet-connected services, effectively transforming an internal machine into a publicly available host for designated purposes. This is especially vital for startups or researchers who may not want to rely solely on public cloud infrastructure for highly specific or experimental applications.
Enhancing Peer-to-Peer Connectivity
While many peer-to-peer (P2P) applications attempt to bypass NAT using techniques like UPnP (Universal Plug and Play) or NAT traversal, port forwarding often provides the most robust and reliable method for establishing direct connections. For applications requiring consistent, high-bandwidth P2P communication – such as custom real-time data streaming, distributed computing projects, or direct file sharing for large datasets – manually configuring port forwarding can significantly improve performance, stability, and security by ensuring a direct pathway between peers.
Security Considerations and Best Practices
While port forwarding is a powerful tool for innovation, it inherently introduces security risks by opening a direct pathway into your local network. It is crucial to implement it with a strong awareness of these risks and adhere to best practices.
Understanding the Risks
Every open port is a potential entry point for malicious actors. If the service or device exposed via port forwarding has vulnerabilities (e.g., outdated software, weak passwords, unpatched exploits), it could be compromised. This could lead to unauthorized access to your internal network, data breaches, or the device being used as part of a botnet.
Implementing Secure Configurations
- Use Strong Passwords: Ensure any service exposed via port forwarding is protected by robust, unique passwords.
- Keep Software Updated: Regularly update the firmware of the device being exposed and the software running the service to patch known vulnerabilities.
- Use Specific Ports: Only forward the exact ports required by the service. Avoid forwarding entire ranges or common ports like 21 (FTP), 23 (Telnet), 80 (HTTP), 443 (HTTPS) if not absolutely necessary and secured.
- Forward to Specific Devices: Always specify the exact private IP address of the device needing access, ensuring that only the intended machine receives the incoming traffic.
- Utilize Firewalls: Implement a software firewall on the internal device receiving the forwarded traffic to add another layer of security. Configure it to only allow traffic on the forwarded port from trusted IP addresses if possible.
- VPN (Virtual Private Network): For remote access to multiple internal services, consider setting up a VPN server on your router or a dedicated internal device. This allows you to securely access your entire internal network as if you were physically there, often negating the need for multiple port forwarding rules.
Monitoring and Maintenance
Once port forwarding is configured, it’s not a set-it-and-forget-it solution. Regularly review your router’s port forwarding rules to ensure only necessary ports are open. Monitor the logs of the exposed services for any unusual activity or attempted breaches. For critical applications, consider implementing intrusion detection systems (IDS) or intrusion prevention systems (IPS) to further safeguard your internal network.
In the realm of Tech & Innovation, port forwarding serves as a fundamental enabler, allowing developers, researchers, and advanced users to push the boundaries of what’s possible with connected systems. By understanding its mechanics and adhering to robust security practices, innovators can leverage this essential networking tool to build, deploy, and manage the next generation of custom, powerful, and remotely accessible technological solutions.