
In an increasingly digitized world, where transactions traverse vast global networks, the security of sensitive financial data stands as a paramount concern for consumers, businesses, and regulatory bodies alike. The Payment Card Industry Data Security Standard (PCI DSS) emerges as a critical framework, a robust set of requirements designed to ensure that all companies that process, store, or transmit credit card information maintain a secure environment. It is more than just a compliance checklist; it represents a fundamental commitment to safeguarding the financial ecosystem against ever-evolving cyber threats. Understanding PCI DSS is essential not only for preventing costly data breaches but also for fostering trust and ensuring the integrity of modern payment systems.
The Imperative of Payment Card Security
The rapid adoption of electronic payments has revolutionized commerce, offering unparalleled convenience and efficiency. However, this digital transformation comes with inherent risks, primarily the potential for widespread data compromise if security measures are inadequate. The financial fallout from a data breach can be catastrophic, encompassing direct financial losses, reputational damage, legal liabilities, and erosion of customer confidence. Recognizing this critical vulnerability, major payment card brands—Visa, Mastercard, American Express, Discover, and JCB—collaborated to establish a unified standard that could be universally applied to protect cardholder data. This collaboration birthed the PCI DSS, a global standard designed to reduce credit card fraud through increased security controls around cardholder data.
The Landscape of Cyber Threats
The digital threat landscape is dynamic and sophisticated. Malicious actors continuously devise new methods to exploit vulnerabilities in payment systems, ranging from sophisticated phishing campaigns and ransomware attacks to insider threats and weak network configurations. Point-of-sale (POS) intrusions, web application attacks, and malware are common vectors for cardholder data theft. Without a standardized, comprehensive security framework like PCI DSS, organizations would be left to develop their own disparate security protocols, leading to inconsistent protection levels and creating weak links in the payment chain that could be exploited. PCI DSS provides a defensive blueprint, mandating specific security practices that address these diverse threats, thereby fortifying the security posture of entities handling sensitive payment card information.
Core Principles and Requirements of PCI DSS
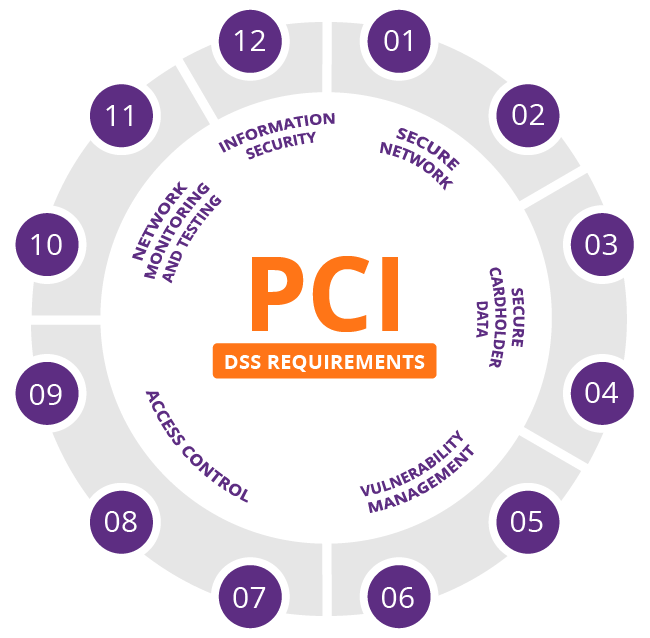
The PCI DSS is built upon twelve core requirements, categorized into six logically grouped goals, each addressing a fundamental aspect of data security. These requirements are extensive and cover virtually every aspect of an organization’s IT infrastructure and security practices that interact with cardholder data. Adherence to these principles forms the bedrock of a secure payment processing environment.
Building and Maintaining Secure Networks
The first goal emphasizes the need for a robust and secure network infrastructure. This involves establishing and maintaining firewalls to protect cardholder data, ensuring that networks are segmented, and implementing strong security configurations. It also mandates avoiding the use of vendor-supplied defaults for system passwords and other security parameters, as these are often publicly known and easily exploited. This foundational step is crucial for creating a secure perimeter around the cardholder data environment (CDE).
Protecting Cardholder Data
At the heart of PCI DSS is the explicit requirement to protect stored cardholder data. This means restricting storage to the absolute minimum necessary, encrypting sensitive authentication data during transmission across open, public networks, and using strong cryptography to protect stored primary account numbers (PAN). Data encryption, tokenization, and truncation are key technologies employed to minimize the risk should data ever be compromised. This requirement directly tackles the goal of making stolen data useless to attackers.
Implementing Robust Access Control Measures
Unauthorized access is a primary vector for data breaches. PCI DSS mandates strict access control. This includes assigning a unique ID to each person with computer access, restricting physical access to cardholder data, and implementing strong password policies. Access to systems and data must be on a “need-to-know” basis, ensuring that employees only have the privileges necessary to perform their job functions. Robust authentication mechanisms, including multi-factor authentication, are also critical components.
Regular Monitoring and Testing of Networks
A secure environment is not static; it requires continuous vigilance. PCI DSS requires regular monitoring and testing of network systems. This involves tracking and monitoring all access to network resources and cardholder data, regularly testing security systems and processes, and performing vulnerability scans and penetration testing. These proactive measures help identify and remediate weaknesses before they can be exploited by malicious actors, ensuring that security controls remain effective against evolving threats.
Maintaining Information Security Policies
Beyond technical controls, PCI DSS emphasizes the human element and organizational processes. It requires the maintenance of an information security policy that addresses all personnel and outlines procedures for handling security incidents. An incident response plan is mandatory, ensuring that organizations are prepared to react swiftly and effectively in the event of a breach, minimizing potential damage and recovery time. Regular security awareness training for all employees is also critical to foster a culture of security.
Achieving and Maintaining PCI DSS Compliance
Compliance with PCI DSS is an ongoing process, not a one-time event. It requires sustained effort, resources, and commitment from an organization. The compliance journey typically involves several key stages, each designed to ensure thoroughness and continuous adherence to the standard.
The Compliance Process
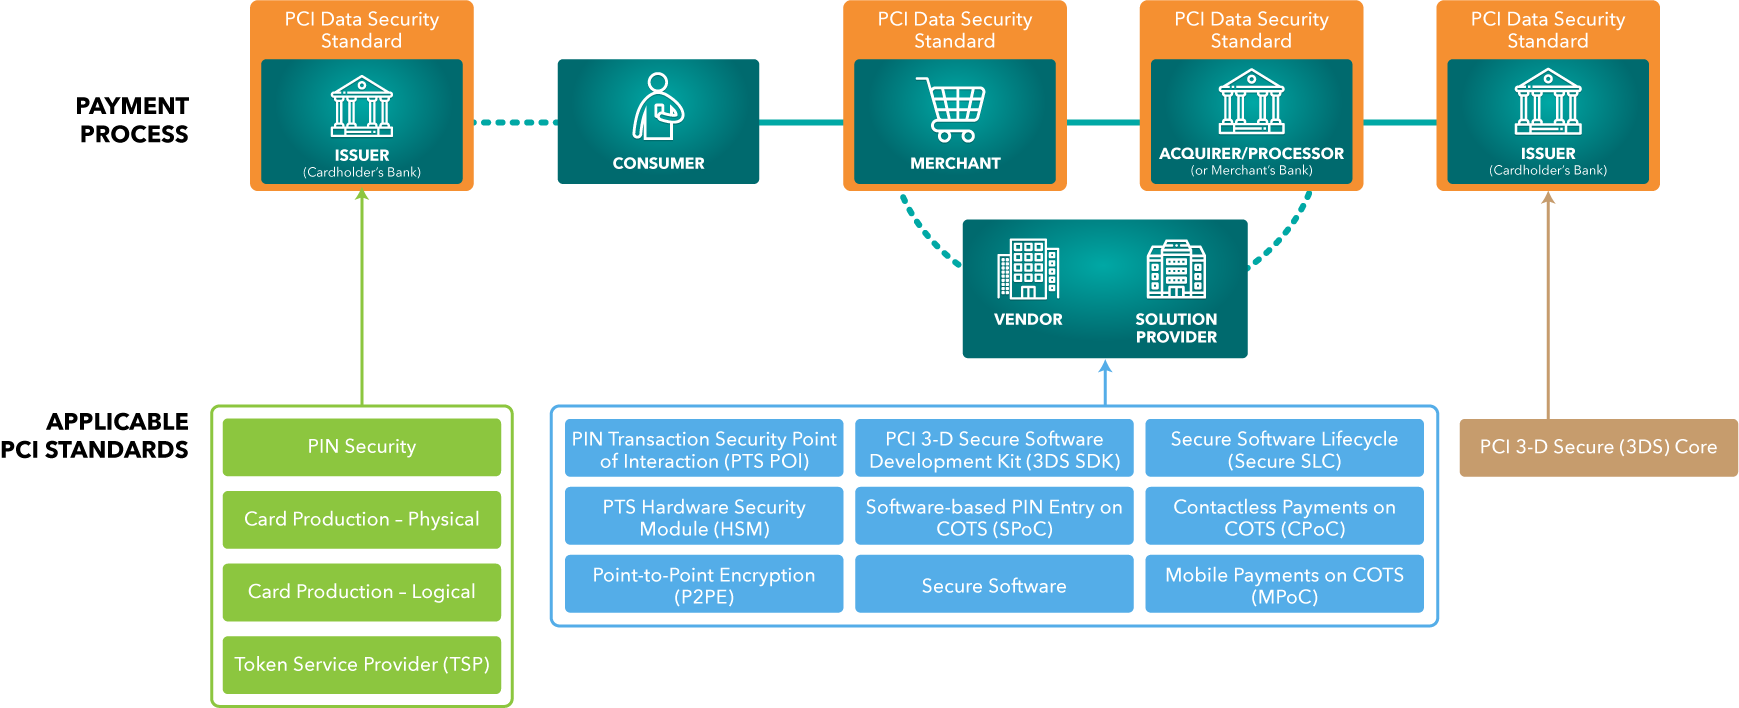
The first step is typically defining the scope of the Cardholder Data Environment (CDE), which includes all systems, processes, and people that store, process, or transmit cardholder data. Once scoped, organizations must conduct an annual self-assessment questionnaire (SAQ) or, for larger entities, a formal audit by a Qualified Security Assessor (QSA). SAQs vary in complexity depending on how an organization processes card payments. For example, an e-commerce merchant using a fully outsourced payment gateway might use a simpler SAQ than a large retailer processing payments directly. Additionally, vulnerability scans must be conducted by an Approved Scanning Vendor (ASV) quarterly to identify and address external vulnerabilities. The results of these assessments are then submitted to acquiring banks and payment brands.
Challenges in Attaining Compliance
Achieving PCI DSS compliance can be a significant undertaking, particularly for organizations with complex IT environments or legacy systems. Common challenges include accurately scoping the CDE, which can be difficult as cardholder data may flow through unexpected systems. Implementing strong encryption and data protection measures across diverse systems can also be technically challenging. Furthermore, ensuring that all third-party service providers (e.g., cloud providers, payment gateways) are also PCI DSS compliant adds another layer of complexity, as organizations are ultimately responsible for their entire payment chain. The ongoing nature of compliance, requiring continuous monitoring, training, and policy updates, also demands consistent resource allocation.
Continuous Compliance and Risk Management
True security is not achieved merely by passing an annual audit. Maintaining PCI DSS compliance requires a continuous commitment to security best practices and an active risk management strategy. This includes regular internal audits, ongoing employee training, continuous monitoring of security systems, and prompt patching of vulnerabilities. Organizations must establish a governance model that ensures security is embedded into their operational fabric, from new system development to daily business processes. This proactive approach helps organizations stay ahead of emerging threats and maintain a strong security posture year-round.
Benefits Beyond Compliance
While the primary driver for PCI DSS adoption is regulatory compliance and the avoidance of penalties, the benefits extend far beyond simply meeting a mandate. Adhering to this standard fundamentally improves an organization’s overall security posture, fostering trust and operational resilience.
Enhanced Trust and Brand Reputation
In an era where consumers are increasingly aware of data privacy and security risks, demonstrating a commitment to protecting their financial information is a powerful differentiator. PCI DSS compliance signals to customers, partners, and stakeholders that an organization takes security seriously, thereby enhancing trust and bolstering brand reputation. This can lead to increased customer loyalty and a competitive advantage in the marketplace. A single data breach can irreversibly damage a brand, making proactive security an invaluable asset.
Reduced Risk of Data Breaches and Penalties
The most direct benefit of PCI DSS compliance is the significant reduction in the likelihood and impact of data breaches. By implementing robust security controls and processes, organizations erect formidable defenses against cyberattacks. Should a breach still occur, the compliant measures in place can limit the scope of the compromise and facilitate a quicker recovery. Furthermore, avoiding non-compliance means evading hefty fines and penalties levied by payment brands and acquiring banks, which can range from thousands to hundreds of thousands of dollars per month, in addition to potential legal costs and compensatory damages.
Operational Efficiency and Security Best Practices
The requirements of PCI DSS often align with general information security best practices. By implementing the standard, organizations typically improve their overall IT infrastructure, streamline security processes, and develop more coherent data management policies. This can lead to increased operational efficiency, better resource allocation for security, and a clearer understanding of data flows within the organization. The discipline enforced by PCI DSS can transform security from an afterthought into an integral part of business operations.

The Future of PCI DSS in Evolving Tech Landscapes
As technology continues to evolve, so too must security standards. The Payment Card Industry Security Standards Council (PCI SSC) regularly updates the PCI DSS to address new threats and technological advancements, such as cloud computing, mobile payments, and new authentication methods. The standard is designed to be technology-neutral, focusing on security objectives rather than specific technologies, allowing it to adapt to future innovations.
The current version, PCI DSS v4.0, emphasizes a greater focus on customized approaches, encouraging organizations to implement security controls in a way that best fits their unique environment while still meeting the standard’s objectives. It also brings enhanced requirements for multi-factor authentication, risk assessments, and more prescriptive details for securing custom software. As payment methods diversify and the lines between physical and digital commerce blur, PCI DSS will continue to play a vital role in ensuring the secure transmission and storage of payment card data, acting as a dynamic and indispensable cornerstone of global payment security technology and innovation.