
The digital landscape is constantly evolving, with new technologies and security protocols emerging to safeguard our online interactions. Within the realm of messaging applications, security is paramount, and Google Messages, a widely adopted platform, utilizes various methods to ensure user privacy and data integrity. One such element, though not directly displayed to the end-user as a distinct feature, is the concept of One-Time Passwords (OTPs) and their role in securing communication and account verification, particularly when linked to Google’s broader ecosystem.
Understanding One-Time Passwords (OTPs)
A One-Time Password, or OTP, is a unique, randomly generated alphanumeric code that is valid for a single login session or transaction. Unlike traditional passwords, which are static and can be compromised through various means, OTPs offer a transient layer of security. Once used, an OTP is immediately invalidated, making it significantly harder for unauthorized individuals to gain access even if they intercept the code. This ephemeral nature is the core of their strength in multi-factor authentication (MFA) strategies.
The generation of OTPs typically involves sophisticated algorithms that ensure a high degree of randomness and unpredictability. These algorithms are often tied to time-based (TOTP) or event-based (HOTP) mechanisms. Time-based OTPs, for instance, regenerate at regular intervals (e.g., every 30 or 60 seconds), adding another layer of dynamism. Event-based OTPs, on the other hand, are generated based on a counter, ensuring that each code is unique for each event or transaction.
The Role of OTPs in Digital Security
OTPs are a cornerstone of modern multi-factor authentication, a security process that requires users to provide two or more verification factors to gain access to a resource. This approach significantly enhances security by ensuring that even if one factor (like a password) is compromised, an attacker still cannot gain access without the other required factors. Common forms of the second factor include something the user has (like a smartphone) or something the user is (like a fingerprint). OTPs, delivered via SMS, email, or authenticator apps, are a prime example of the “something you have” factor, as they are typically sent to a device the user possesses.
The widespread adoption of OTPs stems from their balance of robust security and user convenience. While they add an extra step to the login process, the ease of receiving and entering a short code is far less cumbersome than managing complex, unique passwords for every service. This makes them an ideal solution for securing sensitive operations such as online banking, e-commerce transactions, and, crucially, account verification and recovery for messaging platforms.
OTPs and Google Messages: A Seamless Integration
While Google Messages itself primarily focuses on facilitating SMS and RCS (Rich Communication Services) conversations, its integration with the broader Google ecosystem means that OTPs play a vital, albeit often invisible, role in its functionality and security. When you set up Google Messages, especially on a new device or after a reset, you might encounter scenarios where Google requires verification of your phone number. This is where OTPs come into play.
SMS-Based OTP Verification
The most common way OTPs interact with Google Messages is through SMS verification. When you install Google Messages or link your phone number to a Google account, Google might send an SMS containing a verification code to your device. This code is an OTP. You are then prompted to enter this code within the Google Messages app or the Google account setup interface to confirm that you are the legitimate owner of the phone number. This process is crucial for several reasons:
- Account Security: It ensures that only the rightful owner of the SIM card and phone number can activate and use the messaging service associated with that number. This prevents malicious actors from impersonating users or taking over their accounts.
- Service Provisioning: For advanced features like RCS messaging, which relies on a verified phone number to establish direct connections between devices, OTP verification is a fundamental step in the onboarding process.
- Device Linking: If you use Google Messages across multiple devices or link your account to other Google services, OTP verification through SMS helps confirm your identity and authorize these connections.
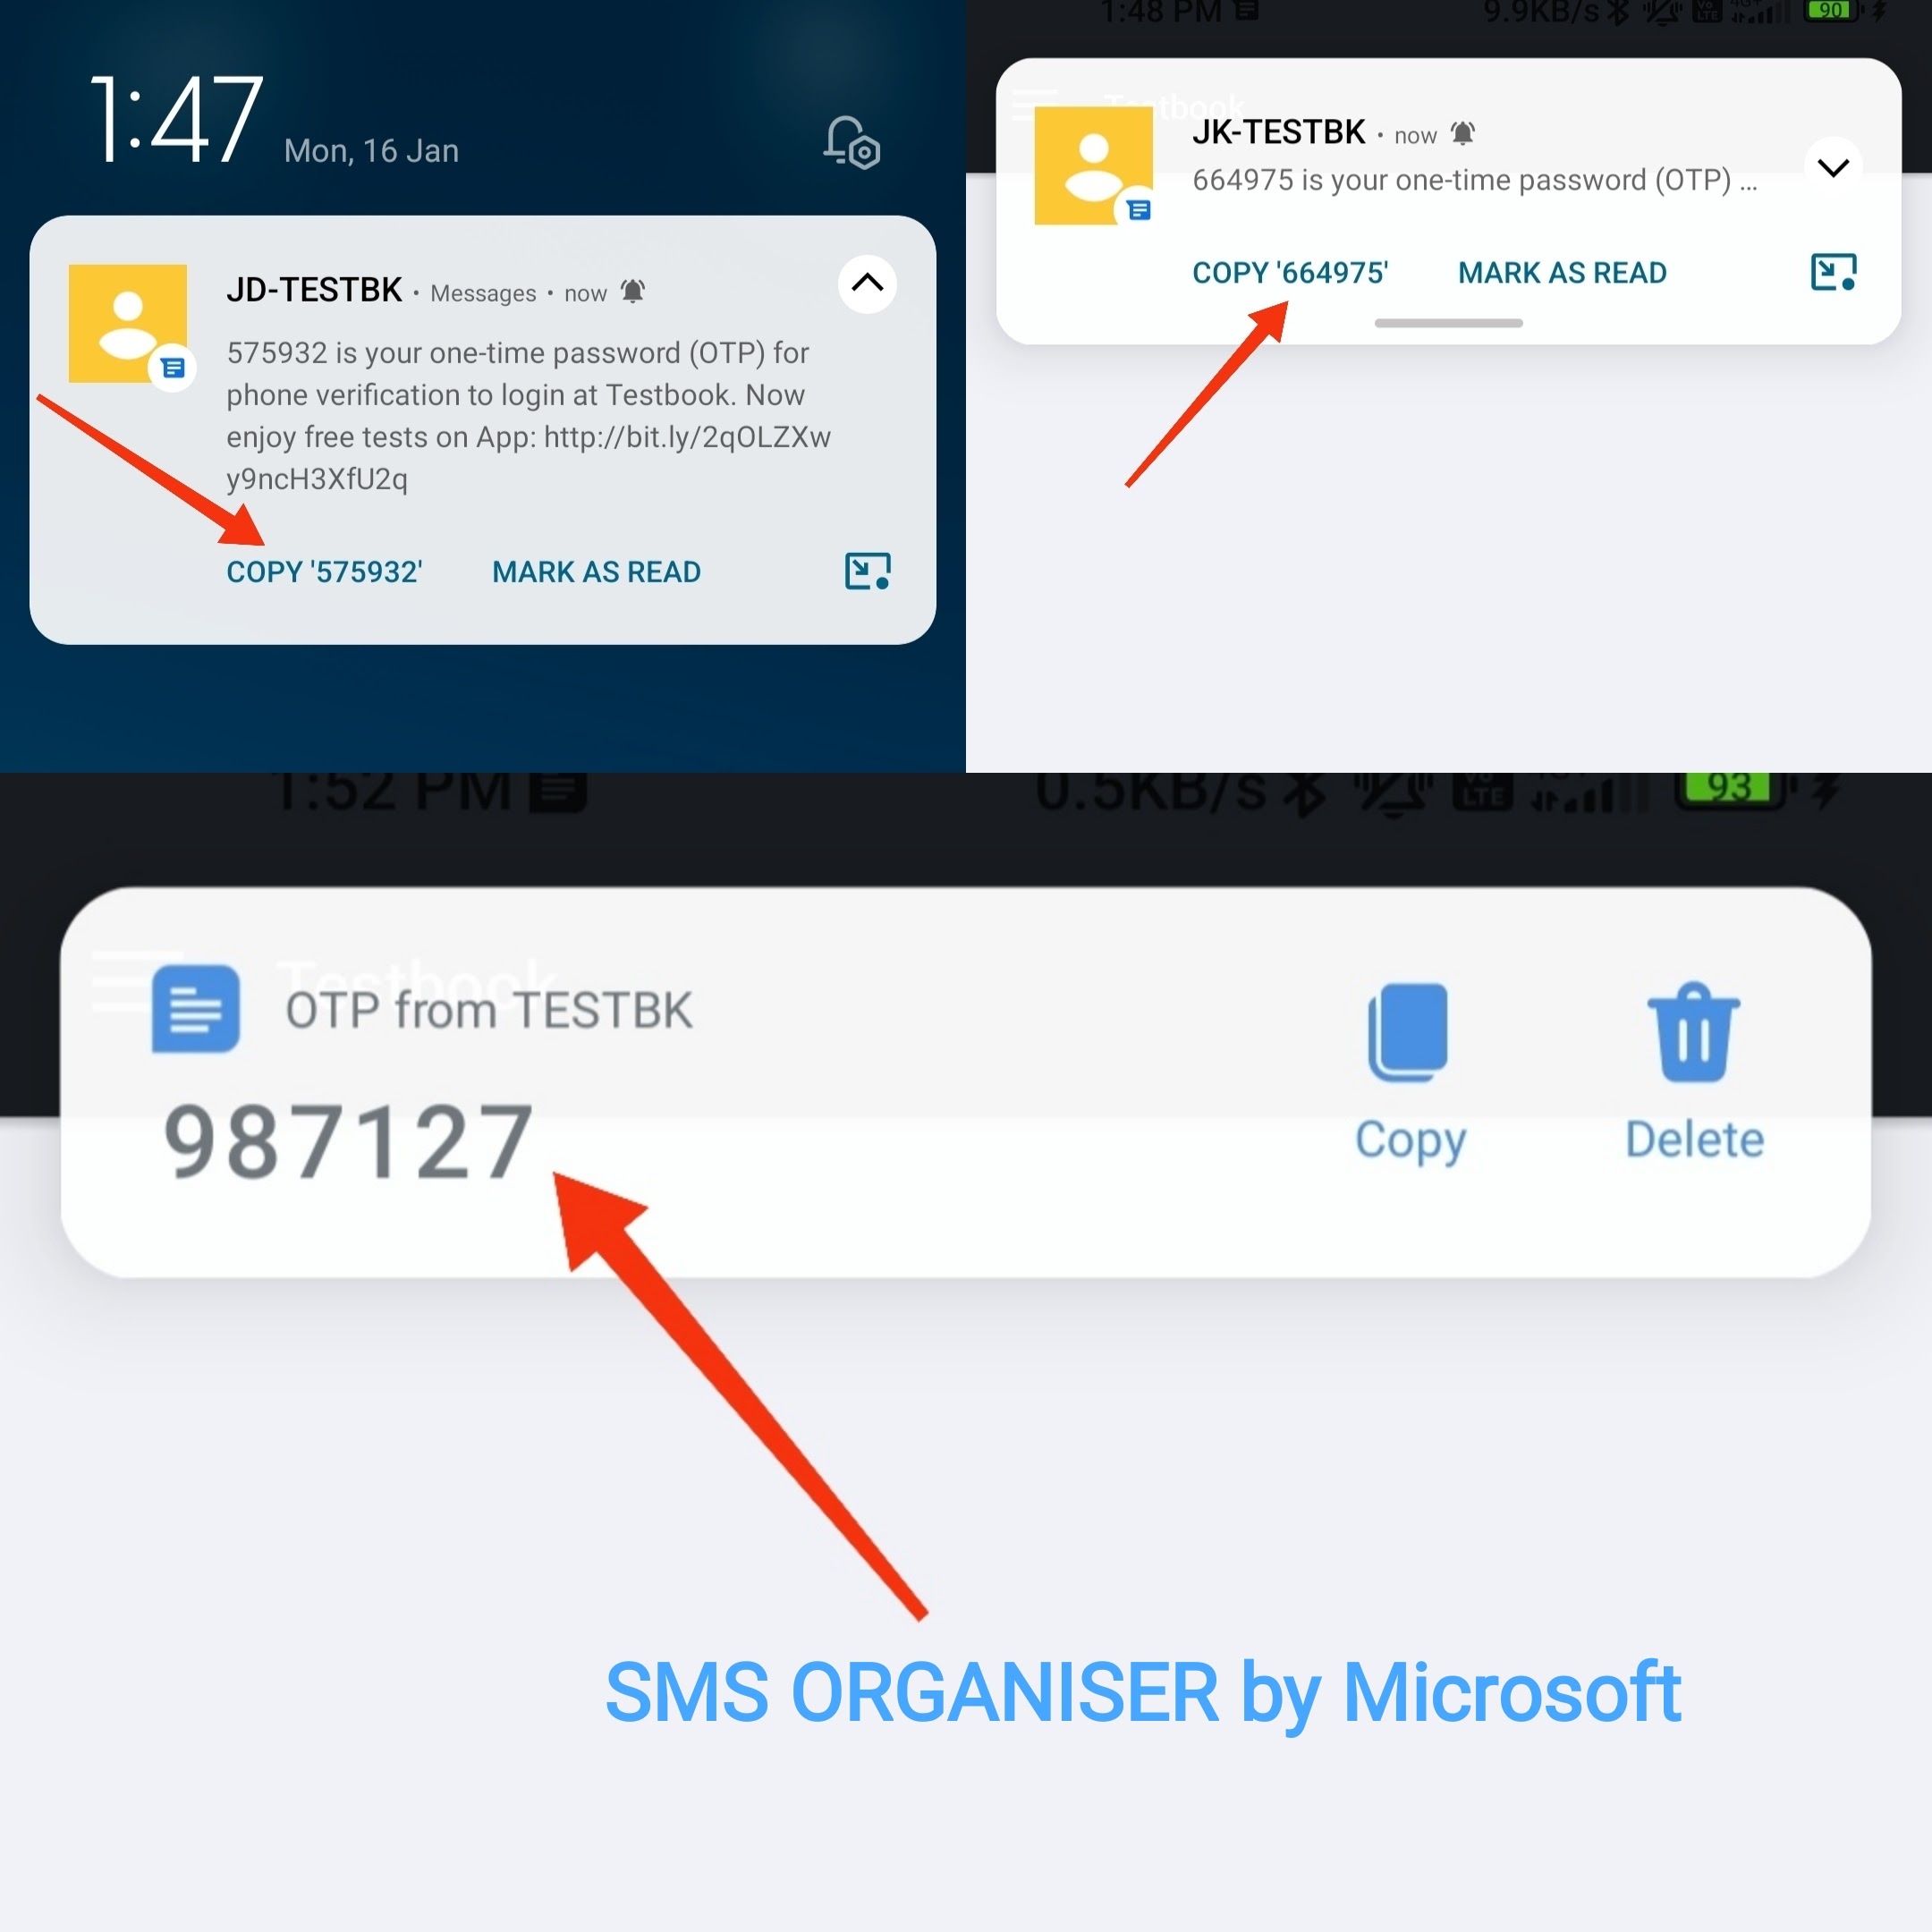
The beauty of this system is its seamlessness. The OTP arrives directly within the Google Messages inbox, and often, the app can automatically detect and pre-fill the code, making the verification process almost instantaneous for the user. This automation is a testament to the advanced capabilities of modern messaging platforms and their ability to integrate with system-level security functions.
The “Message to Self” and Auto-Verification
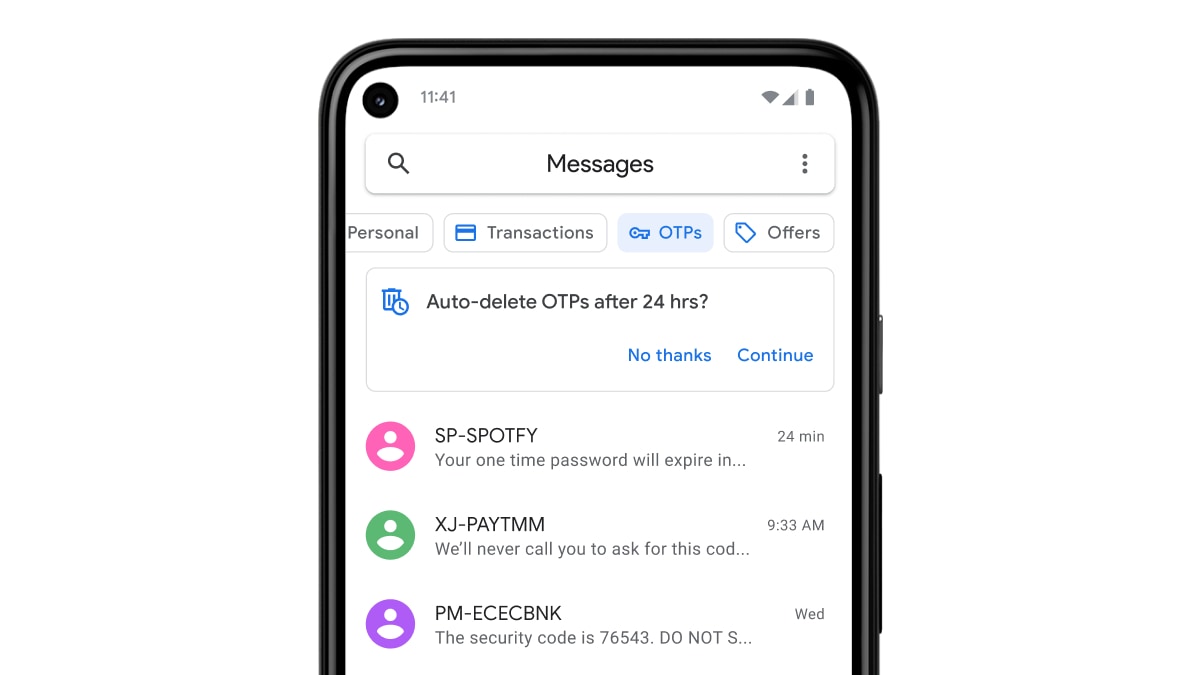
Google has further enhanced the OTP experience within Messages through features like “message to self” and automatic detection and verification. When a verification SMS arrives, Google Messages, with user permission, can often identify it as an OTP and automatically extract the code. In many cases, it will present this code directly in a notification, or even suggest pre-filling it into the relevant field. This reduces the manual effort required from the user, making the security process feel less intrusive and more integrated into the daily use of the app.

For instance, if you are setting up a new account on a platform that sends OTPs via SMS, and you are using Google Messages as your default SMS app, you might see a prompt within the verification screen of that platform offering to fill in the code directly from an incoming message in your Google Messages. This is powered by Google’s ability to analyze incoming SMS content for patterns indicative of OTPs.
Beyond SMS: OTPs in the Wider Google Ecosystem
While Google Messages is the primary conduit for SMS-based OTPs, it’s important to recognize that OTPs are a fundamental security mechanism across many Google services. When you log into your Google account from an unfamiliar device, or when performing sensitive actions like changing your password or payment information, Google often employs OTPs as part of its robust security protocols.
Google Account Security and Recovery
The security of your Google account is paramount, as it often serves as the gateway to a vast array of personal data and services, including Gmail, Google Drive, Google Photos, and, of course, Google Messages. When you try to log in from a new device or browser, or if Google detects unusual activity, you may be prompted to verify your identity. This verification often involves sending an OTP to your trusted phone number, which would then be delivered via SMS to your Google Messages app.
- Two-Factor Authentication (2FA): OTPs are a critical component of Google’s 2FA. After entering your password, you are asked to provide a code that is sent to your phone. This code is an OTP.
- Account Recovery: If you forget your password or lose access to your account, OTPs sent to your recovery phone number can be instrumental in regaining access. This ensures that only someone with access to your registered phone can initiate and complete the recovery process.
Security Keys and Other Advanced Methods
While SMS-based OTPs are common, Google also supports more advanced authentication methods that leverage similar principles of one-time codes. Security keys, for example, are physical devices that generate OTPs or use public-key cryptography to authenticate users without the need for sending codes over less secure channels like SMS. However, for the everyday user, SMS-delivered OTPs remain a primary and highly effective layer of security for many Google services, including those accessed and managed through Google Messages.
The Future of OTPs and Messaging Security
As technology advances, the methods of delivering and using OTPs will likely continue to evolve. While SMS remains a prevalent channel due to its universality, concerns about SMS interception and SIM-swapping attacks are driving interest in more secure alternatives.
Authenticator Apps and Secure Channels
Authenticator apps, like Google Authenticator or Authy, generate OTPs directly on your device, independent of SMS. These codes are time-based and offer a higher level of security as they are not transmitted over vulnerable networks. Google fully supports these apps for 2FA.
Furthermore, advancements in end-to-end encryption for messaging services could eventually lead to OTPs being delivered through more secure, encrypted channels within messaging apps themselves, rather than relying on SMS. However, for a platform like Google Messages that also handles standard SMS, the integration with SMS-based OTPs will remain a critical function for a long time.
Advanced Fraud Detection and Biometrics
The ability of apps like Google Messages to intelligently detect and process OTPs is a glimpse into the future. We can expect more sophisticated fraud detection mechanisms that use AI to analyze the context and content of messages, further strengthening security. Biometric authentication (fingerprint, facial recognition) is also increasingly being integrated into the authentication process, often complementing OTPs to provide an even more secure and user-friendly experience.
In conclusion, while the term “OTP” might not be a feature you actively interact with in Google Messages, it represents a vital, underlying security mechanism. From verifying your phone number for SMS and RCS services to safeguarding your Google account, OTPs play an indispensable role in ensuring the privacy and security of your digital communications and online identity. Their seamless integration within Google Messages, often in an automated fashion, highlights the continuous effort to balance robust security with user convenience in the ever-evolving digital landscape.