
In an era defined by rapid technological advancement, from autonomous flight and sophisticated remote sensing to pervasive AI and machine learning, the bedrock of security and privacy has never been more critical. Within this dynamic landscape, NIST Special Publication 800-53 emerges as a pivotal framework, not merely for compliance but as an essential blueprint for safeguarding the integrity, confidentiality, and availability of information systems. While traditionally associated with federal agencies, its principles and controls are increasingly vital for any organization operating at the cutting edge of tech and innovation, where data is king and systemic resilience is paramount.
A Foundational Framework for Information Security
NIST SP 800-53, formally titled “Security and Privacy Controls for Information Systems and Organizations,” is a comprehensive catalog developed by the National Institute of Standards and Technology (NIST). Its primary purpose is to provide a standardized set of controls that organizations can implement to protect their information systems and the data they process. More than just a checklist, it represents a flexible, risk-based approach to managing cybersecurity and privacy, applicable across diverse technological environments.
Evolution and Scope
Initially conceived to assist U.S. federal agencies in meeting the requirements of the Federal Information Security Modernization Act (FISMA), NIST SP 800-53 has evolved significantly since its first iteration. With each revision, particularly with Release 5 (R5), the scope has broadened to address the complexities of modern information systems, including critical infrastructure, cloud computing, mobile technologies, and the pervasive Internet of Things (IoT). Crucially, R5 explicitly integrated privacy controls, recognizing the intertwined nature of security and privacy in a data-driven world. Its adaptability makes it invaluable not just for government entities but for any private sector organization innovating with advanced technologies that demand robust protection.
Control Families and Baselines
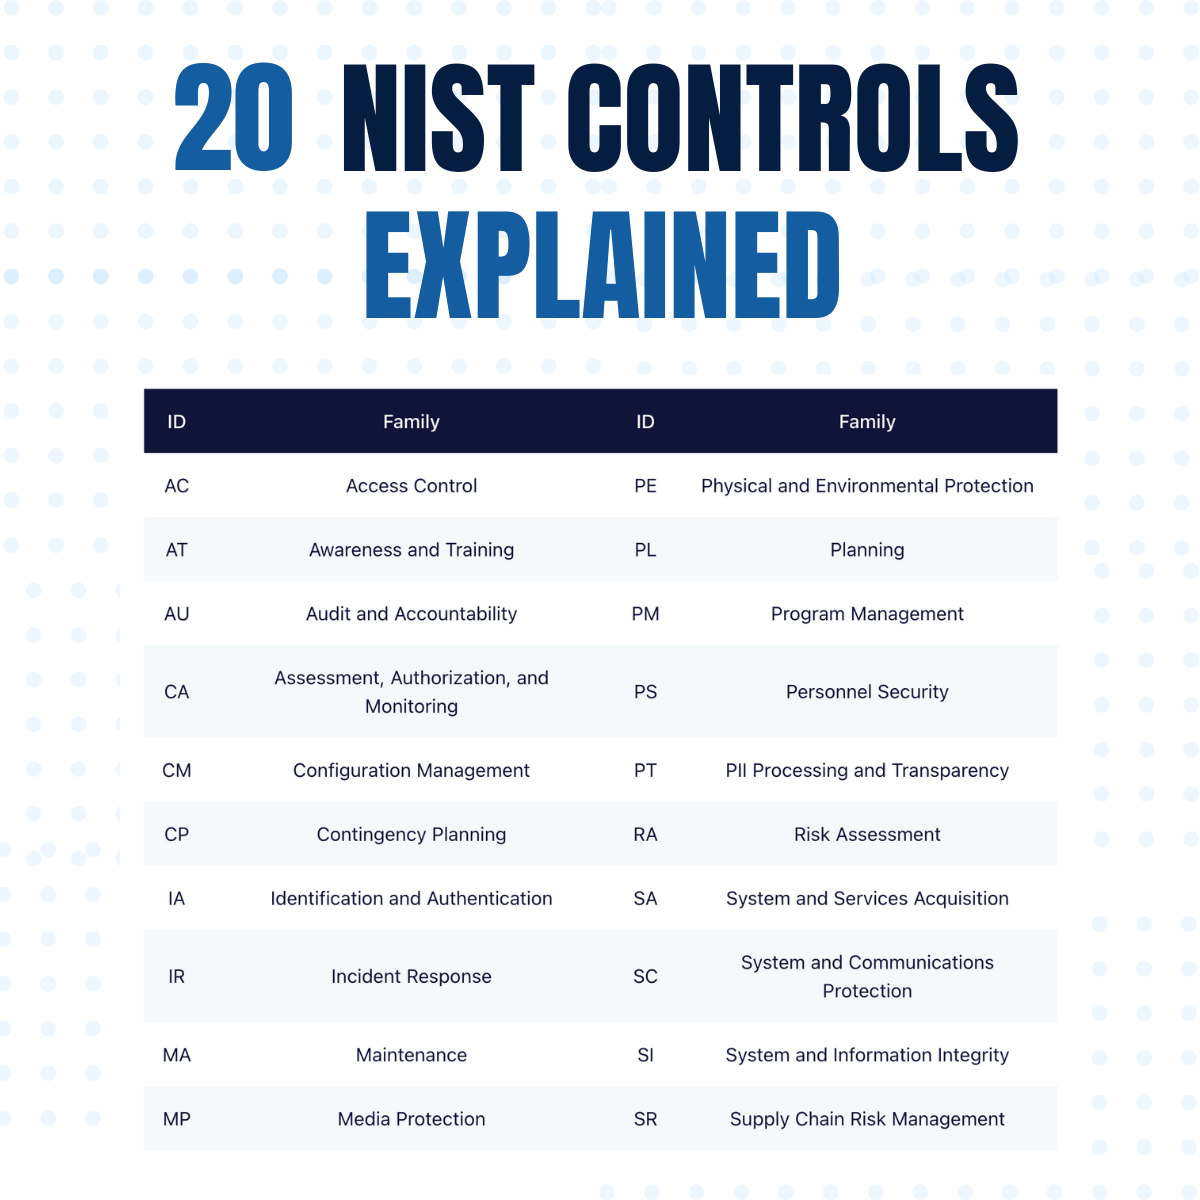
At its core, NIST SP 800-53 organizes security and privacy controls into distinct families. These families span a wide array of technical, operational, and management aspects, such as Access Control (AC), Audit and Accountability (AU), Configuration Management (CM), Incident Response (IR), System and Communications Protection (SC), and System and Information Integrity (SI), among many others. For each control, detailed specifications are provided to guide implementation.
To manage the complexity and tailor controls to specific organizational needs and system criticality, NIST provides “control baselines.” These baselines—low, moderate, and high—offer predefined sets of controls suitable for systems with varying levels of impact should a security breach occur. Organizations are encouraged to select an initial baseline and then “tailor” it, adding or subtracting controls based on a thorough risk assessment and the unique operational context of their innovative technologies. This adaptive approach ensures that security investments are proportionate to the risks faced, optimizing resource allocation while maintaining robust defenses.
Securing the Algorithms: NIST SP 800-53 in AI and Autonomous Systems
The rise of Artificial Intelligence (AI) and autonomous systems represents a quantum leap in technological capability, powering everything from AI follow modes in imaging systems to complex autonomous flight paths for remote sensing. However, the sophistication of these systems introduces novel security and privacy challenges that NIST SP 800-53 is uniquely positioned to address.
Protecting AI Models and Data Integrity
AI systems are fundamentally dependent on data – for training, validation, and real-time operation. The integrity and confidentiality of this data are paramount. NIST SP 800-53 provides controls that are directly applicable to securing the entire AI lifecycle. For instance, controls within the Access Control (AC) family ensure that only authorized personnel and processes can access sensitive training datasets, preventing data poisoning or unauthorized manipulation that could compromise an AI model’s accuracy or introduce biases. Configuration Management (CM) controls ensure that AI algorithms, their parameters, and underlying infrastructure are securely configured and version-controlled, mitigating risks from unapproved changes. Audit and Accountability (AU) controls mandate logging and monitoring of AI system activities, crucial for detecting anomalous behavior, identifying adversarial attacks (e.g., evasion or inference attacks), and ensuring model explainability. By applying these controls, innovators can build and deploy AI systems with greater confidence in their security and reliability.
Ensuring Reliability of Autonomous Operations
Autonomous systems, whether performing precision mapping or operating sophisticated robotic platforms, rely on a delicate interplay of sensors, processors, and actuators. A compromise in any part of this chain could lead to catastrophic failures, privacy breaches, or unauthorized actions. NIST SP 800-53’s focus on system and communication protection is vital here. Controls under System and Communications Protection (SC) are critical for securing the communication channels used by autonomous systems, protecting against jamming, spoofing, or data interception that could derail an operation or expose sensitive telemetry. System and Information Integrity (SI) controls help ensure that the software and firmware running autonomous platforms are free from malicious code and have not been tampered with. Incident Response (IR) controls are essential for defining how organizations detect, analyze, and mitigate security incidents affecting autonomous systems, minimizing downtime and potential harm. By embracing these controls, organizations can develop autonomous capabilities that are not only advanced but also inherently resilient and trustworthy.
Safeguarding Sensitive Data in Mapping and Remote Sensing Operations
Mapping, remote sensing, and other forms of advanced data acquisition generate vast quantities of geospatial and environmental data, often with high resolution and significant sensitivity. From critical infrastructure monitoring to environmental impact assessments, the integrity and privacy of this data are paramount. NIST SP 800-53 offers a robust framework for managing the security and privacy risks associated with these operations.
Data Collection, Processing, and Storage Security
The lifecycle of data in mapping and remote sensing applications begins at collection and extends through processing, analysis, and storage. Each stage presents unique security challenges. NIST SP 800-53’s controls for Media Protection (MP) dictate how raw and processed data should be protected, whether it resides on field devices, in temporary storage, or within long-term archives. Physical and Environmental Protection (PE) controls address the security of facilities housing data servers and processing equipment, guarding against unauthorized access, theft, or environmental damage. Additionally, controls under System and Information Integrity (SI) are crucial for ensuring the authenticity and non-repudiation of collected data, providing assurance that sensor readings and processed maps are accurate and untampered with. For instance, robust encryption (SC-13) and cryptographic key management are vital for protecting sensitive imagery or sensor data both in transit and at rest.
Privacy Considerations for Geospatial Data
High-resolution mapping and remote sensing can inadvertently capture personally identifiable information (PII) or reveal sensitive details about private property and activities. The privacy controls introduced in NIST SP 800-53 R5 are particularly relevant here. These controls guide organizations in assessing privacy risks, implementing privacy-enhancing technologies, and establishing clear policies for data use and retention. For example, controls related to “Consent” (PM-25) and “Data Minimization” (PM-27) prompt organizations to consider what data is truly necessary for their objectives and to seek explicit permission where appropriate. “Individual Access” (PM-29) and “Accountability for Privacy” (PM-30) ensure transparency and provide mechanisms for individuals to understand and control how their data is used, fostering public trust in the deployment of these powerful technologies.
NIST SP 800-53 as an Enabler of Secure Innovation
Far from being a bureaucratic hindrance, NIST SP 800-53 serves as a catalyst for secure innovation. By embedding security and privacy considerations early in the development lifecycle of new technologies, it helps organizations build resilience from the ground up, reducing technical debt and fostering trust in their products and services.
Supply Chain Risk Management for Advanced Tech
The globalized nature of tech innovation means that advanced systems are often built from components and software sourced from numerous suppliers. This complex supply chain introduces significant security risks, as a compromise in a single component could undermine the security of an entire system. NIST SP 800-53’s Supply Chain Risk Management (SR) controls are designed to address these vulnerabilities. These controls mandate due diligence in vendor selection, requiring assessments of supplier security practices, ensuring the integrity of purchased components, and managing the risk of counterfeit parts or malicious insertions. For organizations developing cutting-edge AI or autonomous flight systems, securing the supply chain—from microcontrollers to specialized sensors—is non-negotiable for ensuring the trustworthiness and operational safety of their innovations.
Fostering Trust in Emerging Technologies
The successful adoption of new technologies, especially those with significant societal impact like autonomous vehicles or widespread remote sensing, hinges on public trust. A critical component of this trust is the assurance that these technologies are secure, reliable, and respectful of privacy. By adhering to a recognized and rigorous framework like NIST SP 800-53, innovators can demonstrate a commitment to security and privacy best practices. This commitment translates into greater confidence from customers, regulators, and the public, accelerating market adoption and ensuring that the benefits of technological advancement can be realized responsibly and sustainably.
Implementing Controls in a Dynamic Tech Landscape
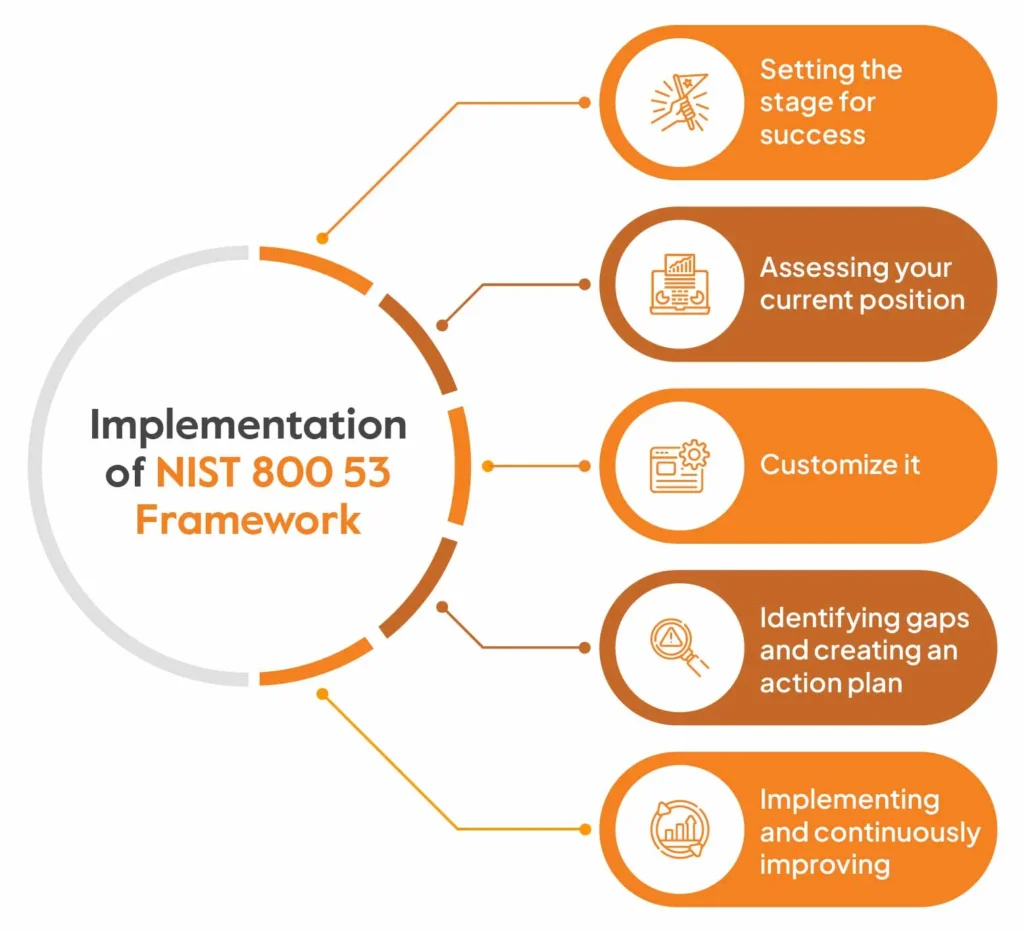
Implementing NIST SP 800-53 controls within rapidly evolving technology sectors requires a nuanced and adaptive approach. It’s not a static compliance exercise but an ongoing commitment to risk management and continuous improvement.
Tailoring and Continuous Monitoring
Given the unique characteristics of AI algorithms, complex sensor arrays, and sophisticated autonomous systems, the “one-size-fits-all” approach to security is ineffective. Organizations must meticulously “tailor” the NIST SP 800-53 control baselines, performing detailed risk assessments to identify specific threats and vulnerabilities pertinent to their innovations. This involves a deep understanding of the technology’s architecture, data flows, operational environment, and potential impact. Furthermore, security is not a destination but a journey. Continuous Monitoring (CA-7) controls are essential for ensuring that security and privacy postures remain effective over time, adapting to new threats, system changes, and evolving operational contexts. Automated tools, threat intelligence feeds, and regular audits are indispensable for maintaining vigilance in a dynamic threat landscape.
Addressing Future Security Challenges
As technology continues to advance, so too will the sophistication of cyber threats. NIST SP 800-53 provides a robust foundation, but innovators must also look beyond current controls to anticipate future challenges. This includes actively participating in security research, adopting emerging security paradigms (e.g., zero trust architectures), and contributing to the development of new standards specific to AI security, quantum-resistant cryptography, and the unique challenges of complex autonomous networks. By integrating the comprehensive approach of NIST SP 800-53 with forward-looking security strategies, organizations can not only protect their current innovations but also pave the way for a more secure and resilient technological future.