
The sprawling landscape of the Internet of Things (IoT) is characterized by interconnected devices, ranging from smart home gadgets and wearable tech to industrial sensors and autonomous vehicles. While the primary user interfaces for these devices are often streamlined for simplicity, a deeper, more intricate layer of functionality frequently exists, colloquially known as the “IoT hidden menu.” This concept extends beyond a simple settings page; it refers to a suite of advanced configurations, diagnostic tools, and developer options deliberately concealed from the average user, offering unparalleled control and insight into a device’s operation. Within the realm of Tech & Innovation, understanding these hidden menus is crucial for engineers, developers, and power users seeking to maximize performance, diagnose complex issues, or unlock latent capabilities in their IoT ecosystems.

The Concept of a Hidden Menu in IoT
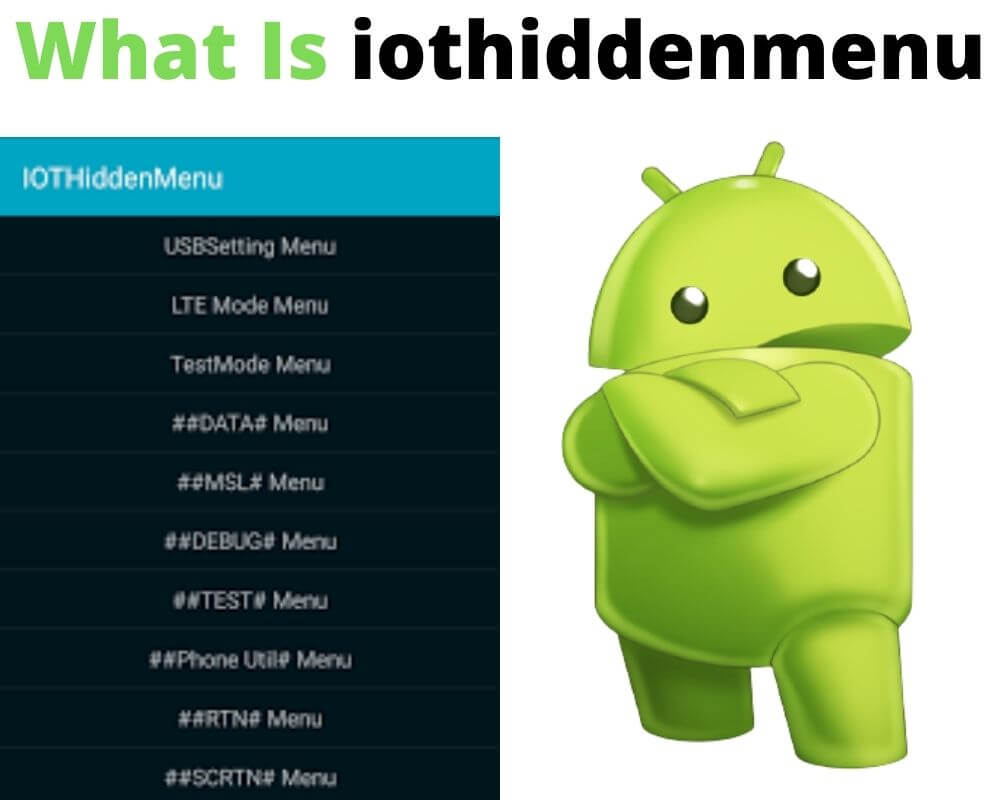
At its core, an IoT hidden menu represents a secondary, often non-intuitive interface designed for specialized access. Unlike the readily available settings, which allow users to connect to Wi-Fi, change display brightness, or set basic preferences, a hidden menu delves into the device’s operational parameters, firmware, and underlying system architecture. These menus are not typically advertised or easily discoverable, requiring specific button sequences, network commands, or specialized software tools to access.
Purpose and Functionality
The existence of hidden menus in IoT devices is driven by several critical objectives. Firstly, they serve as a vital resource for manufacturing and quality control, allowing technicians to calibrate sensors, perform factory resets, and conduct rigorous testing before a product ships. This ensures devices meet stringent performance standards and function reliably in diverse environments, from smart agricultural sensors monitoring soil conditions to environmental monitors in urban infrastructure.
Secondly, hidden menus are indispensable for troubleshooting and diagnostics. When a complex IoT system malfunctions—be it a smart thermostat failing to regulate temperature accurately or an industrial sensor providing erroneous data—support personnel or system administrators can access these menus to retrieve detailed log files, run system checks, and pinpoint the root cause of the problem. This capability significantly reduces downtime and maintenance costs, especially in large-scale industrial IoT (IIoT) deployments where system reliability is paramount.
Finally, these menus often provide advanced configuration options that are deemed too complex or potentially risky for the average consumer. These might include fine-tuning network protocols, adjusting power management profiles for extended battery life in remote sensors, or enabling experimental features not yet fully validated for public release. For developers and integrators, these options are essential for customizing devices to meet specific project requirements, pushing the boundaries of what off-the-shelf IoT hardware can achieve.
Analogy to Traditional Systems
The concept of a hidden menu is not unique to IoT. Personal computers have long featured BIOS/UEFI settings that allow granular control over hardware, while smartphones often have “developer options” or “engineering modes” for advanced debugging and system modification. Gaming consoles have “service menus,” and even traditional appliances like televisions and washing machines may have diagnostic modes.
In the context of IoT, this analogy extends to a distributed network of “mini-computers,” each with its own set of internal operations. Just as a PC’s BIOS is critical for hardware initialization, an IoT device’s hidden menu manages its interaction with its environment and other connected systems. The complexity of IoT, with its diverse array of sensors, actuators, communication protocols, and edge computing capabilities, necessitates these deeper access points to maintain stability, security, and adaptability. Without them, the intricate web of smart devices powering everything from smart cities to precision agriculture would be far more challenging to manage and optimize.
Accessing the Unseen: Methods and Challenges
Gaining entry to an IoT hidden menu is typically not a straightforward process, reflecting its intended purpose as an exclusive interface for advanced users. The methods for access vary significantly depending on the device, manufacturer, and the specific functionality being protected. Understanding these access vectors is key to navigating the deeper layers of IoT technology.
Common Access Vectors
One of the most common methods involves physical interaction with the device. This could be a specific sequence of button presses (e.g., holding a power button while pressing a volume button on a smart speaker, or a specific combination on a smart display). For industrial IoT devices, this might involve interacting with a physical port (like a serial port) or a series of physical switches in a protected enclosure. These physical methods are often used in production environments or for on-site diagnostics.
Network-based access is another prevalent method, especially for devices with robust connectivity. This often involves connecting to the device’s local network, navigating to a specific IP address or hostname, and then entering a hidden URL path or specific commands. Sometimes, special software or scripts are required to send particular packets or requests that trigger the hidden interface. This is common for smart routers, network cameras, or home automation hubs, where administrative access is typically handled over a web interface or a dedicated application. Advanced network scanning tools can sometimes reveal these hidden endpoints, provided they are not adequately secured.
For more sophisticated IoT devices, particularly those with embedded operating systems, firmware-level access might be necessary. This could involve using JTAG (Joint Test Action Group) debuggers, UART (Universal Asynchronous Receiver-Transmitter) interfaces, or even disassembling the device to access internal test points. These methods are typically reserved for deep-level development, security research, or severe recovery scenarios where the device’s primary operating system is compromised or unresponsive.
Finally, manufacturer-specific tools or apps sometimes exist, providing a gated entry point. These proprietary tools, often distributed to authorized service technicians or developers, abstract the underlying complexity, offering a more user-friendly interface for accessing hidden functionalities. These tools might require specific authentication credentials, hardware dongles, or network authorizations to function.
Security Implications and Risks
While access to hidden menus offers immense utility, it simultaneously presents significant security implications and risks. By their very nature, these interfaces bypass standard user controls and authentication mechanisms, making them potential targets for malicious actors.
Unauthorized access is a primary concern. If a hidden menu’s access method is discovered or its default credentials are not changed (a common vulnerability in many IoT devices), attackers could gain control over critical device functions. This could range from disabling security features and injecting malicious firmware to extracting sensitive data or weaponizing the device for denial-of-service attacks. Imagine an attacker gaining hidden menu access to a smart lock, enabling them to bypass its normal authentication and unlock it at will, or to an industrial sensor, allowing them to manipulate data critical for operational decisions.
Furthermore, misconfiguration through a hidden menu can lead to device instability, degraded performance, or even “bricking” the device, rendering it inoperable. Since these menus expose fundamental system settings, incorrect adjustments can have cascading negative effects that are difficult to undo without specialized knowledge or tools. This risk is compounded by the fact that documentation for hidden menus is often sparse or non-existent for the general public.
Manufacturers walk a tightrope, balancing the need for deep access during development and support with the imperative to secure devices in the field. The evolution of IoT security protocols, including secure boot, encrypted firmware updates, and robust authentication mechanisms for administrative interfaces, is partly driven by the challenge of managing these powerful, yet vulnerable, hidden gateways.
Unlocking Advanced Capabilities and Configuration
The primary allure of an IoT hidden menu for power users and professionals within the Tech & Innovation sphere lies in its ability to unlock advanced capabilities and provide granular configuration options that are otherwise inaccessible. This deep-level control empowers users to transcend the limitations of consumer-facing interfaces and tailor devices to highly specific applications or optimize their performance beyond factory defaults.
Enhanced Performance and Customization
For many IoT devices, especially those designed for a broad consumer market, default settings prioritize ease of use and general compatibility. A hidden menu often allows for the fine-tuning of parameters that can significantly enhance performance or customize functionality. For instance, in a smart camera, a hidden menu might allow adjustment of advanced image processing algorithms, sensor gain settings, or specific parameters for AI object recognition beyond simple “person detection.” This could enable specialized use cases like tracking specific wildlife species or monitoring subtle changes in manufacturing lines.
Similarly, power management is a critical aspect of many battery-operated IoT devices, such as remote sensors or wearable trackers. A hidden menu might offer different power profiles, allowing users to sacrifice certain features (e.g., lower sampling rates for sensors, less frequent data uploads) for significantly extended battery life, or conversely, boost performance for critical, short-term tasks. For industrial IoT applications, this level of customization can mean the difference between days and months of operational uptime in remote locations, directly impacting efficiency and cost-effectiveness.
Furthermore, hidden menus can enable specific network configurations, such as custom VPN settings, advanced routing protocols, or specific data encryption standards, which are essential for integrating devices into complex enterprise networks or complying with stringent security regulations. This bespoke configuration capability is a cornerstone of innovation, allowing IoT devices to adapt to evolving technological landscapes and unique operational demands.
Debugging and Diagnostics
One of the most critical roles of an IoT hidden menu is to facilitate comprehensive debugging and diagnostics. When an IoT device malfunctions or behaves unexpectedly, the basic user interface offers little insight into the underlying cause. Hidden menus, however, expose a wealth of diagnostic data and tools.
Engineers can access detailed system logs that record every operation, error, and communication event, providing a forensic trail to pinpoint anomalies. This might include sensor readings over time, CPU and memory utilization, network packet captures, and firmware crash reports. For devices embedded in critical infrastructure or autonomous systems, these logs are invaluable for root cause analysis, helping to prevent future failures and improve system resilience.
Beyond log analysis, hidden menus often provide self-test functions, allowing engineers to individually test hardware components like sensors, radios, and actuators. They can force specific operational states, simulate environmental conditions, or bypass certain system checks to isolate a faulty component or software bug. This capability is particularly vital for intricate systems where component interaction is complex, such as in drone flight controllers or sophisticated medical IoT devices, where precise operation is paramount. The ability to perform real-time monitoring of internal states through these menus can drastically reduce the time and effort required to resolve complex technical issues, fostering continuous improvement in IoT product development.
Developer and Testing Environments
For developers, researchers, and security analysts, hidden menus can unlock a full developer or testing environment within the device itself. This might include access to a command-line interface (CLI), allowing direct interaction with the underlying operating system (e.g., Linux embedded on a smart hub). Developers can install custom applications, modify system files, or experiment with new functionalities without needing to flash entirely new firmware versions.
These environments are crucial for rapid prototyping and iterative development, enabling engineers to test new algorithms for AI features (like enhanced AI follow modes for cameras or improved autonomous navigation logic), evaluate new sensor integration, or experiment with novel communication protocols directly on the hardware. For security researchers, these deeper access points are invaluable for vulnerability assessment, allowing them to probe the device’s defenses and identify potential weaknesses before they can be exploited in the wild. The sandbox environment provided by some hidden menus allows for controlled experimentation, accelerating innovation while mitigating the risk of system-wide failures during development cycles.
Ethical Considerations and Responsible Use
The power conferred by IoT hidden menus comes with significant ethical responsibilities and necessitates a robust understanding of responsible use. As these interfaces often bypass standard safeguards, their improper handling can lead to severe consequences, affecting device integrity, user privacy, and overall system security.
Warranty and Support Ramifications
One of the most immediate consequences of accessing and modifying settings via a hidden menu is the potential to void manufacturer warranties. Most IoT device warranties explicitly state that unauthorized modifications or attempts to access internal systems will invalidate support agreements. This is because manufacturers cannot guarantee the device’s performance or safety once its intended operational parameters have been altered. Users who encounter issues after dabbling in hidden menus may find themselves without recourse for repairs or replacements, incurring unexpected costs.
Furthermore, official customer support channels are typically not equipped to assist with issues arising from hidden menu modifications. Support agents are trained to troubleshoot common problems within the device’s standard operating parameters. When configurations are changed outside these parameters, diagnosing problems becomes significantly more complex, and support teams may simply advise a factory reset (if accessible) or declare the device unsupported. This creates a dilemma for users who wish to unlock advanced features but risk losing essential support infrastructure.
Potential for Misuse and Security Vulnerabilities
The inherent power of hidden menus makes them prime targets for misuse, both intentional and unintentional. From an ethical standpoint, unauthorized access and manipulation pose significant risks. If a hidden menu’s access method is compromised or default credentials are left unchanged, malicious actors could exploit it to gain deep control over an IoT device. This could lead to a range of security breaches:
- Data Theft: Accessing sensitive user data, such as personal information from a smart health device or financial data from a smart payment terminal.
- Device Hijacking: Taking over the device’s functionality, turning a smart camera into a surveillance tool for unauthorized viewing, or repurposing an industrial sensor to report false data, potentially disrupting critical operations.
- Botnet Inclusion: Enrolling the compromised device into a botnet, where it contributes computing resources to malicious activities like distributed denial-of-service (DDoS) attacks, without the owner’s knowledge.
- Systemic Compromise: In complex IoT ecosystems (e.g., smart city infrastructure or connected vehicle fleets), compromising one device via its hidden menu could provide a stepping stone for attackers to infiltrate broader networks and critical systems.
From an innovation perspective, the existence of easily exploitable hidden menus creates a paradoxical challenge. While they enable advanced development and customization, their vulnerabilities can undermine the very trust and security necessary for widespread IoT adoption. Ethical manufacturers strive to secure these interfaces with robust authentication, encryption, and audit trails, ensuring that while the functionality exists, access is strictly controlled and monitored.
The Evolving Landscape of IoT Security
The dynamic nature of IoT means that the security landscape surrounding hidden menus is constantly evolving. As devices become more sophisticated and interconnected, the methods for securing these deeper interfaces must also advance. Manufacturers are increasingly implementing features such as secure boot mechanisms (preventing unauthorized firmware modifications), hardware-backed security modules (for secure credential storage), and remote attestation (verifying device integrity before allowing network access).
The ethical imperative for responsible disclosure of vulnerabilities discovered in hidden menus is also growing. Security researchers who uncover flaws typically follow a protocol of privately notifying manufacturers to allow for patches before publicly disclosing the vulnerability. This collaborative approach between researchers and industry is crucial for strengthening the overall security posture of the IoT ecosystem. Ultimately, the responsible use of IoT hidden menus involves a balance between leveraging their powerful capabilities for innovation and maintaining a steadfast commitment to security, privacy, and ethical operation.
The Future of IoT Interfaces and Configuration
As the Internet of Things continues its rapid expansion, transforming industries from healthcare to smart manufacturing and redefining daily life, the concept of the hidden menu is also evolving. The increasing complexity, diversity, and sheer volume of IoT devices necessitate new approaches to configuration, diagnostics, and advanced feature access. The future promises a blend of enhanced security, user-centric design, and intelligent automation in how we interact with the deepest layers of IoT technology.
One significant trend points towards standardization and unified management platforms. Currently, accessing hidden menus often requires device-specific knowledge and tools, leading to fragmentation and inefficiency. Future IoT ecosystems will likely see a move towards standardized protocols and APIs that allow authorized administrators to manage and configure diverse devices from a centralized platform. This would abstract away much of the device-specific ‘hidden’ nature, replacing it with a more structured and secure enterprise-level control panel. This approach would be particularly beneficial for large-scale industrial IoT (IIoT) deployments, where thousands of sensors and actuators need consistent configuration and monitoring.
AI and Machine Learning will play an increasingly pivotal role in automating the functions traditionally managed through hidden menus. Instead of manually adjusting power profiles or sensor calibration settings, AI algorithms could dynamically optimize these parameters based on real-time operational data, environmental conditions, and predefined performance goals. For instance, a smart camera could automatically adjust its image processing for optimal results under varying light conditions, or a fleet of delivery drones could autonomously fine-tune their navigation parameters based on weather forecasts and traffic patterns, all without explicit human intervention in a ‘hidden menu’. This shift from manual configuration to intelligent, adaptive systems embodies the pinnacle of innovation.
Furthermore, enhanced security measures will become paramount. As IoT devices become more ubiquitous and their roles more critical, the vulnerabilities associated with hidden access points will be addressed with greater rigor. Expect to see widespread adoption of hardware-backed root of trust, secure elements for cryptographic operations, and robust multi-factor authentication for any level of administrative access. The concept of a ‘hidden’ menu might transform into a ‘privileged’ access interface, requiring stringent identity verification and audit trails for every interaction, minimizing the risk of unauthorized access or misuse.
Finally, the boundary between what is ‘hidden’ and what is ‘accessible’ might blur for advanced users. As technology literacy grows, manufacturers might offer tiered access levels, allowing power users to unlock certain advanced features through a more transparent, yet still protected, interface, without exposing the most sensitive system-level configurations. This would democratize some of the customization and diagnostic power, fostering a new wave of user-driven innovation and personalization in the IoT space. The future of IoT hidden menus lies in transforming these elusive interfaces into secure, intelligent, and more integrated components of a sophisticated, self-optimizing technological landscape.