
Understanding the Domain Name System (DNS)
At the heart of how we navigate the internet lies a critical, yet often unseen, piece of technology: the Domain Name System, or DNS. Often referred to as the internet’s phonebook, DNS is a hierarchical and decentralized naming system for computers, services, or any resource connected to the internet or a private network. Its primary function is to translate human-readable domain names, such as “www.google.com,” into machine-readable IP addresses, like “172.217.160.142.” Without DNS, users would need to remember complex numerical IP addresses for every website they wished to visit, an impractical task that would render the internet far less accessible and user-friendly.
The Internet’s Phonebook
The analogy of a phonebook is particularly apt for explaining DNS. When you type a website address into your browser, your computer doesn’t instantly know where that website’s server is located. Instead, it sends a query to a DNS resolver, which then looks up the corresponding IP address. This process involves a series of steps, starting with a recursive resolver (often provided by your Internet Service Provider or a public DNS service like Google’s), which then queries root servers, Top-Level Domain (TLD) name servers (e.g., for .com, .org), and finally authoritative name servers for the specific domain. Each step directs the query closer to the definitive answer, ensuring that the correct IP address is found and returned to your browser, allowing it to establish a connection with the website’s server. This entire intricate process typically occurs in milliseconds, rendering it imperceptible to the average user.
Introducing Google Public DNS: An Innovation in Internet Access
While every internet user relies on DNS daily, many implicitly use the DNS servers provided by their Internet Service Provider (ISP). However, Google, a pioneer in internet infrastructure and services, introduced an alternative in 2009: Google Public DNS. This free, global Domain Name System (DNS) resolution service offers an alternative to ISP-provided DNS resolvers, aiming to make the internet faster, safer, and more reliable for users worldwide. Google Public DNS represents a significant technological offering, leveraging Google’s vast global infrastructure and expertise in network management to enhance a fundamental internet service.
The 8.8.8.8 and 8.8.4.4 Revolution
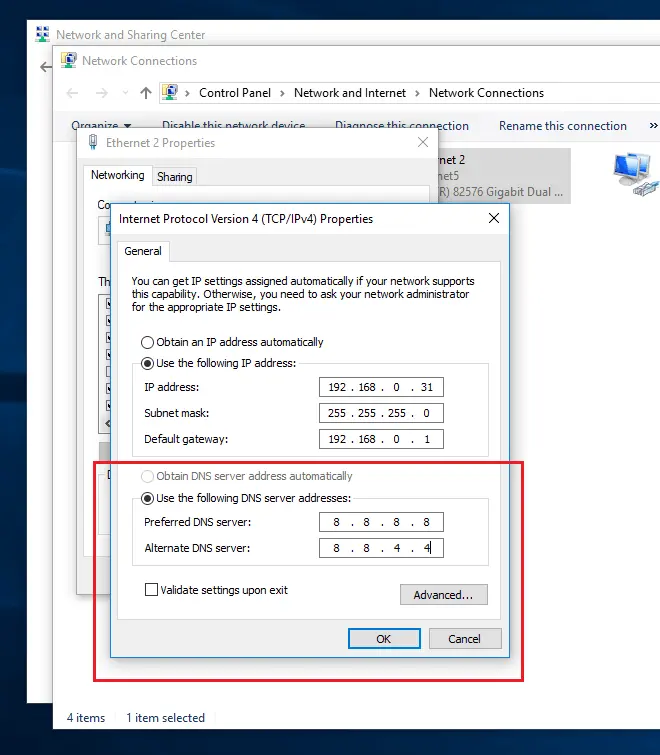
The core of Google Public DNS is its easily memorable IP addresses: 8.8.8.8 and 8.8.4.4 for IPv4, and 2001:4860:4860::8888 and 2001:4860:4860::8844 for IPv6. These addresses represent Google’s open recursive DNS resolvers. By configuring their devices or routers to use these specific IP addresses instead of their ISP’s default settings, users can direct all their DNS queries through Google’s network. This seemingly simple change can have profound implications for a user’s internet experience, impacting everything from website loading times to protection against certain types of online threats. Google’s commitment to providing a robust and accessible public DNS service underscores its broader mission to improve the fundamental underpinnings of the internet.
How Google’s Resolver Works
When a user’s device is configured to use Google Public DNS, all DNS queries are sent directly to Google’s globally distributed network of DNS servers. These servers employ advanced caching mechanisms and intelligent routing to quickly resolve domain names. Unlike many ISP DNS servers, Google’s infrastructure is designed for massive scale and resilience, utilizing anycast routing to direct queries to the nearest available Google DNS server. This geographical proximity, combined with highly optimized query processing, helps minimize latency and accelerate the resolution process. Furthermore, Google’s resolvers are constantly updated with the latest domain information and are engineered to resist various forms of DNS-based attacks, providing an added layer of security and stability that might not be present in every default ISP DNS offering.
The Core Advantages of Utilizing Google’s DNS
Adopting Google Public DNS goes beyond merely switching server addresses; it’s about leveraging a sophisticated technological infrastructure designed to provide tangible benefits for internet users. The primary motivations for users to opt for Google’s service often revolve around improvements in speed, security, reliability, and privacy.
Speed and Performance Optimization
One of the most immediate and perceptible benefits of using Google Public DNS is the potential for improved internet speed, particularly in terms of website loading times. Google’s DNS servers are strategically located in data centers around the world, and their network is highly optimized for performance. When a DNS query is sent to 8.8.8.8, it’s routed to the nearest Google data center that can respond, minimizing latency. Moreover, Google’s servers maintain vast, continuously updated caches of domain name information. This means that frequently requested domain names are often resolved directly from the cache, bypassing the multi-step lookup process and delivering the IP address to the user’s device significantly faster. While DNS resolution is only one factor in overall internet speed, an efficient resolver can noticeably reduce the initial delay in connecting to web resources, contributing to a snappier browsing experience.
Enhanced Security and Reliability
Beyond speed, Google Public DNS offers substantial advantages in terms of security and reliability. Google’s servers are designed with robust defenses against various DNS-related threats, such as DNS cache poisoning and denial-of-service (DoS) attacks. They implement DNSSEC (DNS Security Extensions) validation, which helps prevent forged DNS data from being served, thereby protecting users from being redirected to malicious websites. For instance, if an attacker attempts to hijack a domain by altering its DNS records, DNSSEC validation would detect this tampering and reject the fraudulent information, ensuring that users connect to the legitimate site. Furthermore, Google’s global network infrastructure boasts exceptional redundancy and fault tolerance. In the event of an outage at one server location, queries are automatically rerouted to another operational server, ensuring continuous and uninterrupted DNS resolution, a level of reliability that smaller ISP-based systems might struggle to match.
Privacy Considerations
Privacy is an increasingly critical concern for internet users, and Google Public DNS addresses this with a clearly defined privacy policy. Google states that it does not log personally identifiable information (PII) from DNS queries. While it does temporarily log full IP addresses for a very short period (typically 24-48 hours) for debugging and security purposes, these logs are anonymized or deleted after this timeframe. Longer-term, non-personally identifiable aggregate data (such as ISP and geographic location information, but not your full IP address) is retained for performance analysis and service improvement. This approach offers a different privacy posture compared to many ISP DNS servers, which might log user activity in more detail for various business or regulatory reasons. For users prioritizing a degree of separation between their browsing habits and their ISP’s data collection, Google Public DNS presents a compelling option.
Integrating Google Public DNS into Your Network
Adopting Google Public DNS is a straightforward process that can be implemented at various levels, from individual devices to an entire home or office network. The configuration changes are generally simple, requiring access to network settings on your computer, router, or other internet-connected devices.
Simple Configuration for Devices
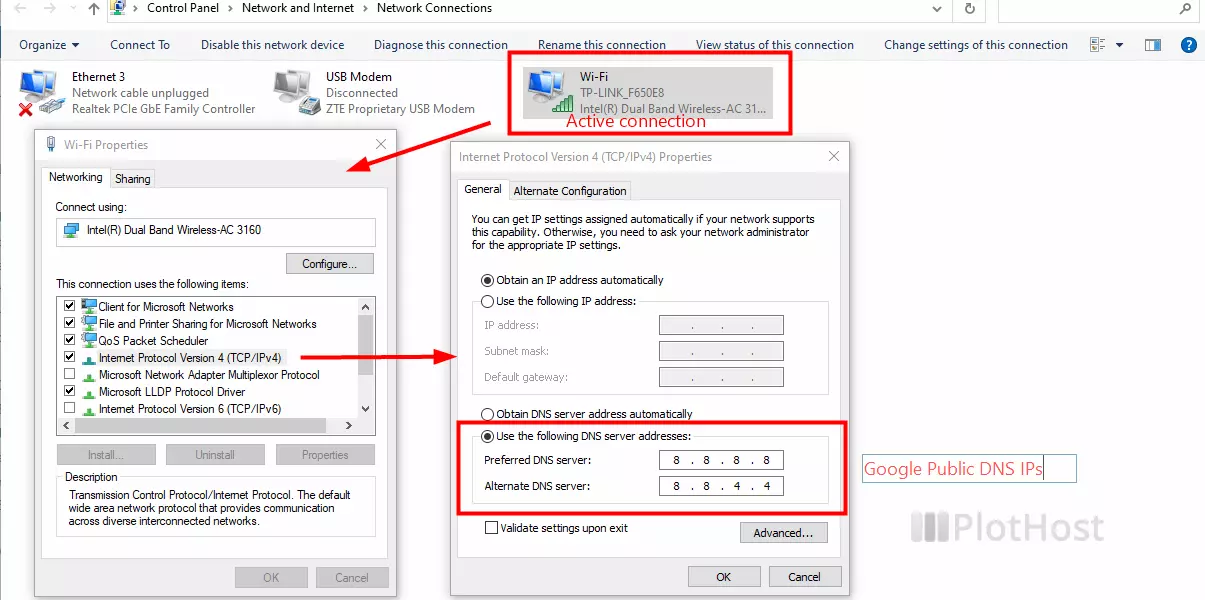
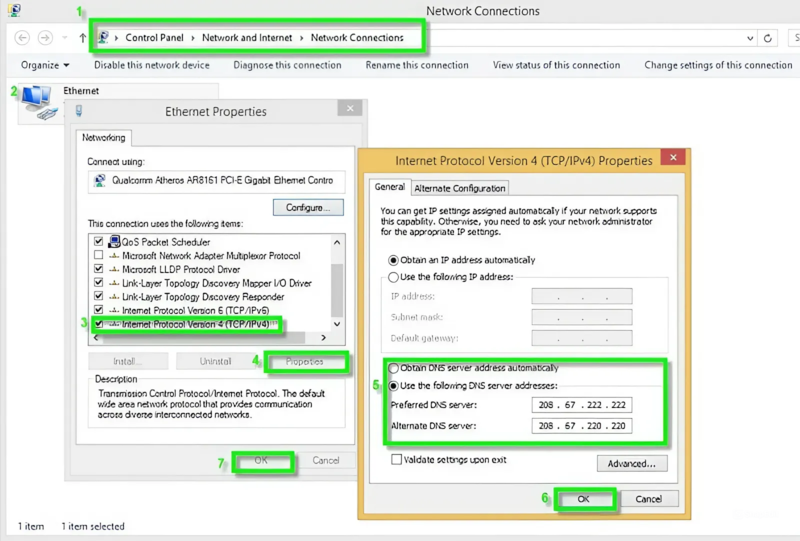
For individual computers, tablets, or smartphones, changing the DNS settings typically involves navigating to the device’s network configuration panel. On Windows, this is usually found in the Network and Sharing Center, under adapter settings for your Wi-Fi or Ethernet connection. On macOS, it’s in System Preferences > Network > Advanced > DNS. Mobile devices have similar settings within their Wi-Fi or cellular network configurations. Users simply replace the existing DNS server addresses with 8.8.8.8 as the primary and 8.8.4.4 as the secondary. This direct device configuration ensures that only that specific device utilizes Google’s resolvers, making it a good option for testing or for users who only want certain devices to benefit from the service.
Network-Wide Implementation
For a more comprehensive solution, configuring Google Public DNS on your router is the most efficient method. By changing the DNS settings within your router’s administration interface, all devices connected to that router (via Wi-Fi or Ethernet) will automatically use Google’s resolvers. This eliminates the need to configure each device individually and ensures a consistent experience across your entire local network. Accessing your router’s interface usually involves typing its IP address (often 192.168.1.1 or 192.168.0.1) into a web browser. Once logged in, navigate to the WAN or Internet settings and locate the DNS server fields. Inputting 8.8.8.8 and 8.8.4.4 there will make Google Public DNS the default for all connected clients. It’s always advisable to restart the router and connected devices after making such changes to ensure they take effect properly.
The Broader Impact and Future of DNS Technology
Google Public DNS, as a leading example of a public DNS resolver, has not only offered a valuable alternative for internet users but has also significantly contributed to the ongoing evolution and innovation within DNS technology. Its existence has pushed ISPs and other providers to enhance their own DNS offerings, fostering a healthier, more competitive ecosystem.
Addressing Modern Internet Challenges
The very nature of Google Public DNS addresses several modern internet challenges. Its global distribution helps overcome geographical disparities in internet infrastructure, providing a consistently fast and reliable service irrespective of a user’s local ISP’s capabilities. Its robust security measures, particularly its strong stance on DNSSEC validation, are crucial in an era of increasing cyber threats, protecting users from phishing and other domain-based attacks. Furthermore, by offering an alternative to ISP-mandated DNS, it provides users with greater control over their internet experience and a choice in how their DNS queries are handled, contributing to an open and user-centric internet.
The Evolution Towards Encrypted DNS
The landscape of DNS is continually evolving, with privacy and security being major drivers of innovation. Technologies like DNS over HTTPS (DoH) and DNS over TLS (DoT) represent the next frontier in DNS security. These protocols encrypt DNS queries, preventing third parties (like ISPs or malicious actors) from snooping on user browsing activity or tampering with DNS responses. Google has been a proponent and implementer of these technologies, integrating DoH support into its Chrome browser and Android operating system, and offering DoT support for its public DNS resolvers. This shift towards encrypted DNS is a critical step in building a more private and secure internet, making it harder for surveillance and censorship efforts to operate at the DNS level. As a major player in this space, Google’s ongoing commitment to developing and deploying these advanced DNS technologies underscores its role as an innovator in foundational internet services, shaping the future of how we connect and interact online.