
Email spoofing is a sophisticated form of cyberattack where the sender intentionally falsifies the “from” address of an email to make it appear as if it originated from a legitimate and trusted source. This deceptive practice is a cornerstone of many widespread cybercrimes, including phishing, Business Email Compromise (BEC), and malware distribution. The core objective is to trick recipients into believing the email is authentic, thereby inducing them to perform actions they otherwise wouldn’t, such as revealing sensitive information, transferring funds, or clicking malicious links.
The underlying mechanism exploits the inherent trust model of email communication protocols, specifically the Simple Mail Transfer Protocol (SMTP), which historically did not include robust authentication to verify the sender’s identity. While modern solutions exist to mitigate spoofing, its prevalence underscores the ongoing challenge in securing digital communication channels. Understanding the intricacies of email spoofing is crucial for both individuals and organizations in developing effective defense strategies against this pervasive threat.

The Mechanics Behind Email Spoofing
At its heart, email spoofing leverages technical loopholes and human psychology to achieve its malicious aims. It’s not about hacking into an email account; rather, it’s about manipulating the displayed sender information to create a false sense of legitimacy.
How Spoofing Works
When an email is sent, various pieces of information are communicated between mail servers and email clients. The sender’s address, often displayed prominently to the recipient, is surprisingly easy to alter. An attacker doesn’t need access to the legitimate sender’s email server or account to send an email that appears to come from them. They merely need to configure their own mail server or use a third-party service to insert the desired “From” address into the email’s header.
This is akin to sending a physical letter with a false return address. The post office delivers the letter based on the destination address, and the recipient sees the fabricated return address without the post office necessarily verifying its authenticity. In the digital realm, email clients and users often rely on the visual “From” field, which is the primary target for spoofers. The actual path the email took, visible in the full email headers, would reveal the true origin, but most users don’t inspect these details.
Technical Underpinnings: SMTP and Headers
The Simple Mail Transfer Protocol (SMTP) is the standard protocol for sending email across the internet. Historically, SMTP was designed for message delivery efficiency rather than robust sender authentication. When an email is sent, the sending server communicates with the receiving server. During this communication, two key “From” addresses come into play:
MAIL FROM(Envelope From): This is the address used by SMTP servers to determine where to send bounce messages if the email cannot be delivered. It’s also often used for Sender Policy Framework (SPF) checks. This address is usually not directly visible to the end-user in their email client.From:Header (Display From): This is the address displayed to the recipient in their email client. This is the field that attackers most commonly spoof because it’s what users see and trust.
An attacker can set the From: header to any address they choose, regardless of the MAIL FROM address or the actual sending server’s domain. This disconnect is the fundamental vulnerability that email spoofing exploits. Without proper authentication mechanisms, a receiving mail server often has no immediate way to verify that the domain in the From: header truly sent the email.
Sophisticated spoofing might also involve manipulating other header fields, such as Reply-To, to direct responses to a different, attacker-controlled address, or including a legitimate-looking name alongside the forged email address to enhance credibility. The blend of technical manipulation and social engineering makes spoofed emails highly effective in deceptive campaigns.
Common Motivations and Types of Spoofing Attacks
Email spoofing is not an end in itself but rather a means to an end, serving as the foundational technique for a variety of cybercriminal activities. The motivations behind these attacks are typically financial gain, data theft, or disruption.
Phishing and Spear Phishing
The most common application of email spoofing is in phishing attacks. Attackers spoof the sender to impersonate well-known entities such as banks, social media platforms, government agencies, or even internal IT departments. The goal is to trick recipients into clicking malicious links that lead to fake login pages or download malware. The spoofed “From” address lends an air of legitimacy, making the phishing email much more convincing than one from an unknown sender.
Spear phishing takes this a step further, targeting specific individuals or organizations with highly personalized and carefully crafted emails. In spear phishing, the attacker might spoof an email address of a colleague, a superior, or a trusted vendor. The personalized nature and the seemingly authentic sender make these attacks particularly dangerous and successful, often leading to significant data breaches or financial fraud.
Business Email Compromise (BEC)
Business Email Compromise (BEC) is a highly lucrative scam that heavily relies on email spoofing, often in conjunction with social engineering. In BEC attacks, cybercriminals impersonate high-level executives (like the CEO or CFO) or trusted external partners. The spoofed email then instructs an employee, typically in finance, to wire money to a fraudulent account, purchase gift cards, or divulge sensitive company information.
These attacks are often characterized by urgency, secrecy, and a seemingly authoritative tone. The financial impact of BEC scams can be devastating for businesses, with losses often reaching millions of dollars annually globally. The convincing nature of a spoofed email from a “CEO” can bypass many standard security checks if employees are not adequately trained.
Malicious Software Distribution
Email spoofing is also a primary vector for distributing various types of malicious software, including ransomware, viruses, and spyware. Attackers spoof a trusted sender and attach a malicious file (e.g., a PDF, Word document, or executable) or embed a link to a malware-hosting site. The recipient, believing the email is from a legitimate source, opens the attachment or clicks the link, inadvertently compromising their system.
The spoofed identity can be that of a delivery service, a utility company, or even a supposed internal memo, making the attachment appear safe and relevant. Once the malware is executed, it can encrypt files, steal data, or provide attackers with remote access to the victim’s network.
Identity Theft and Impersonation
Beyond direct financial gain or malware delivery, email spoofing can be used to facilitate broader identity theft. By impersonating a known entity, attackers can collect personal identifiable information (PII) through deceptive forms or by tricking individuals into “verifying” their details. This stolen information can then be used for various illicit activities, from opening fraudulent accounts to applying for credit in the victim’s name.
Spoofed emails can also be part of a larger social engineering campaign, where the attacker establishes a seemingly legitimate identity over time to gain trust and extract information or influence decisions. The ability to control the perceived sender identity is a powerful tool in these long-game impersonation schemes.

The Far-Reaching Risks of Spoofed Emails
The consequences of successful email spoofing attacks extend far beyond immediate financial losses, impacting an organization’s reputation, operational integrity, and legal standing.
Financial Losses and Data Breaches
The most immediate and tangible risk associated with email spoofing is significant financial loss. BEC scams alone account for billions of dollars in losses annually, directly transferring company funds to cybercriminals. Phishing attacks, facilitated by spoofing, can lead to unauthorized credit card transactions, banking fraud, and direct theft from individual accounts.
Beyond direct monetary theft, spoofed emails are a leading cause of data breaches. When employees fall victim to phishing emails that solicit credentials, attackers gain access to sensitive company systems, databases, and confidential information. This can expose customer data, intellectual property, financial records, and employee PII, leading to massive remediation costs, regulatory fines, and competitive disadvantages.
Reputational Damage
A successful spoofing attack can severely damage an organization’s reputation, both among its customers and within its industry. If an organization’s domain is frequently spoofed by attackers, customers may lose trust, perceiving the organization as insecure or negligent in its cybersecurity practices. This can lead to customer churn, negative public perception, and a decline in brand loyalty.
Conversely, if an organization falls victim to a BEC scam or a data breach originating from a spoofed email targeting its employees, its image as a secure and reliable entity can be tarnished. Public perception of security failures can be difficult to reverse, impacting future business opportunities and partnerships. The effort and cost to rebuild trust often far exceed the immediate losses from the attack itself.
Legal and Compliance Ramifications
Data breaches and financial fraud resulting from email spoofing can trigger a cascade of legal and compliance issues. Organizations are often subject to strict data protection regulations, such as GDPR, CCPA, and HIPAA. Failure to protect sensitive data, even if due to a sophisticated spoofing attack, can result in hefty fines and penalties from regulatory bodies.
Moreover, affected individuals or organizations may pursue legal action, leading to costly lawsuits and settlements. Organizations might also face scrutiny from industry auditors and compliance officers, potentially leading to sanctions or loss of certifications. The legal and compliance landscape increasingly holds organizations accountable for robust cybersecurity measures, making robust defenses against spoofing not just good practice but a regulatory necessity.
Safeguarding Against Email Spoofing
Combating email spoofing requires a multi-layered approach, combining technological defenses with robust user education and organizational policies. No single solution can fully eliminate the threat, but a comprehensive strategy significantly reduces vulnerability.
User Vigilance and Training
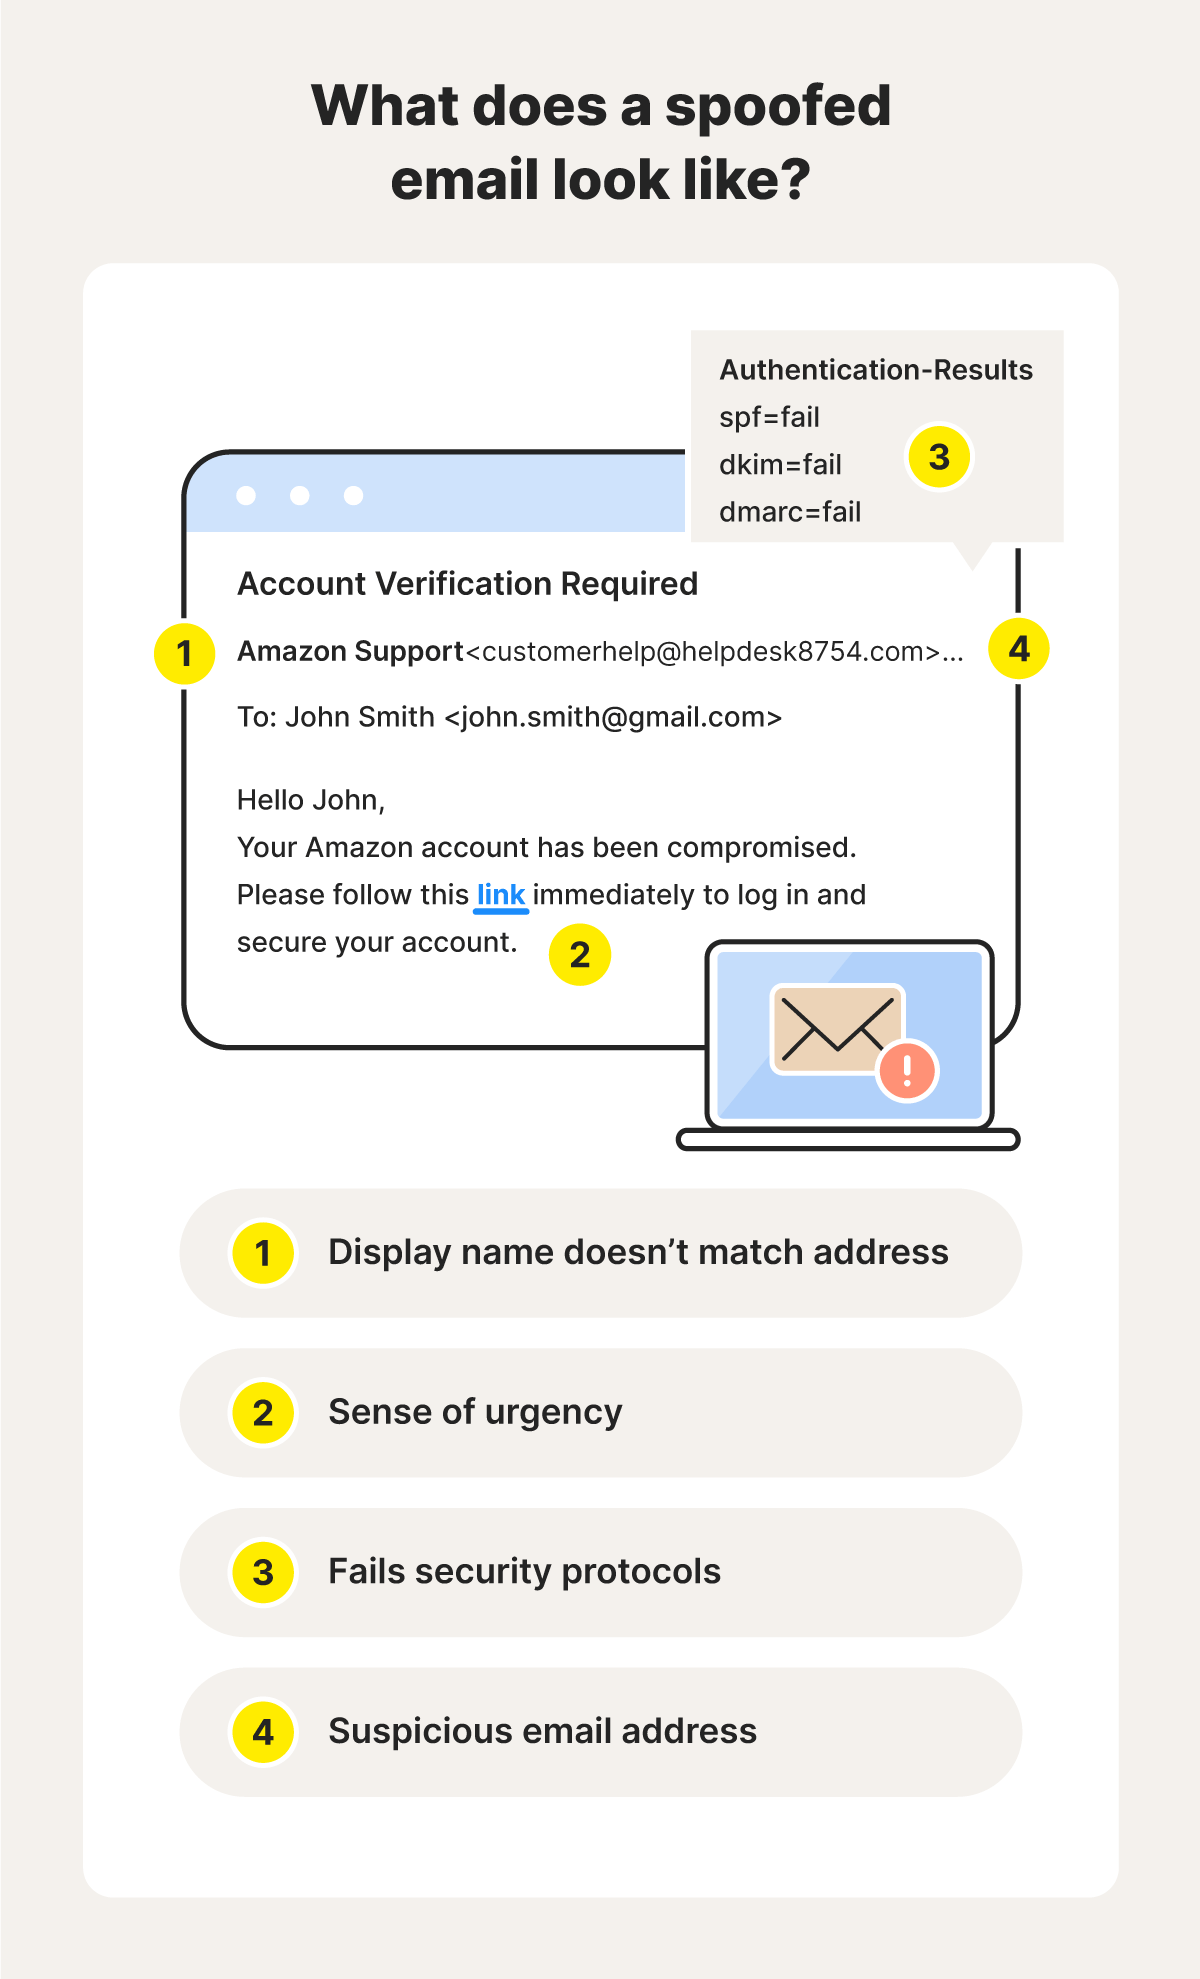
The human element is often the weakest link in cybersecurity, and email spoofing heavily preys on human trust and lack of awareness. Comprehensive and ongoing user training is paramount. Employees should be educated on how to identify the tell-tale signs of a spoofed email:
- Checking the actual sender address: Not just the display name, but expanding the “From” field to see the full email address.
- Looking for inconsistencies: Mismatched domain names (e.g.,
company-support.cominstead ofcompany.com), unusual grammar, spelling errors, or awkward phrasing. - Being wary of urgent requests: Especially those demanding immediate action, wire transfers, or disclosure of sensitive information.
- Hovering over links: Before clicking, hover over embedded links to reveal the actual URL and check for legitimacy.
- Verifying requests out-of-band: If an email from a superior or colleague requests a suspicious action, verify it through a different communication channel (e.g., a phone call or in-person confirmation) using a known contact number, not one provided in the suspicious email.
Regular simulated phishing exercises can also help reinforce training and identify areas where further education is needed.
Email Authentication Protocols (SPF, DKIM, DMARC)
Technical protocols provide critical defenses against email spoofing by allowing receiving mail servers to verify the authenticity of incoming emails. Organizations should implement these protocols for their domains:
- Sender Policy Framework (SPF): SPF allows domain owners to publish a list of authorized mail servers that are permitted to send email on behalf of their domain. A receiving server checks the SPF record to see if the IP address of the sending server is on the authorized list. If not, the email might be flagged as suspicious or rejected. SPF primarily checks the
MAIL FROM(envelope sender) address. - DomainKeys Identified Mail (DKIM): DKIM adds a digital signature to outgoing emails. The sending server signs the email, and the receiving server uses the sender’s public key (published in their DNS records) to verify the signature. This ensures that the email’s content hasn’t been tampered with in transit and that it genuinely originated from the claimed domain. DKIM checks the authenticity of the message content and the
From:header. - Domain-based Message Authentication, Reporting, and Conformance (DMARC): DMARC builds upon SPF and DKIM by providing instructions to receiving mail servers on how to handle emails that fail SPF or DKIM checks. It also provides reporting mechanisms, allowing domain owners to receive feedback on how their emails are being authenticated. DMARC policies can range from “monitor” (no action, just report) to “quarantine” (send to spam) to “reject” (block entirely), offering increasing levels of protection and control. DMARC is critical because it mandates alignment between the
MAIL FROMandFrom:domains.
Implementing and correctly configuring SPF, DKIM, and DMARC is one of the most effective technical steps an organization can take to prevent its domain from being spoofed and to filter out spoofed emails impersonating other domains.
Advanced Email Security Solutions
Beyond basic protocols, advanced email security solutions offer more sophisticated protection. These include:
- Anti-spoofing and Anti-phishing Filters: Email gateways and security services employ machine learning and advanced heuristics to detect anomalies in email headers, content, and sender behavior, identifying and blocking spoofed and phishing emails before they reach inboxes.
- Impersonation Protection: Specialized features can identify emails that attempt to impersonate internal executives or trusted contacts, even if the domain isn’t technically spoofed but visually similar.
- Link Rewriting and Attachment Sandboxing: These features modify links in emails to redirect through a secure proxy or detonate attachments in a safe, isolated environment (sandbox) to check for malicious activity before they can harm the user’s system.
- Brand Indicators for Message Identification (BIMI): An emerging standard that displays a verified brand logo next to the sender’s name in the inbox. While not a direct anti-spoofing measure, it adds another layer of visual authentication, helping users identify legitimate senders.
Multi-Factor Authentication (MFA)
While not a direct defense against receiving spoofed emails, MFA is critical in mitigating the impact of successful phishing attacks that steal credentials. Even if an attacker obtains a user’s password through a spoofed email, MFA prevents them from logging into the account without the second authentication factor (e.g., a code from a mobile app, a biometric scan, or a hardware token). Implementing MFA across all critical systems significantly reduces the risk of account takeover, which is often the ultimate goal of credential-stealing spoofing campaigns.
Incident Response Planning
Despite all preventative measures, no system is entirely foolproof. Organizations must have a robust incident response plan specifically for email-based attacks. This includes:
- Clear reporting mechanisms: Employees should know exactly how to report suspicious emails.
- Rapid investigation and containment: Procedures to quickly analyze reported emails, identify compromised accounts, and contain potential breaches.
- Communication strategy: Plans for informing affected parties, customers, and regulatory bodies in case of a breach or significant incident.
- Post-incident analysis: Learning from each incident to refine defenses and improve training programs.
By integrating these technical safeguards with comprehensive user education and preparedness, organizations can significantly enhance their resilience against the persistent and evolving threat of email spoofing.