
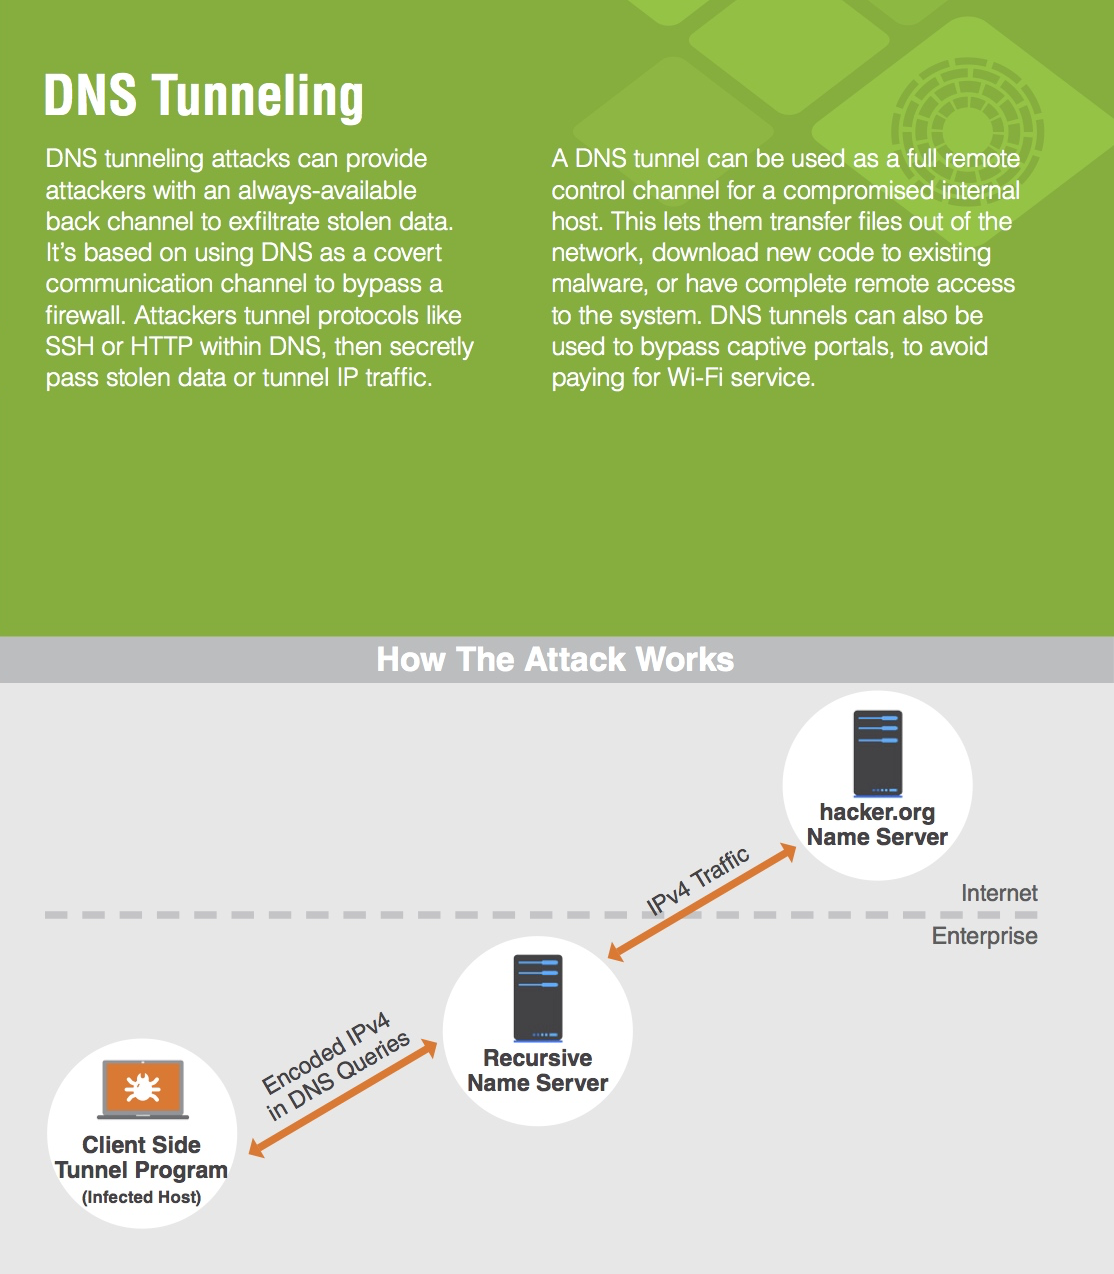
DNS tunneling represents a sophisticated and often insidious method of data exfiltration and covert communication that leverages the very foundation of internet navigation: the Domain Name System (DNS). While DNS is universally recognized as the internet’s phonebook, translating human-readable domain names into machine-readable IP addresses, its ubiquity and design make it a ripe target for exploitation. DNS tunneling effectively encapsulates data from other protocols, such as HTTP or SSH, within DNS queries and responses, enabling communication to bypass traditional firewall rules and detection systems that are not specifically configured to scrutinize DNS traffic beyond basic resolution. This technique, residing at the intersection of network architecture and cybersecurity, poses significant challenges for organizations striving to maintain secure and observable networks.
The Foundation: Understanding DNS Mechanics and Its Vulnerabilities
To grasp the intricacies of DNS tunneling, it’s essential to first appreciate the fundamental role and operational mechanics of the Domain Name System. DNS is a hierarchical and distributed naming system for computers, services, or any resource connected to the internet or a private network. It maps easily memorized domain names to the numerical IP addresses needed for locating and identifying computer services and devices with the underlying network protocols. When a user types a website address into a browser, a DNS query is initiated, traversing a series of resolvers and authoritative servers to retrieve the corresponding IP address.
This process, while critical for internet functionality, inherently involves a high volume of traffic often permitted egress through firewalls with minimal inspection. Most firewalls are configured to allow DNS traffic (UDP port 53 for queries, TCP port 53 for zone transfers) without deep packet inspection, assuming it’s legitimate network infrastructure communication. This trust, born from the necessity of allowing internet access, creates a blind spot. Attackers exploit this blind spot by crafting malicious payloads that mimic legitimate DNS queries or responses. By encoding arbitrary data within various fields of DNS packets – such as the query name, TXT records, or CNAME records – they can establish a covert channel. The distributed nature of DNS, with its multiple servers and recursive queries, further complicates detection, as traffic might bounce through several legitimate DNS servers before reaching the attacker’s controlled server, making direct source tracing challenging.
Deconstructing the Mechanics of DNS Tunneling
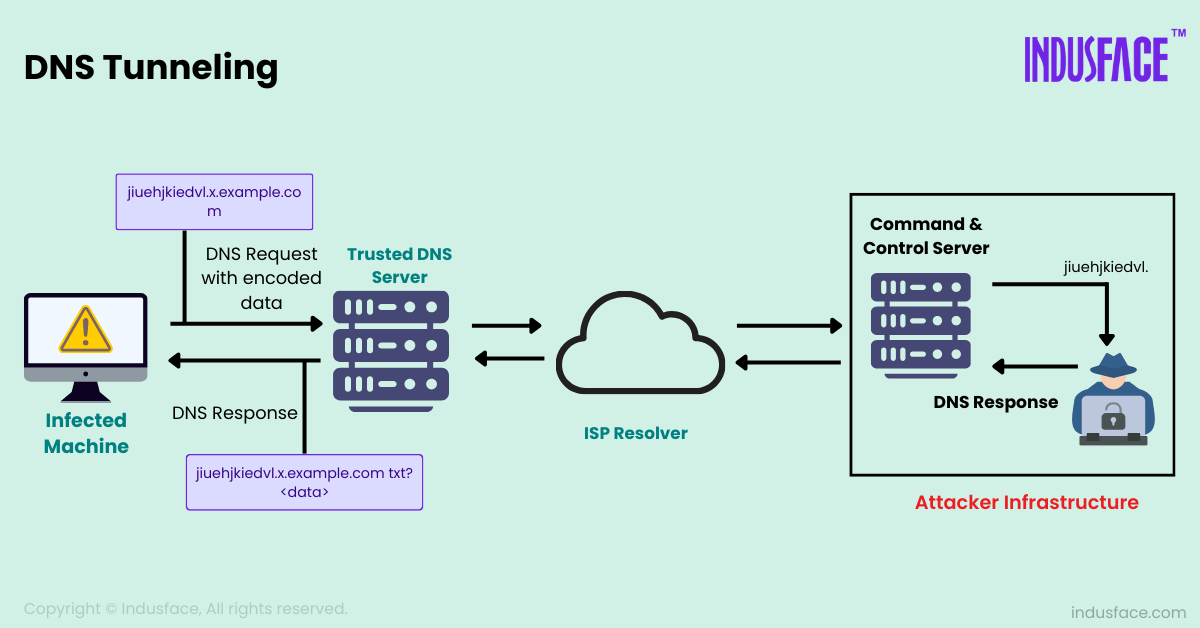
DNS tunneling operates by establishing a client-server architecture where a compromised host (the client) communicates with an attacker-controlled DNS server (the authoritative server for a specific malicious domain). The core principle involves encoding data into legitimate-looking DNS query types and then exfiltrating or receiving information through corresponding DNS responses.
Data Encapsulation and Communication Flow
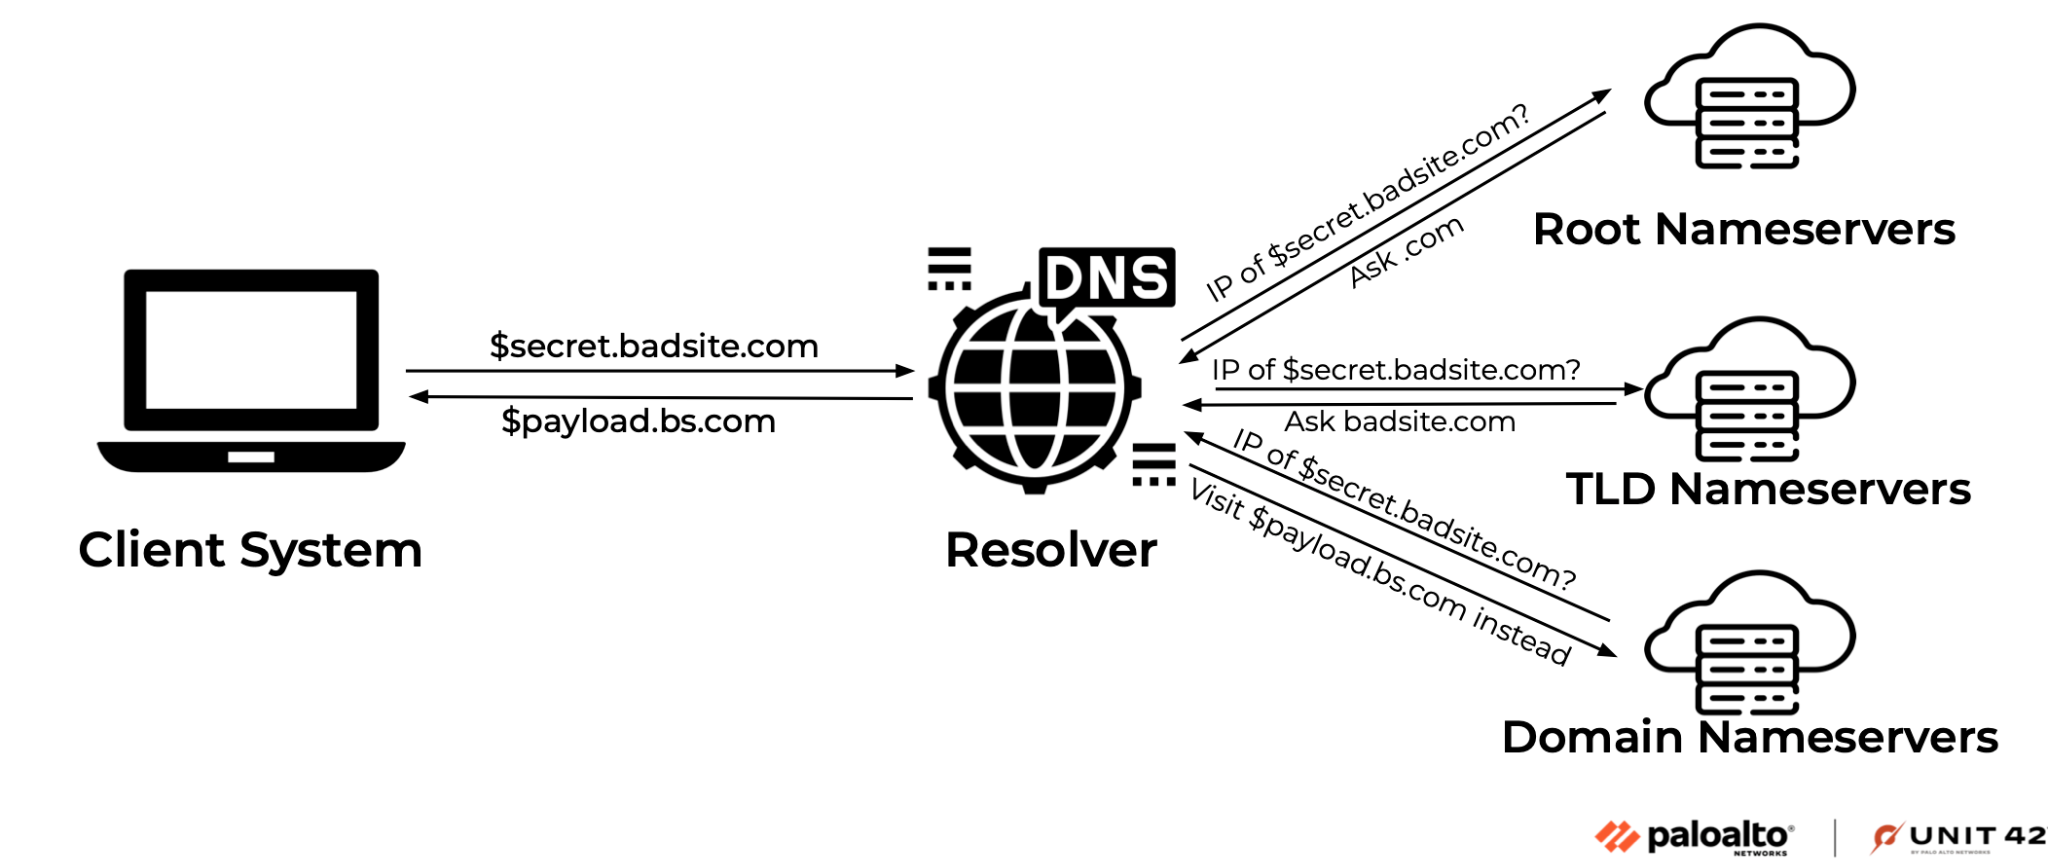
The process typically begins with an infected client on a target network attempting to resolve a domain name under the attacker’s control (e.g., data.segment.example.com). The “data.segment” part of this subdomain is not a standard DNS label but rather an encoded chunk of data from the compromised system.
- Client-Side Encoding: The client software on the compromised machine takes data it wants to send (e.g., a file, a command output) and encodes it, often using base64 or similar schemes, to convert binary data into alphanumeric characters suitable for DNS labels. This encoded data is then prepended to a domain name controlled by the attacker. For instance, if the client wants to send “hello”, it might encode it as “aGVsbG8” and construct a query like
aGVsbG8.maliciousdomain.com. - DNS Resolution Path: This specially crafted DNS query is sent to the local DNS resolver configured on the compromised network. The local resolver, unaware of the malicious intent, follows the standard DNS resolution path. It queries higher-level DNS servers until it reaches the authoritative DNS server for
maliciousdomain.com, which is controlled by the attacker. - Attacker-Side Decoding and Response: The attacker’s authoritative DNS server receives the query. It extracts the encoded data (“aGVsbG8”), decodes it (“hello”), processes it (e.g., executes a command, stores data), and then formulates a response. This response itself can contain encoded commands or data destined for the client, embedded within various DNS record types like TXT records, CNAME records, or even A records pointing to specific IP addresses.
- Client-Side Decoding: The attacker’s crafted DNS response travels back through the legitimate DNS infrastructure to the client’s local resolver, and finally to the compromised client software. The client software extracts and decodes the data from the DNS response, completing the covert communication loop.
This cycle can be continuous, allowing for a persistent, bidirectional communication channel. The slow nature of DNS queries means the bandwidth of a DNS tunnel is relatively low compared to direct TCP/IP connections, but it is often sufficient for command and control (C2) operations, small file transfers, or bypassing firewalls for initial reconnaissance.
Common DNS Record Types Used
Attackers favor specific DNS record types for tunneling due to their flexibility in carrying arbitrary data:
- TXT Records: These records are designed to hold arbitrary text strings and are perhaps the most straightforward for tunneling, as they can carry significant amounts of encoded data in a single response.
- CNAME Records: Canonical Name records, which map an alias name to a canonical domain name, can be used to redirect the client to other domains where data is embedded.
- NULL Records: While less common, NULL records can also be crafted to carry arbitrary data.
- A Records (Address Records): Even basic A records can be manipulated. For example, specific parts of the IP address returned can be used to encode data, though this is less efficient due to the limited data capacity.
Diverse Applications and the Dual Nature of DNS Tunneling
While DNS tunneling is predominantly associated with malicious activities, its underlying principle—encapsulating data within DNS—can technically serve legitimate, albeit rare, purposes. Understanding both facets is crucial for a comprehensive view.
Malicious Uses: The Primary Threat
The primary driver behind the proliferation of DNS tunneling techniques is its utility for cybercriminals and advanced persistent threat (APT) groups.
- Data Exfiltration: This is arguably the most common malicious application. Attackers can slowly siphon sensitive data (e.g., intellectual property, credentials, personally identifiable information) from compromised networks without triggering traditional security alerts. Since DNS traffic is often allowed and minimally inspected, large amounts of data can be “leaked” over time, making it difficult to detect with standard network monitoring tools.
- Command and Control (C2) Channels: DNS tunnels provide a robust and stealthy communication channel for attackers to issue commands to compromised machines and receive feedback. This allows them to maintain persistence within a network, remotely execute malware, pivot to other systems, and orchestrate further attacks without establishing direct TCP/IP connections that might be blocked by egress filtering rules.
- Bypassing Network Restrictions: In environments with strict outbound firewall rules (e.g., captive portals, corporate networks with limited internet access), DNS tunneling can be used to bypass these restrictions. If only DNS queries are permitted, an attacker can establish a full communication channel, effectively “tunneling” other protocols like SSH or HTTP over DNS to gain unfettered internet access from a restricted network segment.
- Evading Detection: The legitimate appearance of DNS traffic helps tunnels blend in. Traditional intrusion detection systems (IDS) and intrusion prevention systems (IPS) might overlook this traffic if they are not equipped with specific DNS-aware analytics, allowing malicious activity to continue undetected for extended periods.
Legitimate Uses: Niche Scenarios
While rare and often overshadowed by its malicious counterpart, DNS tunneling can theoretically be used for legitimate purposes, especially in highly restricted environments where only DNS traffic is permitted.
- Controlled Access in Isolated Networks: In very specific scenarios, such as industrial control systems (ICS) or air-gapped networks where internet access is strictly prohibited but a minimal form of communication is occasionally necessary, a controlled and monitored DNS tunnel could provide a limited, auditable channel for specific diagnostics or updates. However, the security risks usually outweigh the benefits.
- Testing and Research: Cybersecurity researchers and penetration testers might use DNS tunneling tools to assess the efficacy of an organization’s security controls and their ability to detect such covert channels. This helps in identifying blind spots and improving defensive strategies.
- Circumvention of Censorship (Highly Debatable): In certain heavily censored regions where only DNS traffic is allowed, individuals might attempt to use DNS tunneling to bypass restrictions and access the open internet. However, this is a risky endeavor, often quickly detected and blocked by national firewalls.
In practice, the inherent stealth and abuse potential of DNS tunneling means its usage is overwhelmingly skewed towards malicious actors, compelling network defenders to prioritize its detection and mitigation.
Detecting and Mitigating DNS Tunneling
Given the stealthy nature and potential for significant damage, detecting and mitigating DNS tunneling is a critical component of modern cybersecurity strategies. It requires a multi-layered approach that goes beyond basic network monitoring.
Detection Strategies
Effective detection relies on scrutinizing DNS traffic patterns and payloads for anomalies that indicate tunneling activity.
- Traffic Volume and Rate Anomalies: Legitimate DNS queries are typically small and infrequent. Tunnels often generate an unusually high volume of DNS queries or responses, especially with long query names, or a sustained rate of specific query types (e.g., TXT records). Monitoring tools should flag sudden spikes in DNS traffic to specific external domains.
- Query Length and Entropy: Malicious DNS queries often contain long, seemingly random strings of characters as subdomains (e.g.,
aGVsbG8.maliciousdomain.com). Analyzing the length and entropy (randomness) of queried domain names can reveal encoded data. Tools that identify high entropy or exceptionally long domain names are crucial. - Unusual Record Types: While legitimate DNS uses A, AAAA, MX, and NS records frequently, the prevalence of TXT, CNAME, or even NULL record queries and responses to specific external domains, especially in high volumes, can be a strong indicator of tunneling.
- Destination Reputation and Whitelisting: Regularly querying external DNS servers is normal. However, if a high volume of internal DNS requests is directed to newly registered domains, domains with low reputation scores, or domains not typically accessed by the organization, this should raise a red flag. Employing DNS firewalls that leverage threat intelligence feeds to block access to known malicious domains is vital.
- Behavioral Analysis: Observing the behavior of endpoints is key. If a client is continuously sending DNS queries to an external domain without any corresponding web browsing or application activity, it could indicate a C2 channel. Correlating DNS traffic with other network activity logs can expose suspicious patterns.
- Deep Packet Inspection (DPI): Advanced security appliances capable of performing deep packet inspection on DNS traffic can analyze the contents of DNS queries and responses for encoded data patterns or signatures of known tunneling tools.
Mitigation Techniques
Once detected, or even preemptively, several strategies can be employed to mitigate the risk of DNS tunneling.
- DNS Sinkholing: By directing queries for known malicious domains to a non-existent IP address or a controlled server (a “sinkhole”), organizations can prevent the client from reaching the attacker’s server and analyze the attempts.
- Egress Filtering and DNS Proxies: Implement strict egress filtering on firewalls to restrict outbound DNS queries to only approved, internal, or enterprise-managed DNS resolvers. This prevents clients from directly communicating with external, potentially malicious, authoritative DNS servers. Deploying a DNS proxy or forwarder that can inspect and filter DNS requests before they leave the network enhances control.
- Rate Limiting: Implement rate limits on DNS queries per client and per domain to prevent the high volume of traffic typically associated with tunneling.
- Content Filtering for DNS: Use DNS firewalls and security gateways that can inspect DNS payloads and block queries containing high entropy strings, unusually long domain names, or known malicious patterns. Some solutions can even block specific DNS record types for external communication if they are not legitimately required.
- Network Segmentation: Isolate critical assets and sensitive data within network segments that have highly restrictive outbound communication policies, further limiting the potential for data exfiltration via DNS.
- User and Entity Behavior Analytics (UEBA): Leverage UEBA tools to baseline normal DNS behavior for users and devices, making it easier to spot deviations indicative of tunneling or other covert activities.
- Security Awareness and Training: Educate employees about the risks of phishing and malware that can establish these covert channels. While technical controls are paramount, an informed workforce reduces the initial compromise vector.
DNS tunneling remains a persistent challenge due to its clever abuse of a fundamental internet protocol. A proactive and adaptive security posture, combining robust technical controls with continuous monitoring and threat intelligence, is essential to defend against this stealthy form of cyber attack.