In the intricate world of drone technology, particularly within the advanced domains of AI, autonomous flight, mapping, and remote sensing, the term “deadlocked” signifies a critical and potentially catastrophic operational state. Far from a simple glitch, a deadlock represents a condition where two or more processes or threads are unable to proceed because each is waiting for the other to release a resource. This concept, deeply rooted in computer science and operating systems, takes on profound implications when applied to complex, safety-critical systems like unmanned aerial vehicles (UAVs) that rely on real-time data processing, concurrent operations, and precise control. Understanding deadlocks is crucial for developers, operators, and researchers striving to push the boundaries of drone capabilities while ensuring reliability and safety.
Understanding Deadlock in Autonomous Drone Systems
Autonomous drones are essentially flying computers, integrating numerous sophisticated subsystems that must operate in concert. From flight control algorithms and navigation systems to AI-powered object recognition and mission planning modules, these components often run concurrently, sharing access to finite computational resources such as CPU cores, memory, communication channels, and sensor data streams. It is within this highly concurrent environment that the specter of deadlock emerges.
The Concurrency Challenge in UAVs
The essence of autonomy in drones lies in their ability to perform multiple tasks simultaneously and react dynamically to their environment. This necessitates a high degree of concurrency, where various software processes and hardware components operate in parallel. For instance, an autonomous drone might simultaneously be:
- Executing flight path calculations based on GPS and IMU data.
- Processing video feeds for obstacle avoidance using AI vision algorithms.
- Communicating with ground control or other drones.
- Collecting data from specialized sensors for mapping or remote sensing purposes.
- Managing power consumption and battery health.
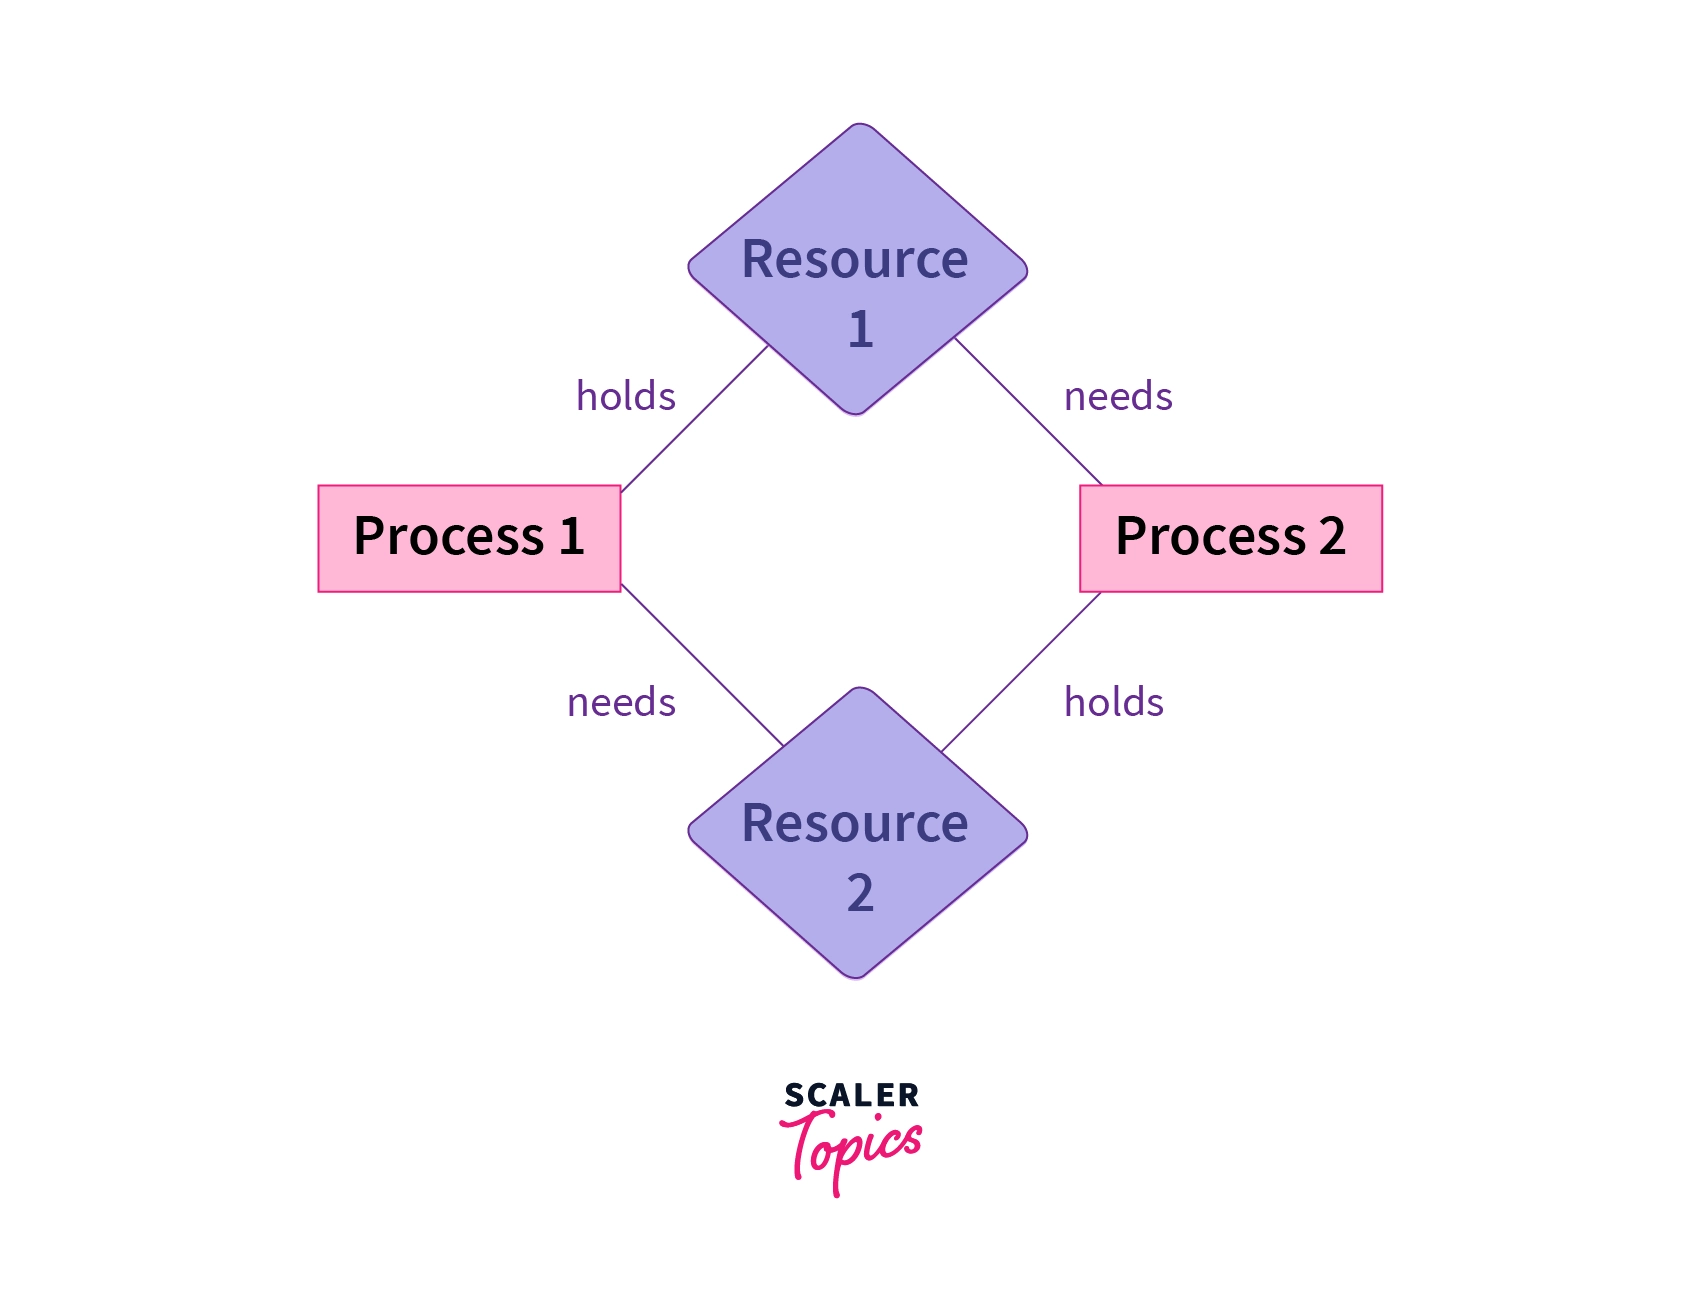
Each of these tasks often requires exclusive access to specific resources for a period. If not managed meticulously, a scenario can arise where Process A holds Resource X and requests Resource Y, while Process B holds Resource Y and requests Resource X. Both processes become indefinitely stalled, waiting for a resource held by the other, leading to a system-wide halt – a classic deadlock.
Resource Scarcity and Contention
Resources in a drone’s computational architecture are not limitless. The small form factor, power constraints, and real-time processing demands impose strict limitations on available CPU power, memory, bus bandwidth, and even the rate at which sensor data can be accessed. When multiple demanding applications, such as high-resolution mapping, complex AI inference, and precise flight stabilization, compete for these limited resources, the likelihood of contention increases.
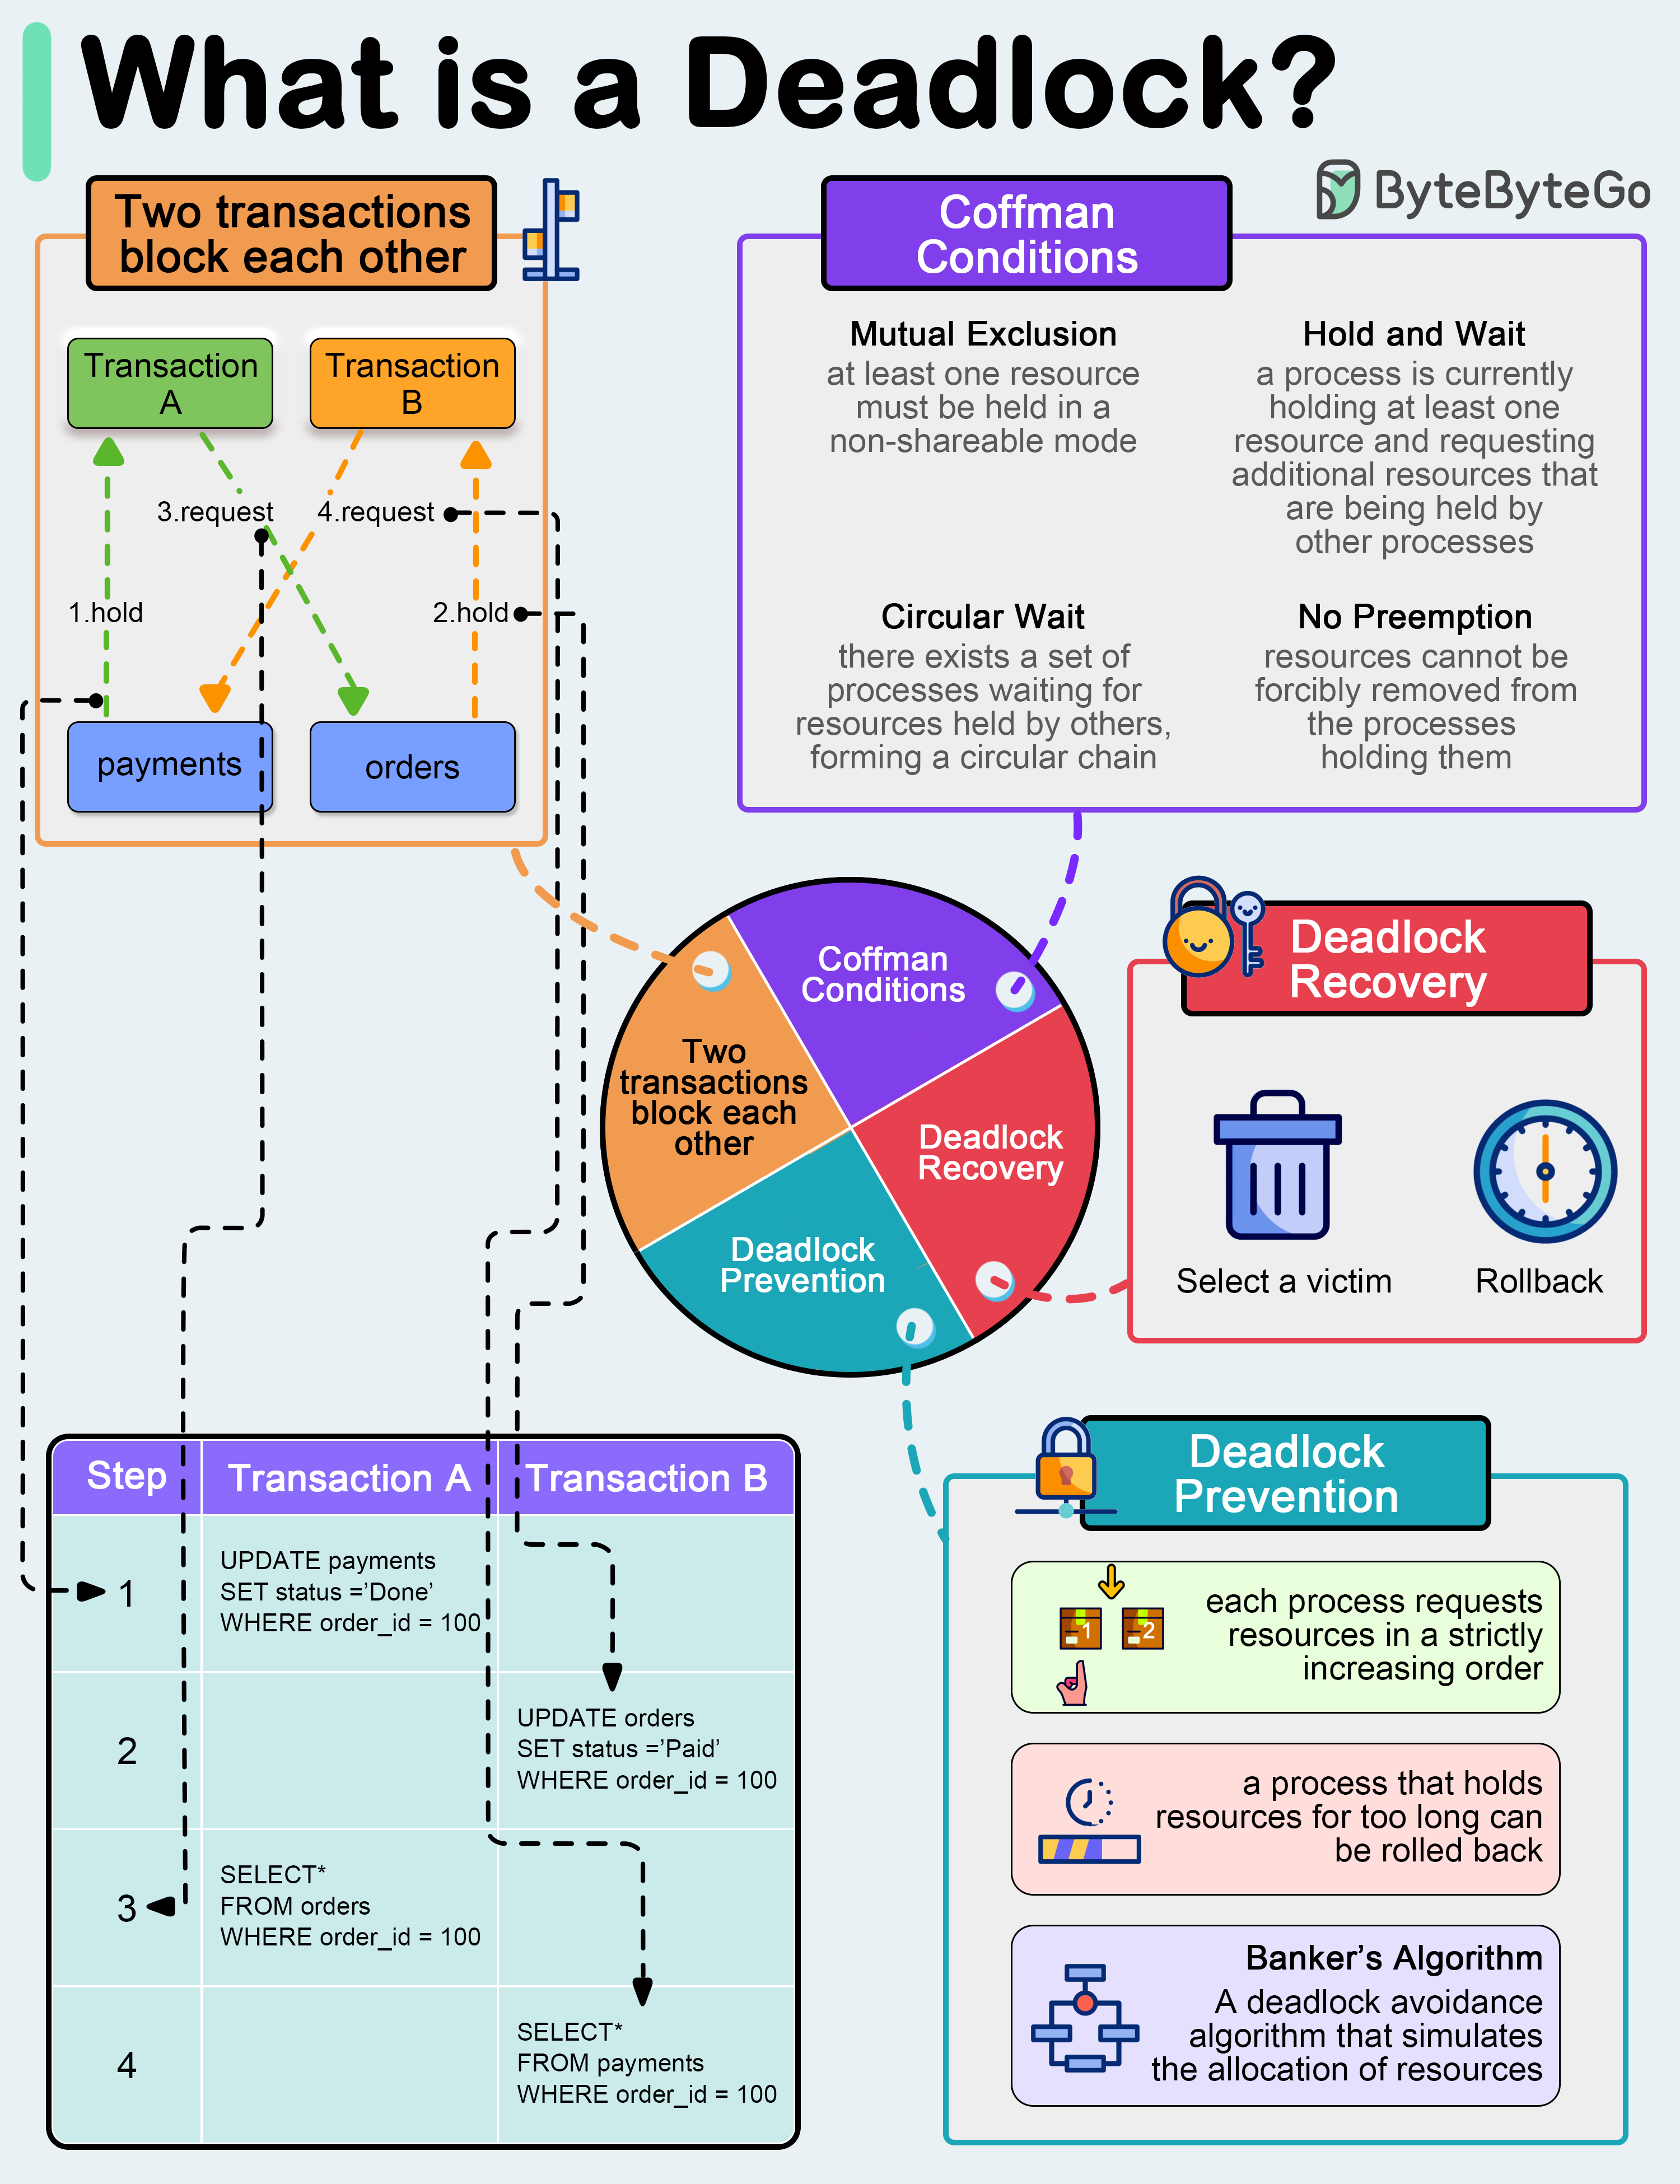
A deadlock typically requires four specific conditions to be met, known as the Coffman Conditions:
- Mutual Exclusion: At least one resource must be held in a non-sharable mode, meaning only one process can use it at any given time. This is common for many critical drone components like a specific sensor’s data bus or a section of memory dedicated to a flight control algorithm.
- Hold and Wait: A process must be holding at least one resource and waiting to acquire additional resources that are currently held by other processes. For example, an AI vision module might hold access to the camera feed while waiting for a CPU core allocated to the navigation system.
- No Preemption: Resources cannot be forcibly taken from a process that is holding them. They must be voluntarily released by the process. In a drone, prematurely preempting a critical flight control process could lead to instability or crashes.
- Circular Wait: A set of processes (P0, P1, P2, …, Pn) must exist such that P0 is waiting for a resource held by P1, P1 is waiting for a resource held by P2, …, and Pn is waiting for a resource held by P0. This forms a closed chain of dependencies.
When these conditions coalesce, an autonomous drone system can become completely unresponsive, unable to execute its mission or even maintain stable flight.
Common Scenarios Leading to Deadlock in Drone Tech
The highly integrated and parallel nature of modern drone systems makes them susceptible to various deadlock scenarios. These often emerge from the complex interactions between different software modules and hardware components.
Multi-threading in Flight Control and AI
Modern drone flight controllers and AI systems heavily rely on multi-threading to achieve real-time performance and efficient resource utilization. For instance, one thread might handle IMU data processing, another GPS signal interpretation, a third PID control loop execution, and a fourth AI inference for object detection. If these threads require access to shared data structures or hardware interfaces (e.g., a shared buffer for sensor data, a communication bus to an ESC controller), careful synchronization mechanisms like mutexes, semaphores, or locks are employed.
A common deadlock scenario here is when Thread A locks Mutex M1, then attempts to lock Mutex M2. Simultaneously, Thread B locks Mutex M2 and then attempts to lock Mutex M1. Both threads become perpetually blocked, leading to a frozen flight control system or a non-responsive AI module, which can have immediate and severe consequences for flight stability and safety.
Distributed Systems and Sensor Fusion
Advanced drones often incorporate distributed computing paradigms, especially in larger platforms or swarms, where different processing units handle specialized tasks (e.g., a dedicated vision processing unit, a flight management unit, a communication module). Sensor fusion, a critical component of autonomous navigation and perception, involves integrating data from multiple heterogeneous sensors (Lidar, Radar, cameras, ultrasonic, IMU) to create a more accurate and complete understanding of the environment.
In a distributed setup, data communication between these units is vital. If Module A, responsible for Lidar processing, sends data to a central fusion module and expects an acknowledgment before proceeding, but the fusion module is simultaneously waiting for data from Module B (a camera processing unit) which itself is stalled awaiting a resource held by Module A, a complex distributed deadlock can occur. This can lead to a breakdown in environmental awareness, making obstacle avoidance or precise navigation impossible.
Inter-process Communication (IPC) Failures
Inter-process communication (IPC) mechanisms are fundamental for coordination between different software components within a drone’s operating system. These include shared memory, message queues, pipes, and remote procedure calls. A deadlock can arise if processes rely on synchronous IPC, where one process waits for a response from another, and the dependency forms a cycle.
Consider a mission planning process that sends a command to the autonomous navigation process and waits for a “mission accepted” signal. Concurrently, the navigation process might need to query the sensor management process for updated map data before it can accept the mission, while the sensor management process is waiting for an acknowledgment from the mission planning process that it successfully received previous sensor data. This circular dependency can halt the entire mission execution pipeline, rendering the drone inert or unable to proceed with its programmed tasks.
Implications of Deadlock for Drone Operations
The occurrence of a deadlock in a drone’s critical systems has far-reaching and often severe implications, impacting everything from mission success to safety and regulatory compliance.
Operational Halts and Mission Failure
The most immediate consequence of a deadlock is a complete cessation of functionality in the affected subsystems. If a deadlock occurs in the flight control system, the drone may lose its ability to maintain stable flight, execute commands, or even land safely. For autonomous missions, such as package delivery, infrastructure inspection, or search and rescue, a deadlock means mission abortion. The drone might hover indefinitely, unable to proceed, or worse, become uncontrollable. This leads to wasted resources, financial losses, and failure to achieve mission objectives.
Safety and Reliability Concerns
In safety-critical applications, a deadlock poses a significant hazard. An unresponsive flight controller or an incapacitated obstacle avoidance system can lead directly to uncontrolled flight, collisions, or crashes. Imagine a drone inspecting power lines that suddenly becomes deadlocked and drifts into the structure, or a delivery drone halting mid-air over a populated area. The reliability of autonomous drones hinges on their ability to consistently perform their tasks without unexpected halts. Deadlocks severely undermine this reliability, raising serious safety concerns for bystanders, property, and the drone itself. Furthermore, recovering from a deadlock often requires a system reset, which in mid-flight can be equivalent to a crash or a forced emergency landing, itself a risky maneuver.
Performance Degradation and Unresponsiveness
Even if a deadlock doesn’t immediately lead to a crash, it can manifest as severe performance degradation or partial unresponsiveness. For instance, if the AI vision system is partially deadlocked, it might only process frames sporadically, leading to delayed or inaccurate obstacle detection. This can compromise the drone’s ability to react to dynamic changes in its environment, making its autonomous functions unreliable and potentially dangerous. Operators might experience significant delays in telemetry updates, command responses, or video feeds, making manual intervention difficult or impossible.
Strategies for Deadlock Prevention and Resolution
Mitigating the risk of deadlocks in complex drone systems requires a multifaceted approach, integrating careful design, robust software engineering practices, and advanced algorithmic solutions.
Resource Allocation and Ordering
One of the most effective strategies for deadlock prevention is to ensure that the Coffman conditions are not met. The “circular wait” condition is often the easiest to break. This can be achieved through a strict global ordering of resources. If all processes acquire resources in a predefined, ascending order, a circular wait becomes impossible. For example, if all threads always acquire Mutex A before Mutex B, and Mutex B before Mutex C, then a thread cannot simultaneously hold C and wait for A, or hold B and wait for A (if A < B). Implementing this in complex drone software requires meticulous design of resource access protocols across all subsystems, ensuring that every component adheres to the established hierarchy.
Another approach is to design systems such that a process either acquires all necessary resources simultaneously or releases all held resources if it cannot acquire all. This “all or nothing” approach prevents the “hold and wait” condition.
Timeouts and Deadlock Detection Algorithms
While prevention is ideal, it’s not always entirely feasible in highly dynamic and complex systems. Therefore, mechanisms for deadlock detection and recovery are also crucial. Timeouts are a simpler form of detection: if a process waits for a resource for an unreasonably long period, it can be assumed to be deadlocked or in a critical state. The system can then be programmed to abort the waiting process, roll back its operations, or attempt to release its resources.
More sophisticated deadlock detection algorithms involve periodically analyzing the resource allocation graph to identify cycles. If a cycle is detected, indicating a deadlock, the system must then implement a recovery strategy. This typically involves:
- Process Termination: Aborting one or more processes involved in the deadlock to break the cycle. This choice must be carefully considered based on the criticality of the processes.
- Resource Preemption: Forcibly taking a resource from one process and allocating it to another, then restarting the preempted process. This is complex and risky, particularly in real-time flight control.
- Rollback: Restoring processes to a previous safe state, typically before they acquired the resources involved in the deadlock.
Robust Software Architecture and Testing
The foundation for deadlock prevention lies in a robust software architecture. Adopting principles of modularity, clear interface definitions, and careful state management can significantly reduce the complexity that often leads to deadlocks. Using well-tested libraries and frameworks for concurrency control, rather than implementing custom solutions, can also help avoid common pitfalls.
Extensive testing is paramount. This includes:
- Unit Testing: Verifying individual components and their concurrency mechanisms.
- Integration Testing: Testing how different subsystems interact, specifically looking for resource contention.
- Stress Testing: Pushing the system to its limits with high loads to expose race conditions and potential deadlocks.
- Fuzz Testing: Introducing random inputs and conditions to uncover unforeseen interaction patterns.
- Formal Verification: For safety-critical modules, using mathematical methods to prove the absence of deadlocks, though this is computationally intensive and usually limited to specific critical components.

Redundancy and Fault Tolerance
For the most critical drone systems, incorporating redundancy and fault tolerance mechanisms can help mitigate the impact of deadlocks, even if they cannot always prevent them. This might involve:
- Backup Systems: Having a secondary flight controller or processing unit that can take over if the primary system becomes unresponsive due to a deadlock.
- Watchdog Timers: Hardware or software timers that monitor critical processes. If a process fails to “pet” the watchdog within a specified interval (indicating it’s stalled or deadlocked), the watchdog can trigger a reset or switch to a backup system.
- Graceful Degradation: Designing systems to shed non-essential tasks or enter a safe mode (e.g., controlled descent, emergency hover) if critical resources become unavailable or a partial deadlock occurs.
In conclusion, deadlocks pose a formidable challenge to the development and deployment of advanced autonomous drone technologies. As drones become more sophisticated, integrating complex AI, intricate navigation, and diverse sensing capabilities, the likelihood and severity of deadlocks increase. By understanding the underlying causes, implementing rigorous prevention strategies, and designing robust detection and recovery mechanisms, engineers can build more reliable, safer, and truly autonomous drone systems that fulfill their immense potential in various applications.