
Understanding AWS CloudTrail for Enhanced Security and Governance
In the dynamic landscape of cloud computing, particularly within Amazon Web Services (AWS), understanding the operational activities within your environment is paramount. This is where AWS CloudTrail emerges as a critical service, providing a comprehensive history of actions taken by a user, role, or an AWS service in your AWS account. Essentially, CloudTrail acts as a powerful audit log, offering invaluable insights into who did what, when, and from where within your AWS infrastructure. For organizations leveraging AWS, a thorough grasp of CloudTrail is not merely beneficial; it’s a foundational element for robust security, compliance, and operational troubleshooting.
The Core Functionality of CloudTrail
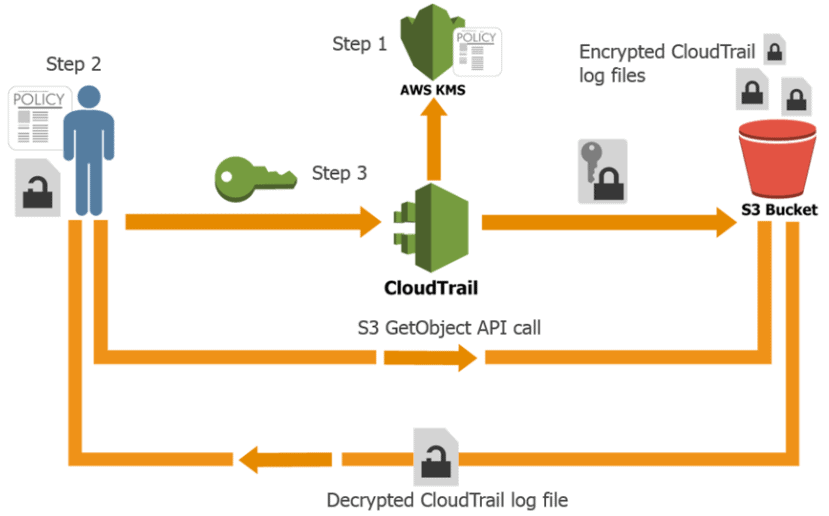
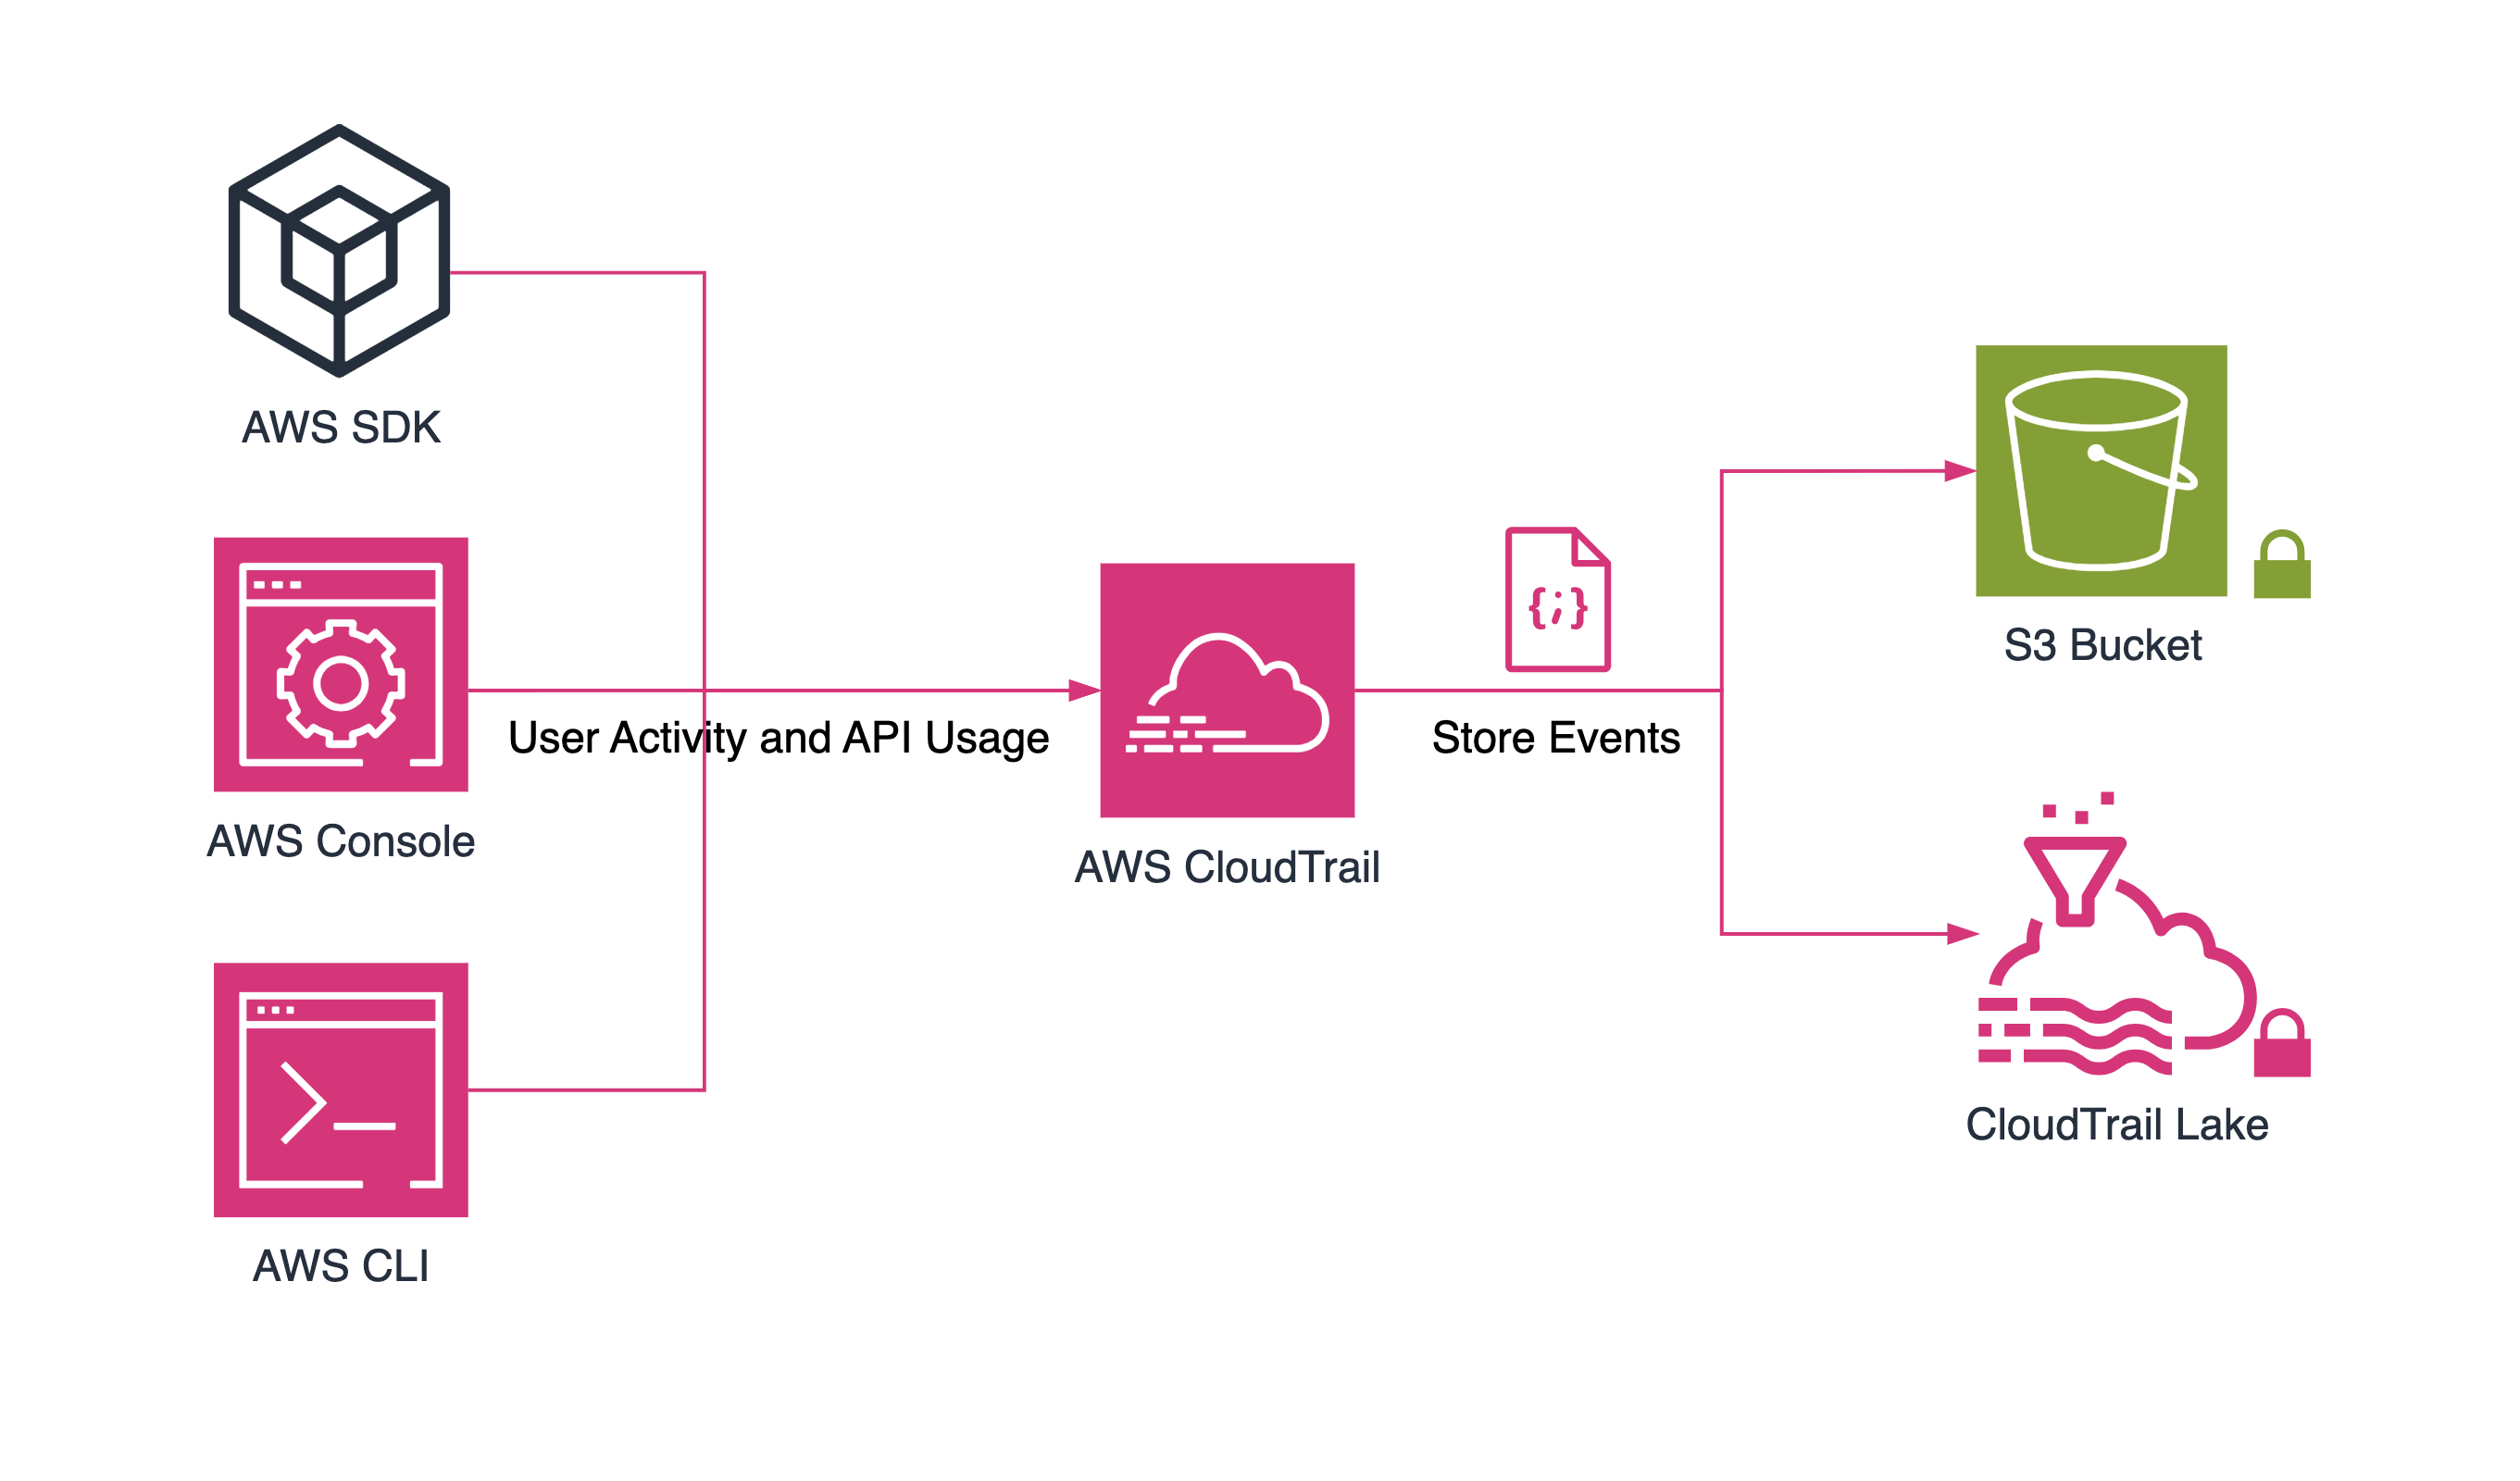
At its heart, CloudTrail records API calls made in your AWS account. Every interaction with an AWS service, whether initiated by a human user through the AWS Management Console, an SDK, command-line tool, or another AWS service, generates an event. CloudTrail captures these events and stores them as log files, making them accessible for analysis. This capability is fundamental for several key reasons:
- Auditing and Compliance: Many industry regulations and compliance frameworks (such as PCI DSS, HIPAA, SOX) mandate detailed audit trails of system activities. CloudTrail provides the necessary data to demonstrate adherence to these requirements, allowing you to track access to sensitive data, configuration changes, and user actions. This significantly simplifies audit preparation and reporting.
- Security Analysis: By examining CloudTrail logs, security teams can identify suspicious activities, unauthorized access attempts, or policy violations. This includes tracking who is accessing specific resources, when they are accessing them, and from what geographical locations. It helps in detecting potential security breaches early and facilitates incident response.
- Troubleshooting and Operational Diagnostics: When unexpected behavior or issues arise within your AWS environment, CloudTrail logs can be invaluable in pinpointing the root cause. By reviewing the sequence of API calls leading up to an event, administrators can diagnose configuration errors, understand resource lifecycle changes, and resolve operational problems more efficiently.
- Resource Change Tracking: CloudTrail records configuration changes to AWS resources. This allows you to see when resources were created, modified, or deleted, providing a clear historical record of your infrastructure’s evolution. This is crucial for understanding how your environment has changed over time and for reverting unintended modifications.
Types of CloudTrail Events
CloudTrail captures several types of events, each serving a distinct purpose in providing a complete picture of your AWS account activity:
- Management Events: These are the most commonly used events and log management operations performed on AWS resources. This includes operations performed through the AWS Management Console, AWS SDKs, command-line tools, and other AWS services. Examples include
RunInstances(launching an EC2 instance),CreateBucket(creating an S3 bucket),UpdateSecurityGroup(modifying a security group), andDeleteUser(deleting an IAM user). These events are crucial for understanding administrative activities and configuration changes. - Data Events: While management events cover control plane operations, data events log resource-level operations performed on or within a resource. For services like Amazon S3, data events record object-level API activity (e.g.,
GetObject,PutObject,DeleteObject). For AWS Lambda, they log function execution activity (Invoke). Data events can be very granular and are often enabled for specific resources or buckets where detailed operational visibility is required. It’s important to note that enabling data events for a large number of resources can generate a significant volume of logs and incur additional costs. - Insights Events: CloudTrail Insights is an intelligent feature that automatically analyzes and identifies unusual patterns in your AWS account activity. It differentiates between normal and unusual activity by looking for anomalies in API call rates, error rates, and other metrics. When it detects an anomaly, it creates a CloudTrail event that provides contextual information about the unusual activity, helping you to quickly identify and respond to potential operational or security issues.
Setting Up and Managing CloudTrail
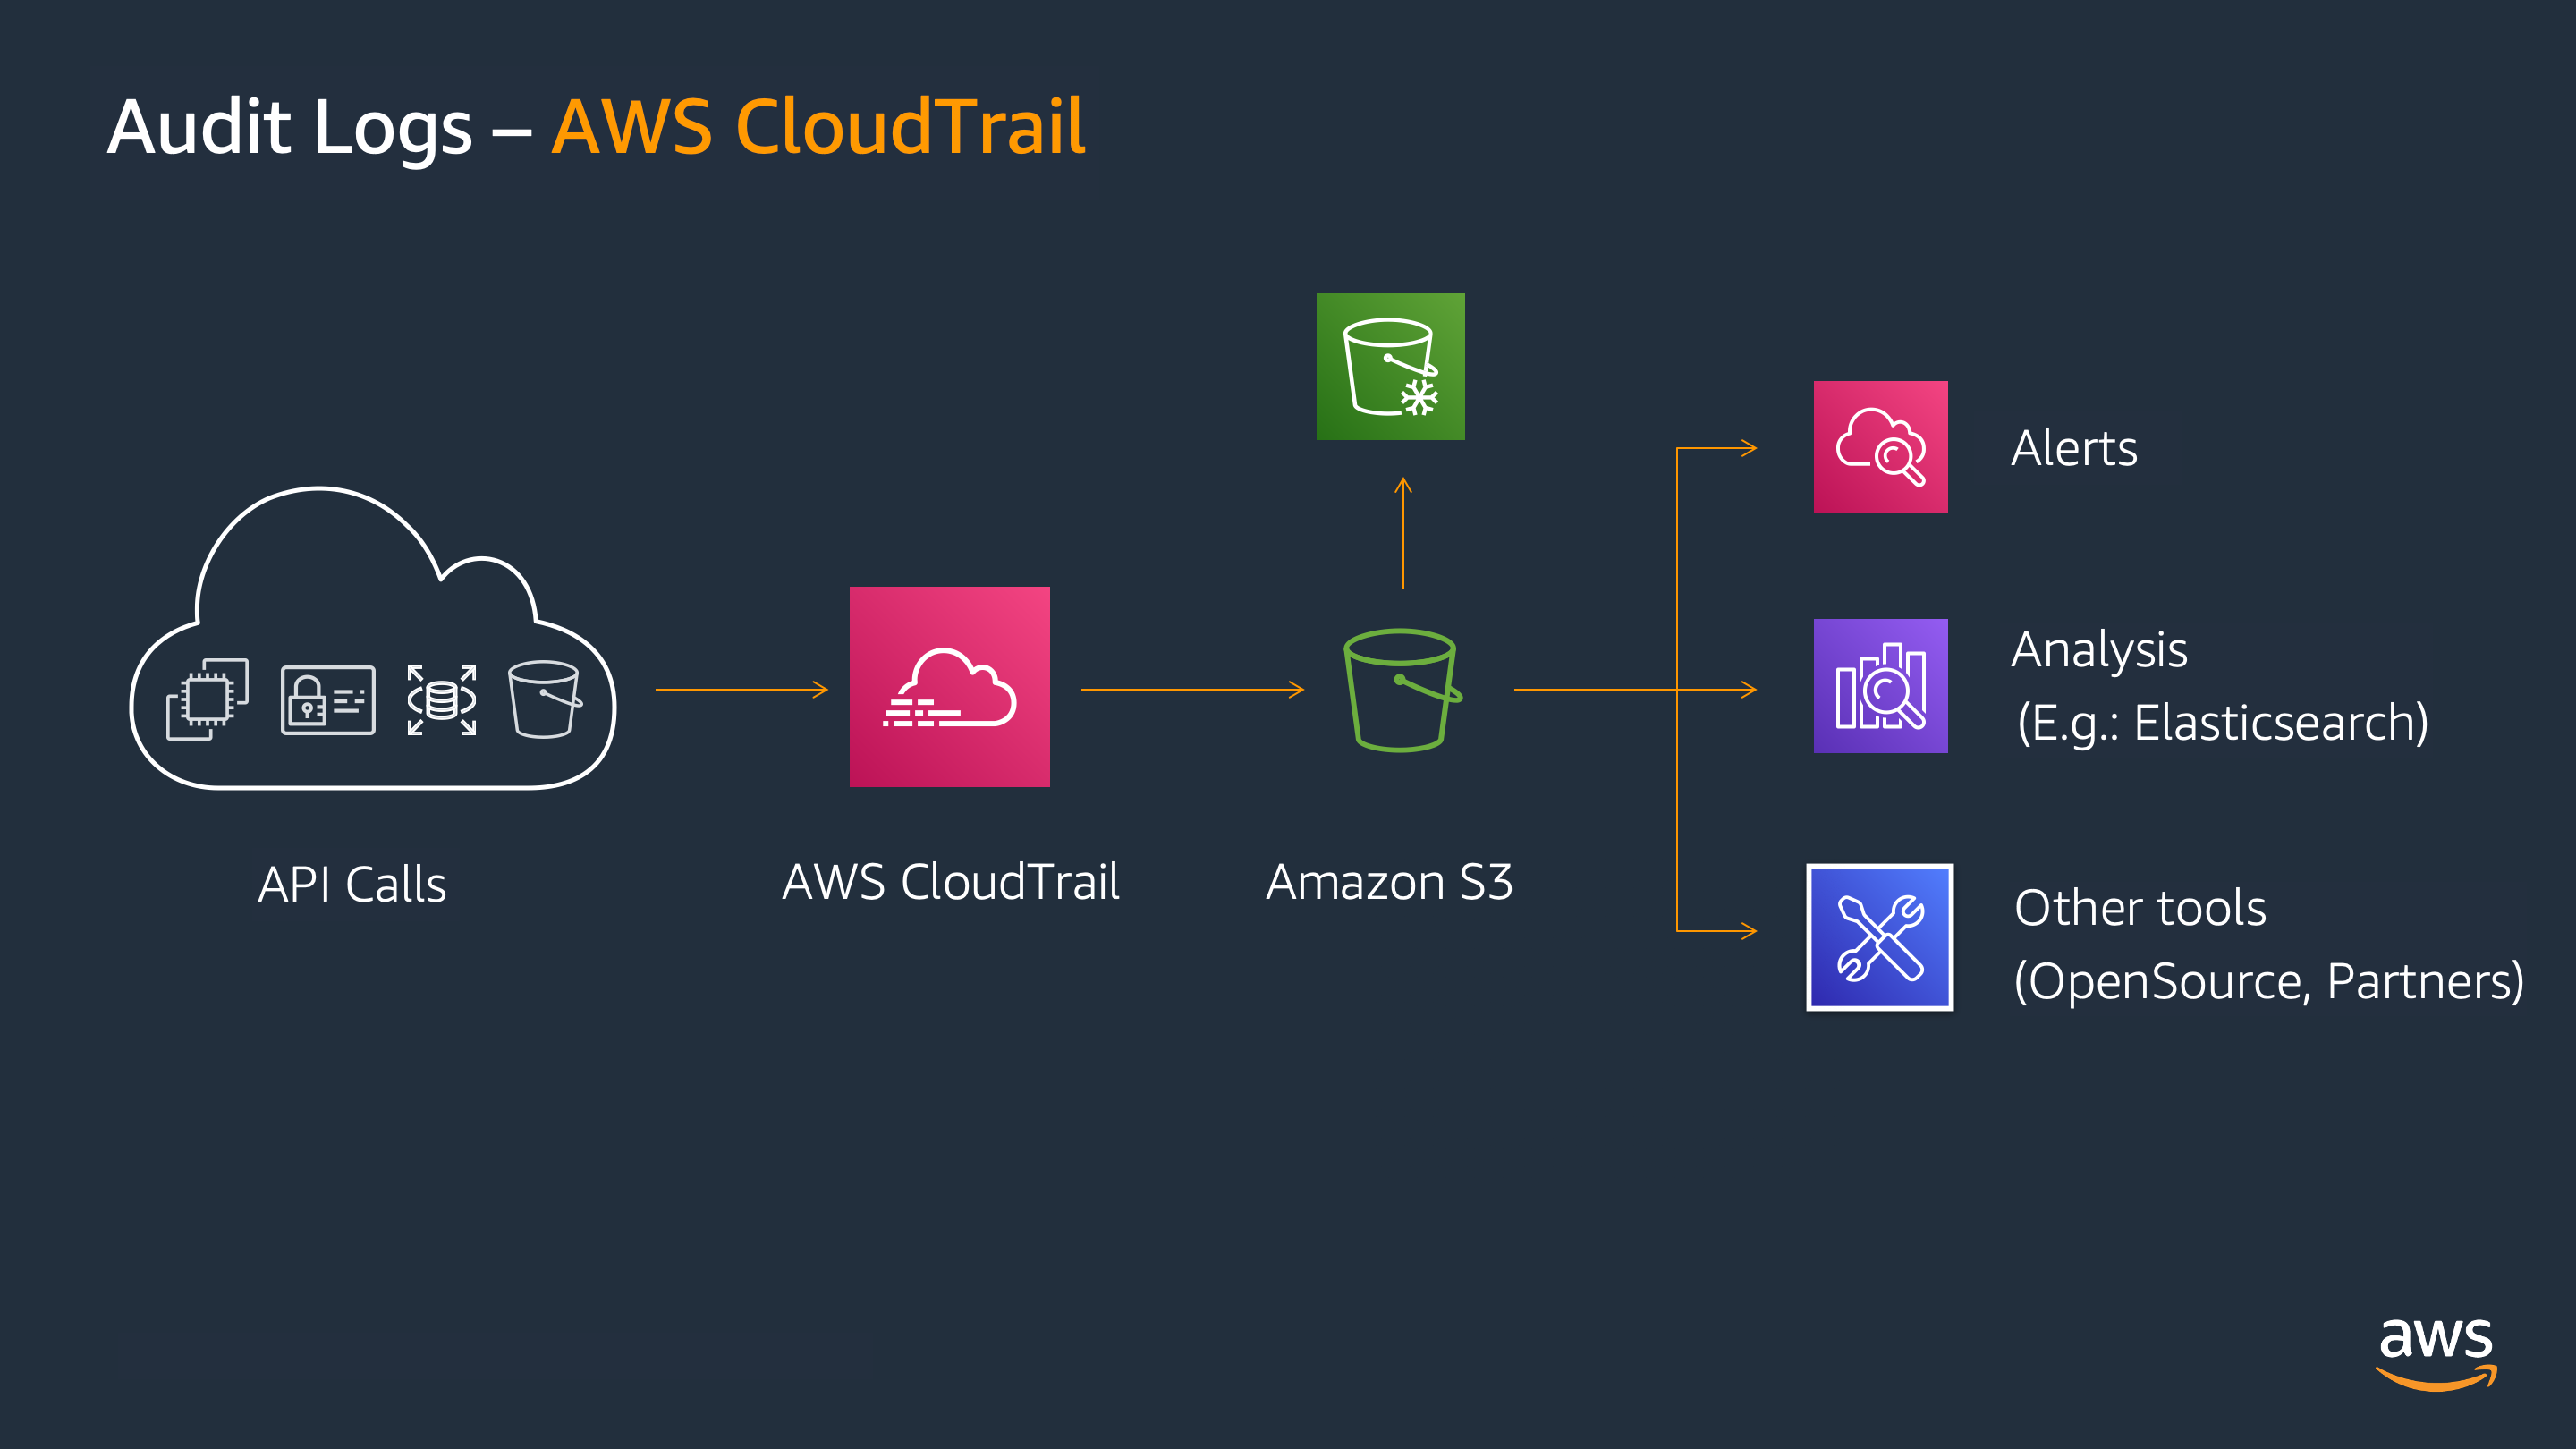
Implementing CloudTrail is a straightforward process within the AWS Management Console. Organizations typically create one or more trails to log events. A trail is a configuration that enables delivery of CloudTrail events to an Amazon S3 bucket and optionally to Amazon CloudWatch Logs.
Key Configuration Aspects
When setting up a trail, several important considerations come into play:
- Single Region vs. All Regions: You can configure a trail to log events in a single AWS Region or across all AWS Regions in your account. It is a best practice to configure a multi-region trail to capture all activity across your global AWS footprint. This ensures comprehensive visibility regardless of where actions are performed.
- Log File Delivery: CloudTrail delivers log files to an Amazon S3 bucket that you specify. This bucket becomes the central repository for your audit logs. It’s crucial to secure this S3 bucket appropriately, restricting access to authorized personnel and configuring lifecycle policies for log retention.
- Log File Integrity Validation: CloudTrail provides a feature to validate the integrity of your log files. It digitally signs each log file, allowing you to verify that the log files have not been tampered with after they were delivered. This is a critical security feature for ensuring the trustworthiness of your audit data.
- Integration with CloudWatch Logs: For real-time monitoring and alerting, CloudTrail can be configured to send events to CloudWatch Logs. This integration enables you to create alarms based on specific events, such as unauthorized access attempts or significant configuration changes. This proactive approach allows for immediate notification of critical events.
- Event Filtering: To manage the volume of logs and reduce costs, CloudTrail allows you to configure event filters. You can specify which event types (management, data, or Insights) and which resources you want to log events for. This granular control ensures that you capture the most relevant information without being overwhelmed by excessive data.
Best Practices for CloudTrail
To maximize the effectiveness of CloudTrail, consider these best practices:
- Enable CloudTrail in All Regions: As mentioned, configuring a multi-region trail is essential for comprehensive visibility.
- Secure Your S3 Log Bucket: Implement strict access control policies for the S3 bucket where CloudTrail logs are stored. Consider encryption at rest and in transit.
- Configure Log File Integrity Validation: Always enable this feature to ensure the integrity of your audit logs.
- Use CloudWatch Logs for Real-time Monitoring: Integrate CloudTrail with CloudWatch Logs to set up alerts for critical security and operational events.
- Implement Log Retention Policies: Define appropriate retention periods for your CloudTrail logs based on compliance requirements and organizational policies. Use S3 Lifecycle policies to automate log archival or deletion.
- Consider Data Event Logging Strategically: While data events provide granular detail, they can generate a high volume of logs. Enable them only for resources where such detailed logging is necessary.
- Regularly Review CloudTrail Logs: Proactive analysis of CloudTrail logs is key to identifying potential security threats and operational issues before they escalate.
Advanced CloudTrail Features and Integrations
Beyond its core logging capabilities, CloudTrail integrates with other AWS services to offer enhanced functionality and insights:
- CloudTrail Lake: CloudTrail Lake is a new capability that allows you to aggregate your CloudTrail events from multiple AWS Regions and accounts into a dedicated, highly available, and durable data store. This enables you to run SQL-based queries directly on your audit logs to perform sophisticated analysis and investigations. CloudTrail Lake simplifies long-term storage and analysis of audit logs, making it easier to meet compliance requirements and conduct forensic investigations.
- AWS Config Integration: CloudTrail and AWS Config work in tandem. While CloudTrail records who made what change, AWS Config records the state of your AWS resources. Together, they provide a powerful mechanism for understanding resource configurations and changes over time, which is invaluable for security and compliance.
- Security Hub Integration: AWS Security Hub can ingest CloudTrail findings, along with findings from other security services, into a centralized dashboard. This provides a consolidated view of your security posture and helps prioritize remediation efforts.
- EventBridge Integration: CloudTrail events can be sent to Amazon EventBridge (formerly CloudWatch Events), allowing you to trigger automated responses to specific events. For example, you could trigger a Lambda function to snapshot an EC2 instance if an unauthorized user attempts to stop it.
Conclusion
AWS CloudTrail is an indispensable service for any organization operating within Amazon Web Services. It provides the essential audit trail needed for security monitoring, compliance auditing, and operational troubleshooting. By understanding its core functionalities, configuring it effectively, and leveraging its integrations with other AWS services, you can significantly enhance the security, governance, and manageability of your cloud environment. In the complex and ever-evolving world of cloud computing, CloudTrail acts as your vigilant observer, ensuring transparency and accountability across your AWS operations.