
Azure Sentinel, now known as Microsoft Sentinel, represents a significant leap forward in cloud-native Security Information and Event Management (SIEM) and Security Orchestration, Automation, and Response (SOAR) solutions. It’s designed to help organizations detect, investigate, and respond to security threats across their entire digital estate, from on-premises infrastructure to multiple cloud environments. This powerful platform leverages the scalability and flexibility of Microsoft Azure to provide advanced threat intelligence, machine learning, and automation capabilities, fundamentally changing how security operations centers (SOCs) operate.
The Evolution of SIEM and SOAR with Microsoft Sentinel
The traditional SIEM landscape, while foundational, often struggled with the sheer volume and velocity of data generated by modern IT environments. Managing on-premises hardware, ensuring sufficient storage, and keeping up with evolving threat vectors proved to be resource-intensive and often reactive. SOAR solutions emerged to address the manual, time-consuming tasks involved in incident response, but integrating them with existing SIEMs could be complex and costly.

Microsoft Sentinel was engineered from the ground up as a cloud-native service, designed to overcome these limitations. It seamlessly integrates SIEM and SOAR functionalities into a single, unified platform, offering a holistic approach to security management. This integration is crucial in today’s threat landscape, where speed and efficiency are paramount in mitigating damage from cyberattacks.
Key Concepts: SIEM and SOAR in the Cloud Context
Security Information and Event Management (SIEM) traditionally focuses on collecting, aggregating, and analyzing security data from various sources within an organization. This includes logs from servers, network devices, applications, and endpoints. The primary goal is to identify suspicious activities, detect security threats, and provide visibility into the security posture of the environment. In the cloud, this data can originate from a vast array of services and applications spread across different cloud providers and on-premises systems.
Security Orchestration, Automation, and Response (SOAR) builds upon SIEM by providing capabilities to automate and orchestrate repetitive security tasks and incident response workflows. This can include tasks like enriching alerts with threat intelligence, quarantining infected endpoints, blocking malicious IP addresses, or creating support tickets. The aim is to reduce the manual effort required by security analysts, enabling them to focus on more complex investigations and strategic security initiatives.
Microsoft Sentinel unifies these two critical functions. It ingests vast amounts of data, performs sophisticated analytics to detect threats, and then provides the tools to automate response actions, all within a single, cloud-native platform. This synergistic approach allows organizations to move from a reactive stance to a more proactive and intelligent security posture.
Core Capabilities and Functionality
Microsoft Sentinel’s power lies in its comprehensive suite of capabilities, designed to address the entire security lifecycle from detection to response.
Data Ingestion and Management
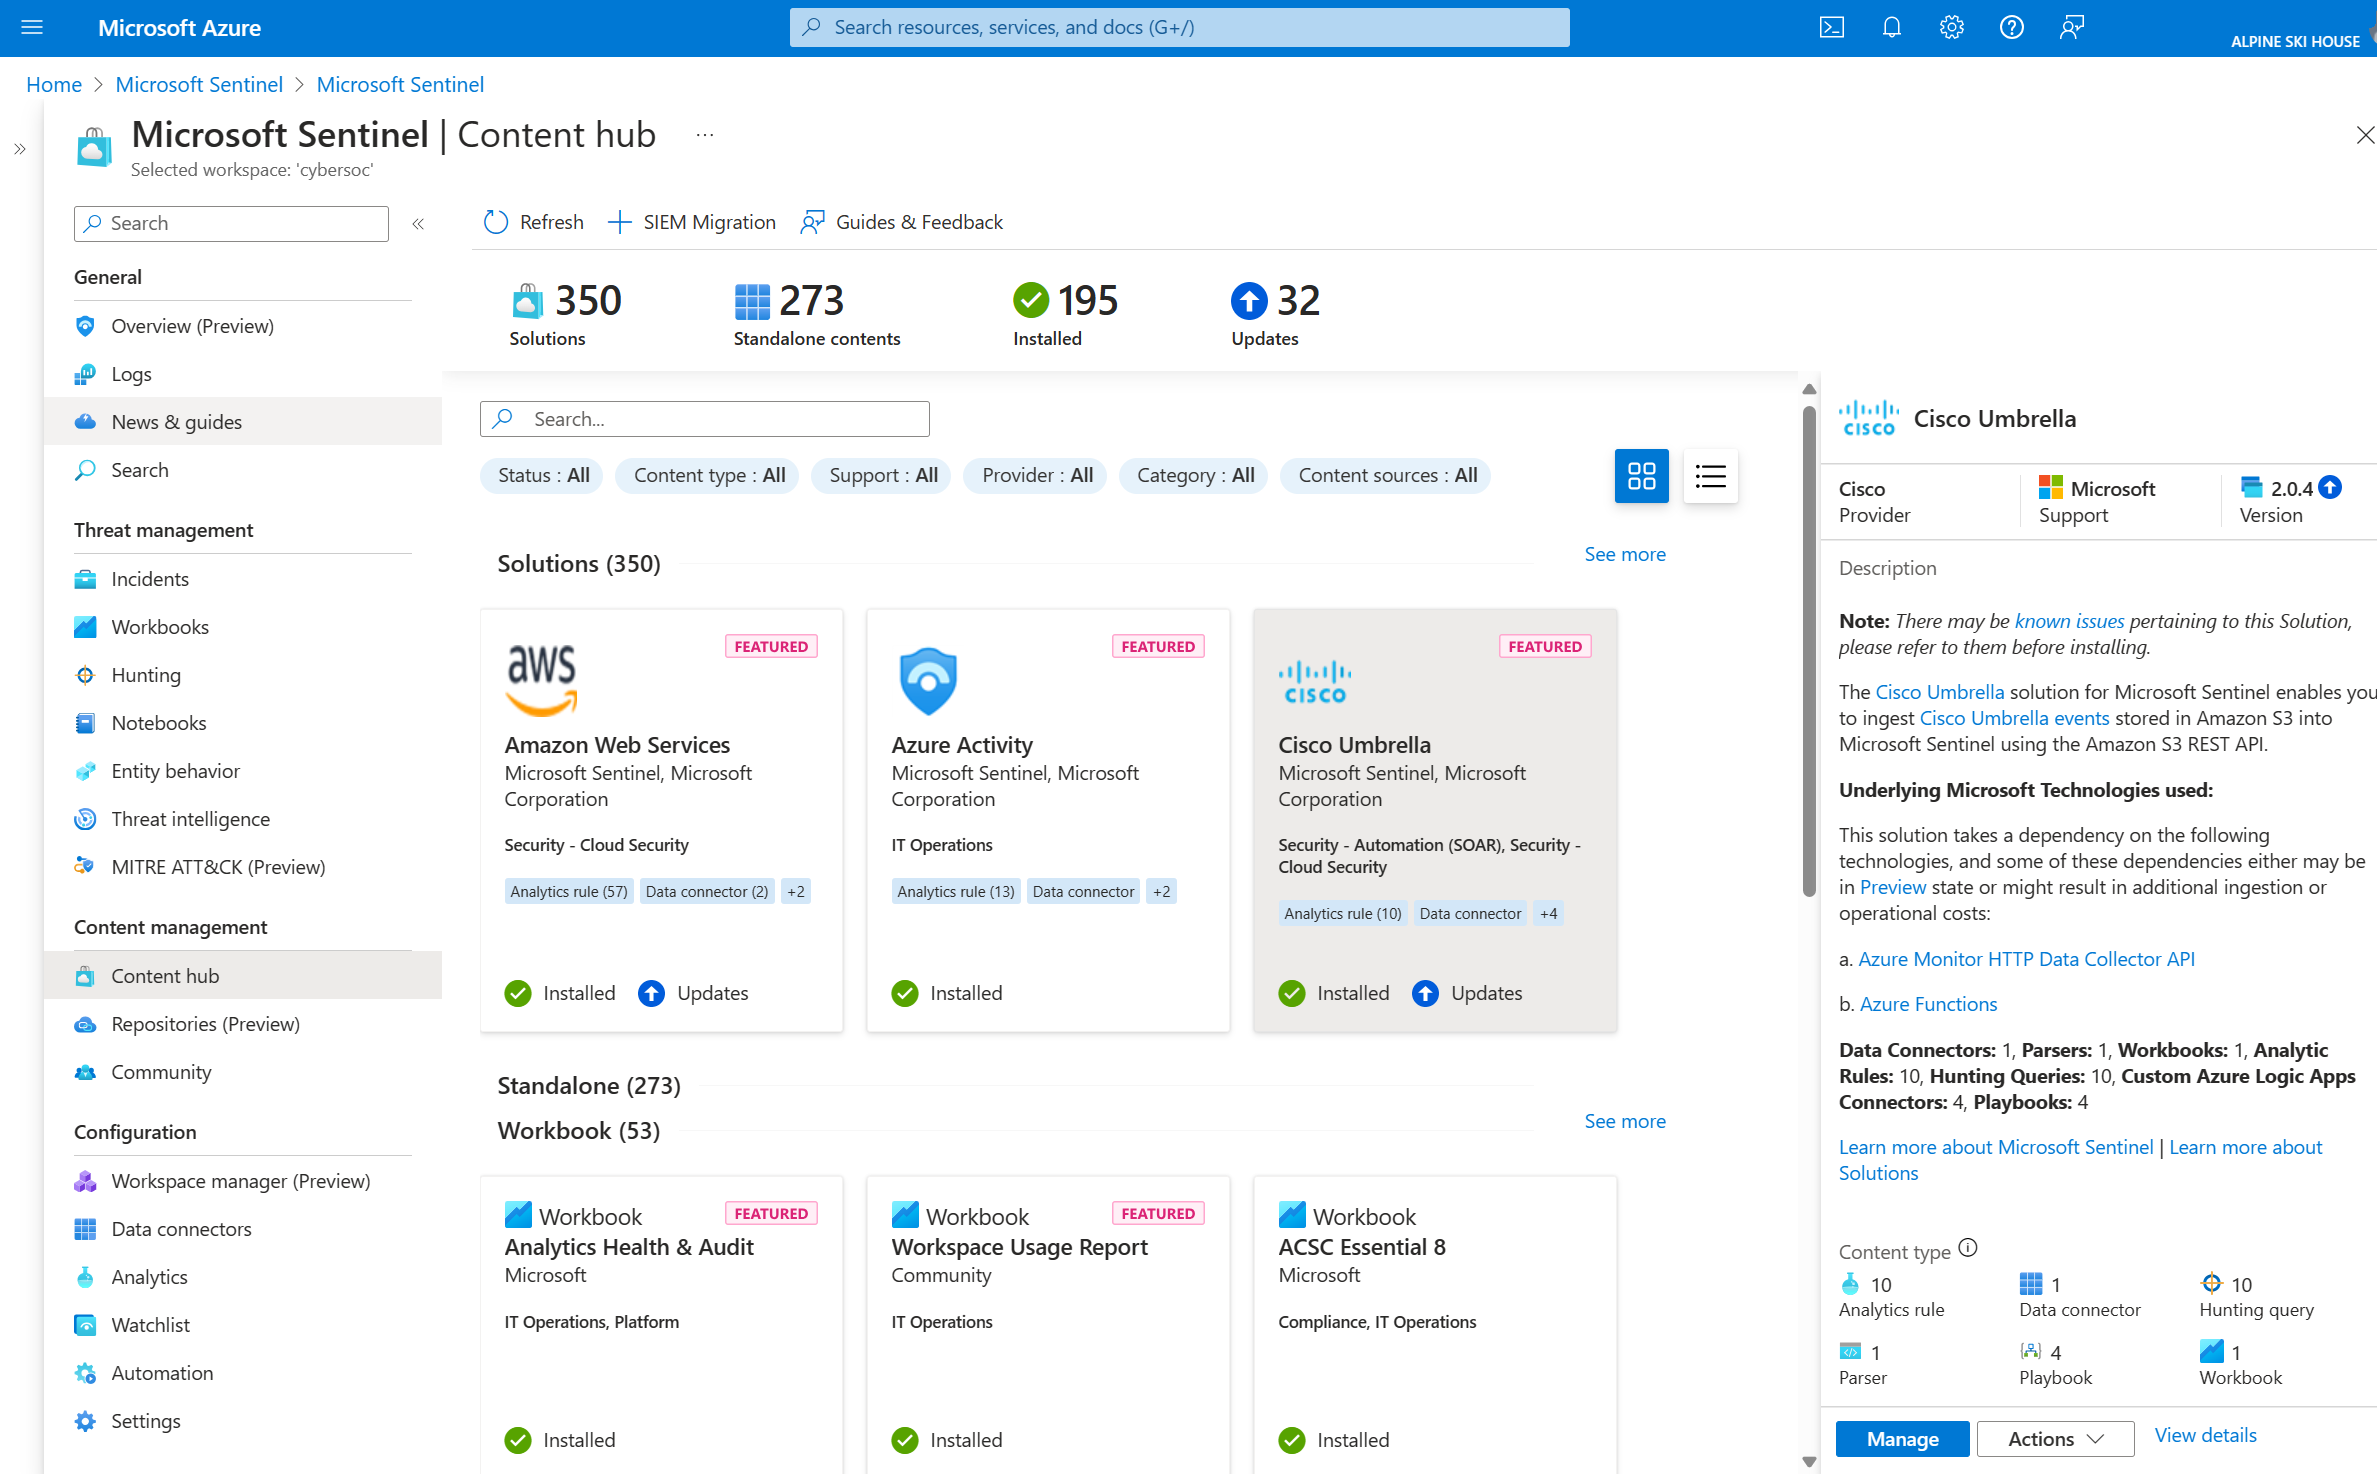
A fundamental aspect of any SIEM is its ability to ingest data from a wide range of sources. Microsoft Sentinel excels in this area, offering robust connectors for various Microsoft services (Azure, Microsoft 365, Microsoft Defender), as well as numerous third-party security solutions, operating systems, and cloud platforms. This ensures that security teams have a unified view of their entire digital footprint.
- Built-in Connectors: Sentinel offers a vast library of pre-built connectors that simplify the process of ingesting data from common security and IT sources. This includes cloud services like AWS and Google Cloud Platform, as well as on-premises systems and popular SaaS applications.
- Custom Connectors: For less common sources, Sentinel provides mechanisms to create custom connectors, ensuring that no critical data is left out of the security analysis.
- Scalable Storage: Leveraging Azure’s robust storage infrastructure, Sentinel can handle massive volumes of data, making it suitable for organizations of all sizes. Data can be retained for extended periods, aiding in forensic investigations and compliance requirements.
- Log Analytics Integration: At its core, Sentinel is built on Azure Monitor Logs, providing a powerful query language (Kusto Query Language – KQL) for detailed data exploration and analysis.
Threat Detection and Analytics
This is where Sentinel truly shines, moving beyond basic log correlation to employ advanced analytics and artificial intelligence.
- Built-in Analytics Rules: Sentinel comes with a comprehensive set of pre-defined analytics rules that leverage Microsoft’s extensive threat intelligence and behavioral analytics. These rules are designed to detect known attack patterns and suspicious activities across various threat vectors.
- Machine Learning (ML) and AI: Sentinel employs advanced ML algorithms to identify anomalies and detect threats that might be missed by traditional rule-based systems. This includes User and Entity Behavior Analytics (UEBA) capabilities that profile normal user and system behavior, flagging deviations that could indicate compromised accounts or insider threats.
- Custom Analytics Rules: Organizations can create their own custom analytics rules using KQL to tailor detection to their specific environment and unique risk profiles. This allows for highly targeted threat hunting.
- Threat Intelligence Integration: Sentinel seamlessly integrates with various threat intelligence feeds, both Microsoft’s and third-party sources, enriching alerts with context about known malicious indicators.
Incident Investigation and Workflow Automation
Once a threat is detected, the efficiency of the investigation and response process is critical. Sentinel streamlines this with its SOAR capabilities.
- Incident Management: Sentinel aggregates related alerts into incidents, providing a consolidated view for investigation. This helps reduce alert fatigue and allows analysts to focus on the most critical threats.
- Investigation Graph: A visually intuitive investigation graph allows analysts to explore the relationships between entities, alerts, and users involved in an incident, making it easier to understand the scope and impact of a compromise.
- Playbooks (Automation): Sentinel’s SOAR capabilities are powered by playbooks, which are automated workflows built using Azure Logic Apps. These playbooks can be triggered by alerts and can perform a wide range of actions, such as:
- Enriching alerts with data from threat intelligence platforms.
- Blocking IP addresses on firewalls.
- Disabling user accounts.
- Isolating infected endpoints.
- Sending notifications to relevant stakeholders.
- Built-in Playbooks: Sentinel offers a library of pre-built playbooks for common response scenarios, allowing organizations to get started with automation quickly.
- Custom Playbooks: Playbooks can be customized or built from scratch to align with an organization’s specific incident response procedures.
Threat Hunting and Proactive Security
Sentinel empowers security analysts to move beyond reactive incident response and proactively hunt for threats within their environment.
- Kusto Query Language (KQL): The powerful KQL allows analysts to perform deep dives into their security data, crafting complex queries to uncover hidden threats or validate hypotheses.
- Hunting Queries: Sentinel provides a rich set of pre-built hunting queries that can be used as starting points for proactive threat hunting. These queries are designed to look for indicators of compromise (IoCs) and suspicious behaviors.
- Data Exploration: The platform’s integrated data exploration tools make it easy to visualize and analyze security data, aiding in the discovery of anomalies and potential threats.
Benefits of Adopting Microsoft Sentinel
The adoption of Microsoft Sentinel offers a multitude of benefits for organizations looking to strengthen their security posture.
Cloud-Native Scalability and Cost-Effectiveness
As a cloud-native service, Sentinel offers unparalleled scalability to handle the ever-increasing volume of security data. Organizations avoid the significant capital expenditure and operational overhead associated with managing on-premises SIEM hardware. Pricing is consumption-based, allowing organizations to scale their usage and costs as needed.
Unified SIEM and SOAR Capabilities
The integration of SIEM and SOAR functionalities into a single platform simplifies security operations. This eliminates the need to manage separate tools, reduces integration complexities, and streamlines workflows, leading to faster incident response times and improved operational efficiency.
Enhanced Threat Detection with AI and ML
The advanced analytics, machine learning, and AI capabilities in Sentinel enable the detection of sophisticated threats that traditional security solutions might miss. This proactive approach helps organizations stay ahead of evolving cyberattack techniques.
Reduced Alert Fatigue and Improved Analyst Productivity
By consolidating alerts into incidents and providing powerful investigation tools, Sentinel helps reduce the burden on security analysts. Automated response actions further free up analyst time, allowing them to focus on higher-value tasks and strategic security initiatives.
Comprehensive Visibility Across Hybrid and Multi-Cloud Environments
Sentinel’s ability to ingest data from a wide array of sources, including on-premises systems, Azure, Microsoft 365, and other cloud providers, provides a unified and comprehensive view of the security landscape. This is crucial for organizations operating in complex hybrid and multi-cloud environments.
Integration with the Microsoft Security Ecosystem
Sentinel integrates seamlessly with other Microsoft security products, such as Microsoft Defender for Endpoint, Microsoft Defender for Cloud, and Azure Active Directory. This deep integration enhances the effectiveness of threat detection and response by leveraging contextual data from across the Microsoft security stack.
Use Cases and Applications
Microsoft Sentinel is a versatile solution applicable to a wide range of security challenges faced by modern organizations.
Advanced Threat Detection and Response
This is the primary use case, where Sentinel’s SIEM and SOAR capabilities are employed to identify, investigate, and remediate security incidents in near real-time.
Compliance and Auditing
Sentinel’s robust data ingestion and retention capabilities facilitate compliance with various regulatory requirements by providing a comprehensive audit trail of security events.
Insider Threat Detection
By analyzing user and entity behavior, Sentinel can identify anomalous activities that may indicate malicious insider actions or compromised employee accounts.
Cloud Security Posture Management
Sentinel can be used to monitor cloud environments for misconfigurations, vulnerabilities, and policy violations, helping organizations maintain a strong security posture in the cloud.
Security Operations Center (SOC) Modernization
For organizations looking to modernize their SOC operations, Sentinel offers a cloud-native platform that enhances efficiency, automation, and threat intelligence.

Getting Started with Microsoft Sentinel
Implementing Microsoft Sentinel involves several key steps, from initial setup to ongoing operationalization.
- Provisioning a Sentinel Workspace: The first step is to deploy Microsoft Sentinel within an Azure subscription. This involves creating a dedicated Log Analytics workspace.
- Connecting Data Sources: Configure connectors to ingest data from relevant sources. This is a critical step to ensure comprehensive visibility.
- Configuring Analytics Rules: Enable built-in analytics rules and create custom rules to align with specific organizational needs.
- Developing Playbooks: Design and implement playbooks for automated incident response workflows.
- Training and Operationalization: Ensure security analysts are trained on using Sentinel for investigation, threat hunting, and managing automated responses.
Microsoft Sentinel represents the future of cloud-native security operations. By unifying SIEM and SOAR capabilities and leveraging the power of AI and machine learning, it empowers organizations to defend against the ever-evolving threat landscape with greater speed, efficiency, and intelligence.