
In the dynamic landscape of modern software development, where projects grow increasingly complex and demands for rapid innovation escalate, tools that streamline efficiency and promote collaboration are invaluable. Among these, the Node Package Manager (npm) stands out as a cornerstone for JavaScript-centric development, particularly in an era driven by web technologies, server-side applications, and increasingly, embedded systems and AI. At its heart, npm manages and distributes “npm packages”—a fundamental concept that underpins much of today’s technological advancement. Understanding what an npm package is, and its profound implications for technological innovation, is crucial for anyone navigating the current tech ecosystem.
The Foundation of Modern JavaScript Development
An npm package is essentially a self-contained module of JavaScript code, accompanied by a metadata file, designed to be shared and reused across different projects. While often associated with Node.js, npm also serves as a crucial package manager for front-end JavaScript frameworks and tools. It’s not merely a repository for code; it represents a systematic approach to managing project dependencies, fostering modularity, and enabling a global community of developers to build upon each other’s work.
The Role of Package Managers
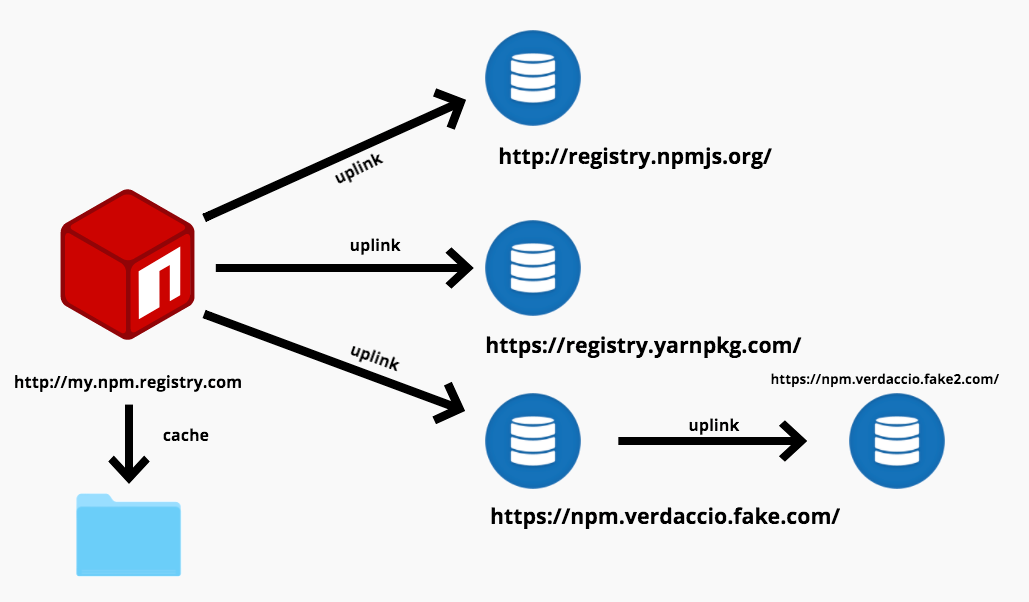
Before the advent of robust package managers like npm, developers often faced significant hurdles in managing external code. Integrating third-party libraries involved manual downloads, convoluted dependency tracking, and often, versioning conflicts that could cripple a project. Package managers like npm automate this entire process. They provide a centralized registry where packages are published, and a command-line interface (CLI) tool that allows developers to easily install, update, and manage these packages within their projects. This automation drastically reduces setup time, ensures consistency across development environments, and minimizes the risk of human error in dependency management. For any modern tech endeavor, from developing sophisticated web applications to building the backend for autonomous systems, efficient dependency management is non-negotiable for project scalability and maintainability.
Anatomy of an npm Package
A typical npm package consists of several key components that define its functionality and how it integrates into other projects. Primarily, it includes JavaScript code files (or files written in languages that compile to JavaScript, like TypeScript) that export specific functions, objects, or classes. These are the core logic units that the package provides. Crucially, every npm package must contain a package.json file at its root. This metadata file acts as the package’s manifest, detailing critical information such as:
name: The unique identifier for the package.version: Following semantic versioning (SemVer), this indicates the package’s current iteration, helping manage compatibility and updates.description: A brief summary of what the package does.main: Specifies the entry point file of the package when it’s required by another module.scripts: Defines custom commands that can be run via npm (e.g., for testing, building, or starting the application).dependencies: Lists other npm packages that this package relies on to function correctly. This is the heart of npm’s dependency management, creating a dependency tree.devDependencies: Lists packages needed only for development and testing, not for the production runtime.
This structured format ensures that any developer can quickly understand a package’s purpose, its dependencies, and how to use it, significantly lowering the barrier to entry for collaboration and reuse.
Fostering Innovation and Efficiency in Tech
The existence of npm packages, and the npm ecosystem itself, is a powerful driver of innovation and efficiency across the tech spectrum. By democratizing access to high-quality code modules and simplifying their integration, npm enables developers to focus on unique problem-solving rather than reinventing foundational components.
Code Reusability and Modularity
One of the most significant benefits of npm packages is the promotion of code reusability. Instead of writing every piece of functionality from scratch, developers can leverage a vast repository of pre-built, tested, and optimized modules. Need to parse dates? There’s a package for that. Want to make HTTP requests? Multiple robust packages are available. This modular approach means that complex applications are built by assembling smaller, manageable components, each solving a specific problem. This not only speeds up development but also improves code quality and reduces the likelihood of bugs, as commonly used packages are often peer-reviewed and rigorously tested by the community. For fields requiring rapid prototyping or iterative development, such as developing features for AI-powered autonomous systems or new sensing technologies, this modularity is indispensable.
Accelerated Development Cycles
The ability to quickly integrate existing solutions translates directly into accelerated development cycles. Instead of spending weeks or months building authentication systems, database connectors, or user interface components, developers can incorporate battle-tested packages in a matter of minutes. This allows development teams to bring products and features to market faster, respond more agilely to user feedback, and iterate on innovative ideas with greater velocity. In competitive tech sectors, where the first to innovate often gains a significant advantage, npm’s contribution to development speed is a critical factor. It shifts the focus from foundational implementation to higher-level architectural design and feature innovation.
Community Collaboration and Open Source
The npm ecosystem thrives on community collaboration, largely driven by the open-source ethos. The vast majority of npm packages are open source, meaning their code is publicly available, inspectable, and often, extensible. This fosters a vibrant environment where developers worldwide contribute to improving existing packages, identifying and fixing bugs, and creating new solutions. This collective intelligence leads to more robust, secure, and feature-rich tools than any single organization could produce in isolation. For emerging technologies, where standards are still evolving and complex challenges require diverse perspectives, this global collaborative model is a powerful engine for progress. It allows for rapid iteration and adaptation of software components to new requirements, such as those that might arise in advanced flight navigation or drone-based data processing.
Beyond Basic Libraries: Advanced Uses and Ecosystem Impact
While often thought of as simple code libraries, npm packages extend far beyond basic utility functions. They form the backbone of entire development frameworks, provide essential tooling, and enable the creation of highly sophisticated applications that power much of the modern digital world.
Command-Line Interface (CLI) Tools
Many powerful command-line interface tools are distributed as npm packages. These CLIs allow developers to automate tasks, scaffold new projects, interact with services, and manage various aspects of their development workflow directly from the terminal. Examples include build tools like Webpack, transpilers like Babel, project generators for frameworks like Angular or React, and tools for cloud service deployment. These CLI tools are crucial for streamlining development operations, enabling continuous integration/continuous deployment (CI/CD) pipelines, and generally boosting developer productivity, which is vital for managing complex tech projects.
Frameworks and Build Tools
Major JavaScript frameworks and libraries that define modern web development—such as React, Angular, and Vue.js—are themselves npm packages or collections of npm packages. Furthermore, the essential build tools that transform developer-friendly code into optimized, production-ready assets (e.g., minification, bundling, tree-shaking) are also predominantly distributed via npm. This interconnected ecosystem means that developers can easily pull in entire application architectures and sophisticated build processes with simple npm commands, allowing them to jumpstart complex projects with robust foundations. This capability is paramount for developing innovative interfaces and powerful data processing front-ends for any tech application, including those that might interface with drone systems or sensor data.
Enabling Complex Systems
The foundational nature of npm packages extends to enabling increasingly complex systems across various tech domains. On the server side, Node.js and its npm ecosystem are used to build highly scalable backend services, APIs, and microservices that power everything from social media platforms to IoT device management systems. For instance, the data ingestion and processing pipelines for remote sensing data or the backend services for drone fleet management could heavily rely on npm packages. Similarly, the rise of JavaScript in embedded systems and edge computing means that npm packages are increasingly finding their way into devices themselves, providing modularity and ease of development for software running on hardware platforms, including those within drones. Furthermore, many AI and machine learning tools and libraries, particularly those focused on JavaScript environments or web deployment of models, are also distributed through npm, pushing the boundaries of what can be achieved in AI-driven innovation.
The Developer’s Perspective: Best Practices and Security
While npm packages offer immense advantages, developers must also adhere to best practices to harness their power effectively and mitigate potential risks, particularly concerning project security and maintainability.
Managing Dependencies
Effective dependency management goes beyond simply installing packages. Developers need to understand how to specify dependency versions (^ for compatible updates, ~ for patch updates, or exact versions) to balance stability with access to new features and security patches. The package-lock.json file, automatically generated by npm, is critical for ensuring deterministic installations across different environments, guaranteeing that everyone on a team (or in a CI/CD pipeline) uses the exact same versions of all dependencies. This precision is essential for robust and reliable deployments, especially for mission-critical applications where consistency is paramount.
Versioning and Compatibility
Semantic Versioning (SemVer) is a critical convention that npm strongly encourages for packages. It provides a clear way to communicate the nature of changes in each new release:
- MAJOR version (1.0.0): Incompatible API changes.
- MINOR version (0.1.0): Backward-compatible new functionality.
- PATCH version (0.0.1): Backward-compatible bug fixes.
Understanding SemVer allows developers to confidently update packages, knowing whether an update might break existing code. Maintaining compatibility and understanding the impact of version changes is vital for the long-term health and innovation trajectory of any software project.
Security Considerations in the npm Ecosystem
The vastness and open nature of the npm ecosystem, while a strength, also present security challenges. Malicious packages, vulnerabilities in legitimate packages, and supply chain attacks are persistent threats. Developers must practice due diligence:
- Audit dependencies: Regularly scan for known vulnerabilities using tools like
npm audit. - Review package popularity and maintainers: Prefer well-maintained, widely used packages from trusted sources.
- Minimize dependencies: Only include necessary packages to reduce the attack surface.
- Keep dependencies updated: Timely updates patch security flaws.
Addressing security proactively is not just good practice; it’s a fundamental responsibility for anyone building technology in an interconnected world, particularly for systems handling sensitive data or controlling physical hardware.
The Future of npm and Software Innovation
The npm ecosystem continues to evolve, adapting to new technologies and developer needs. As JavaScript solidifies its role across various domains—from web and mobile to desktop, IoT, and machine learning—npm’s importance as a central pillar of software innovation will only grow.
Evolving Standards and Tooling
The npm CLI and registry constantly receive updates, improving performance, security features, and developer experience. The JavaScript language itself, through its ECMAScript standardization process, introduces new features regularly, and npm facilitates the adoption of these new standards through transpilers and polyfills. Tools built around npm, such as module bundlers and testing frameworks, are also continuously innovated upon, further enhancing the capabilities and efficiency of JavaScript development. This constant evolution ensures that the npm ecosystem remains at the forefront of software development trends.

Impact on Emerging Technologies
npm packages are not just for web development anymore. They are instrumental in the growth of new technological frontiers. The rise of JavaScript-driven IoT platforms, for example, means that npm packages can abstract away hardware interactions, making it easier to prototype and deploy smart devices. In the realm of AI and machine learning, particularly with the proliferation of JavaScript-based libraries for client-side model inference (e.g., TensorFlow.js), npm facilitates the rapid development and deployment of intelligent applications. For areas like advanced robotics, autonomous systems, or sophisticated data processing pipelines for new sensor technologies, the modularity, reusability, and community-driven innovation provided by npm packages are fundamental enablers, allowing developers to build sophisticated and reliable software solutions faster than ever before. In essence, npm packages are the atomic units of innovation in the modern software world, allowing complex technological visions to be realized through collaborative, efficient, and scalable development practices.