
Understanding the Core Concept of Encrypting File Systems (EFS)
An Encrypting File System (EFS) is a powerful security feature that enables files and folders to be transparently encrypted on a storage volume. Unlike full disk encryption (FDE), which encrypts an entire drive or partition, EFS operates at a more granular level, allowing users to select specific files or directories for encryption. The defining characteristic of EFS is its transparency: once configured, the encryption and decryption processes occur automatically in the background as an authorized user accesses or saves files. This means an authorized user works with encrypted files as if they were unencrypted, without needing to manually decrypt them each time.
The primary purpose of EFS is to provide data confidentiality and integrity, protecting sensitive information from unauthorized access, even if the physical storage medium is compromised or stolen. For instance, if a laptop or server drive containing encrypted files is removed and connected to another system, the files remain unreadable without the correct decryption keys. This stands in contrast to merely setting permissions, which can often be bypassed by an attacker with direct access to the storage. In the rapidly evolving landscape of Tech & Innovation, where vast quantities of proprietary algorithms, highly sensitive sensor data, and personally identifiable information (PII) are generated by AI models, autonomous systems, remote sensing platforms, and advanced mapping operations, EFS offers a critical layer of protection. This data, whether in development, transit, or at rest, represents invaluable intellectual property or carries significant privacy implications, necessitating robust safeguards against unauthorized disclosure or theft.
How Encrypting File Systems Work
The underlying mechanisms of an Encrypting File System blend symmetric and asymmetric cryptography, integrated seamlessly into the operating system’s file management layer. This sophisticated interplay ensures both strong encryption and transparent user experience.
The Encryption Process
When a user initiates the encryption of a file or folder using EFS, a specific sequence of events unfolds:
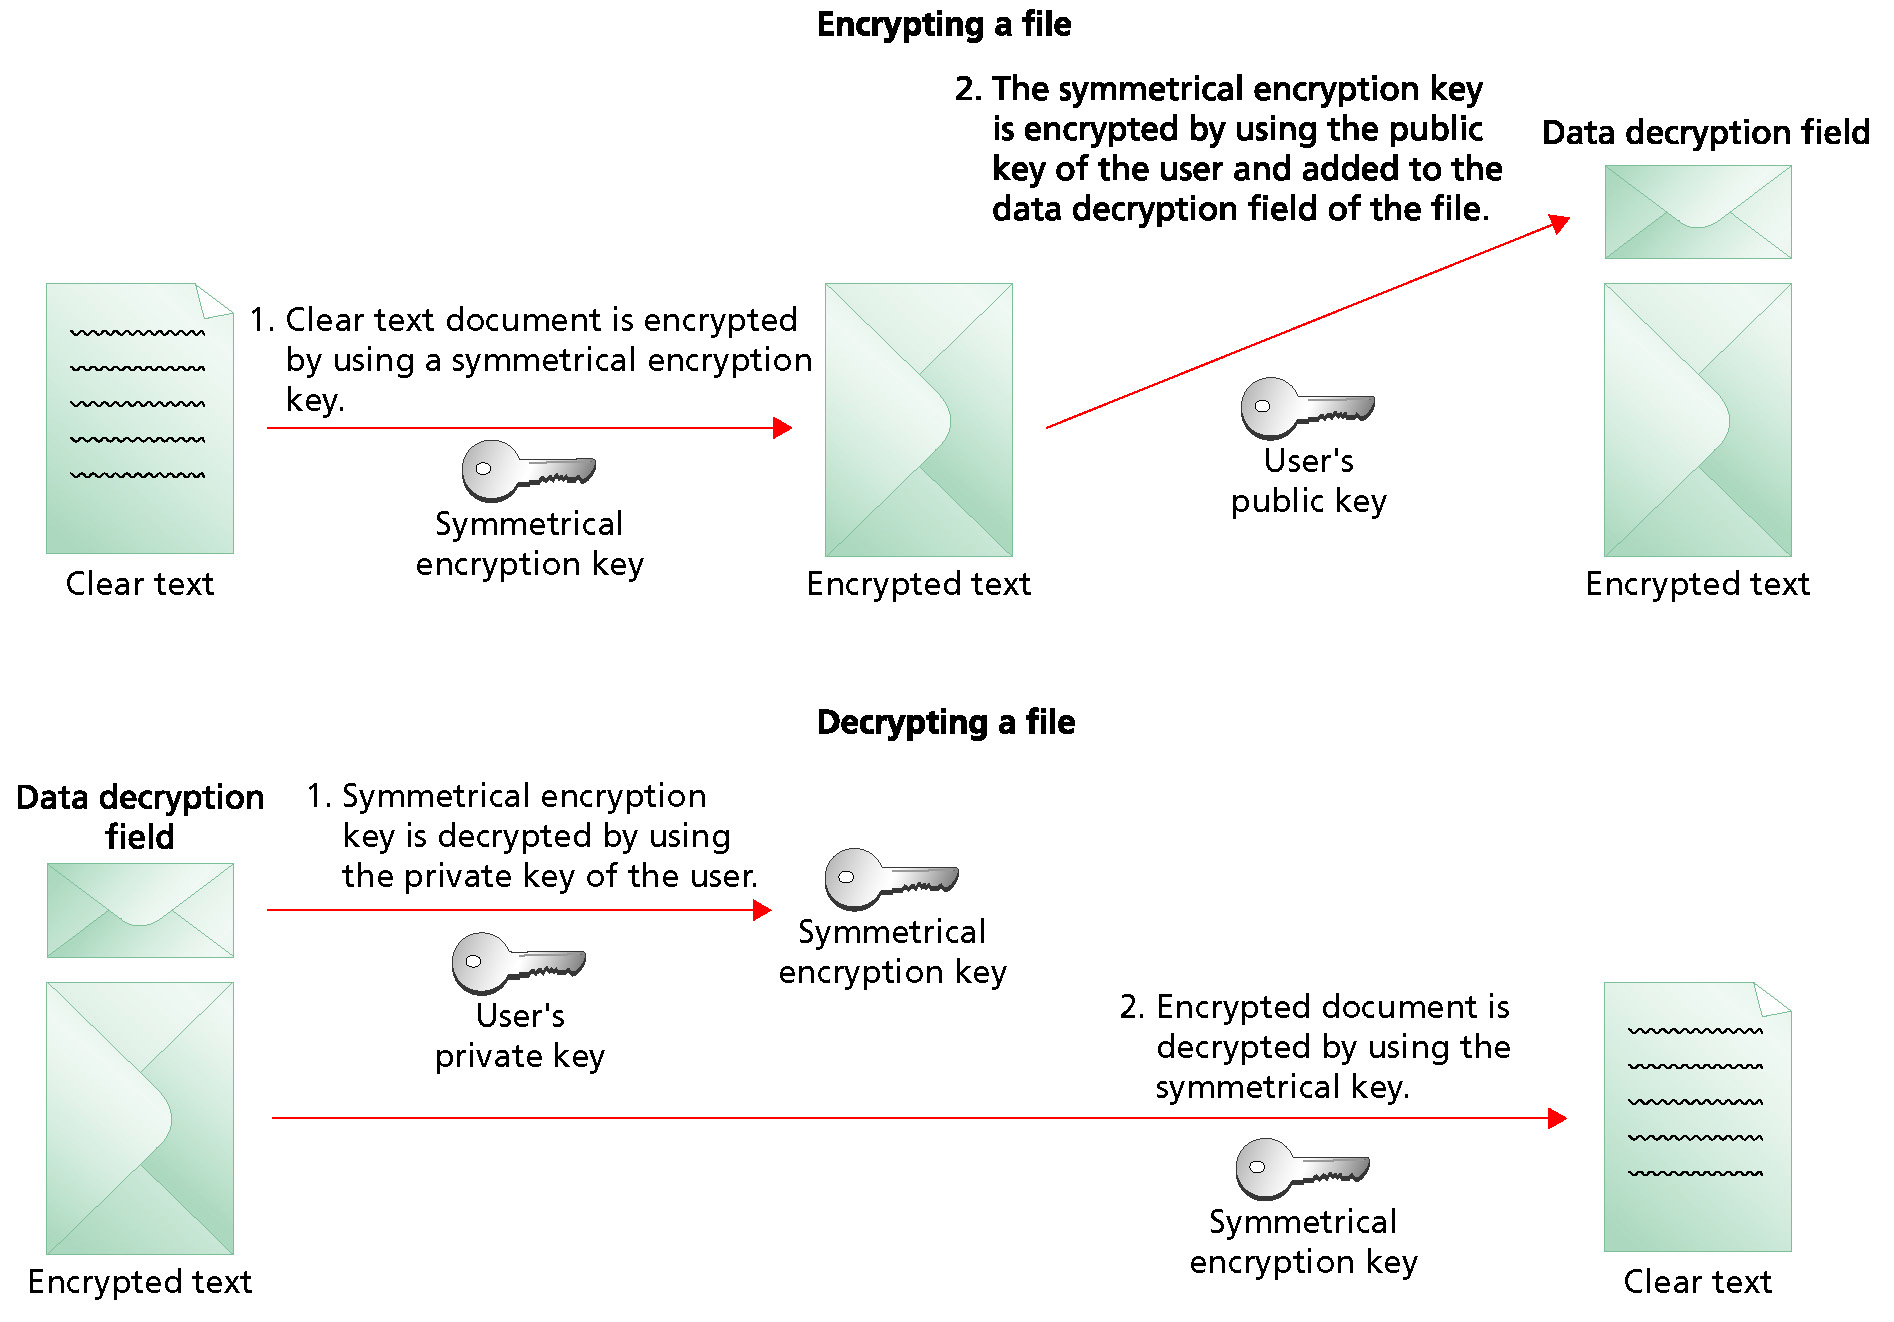
- File Encryption Key (FEK) Generation: For each file chosen for encryption, EFS generates a unique, random symmetric key known as the File Encryption Key (FEK). This FEK is solely responsible for encrypting the actual data content of that specific file. Using a unique FEK per file enhances security, as compromising one FEK does not compromise other files.
- Data Encryption: The FEK is then used with a robust symmetric encryption algorithm, commonly AES-256, to encrypt the raw data of the file. Symmetric encryption is chosen for this step due to its speed and efficiency in handling large data volumes.
- FEK Encryption: To secure the FEK itself, it is encrypted using the public key from the user’s personal digital certificate. This certificate is unique to the user who encrypted the file. This step employs asymmetric encryption, where the public key encrypts the FEK, and only the corresponding private key can decrypt it.
- Storage: The encrypted FEK, along with other metadata like the user’s certificate thumbprint, is stored as an extended attribute or within a dedicated metadata stream alongside the encrypted file. The original, unencrypted FEK is never stored directly.
The Decryption Process
When an authorized user attempts to access an encrypted file, EFS performs the following transparently:
- FEK Retrieval: The operating system detects that the file is encrypted and retrieves the encrypted FEK from the file’s metadata.
- FEK Decryption: Using the accessing user’s private key (which corresponds to the public key used during encryption and is securely stored, often protected by a password or hardware token), EFS decrypts the FEK. This is where user authentication plays a crucial role; without access to the correct private key, the FEK cannot be decrypted.
- Data Decryption: Once the FEK is successfully decrypted, it is then used to decrypt the file’s content, making it readable and usable by the application or user. This entire process happens within the operating system’s kernel, imperceptible to the user.
Key Management and Certificates
EFS relies heavily on a robust Public Key Infrastructure (PKI) for managing user identities and encryption keys. Each user authorized to encrypt or decrypt files possesses a unique digital certificate containing a public/private key pair. The private key is paramount for decryption and must be kept secure.
For enterprise environments, a critical component is the Data Recovery Agent (DRA) certificate. Designated DRAs are equipped with a special certificate whose public key is also used to encrypt the FEK of every file encrypted within the organization. This allows DRAs, possessing the corresponding private key, to decrypt any EFS-encrypted file, ensuring business continuity and data access even if an employee leaves or loses their private key. Without proper key management, including secure storage, backup, and recovery mechanisms for private keys and DRA certificates, encrypted data can become permanently inaccessible.
The Imperative for EFS in Modern Tech & Innovation
In an era defined by rapid technological advancements, the security of digital assets is not merely a best practice but a fundamental necessity. Encrypting File Systems play a pivotal role in protecting the sensitive data generated and processed by cutting-edge innovations in AI, autonomous systems, mapping, and remote sensing.
Safeguarding Proprietary Algorithms and Intellectual Property
The core value of many tech companies lies in their proprietary algorithms, machine learning models, and unique datasets. In the realm of AI and autonomous systems, these assets represent years of research and development, forming the very foundation of competitive advantage. EFS serves as a crucial defense mechanism against industrial espionage, internal theft, or unauthorized replication. Whether these intellectual properties reside on developer workstations, training servers, edge devices, or cloud storage, EFS ensures that the underlying code, model weights, and sensitive data remain encrypted at rest. This protection is vital for maintaining market leadership and preventing the compromise of unique capabilities that drive innovation.
Ensuring Data Privacy and Regulatory Compliance
Modern innovations in remote sensing and advanced mapping frequently involve the collection and analysis of vast quantities of data that can contain highly sensitive information, including geographical features, critical infrastructure details, or even inferred personal identifiable information (PII) from high-resolution imagery. Global regulatory frameworks such as GDPR, HIPAA, CCPA, and various national data protection acts impose stringent requirements for the protection of such data. EFS provides a foundational, technical layer of security to meet these compliance mandates by encrypting data at rest. By ensuring that sensitive data is unreadable to unauthorized parties, organizations can significantly mitigate the risks of data breaches, avoid costly penalties, and maintain trust with their users and partners.
Securing Edge Computing and IoT Devices
The proliferation of edge computing, exemplified by drones, autonomous vehicles, and a wide array of smart sensors, means that critical data collection and initial processing often occur outside traditional secure data centers. These devices, by their very nature, are physically distributed and thus more susceptible to loss, theft, or tampering. EFS offers an indispensable layer of security for the local storage on these edge nodes. Should an autonomous vehicle’s onboard computer or a drone’s storage module be compromised, lost, or stolen, EFS ensures that the collected sensor data, operational logs, or navigation maps stored on its local file system remain unreadable without the proper decryption keys, thereby preventing data exfiltration and intellectual property loss.
Protecting Against Insider Threats and Physical Breaches
While network security measures primarily focus on thwarting external cyber threats, EFS provides critical defense against a different class of risks: insider threats and physical breaches. It safeguards against scenarios where authorized personnel might misuse their access to sensitive files or where physical storage media (e.g., hard drives from decommissioned servers, lost external drives, or stolen laptops) fall into the wrong hands. For innovation hubs and R&D departments dealing with cutting-edge prototypes and confidential data, EFS ensures that even if physical access is gained, the data remains cryptographically protected. This comprehensive approach to data security acknowledges that threats can originate from multiple vectors, both digital and physical.
Benefits and Challenges of Implementing EFS
Integrating an Encrypting File System into an organization’s security posture offers substantial advantages but also introduces complexities that require careful management. Understanding both sides is crucial for effective deployment, particularly in data-intensive and innovation-driven environments.
Benefits
- Granular Data Protection: A key advantage of EFS is its ability to encrypt individual files or folders, rather than an entire disk. This provides fine-grained control, allowing organizations to classify data sensitivity and apply encryption only where necessary. This flexibility is invaluable for environments handling diverse datasets, from publicly available information to highly confidential R&D specifics.
- Enhanced Security Posture: EFS significantly strengthens an organization’s overall security by protecting data at rest from unauthorized access, even in scenarios involving physical theft of devices or storage media. This reduces the attack surface and mitigates the impact of potential breaches.
- Regulatory Compliance: By ensuring data is encrypted at rest, EFS helps organizations meet a wide array of data protection and privacy regulations (e.g., GDPR, HIPAA, CCPA). It provides a verifiable technical control that demonstrates due diligence in protecting sensitive information.
- User Transparency: Once configured and integrated into the operating system, EFS operates seamlessly in the background. Users rarely need to interact directly with the encryption process, making it unintrusive and promoting user adoption without disrupting workflows.
- Access Control Integration: EFS inherently integrates with existing user authentication and authorization systems. Access to encrypted files is directly linked to the user’s login credentials and certificate, ensuring that only authenticated and authorized individuals can decrypt and read the data.
Challenges
- Performance Overhead: Encryption and decryption are computationally intensive processes. While modern CPUs often include hardware acceleration for cryptographic operations, EFS can still introduce a performance penalty, especially for large files, high-frequency access patterns, or on systems with limited resources. This consideration is vital for applications dealing with real-time sensor data or large-scale AI model training.
- Key Management Complexity: The core strength of EFS – its reliance on digital certificates and cryptographic keys – is also its greatest challenge. Securely generating, storing, backing up, and recovering private keys and Data Recovery Agent (DRA) certificates is paramount. Loss of a private key without a proper recovery mechanism (like a DRA or a secure key escrow system) will lead to irreversible data loss. Organizations must implement robust PKI management policies and infrastructure.
- Compatibility Issues: While EFS is a standard feature on major operating systems (e.g., Windows EFS), its specific implementations can vary. Moving EFS-encrypted files between different operating systems or disparate EFS versions can pose compatibility challenges, requiring careful planning or decryption before transfer.
- Backup and Recovery Considerations: Encrypted files must be backed up along with their corresponding recovery keys. Backing up only the encrypted files without the means to decrypt them renders the backups useless. Implementing secure backup strategies that account for key management is critical for disaster recovery.
- Potential for Misconfiguration: Incorrect setup or lax policy enforcement can undermine the security benefits of EFS. For instance, storing private keys on the same unencrypted drive as the data, or failing to designate DRAs, can leave data vulnerable or irrecoverable. Comprehensive training and strict policy adherence are essential.
Future Trends and Integration of EFS in Advanced Tech Ecosystems
As technology continues its relentless march forward, the landscape of data security, and specifically Encrypting File Systems, must evolve in tandem. EFS is poised to become even more deeply integrated and sophisticated to meet the demands of emerging tech ecosystems.
Cloud Integration and Hybrid Environments
The shift towards cloud computing for AI model training, vast data storage from remote sensing, and distributed autonomous system management means EFS solutions must extend beyond traditional on-premises file systems. Future EFS implementations will feature seamless integration with cloud key management services (KMS), providing unified control over encryption keys across hybrid environments. This ensures that data remains protected whether it resides on local servers, public cloud storage, or edge devices, enabling consistent security policies across complex, multi-cloud architectures.
Blockchain and Decentralized Identity
Emerging technologies like blockchain hold promise for revolutionizing key management and access control within EFS. Decentralized identity solutions could provide more robust, tamper-proof mechanisms for managing user certificates and private keys, reducing reliance on centralized authorities. Furthermore, blockchain’s immutable ledger could offer an unprecedented level of auditability for file access and decryption events, enhancing transparency and accountability, particularly critical for sensitive data in regulated industries.
Post-Quantum Cryptography Integration
The advent of quantum computing poses a long-term threat to current public-key cryptographic algorithms, which form the bedrock of EFS’s key management. To safeguard data over the decades, EFS implementations will need to integrate post-quantum cryptographic (PQC) algorithms. This proactive shift will ensure that the confidentiality of critical innovation data, from long-term research projects to mapping archives, remains uncompromised against future quantum attacks.
Hardware-Accelerated Encryption and Efficiency
To overcome the performance overhead inherent in encryption, future EFS systems will increasingly leverage dedicated hardware encryption engines found in modern CPUs (e.g., Intel AES-NI, ARMv8 Cryptography Extensions). This hardware acceleration enables cryptographic operations to be executed significantly faster and more efficiently, making EFS more viable for high-performance computing tasks, real-time data processing, and high-throughput data streams common in AI inference and remote sensing data acquisition.
Automated Policy Enforcement and AI-Driven Security
The sheer volume and diversity of data generated by advanced tech necessitate intelligent security solutions. Future EFS systems will integrate more deeply with AI-driven security platforms to automatically classify data sensitivity, apply appropriate encryption policies based on content or context, and dynamically adjust access controls. This intelligent automation will allow EFS to react proactively to identified threats or anomalies in data access patterns, enhancing the overall security posture with minimal human intervention, particularly crucial for managing vast and evolving datasets.
Zero-Trust Architectures
EFS is a cornerstone of the zero-trust security model. In a zero-trust environment, no user or device is inherently trusted, regardless of their location on the network. EFS ensures that even if a network perimeter is breached, or an insider gains unauthorized network access, data at rest remains cryptographically protected, requiring explicit verification for every access attempt. This principle is vital for securing the highly distributed and interconnected components of modern tech ecosystems, from remote sensing platforms to autonomous vehicle fleets.