
In the vast and ever-expanding digital landscape, the security of personal information and online transactions has become paramount. Companies like Amazon, which handle billions of customer interactions and vast quantities of sensitive data daily, deploy sophisticated security protocols to safeguard their users. Central to these defenses is the One-Time Password (OTP), a dynamic security measure that adds a crucial layer of protection. An Amazon OTP number is precisely this: a unique, time-sensitive code generated by Amazon and sent to a user’s registered mobile device or email address, designed to verify their identity during critical actions such as logging in, authorizing a purchase, or making changes to their account. It’s a critical component of multi-factor authentication (MFA), a standard in modern digital security architecture that significantly mitigates the risks associated with compromised passwords or unauthorized access.
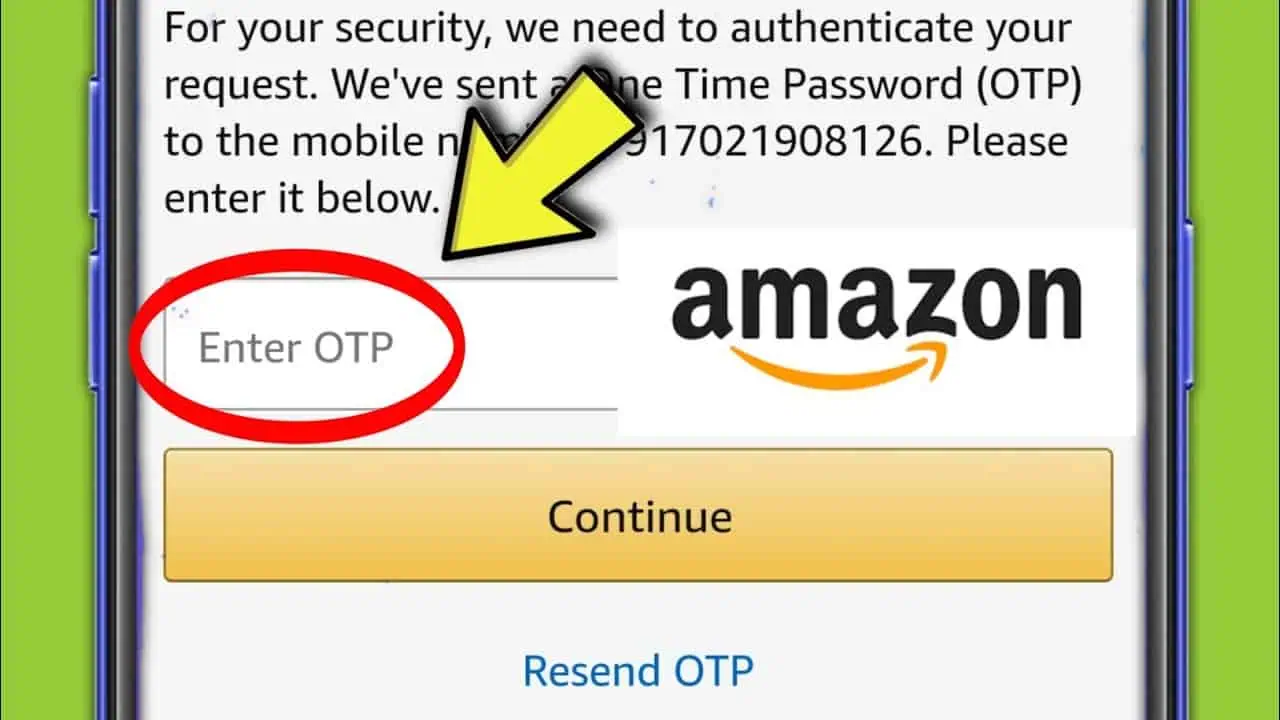
The Core of Digital Security: Understanding OTPs
One-Time Passwords represent a significant advancement over static password systems. While a traditional password remains constant until changed by the user, an OTP is ephemeral, valid for only a single login session or transaction, and typically expires within a very short timeframe, often just a few minutes. This transient nature is its greatest strength, rendering it useless to an attacker even if intercepted, as it cannot be reused.
How One-Time Passwords Function
The mechanics of an OTP system are rooted in cryptographic principles and real-time communication. When a user initiates an action requiring an OTP – for instance, attempting to log into their Amazon account from a new device – the system does not immediately grant access based solely on the username and static password. Instead, it triggers the generation of a unique, random alphanumeric code. This code is then transmitted via a trusted channel, usually an SMS message to the user’s registered mobile phone number or an email to their verified address. The user must then retrieve this code and enter it into the Amazon platform within the allotted time. Only upon successful validation of this OTP, in conjunction with the correct username and password, is access granted or the transaction approved. This process ensures that anyone attempting to access the account must not only know the static credentials but also possess the registered device or access the registered email account.
The Imperative of Multi-Factor Authentication (MFA)
OTPs are a cornerstone of Multi-Factor Authentication (MFA), a security paradigm that requires users to provide two or more verification factors to gain access to an account or system. These factors typically fall into three categories:
- Something you know: This is traditionally a password or PIN.
- Something you have: This includes a physical token, a mobile phone (receiving an OTP), or a smart card.
- Something you are: This refers to biometric data like fingerprints, facial recognition, or iris scans.
Amazon’s use of OTPs primarily leverages the “something you have” factor. By combining a password (something you know) with an OTP delivered to your phone (something you have), Amazon ensures that even if a malicious actor manages to obtain your password through phishing or data breaches, they cannot access your account without also having physical possession of your registered mobile device or access to your email, thereby dramatically increasing the security barrier. MFA, with OTPs at its core, is no longer just an optional security feature but a fundamental requirement in protecting sensitive online accounts in today’s interconnected world.
Amazon’s Implementation of OTPs: A Layered Defense
As one of the world’s largest e-commerce and cloud computing platforms, Amazon’s security infrastructure is designed to withstand a constant barrage of threats. OTPs are strategically integrated into various critical junctures of the user experience to provide robust protection where it matters most. This layered approach ensures that security is not a single point of failure but a resilient system of interconnected safeguards.
Securing Logins and Account Access
The most common scenario where users encounter an Amazon OTP is during the login process, particularly when logging in from an unrecognized device or location. When Amazon’s security algorithms detect unusual activity, such as a login attempt from a new browser, an unfamiliar IP address, or a geographically distant location, it may prompt the user for an OTP. This proactive measure prevents unauthorized access even if a user’s primary password has been compromised. Furthermore, Amazon allows users to explicitly enable Two-Step Verification (their term for MFA), which mandates an OTP for every login, providing an even higher level of security for those who choose it. This system acts as a digital bouncer, ensuring that only the legitimate account holder can enter, even if their “key” (password) has been stolen.
Protecting Transactions and Sensitive Information
Beyond initial account access, Amazon also deploys OTPs to secure high-value transactions or sensitive account modifications. For instance, if a user attempts to update their payment methods, change their shipping address to a new location, or make a large purchase that deviates from their typical spending patterns, Amazon may trigger an OTP verification. This step provides an additional layer of assurance that the person making these changes or authorizing these payments is indeed the account owner, preventing fraudulent activity and protecting financial data. This real-time, dynamic verification is crucial for an e-commerce giant where financial transactions are constantly flowing.
The User Experience Perspective

While security is paramount, Amazon also strives to balance robust protection with a streamlined user experience. The implementation of OTPs is generally designed to be as unobtrusive as possible, only appearing when truly necessary or when a user has opted for maximum security. The process of receiving and entering an OTP is typically quick and intuitive, ensuring that the added security doesn’t become a significant hurdle to legitimate users. Clear on-screen instructions guide users through the process, and mechanisms are in place for users to resend OTPs if the initial message is delayed. This focus on user experience ensures that the security measures are adopted and utilized effectively, rather than bypassed due to frustration.
Beyond the Basics: The Broader Tech Landscape of Authentication
The evolution of OTPs within platforms like Amazon is part of a larger, ongoing technological arms race between security providers and malicious actors. As cyber threats become more sophisticated, so too must the methods used to protect digital identities and assets. The principles underpinning OTPs are constantly being refined and integrated with other innovative technologies to create even more resilient authentication systems.
Evolving Threats and Adaptive Security Measures
Cybercriminals are continuously devising new methods to circumvent security measures, from advanced phishing campaigns that mimic legitimate websites to sophisticated malware designed to intercept communications. In response, tech giants like Amazon must employ adaptive security measures. This includes leveraging machine learning algorithms to detect anomalous behavior patterns that might indicate a breach attempt, automatically escalating security requirements (like an OTP prompt) when such anomalies are detected. For example, if a user’s login history shows consistent access from New York, but an attempt suddenly originates from a different continent, an OTP request becomes a critical verification step that prevents immediate compromise. The dynamism of OTPs makes them particularly effective against many common attack vectors, as they don’t rely on static, easily compromisable information.
The Future of Authentication: Biometrics and Beyond
While OTPs remain a powerful tool, the future of authentication is moving towards even more integrated and seamless methods. Biometric authentication, utilizing unique physical or behavioral characteristics such as fingerprints, facial recognition, or voice patterns, is gaining widespread adoption. Many smartphones and devices now feature integrated biometric scanners, making “something you are” factors increasingly accessible and convenient. For Amazon, this could mean future integrations where an OTP is supplemented or even replaced by a quick facial scan or fingerprint match for certain high-security actions. Furthermore, technologies like FIDO (Fast IDentification Online) alliances are pushing for “passwordless” authentication, where cryptographic keys stored securely on devices replace traditional passwords and OTPs, offering a more secure and user-friendly experience. The goal is to move towards systems that are not only more secure but also less burdensome for the user.
The Role of AI in Fraud Detection and Prevention
Artificial Intelligence (AI) plays an increasingly critical role in making authentication systems, including OTPs, more effective. AI algorithms can analyze vast datasets of user behavior, transaction histories, network patterns, and known fraud indicators in real-time. This allows platforms like Amazon to identify suspicious activities that deviate from a user’s typical profile with remarkable accuracy. If an AI system flags a transaction or login attempt as potentially fraudulent, it can automatically trigger additional security checks, such as an OTP, even if the primary login credentials appear correct. AI can also help detect sophisticated phishing attempts by analyzing email content and sender reputation, further fortifying the entire security ecosystem around OTP delivery and usage.
Best Practices for Users in an OTP-Enabled World
While companies like Amazon invest heavily in sophisticated security technologies, the ultimate effectiveness of OTPs and other authentication methods also depends significantly on user vigilance and adherence to best practices. Users are the first line of defense, and understanding how to protect their part of the security chain is crucial.
Safeguarding Your Mobile Device
Since OTPs are typically delivered to your mobile phone, the security of that device is paramount. Ensure your phone is protected with a strong passcode, biometric lock (fingerprint or facial recognition), or both. Keep your phone’s operating system and apps updated to patch security vulnerabilities. Be wary of public Wi-Fi networks for sensitive transactions, as they can sometimes be compromised. If your phone is lost or stolen, immediately contact your mobile carrier to suspend service and inform Amazon to temporarily lock your account or disable OTP delivery to that device.
Recognizing Phishing Attempts
Scammers frequently attempt to trick users into divulging their OTPs through elaborate phishing schemes. These often involve fake websites or emails that mimic Amazon’s official communications, asking you to “verify” your account by entering an OTP. Always double-check the sender’s email address and the website URL to ensure they are legitimate. Amazon will never ask you to provide an OTP outside of its official login or transaction pages. Be skeptical of unsolicited messages that create a sense of urgency or threaten account closure if you don’t act immediately. If in doubt, navigate directly to Amazon’s official website rather than clicking links in suspicious emails.

Regular Security Audits
Periodically review your security settings on Amazon and other important online accounts. Enable Two-Step Verification (MFA) on all platforms that offer it. Check your registered mobile number and email address to ensure they are current and secure. Review your recent order history and login activity for any unauthorized actions. Changing your primary password periodically, especially if you suspect it might have been exposed in a data breach, also adds a layer of proactive security. By taking these simple yet effective steps, users can significantly enhance their personal digital security posture in an era where an Amazon OTP number is a common, yet critical, gatekeeper to their online identity and assets.