
In the vast and interconnected digital landscape, where information flows freely across borders and devices, the concept of trust is paramount. A website certificate, often known by its underlying technology, SSL/TLS, is the cornerstone of this trust, serving as a digital passport that authenticates a website’s identity and encrypts the data exchanged between a user’s browser and the web server. Without these crucial digital assets, the internet as we know it—a platform for secure e-commerce, private communication, and reliable information exchange—would simply not exist.
The Foundation of Trust: SSL/TLS
At its core, a website certificate is a data file that digitally binds a cryptographic key to an organization’s details. When a web browser connects to a secured website, it retrieves this certificate and uses it to verify the server’s identity. This process ensures that the user is communicating with the intended website and not an impostor. The technology underpinning this security is SSL (Secure Sockets Layer) and its successor, TLS (Transport Layer Security).
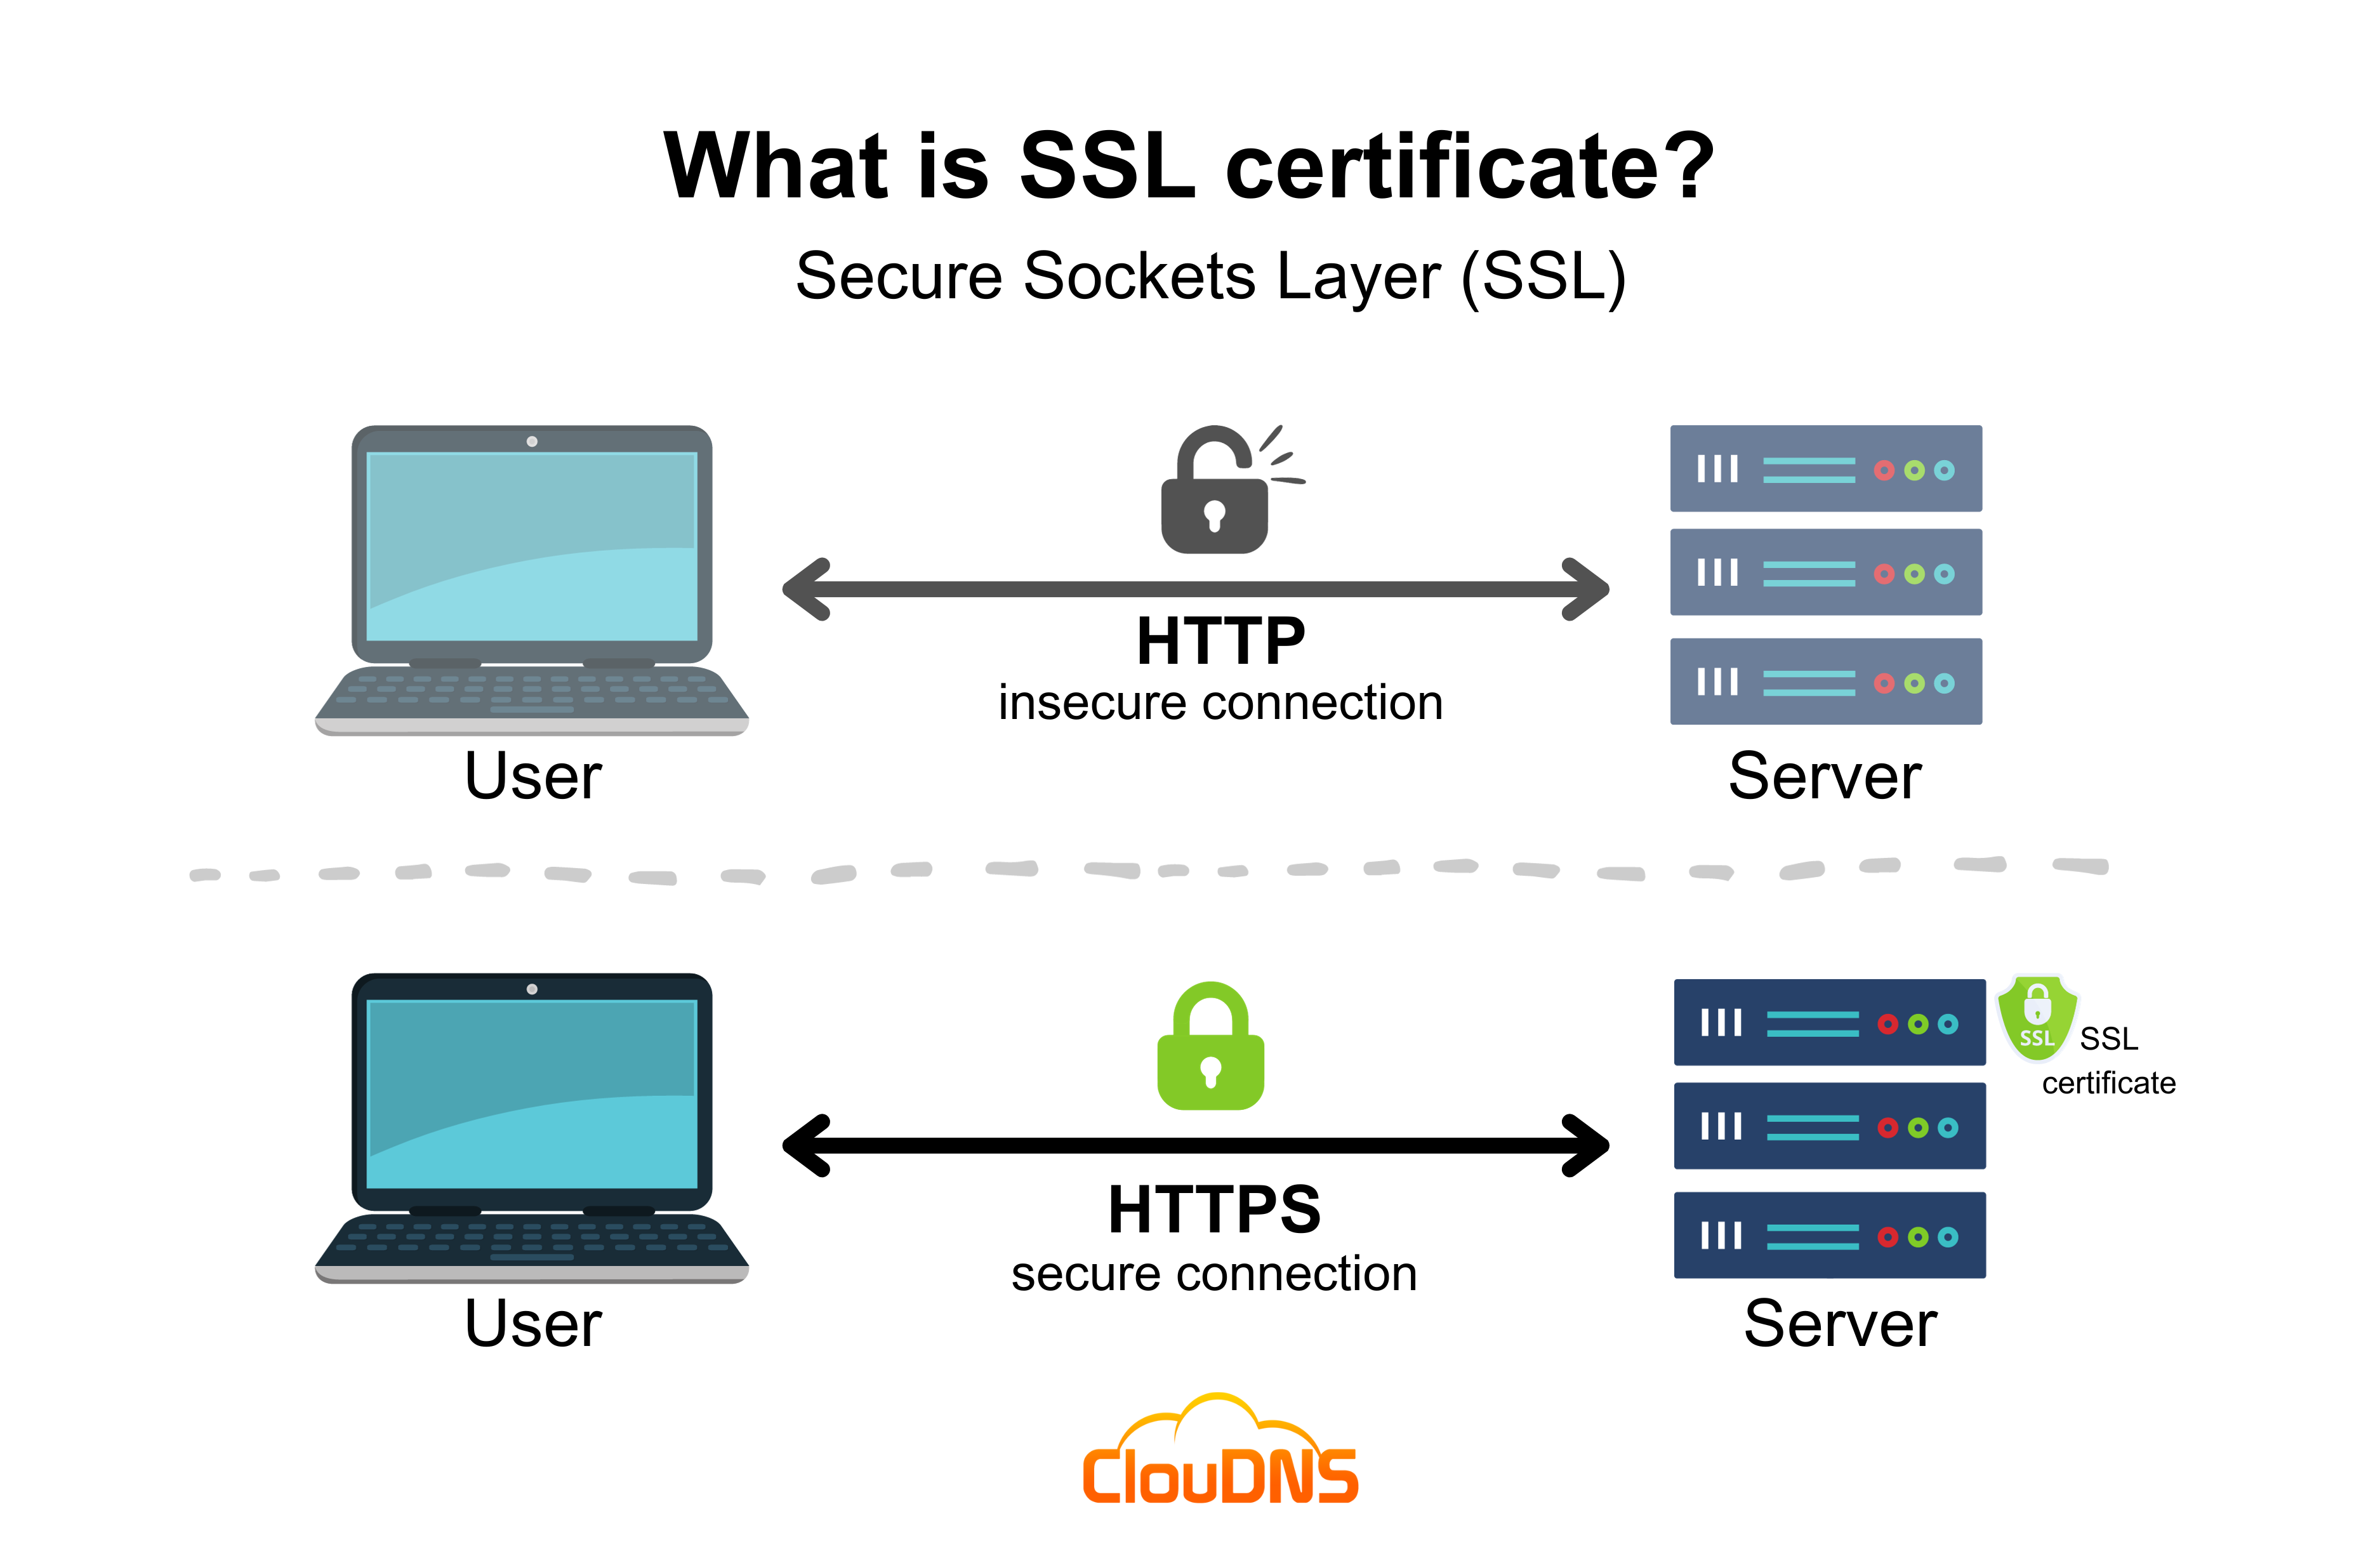
Historically, SSL was the pioneering protocol for encrypting internet traffic. Over time, vulnerabilities were discovered, leading to the development of more robust and secure versions of TLS. While technically most modern certificates use TLS, the term “SSL certificate” remains widely used and understood. The most immediate and visible indicator of a website protected by a certificate is the “HTTPS” (Hypertext Transfer Protocol Secure) prefix in the URL and the padlock icon displayed in the browser’s address bar. This seemingly small change from “HTTP” signifies a profound leap in security, indicating that all data sent between your browser and the website is encrypted and protected from interception and tampering.
The primary function of SSL/TLS is two-fold: encryption and authentication. Encryption scrambles the data, rendering it unreadable to anyone without the correct decryption key, thereby safeguarding sensitive information like login credentials, financial details, and personal data from malicious actors. Authentication, on the other hand, verifies the legitimacy of the website, assuring users that they are indeed interacting with the genuine domain they intended to visit, rather than a fraudulent phishing site attempting to steal their information. This dual protection mechanism is fundamental to maintaining privacy, integrity, and user confidence in the digital realm.
How Website Certificates Work
Understanding the operational mechanics of website certificates involves delving into the principles of public-key cryptography and the role of trusted third parties known as Certificate Authorities.
Cryptographic Keys and Handshake
The core of SSL/TLS security relies on a pair of cryptographic keys: a public key and a private key. When a website requests an SSL/TLS certificate, a unique pair of these keys is generated. The public key is embedded within the certificate and is accessible to anyone, including a user’s web browser. The private key, however, remains securely stored on the web server and is never shared.
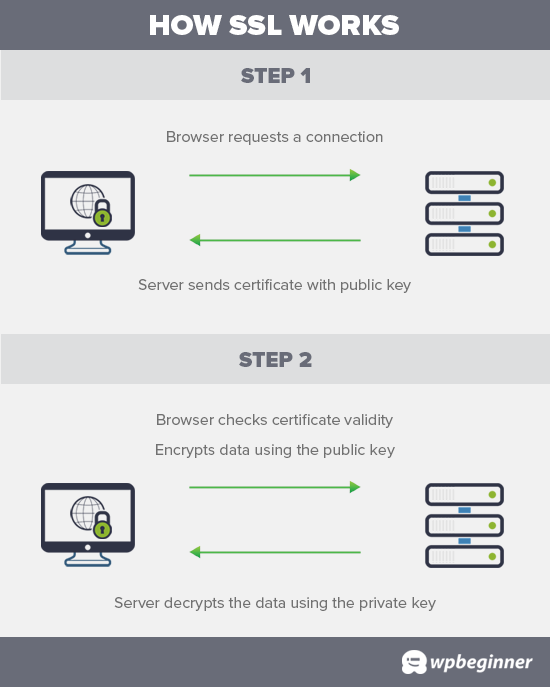
When a user’s browser attempts to connect to an HTTPS-secured website, an intricate process called the “SSL/TLS handshake” begins. This handshake involves several steps:
- Client Hello: The browser sends a “Client Hello” message to the server, indicating its supported SSL/TLS versions, cipher suites, and other capabilities.
- Server Hello: The server responds with a “Server Hello,” selecting the highest mutually supported SSL/TLS version and a chosen cipher suite. Crucially, it also sends its website certificate to the browser.
- Certificate Verification: The browser then verifies the received certificate. It checks if the certificate is valid, hasn’t expired, and is issued by a trusted Certificate Authority. It also confirms that the domain name in the certificate matches the website’s domain.
- Key Exchange: If the certificate is valid, the browser generates a unique session key using the server’s public key (from the certificate). This session key is encrypted and sent back to the server. Only the server, possessing the corresponding private key, can decrypt this session key.
- Encrypted Session: Both the browser and the server now possess the same session key, which is used for symmetric encryption of all subsequent communication during that browsing session. This symmetric encryption is significantly faster than public-key cryptography and ensures efficient, secure data transfer.
Certificate Authorities (CAs)
The integrity of this entire system hinges on the trustworthiness of Certificate Authorities (CAs). CAs are organizations that act as impartial third parties, responsible for verifying the identity of websites (and the entities that own them) and issuing digital certificates. They are like digital notaries, vouching for the legitimacy of a website’s claim to identity.
When a CA issues a certificate, it digitally signs it using its own private key. Web browsers come pre-configured with a list of trusted “root certificates” from major CAs. When a browser verifies a website’s certificate, it traces the certificate’s chain of trust back to one of these trusted root certificates. If the chain is unbroken and valid, the browser trusts the website. This hierarchical model ensures that users only connect to websites whose identities have been independently verified by a globally recognized and trusted authority, preventing man-in-the-middle attacks where an attacker could impersonate a legitimate website.
Types of Website Certificates
Not all website certificates are created equal. They vary in their level of validation, the rigor of the identity checks performed by the CA, and consequently, the degree of trust they convey to users.
Domain Validation (DV) Certificates
Domain Validation (DV) certificates offer the lowest level of validation. To obtain a DV certificate, the applicant merely needs to prove control over the domain name. This is typically done through email verification, a DNS record change, or uploading a file to the web server. DV certificates are the quickest and most affordable to issue, often within minutes. They provide the essential padlock icon and HTTPS, encrypting data, but offer minimal identity assurance beyond domain ownership. They are suitable for personal blogs, small informational websites, or internal systems where identity verification is less critical.
Organization Validation (OV) Certificates
Organization Validation (OV) certificates offer a higher level of assurance. In addition to verifying domain ownership, the CA also conducts a thorough vetting process to confirm the legitimacy of the organization applying for the certificate. This usually involves checking public records, business registration databases, and sometimes even a direct phone call to the organization. While OV certificates provide the same encryption as DV certificates, they also embed the organization’s verified name within the certificate details, which users can view by clicking the padlock icon. This added layer of identity verification makes OV certificates ideal for general business websites, corporate intranets, and any site where customers might appreciate knowing the legitimate business behind the domain.
Extended Validation (EV) Certificates
Extended Validation (EV) certificates provide the highest level of trust and assurance. The validation process for an EV certificate is the most rigorous, involving extensive background checks on the organization’s legal, operational, and physical existence, often adhering to globally recognized guidelines (like the CA/Browser Forum’s EV Guidelines). Historically, EV certificates caused the organization’s name to appear directly in the browser’s address bar alongside the padlock, making it highly visible to users. While modern browsers have evolved how they display EV indicators, the underlying stringent validation still signifies the pinnacle of identity assurance. EV certificates are essential for e-commerce sites, banks, financial institutions, and any online platform dealing with highly sensitive customer data, where maximizing user trust and preventing phishing attacks are paramount.
Wildcard and Multi-Domain (SAN) Certificates
Beyond the validation levels, certificates can also differ in their scope:
- Wildcard Certificates: A wildcard certificate secures a primary domain and an unlimited number of its first-level subdomains. For example, a wildcard certificate for
*.example.comwould secureblog.example.com,shop.example.com,mail.example.com, and so on, all with a single certificate. This simplifies management and reduces costs for organizations with many subdomains. - Multi-Domain (SAN) Certificates: Also known as Subject Alternative Name (SAN) certificates, these can secure multiple distinct domain names and subdomains with a single certificate. For instance, a SAN certificate could secure
example.com,example.net,example.org,shop.example.com, andsecure.anotherdomain.com. This offers flexibility for businesses managing multiple top-level domains or diverse web properties.
Why Website Certificates Are Essential for Modern Tech
Website certificates are no longer an optional security enhancement; they are a fundamental requirement for any serious online presence in the modern technological landscape. Their importance spans data security, user trust, technical functionality, and even search engine optimization.
Data Security and Privacy
The primary and most critical role of website certificates is to protect sensitive data. In an age where data breaches are rampant and privacy concerns are escalating, SSL/TLS encryption ensures that any information transmitted between a user and a website—passwords, credit card numbers, personal identifiable information (PII), health records, etc.—is protected from eavesdropping and interception by malicious entities. This adherence to data protection is not just good practice; it’s often a legal requirement under regulations like GDPR, HIPAA, and CCPA, where failure to protect user data can lead to severe penalties and reputational damage.
User Trust and Brand Reputation
Users are increasingly savvy about online security. The absence of “HTTPS” and the padlock icon can immediately trigger “Not Secure” warnings in modern browsers, signaling a lack of care for user safety. This erodes user confidence, driving potential customers away and severely damaging a brand’s reputation. Conversely, a secure connection reassures users that their interactions are private and that the website is legitimate, fostering trust and encouraging engagement, conversions, and repeat visits. For e-commerce and financial services, this trust is non-negotiable.
SEO Benefits
Search engines, particularly Google, explicitly consider HTTPS as a positive ranking signal. Websites secured with SSL/TLS are given a slight advantage in search engine results pages (SERPs) over their unsecured counterparts. This means that migrating to HTTPS can not only improve security but also enhance a website’s visibility and organic traffic, making it a critical aspect of any comprehensive digital marketing strategy.
Browser Compatibility and New Technologies
Many modern browser features and web technologies now explicitly require a secure HTTPS connection to function. These include advanced features like HTTP/2 (for faster web performance), Service Workers (enabling offline experiences and push notifications), Geolocation APIs, WebRTC (real-time communication), and many more cutting-edge web functionalities. Without an SSL/TLS certificate, websites are effectively locked out of leveraging these innovations, limiting their capabilities and falling behind competitors. Furthermore, browsers are becoming stricter, increasingly marking unsecured HTTP pages with prominent “Not Secure” warnings, further pushing websites towards mandatory HTTPS adoption.
Integrity and Authenticity
Beyond encryption, certificates also guarantee data integrity and website authenticity. Integrity ensures that the data exchanged between the browser and server has not been tampered with or altered in transit. Authenticity confirms that the user is indeed connected to the legitimate website server and not a fraudulent phishing site disguised as the real thing. This protects against identity spoofing and content manipulation, safeguarding both users and the reputation of the legitimate online entity.
The Future of Web Security and Certificates
The landscape of web security is constantly evolving, and website certificates are at the forefront of this progression, adapting to new threats and embracing technological advancements.
Automation and Accessibility
A significant trend in recent years has been the democratization of secure connections. Initiatives like Let’s Encrypt, a free, automated, and open Certificate Authority, have made it possible for virtually anyone to obtain and install DV certificates, drastically lowering the barrier to entry for HTTPS adoption. This has led to a massive increase in the percentage of web traffic that is encrypted. The ACME (Automated Certificate Management Environment) protocol allows web servers to automatically obtain and renew certificates, simplifying management and reducing human error, a vital innovation for scaling secure web services.
Quantum-Resistant Cryptography
As quantum computing advances, there is a looming concern that current cryptographic algorithms, including those used in SSL/TLS, could eventually be broken. Researchers and standards bodies are actively working on “post-quantum cryptography” (PQC) algorithms that are designed to resist attacks from future quantum computers. The next generation of website certificates will likely incorporate these quantum-resistant algorithms, ensuring the long-term security of online communications in a post-quantum world. This proactive innovation is crucial for protecting sensitive data that needs to remain confidential for decades.
Certificate Transparency Logs
To combat mis-issuance and improve the trustworthiness of the CA ecosystem, Certificate Transparency (CT) logs have become a critical component. These public, auditable, and append-only logs record every SSL/TLS certificate issued by CAs. Browsers often require certificates to be logged in CT logs before they are considered valid, allowing domain owners and security researchers to monitor for unauthorized certificate issuance for their domains, thereby adding another layer of security and accountability to the system.

Evolution of TLS Protocols
The TLS protocol itself continues to evolve, with new versions being developed to enhance security, improve performance, and address new attack vectors. TLS 1.3, for instance, offers a more streamlined handshake process, stronger cryptographic algorithms, and removes outdated, vulnerable features, resulting in faster and more secure connections. The continuous refinement of these protocols is essential to stay ahead of malicious actors and ensure that the digital backbone of the internet remains robust and trustworthy for all users and applications in the ever-expanding tech landscape. The integration of DNSSEC (Domain Name System Security Extensions) with TLS also promises more end-to-end assurance by cryptographically signing DNS data, further bolstering trust in domain name resolution.