
The omnipresence of wireless networks in modern life makes the term “Wi-Fi security key” a common one, yet its fundamental importance and underlying mechanisms are often overlooked. Far more than just a password, a security key is the critical component that underpins the privacy and integrity of virtually every wireless connection we make. In an increasingly interconnected world, where devices from smart home appliances to advanced robotics rely on seamless and secure data exchange, understanding the nature and function of a Wi-Fi security key is paramount to safeguarding our digital infrastructure. It represents a foundational element of secure network communication, a cornerstone of reliable and private operation in an age defined by pervasive connectivity and innovative technological advancements.
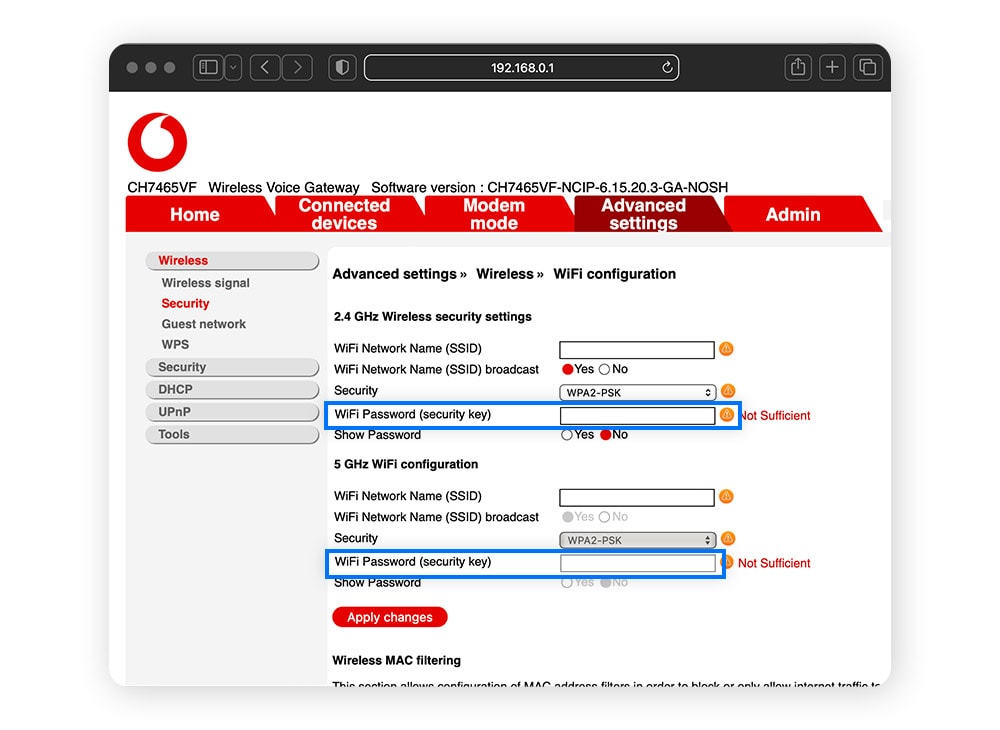
The Foundational Role of Wi-Fi Security
At its core, a Wi-Fi security key serves as a digital gatekeeper, protecting wireless networks from unauthorized access and potential data interception. Without it, any device within range could connect to a network, potentially exploiting bandwidth, accessing shared resources, or, more critically, monitoring the data transmitted over that network. In a landscape where technologies are increasingly interdependent and remotely controlled, the integrity of the wireless link is not merely a convenience but a critical operational requirement. This key enables encryption, transforming readable data into an unreadable format, and authentication, verifying the identity of devices attempting to join the network.
Understanding the “Key”
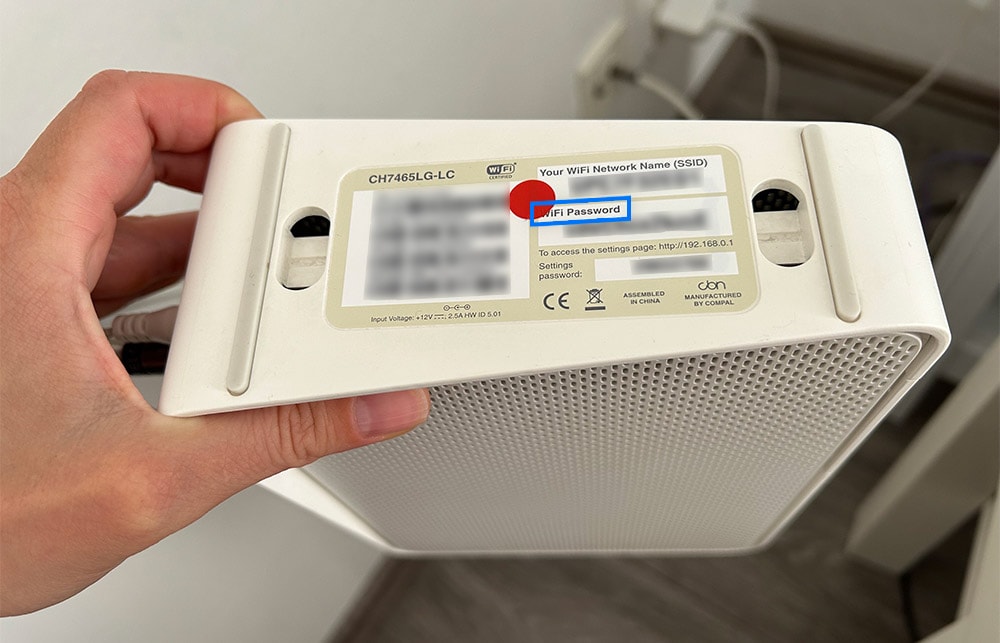
In the context of Wi-Fi, the “security key” is a passphrase or a string of characters (alphanumeric, symbols) that is required to establish a secure connection to a wireless network. While often colloquially referred to as a “Wi-Fi password,” the term “security key” is more accurate as it encompasses the complex cryptographic processes it facilitates. This key is shared only between the legitimate users or devices and the Wi-Fi router (access point). When a device attempts to connect, it must provide this key to the router. If the keys match, a secure session can be initiated, and all subsequent data exchanged between the device and the router will be encrypted using cryptographic algorithms derived from this shared secret.
Types of Wi-Fi Security Protocols
The evolution of Wi-Fi security protocols reflects a continuous arms race between those seeking to protect data and those attempting to breach it. Each generation has introduced stronger encryption methods and more robust authentication processes, adapting to new threats and computational capabilities. Understanding these protocols is essential for comprehending the varying levels of protection a security key can offer.
WEP: The Early Attempt
Wireless Equivalent Privacy (WEP) was one of the first security protocols introduced for Wi-Fi networks, standardized in 1999. It employed a 64-bit or 128-bit encryption key and aimed to provide a level of security comparable to a wired network. However, WEP quickly proved to be highly vulnerable. Its cryptographic design contained fundamental flaws, particularly in its use of initialization vectors (IVs) and its key management, making it relatively easy for attackers with readily available tools to crack WEP keys in a matter of minutes. Its deprecation highlighted the need for more sophisticated security measures.
WPA: Enhanced Security
Wi-Fi Protected Access (WPA) emerged in 2003 as an interim solution to address WEP’s severe weaknesses, specifically designed to be backward compatible with existing Wi-Fi hardware. WPA introduced the Temporal Key Integrity Protocol (TKIP) for encryption, which dynamically changed the encryption keys, making it much harder to crack than WEP’s static keys. It also brought in message integrity checks to prevent tampering with data packets. For authentication, WPA offered two modes: WPA-Personal (WPA-PSK, using a pre-shared key, ideal for home or small office networks) and WPA-Enterprise (using an 802.1X authentication server for larger organizations). While a significant improvement, TKIP itself was found to have vulnerabilities, prompting further development.
WPA2: The Industry Standard
Introduced in 2004, WPA2 became the mandatory standard for Wi-Fi security and quickly replaced WPA. Its primary enhancement was the adoption of the Advanced Encryption Standard (AES) with Counter Mode with Cipher Block Chaining Message Authentication Code Protocol (CCMP) for stronger encryption. AES-CCMP is a much more robust cryptographic algorithm, widely considered secure enough for government and enterprise use. Like WPA, WPA2 offers WPA2-Personal (WPA2-PSK) and WPA2-Enterprise modes. WPA2-PSK remains the most common security protocol for home and small business networks, providing strong protection when used with a complex, unique security key. Despite its strength, a vulnerability known as KRACK (Key Reinstallation Attacks) was discovered in 2017, demonstrating that even robust protocols require continuous vigilance and updates.
WPA3: The Latest Evolution
WPA3, launched in 2018, represents the current generation of Wi-Fi security, addressing some of the lingering concerns and enhancing protection against modern threats. Key improvements include:
- Stronger Encryption for Personal Networks: WPA3-Personal employs 128-bit cryptographic strength for all connections, ensuring even simple, commonly used passwords are more resistant to offline dictionary attacks through the Simultaneous Authentication of Equals (SAE) handshake protocol. SAE replaces WPA2’s Pre-Shared Key (PSK) exchange, offering stronger protections against password guessing attacks.
- Enhanced Open Networks: WPA3 introduces Opportunistic Wireless Encryption (OWE), providing individualized data encryption for users on open (password-free) public Wi-Fi networks, preventing passive eavesdropping.
- Easier Configuration for IoT Devices: WPA3 simplifies the process of securely onboarding IoT devices that may lack traditional input interfaces, offering a more robust alternative to WPS (Wi-Fi Protected Setup).
- Robustness against Side-Channel Attacks: WPA3 incorporates features to harden against various sophisticated attacks.
While WPA2 remains prevalent, WPA3 is the recommended standard for new devices and networks, offering a significant leap forward in wireless security, particularly in an environment increasingly populated by diverse, interconnected technological devices.
How Wi-Fi Security Keys Work
The security key’s role is integral to a multi-step process that ensures both the confidentiality and integrity of wireless communication. This process involves initial authentication, key derivation, and continuous encryption.
The Handshake Process
When a device attempts to connect to a WPA2 or WPA3 secured Wi-Fi network, it initiates a “handshake” protocol. For WPA2-PSK, this is a “4-way handshake.”
- Authenticator (AP) sends an ANonce: The Wi-Fi router (Access Point) sends a randomly generated number (ANonce) to the client.
- Client sends an SNonce: The client device generates its own random number (SNonce) and sends it back to the router. Both the ANonce and SNonce are crucial for generating session keys.
- Client and AP derive the PMK and PTK: Both the client and the router independently use the Wi-Fi security key (pre-shared key), the ANonce, SNonce, and the MAC addresses of both devices to derive a Pairwise Master Key (PMK) and then a Pairwise Transient Key (PTK). The PTK is a unique encryption key for that specific session.
- AP and client exchange MIC and confirm: The router sends a Message Integrity Code (MIC) using the PTK to confirm the key’s validity. The client then sends its own MIC to confirm.
Once the handshake is successfully completed, both the router and the client possess the same PTK, which is then used to encrypt and decrypt all subsequent data exchanged during that session. WPA3’s SAE handshake enhances this by providing stronger protection against offline dictionary attacks, making it more robust against brute-force attempts to guess the security key.
Encryption and Authentication
The security key is central to both encryption and authentication.
- Authentication: By requiring the correct security key, the network authenticates that the connecting device is authorized to join. This prevents unauthorized users from simply connecting to the network.
- Encryption: After successful authentication, the derived session key (PTK) is used to encrypt all data transmitted between the device and the router. For WPA2, this typically uses AES-CCMP. For WPA3, it’s SAE for personal networks and OWE for open networks. This encryption scrambles the data into an unreadable format, ensuring that even if an attacker intercepts the wireless signals, they cannot decipher the content without the correct key. This provides confidentiality, protecting sensitive information from eavesdropping.
Why a Robust Security Key is Essential
The importance of a robust security key extends far beyond simple privacy. In an environment rich with advanced technology and interconnected systems, a weak or compromised key can have significant repercussions, impacting data integrity, system stability, and overall security posture.
Protecting Data Integrity
A strong security key, coupled with a modern protocol like WPA2 or WPA3, ensures that data transmitted over Wi-Fi remains confidential and unaltered. This is crucial for innovative applications, such as real-time telemetry from autonomous systems, sensitive sensor data transmission, or secure command-and-control links. Without proper encryption, intercepted data could be read, altered, or even injected with malicious payloads, leading to incorrect actions, data corruption, or system compromises.
Preventing Unauthorized Access
Unauthorized access to a Wi-Fi network is a gateway to numerous vulnerabilities. An intruder could not only consume bandwidth but also gain access to connected devices, network resources, and potentially the wider internet connection. This could lead to data theft, installation of malware, or the exploitation of other connected systems, impacting operational continuity and intellectual property. In the context of cutting-edge technology, this could mean compromising control over sophisticated devices, altering critical programming, or exfiltrating proprietary data. A strong security key acts as the first line of defense against such intrusions.
Maintaining Network Stability
A compromised Wi-Fi network can also suffer from degraded performance and instability. Unauthorized users can consume significant bandwidth, slowing down legitimate operations. Furthermore, malicious activity on the network can lead to denial-of-service attacks, network crashes, or the introduction of disruptive traffic, all of which impede the reliable operation of interconnected systems. For innovative technologies that rely on low-latency, high-bandwidth connections, network stability secured by a robust key is not merely beneficial but absolutely critical for consistent performance.
Best Practices for Wi-Fi Security in a Connected World
Maintaining strong Wi-Fi security is an ongoing commitment. To ensure the highest level of protection for interconnected technologies and sensitive data, several best practices should be observed:
- Choose WPA3: Whenever possible, use WPA3 as the security protocol. If not available, ensure WPA2 with AES encryption is enabled. Avoid WEP and WPA (TKIP) entirely.
- Create Strong, Unique Passphrases: Your security key should be long (at least 12-16 characters), complex (mixing uppercase, lowercase, numbers, and symbols), and unique. Avoid easily guessable information like birthdays, pet names, or common dictionary words. Consider using a passphrase generator or a mnemonic phrase.
- Change Default Credentials: Always change the default username and password for your router’s administration interface, as these are widely known and easily exploited.
- Disable WPS (Wi-Fi Protected Setup): While convenient, WPS has known vulnerabilities that can allow attackers to bypass the security key. Disable it in your router settings if not actively used.
- Keep Firmware Updated: Router firmware updates often include critical security patches. Regularly check for and install updates from your router manufacturer.
- Implement a Guest Network: For visitors or less trusted devices, set up a separate guest network. This isolates them from your primary network, protecting your core devices and data.
- Consider Network Segmentation: For advanced setups, especially involving critical technological assets, segmenting your network into different VLANs (Virtual Local Area Networks) can add an extra layer of security, limiting the blast radius of a potential breach.
In the rapidly advancing landscape of technology and innovation, where reliance on seamless wireless communication only grows, the Wi-Fi security key remains an unsung hero. Its proper implementation and management are not just a technical detail but a fundamental pillar supporting the secure and reliable operation of our connected future.