
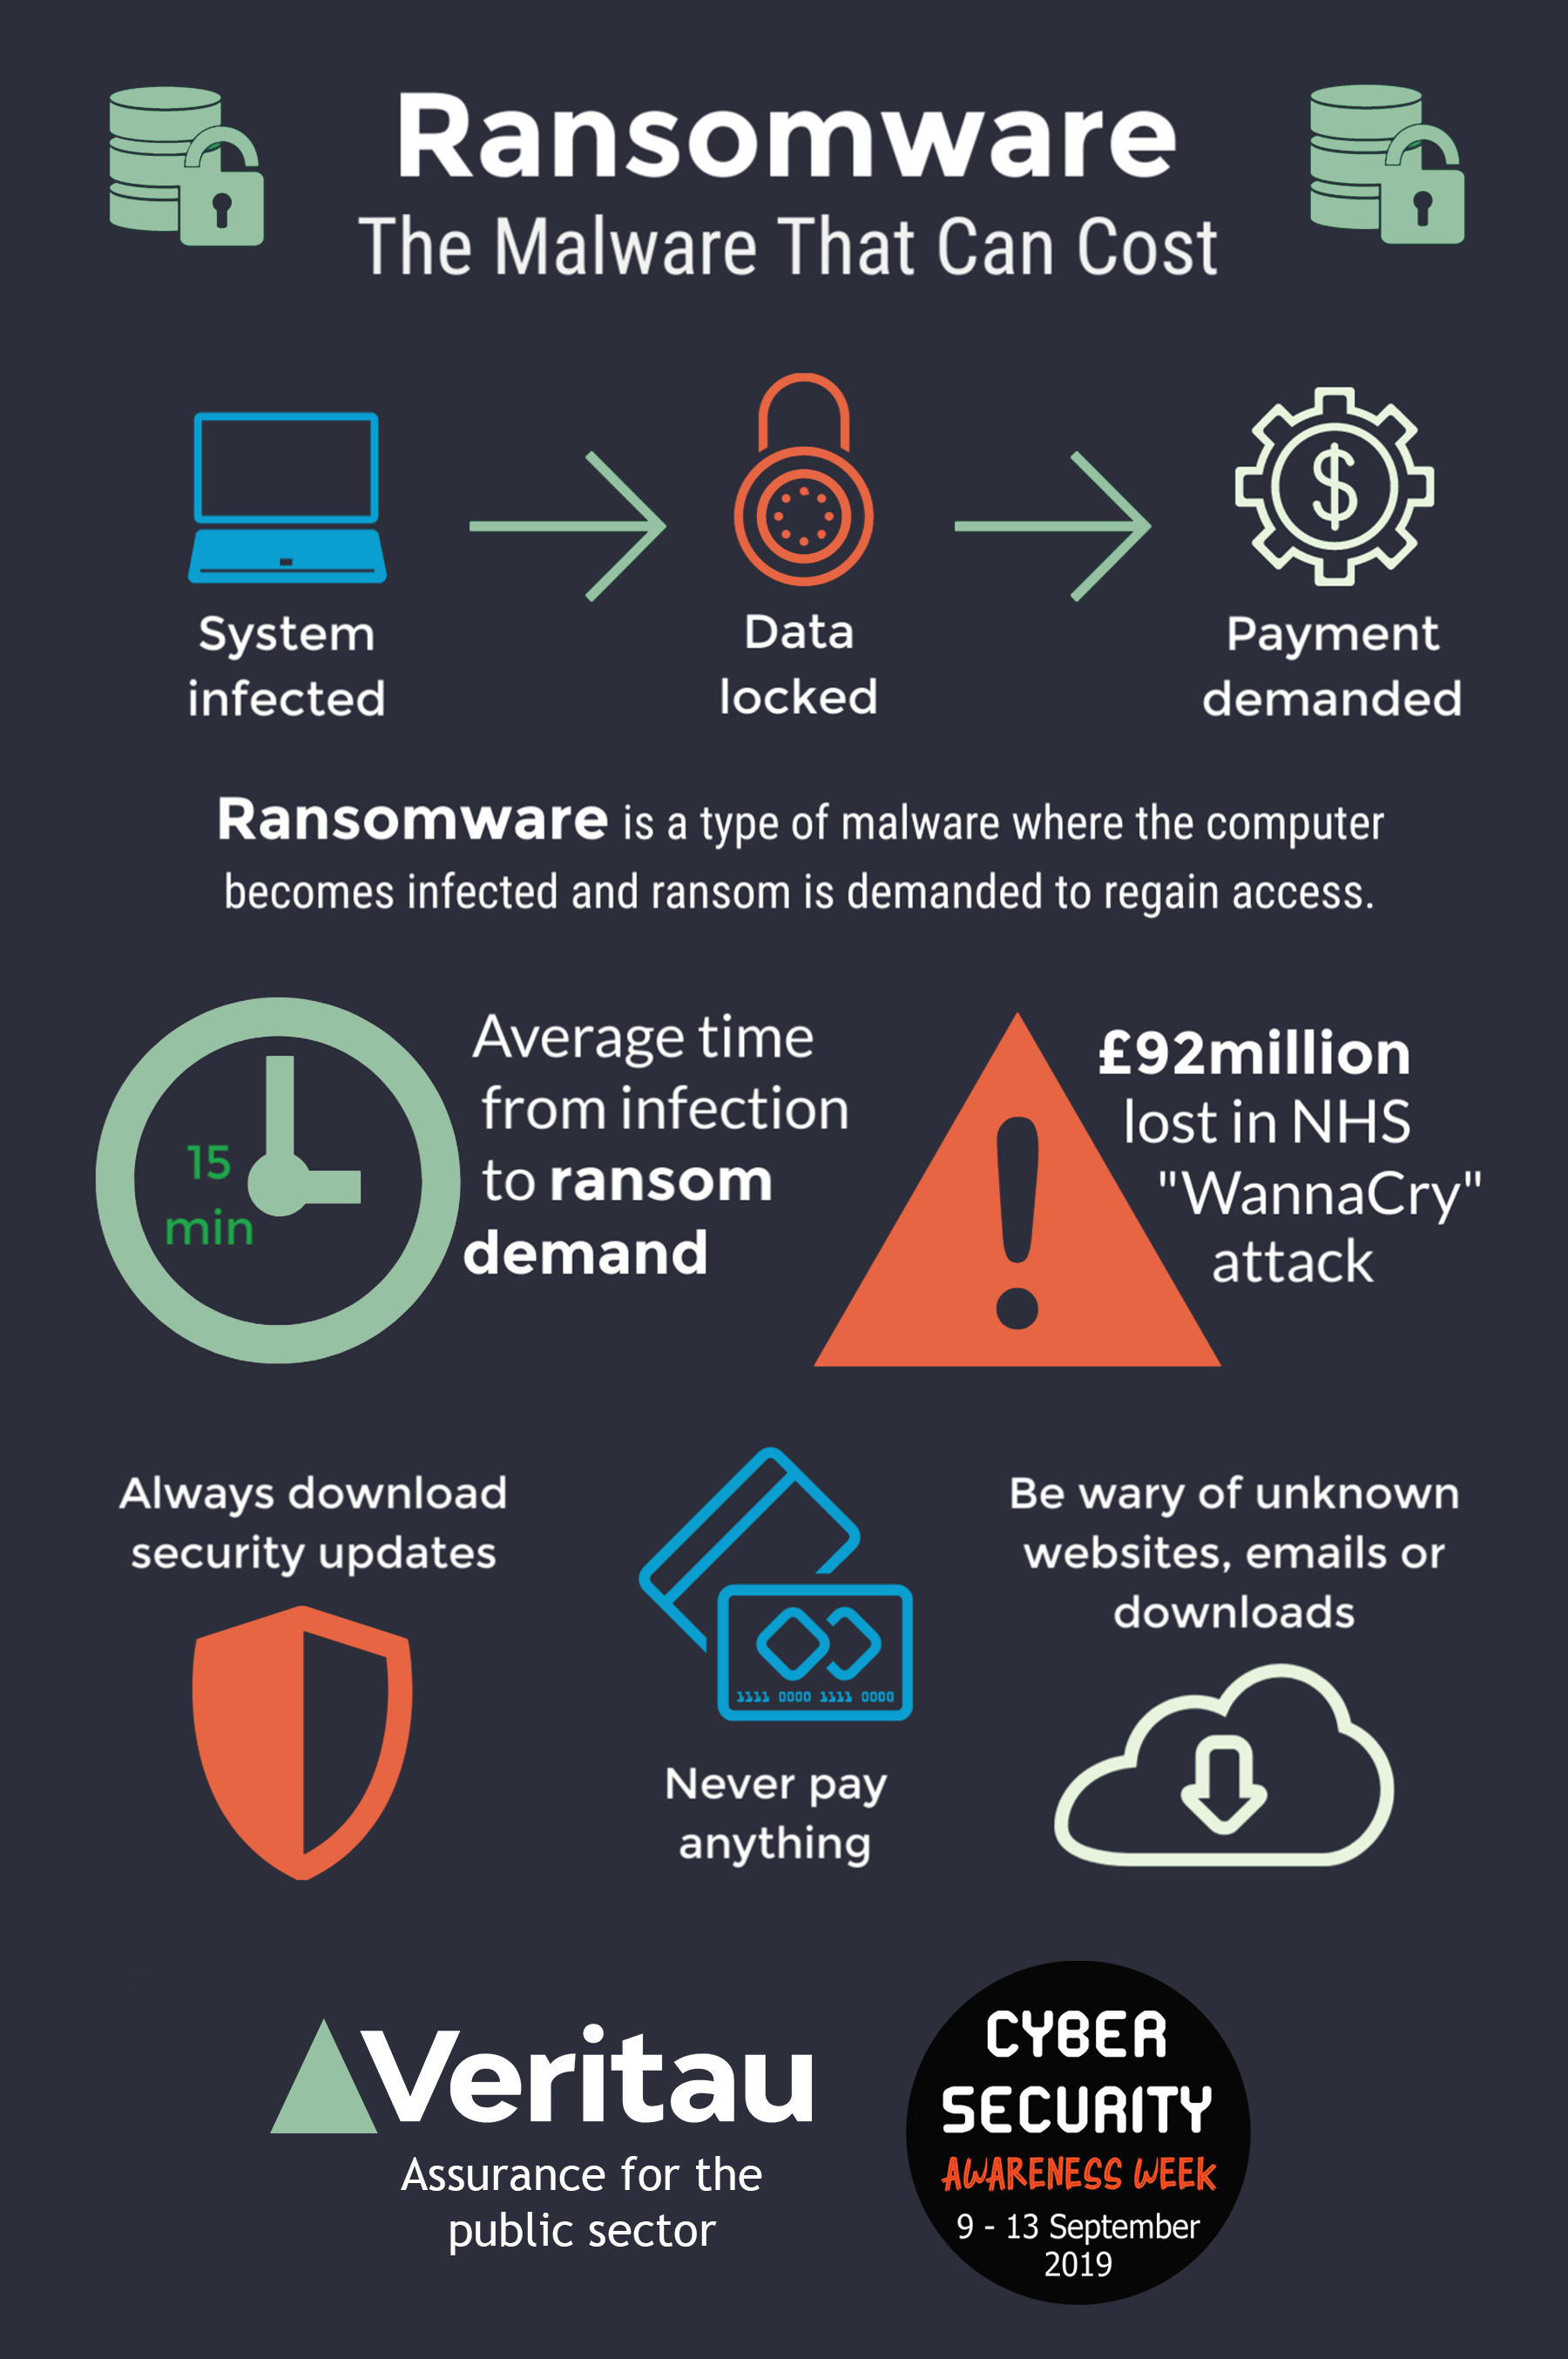
In the intricate tapestry of modern digital infrastructure, ransomware stands as one of the most insidious and pervasive threats. It represents a sophisticated evolution in cybercrime, leveraging advanced technological mechanisms to disrupt operations, extort money, and compromise data integrity on an unprecedented scale. At its core, ransomware is a type of malicious software, or malware, that, once it infiltrates a system, encrypts the victim’s files, rendering them inaccessible. The attackers then demand a ransom, typically in cryptocurrency, in exchange for a decryption key or promise to restore access. Understanding the technological underpinnings of ransomware is crucial for comprehending its impact and developing robust defense strategies within the broader landscape of tech and innovation.
The Anatomy of a Ransomware Attack
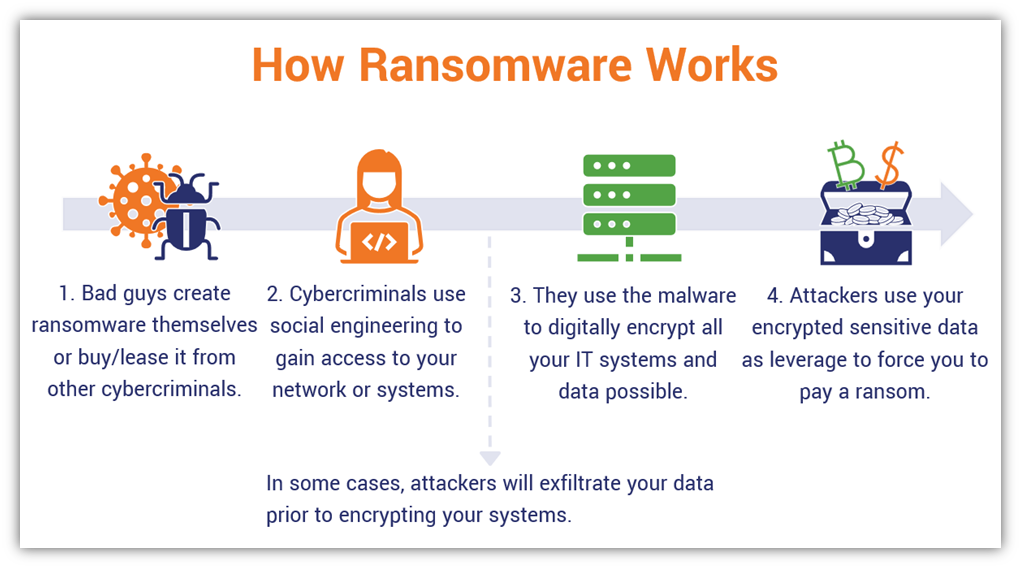
A ransomware attack is rarely a simple, one-step process; it involves a complex chain of technological exploits and social engineering tactics. The journey often begins with an initial compromise, where attackers gain unauthorized access to a victim’s network. This can occur through various vectors, each exploiting different technological vulnerabilities or human factors.
Initial Access Vectors
One of the most common entry points is phishing, where malicious emails containing infected attachments or deceptive links trick users into executing the malware. These emails often employ sophisticated social engineering techniques, making them appear legitimate and urgent, thus circumventing basic user awareness. Another prevalent method involves exploiting vulnerabilities in remote access services like Remote Desktop Protocol (RDP). Weak or compromised RDP credentials allow attackers to bypass perimeter defenses and gain direct access to internal network resources. Furthermore, unpatched software, particularly operating systems, applications, and network devices, provides fertile ground for exploitation. Attackers leverage known or zero-day vulnerabilities in these technologies to establish a foothold without user interaction. Supply chain attacks, targeting trusted software vendors or service providers, have also emerged as a critical vector, allowing ransomware to propagate downstream to numerous unsuspecting organizations.
Encryption and Exfiltration Mechanisms
Once inside, ransomware deploys its primary payload: encryption. Modern ransomware variants utilize robust, industry-standard encryption algorithms, such as AES-256 and RSA-2048, making decryption without the private key practically impossible. The malware typically scans the compromised system and connected network drives for valuable files, encrypting them in place or by creating encrypted copies and deleting the originals. During this phase, many advanced ransomware strains also engage in data exfiltration. Before locking files, they steal sensitive information from the victim’s network and transfer it to attacker-controlled servers. This “double extortion” tactic adds another layer of pressure, as victims face not only data loss but also the public release or sale of their confidential data if the ransom is not paid. The final step involves displaying a ransom note, detailing the demand, payment instructions (usually in Bitcoin or Monero), and threatening consequences for non-compliance.
The Evolution and Landscape of Ransomware Innovation
Ransomware has not remained static; it has undergone significant technological evolution, transforming from rudimentary locking mechanisms to highly sophisticated, multi-stage attacks. This continuous innovation from threat actors presents an ongoing challenge for cybersecurity professionals.
From Locker to Crypto and Beyond
Early forms of ransomware, often dubbed “locker-ransomware,” primarily focused on locking users out of their operating systems without encrypting files. Their technological sophistication was limited, making recovery relatively straightforward. The major shift occurred with the advent of crypto-ransomware, pioneered by strains like CryptoLocker, which leveraged strong encryption. This innovation fundamentally changed the game, as file access became genuinely unattainable without the correct decryption key. Further innovation led to the development of fileless ransomware, which operates entirely in memory, making it harder to detect by traditional signature-based antivirus solutions.
The Rise of Ransomware-as-a-Service (RaaS)
A pivotal technological and operational innovation has been the emergence of Ransomware-as-a-Service (RaaS). This model democratizes cybercrime by allowing individuals with limited technical skills to launch ransomware attacks. RaaS providers develop and maintain the ransomware code, infrastructure, and payment processing systems, while affiliates handle the distribution and execution of attacks. The RaaS platform typically offers user-friendly dashboards, support services, and a profit-sharing model, significantly lowering the barrier to entry for cybercriminals. This “service-oriented” approach has led to a proliferation of attacks and the rapid deployment of new, more potent ransomware variants, akin to legitimate software development cycles.
Double Extortion and Targeted Attacks
The innovation of double extortion by groups like Maze marked another significant escalation. Recognizing that many organizations had robust backup systems, rendering file encryption less impactful, attackers began exfiltrating data prior to encryption. This created an additional leverage point: pay the ransom or your sensitive data will be leaked or sold. This tactic has forced organizations to rethink their incident response and data protection strategies. Concurrently, ransomware operations have become increasingly targeted, moving away from indiscriminate spam campaigns to focus on high-value organizations capable of paying larger ransoms. This involves extensive reconnaissance, network mapping, and tailored exploits, often bypassing enterprise-grade security solutions. The shift towards targeted attacks reflects a more strategic, almost corporate-like, approach to cybercrime.
Impact and Consequences Across the Digital Realm
The ramifications of a ransomware attack extend far beyond the immediate financial demand, creating a cascade of technological, operational, and economic disruptions that underscore its severity.
Operational Disruption and Data Loss
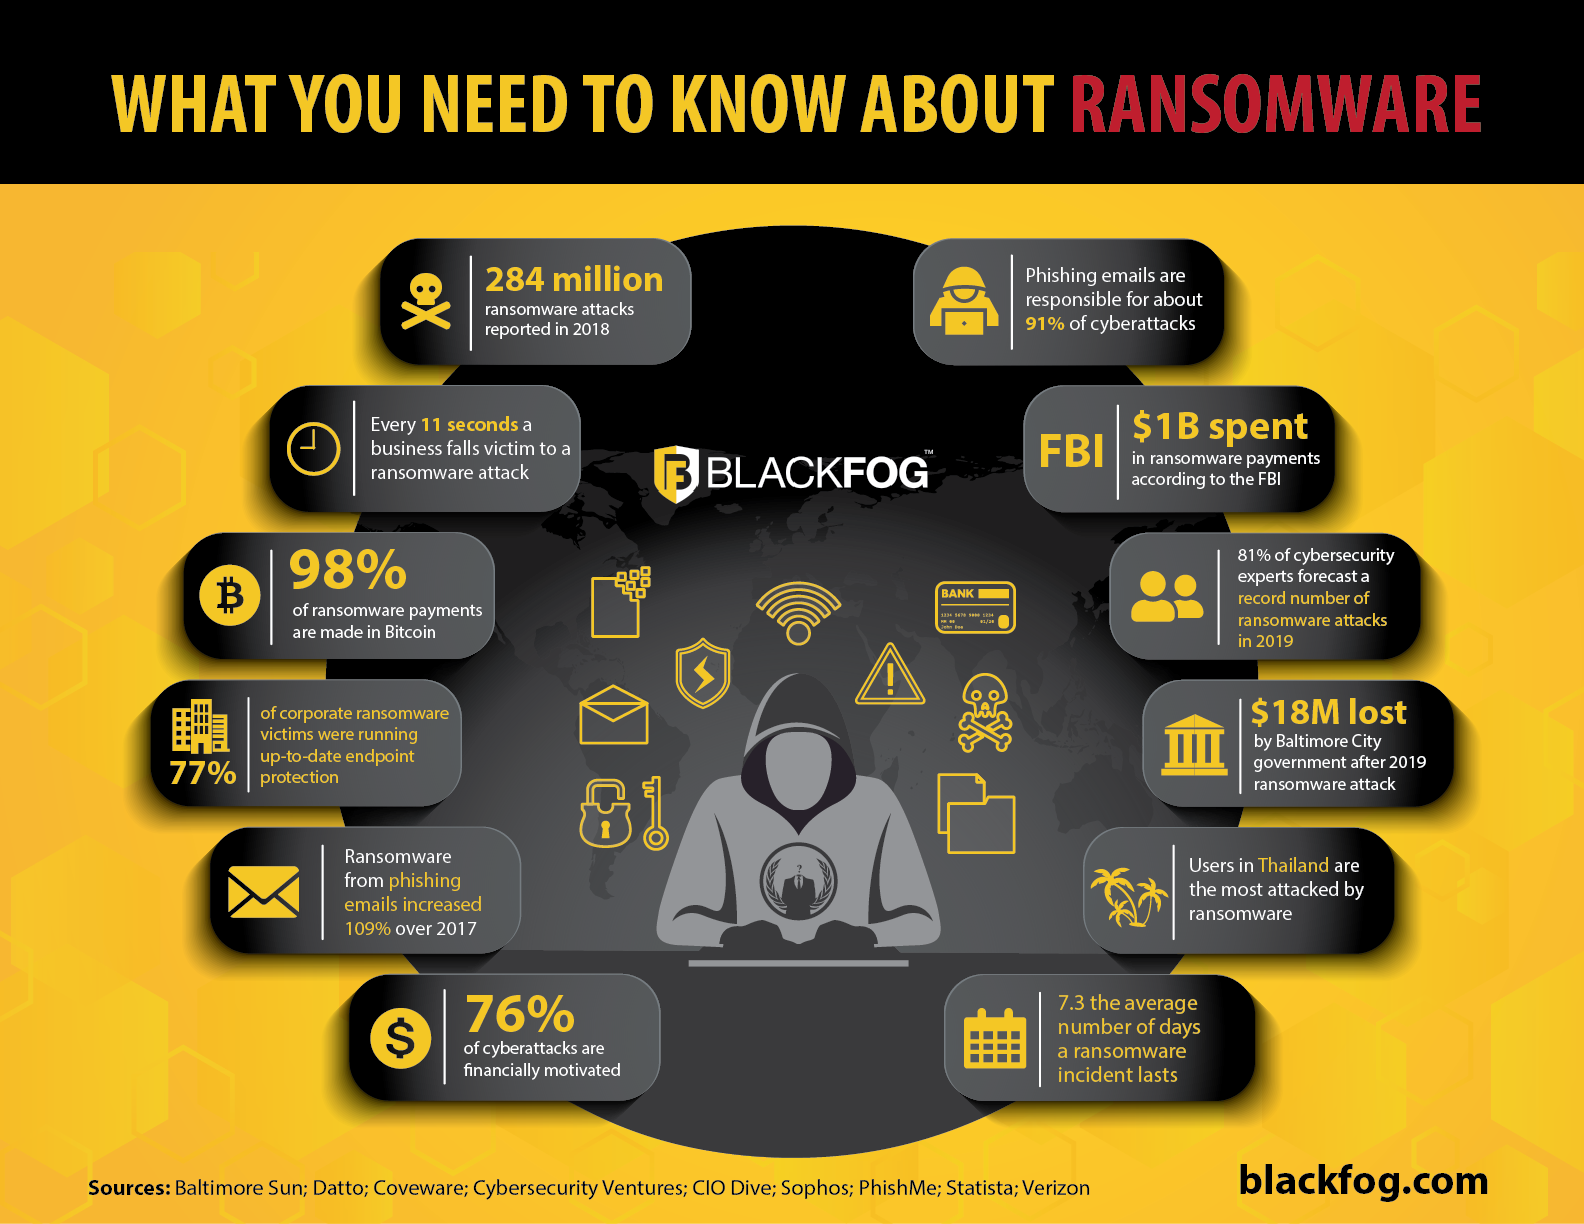
The most immediate impact is the crippling of an organization’s operations. When critical systems, databases, and files are encrypted, essential business processes halt. Healthcare providers may lose access to patient records, manufacturing plants may cease production, and financial institutions may be unable to process transactions. The downtime can last for days or even weeks, leading to massive productivity losses. Even if a ransom is paid and decryption keys are provided, the recovery process is often slow, complex, and prone to errors. Furthermore, decryption tools provided by attackers may not always work perfectly, leading to permanent data loss for some files, regardless of payment. In cases of double extortion, the stolen data can be used for further attacks, identity theft, or competitive espionage, creating long-term liabilities.
Financial and Reputational Costs
The direct financial cost of ransomware includes not only the ransom payment itself but also significant expenses related to incident response, forensic investigations, system recovery, legal fees, and potential regulatory fines. Insurance premiums for cyber liability have also skyrocketed in response to the increased threat. Beyond direct costs, organizations suffer severe reputational damage. Public disclosure of a breach can erode customer trust, deter new business, and impact shareholder confidence. For publicly traded companies, the stock price can plummet, reflecting investor apprehension about the organization’s cybersecurity posture and future viability. The loss of customer data, especially Personally Identifiable Information (PII), can lead to class-action lawsuits and severe penalties under data protection regulations like GDPR and CCPA.
Supply Chain and Systemic Risk
Modern technological ecosystems are highly interconnected, and a ransomware attack on one entity can trigger a domino effect across an entire supply chain. A compromised third-party vendor, for example, can become a vector for attacks on its clients, as seen with software supply chain attacks. This interconnectedness means that even organizations with robust internal defenses can be impacted by vulnerabilities in their partners’ systems. The systemic risk posed by ransomware highlights the need for a collaborative approach to cybersecurity, emphasizing shared responsibility and proactive threat intelligence across industries. The reliance on digital infrastructure makes nearly every sector vulnerable, from critical national infrastructure to small businesses, posing a significant threat to global economic stability.
Defending Against Ransomware: Technological & Strategic Measures
Combating ransomware requires a multifaceted approach that integrates advanced technological solutions with robust strategic planning and continuous innovation in defense.
Proactive Prevention and Robust Backups
The first line of defense is preventing ransomware from gaining initial access. This involves implementing strong endpoint detection and response (EDR) solutions and next-generation antivirus (NGAV) that leverage artificial intelligence and machine learning to identify and block malicious activity, including fileless attacks. Regular patching and vulnerability management are critical to close known security gaps that attackers frequently exploit. Network segmentation can limit the lateral movement of ransomware once it breaches the perimeter, containing the damage. Multi-factor authentication (MFA) on all critical systems, especially remote access points like RDP and VPNs, significantly reduces the risk of credential compromise.
Perhaps the most crucial technological defense against ransomware is a comprehensive and tested backup and recovery strategy. Data should be backed up regularly, securely, and isolated from the primary network (offline or immutable backups) to prevent ransomware from encrypting or deleting them. The “3-2-1 rule” (three copies of data, on two different media, with one copy offsite) provides a robust framework. Regularly testing these backups ensures that they are viable for restoration in the event of an attack, often enabling recovery without paying a ransom.
Incident Response and Threat Intelligence
Despite best efforts, a breach may occur. A well-defined and frequently rehearsed incident response plan is paramount. This plan outlines the steps for detection, containment, eradication, and recovery, minimizing downtime and damage. Leveraging Security Information and Event Management (SIEM) systems and security orchestration, automation, and response (SOAR) platforms enables real-time monitoring and automated responses to suspicious activities, accelerating detection. Threat intelligence platforms provide valuable insights into emerging ransomware variants, tactics, techniques, and procedures (TTPs) of attack groups, allowing organizations to proactively adjust their defenses. While controversial, some organizations also explore decryption tools and resources provided by law enforcement or cybersecurity firms, or even engage in professional negotiation services, though these options come with their own risks and ethical considerations.
The Future of Ransomware and Cyber Resilience
The battle against ransomware is an ongoing arms race, with both attackers and defenders constantly innovating. The future landscape will likely see even more sophisticated attacks and a greater emphasis on building systemic cyber resilience.
Emerging Threats and AI in Attack & Defense
As AI and machine learning mature, their application in ransomware attacks is a looming concern. AI-powered ransomware could potentially learn network layouts, identify high-value targets, and adapt its encryption methods dynamically, making it more evasive and potent. Conversely, AI and machine learning are also vital tools in defense, enhancing threat detection, automating incident response, and predicting future attack vectors. The development of quantum-safe encryption is another area of innovation, preparing for a future where quantum computers could theoretically break current cryptographic standards, posing a risk to all encrypted data.
Collaborative Security and Digital Fortification
Building collective cyber resilience against ransomware requires unprecedented collaboration among governments, industries, and international bodies. Sharing threat intelligence, developing common security standards, and coordinating law enforcement efforts are essential. Technologically, this means investing in resilient architectures, emphasizing zero-trust security models, and developing advanced behavioral analytics to detect anomalous activity indicative of ransomware. The continuous innovation in cloud security, immutable storage technologies, and secure-by-design principles will be critical in fortifying digital infrastructure against this evolving and persistent threat. The goal is not just to recover from attacks, but to engineer systems that are inherently difficult to compromise and quick to restore, fundamentally altering the economics of ransomware for cybercriminals.