
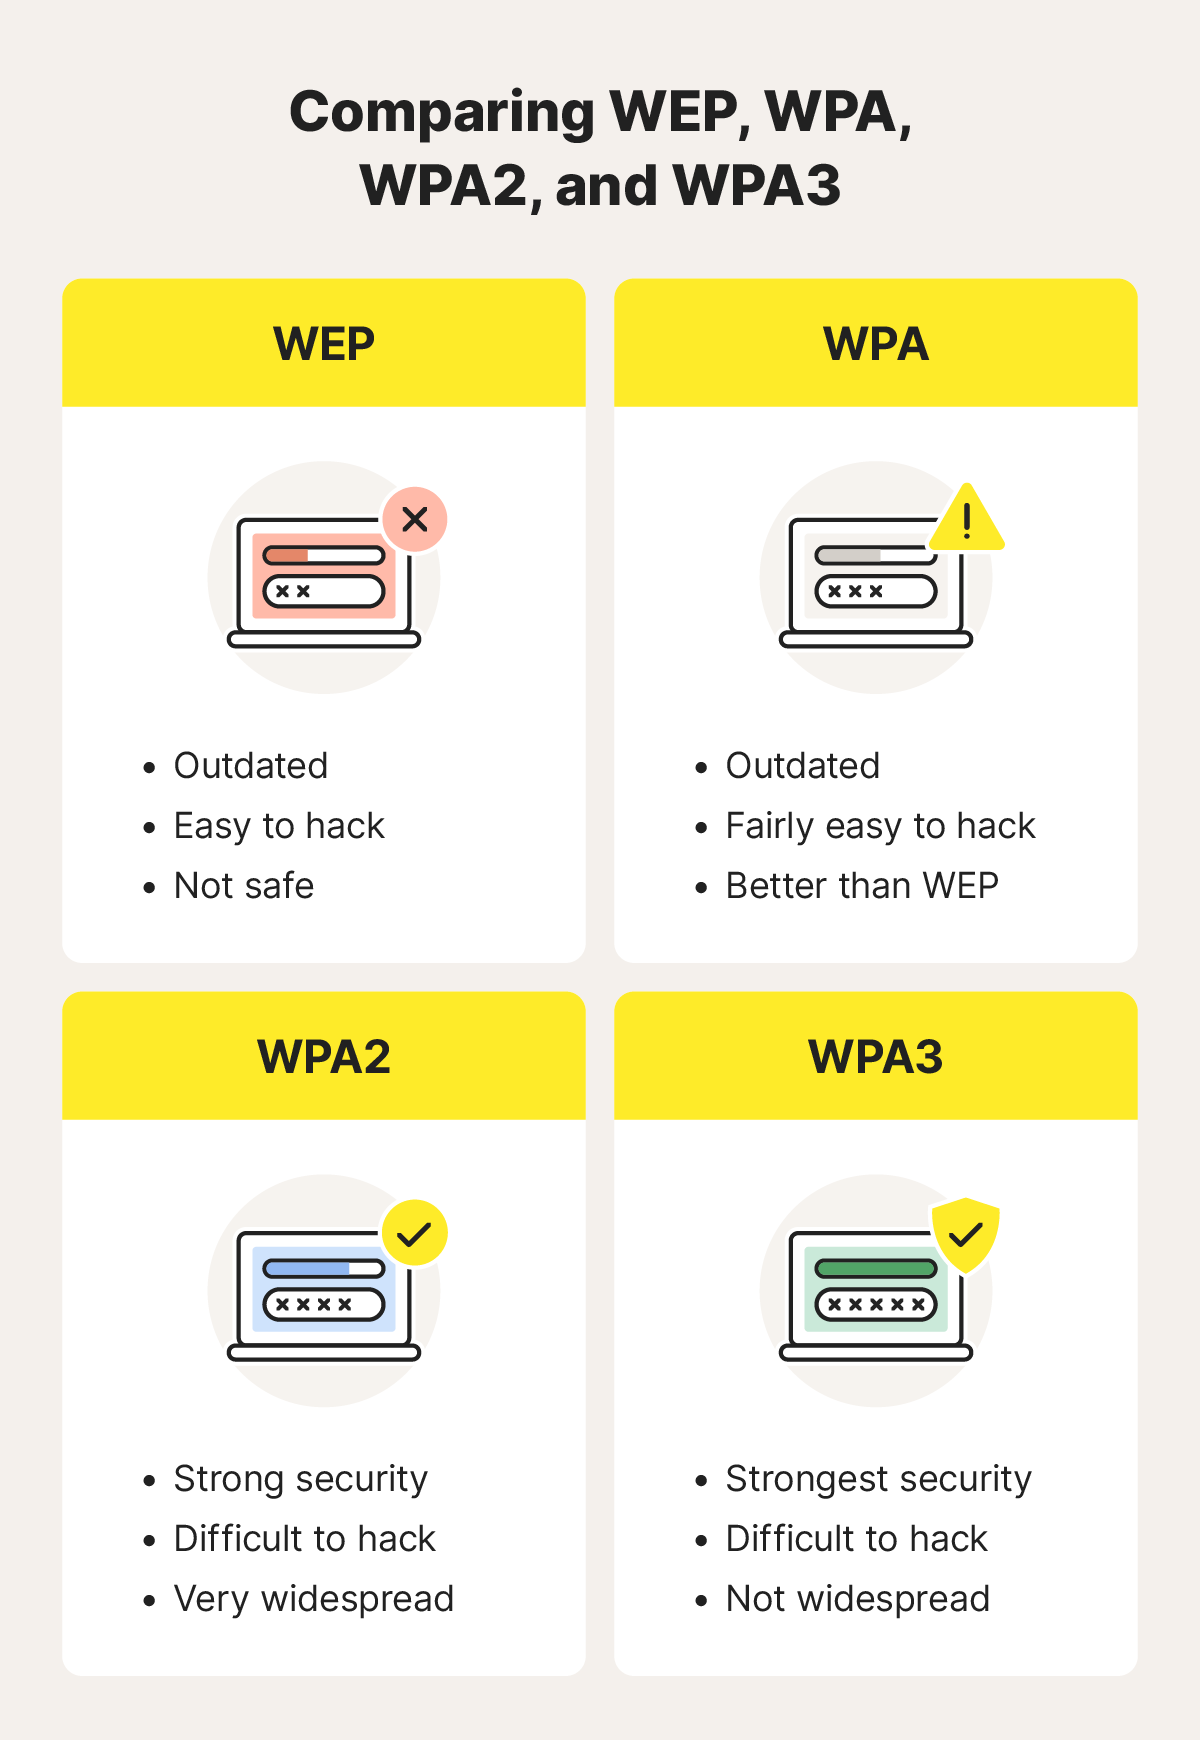
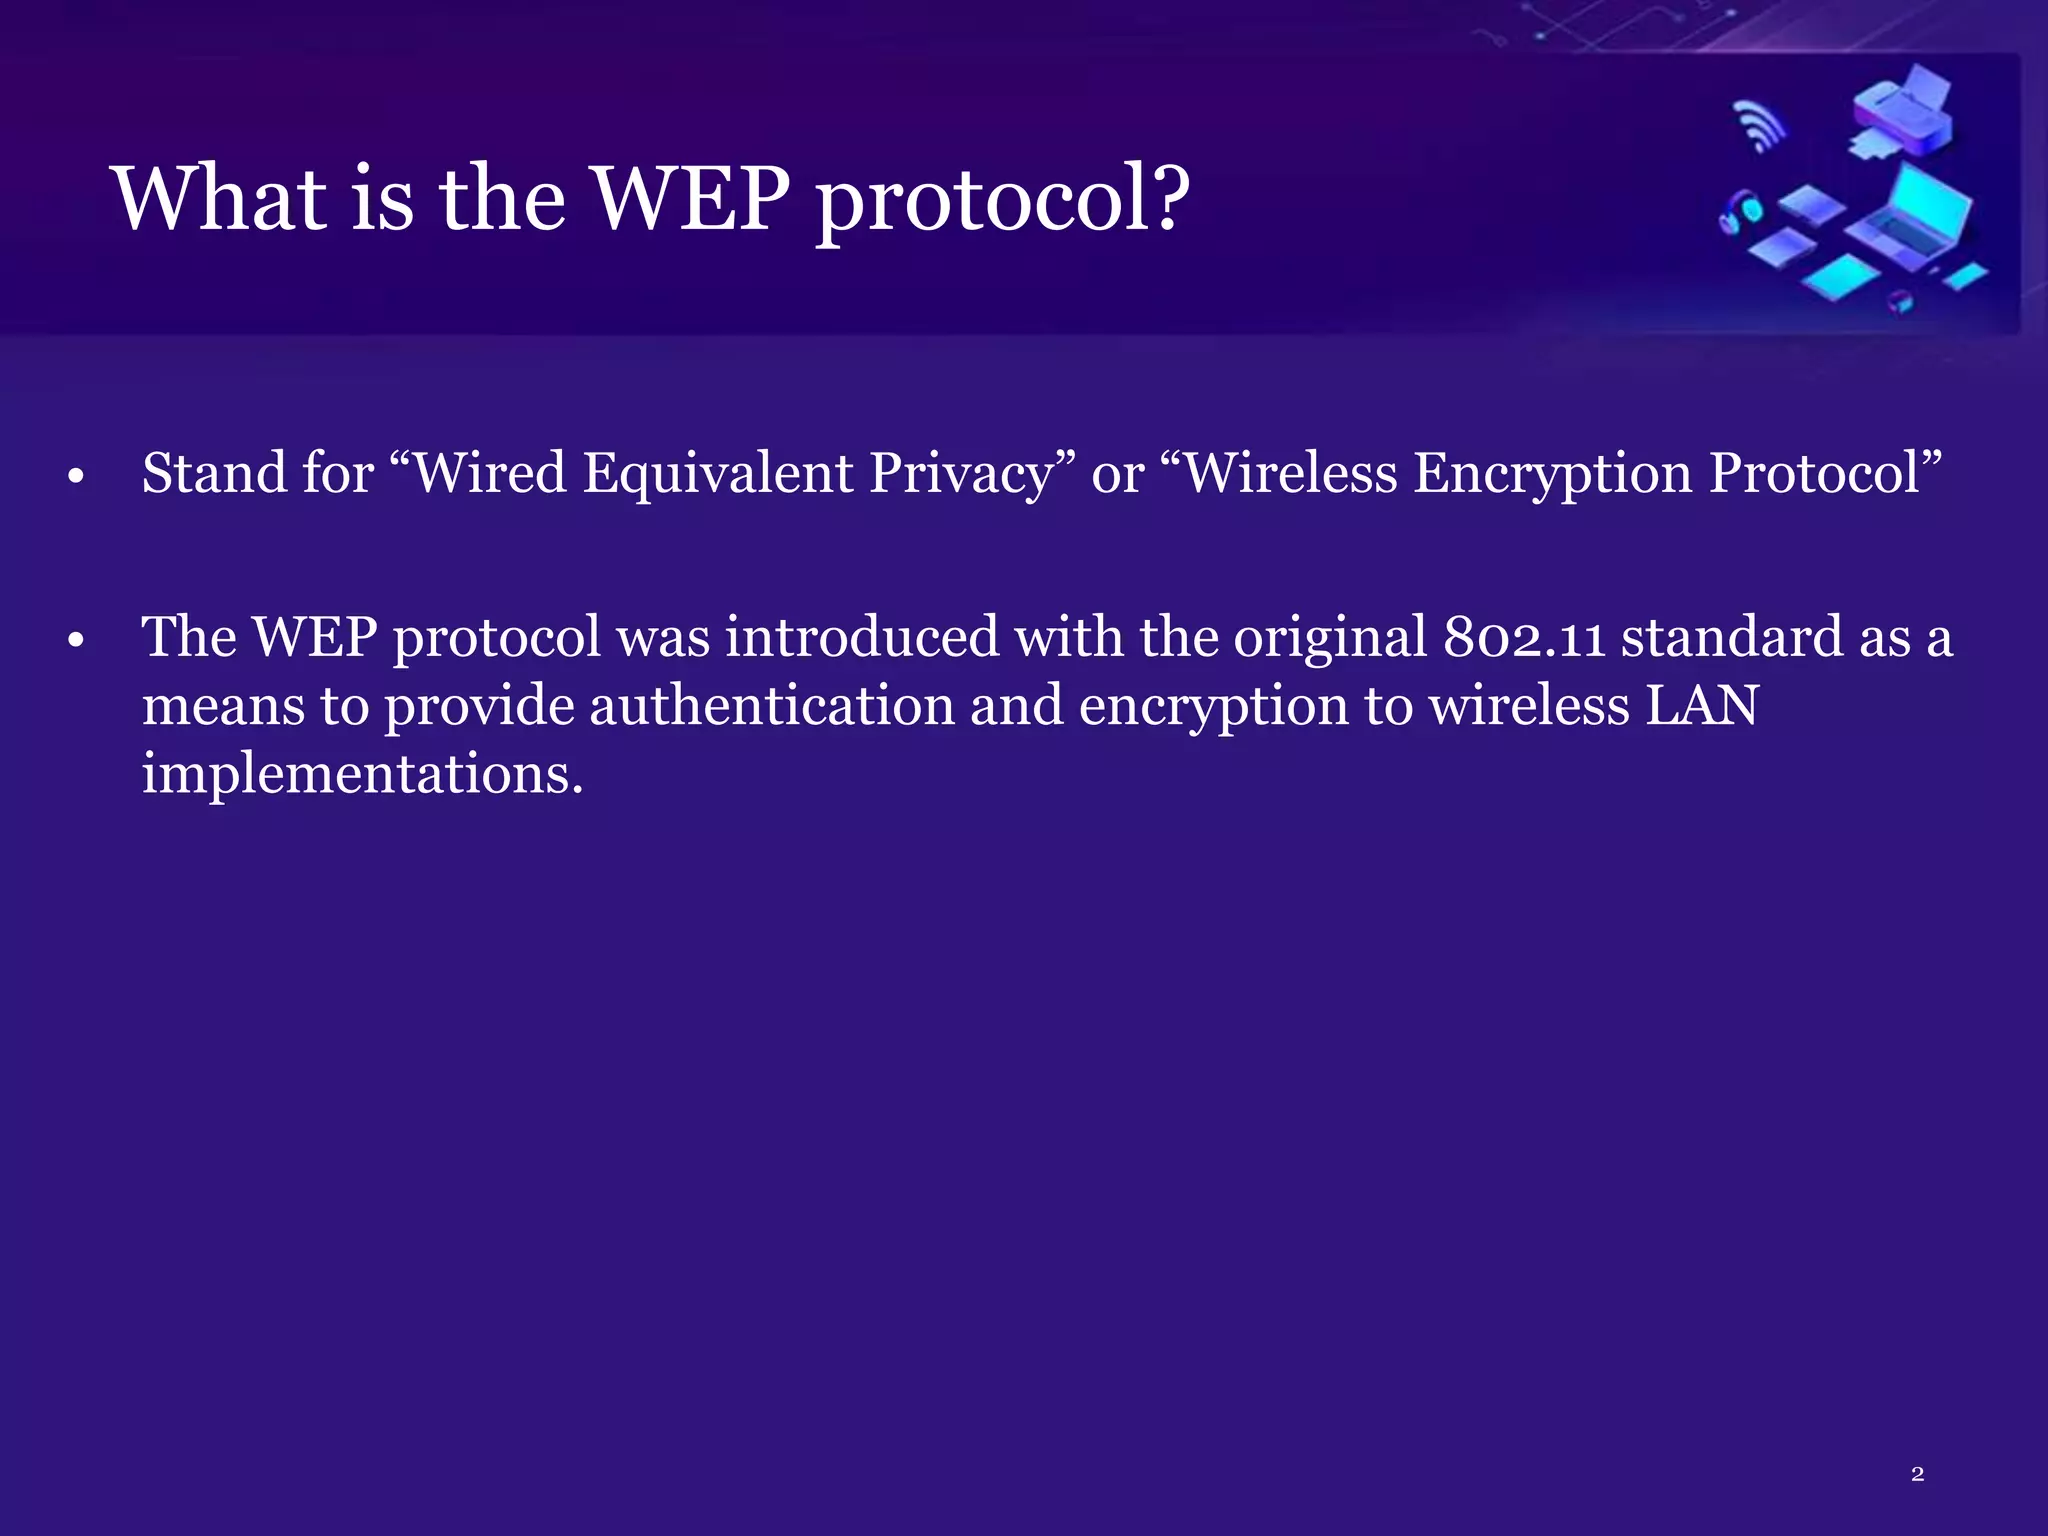
WEP stands for Wired Equivalent Privacy. Introduced in 1999 as part of the IEEE 802.11 standard for wireless networks, WEP was the original security algorithm designed to provide a level of data protection for wireless local area networks (WLANs) comparable to that of wired networks. At its inception, WEP represented a significant step forward in securing the nascent world of wireless connectivity, aiming to prevent unauthorized access to a network and protect data as it traveled over the airwaves. However, despite its ambitious goal, WEP quickly revealed profound vulnerabilities that would necessitate its eventual obsolescence, teaching invaluable lessons about the critical importance of robust cryptographic design in all forms of tech and innovation.
The Dawn of Wireless: Defining Wired Equivalent Privacy
When wireless networking began to gain traction in the late 1990s, the convenience of untethered access brought with it new security challenges. Unlike wired networks where physical access often implied a level of control, wireless signals broadcast freely, making them susceptible to eavesdropping and unauthorized intrusion. WEP was conceived to address these concerns by encrypting data transmitted between a client device and a wireless access point, thereby mimicking the perceived security of a physical cable where data was not easily intercepted by external parties.
The Initial Vision and Purpose
The primary objective of WEP was two-fold: to prevent eavesdropping and to protect against unauthorized access. By encrypting data, WEP aimed to ensure that only authorized devices with the correct encryption key could decrypt and read the information being exchanged. This was crucial for businesses and individuals who were keen to embrace wireless technology but demanded assurance that their sensitive data—whether corporate communications, financial transactions, or personal information—remained private. The “equivalent privacy” in its name reflected the design’s aspiration to bring wireless security on par with the inherent privacy afforded by physical connections.
How WEP Aimed to Work
WEP employed the RC4 stream cipher for encryption, a relatively simple and fast algorithm suitable for the limited computational power of early wireless devices. Before data transmission, both the client and the access point would need to share a secret key, typically a 64-bit or 128-bit hexadecimal string. This shared key was combined with a 24-bit Initialization Vector (IV) to create a unique per-packet key. The RC4 cipher then used this per-packet key to generate a keystream, which was XORed with the plaintext data to produce the ciphertext. On the receiving end, the same process, using the identical shared key and IV, would be performed to decrypt the data. Additionally, WEP included a basic integrity check using a Cyclic Redundancy Check (CRC-32) to detect accidental corruption of data during transmission, though this proved to be a critical flaw rather than a strength in terms of security.
A Flawed Foundation: The Inherent Weaknesses of WEP
Despite its initial promise, WEP’s design contained several fundamental cryptographic flaws that were systematically exposed by security researchers within a few years of its introduction. These vulnerabilities rendered WEP largely ineffective against determined attackers, leading to its widespread deprecation. The failures of WEP highlighted the often-overlooked complexities of cryptographic engineering and the vital importance of rigorous security analysis.
The RC4 Cipher’s Misuse
While RC4 itself is a viable stream cipher when implemented correctly, WEP’s application of it was fatally flawed. The core issue lay in the reuse of Initialization Vectors (IVs) and the method by which they were combined with the shared secret key. Because the IV was only 24 bits long, and the number of possible IVs was relatively small (2^24, or about 16 million), it was statistically probable for an IV to be reused with the same secret key after a relatively short period of network activity, especially on a busy network. When the same keystream is used to encrypt different plaintexts (which happens with IV reuse), an attacker can perform a known-plaintext attack or statistical analysis to deduce the keystream and, subsequently, the secret WEP key.
Initialization Vector (IV) Collisions
The repeated use of IVs, particularly with weak IVs (those that reveal partial information about the secret key), created “IV collisions.” Attackers could passively collect a sufficient number of these weak IVs and their corresponding encrypted packets. Specialized tools, such as Aircrack-ng, could then exploit these collisions to mathematically derive the WEP key in a matter of minutes, sometimes even seconds, using sophisticated statistical attacks like the FMS attack (Fluhrer, Mantin, Shamir). This meant that WEP offered practically no protection against a determined adversary with basic off-the-shelf hardware and software.
Lack of Message Integrity
Another critical vulnerability stemmed from WEP’s method of ensuring message integrity. WEP used a CRC-32 checksum, which is designed to detect random errors, not malicious tampering. Because CRC-32 is a linear function, an attacker could predict how changes to the ciphertext would affect the checksum. This allowed an adversary to flip bits in an encrypted message and adjust the CRC-32 checksum accordingly, making the altered message appear valid to the receiver without knowing the encryption key. This complete lack of strong message authentication meant that not only could data be read, but it could also be altered in transit without detection, severely compromising data integrity and trust.
The Inevitable Obsolescence: Paving the Way for Stronger Security
The widespread discovery and exploitation of WEP’s vulnerabilities quickly made it clear that a new, more robust wireless security standard was desperately needed. The Wi-Fi Alliance, an industry group that promotes Wi-Fi technology, responded by developing stronger security protocols to replace WEP, understanding that the future of wireless technology depended on a foundation of trust and reliability.
The Emergence of WPA and WPA2
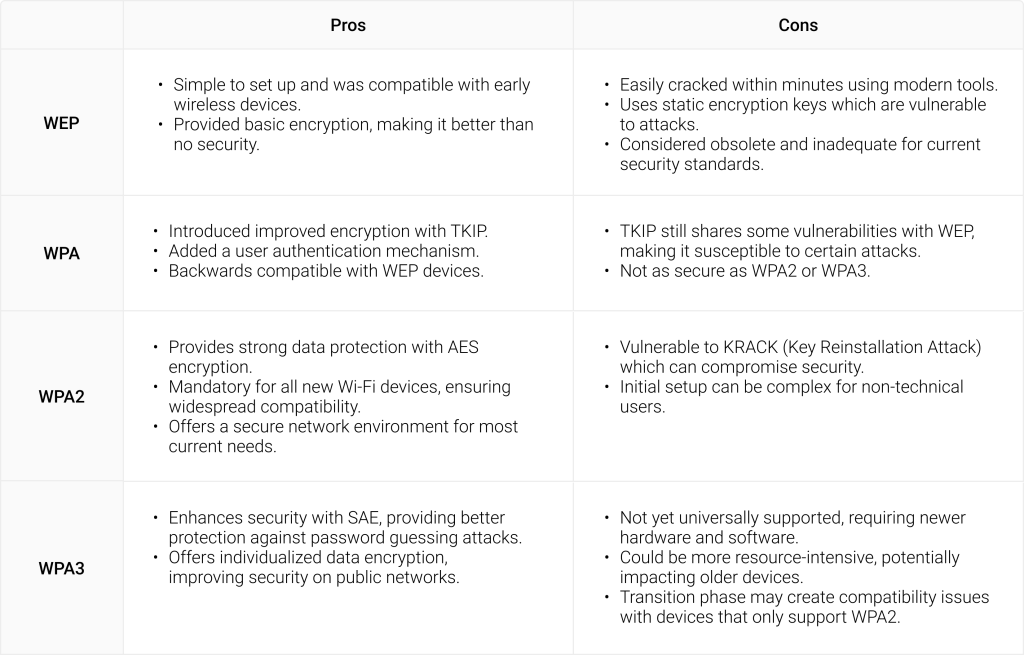
The first successor to WEP was Wi-Fi Protected Access (WPA), released in 2003 as an interim solution while a full new standard was being developed. WPA addressed many of WEP’s core flaws by introducing the Temporal Key Integrity Protocol (TKIP) for dynamic per-packet key generation and a more robust message integrity check (Michael). TKIP significantly mitigated the IV reuse problem and made key derivation much harder. WPA also brought in 802.1X authentication for enterprise environments, providing stronger user authentication.
WPA was quickly followed by WPA2 in 2004, which became the definitive replacement for WEP and the industry standard for over a decade. WPA2 replaced TKIP with the Advanced Encryption Standard (AES) cipher, specifically using the Counter Mode with Cipher Block Chaining Message Authentication Code Protocol (CCMP). AES-CCMP is a much stronger, government-grade encryption standard, virtually immune to the types of attacks that plagued WEP and TKIP. WPA2 also offered stronger key management and authenticated key exchange, ensuring a much more secure wireless environment.
WPA3: The Current Standard
While WPA2 served admirably, the evolving threat landscape and the emergence of new attack vectors (such as KRACK) prompted the development of WPA3, introduced in 2018. WPA3 offers several key enhancements, including:
- Individualized Data Encryption: Even on open networks, WPA3 provides individualized data encryption for all users, offering enhanced privacy.
- Stronger Cryptography: It mandates the use of 192-bit cryptographic strength in enterprise modes.
- Simultaneous Authentication of Equals (SAE): This new key establishment protocol replaces the Pre-Shared Key (PSK) exchange used in WPA2, providing stronger protection against offline dictionary attacks and forwarding secrecy, ensuring past communications remain private even if the key is compromised later.
- Simplified IoT Device Configuration: WPA3 aims to simplify the configuration of devices without display interfaces, making it easier to integrate smart home devices securely.
WPA3 represents the culmination of lessons learned from WEP and WPA/WPA2, providing the strongest and most resilient security for wireless networks to date, crucial for the increasingly interconnected world of IoT, smart cities, and autonomous systems.
The Enduring Legacy: Lessons for Modern Tech & Innovation
The story of WEP is more than just a chapter in the history of wireless security; it’s a foundational case study in the broader field of tech and innovation. Its rapid failure underscored critical principles that continue to guide the development of secure systems, particularly in areas like remote sensing, drone operations, and other advanced technologies heavily reliant on wireless communication.
The Importance of Robust Cryptography in Wireless Communication
WEP’s vulnerabilities vividly demonstrated that cryptographic design is highly intricate and unforgiving. Even seemingly minor flaws in how a cryptographic primitive (like RC4) is implemented, or how keys and IVs are managed, can completely undermine the security of an entire system. For modern tech, whether it’s drone-to-ground station communication, data links for remote sensing payloads, or secure command and control for autonomous vehicles, robust, peer-reviewed, and continuously updated cryptographic protocols are non-negotiable. The integrity and confidentiality of data transmitted wirelessly are paramount for operational safety, regulatory compliance, and mission success.
Impact on Trust and Reliability in Emerging Technologies
The collapse of WEP security taught the industry a harsh lesson about user trust. When a foundational security mechanism proves to be fundamentally broken, it erodes confidence in the underlying technology. For cutting-edge innovations like AI-powered autonomous flight, advanced mapping, and sophisticated remote sensing applications, reliability and security are inextricably linked. Weak wireless security could lead to hijacked drones, intercepted sensor data, or compromised control systems. The shift from WEP to WPA/WPA2/WPA3 has been crucial in building and maintaining the trust necessary for these technologies to flourish and integrate into critical infrastructure. Developers and innovators in these fields must prioritize secure-by-design principles, understanding that the smallest security oversight can have catastrophic real-world consequences.
Continuous Evolution of Security in a Connected World
Finally, WEP’s story highlights the dynamic and adversarial nature of cybersecurity. No security standard is impregnable indefinitely. As computing power increases and new attack methodologies emerge, even strong protocols eventually face new threats. The evolution from WEP to WPA, WPA2, and now WPA3 underscores the necessity for continuous innovation and adaptation in security technologies. This iterative improvement is a core tenet for any field built on digital communication, reminding us that “good enough” security today may be wholly inadequate tomorrow. For those working in tech and innovation, especially in rapidly advancing areas that push the boundaries of wireless communication and data transfer, vigilance, research, and proactive security upgrades are not just best practices—they are existential requirements.