
A computer virus, in the digital realm, is a malicious piece of code designed to infiltrate and disrupt the normal functioning of a computer system. Unlike a biological virus that infects living organisms, a computer virus targets software and data, aiming to replicate itself and spread to other computers. The term “virus” is often used interchangeably with other forms of malware, but technically, a virus requires a host program to spread and execute its payload. Understanding the core functionalities of a computer virus is crucial for comprehending the broader landscape of cybersecurity threats and developing effective defense mechanisms.

The Mechanics of Infection and Replication
The fundamental characteristic of a computer virus is its ability to self-replicate. This replication process is the key to its propagation, allowing it to spread from one file or system to another without direct user intervention. The infection typically occurs when an infected file is executed, opened, or accessed.
Initial Entry Points
Viruses can enter a system through various vectors, often exploiting human behavior or software vulnerabilities.
Exploiting User Actions
A significant portion of virus infections originate from unsuspecting user actions. This includes:
- Opening Infected Email Attachments: Phishing emails often contain malicious attachments disguised as legitimate documents, invoices, or updates. Opening these attachments can trigger the virus’s execution.
- Downloading Infected Files: Malicious software can be disguised as free software, games, or media files downloaded from untrusted websites or peer-to-peer networks.
- Clicking on Malicious Links: Suspicious links in emails, social media, or websites can redirect users to pages that automatically download or execute malware.
- Using Infected Removable Media: USB drives, external hard drives, or even older forms of media like CDs can carry viruses. If an infected drive is connected to a clean system and its contents are accessed, the virus can spread.
Leveraging Software Vulnerabilities
Beyond user actions, viruses can exploit weaknesses in operating systems or application software.
- Unpatched Software: Developers release patches and updates to fix security vulnerabilities. If a system or application is not regularly updated, it remains susceptible to exploits that can allow viruses to gain access.
- Zero-Day Exploits: These are vulnerabilities that are unknown to the software vendor, meaning there is no patch available. Attackers can use these to deploy viruses before defenses can be put in place.
The Replication Process
Once a virus has successfully infected a system, its primary objective is to replicate.
- Attaching to Executable Files: Many viruses attach themselves to executable files (.exe, .com, .bat). When the host program is run, the virus code is also executed, allowing it to infect other executable files on the system.
- Boot Sector Viruses: These older types of viruses infect the boot sector of a hard drive or floppy disk. When the computer starts up, the infected boot sector is loaded into memory, and the virus can then take control.
- Macro Viruses: These viruses are written in macro languages embedded within documents (e.g., Microsoft Word, Excel). When an infected document is opened, the macro is executed, and it can then infect other documents or applications.
- Fileless Viruses: Modern viruses are increasingly “fileless,” meaning they don’t reside in traditional files. Instead, they operate in the computer’s memory or leverage legitimate system tools to execute their malicious code. This makes them harder to detect and remove.
The Malicious Payload: What Viruses Do to Your System
Beyond replication, the true harm of a computer virus lies in its “payload” – the set of actions the virus is designed to perform. These actions can range from minor annoyances to catastrophic data loss and system compromise.
Data Corruption and Deletion
One of the most common and damaging payloads is the ability to corrupt or delete data.
- File Encryption (Ransomware): While often associated with specific types of malware, some viruses can encrypt a user’s files, making them inaccessible. The attackers then demand a ransom for the decryption key.
- Data Overwriting: Some viruses can overwrite the contents of files, rendering them unusable and permanently damaging data.
- System File Damage: Critical operating system files can be targeted, leading to system instability, crashes, and the inability to boot the computer.
Performance Degradation and System Instability
Viruses can significantly impact the performance and stability of a computer.
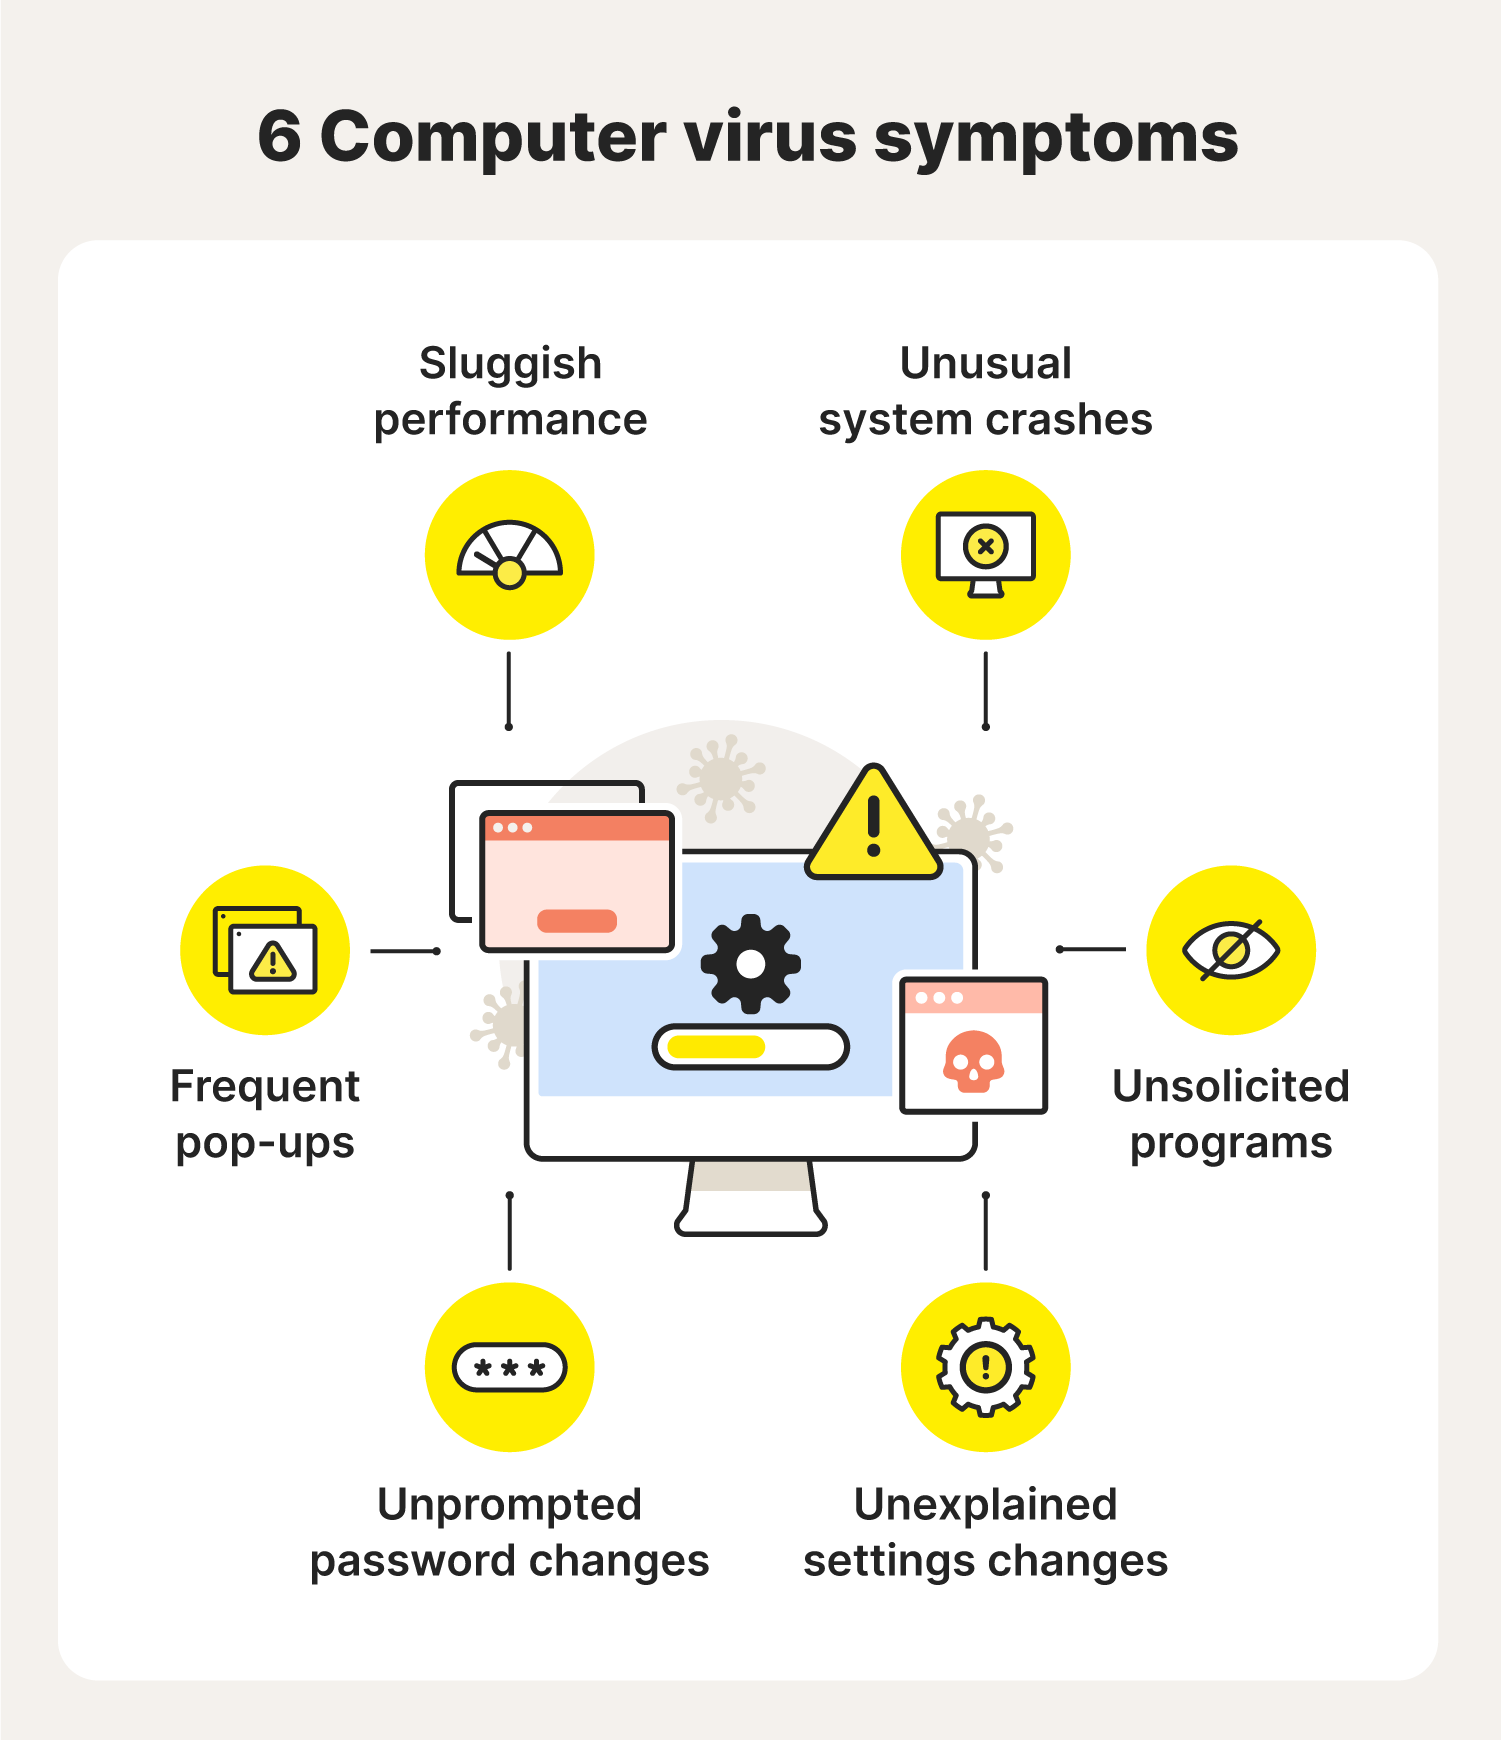
- Resource Hogging: Viruses often consume excessive CPU, memory, or network bandwidth, slowing down the system to a crawl. This can make it difficult or impossible to run legitimate applications.
- Frequent Crashes and Freezes: By corrupting system files or interfering with running processes, viruses can cause the computer to crash or freeze unexpectedly, leading to lost work and frustration.
- Unusual Pop-ups and Advertisements: Some viruses display an excessive number of pop-up ads or redirect web browsers to unwanted sites, disrupting the user experience.
Information Theft and Privacy Invasion
A particularly insidious aspect of virus activity is its potential for stealing sensitive information.
- Keyloggers: These are programs that record every keystroke a user makes, capturing usernames, passwords, credit card numbers, and other confidential information.
- Spyware: Viruses can act as spyware, monitoring user activity, collecting personal data, and transmitting it to the attacker. This can include browsing history, email contents, and even webcam footage.
- Credential Harvesting: Viruses can scan systems for stored passwords or attempt to trick users into revealing them through fake login pages.
Network Disruption and Remote Control
Viruses can also be used to compromise networks and gain remote access.
- Creating Botnets: Infected computers can be turned into “bots” controlled by a remote attacker, forming a botnet. These botnets can be used to launch Distributed Denial of Service (DDoS) attacks, send spam, or mine cryptocurrency without the user’s knowledge.
- Network Spreading: Some viruses are designed to actively scan networks for vulnerable systems and spread themselves, turning a single infection into a widespread outbreak.
- Backdoors: Viruses can install backdoors, allowing attackers to bypass security measures and gain persistent remote access to the infected system.
Types of Computer Viruses and Their Behavior
While the general principles of infection and payload apply broadly, different types of viruses exhibit distinct behaviors and propagation methods.
Boot Sector Viruses
- Behavior: Infect the master boot record (MBR) or the boot sector of a disk. They load into memory when the computer boots up, often before the operating system is fully loaded.
- Impact: Can prevent the computer from booting, spread to other disks, and corrupt boot information.
File Infector Viruses
- Behavior: Attach themselves to executable files. When the infected file is run, the virus code executes and infects other files.
- Impact: Corrupt program files, lead to system instability, and spread easily when infected files are shared.
Macro Viruses
- Behavior: Embedded within documents (e.g., Microsoft Word, Excel) and use macro languages. They execute when the document is opened and the macros are enabled.
- Impact: Can infect other documents, spread through email attachments, and potentially damage or delete data within spreadsheets or word processing files.
Polymorphic Viruses
- Behavior: Change their code with each infection, making them difficult for traditional signature-based antivirus software to detect. They use encryption and variable routines to alter their appearance.
- Impact: Evade detection, making them a persistent threat.
Metamorphic Viruses
- Behavior: More advanced than polymorphic viruses, they rewrite their entire code with each new infection, creating a completely new virus body. They may also use code obfuscation techniques.
- Impact: Extremely challenging to detect and remove due to their constantly evolving nature.
Resident Viruses
- Behavior: Load themselves into the computer’s memory and remain active. They can intercept system operations and infect files as they are accessed or executed.
- Impact: Can continuously infect files and spread throughout the system without requiring direct user interaction for each new infection.
Non-Resident Viruses
- Behavior: Do not remain in memory. They activate when an infected file is run, perform their actions, and then exit.
- Impact: Generally less persistent than resident viruses but can still cause significant damage when executed.
Conclusion: The Ever-Evolving Threat Landscape
The question of “what does a computer virus do” reveals a complex and constantly evolving threat landscape. From simple self-replication to sophisticated data theft and system hijacking, viruses represent a significant challenge to digital security. Their ability to adapt, exploit vulnerabilities, and leverage human behavior means that a proactive and multi-layered approach to cybersecurity is essential. Understanding the fundamental mechanisms of how viruses infect, replicate, and deploy their malicious payloads empowers users and organizations to better protect themselves against these persistent digital adversaries. Vigilance, regular software updates, robust antivirus protection, and cautious online behavior remain the cornerstones of defense against the ever-present threat of computer viruses.