
The Imperative of Security in Drone Technology
The rapid evolution of drone technology has ushered in an era of unprecedented innovation, transforming industries from logistics and agriculture to infrastructure inspection and public safety. Modern drones are no longer mere remote-controlled aircraft; they are sophisticated platforms integrating advanced AI, autonomous flight capabilities, precise navigation, and powerful remote sensing payloads. This technological advancement means that drones are increasingly involved in collecting, processing, and transmitting highly sensitive and valuable data. Whether it’s detailed geospatial maps of critical infrastructure, proprietary agricultural insights, personal data captured during surveillance, or the intricate flight plans for autonomous delivery networks, the information handled by drone systems carries significant weight.

With this proliferation of sensitive data and mission-critical operations comes an escalating demand for robust security. Unauthorized access, data breaches, and system compromises pose severe risks, potentially leading to operational failures, intellectual property theft, privacy violations, and even physical harm if autonomous systems are manipulated. For innovators pushing the boundaries of drone capabilities – from AI follow modes and predictive analytics to complex swarm intelligence and urban air mobility – ensuring the integrity and confidentiality of their systems and data is not just a best practice; it is a foundational requirement for trust and widespread adoption. Robust authentication, built upon secure mechanisms like password hashing, stands as the first line of defense in protecting these cutting-edge innovations from a rapidly evolving threat landscape.
Understanding Password Hashing: A Core Security Mechanism
At its heart, password hashing is a cryptographic process designed to safeguard user authentication credentials. Rather than storing passwords in a recoverable format, systems convert them into a unique, fixed-length string of characters – known as a hash value or digest – before storage. This seemingly simple step is a monumental leap in cybersecurity, particularly relevant for protecting the intricate ecosystems surrounding drone technology.
The Basics of Hashing
A hash function is a one-way mathematical algorithm that takes an input (in this case, a password) and produces a fixed-size string of characters. Key properties define its effectiveness:
- Deterministic: The same input will always produce the same output hash.
- Fast to Compute: It should be quick to generate a hash from a given input.
- One-Way (Irreversible): It is computationally infeasible to reverse the hash to find the original input. This means you cannot get the original password back from its hash.
- Collision Resistance (within practical limits): It should be extremely difficult to find two different inputs that produce the same hash output.
Think of a hash as a digital fingerprint for a piece of data. Just as two different people won’t have the same fingerprint, two different passwords should ideally produce different hashes. If an attacker gains access to a database of hashed passwords, they have a collection of fingerprints, not the actual identities.
Why Not Store Passwords in Plaintext?
The alternative to hashing is storing passwords in plaintext – their original, readable form. This practice is universally condemned in cybersecurity for good reason. If a system’s database is breached (a common occurrence, unfortunately), any passwords stored in plaintext become instantly available to the attackers. This catastrophic scenario grants adversaries immediate access to user accounts, not just within the compromised system but potentially across multiple services if users have reused passwords. For drone platforms handling sensitive operational data or controlling expensive hardware, a plaintext breach could lead to devastating consequences, including financial loss, operational disruption, intellectual property theft, or even the weaponization of drone capabilities.
How Hashing Protects
By storing only the hashed version of a password, even if an attacker successfully breaches a system’s database, they do not gain immediate access to user credentials. What they obtain are hash values. To convert these hashes back into usable passwords, an attacker would need to employ brute-force attacks (trying every possible combination of characters until a match is found) or utilize “rainbow tables” (pre-computed lists of hashes for common passwords). Both methods are significantly more resource-intensive and time-consuming than simply reading plaintext passwords. Modern hashing techniques, especially when combined with salting and key stretching, make these attacks computationally prohibitive, buying time for detection and mitigation, and vastly increasing the effort required for a successful compromise.
Hashed Passwords in the Drone Ecosystem
The integration of advanced technologies like AI, autonomous flight, and remote sensing into drones means that security, underpinned by robust authentication methods like password hashing, is critical across numerous touchpoints within the drone ecosystem.
Securing Drone Platforms and Ground Control Stations (GCS)
Every drone operation, whether for a single mission or a fleet-wide deployment, begins with authentication. Users log into cloud-based drone management platforms, ground control station (GCS) software, or proprietary enterprise systems. These platforms are the nerve centers where flight plans are meticulously crafted, mission parameters are defined, airspace clearances are managed, and real-time operational data is monitored.
Without strong password hashing, an attacker who compromises the database of one of these systems could gain access to:
- Sensitive Operational Data: This includes flight paths over critical infrastructure, details of valuable assets being monitored, or surveillance targets.
- Autonomous Mission Control: The ability to initiate, alter, or cancel autonomous missions, potentially diverting drones, disrupting operations, or causing significant damage.
- Fleet Management: Unauthorized control over an entire fleet of drones, impacting logistics, delivery services, or emergency response capabilities.
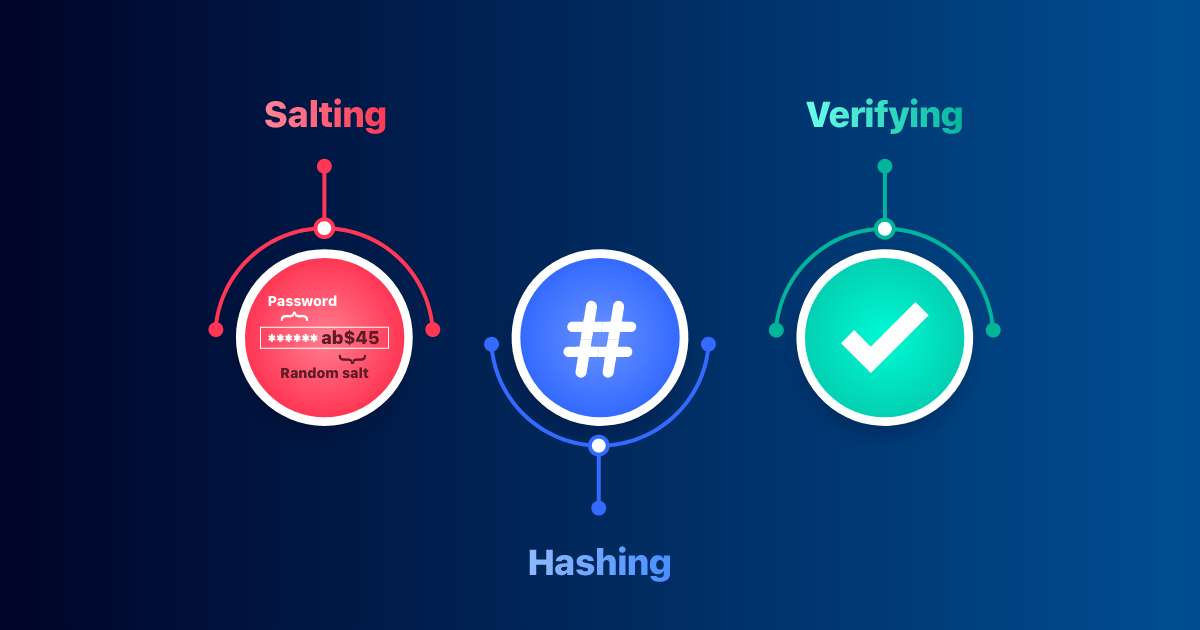
Hashing ensures that even if credentials databases are compromised, the actual passwords remain unexposed, safeguarding the integrity of drone operations and the sensitive data associated with them.
Protecting Drone-Generated Data and Remote Sensing Outputs
Drones equipped with high-resolution cameras, thermal imagers, LiDAR, and multispectral sensors generate enormous volumes of valuable data. This includes:
- Mapping Data: High-fidelity 2D maps, 3D models, and digital elevation models used in construction, urban planning, and environmental monitoring.
- Inspection Data: Critical imagery and analytical reports from inspecting power lines, wind turbines, bridges, or pipelines.
- Agricultural Insights: Data on crop health, soil conditions, and yield predictions.
- AI-Processed Insights: Derived intelligence from raw drone data, such as anomaly detection in infrastructure or object recognition in surveillance feeds.
This data is often stored in cloud repositories or secure on-premise servers. Access to these storage solutions, data processing pipelines, and analytical dashboards is typically protected by user accounts. Hashed passwords are fundamental to:
- Access Control: Ensuring that only authorized personnel can view, download, or analyze sensitive drone-generated data.
- Data Integrity: Preventing unauthorized individuals from tampering with critical data or AI models derived from it.
- Compliance: Meeting stringent data protection regulations (e.g., GDPR, HIPAA for health-related drone data) that mandate robust security for sensitive information.
A breach of password hashes here, while not ideal, is vastly preferable to a plaintext breach, as it provides a critical layer of defense against direct access to valuable intellectual property and confidential information.
Ensuring Integrity of Autonomous Flight Systems and AI Models
While drones themselves typically don’t have “login screens” in the traditional sense, the systems that manage and update their firmware, AI models, and mission parameters do. For autonomous flight to be reliable and secure, the underlying software and AI algorithms must be protected from malicious alteration.
- Firmware Updates: Authentication is required for secure over-the-air (OTA) or wired updates of drone firmware, ensuring only verified software is installed.
- AI Model Deployment: Access to deploy new or updated AI models (e.g., for object recognition, navigation, or anomaly detection) must be strictly controlled.
Hashing contributes to this by securing the accounts of developers, operators, and administrators who have the privileges to interact with these critical system components. By protecting their credentials, it indirectly safeguards the integrity and trustworthiness of the autonomous systems themselves, preventing unauthorized code injection or manipulation that could lead to erratic behavior or compromised missions.
API and Inter-System Communication
Modern drone ecosystems are highly interconnected, relying on Application Programming Interfaces (APIs) to facilitate communication between various services. This includes integrating with airspace management systems, weather data providers, post-processing analytics platforms, and command-and-control applications. Secure API keys and authentication tokens, often generated or protected by user credentials that employ hashing, are vital for ensuring that only authorized systems and applications can exchange data. This complex web of interactions underscores the pervasive need for strong, hashed password protection at every entry point and interaction layer.
Advancements in Hashing and Future Implications for Drone Security
The field of cybersecurity is constantly evolving, and password hashing techniques have advanced significantly to counter increasingly sophisticated threats. For drone technology to remain at the forefront of innovation, it must integrate these cutting-edge security practices.
Salting
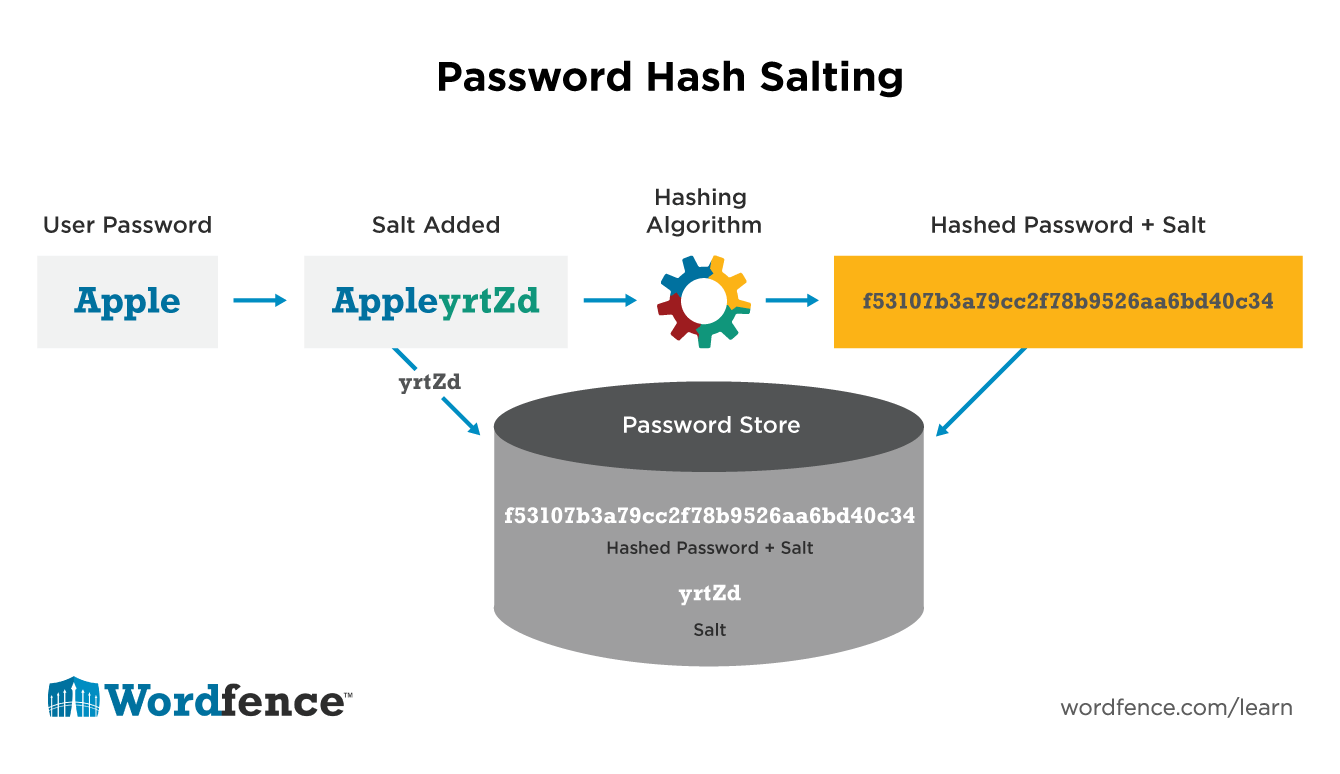
A critical advancement is “salting.” A salt is a unique, random string of data added to each password before it is hashed. This means that even if two users choose the exact same password, their stored hashes will be completely different because different salts were used.
- Mitigates Rainbow Tables: Rainbow tables, pre-computed lists of hashes for common passwords, become useless because the salt makes each hash unique.
- Prevents Hash Collisions for Identical Passwords: An attacker cannot tell if two users have the same password by simply comparing their hashes, as each will be salted differently.
- Increased Brute-Force Difficulty: Attackers must now perform a separate brute-force attack for each individual salted hash, dramatically increasing the computational effort required.
Iteration / Key Stretching
Modern hashing algorithms go beyond simple, single-pass hashing. “Key stretching” or “iteration” involves repeatedly hashing the password (and salt) hundreds or thousands of times. This process intentionally makes hashing slower. While imperceptible to a single user logging in, it significantly increases the computational cost for an attacker attempting millions or billions of guesses per second. Algorithms specifically designed for this, such as PBKDF2, bcrypt, scrypt, and Argon2, are considered industry standards for password storage today. Their adoption within drone platform authentication systems ensures maximum resistance against brute-force attacks.
Multi-Factor Authentication (MFA) and Beyond
While password hashing forms the bedrock of secure authentication, Multi-Factor Authentication (MFA) adds crucial layers of security. By requiring users to provide two or more verification factors (e.g., something they know like a password, something they have like a phone or hardware token, or something they are like a fingerprint), MFA drastically reduces the risk of unauthorized access even if a password or hash is compromised. Integrating MFA into drone management systems, GCS applications, and data repositories is an indispensable step to fortify security for autonomous flight and advanced remote sensing operations. Future developments will likely see greater adoption of FIDO standards, biometric authentication, and passwordless systems, all building upon the foundational principles of secure identity verification.
The Evolving Threat Landscape
The journey of securing drone technology is continuous. As quantum computing emerges, there are long-term concerns about its potential to break current cryptographic hashes, necessitating research into quantum-resistant cryptography. In the nearer term, social engineering, phishing attacks, and sophisticated malware continue to pose threats. Therefore, maintaining robust, up-to-date hashing algorithms, combining them with MFA, and educating users on best security practices are essential to protecting the cutting-edge innovations that drones bring to the world. Hashed passwords remain an indispensable component in this ongoing endeavor, ensuring the integrity and confidentiality of the complex digital fabric underpinning modern drone operations.