
The Fundamental Role of HTTP Cookies in Web Innovation
In the vast and interconnected digital landscape, HTTP cookies stand as unassuming yet profoundly influential pieces of web technology, fundamental to the interactive and personalized experiences we routinely encounter online. Far from being a recent invention, the concept of the “magic cookie” dates back to earlier computing contexts, but its application to the World Wide Web, pioneered by Lou Montulli at Netscape Communications in 1994, revolutionized internet functionality. Essentially, a cookie is a small piece of data that a server sends to a user’s web browser. The browser may then store it and send it back with the next request to the same server. This simple mechanism allows websites to “remember” stateful information or to record the user’s browsing activity. Without cookies, the stateless nature of HTTP would make many common web functions – like logging in, maintaining a shopping cart, or remembering user preferences – either impossible or significantly more cumbersome to implement. They enabled a paradigm shift, transforming the web from a static repository of documents into a dynamic, interactive platform tailored to individual users.
Session Management and User Experience
One of the most critical functions of HTTP cookies is session management. When a user logs into a website, the server typically generates a unique session ID. This ID is then stored in a cookie on the user’s browser. With every subsequent request the user makes to that website, their browser sends this session ID cookie back to the server. The server uses this ID to identify the user and retrieve their session data, such as their authentication status, items in their shopping cart, or other temporary preferences for that browsing session. This seamless exchange allows users to navigate through multiple pages on a website without having to re-authenticate or re-enter information repeatedly. For instance, an e-commerce site relies heavily on session cookies to keep track of items added to a shopping cart as a user browses different product pages. Without this, each click would be an isolated event, making the online shopping experience impractical and frustrating. The ability to maintain state across multiple interactions is a cornerstone of modern web applications, fostering a smoother, more efficient, and user-friendly online experience. This extends beyond e-commerce to social media platforms, banking portals, and any service requiring user authentication or persistent state.
Personalization and Targeted Content
Beyond session management, cookies are instrumental in personalizing user experiences and delivering targeted content. By tracking user behavior over time – such as pages visited, products viewed, or searches performed – websites can build a profile of a user’s interests. This information can then be leveraged to customize the website’s content, recommendations, and advertisements. For example, a news website might use cookies to remember a user’s preferred topics and display more relevant articles on their homepage. An online retailer might suggest products based on past purchases or browsing history, enhancing the likelihood of conversion. This level of personalization, while often raising privacy concerns, undeniably contributes to a more engaging and relevant internet for many users. The underlying innovation here is the shift from a one-size-fits-all web to an individualized digital landscape, where content dynamically adapts to reflect user preferences and historical interactions. This has been a driving force behind the success of many internet businesses, enabling them to provide highly curated experiences that foster engagement and loyalty.
Technical Mechanisms and Types of Cookies
Understanding cookies requires a grasp of their fundamental technical characteristics and classifications. While they all serve the purpose of storing small pieces of data, the context, duration, and origin of these cookies dictate their specific functionalities and implications.
First-Party vs. Third-Party Cookies
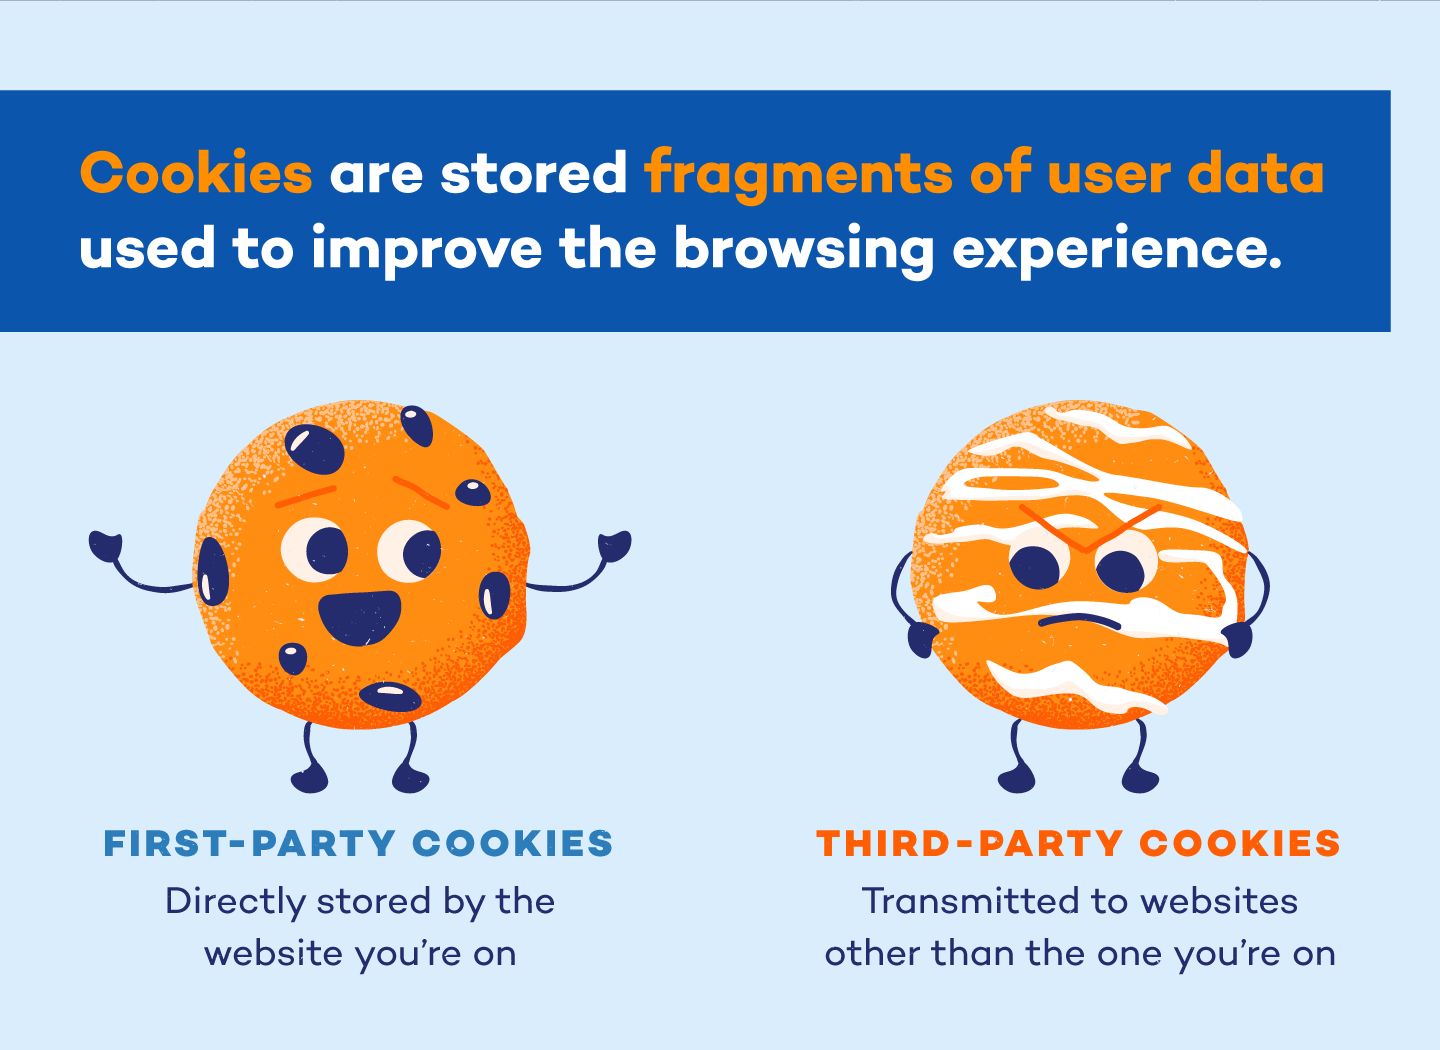
Cookies are primarily categorized by their origin relative to the website the user is currently visiting. A first-party cookie is created and set by the domain that the user is directly visiting. For instance, when you visit example.com, any cookie set by example.com is a first-party cookie. These are generally used for legitimate site functions like remembering login status, user preferences, or tracking items in a shopping cart, directly enhancing the user’s experience on that specific site. They are crucial for a website’s core functionality.
In contrast, a third-party cookie is set by a domain other than the one the user is currently visiting. These often originate from external services embedded within the website, such as advertisers, analytics providers, or social media widgets. For example, if example.com uses an advertising network adnetwork.com to display ads, adnetwork.com might set a third-party cookie on the user’s browser. These cookies are primarily used for cross-site tracking, enabling advertisers to follow a user’s browsing habits across different websites to build comprehensive profiles for targeted advertising. While useful for ad monetization and analytics, third-party cookies have become a significant focus of privacy debates due to their potential for extensive user tracking without explicit consent, leading many browsers to restrict or block them by default.
Persistent vs. Session Cookies
Another key distinction is based on a cookie’s lifespan. Session cookies are temporary and are only stored for the duration of a user’s browsing session. They are deleted from the user’s device once the browser is closed. These are predominantly used for session management, ensuring that a user remains logged in or their shopping cart contents are preserved as they navigate within a single website during a visit. They facilitate a continuous experience for the user without leaving a lasting trace on their device beyond the active session.
Persistent cookies, on the other hand, remain on the user’s device for a specified period, even after the browser is closed. They have an expiration date set by the web server (e.g., one month, one year, or even several years). These are used for remembering user preferences over longer periods, such as language settings, theme choices, or login credentials (if the “remember me” option is selected). They are also essential for analytics to track returning users and their long-term browsing patterns. The extended lifespan of persistent cookies makes them valuable for maintaining continuity of experience across multiple visits, but also raises further considerations regarding data retention and privacy.
Secure and HTTP-Only Flags
Modern web security incorporates specific attributes to enhance cookie safety. The Secure flag ensures that a cookie is only sent over HTTPS (encrypted) connections, preventing sensitive information from being intercepted by attackers over insecure networks. The HttpOnly flag prevents client-side scripts (like JavaScript) from accessing the cookie. This significantly mitigates the risk of cross-site scripting (XSS) attacks, where malicious scripts could otherwise steal sensitive cookies (such as session IDs) and hijack user accounts. These flags represent crucial technical innovations in safeguarding user data transmitted via cookies, reflecting an ongoing effort to balance functionality with robust security.
Privacy Implications and Regulatory Responses
While cookies have been instrumental in enabling much of the web’s functionality and personalized experience, their pervasive use, particularly by third parties, has ignited significant privacy concerns. The ability to track users across disparate websites and build detailed behavioral profiles without explicit consent has led to calls for greater transparency and control.
Data Collection and Profiling Concerns
The primary privacy concern stems from the vast amounts of data that can be aggregated through cookies. Third-party cookies, especially, allow advertising networks and data brokers to construct comprehensive user profiles encompassing browsing history, interests, demographics (inferred), and even purchasing habits. This data can then be used for highly targeted advertising, which, while beneficial for marketers, can feel intrusive and manipulative to users. There are also concerns about data security – if these extensive profiles are breached, sensitive personal information could be exposed. Furthermore, the lack of transparency about who is collecting this data, how it’s being used, and how long it’s stored often leaves users feeling disempowered and unaware of their digital footprint. The practice of “retargeting,” where ads for products a user has viewed follow them across the internet, is a direct consequence of this profiling capability and often cited as an example of intrusive cookie use.
GDPR, CCPA, and Cookie Consent
The growing public and regulatory scrutiny over data privacy has led to the enactment of landmark legislation designed to empower users and regulate data collection practices. The General Data Protection Regulation (GDPR), implemented in the European Union in 2018, is perhaps the most comprehensive data privacy law globally. It mandates that websites obtain explicit, informed consent from users before setting most non-essential cookies. Users must be presented with clear choices regarding what data is collected and for what purpose, with the option to accept or reject different categories of cookies. This “opt-in” requirement has led to the ubiquitous “cookie consent banners” seen across websites serving EU citizens.
Similarly, the California Consumer Privacy Act (CCPA), enacted in 2020, provides California residents with rights concerning their personal information, including the right to know what data is being collected and the right to opt-out of its sale. While CCPA’s approach to cookie consent is slightly different, generally allowing for “opt-out” rather than “opt-in,” both GDPR and CCPA have profoundly reshaped how websites implement and manage cookies, pushing for greater transparency and user control. These regulatory innovations represent a significant shift towards prioritizing user privacy in the digital age, compelling technology providers to rethink their data collection strategies.
The Evolving Landscape of Web Tracking
The tension between the utility of cookies for web functionality and their implications for user privacy has spurred significant innovation in both alternatives to traditional cookies and browser-level controls, pointing towards a future where user privacy is increasingly paramount.
Cookie Alternatives and Future Trends
The deprecation of third-party cookies by major browser vendors, notably Google Chrome’s planned phase-out, marks a pivotal shift in the web tracking landscape. This move is largely driven by privacy concerns and aims to reduce cross-site tracking. In response, the industry is exploring and developing various cookie alternatives. One such innovation is Federated Learning of Cohorts (FLoC), proposed by Google as part of its Privacy Sandbox initiative (though FLoC itself has been replaced by the “Topics API”). The idea behind these approaches is to allow advertisers to target groups of users with similar interests (cohorts) rather than individual users, thereby preserving a degree of privacy while still enabling relevant advertising. Other alternatives include various forms of contextual advertising, first-party data strategies, and probabilistic fingerprinting (though fingerprinting is also highly controversial due to its invasiveness). The challenge lies in finding solutions that maintain the economic viability of the ad-supported web without compromising user privacy. The development and adoption of these new standards represent a significant area of ongoing tech innovation.

Browser Innovations and User Control
Web browsers are at the forefront of implementing privacy-enhancing technologies and providing users with more control over their online data. Beyond blocking third-party cookies by default (as done by Safari and Firefox for years), browsers are introducing features like Enhanced Tracking Protection, Intelligent Tracking Prevention, and various privacy dashboards. These tools allow users to easily see what trackers are active on a site, block them, or manage their cookie preferences more granularly. Browser extensions also offer additional layers of control, enabling users to block ads and trackers more aggressively. The trend is clearly towards giving users more transparent information and direct agency over how their data is collected and used. These innovations in browser technology are not merely incremental updates but represent a fundamental re-evaluation of the power balance between websites, advertisers, and the individual user, pushing the entire ecosystem towards more privacy-centric designs. The shift signifies a maturity in web technology, acknowledging the social responsibility that accompanies such powerful data collection capabilities.