
The Foundation of Secure Remote Tech & Innovation
In the expansive and interconnected world of modern technology, where innovation constantly pushes the boundaries of what’s possible—from autonomous systems and AI-driven platforms to sophisticated remote sensing applications—secure communication stands as an indispensable pillar. At the heart of much of this secure remote interaction lies the Secure Shell (SSH) protocol. While many complex systems and protocols operate behind the scenes, understanding the basics of SSH, particularly its default operational port, provides critical insight into the secure infrastructure supporting cutting-edge tech.
Demystifying SSH and its Default Port
SSH, or Secure Shell, is a cryptographic network protocol for operating network services securely over an unsecured network. It is predominantly used for remote command-line login and remote command execution, but it also supports secure file transfers and port forwarding. When a client initiates an SSH connection to a server, it attempts to establish a secure, encrypted tunnel through which all subsequent communication will pass. This ensures confidentiality, integrity, and authentication.
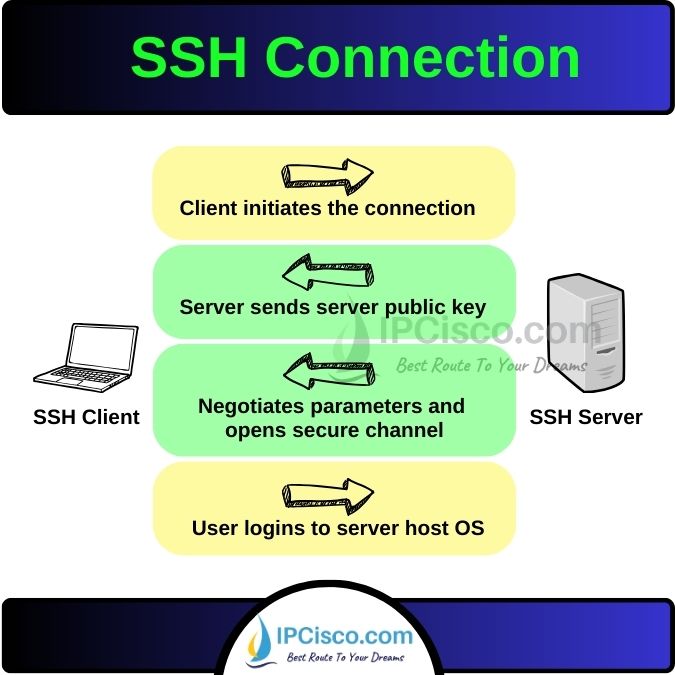
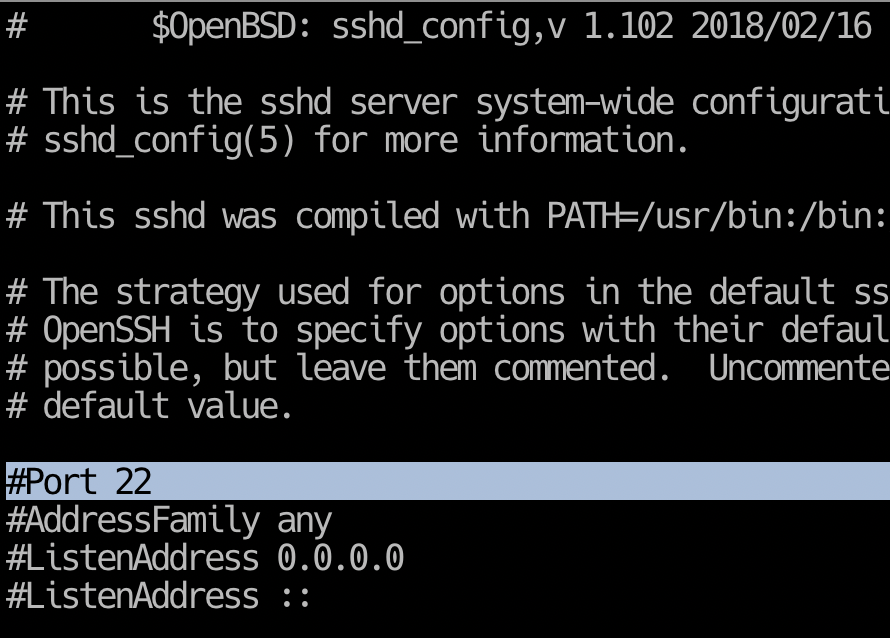
For this connection to be established, both the client and the server must agree on a designated communication channel, which is defined by a specific port number. The widely recognized and default port for SSH is TCP port 22. This port assignment is standardized by the Internet Assigned Numbers Authority (IANA) and is universally recognized, making it the first point of contact for most SSH clients attempting to connect to a server. While default, this port number is configurable on the server side, a practice often employed for enhanced security measures.
Why Secure Connectivity Matters for Advanced Tech
The relevance of SSH and its secure communication framework is magnified within the context of “Tech & Innovation.” Autonomous flight systems, for instance, often rely on ground control stations to monitor performance, push software updates, or retrieve diagnostic logs. AI models, particularly those deployed on distributed computing clusters or edge devices, require secure channels for data ingestion, model updates, and performance monitoring. Remote sensing platforms, from advanced drone payloads to satellite-based sensors, generate vast quantities of sensitive data that must be transferred securely for analysis.
In each of these scenarios, an unsecured connection poses significant risks: data breaches, unauthorized system access, intellectual property theft, or even malicious manipulation of critical operational parameters. SSH mitigates these risks by providing robust encryption and authentication mechanisms. It ensures that only authorized users or systems can access remote resources and that all data exchanged remains private and unaltered. This secure foundation is not merely a convenience but a fundamental requirement for maintaining the integrity, reliability, and trustworthiness of innovative technological deployments, underpinning everything from research and development to operational deployment and maintenance.
SSH in the Era of Autonomous Systems and AI
The proliferation of autonomous systems and advanced artificial intelligence technologies has introduced unprecedented complexities in system management, data handling, and security. SSH plays a pivotal, often unseen, role in ensuring the smooth and secure operation of these sophisticated technological ecosystems.
Securing Remote Access for Drone Fleets and Robotics
Consider a fleet of autonomous drones deployed for infrastructure inspection or environmental monitoring. Each drone is a complex computing platform that requires regular software updates, configuration adjustments, and periodic diagnostic checks. Manually accessing each drone for these tasks is impractical, if not impossible. SSH provides the secure remote access mechanism that allows operators or automated management systems to connect to individual drones or an entire fleet from a central command center. Through SSH, secure shell commands can be executed to:
- Push firmware updates: Ensuring all drones are running the latest, most secure, and feature-rich software.
- Retrieve diagnostic logs: Essential for troubleshooting performance issues, identifying potential hardware failures, or analyzing flight data.
- Adjust operational parameters: Modifying flight paths, sensor sensitivities, or mission profiles securely.
- Manage on-board applications: Starting, stopping, or configuring specialized applications running on the drone’s compute unit.
Similarly, advanced robotics in manufacturing or logistics benefit immensely from SSH for remote maintenance, secure programming, and integration into broader operational networks. The ability to securely connect to these intelligent machines remotely is crucial for minimizing downtime, enhancing efficiency, and protecting proprietary operational logic.
Data Integrity and Transfer for AI/ML Workflows
AI and Machine Learning (ML) initiatives are inherently data-intensive. Training sophisticated neural networks often requires terabytes or even petabytes of data, which may originate from diverse sources, including remote sensors, scientific instruments, or drone-collected imagery. This data must be securely transferred to high-performance computing clusters, cloud environments, or edge inference devices.
SSH, particularly through its associated secure file transfer protocols like SFTP (SSH File Transfer Protocol) or SCP (Secure Copy Protocol), provides the necessary robust and encrypted channels for this critical data movement. It ensures:
- Confidentiality: Preventing unauthorized access to sensitive training data.
- Integrity: Guaranteeing that data is not altered during transit, which is paramount for unbiased model training.
- Authentication: Verifying the identity of both the sender and receiver, preventing spoofing.
Beyond initial data transfer, SSH is also vital for managing the remote servers where AI models are trained and deployed. Data scientists and ML engineers frequently use SSH to log into GPU clusters, manage virtual environments, monitor training progress, and deploy trained models—all within a secure and authenticated session.
Configuration Management for Edge Devices
The rise of edge computing, where processing occurs closer to the data source—often at the network’s periphery, like on a drone or an IoT device—demands robust remote management capabilities. Edge devices, by their nature, can be physically difficult to access and operate in diverse, sometimes hostile, environments. SSH is a primary tool for securely configuring, updating, and troubleshooting these devices remotely. Whether it’s adjusting sensor calibration settings on an environmental monitoring drone, updating the inference engine on an AI-powered security camera, or pushing new control logic to an autonomous ground vehicle, SSH enables secure, non-intrusive management without exposing sensitive data or control planes to potential attackers. This capability is fundamental to scaling innovative edge solutions efficiently and securely.
Enhancing Security Beyond the Default Port
While SSH’s default port 22 is universally recognized, relying solely on this default configuration can present a security posture that, while robust in its encryption, is often targeted by automated scanning tools looking for easy entry points. Enhancing SSH security involves several layers of defense, extending beyond merely understanding the default port.
The Rationale for Changing SSH Port
One common security practice is to change the default SSH port from 22 to a non-standard, higher-numbered port (e.g., above 1024 or even above 49151 to avoid well-known ports). The primary reason for this is to deter automated, indiscriminate scanning and brute-force attacks. Many automated bots and scripts are programmed to exclusively target port 22 when attempting to discover and exploit SSH servers. By moving SSH to a different port, these unsophisticated attackers will bypass your server entirely, reducing the volume of malicious traffic and noise in your server logs.
It’s important to note that this practice is a form of “security through obscurity” and should not be considered a standalone solution. It merely reduces visibility to casual attackers; determined adversaries can still find an SSH service running on a non-standard port through port scanning techniques. However, it adds an initial layer of defense and reduces the attack surface from common, automated threats, allowing system administrators to focus on more sophisticated threats.
Best Practices for SSH Security
Beyond changing the default port, several critical best practices significantly enhance SSH security, particularly for systems involved in sensitive tech and innovation projects:
- Use Strong Passphrases or SSH Keys: Relying solely on passwords, especially weak ones, is a significant vulnerability. SSH keys provide a much stronger, more secure, and convenient method of authentication. A public-private key pair is generated, with the public key stored on the server and the private key securely held by the client. This eliminates the need for password exchange over the network and offers much higher cryptographic strength. If passwords must be used, enforce strong, complex passphrases and implement multi-factor authentication (MFA).
- Disable Password Authentication (if using keys): Once SSH key-based authentication is fully implemented and tested, it is highly recommended to disable password authentication entirely on the SSH server. This eliminates the possibility of brute-force password attacks.
- Disable Root Login: Direct SSH login as the
rootuser should be disabled. Instead, users should log in with a regular user account and then usesudoto gain root privileges when necessary. This limits the potential damage if a user account is compromised. - Implement Firewall Rules: Configure firewalls (e.g.,
ufw,firewalld, AWS Security Groups) to restrict SSH access to only trusted IP addresses or networks. This severely limits who can even attempt to connect to the SSH port, regardless of whether it’s the default or a custom one. - Regularly Update SSH Software: Keep the SSH client and server software (OpenSSH) up to date. Security patches often address newly discovered vulnerabilities that could be exploited by attackers.
- Monitor SSH Logs: Regularly review SSH logs for unusual activity, such as failed login attempts, login attempts from unfamiliar IPs, or unusually frequent connections. Intrusion detection systems (IDS) can automate this monitoring.
- Implement Fail2Ban or Similar Tools: Tools like Fail2Ban automatically ban IP addresses that show signs of malicious activity, such as multiple failed login attempts, protecting against brute-force attacks.

Integrating SSH with Modern Security Protocols
In advanced “Tech & Innovation” environments, SSH is often integrated into a broader security architecture. This can include:
- Virtual Private Networks (VPNs): SSH connections are often made over a VPN, adding another layer of encryption and network segmentation, especially for remote access to private cloud resources or corporate networks.
- Identity and Access Management (IAM) Systems: Integrating SSH authentication with centralized IAM systems (like LDAP, Active Directory, or cloud-based IAM solutions) ensures consistent user management and enforcement of granular access policies across an organization’s tech stack.
- Security Information and Event Management (SIEM) Systems: SSH logs are fed into SIEM platforms for centralized logging, correlation with other security events, and real-time threat detection, providing a comprehensive view of the security posture.
By adopting these advanced practices, organizations can ensure that their innovative ventures, from designing autonomous robots to deploying AI-powered analytics platforms, are underpinned by an SSH infrastructure that is not only functional but also resilient against evolving cyber threats.
SSH’s Role in Remote Sensing and Data Analysis
Remote sensing is a cornerstone of numerous “Tech & Innovation” fields, from climate science and precision agriculture to urban planning and defense. It involves collecting information about an object or phenomenon without making physical contact, typically using sensors on platforms like satellites, aircraft, or, increasingly, drones. SSH plays a crucial role in managing these remote sensing operations and securing the vast amounts of data they generate.
Secure Data Ingress from Remote Sensors
Modern remote sensing platforms, especially high-end drones equipped with LiDAR, hyperspectral cameras, or synthetic aperture radar (SAR), generate enormous datasets during a single mission. This data often contains sensitive or proprietary information—whether it’s detailed topographic maps, crop health metrics, or critical infrastructure imagery. Transferring this data from the drone’s on-board storage to ground control stations, cloud storage, or analytical servers requires a robust and secure mechanism.
SSH-based file transfer protocols like SFTP or SCP are frequently employed for this purpose. They ensure that the data:
- Remains confidential: Encrypted during transit, preventing eavesdropping or interception by unauthorized parties.
- Maintains integrity: Cryptographic hashes verify that the data has not been tampered with or corrupted during transfer, which is vital for the accuracy of subsequent analyses.
- Is properly authenticated: Only authorized ground systems or personnel can retrieve data from the remote sensor platform, preventing unauthorized extraction.
This secure ingress is fundamental for applications where data integrity and confidentiality are paramount, such as military reconnaissance, proprietary geological surveys, or sensitive environmental monitoring initiatives.
Managing High-Performance Computing Resources
Once remote sensing data is collected, it often requires significant computational power for processing, analysis, and transformation into actionable intelligence. This typically involves high-performance computing (HPC) clusters, cloud-based GPU instances, or specialized data centers. Researchers and analysts use SSH to remotely access and manage these powerful computing resources.
Through SSH, they can:
- Launch and monitor complex processing jobs: Orchestrating workflows that might involve photogrammetry, AI-driven image classification, or large-scale geospatial analysis.
- Transfer input and output data: Moving raw sensor data to the HPC cluster and retrieving processed results, such as 3D models, thematic maps, or analytical reports, all securely.
- Configure and maintain software environments: Installing necessary libraries, frameworks (e.g., TensorFlow, PyTorch, GDAL), and custom scripts required for specific remote sensing applications.
- Debug applications: Identifying and resolving issues in processing pipelines or analytical algorithms running on remote machines.
The ubiquitous nature of SSH in HPC environments ensures that the entire lifecycle of remote sensing data—from collection to advanced analysis—is enveloped in a secure and controllable framework.
Enabling Collaborative Innovation
“Tech & Innovation” thrives on collaboration, especially in complex fields like remote sensing, which often involve multidisciplinary teams across different geographical locations. Researchers, engineers, and data scientists may need to collaboratively access and work on shared datasets and computing resources. SSH facilitates this by providing a secure, authenticated channel for multiple users to interact with the same remote systems.
This enables:
- Shared access to project data: Teams can securely access common data repositories or processing environments.
- Collaborative code development: Developers can use SSH to push and pull code from version control systems on remote servers and collaborate on scripts and applications for data processing and analysis.
- Remote instruction and support: Experts can securely connect to a colleague’s remote session to provide assistance or demonstrate procedures, fostering knowledge transfer and accelerating problem-solving.
In essence, SSH is not just a tool for individual access but a foundational technology that underpins secure, distributed, and collaborative efforts in the rapidly evolving landscape of remote sensing and data analysis, propelling forward innovative solutions to global challenges.
Future Implications: SSH and Quantum-Safe Computing
As “Tech & Innovation” continues its relentless march forward, new paradigms and threats emerge, necessitating continuous evolution in foundational technologies like SSH. One of the most significant long-term challenges on the horizon is the advent of quantum computing and its potential impact on current cryptographic standards.
Addressing Emerging Threats
The cryptographic algorithms that underpin the security of current SSH implementations—such as RSA and ECC for key exchange and digital signatures—are considered secure against classical computers. However, future fault-tolerant quantum computers, once they become sufficiently powerful, could potentially break these algorithms through algorithms like Shor’s algorithm. This poses a significant long-term threat to the confidentiality and integrity of data secured with today’s public-key cryptography, including SSH sessions.
While practical, large-scale quantum computers capable of breaking current cryptography are still years, if not decades, away, the principle of “harvest now, decrypt later” is a genuine concern. Adversaries could theoretically collect encrypted SSH traffic today and store it, hoping to decrypt it once quantum computers become available. This necessitates proactive research and development into “quantum-safe” or “post-quantum” cryptography.
The Path to Post-Quantum Cryptography
The “Tech & Innovation” community, including cryptographic experts and organizations like the National Institute of Standards and Technology (NIST), is actively engaged in developing and standardizing new cryptographic algorithms that are resistant to attacks from quantum computers. These post-quantum cryptography (PQC) algorithms include lattice-based cryptography, code-based cryptography, multivariate polynomial cryptography, and hash-based cryptography.
The future evolution of SSH will undoubtedly involve integrating these new PQC algorithms. This will likely occur in stages:
- Hybrid Modes: Initial implementations may involve “hybrid” key exchange mechanisms, where both classical (e.g., ECDH) and post-quantum key exchange algorithms are used simultaneously to establish a shared secret. This offers a “belt-and-suspenders” approach, providing security even if one of the underlying algorithms is eventually broken.
- Algorithm Migration: As PQC algorithms mature and gain widespread adoption, SSH implementations will transition to primarily or exclusively use these quantum-resistant primitives for key exchange, authentication, and digital signatures.
- Standardization and Interoperability: Ensuring that new PQC-enabled SSH clients and servers can seamlessly communicate and interoperate will be critical for a smooth transition across the vast landscape of interconnected systems and services.
For sectors heavily reliant on SSH for securing critical infrastructure, sensitive data, and intellectual property—such as those involved in autonomous systems, AI research, and remote sensing—the transition to quantum-safe SSH is not merely an academic exercise but a strategic imperative. It underscores the continuous need for innovation in fundamental security technologies to safeguard the advancements driving our technological future. The secure communication facilitated by SSH, regardless of the underlying cryptographic algorithms, will remain a cornerstone for enabling trust and resilience in the face of emerging computational paradigms and threats.