
The Engineering Marvel of Statelessness: How Cookies Revolutionized Web Interactions
The internet, in its foundational design, is a stateless environment. This inherent characteristic of the Hypertext Transfer Protocol (HTTP) meant that each request from a web browser to a server was treated as an entirely new interaction, devoid of any memory of previous exchanges. While efficient for simple document retrieval, this statelessness posed a significant challenge for developing dynamic, interactive web applications that required maintaining user context across multiple pages – think of a shopping cart, a logged-in session, or personalized content. The advent of internet cookies marked a profound technological innovation, providing the crucial mechanism to bridge this stateless gap and enable the rich, interactive web experiences we now take for granted.

Bridging the HTTP Gap: Early Web Constraints
Before cookies, building a continuous user experience was cumbersome. Developers resorted to less elegant solutions like embedding session IDs directly into URLs or hidden form fields, which were prone to security vulnerabilities, difficult to manage, and limited in scope. The very structure of HTTP, designed for swift, independent transactions, became a bottleneck for persistent interactions. The challenge was to give the web a memory, allowing servers to “remember” individual users and their state without fundamentally altering the lightweight nature of HTTP. This required an ingenious, client-side data storage solution.
The Client-Side Data Store: A Simple Yet Profound Solution
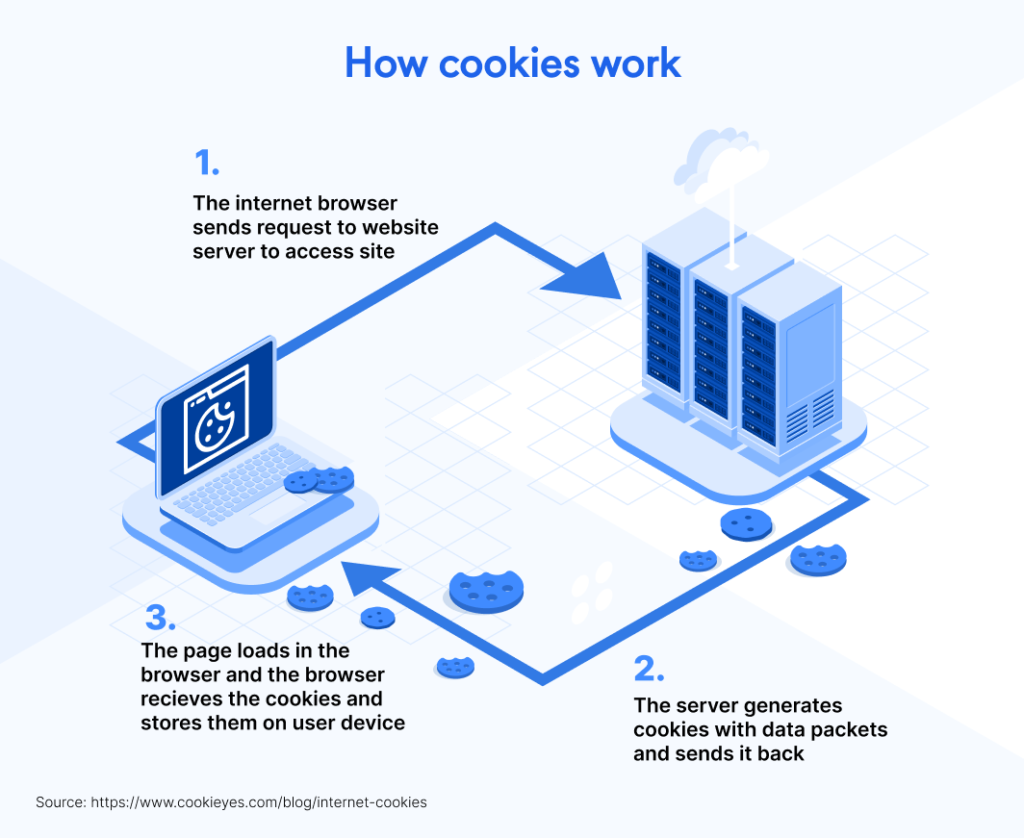
Introduced by Netscape in the mid-1990s, HTTP cookies emerged as that elegant solution. At their core, cookies are small pieces of data, typically text files, that a website’s server sends to a user’s web browser. The browser then stores these cookies and sends them back to the same server with every subsequent request. This seemingly simple mechanism instantly transformed the web’s capabilities. A server could now, for instance, issue a unique session ID cookie upon a user’s first visit. For all subsequent requests within that session, the browser would return this ID, allowing the server to retrieve the user’s specific data (like items in a shopping cart or login status) from its own backend, effectively simulating a stateful connection over a stateless protocol. This innovative approach to client-side data management became a cornerstone for nearly every interactive web application, fundamentally altering how developers approached web design and user experience.
Architectural Layers: Understanding Cookie Classifications and Their Digital Ecosystem Roles
The term “cookie” often elicits a singular image, but in practice, these tiny data packets exhibit diverse functionalities and architectural roles within the digital ecosystem. Understanding their classifications is key to appreciating their nuanced impact on web navigation, personalization, and the intricate world of online advertising. These variations represent different layers of technological implementation, each serving distinct purposes.
Functional Pillars: Session, Persistent, and Secure Cookies
Cookies can be broadly categorized by their lifespan and security attributes. Session cookies are ephemeral. They exist only temporarily while a user is actively browsing a website. Once the browser is closed, or the user logs out, these cookies are deleted. Their primary function is to maintain user context for the duration of a single visit, enabling seamless navigation through multi-page processes like online banking transactions or e-commerce checkouts. They are crucial for preserving the “state” of a user’s interaction.
In contrast, persistent cookies (also known as tracking cookies) have a defined expiration date, ranging from a few minutes to several years. They remain stored on the user’s device even after the browser is closed. These cookies are instrumental in remembering user preferences (e.g., language settings, theme choices), keeping users logged in across sessions, or tracking return visits for analytical purposes. Their longevity allows for a more personalized and consistent user experience over time.
Beyond lifespan, secure cookies introduce an important security layer. These cookies are transmitted only over encrypted HTTPS connections, preventing them from being intercepted by malicious actors during transit. This is vital for protecting sensitive information, such as login credentials or payment details, ensuring that the data exchanged between the browser and server remains confidential. Their implementation is a testament to the evolving security considerations in web technology.
The Tracking Dimension: First-Party vs. Third-Party Dynamics
A critical distinction, particularly in the context of privacy and advertising technology, is that between first-party and third-party cookies. First-party cookies are set by the website a user is directly visiting. For instance, when you log into an online store, that store places a cookie on your device to remember your login status or items in your cart. These cookies are generally considered essential for core website functionality and improving the user’s direct experience on that specific site. They are an intrinsic part of the site’s own technological infrastructure.
Third-party cookies, however, are set by a domain other than the one the user is currently visiting. These often originate from embedded content, such as advertisements, social media widgets, or analytics scripts, hosted on domains separate from the primary website. The innovative (and often controversial) application of third-party cookies lies in their ability to track user behavior across multiple, unrelated websites. For example, an advertising network might place a third-party cookie on a user’s browser when they visit Site A. If the user then visits Site B, which also uses the same advertising network, the network can read that same cookie, building a profile of the user’s browsing habits across diverse websites. This cross-site tracking capability forms the backbone of targeted advertising and audience segmentation, representing a significant technological leap in how digital marketing operates. However, it also sparked considerable debate regarding user privacy and data control, leading to significant shifts in browser technology and regulatory frameworks.
Cookies as Catalysts for Digital Innovation: E-commerce, Personalization, and Analytics
The humble cookie, despite its technical simplicity, proved to be an extraordinary catalyst for digital innovation. Its ability to maintain state and context fundamentally unlocked new paradigms for online interaction, transforming the web from a collection of static documents into a dynamic marketplace, an individualized content hub, and an indispensable source of actionable data.
Driving the E-commerce Revolution
The birth of e-commerce as a viable industry owes an immeasurable debt to cookie technology. Before cookies, the idea of adding multiple items to a virtual shopping cart, navigating to different product pages, and then proceeding to a unified checkout process was technically challenging, if not impossible, without complex server-side session management. Cookies provided the elegant solution. By assigning a unique session ID to a user, the e-commerce platform could store the contents of their cart on the server, linked to that ID. As the user browsed, the browser would send the cookie with each request, allowing the server to retrieve and update the correct cart. This made multi-step transactions seamless and user-friendly, paving the way for the explosive growth of online retail giants and countless smaller businesses. Without this foundational technology, the digital storefront as we know it would likely not exist in its current form.
Tailoring the User Experience: From Recommendations to Content Delivery
Beyond e-commerce, cookies became instrumental in creating personalized online experiences. Persistent cookies allowed websites to “remember” user preferences, such as language choices, regional settings, or even preferred layouts. This meant users no longer had to re-configure their settings on every visit, fostering a sense of familiarity and ease.
More sophisticated applications emerged in content personalization. News websites, streaming services, and social media platforms leveraged cookies to track user interactions – what articles they read, what videos they watched, what posts they engaged with. This behavioral data, combined with algorithms, enabled the delivery of highly tailored recommendations, ensuring that users were presented with content most relevant to their interests. This shift from a one-size-fits-all web to an individualized digital landscape dramatically increased engagement and retention, making online services feel more intuitive and valuable to the end-user. The ability to dynamically adapt content based on past interactions became a hallmark of modern web innovation.
Fueling Data-Driven Decisions: The Analytics Backbone
The capacity of cookies, especially persistent and third-party varieties, to track user journeys across websites and over time, laid the groundwork for the modern web analytics industry. Prior to robust cookie implementation, understanding user behavior on a grand scale was speculative. With cookies, website owners and digital marketers gained unprecedented insight into traffic sources, navigation paths, conversion rates, and user demographics.
Web analytics tools, built atop cookie technology, could meticulously map out how users interacted with a site, identifying popular pages, drop-off points, and effective marketing channels. This data became invaluable for optimizing website design, refining content strategies, and making informed business decisions. Furthermore, third-party cookies enabled the development of sophisticated advertising networks. By building detailed user profiles based on cross-site browsing history, these networks could deliver highly targeted advertisements, dramatically increasing the efficiency and effectiveness of online marketing campaigns. The innovative application of cookies transformed raw browsing data into actionable intelligence, fueling the data-driven economy of the internet.
Navigating the Future: Technological Shifts Beyond the Traditional Cookie
While internet cookies have been indispensable for decades, the technological landscape is in constant flux. Mounting privacy concerns, evolving regulatory frameworks, and advancements in alternative tracking methods are collectively pushing the industry towards a future less reliant on the traditional cookie, particularly the third-party variant. This represents a significant period of innovation, as developers and tech companies seek new ways to maintain functionality, personalization, and monetization while respecting user privacy.
Privacy Concerns and the Push for Alternatives
The cross-site tracking capabilities of third-party cookies, while powerful for advertising, increasingly drew scrutiny over user privacy. Users grew wary of their online activities being monitored without explicit consent, leading to a demand for greater transparency and control over personal data. Regulatory bodies worldwide responded with landmark legislation like the GDPR (General Data Protection Regulation) in Europe and the CCPA (California Consumer Privacy Act) in the US, mandating stricter rules around data collection and user consent. These regulations, combined with growing public awareness, created immense pressure on tech companies to innovate beyond methods perceived as privacy-invasive. The industry began to explore alternative identifiers and privacy-preserving approaches that could achieve similar outcomes without compromising user trust.
Browser Innovations and Privacy Sandboxes
Major browser developers have been at the forefront of this shift. Browsers like Safari and Firefox have already implemented aggressive third-party cookie blocking by default, significantly curtailing their efficacy. Google Chrome, the dominant browser, has announced its intention to phase out third-party cookies entirely by late 2024. This move is not merely a removal but an ambitious technological re-imagining through initiatives like the Privacy Sandbox.
The Privacy Sandbox is a suite of proposals designed to create new standards for privacy-preserving advertising, measurement, and analytics on the web. Instead of individual user tracking, it focuses on aggregated, anonymized data within the browser. Technologies like FLEDGE (First Locally-Executed Decision over Groups of Expedited) aim to enable interest-based advertising by allowing advertisers to show relevant ads to groups of users with shared interests, without knowing individual browsing history. Similarly, Topics API proposes categorizing user interests into broad, predefined topics directly within the browser, which can then be shared with websites without revealing specific browsing history. These represent complex cryptographic and algorithmic innovations to balance personalized experiences with enhanced user privacy, shifting the intelligence from external servers to the user’s own device.
Emerging Methodologies: Device Fingerprinting and Server-Side Solutions
In the void left by diminishing third-party cookies, other technologies have emerged or gained prominence. Device fingerprinting is one such method, which involves collecting numerous pieces of data about a user’s device (e.g., browser type and version, operating system, installed fonts, screen resolution, IP address) and compiling them into a unique “fingerprint” that can identify a user across different websites, often without their explicit knowledge or consent. This method, while powerful, is even more controversial than cookies due to its surreptitious nature and difficulty for users to control.
Another area of innovation involves server-side tracking and first-party data strategies. Instead of relying on client-side third-party cookies, businesses are increasingly implementing server-side tracking, where data is collected and processed directly by their own servers before being sent to marketing or analytics platforms. This allows for greater control over data, reduced reliance on third parties, and often bypasses browser-level cookie restrictions. Furthermore, companies are investing heavily in collecting and utilizing first-party data – data voluntarily provided by users or generated through their direct interactions with a brand’s properties. This shift encourages direct relationships with customers and fosters trust, as users are more likely to consent to data usage when they perceive a direct value exchange.
The evolution away from traditional cookies signifies a pivotal moment in web technology, driving innovation in privacy-preserving techniques, robust first-party data strategies, and new paradigms for advertising and personalization that prioritize user consent and data security. The ingenuity applied to solving the statelessness problem decades ago is now being redirected to building a more private, yet equally functional, internet.