
In the dynamic and interconnected world of modern technology, where digital interactions underpin everything from financial transactions to the control of advanced autonomous systems, cybersecurity stands as an immutable pillar of trust and functionality. Among the myriad vulnerabilities that threaten the integrity and confidentiality of these digital ecosystems, Cross-Site Request Forgery (CSRF), often pronounced “sea-surf,” remains a significant and often underestimated threat. This sophisticated attack vector exploits the trust a web application places in a user’s browser, compelling it to execute unauthorized commands without the user’s explicit consent or even their knowledge. Understanding CSRF is not merely an academic exercise for security professionals; it is a critical requirement for developers, IT architects, and anyone interacting with web-based services, particularly as tech innovation pushes the boundaries into areas like cloud-based drone management, IoT systems, and complex API-driven applications.
The Mechanics of a CSRF Attack
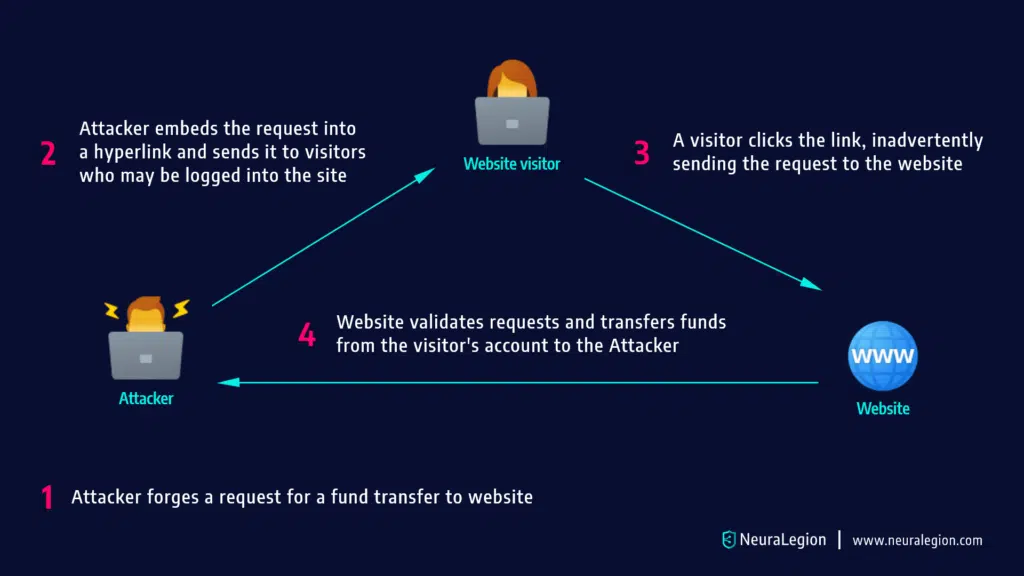
At its core, a CSRF attack leverages a user’s authenticated session with a legitimate website to trick their browser into sending a forged request to that site. This seemingly simple premise masks a powerful technique that can lead to severe consequences if not properly mitigated.
The Trust Factor: How Legitimate Requests Are Exploited
Most web applications use cookies to manage user sessions, authenticating a user once and then relying on these cookies for subsequent requests within that session. When a user logs into a website, the server issues a session cookie that the browser stores. For every subsequent request to that website, the browser automatically includes this cookie, proving the user’s identity. This mechanism is efficient but also forms the bedrock of the CSRF vulnerability. The web application implicitly trusts requests accompanied by a valid session cookie, assuming they originate from the legitimate user. An attacker exploits this trust by crafting a malicious request that, when triggered by the user’s browser, appears to the target website as a legitimate action performed by the authenticated user.
Forging a Request: The Attacker’s Role in Tricking the User’s Browser
An attacker typically hosts a malicious web page designed to deliver a forged request. This request can be hidden within an image tag, a form submission, an AJAX call, or even a simple link. For example, an attacker might embed an <img> tag where the src attribute points to a URL that, when accessed, performs a critical action on a vulnerable site (e.g., src="http://bank.com/transfer?account=attacker&amount=1000"). If an authenticated user of bank.com visits the attacker’s page, their browser, unaware of the malicious intent, will attempt to load the “image.” In doing so, it automatically includes the session cookie for bank.com, causing the bank’s server to process the request as if the user initiated a transfer to the attacker’s account. The user sees nothing amiss, perhaps just a broken image icon, while the unauthorized action is completed in the background.
Session Hijacking vs. CSRF: Differentiating Similar Attack Vectors
It’s crucial to distinguish CSRF from other web security threats, particularly session hijacking. While both involve exploiting user sessions, their methods and objectives differ. Session hijacking involves an attacker directly stealing a user’s session ID (e.g., via XSS or network sniffing) and then impersonating the user directly. The attacker operates as the user, having full control over their session. CSRF, on the other hand, does not involve stealing the session ID. Instead, the attacker leverages the user’s browser to force the user to send a request on their own behalf to the legitimate site. The attacker never gains direct access to the user’s session or the site’s data; they merely manipulate the user’s browser into performing an action. This distinction is vital for implementing appropriate defense mechanisms.
Real-World Impact and Exploitation Scenarios
The potential consequences of a successful CSRF attack range from minor annoyances to catastrophic data breaches and financial losses. Its effectiveness lies in its ability to bypass traditional authentication checks by leveraging an already authenticated session.
Financial Transactions: Unauthorized Transfers
One of the most concerning scenarios involves financial institutions. A CSRF attack can trick an authenticated user’s browser into initiating unauthorized money transfers, changing beneficiary details, or altering account settings. The attacker doesn’t need to know the user’s login credentials; they only need the user to be logged into their banking portal while simultaneously visiting a malicious site. The resulting damage can be immediate and severe, making robust CSRF protection an absolute necessity for banking and e-commerce platforms.
Account Management: Changing Passwords, Email Addresses
Beyond financial implications, CSRF can compromise user accounts on almost any web service. An attacker could craft a request that forces a user to change their account’s associated email address, effectively seizing control of the account through a password reset mechanism. Similarly, a forced password change could lock the legitimate user out of their account, granting the attacker exclusive access. This is particularly dangerous for platforms that manage sensitive personal data, intellectual property, or critical infrastructure access.
Data Manipulation: Deleting or Altering User Data
Many web applications allow users to manage their data, such as profile information, forum posts, or files. A CSRF vulnerability could be exploited to delete user-generated content, alter database entries, or even inject malicious data. Imagine a scenario where a project management tool allows collaborators to delete tasks. A CSRF attack could force a user to delete critical project milestones or sensitive documents, disrupting operations and potentially leading to significant financial or reputational damage.
Remote Control Systems & IoT: Implications for Connected Devices
As the Internet of Things (IoT) expands and remote control systems become more prevalent, the implications of CSRF extend beyond traditional web applications. Cloud-based drone fleet management platforms, smart home systems, industrial control panels accessed via web interfaces, and even connected vehicle dashboards could be vulnerable. An attacker could potentially trick an authenticated operator’s browser into sending commands to deploy a drone, alter its flight path, unlock a smart door, or trigger an industrial process. The consequences in such scenarios could range from privacy breaches and equipment damage to physical harm or widespread service disruptions, highlighting the critical need for comprehensive security considerations in this burgeoning sector of technology.

Protecting Against CSRF: Essential Defense Strategies
Given the insidious nature of CSRF, robust defense mechanisms are paramount. While no single solution is foolproof, a layered approach combining server-side and client-side strategies offers the best protection.
Anti-CSRF Tokens: The Primary Defense Mechanism
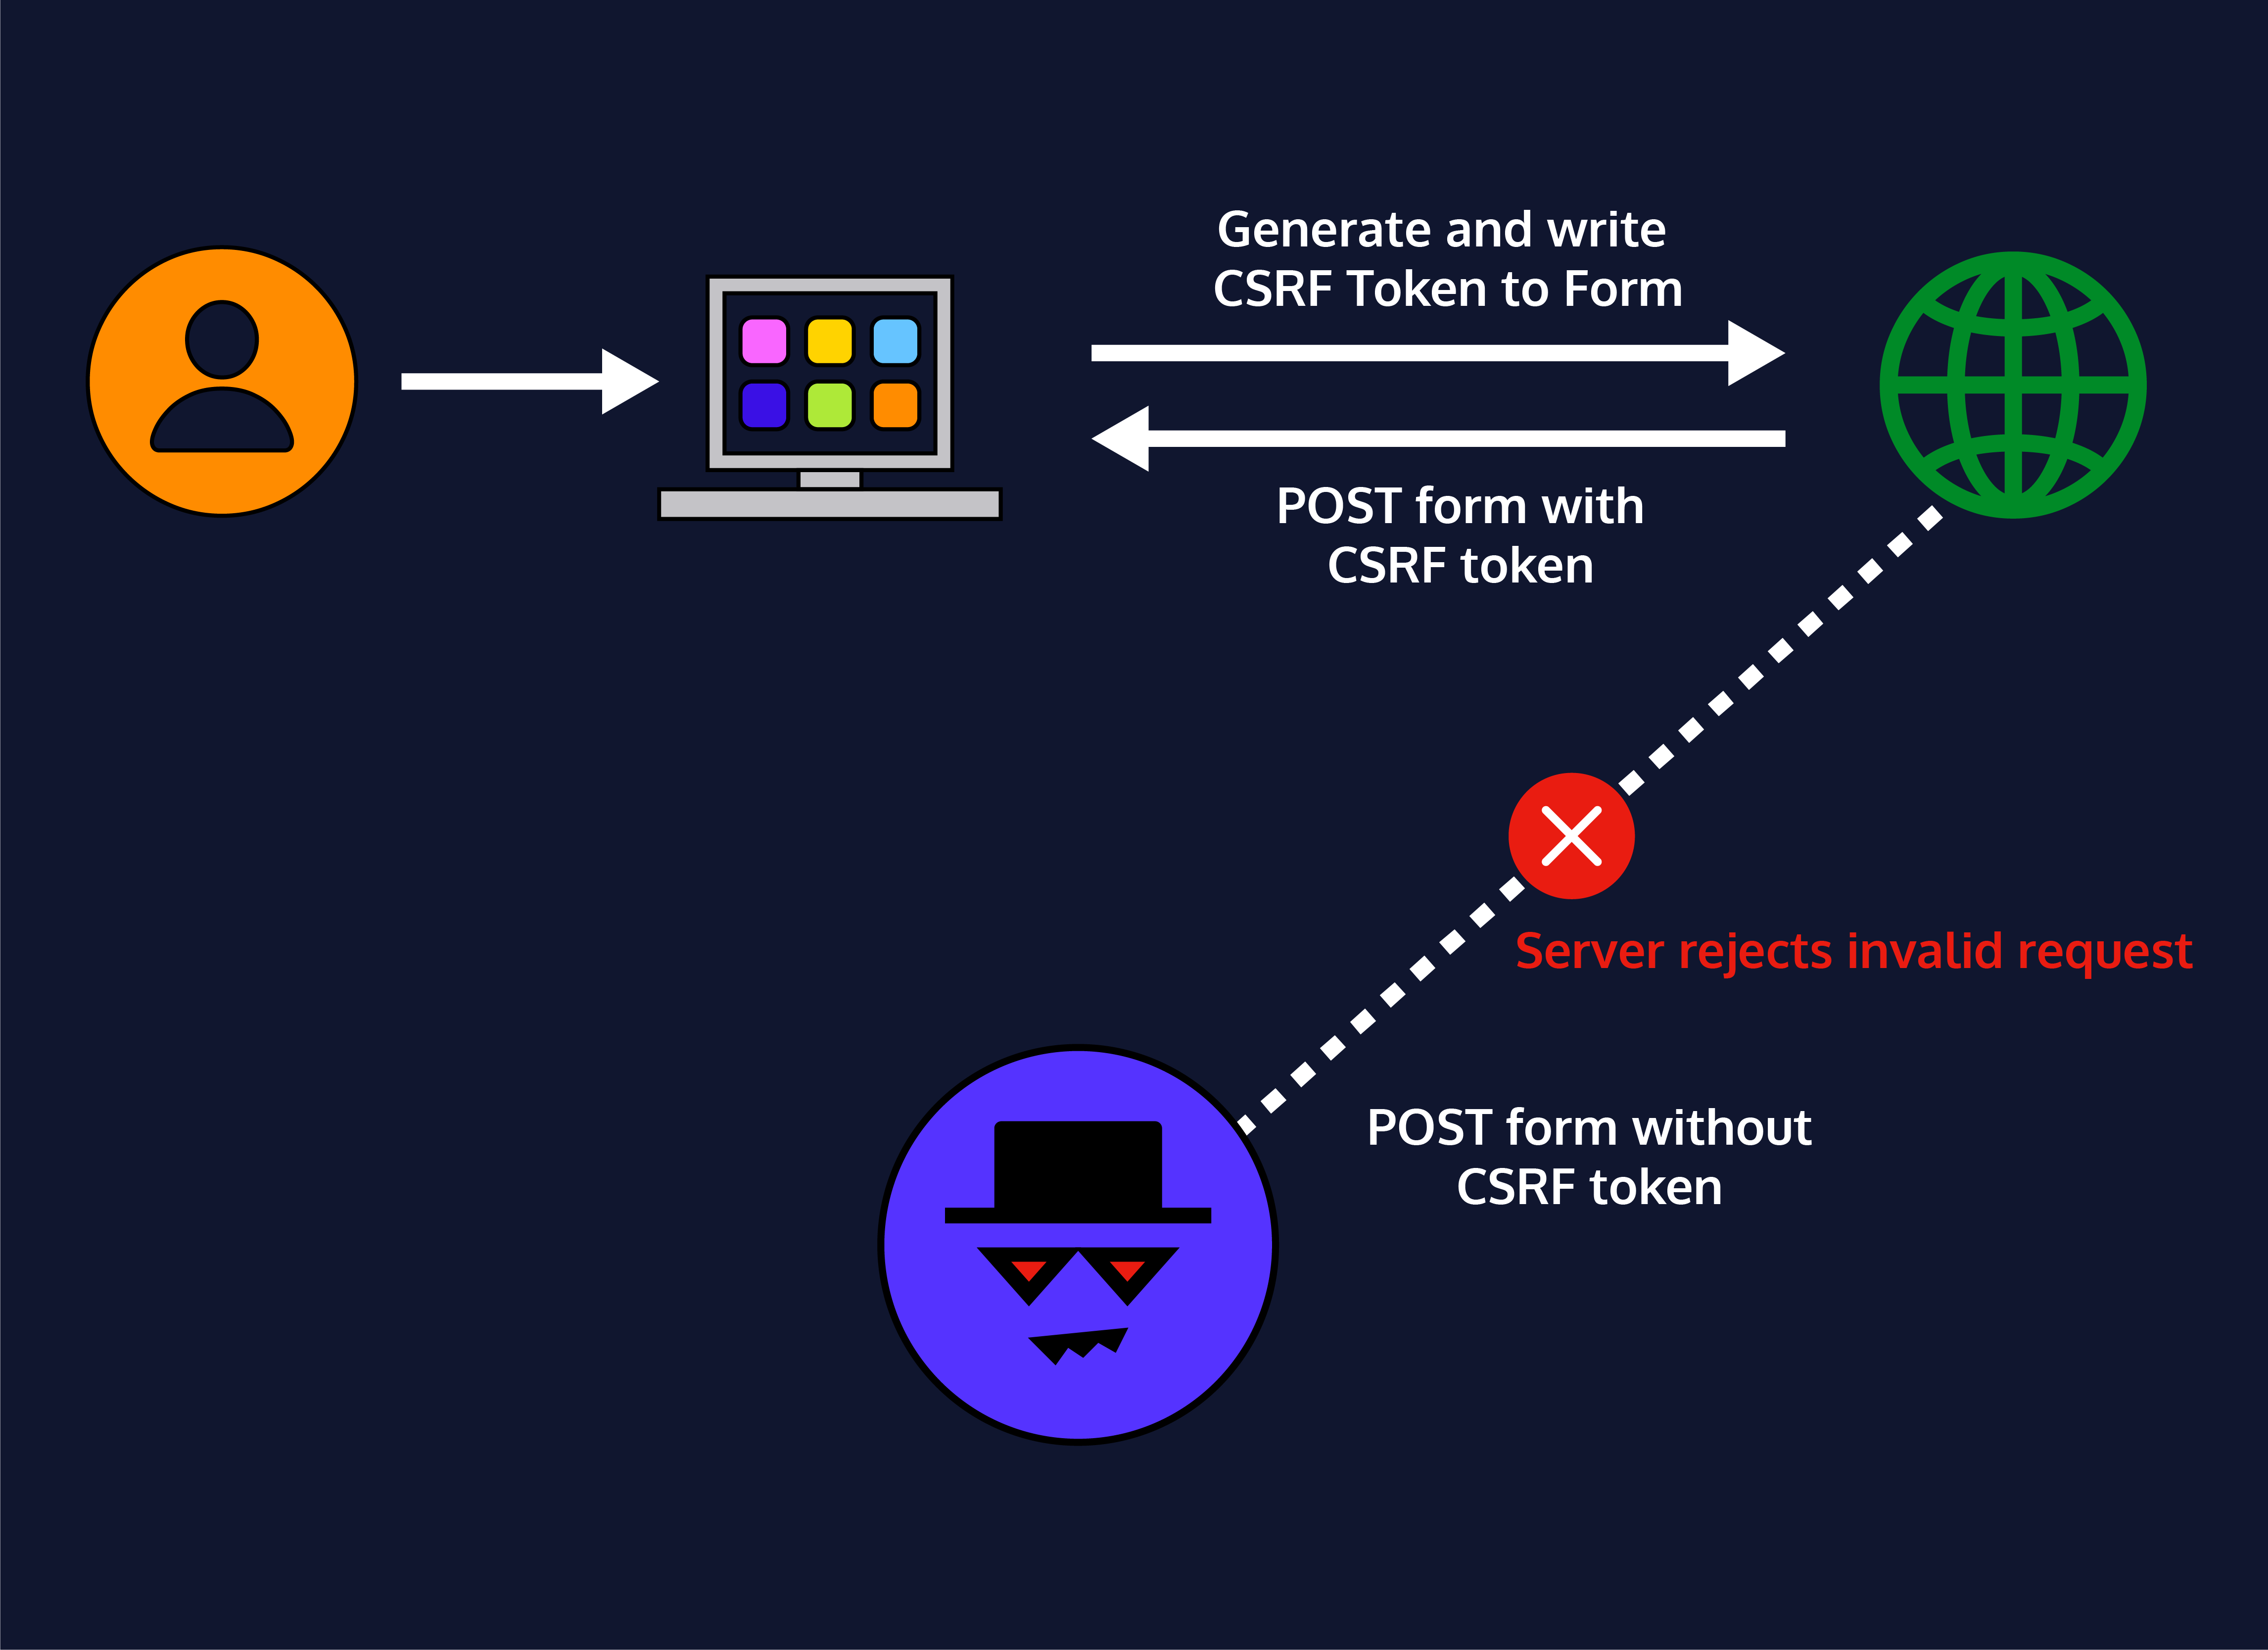
The most effective and widely adopted defense against CSRF is the use of anti-CSRF tokens. These are unique, unpredictable, and secret values generated by the server and included in every form submission or critical request. When a legitimate request is made, the server validates the received token against the one it generated and stored (e.g., in the user’s session). If the tokens match, the request is processed; if not, it’s rejected. An attacker, lacking access to the legitimate user’s session or the server’s secret, cannot predict or forge a valid token, thus making their forged requests detectable and preventable. Frameworks often automate the inclusion and validation of these tokens.
SameSite Cookie Attribute: Enhancing Browser-Level Protection
Modern web browsers offer an additional layer of defense through the SameSite cookie attribute. This attribute allows developers to declare whether cookies should be restricted to a first-party context or included with requests initiated from third-party websites. Setting SameSite to Lax (the default in many modern browsers) or Strict can prevent browsers from sending cookies with cross-site requests, effectively neutralizing many CSRF attacks. While Strict offers the strongest protection by only sending cookies for same-site requests, Lax is a good balance, allowing cookies for top-level navigation (like clicking a link) but preventing them for other cross-site requests (like image tags), without overly impacting user experience.
Referer Header Checking: A Secondary, Less Reliable Defense
Another defensive measure involves checking the Referer HTTP header, which indicates the origin of the request. A server can be configured to reject requests if the Referer header does not match the application’s domain. However, this method is less reliable. The Referer header can be manipulated by attackers, suppressed by privacy-conscious browsers, or simply not sent in certain scenarios. Therefore, it should only be used as a secondary or supplementary defense, never as the sole protection.
User Interaction and Confirmation: Mitigating Critical Actions
For extremely sensitive operations, such as transferring large sums of money or deleting an account, requiring explicit user interaction can add a significant layer of security. This could involve re-authenticating with a password, confirming the action via a second factor (e.g., a one-time code sent to a mobile device), or solving a CAPTCHA. These steps ensure that a human user intentionally performs the action, making it much harder for a CSRF attack to succeed undetected.
Best Practices for Developers: Secure Coding Principles
Beyond specific technical implementations, developers must adopt secure coding practices. This includes understanding the threat model, regularly updating frameworks and libraries, and conducting security audits. Training developers on common web vulnerabilities, including CSRF, and integrating security checks into the CI/CD pipeline are essential steps towards building resilient and trustworthy technological solutions.
CSRF in the Evolving Tech Landscape
As technology continues its rapid evolution, embracing microservices, APIs, and cloud-native architectures, the landscape for CSRF vulnerabilities also shifts, presenting new challenges and requiring adaptive security strategies.
API Security and Microservices: New Frontiers for CSRF
The shift towards API-driven architectures and microservices means that many applications communicate not just via traditional web forms but also through RESTful or GraphQL APIs. While many APIs are designed for machine-to-machine communication and might use token-based authentication (like OAuth tokens) that are not typically susceptible to traditional cookie-based CSRF, “browser-bound” APIs that rely on cookies or basic authentication are still vulnerable. Developers building services that leverage user-authenticated sessions via cookies must extend CSRF protection to all relevant API endpoints, not just traditional web forms, to prevent malicious clients from forcing unauthorized actions.
Cloud-Based Platforms: The Shared Responsibility Model and CSRF
Cloud adoption means that infrastructure and platform security are often shared responsibilities. While cloud providers secure the underlying infrastructure, customers are responsible for securing their applications and data deployed on that infrastructure. For web applications hosted in the cloud, CSRF protection remains firmly within the customer’s domain. Misconfigurations or neglect in implementing CSRF defenses within cloud-native applications can leave them exposed, highlighting the need for vigilance even when leveraging advanced cloud services. This extends to cloud-based management portals for IoT devices, remote sensing platforms, and drone operation centers, where unauthorized access via CSRF could have far-reaching operational implications.
User Experience vs. Security: Balancing Robust Protection with Usability
Implementing robust CSRF protection must always be balanced with maintaining a smooth and intuitive user experience. Overly complex security measures, such as excessive re-authentication prompts, can lead to user frustration and potentially encourage users to bypass security features. The challenge for innovators and security architects is to integrate seamless, transparent CSRF defenses, such as automatically generated and validated anti-CSRF tokens, that provide strong protection without impeding the user’s interaction with cutting-edge technologies.
In conclusion, Cross-Site Request Forgery is a persistent and potent threat in the digital realm. Its ability to hijack authenticated user sessions to perform unauthorized actions makes it a critical concern across all sectors of technology, from personal banking to the intricate controls of autonomous systems. By understanding its mechanisms, recognizing its potential impact, and rigorously applying a combination of anti-CSRF tokens, SameSite cookies, and secure coding practices, developers and organizations can significantly fortify their digital assets against this pervasive vulnerability, ensuring trust and integrity in our increasingly interconnected world.