
In an increasingly digital world, where every interaction, transaction, and piece of data is vulnerable to sophisticated threats, the concept of security has evolved far beyond simple passwords. At the forefront of this evolution is “two-factor authentication,” commonly referred to as 2FA. More than just a buzzword, 2FA represents a critical technological advancement designed to significantly bolster the protection of digital assets, identities, and systems. It’s an innovative layer of defense that moves beyond a single point of failure, embracing a multi-faceted approach to verify a user’s identity.
At its essence, two-factor authentication requires users to present two different types of credentials from distinct categories to prove their identity when accessing an account or system. This method adds a substantial barrier for unauthorized access, making it exponentially more difficult for malicious actors to compromise accounts even if they manage to steal a password. It’s a fundamental shift in security paradigms, recognizing that a single piece of information is no longer sufficient to secure the vast and complex digital landscapes we navigate daily.
The Core Concept of Enhanced Security
The internet and interconnected devices have revolutionized how we live, work, and interact. With this convenience comes an inherent risk: the exposure of personal and sensitive information to potential breaches. Traditional security models, heavily reliant on a single password, have proven to be increasingly inadequate against the ingenuity of cybercriminals. Two-factor authentication emerges as a powerful countermeasure, built on the principle of requiring multiple, distinct forms of verification.
Beyond Passwords: A Multi-Layered Approach
The strength of 2FA lies in its requirement for verification from two different categories of factors. These categories are generally classified as: something you know, something you have, and something you are. A single-factor authentication system, like a username and password, only relies on “something you know.” If that password is stolen, guessed, or phished, the account is immediately vulnerable.
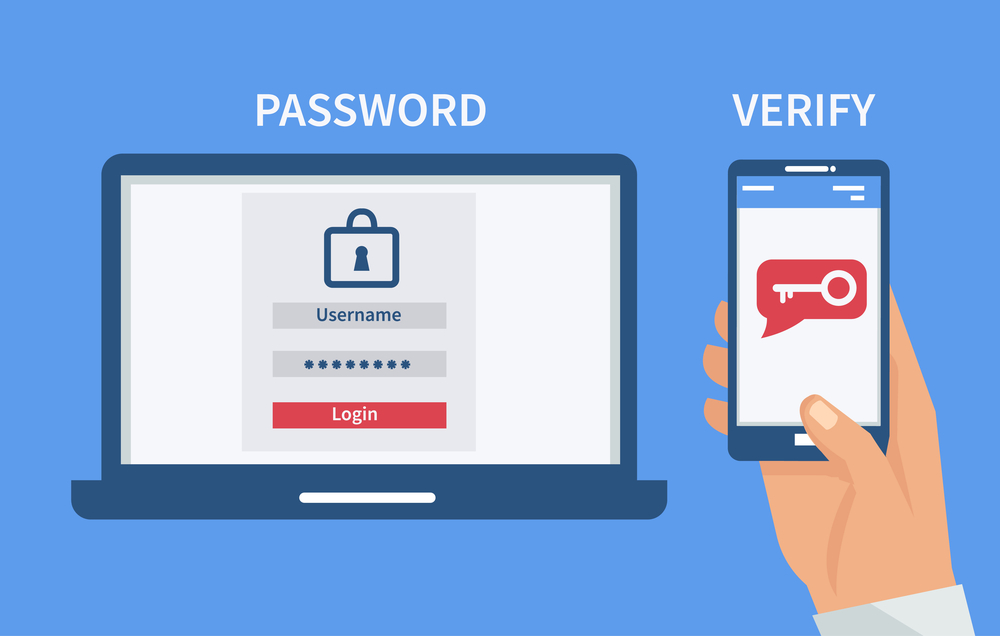
2FA demands a combination, such as “something you know” (your password) plus “something you have” (a temporary code sent to your phone) or “something you know” plus “something you are” (a fingerprint scan). This multi-layered approach ensures that even if one factor is compromised, the attacker still needs to acquire the second, independent factor to gain access. This drastically reduces the attack surface and significantly enhances overall security posture.
Why Traditional Passwords Fall Short
Passwords, despite their ubiquitous presence, are inherently flawed. They can be:
- Weak and Predictable: Many users choose simple, easy-to-remember passwords that are easily guessed or cracked by brute-force attacks.
- Reused: The temptation to reuse passwords across multiple services creates a massive vulnerability. If one service is breached, all other accounts using that same password become exposed.
- Phished: Sophisticated phishing attacks can trick users into revealing their credentials on fake websites.
- Stolen in Data Breaches: High-profile data breaches regularly expose millions of usernames and passwords, which are then sold on the dark web.
- Logged by Malware: Keyloggers and other malicious software can capture passwords as they are typed.
In an environment rife with these vulnerabilities, relying solely on a password is akin to locking your front door but leaving the back door wide open. 2FA closes that second door, making it profoundly more difficult for unauthorized entry.
How Two-Factor Authentication Works
Understanding the mechanics of 2FA is crucial for appreciating its effectiveness. It operates by demanding proof of identity from at least two of the three distinct categories of authentication factors: knowledge, possession, and inherence.
Something You Know (Knowledge Factor)
This is the most common and traditional form of authentication. It involves information that only the legitimate user is supposed to know.
- Passwords: A string of characters chosen by the user.
- PINs (Personal Identification Numbers): Shorter numerical codes, often used for ATMs or device unlock.
- Security Questions: Questions only the user can answer, like “What was your mother’s maiden name?” (though these are often considered less secure due to public information availability).
This factor forms the primary layer of defense and is almost always combined with one of the other two factors in a 2FA setup.
Something You Have (Possession Factor)
This factor relies on a physical item or device that is uniquely associated with the user. Possession of this item is required to complete authentication.
- Smartphones/Mobile Devices: The most common form, where a temporary, time-sensitive code (TOTP – Time-based One-Time Password) is sent via SMS, generated by an authenticator app (like Google Authenticator, Authy), or received as a push notification.
- Hardware Security Keys (e.g., YubiKey): Physical USB or Bluetooth devices that generate codes or perform cryptographic functions when plugged in or tapped. These are considered highly secure.
- Key Fobs: Small devices that display a rotating code.
- SIM Cards: Used for SMS-based codes.
The key here is that the attacker would need to physically possess your device or key, in addition to knowing your password, to gain access.
Something You Are (Inherence Factor)
This factor utilizes unique biological or behavioral characteristics of the user. It is often referred to as biometric authentication.
- Fingerprint Scans: Using a unique ridge pattern of a finger.
- Facial Recognition: Analyzing unique facial features.
- Iris Scans: Analyzing the unique patterns in the iris of the eye.
- Voice Recognition: Analyzing unique vocal patterns.
- Behavioral Biometrics: Analyzing unique patterns in how a user types, walks, or interacts with a device.
Biometric factors offer a high level of convenience and are difficult to forge, though they also raise privacy concerns and have specific vulnerabilities (e.g., a high-quality photo could bypass some facial recognition systems).
The Authentication Process in Action
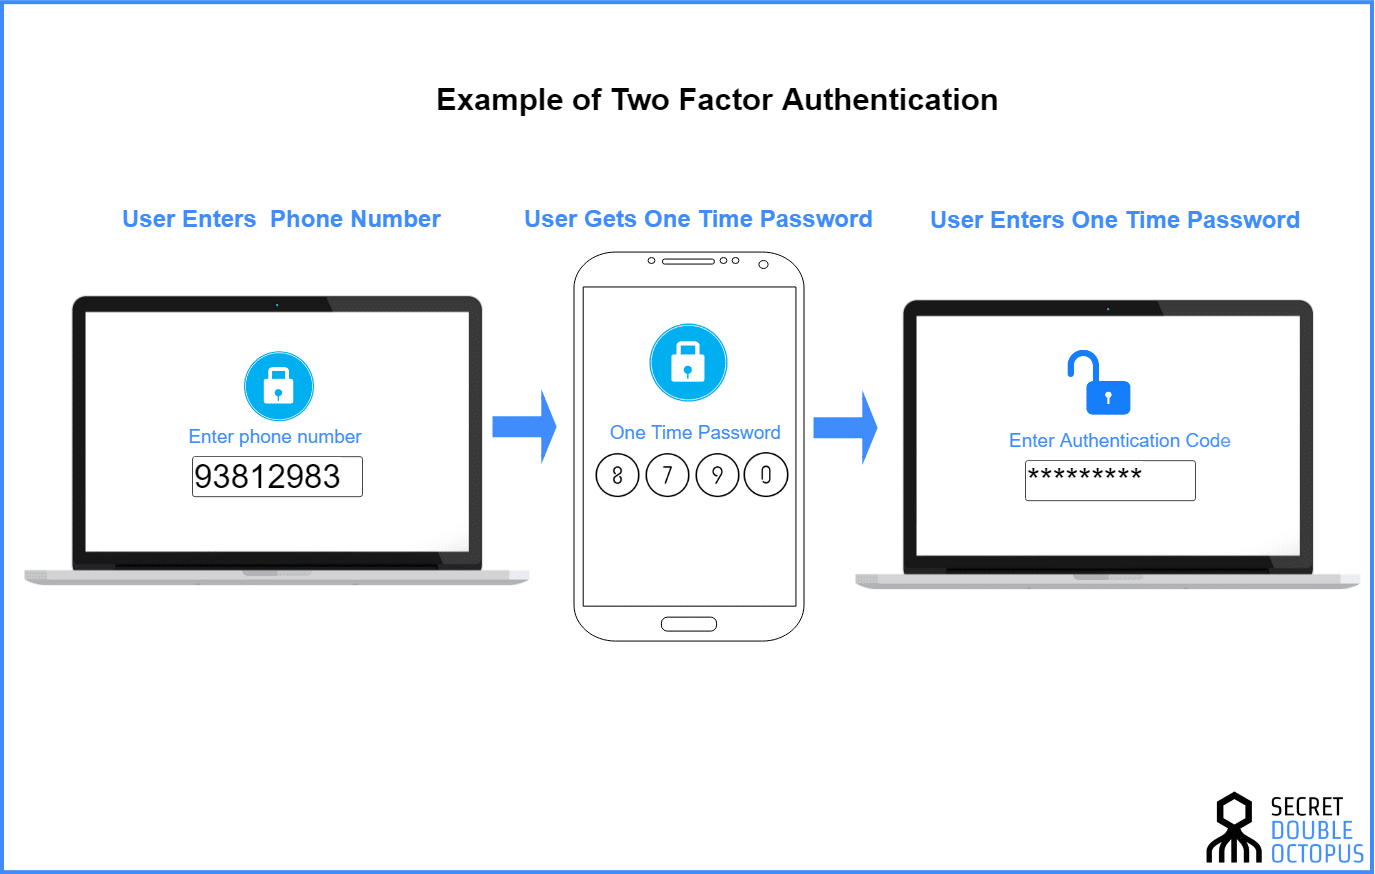
When 2FA is enabled, the login process typically looks like this:
- Enter First Factor: The user inputs their username and password (something they know).
- System Verification: The system verifies the first factor.
- Prompt for Second Factor: If the first factor is correct, the system then prompts for the second factor. This could be a code from an authenticator app, an SMS code, a tap on a security key, or a biometric scan.
- Enter Second Factor: The user provides the second piece of information.
- Access Granted: If both factors are correctly verified, access to the account is granted. If either factor is incorrect, access is denied.
This sequential requirement creates a robust defense, as an attacker would need to overcome two independent hurdles to breach the account.
The Indispensable Role in Modern Tech
In the rapidly evolving landscape of technology and innovation, two-factor authentication has transitioned from a niche security feature to an essential, almost mandatory, component of any robust digital infrastructure. Its importance is amplified by the sheer volume and sensitivity of data being generated, processed, and stored across various platforms and devices.
Protecting Digital Identities and Data
Every user has a digital identity tied to numerous accounts – email, social media, banking, cloud storage, e-commerce, and professional applications. Compromise of any one of these can have cascading effects, leading to identity theft, financial fraud, reputational damage, and loss of private information. 2FA serves as the primary guardian against such widespread digital identity theft. By requiring a second verification, it creates a formidable barrier that protects personal information, financial assets, and critical data from falling into the wrong hands. For businesses, this translates to safeguarding intellectual property, customer data, and operational continuity.
Mitigating Cyber Threats
The nature of cyber threats is constantly advancing. Phishing attacks are more sophisticated, malware more pervasive, and data breaches more common. 2FA is a highly effective mitigation strategy against many prevalent attack vectors:
- Phishing: Even if a user falls victim to a phishing scam and enters their password on a fake site, the attacker still won’t have the second factor (e.g., the code from an authenticator app on the user’s phone), rendering the stolen password useless.
- Credential Stuffing: This attack involves using credentials from one data breach to try and log into other services. With 2FA, even if your password from a breached site matches one used elsewhere, the attacker cannot proceed without the second factor.
- Brute-Force Attacks: These automated attempts to guess passwords are often thwarted because the system typically prompts for the second factor only after the password is correct, adding a manual or time-gated step that automates brute-forcing impossible.
As technology continues to integrate deeply into every aspect of life, from smart homes to critical infrastructure, the proactive adoption of 2FA becomes not just a recommendation but a necessity for maintaining security and trust.
Two-Factor Authentication in the Drone Ecosystem
While 2FA is a general cybersecurity principle, its application within specialized technological domains like the drone ecosystem highlights its versatile and critical nature. The integration of drones into various industries—from aerial surveying and mapping to delivery services and infrastructure inspection—introduces unique security challenges that 2FA can effectively address.
Securing Flight Planning and Data Management
Modern drone operations heavily rely on sophisticated software for flight planning, mission execution, and data post-processing. These applications often store sensitive information such as flight logs, mission parameters, GPS coordinates of critical infrastructure, and even proprietary algorithms. Access to these systems, often cloud-based or accessible via dedicated apps, requires robust authentication.
- Unauthorized Access Prevention: 2FA ensures that only authorized personnel can log into these platforms, preventing competitors or malicious actors from stealing flight plans, accessing sensitive mapping data, or disrupting scheduled operations.
- Data Integrity: By securing access to data management systems, 2FA helps maintain the integrity of collected information, ensuring that drone-derived data (e.g., high-resolution imagery, thermal scans, LiDAR data) remains untampered and reliable for analysis and decision-making.
Safeguarding Access to Drone Systems and Services
Beyond planning software, 2FA can be instrumental in securing the actual drone systems and associated services. While direct 2FA on a drone’s flight controller might be impractical or introduce latency, it is vital for controlling access to linked components:
- Remote Control Apps: Many advanced drones are controlled via smartphone or tablet apps. Implementing 2FA for logging into these apps prevents an unauthorized individual from taking control of a drone if their login credentials are stolen.
- Firmware Updates & Diagnostics: Access to portals for firmware updates, diagnostic tools, and configuration settings for a drone fleet can be protected with 2FA, preventing the injection of malicious code or unauthorized changes to flight parameters.
- Fleet Management Platforms: Companies operating large drone fleets use centralized management platforms. 2FA on these platforms ensures that only approved administrators can monitor drone locations, schedule maintenance, or assign missions, thereby protecting the entire operation from potential sabotage or theft.
Protecting Intellectual Property and Mission-Critical Information
The data collected by drones often constitutes valuable intellectual property or mission-critical information. For example, a drone surveying a new development site might capture detailed topological data, or an inspection drone might record sensitive information about critical infrastructure.
- Confidentiality: 2FA acts as a gatekeeper, ensuring that access to this confidential data is restricted only to those with appropriate authorization, protecting against corporate espionage or breaches of national security.
- Compliance: For industries with stringent regulatory requirements (e.g., defense, energy, agriculture), 2FA helps organizations meet compliance standards for data security and access control, mitigating legal and financial risks.
Implementing and Best Practices
Adopting two-factor authentication is a significant step towards a more secure digital life. However, its effectiveness hinges on proper implementation and adherence to best practices.
Choosing the Right 2FA Method
Not all 2FA methods are created equal in terms of security and convenience.
- Authenticator Apps (TOTP): Generally considered very secure and convenient. They generate time-sensitive codes directly on your device, making them resistant to SIM swap attacks (where an attacker takes control of your phone number).
- Hardware Security Keys: Offer the highest level of security, particularly against sophisticated phishing attacks. They require physical possession and are cryptographically strong.
- SMS-based Codes: While better than no 2FA, SMS is vulnerable to SIM swap attacks and can be intercepted. Use with caution for highly sensitive accounts.
- Biometrics: Convenient but can have specific vulnerabilities and raise privacy considerations. Ensure the biometric system used is robust.
For critical accounts, a combination of a strong password and an authenticator app or hardware security key is highly recommended.
Regular Updates and Vigilance
The security landscape is constantly changing, and so too should your practices.
- Update Software: Keep your operating systems, applications, and authenticator apps updated. Software updates often include security patches that address newly discovered vulnerabilities.
- Phishing Awareness: Remain vigilant against phishing attempts. Always double-check URLs before entering credentials, and be suspicious of unsolicited messages asking for personal information or urgent action.
- Review Account Activity: Regularly review your account login history and activity logs for any suspicious behavior.
Backup Codes and Recovery Options
While 2FA significantly enhances security, it’s crucial to plan for scenarios where you might lose your second factor (e.g., lost phone, broken hardware key).
- Backup Codes: Most services offering 2FA provide a set of one-time backup codes. Store these codes in a secure, offline location (e.g., a locked safe, encrypted drive) separate from your primary devices.
- Recovery Options: Understand the account recovery process for each service. This often involves providing alternative contact methods or answering security questions, which should also be unique and securely stored.
By embracing 2FA and adhering to these best practices, individuals and organizations alike can fortify their digital defenses, protecting their valuable assets and maintaining peace of mind in an increasingly connected, yet vulnerable, world. It’s not just a security feature; it’s a testament to continuous innovation in safeguarding our digital lives.