
Understanding the Benefits of OpenVPN on Your Netgear Router
Integrating OpenVPN onto a Netgear router offers a significant upgrade to your home network’s security and privacy. This robust open-source VPN protocol provides a secure tunnel for all your internet traffic, encrypting data between your router and a VPN server. This means every device connected to your Netgear router – from your smart TV and gaming console to your laptops and smartphones – will automatically benefit from VPN protection, without needing individual client installations on each device.
The advantages are manifold. Firstly, enhanced privacy is paramount. By routing your traffic through an encrypted tunnel, your Internet Service Provider (ISP) can no longer snoop on your online activities, view the websites you visit, or throttle your connection based on your usage. This is particularly crucial for users who handle sensitive information, engage in online banking, or simply value their digital anonymity.
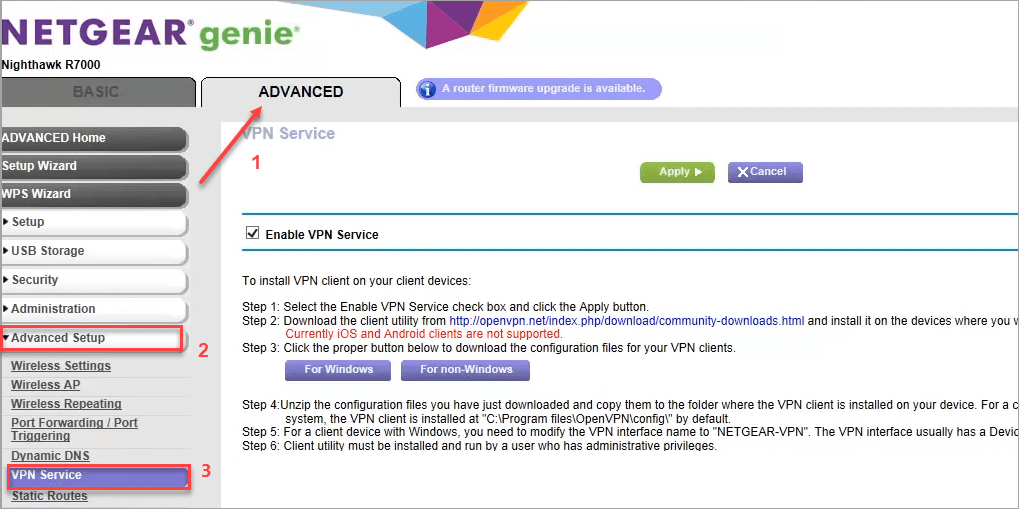
Secondly, security is bolstered considerably. OpenVPN uses strong encryption algorithms (like AES-256) and secure authentication methods to protect your data from prying eyes, especially on public Wi-Fi networks. When you connect to a VPN server, your IP address is masked, making it much harder for websites and online services to track your location and browsing habits.
Thirdly, geographical restrictions can be bypassed. By connecting to a VPN server in a different country, you can access content that might be geo-blocked in your region. This includes streaming services, websites, and online games. For businesses, a VPN can also facilitate secure remote access to company resources, allowing employees to connect to the office network safely from anywhere.
Finally, for advanced users, setting up OpenVPN on a router provides a centralized point of control for your VPN connection. You can manage multiple VPN profiles, switch between servers easily, and ensure consistent protection across your entire network. This eliminates the need to remember to activate VPN clients on every single device, preventing accidental unencrypted connections and offering a seamless user experience. While the process might seem daunting initially, with the right guidance, installing OpenVPN on a Netgear router becomes an achievable and highly rewarding endeavor for enhancing your digital security and freedom.
Prerequisites for OpenVPN Installation
Before embarking on the journey of installing OpenVPN on your Netgear router, a thorough understanding of the prerequisites is essential for a smooth and successful setup. Attempting the installation without these foundational elements can lead to frustration and failed attempts.
Router Compatibility and Firmware
The cornerstone of this process is ensuring your Netgear router is compatible with custom firmware that supports OpenVPN. Not all Netgear routers have this capability out-of-the-box. Many consumer-grade routers come with proprietary firmware that restricts advanced functionalities like VPN client integration.
- Check Router Model: The first step is to identify your exact Netgear router model number. This is typically found on a sticker on the bottom or back of the device.
- Firmware Support: Once you have the model number, you need to determine if it supports custom firmware like DD-WRT, Tomato, or OpenWrt, which are known for their OpenVPN capabilities. Websites like the DD-WRT router database or forums dedicated to Tomato and OpenWrt firmware are invaluable resources for checking compatibility.
- Stock Firmware Limitations: If your router’s stock Netgear firmware does not explicitly list OpenVPN client support, it’s highly unlikely to be achievable without flashing custom firmware. Netgear’s own firmware typically focuses on basic networking and may not include the advanced features required for a VPN client.
VPN Service Provider and Configuration Files
A crucial component of the OpenVPN setup is your chosen VPN service provider. You will need an active subscription with a provider that supports OpenVPN connections and, most importantly, provides the necessary configuration files.
- VPN Provider Selection: Choose a reputable VPN provider that offers OpenVPN as a protocol option. Factors to consider include server locations, connection speeds, logging policies, and customer support.
- OpenVPN Configuration Files (.ovpn): Your VPN provider will supply
.ovpnconfiguration files. These files contain all the critical information the router needs to establish a connection to the VPN server, including server addresses, ports, certificates, and encryption settings. - Download Configuration Files: Log into your VPN provider’s account dashboard on their website. Navigate to the section for manual configurations or OpenVPN setup. Download the
.ovpnfiles for the server locations you intend to use. It’s often recommended to download files for multiple locations.
Network Understanding and Basic Networking Skills
While the installation process will be guided, a foundational understanding of networking concepts can be extremely beneficial.
- IP Addressing: Familiarity with IP addresses, subnet masks, and default gateways will help you understand the network configurations.
- Router Interface Navigation: You should be comfortable navigating the web-based interface of your Netgear router.
- Command Line Interface (CLI) (Optional but Helpful): For some advanced custom firmwares, limited CLI interaction might be necessary, though most OpenVPN installations can be done entirely through a graphical user interface (GUI).
Backup of Existing Router Configuration
Before making any significant changes to your router’s firmware or settings, it is imperative to back up your current configuration. This backup serves as a safety net, allowing you to revert to your previous settings if something goes wrong during the installation or configuration process.
- Locate Backup Option: In your Netgear router’s web interface, navigate to the administration or advanced settings section. Look for an option like “Backup & Restore” or “Save/Load Settings.”
- Perform Backup: Click the “Backup” or “Save” button. The router will typically download a configuration file to your computer. Store this file in a safe and accessible location.
By diligently addressing these prerequisites, you pave the way for a successful and secure OpenVPN installation on your Netgear router, unlocking a new level of privacy and control over your home network’s internet traffic.
Step-by-Step Installation Guide for OpenVPN on Netgear Routers
The process of installing OpenVPN on a Netgear router typically involves flashing custom firmware, as stock Netgear firmware rarely includes built-in OpenVPN client functionality. This guide assumes you have identified a compatible router model and are prepared to flash custom firmware. Proceed with caution, as flashing incorrect firmware or interrupting the process can brick your router.
Flashing Custom Firmware (e.g., DD-WRT)
This is often the most critical and potentially risky step. We will use DD-WRT as a common example, but the principles apply to other compatible firmwares like Tomato or OpenWrt.
1. Download the Correct DD-WRT Firmware
- Identify Router Revision: You need the exact model number and revision number of your Netgear router (e.g., Nighthawk R7000 v2). This information is usually on the router’s label.
- Visit DD-WRT Website: Go to the DD-WRT website (dd-wrt.com) and navigate to their router database.
- Search for Your Router: Search for your specific Netgear model and revision.
- Select Firmware Type: DD-WRT offers different builds. For most users, a “Mega” or “VPN” build is recommended as it includes OpenVPN client support. Download the appropriate
.chkfile for your router. Do NOT use the generic firmware files.
2. Perform a Factory Reset (Recommended)
- Reset Button: Locate the reset button on your router. It’s usually a small, recessed button that requires a paperclip or pin to press.
- Power On and Press: With the router powered on, press and hold the reset button for about 10-30 seconds until the lights on the router flicker or change.
- Wait for Reboot: Allow the router to fully reboot. This ensures it starts with a clean slate.
3. Access the Router’s Stock Firmware Interface
- Connect via Ethernet: Connect your computer directly to one of the LAN ports on the Netgear router using an Ethernet cable. Avoid using Wi-Fi for this process.
- Default IP Address: Open a web browser and navigate to your router’s default IP address. For most Netgear routers, this is
192.168.1.1or192.168.0.1. - Login Credentials: Enter the default username and password. For Netgear, this is often
adminfor the username andpasswordor blank for the password. Check your router’s documentation if unsure.
4. Upload the DD-WRT Firmware
- Navigate to Firmware Upgrade: In the router’s web interface, find the “Firmware Upgrade,” “Administration,” or “Advanced Settings” section.
- Select Firmware File: Browse your computer and select the DD-WRT
.chkfile you downloaded earlier. - Start Upgrade: Click the “Upgrade” or “Upload” button.
- DO NOT INTERRUPT: This is the crucial part. Never turn off the router, unplug the Ethernet cable, or close the browser window during the firmware flashing process. This can take several minutes. The router will typically reboot automatically once the upgrade is complete.
5. Verify DD-WRT Installation
- New IP Address: After rebooting, the router might have a new IP address (often
192.168.1.1). You may need to renew your computer’s IP address via DHCP. - Access DD-WRT Interface: Open your web browser and navigate to the new IP address. You should be greeted by the DD-WRT login screen.
- Login: The default username is usually
root, and the password isadmin. You will be prompted to change these immediately.
Configuring OpenVPN Client on DD-WRT
Once DD-WRT is successfully installed, you can proceed to configure the OpenVPN client.
1. Obtain VPN Configuration Files from Your Provider
- Log in to VPN Account: Access your VPN provider’s website and log in to your account.
- Download .ovpn Files: Navigate to the manual configuration or OpenVPN setup section. Download the
.ovpnconfiguration files for the server locations you wish to use. You will also likely need to download certificate files (.crtor.pem). Some providers offer a zip file containing all necessary files.
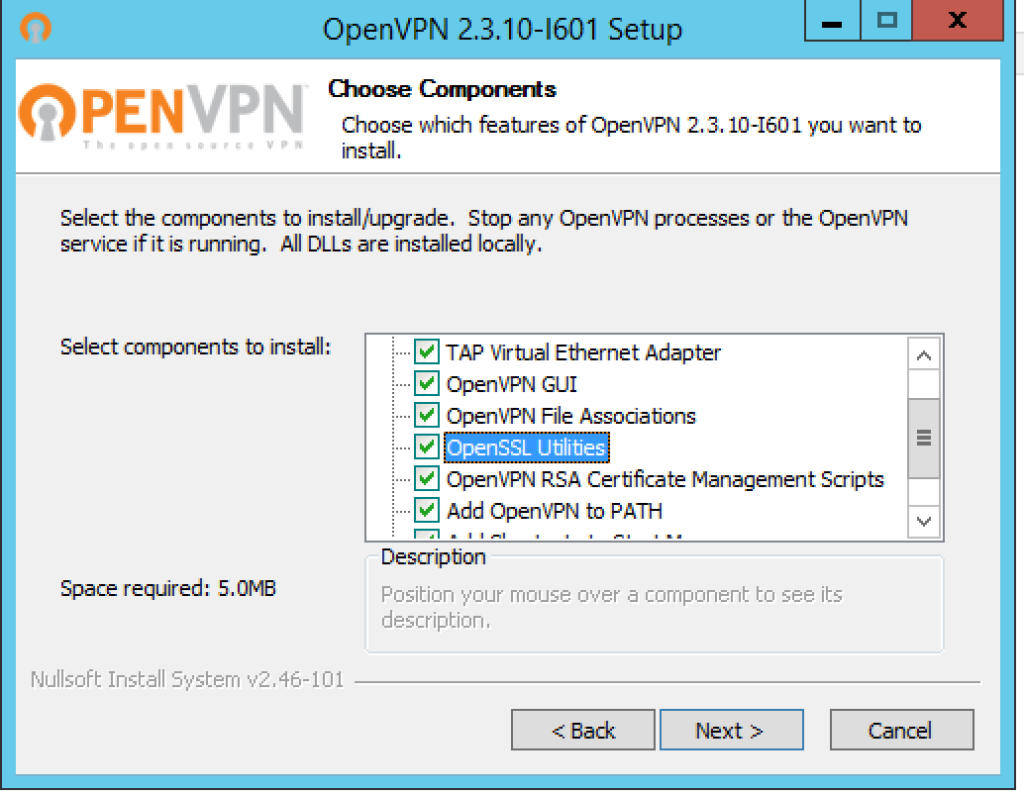
2. Access DD-WRT OpenVPN Client Settings
- Login to DD-WRT: Access your router’s DD-WRT interface (
192.168.1.1or your custom IP). - Navigate to VPN Settings: Go to
Services>VPN. - Enable OpenVPN Client: Find the “OpenVPN Client” section and set “Start OpenVPN Client” to
Enable.
3. Enter VPN Server and User Credentials
- Server IP/Name: In the “Server IP/Name” field, enter the IP address or hostname of the VPN server you want to connect to. This information is usually found within the
.ovpnfile itself or provided by your VPN service. - Port: Enter the port number specified by your VPN provider (commonly
1194for UDP or443for TCP). - Tunnel Protocol: Select the correct protocol (UDP or TCP) as specified by your provider. UDP is generally faster, while TCP is more reliable.
- Tunnel Device: Choose
TUNfor most OpenVPN configurations. - Encryption Cipher: Select the AES cipher specified by your provider (e.g.,
AES-256-CBC). - Hash Algorithm: Select the SHA algorithm (e.g.,
SHA256). - Username/Password Authentication: If your VPN provider uses username and password authentication, enter your VPN credentials in the “Username” and “Password” fields.
4. Configure Certificates and Keys
This is a critical step and requires careful copying and pasting from your downloaded configuration files.
- CA Cert: Open your downloaded
.ovpnfile in a text editor. Find the section starting with<ca>and ending with</ca>. Copy the entire content between these tags, including the-----BEGIN CERTIFICATE-----and-----END CERTIFICATE-----lines. Paste this into the “CA Cert” field in DD-WRT. - Public Client Cert: If your provider uses client certificates, locate the section
<cert>and</cert>. Copy and paste the content into the “Public Client Cert” field. - Private Client Key: If your provider uses client keys, locate the section
<key>and</key>. Copy and paste the content into the “Private Client Key” field. - TLS Auth Key (Optional): Some providers use a TLS authentication key for added security. Look for
<tls-auth>and</tls-auth>tags. Copy the content and paste it into the “TLS Auth Key” field. If prompted, set “Key Direction” accordingly (often1).
5. Additional OpenVPN Settings
- Additional Config: This field is for any extra directives from your
.ovpnfile that don’t have dedicated fields in DD-WRT. Common directives includeremote-cert-tls server,nobind, andpersist-key,persist-tun. Copy these directly from your.ovpnfile if they exist. - NAT: Ensure “NAT” is enabled. This allows devices on your local network to share the VPN connection.
6. Save and Apply Settings
- Save: Click the “Save” button at the bottom of the page.
- Apply Settings: After saving, click the “Apply Settings” button to make the changes active.
7. Monitor VPN Connection Status
- Status Page: Navigate to
Status>OpenVPN. This page will show the connection status of your OpenVPN client. Look for a “Client: CONNECTED SUCCESS” message. - Troubleshooting: If the connection fails, carefully re-check all entered credentials, server details, and especially the copied certificate and key data. Ensure you have copied them exactly, including all whitespace and line breaks. Check your VPN provider’s support documentation for specific DD-WRT setup instructions.
8. Verify Your IP Address
- External IP Check: Once connected, visit a website like
whatismyip.comfrom any device connected to your router. The IP address displayed should be that of the VPN server, not your ISP’s IP address. This confirms your VPN is working correctly and all traffic is being routed through the tunnel.
By following these steps, you can successfully install and configure OpenVPN on your Netgear router using custom firmware, thereby securing your entire home network with a robust VPN connection. Remember to repeat the configuration process for each .ovpn file if you wish to easily switch between different VPN server locations.
Advanced Configuration and Troubleshooting
Once your OpenVPN client is running on your Netgear router, several advanced configurations and troubleshooting techniques can further enhance its performance and reliability. Understanding these aspects can transform your VPN experience from basic security to a sophisticated network tool.
Policy-Based Routing (Split Tunneling)
Policy-based routing, often referred to as split tunneling, allows you to selectively route traffic through the VPN tunnel. This is invaluable when you want certain devices or applications to use the VPN for privacy while others (like local media servers or specific gaming connections) bypass it for performance or compatibility reasons.
1. Identify Traffic to Route via VPN
- Device IP Addresses: Determine the IP addresses of the devices you want to route through the VPN. You can assign static IP addresses to these devices in your router’s DHCP settings for consistency.
- Application/Port Specific Routing: In some advanced firmware setups, you can even route traffic based on specific application ports.
2. Configure Static Routes in DD-WRT
- Navigate to Static Routing: In DD-WRT, go to
Setup>Static Routing. - Add New Route: Click the “Add” button to create a new static route.
- Destination IP/Mask: Enter the IP address or network range of the device(s) you want to send through the VPN. For a single device, the mask would be
255.255.255.255. - Gateway: This is the IP address of your OpenVPN tunnel interface. You can usually find this by checking the
Status>OpenVPNpage after a successful connection. It often looks like10.8.0.1or similar. - Interface: Select
LANor the appropriate local network interface. - Add New Route (for non-VPN traffic): You may also need to add a default route for traffic that should not go through the VPN, pointing it to your regular WAN gateway.
Note: The exact implementation of policy-based routing can vary significantly between DD-WRT builds and other firmwares. Consult the specific documentation for your firmware version.
DNS Leak Protection
A DNS leak occurs when your device’s DNS requests bypass the VPN tunnel and are sent through your ISP’s DNS servers, potentially revealing your browsing activity. Ensuring your router uses VPN provider’s DNS servers is crucial.
1. Configure DNSMasq in DD-WRT
- Navigate to DNSMasq Settings: Go to
Services>Services. - DNSMasq Options: Under the “DNSMasq” section, you’ll find “Additional DNSMasq Options.”
- Add DNS Server Directives: You can explicitly tell DNSMasq to use your VPN provider’s DNS servers. For example, if your VPN provider recommends
1.1.1.1and8.8.8.8, you would add lines like:
server=/your-vpn-domain.com/1.1.1.1

server=/your-vpn-domain.com/8.8.8.8
Replaceyour-vpn-domain.comwith a domain relevant to your VPN service if provided, or simply use genericserver=1.1.1.1andserver=8.8.8.8if your VPN client configuration directs DNS traffic appropriately. - Force DNS Redirect: Ensure that DNS requests are forced through the VPN. Some OpenVPN configurations automatically handle this, but you might need additional
push "dhcp-option DNS X.X.X.X"entries in the client configuration if your provider supports it.
2. Test for DNS Leaks
- Use Online Tools: After configuration, use websites like
dnsleaktest.comoripleak.netto check for DNS leaks. The displayed DNS servers should belong to your VPN provider or be generic public DNS servers that your VPN provider trusts.
Kill Switch Functionality
A kill switch prevents internet access if the VPN connection drops unexpectedly, thus avoiding accidental exposure of your real IP address. While not a native feature in all router firmware, it can often be implemented.
1. Firewall Rules for Kill Switch
- Navigate to Firewall: In DD-WRT, go to
Administration>Commands. - Add Script: You can add firewall rules to block all outgoing traffic except that destined for the VPN server. This requires careful scripting. A basic example might involve blocking traffic on the WAN interface that is not related to the VPN tunnel’s IP range.
- Example (Conceptual):
bash

iptables -I FORWARD -o $(nvram get wan_ifname) -j REJECT --reject-with icmp-host-prohibited

# Add exception for VPN server IP/Port
Warning: Implementing a kill switch via firewall rules is complex and prone to errors. Incorrect rules can block all internet access. It’s often best to rely on the VPN client’s built-in kill switch if available or use a VPN provider that offers router-specific client software with this feature.
Advanced OpenVPN Options
- Keepalive Settings: Configure
keepalivedirectives in your OpenVPN client settings (Services>VPN>OpenVPN Client) to periodically send pings to the server, helping to maintain a stable connection and detect drops faster. For example,keepalive 10 60means ping every 10 seconds, and if no response is received for 60 seconds, consider the connection dropped. - Mullvad, NordVPN, ExpressVPN Specifics: If you are using a specific provider like Mullvad, NordVPN, or ExpressVPN, they often have detailed guides and recommended settings for DD-WRT. These can include specific cipher suites, TLS settings, and routing configurations that are optimized for their services. Always check your VPN provider’s support pages for router setup guides.
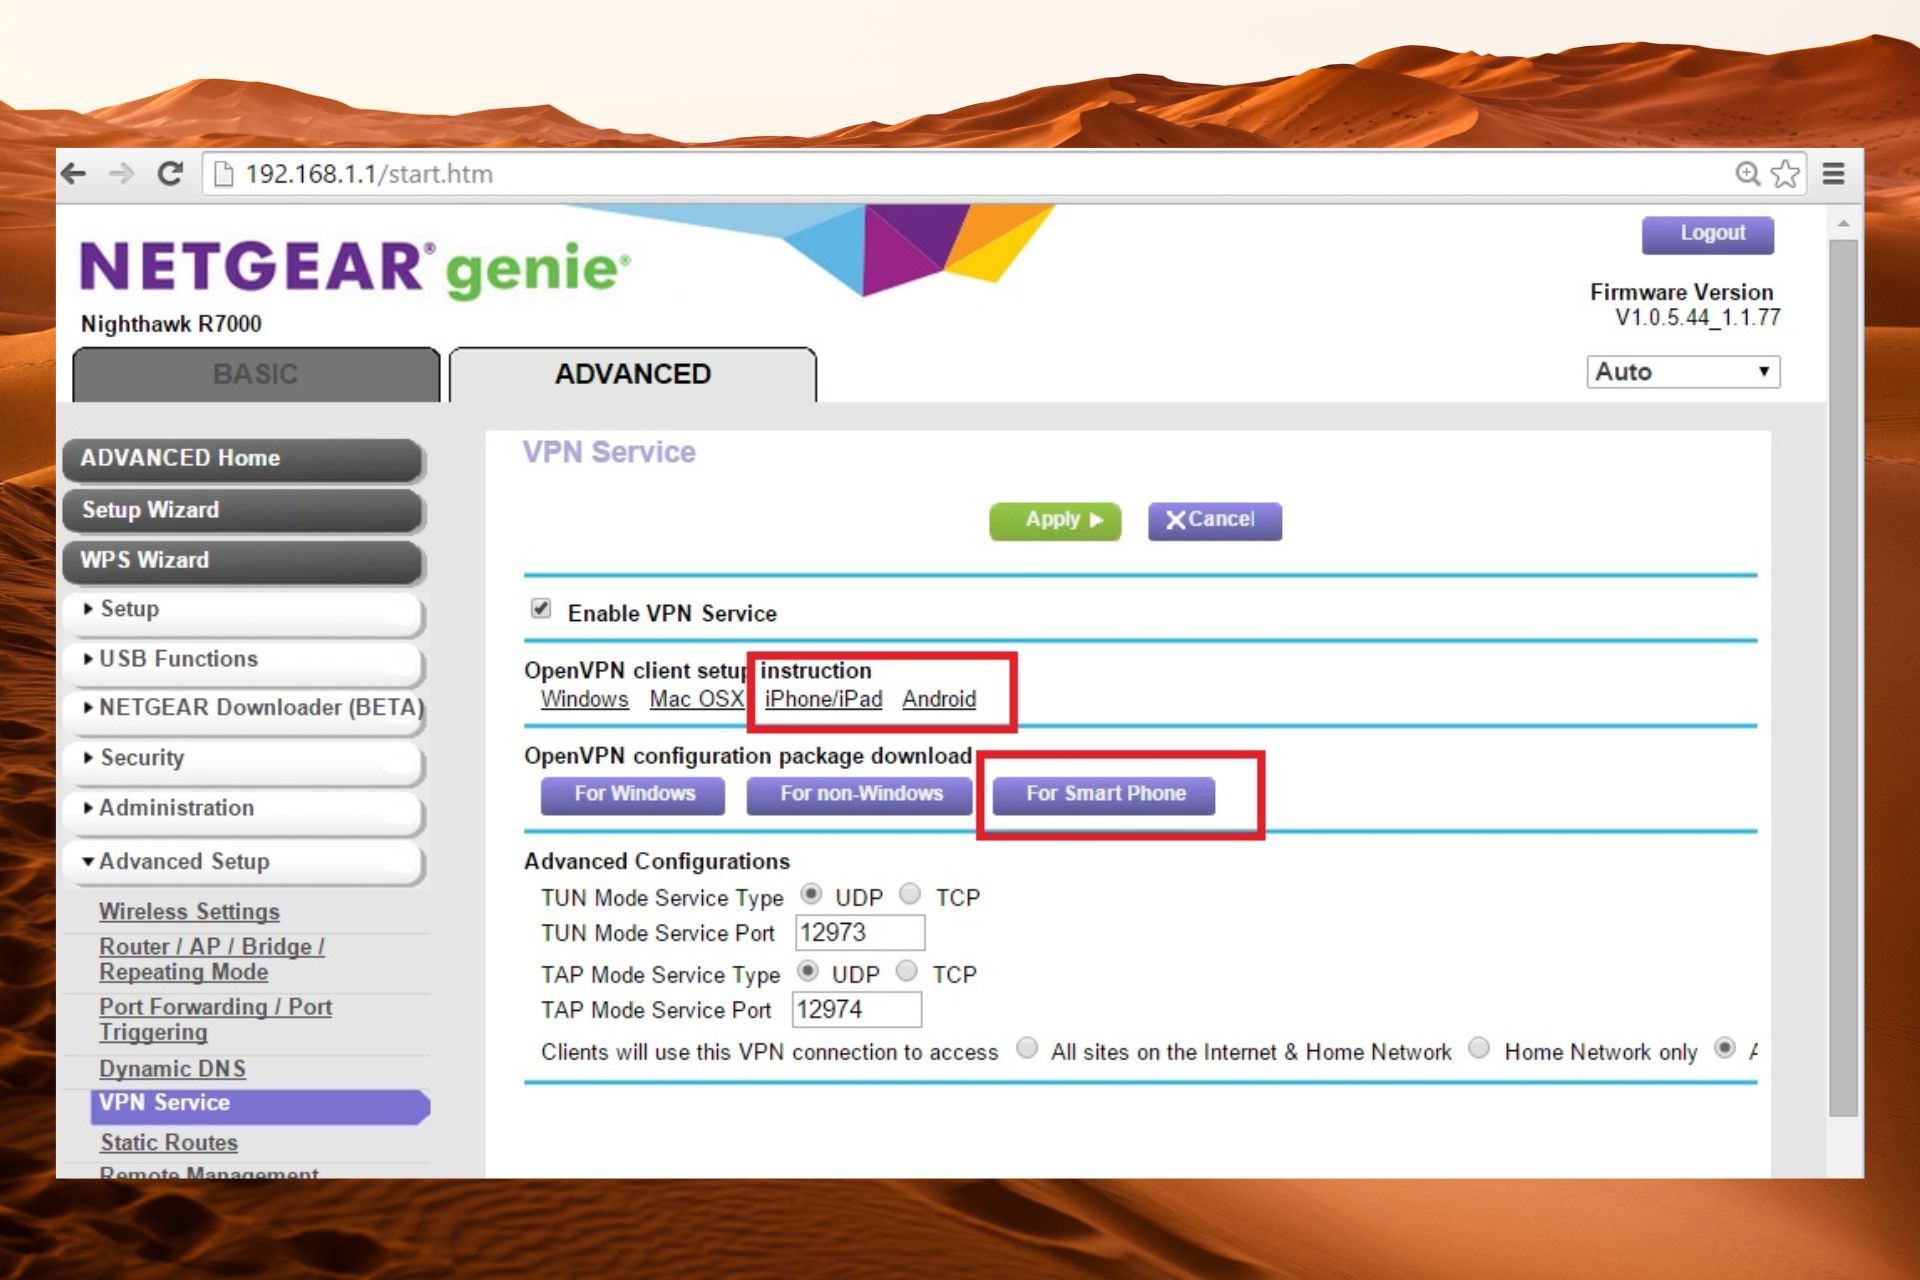
Troubleshooting Common Issues
- “Client: CONNECT ERROR” or “Auth Failure”:
- Credentials: Double-check your VPN username and password.
- Certificates/Keys: Ensure all certificates and keys were copied correctly without any modifications. Even a single extra space can cause failure.
- Server IP/Port: Verify the server address and port are correct.
- Time Sync: Ensure your router’s time is accurate (usually set via NTP). Incorrect time can cause certificate validation issues.
- No Internet Access After Connection:
- NAT: Check if NAT is enabled for the OpenVPN client.
- DNS: Verify DNS settings and test for leaks.
- Firewall Rules: Review any custom firewall rules.
- Policy Routing: If using split tunneling, ensure the routes are correctly configured.
- Slow Speeds:
- Protocol: Try switching between UDP and TCP.
- Server Location: Connect to a server geographically closer to you.
- Encryption: While AES-256 is secure, it can be CPU-intensive. Some older routers might struggle. Verify if your provider offers options with lower encryption levels (use with caution).
- Router Hardware: Older or lower-powered routers may not be able to handle the encryption and routing overhead of VPN connections efficiently.
By delving into these advanced configurations and troubleshooting steps, you can optimize your Netgear router’s OpenVPN setup for enhanced security, privacy, and performance, making it a truly robust gateway for your entire home network.