
In an era defined by relentless digital transformation and increasingly sophisticated cyber threats, the Security Operations Center (SOC) stands as a critical bastion of defense for organizations worldwide. Far from a simple IT helpdesk, a SOC is a centralized unit comprising skilled cybersecurity professionals, advanced technologies, and structured processes designed to monitor, detect, analyze, and respond to cyber incidents continuously. It is the nerve center of an organization’s cyber defense strategy, an embodiment of ongoing innovation in safeguarding digital assets against an ever-evolving threat landscape.
The Evolving Landscape of Cyber Threats and the Imperative for a SOC
The digital domain, while offering unparalleled opportunities for connectivity and innovation, simultaneously presents a complex and perilous environment. As businesses increasingly rely on interconnected systems, cloud infrastructure, and remote workforces, their attack surface expands dramatically. This proliferation of digital touchpoints provides fertile ground for malicious actors, necessitating a dedicated and proactive defense mechanism like the SOC.

Proliferation of Advanced Persistent Threats (APTs)
Gone are the days when cyberattacks were limited to simple viruses or opportunistic phishing attempts. Today’s threat actors, often state-sponsored groups or highly organized criminal syndicates, deploy Advanced Persistent Threats (APTs). These sophisticated attacks involve meticulous planning, stealthy infiltration, prolonged presence within a network, and a clear objective, often data exfiltration or system disruption. APTs are designed to bypass traditional perimeter defenses, making continuous monitoring and in-depth analysis – the core functions of a SOC – absolutely essential. A SOC utilizes cutting-edge threat intelligence and behavioral analytics to identify the subtle indicators of compromise (IOCs) that signify an APT’s presence, moving beyond signature-based detection to uncover more insidious threats.
The Interconnected Digital Ecosystem
Modern enterprises operate within a sprawling digital ecosystem, encompassing on-premises data centers, multiple cloud environments (public, private, hybrid), SaaS applications, IoT devices, and an increasingly mobile workforce. Each of these components introduces potential vulnerabilities and expands the volume of security data that needs to be processed. Without a centralized SOC, managing this complexity becomes insurmountable, leading to potential blind spots where threats can fester unnoticed. The SOC integrates data from diverse sources – network traffic, endpoint logs, cloud activity, application logs – to provide a holistic view of the security posture, enabling faster detection and more effective response across this intricate landscape.
Core Functions and Technological Pillars of a SOC
A modern SOC is built upon a foundation of robust technology and well-defined processes, enabling it to execute its mission effectively. These core functions represent the operational heartbeat of cybersecurity.
Monitoring and Alerting Systems
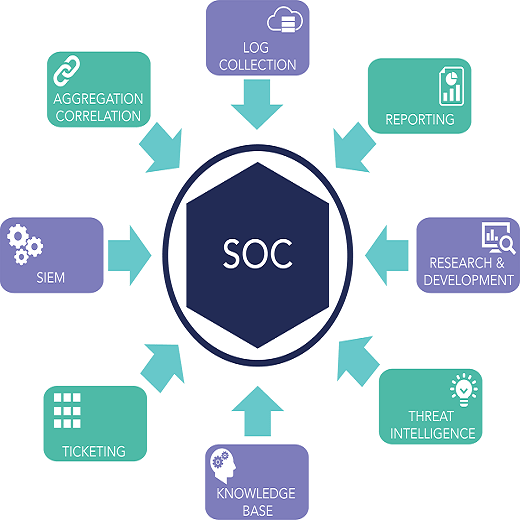
At the heart of any SOC is 24/7 monitoring. This involves the continuous collection and analysis of security event data from virtually every device and application within an organization’s IT infrastructure. Security Information and Event Management (SIEM) systems are the backbone of this function. SIEM platforms aggregate log data from firewalls, intrusion detection/prevention systems (IDS/IPS), servers, endpoints, databases, and applications. They then normalize this data, correlate events, and apply rules to identify potential security incidents, generating alerts for SOC analysts. The innovation here lies in real-time processing and intelligent correlation, reducing alert fatigue while highlighting true threats.
Threat Intelligence Integration
An effective SOC doesn’t just react; it anticipates. Threat intelligence feeds provide crucial context about emerging threats, attacker tactics, techniques, and procedures (TTPs), and known vulnerabilities. These feeds, often from commercial providers, government agencies, or open-source communities, are integrated into SIEM and other security tools. This allows the SOC to proactively identify indicators of compromise (IOCs) before an attack materializes, enrich incident data with relevant threat context, and prioritize responses based on the criticality of threats. The continuous flow and integration of this intelligence are vital to staying ahead of sophisticated adversaries.
Incident Response and Management
When an alert escalates to an confirmed incident, the SOC shifts into incident response mode. This involves a structured approach to containing, eradicating, and recovering from cyberattacks. Incident response plans detail specific steps, roles, and responsibilities for different types of incidents, ensuring a swift and coordinated reaction. The management aspect includes tracking incidents from detection to resolution, documenting findings, and conducting post-incident analysis to identify root causes and improve future defenses. Innovation in this area includes automated playbooks and rapid deployment of mitigation strategies to minimize damage.
Security Orchestration, Automation, and Response (SOAR)
One of the most significant innovations in modern SOC operations is the adoption of SOAR platforms. SOAR tools integrate and automate tasks across various security products, orchestrating complex workflows that would otherwise require manual intervention. For instance, upon receiving an alert, a SOAR platform can automatically enrich the alert with threat intelligence, check an endpoint for malicious files, block an IP address on a firewall, and open a ticket in an incident management system. This automation dramatically reduces response times, minimizes human error, and allows analysts to focus on more complex, investigative tasks. SOAR is a testament to how technology is enabling more efficient and effective cybersecurity operations.
The Human Element: Skills and Roles within a SOC
While technology forms the bedrock of a SOC, it is the highly skilled cybersecurity professionals who breathe life into its operations. Their expertise, critical thinking, and continuous learning are indispensable.
Tier 1 Analysts: The First Line of Defense
Tier 1 analysts are often the first to review incoming alerts from SIEMs and other monitoring tools. Their primary role is to triage alerts, differentiating between false positives and genuine threats. They perform initial investigations, collect basic contextual information, and escalate legitimate incidents to higher tiers. This role requires a strong understanding of fundamental security principles, network protocols, and common attack vectors. The innovation in tools that help these analysts quickly assess and correlate data is crucial for their efficiency.
Tier 2 Analysts: Deep Dive Investigations
When an incident is escalated, Tier 2 analysts conduct more in-depth investigations. They utilize advanced forensic tools, threat intelligence, and behavioral analytics to understand the scope, impact, and root cause of an attack. They develop containment strategies and contribute to eradication efforts. These analysts possess a deeper technical understanding of operating systems, network architecture, malware analysis, and cloud security, enabling them to dissect complex attacks. Their ability to leverage advanced analytical platforms is key to uncovering hidden threats.
Tier 3 Analysts/Hunters: Proactive Threat Detection
Tier 3 analysts, often referred to as threat hunters, are the proactive arm of the SOC. Instead of waiting for alerts, they actively search for undiscovered threats within the network using hypotheses about potential attacker activity. They leverage advanced tools, custom scripts, and deep knowledge of attacker TTPs to uncover stealthy intrusions that may have bypassed automated defenses. This role requires extensive experience, creativity, and a detective-like mindset. Threat hunting is a prime example of human-driven innovation in cybersecurity, pushing the boundaries beyond reactive defense.
SOC Managers and Engineers
SOC managers oversee the entire SOC operation, defining strategy, managing teams, and ensuring adherence to policies and SLAs. SOC engineers are responsible for the deployment, maintenance, and optimization of the security tools and infrastructure, including SIEM, SOAR, EDR (Endpoint Detection and Response), and network security devices. Their work ensures that the SOC’s technological stack remains robust, up-to-date, and capable of addressing emerging threats. Their role in integrating new technologies and optimizing existing ones is a continuous cycle of innovation.
Innovation Driving SOC Evolution
The landscape of cyber threats is in constant flux, demanding that SOCs continuously innovate and adapt. The evolution of SOC capabilities is directly tied to advancements in technology and methodologies.
Artificial Intelligence and Machine Learning in Threat Detection
AI and Machine Learning (ML) are revolutionizing threat detection within SOCs. Instead of relying solely on predefined rules, ML algorithms can analyze vast datasets to identify anomalous behaviors that deviate from normal patterns, indicating potential threats. This includes detecting unusual network traffic, user login anomalies, or suspicious file access patterns that would be missed by traditional methods. AI-driven analytics enhance the speed and accuracy of threat identification, significantly reducing the burden on human analysts and allowing them to focus on high-fidelity alerts.
Behavioral Analytics and Anomaly Detection
Beyond signature-based detection, modern SOCs heavily rely on behavioral analytics. This involves establishing baselines of normal user, endpoint, and network behavior. Any significant deviation from these baselines triggers an alert. For example, an employee suddenly accessing unusual files or logging in from an unfamiliar location could indicate a compromised account. This proactive, context-aware approach is highly effective against zero-day exploits and sophisticated attacks that do not have known signatures.
Cloud-Native SOCs and XDR Platforms
As organizations migrate to the cloud, SOCs are adapting. Cloud-native SOCs leverage cloud-based security tools and platforms to monitor cloud infrastructure, applications, and data. The emergence of Extended Detection and Response (XDR) platforms is another significant innovation. XDR unifies and correlates security data across multiple domains—endpoints, network, cloud, email, and identity—providing a more comprehensive view than traditional SIEM or EDR solutions. This integrated approach simplifies security operations, improves detection capabilities, and streamlines incident response across hybrid and multi-cloud environments.
Proactive Threat Hunting and Purple Teaming
The shift from purely reactive defense to proactive threat hunting is a major innovation. Threat hunters actively seek out threats that have bypassed automated defenses, using intelligence and hypothesis-driven searches. Purple teaming, a collaborative approach between red teams (offensive security) and blue teams (defensive security), further refines SOC capabilities. Red teams simulate attacks, while blue teams defend, and both share knowledge to strengthen the organization’s overall security posture. This continuous feedback loop fosters an environment of learning and improvement, ensuring the SOC’s defenses are constantly tested and hardened against the latest adversarial tactics.
Establishing and Optimizing a Modern SOC
Building and maintaining an effective SOC is an ongoing journey that requires strategic planning, continuous investment, and a culture of perpetual improvement.
Strategic Planning and Technology Adoption
Establishing a SOC begins with a clear strategy aligned with business objectives and risk appetite. This involves assessing the current threat landscape, identifying critical assets, and selecting the right blend of technologies and processes. The choice of SIEM, SOAR, EDR, and other tools is paramount, requiring careful evaluation of their capabilities, scalability, and integration potential. A focus on adopting cutting-edge technologies that offer automation, AI/ML capabilities, and comprehensive visibility is crucial for a future-ready SOC.
Continuous Improvement and Adaptability
A SOC cannot remain static. It must continuously adapt to new threats, leverage emerging technologies, and refine its processes. This involves regular training for analysts, conducting tabletop exercises to test incident response plans, performing periodic security audits, and embracing feedback from red team engagements. The iterative process of learning, adapting, and optimizing ensures that the SOC remains an agile and resilient defense mechanism, embodying the spirit of ongoing innovation in the face of an ever-changing cyber world.