
The rapidly evolving landscape of drone technology—encompassing innovations like AI follow mode, autonomous flight, sophisticated mapping, and remote sensing—is not only pushing the boundaries of what’s possible but also creating complex new challenges in data security. In this vibrant ecosystem, understanding and adhering to robust security standards becomes paramount. Among the foundational frameworks for safeguarding sensitive information is the Payment Card Industry Data Security Standard, or PCI-DSS. While primarily associated with financial transactions, the core principles of PCI-DSS are critically relevant to any tech enterprise, including those at the forefront of drone innovation, guiding them toward comprehensive data protection practices that build trust and ensure operational integrity.
Securing the Digital Frontier of Drone Innovation
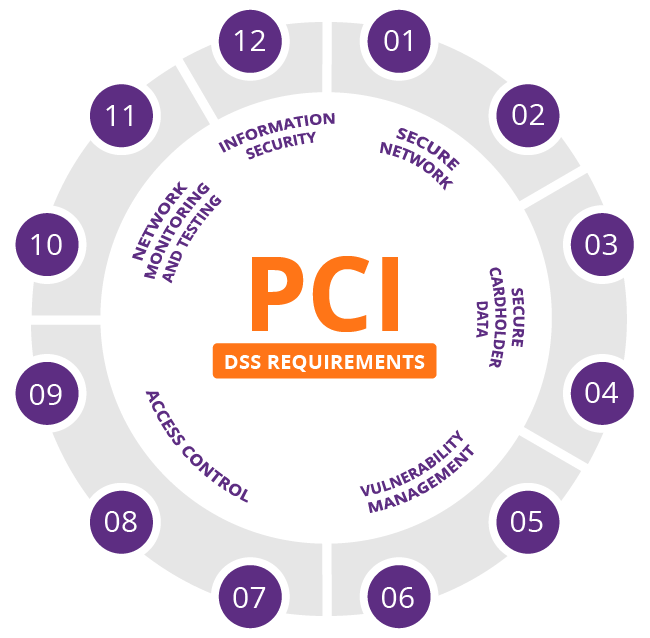
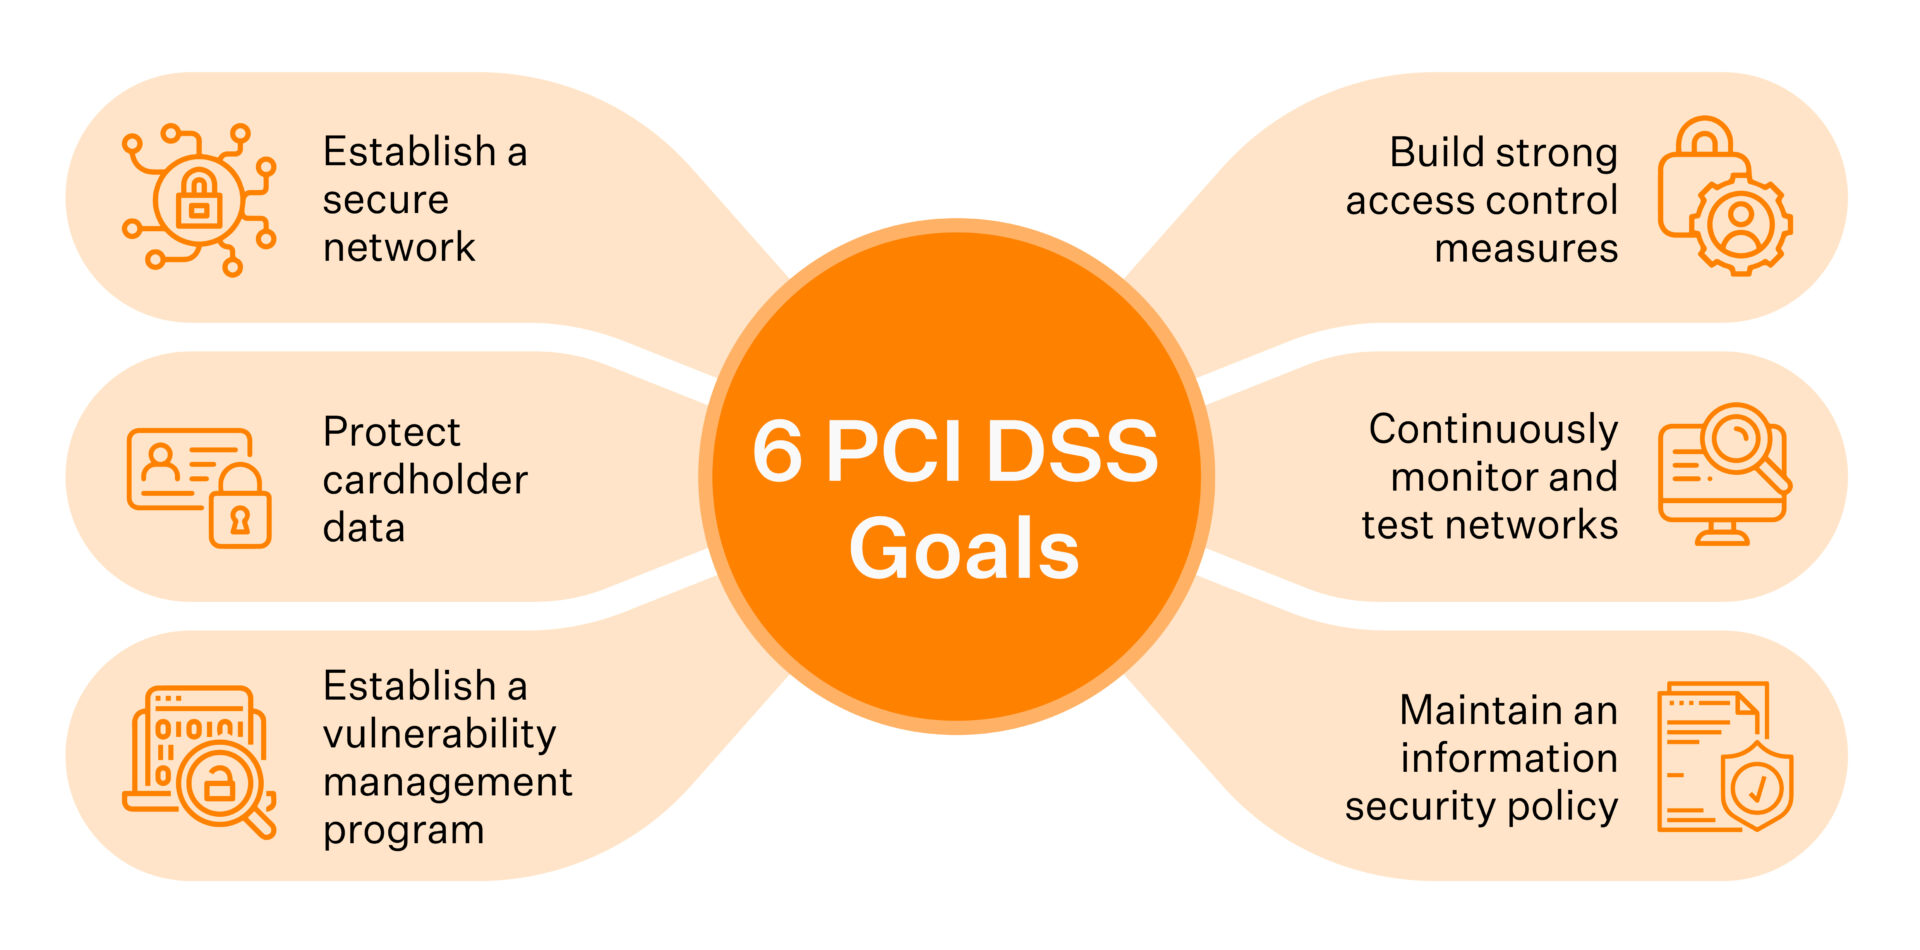
At its heart, PCI-DSS is a set of security standards designed to ensure that all companies that process, store, or transmit credit card information maintain a secure environment. This encompasses a rigorous set of 12 requirements, covering network security, data protection, vulnerability management, access control, regular monitoring, and information security policies. For drone technology companies, which often operate at the nexus of hardware, software, cloud services, and real-world data collection, the implications of PCI-DSS and its underlying philosophy extend far beyond simply handling customer payments. It represents a blueprint for securing the vast amounts of valuable, and often sensitive, data that modern drones generate and process.
Beyond Payment Cards: Data Integrity in Drone Operations
Drone operations, particularly those involving advanced features like high-resolution mapping, precise remote sensing for agriculture or infrastructure, or even AI-driven object recognition for autonomous flight, generate immense volumes of data. This includes aerial imagery, LiDAR point clouds, thermal data, telemetry logs, flight plans, and potentially even personally identifiable information. While this data may not directly be “cardholder data,” its confidentiality, integrity, and availability are crucial for the drone company’s reputation, operational success, and legal compliance. Breaches of such data can lead to significant financial losses, intellectual property theft, competitive disadvantage, and severe damage to customer trust. The robust data handling principles enshrined in PCI-DSS—such as encrypting data at rest and in transit, implementing strong access controls, and regular vulnerability scanning—serve as an excellent foundation for securing all sensitive data within a drone company’s purview, not just payment card information.
Why Drone Tech Companies Must Heed Data Security Standards
Drone tech companies, whether they are manufacturing drones, developing flight control software, offering drone-as-a-service (DaaS) for mapping and inspections, or selling cloud-based analytics for remote sensing data, invariably handle financial transactions. Customers pay for hardware, software subscriptions, data processing services, or drone operational hours. If a drone tech company directly processes these payments, it automatically falls under PCI-DSS compliance requirements. Failure to comply can result in substantial fines, increased transaction fees, loss of ability to process credit card payments, and reputational damage. Beyond direct compliance, embracing a PCI-DSS-level security posture signals a commitment to data integrity and customer privacy, which is a significant competitive differentiator in a market increasingly sensitive to cybersecurity risks. For instance, a mapping service provider demonstrating strong data security will naturally inspire more confidence in clients entrusting them with sensitive geographic or industrial data.
Adapting PCI-DSS Controls for Drone-Specific Technologies
The 12 requirements of PCI-DSS are broad enough to be adapted and applied to the unique technological stack and operational paradigms of the drone industry. This requires a thoughtful interpretation of each control in the context of ground control stations, cloud-based data analytics, autonomous flight software, and specialized drone hardware.
Network Security for Ground Control Systems and Cloud Platforms
PCI-DSS mandates building and maintaining a secure network, including installing and maintaining a firewall configuration and prohibiting the use of vendor-supplied defaults for system passwords and other security parameters. In the drone world, this translates to securing the communication links between the drone and its ground control station (GCS), implementing robust firewalls and network segmentation for internal company networks where sensitive data is stored or processed, and ensuring that cloud environments used for processing mapping data or hosting AI algorithms (e.g., for AI follow mode) are configured with the highest security standards. This includes segregating environments for development, testing, and production, and rigorously managing access to all network components. Default credentials, often a weak link, must be changed on all drone-related hardware and software, from onboard flight controllers to GCS software and network routers.
Protecting Sensitive Data in Drone Imaging and Sensing
PCI-DSS places a strong emphasis on protecting stored cardholder data, including encryption. For drone companies specializing in mapping, remote sensing, or even AI-driven visual analytics (like identifying objects for AI follow mode), the sheer volume and sensitivity of collected data present unique security challenges. This often includes high-resolution imagery, thermal data, LiDAR scans, and telemetry that may reside on the drone’s onboard storage, be transmitted to ground control systems, or uploaded to cloud processing platforms. Implementing robust encryption standards (e.g., AES-256) is crucial for data at rest (on drone storage, GCS hard drives, cloud storage) and in transit (during transmission from drone to GCS, or GCS to cloud). Furthermore, data tokenization or anonymization techniques can be employed for non-payment sensitive data to reduce its attack surface, echoing PCI-DSS principles of minimizing data exposure.
Developing Secure Software for Autonomous Flight and AI Modules
The standard requires developing and maintaining secure systems and applications. This is critical for drone manufacturers and software developers. Secure coding practices must be integrated into the entire software development lifecycle for autonomous flight systems, AI modules, mapping software, and mission planning applications. Regular vulnerability scanning and penetration testing of these applications are essential to identify and remediate security flaws before they can be exploited. This includes ensuring that AI algorithms used for autonomous flight or remote sensing data analysis are not susceptible to adversarial attacks that could compromise their integrity or lead to incorrect (and potentially dangerous) decisions. Patch management for operating systems, flight control software, and ground control applications must be rigorous and timely to protect against known vulnerabilities.
Operationalizing Compliance in a Dynamic Drone Environment
Maintaining PCI-DSS compliance, or indeed any high level of data security, is an ongoing process, especially in the fast-paced, innovative drone industry. It requires continuous vigilance, adaptive policies, and a culture of security throughout the organization.
Continuous Monitoring for Autonomous Fleets and Data Streams
PCI-DSS mandates regular monitoring and testing of networks and data access. For drone companies managing autonomous fleets or processing continuous streams of remote sensing data, this means implementing robust logging and auditing mechanisms across all systems—from individual drone flight logs and ground control interactions to cloud-based data processing and storage access. Real-time security information and event management (SIEM) systems can help detect unusual activities or potential security incidents promptly. Regular internal and external vulnerability scans, coupled with penetration testing, are vital to proactively identify weaknesses in the drone ecosystem’s security posture, especially as new technologies and operational models (like beyond visual line of sight autonomous operations) are introduced.
Access Control for Sensitive Drone Data and System Management
The standard emphasizes implementing strong access control measures, including restricting access to sensitive data on a “need-to-know” basis and assigning a unique ID to each person with computer access. In the drone context, this means stringent controls over who can access drone telemetry, collected imagery and sensor data, flight plans, and administrative functions of GCS or cloud platforms. Multi-factor authentication (MFA) should be mandatory for accessing all critical systems. Role-based access control (RBAC) should be meticulously defined, ensuring drone pilots only have access to flight-critical data, while data analysts have access to processed remote sensing data, and engineers to system diagnostics, all according to their job functions. This granular control minimizes the risk of unauthorized access or insider threats.
Policies and Employee Training for Drone-Specific Security Risks
PCI-DSS requires maintaining an information security policy that addresses all 12 requirements and ensuring all personnel are aware of it. For drone companies, this means developing comprehensive security policies tailored to their unique operations, covering everything from secure drone deployment protocols and data handling procedures for mapping projects to incident response plans for a cybersecurity breach affecting autonomous flight systems or remote sensing data. Regular and mandatory security awareness training for all employees—including drone pilots, data analysts, software engineers, and administrative staff—is crucial. This training should educate them about phishing attempts targeting drone system credentials, social engineering tactics, the secure handling of physical storage media (e.g., SD cards from drones), and the importance of reporting suspicious activities.
The Strategic Role of Security in Drone Innovation
Beyond compliance, integrating the rigorous security principles of PCI-DSS into the fabric of a drone tech company’s operations is a strategic move. It transforms security from a mere regulatory burden into a fundamental enabler of innovation, trust, and market leadership.
Building Trust in Autonomous Systems and Remote Services
As drone technology advances towards greater autonomy—from AI follow mode to fully autonomous inspection and delivery systems—public trust becomes paramount. Demonstrable adherence to robust security standards, whether directly PCI-DSS or security practices inspired by it, builds confidence in these nascent technologies. When a drone delivery service can assure customers that their payment details and package tracking information are secure, or an autonomous agricultural drone operator can guarantee the privacy and integrity of farm data collected via remote sensing, it fosters widespread adoption. Security, in this sense, becomes a foundational layer upon which the future of autonomous systems is built.
Data Governance as a Competitive Advantage in AI and Mapping
In the competitive world of drone-based mapping and AI-driven analytics, data governance—including its security, privacy, and ethical use—is a significant differentiator. Companies that can not only generate superior mapping data but also provide ironclad guarantees about its security, as evidenced by practices akin to PCI-DSS, will stand out. This attracts more enterprise clients who are themselves bound by strict data protection regulations. A robust security posture becomes a hallmark of quality and reliability, translating into greater market share and stronger partnerships in segments like infrastructure inspection, environmental monitoring, or advanced urban planning, where data sensitivity is often high.
Future-Proofing Drone Technology Against Evolving Threats
The cyber threat landscape is constantly evolving, with new vulnerabilities and attack vectors emerging regularly. By adopting a security-first mindset, deeply influenced by standards like PCI-DSS, drone innovators can future-proof their technologies. Designing security into autonomous systems from conception, rather than as an afterthought, ensures resilience against both current and anticipated threats. This proactive approach not only protects sensitive payment card data and proprietary drone technology but also safeguards the privacy of individuals and organizations whose data is collected via remote sensing. It enables continuous innovation while mitigating risks, ensuring that the drone industry can continue its trajectory of groundbreaking advancements safely and securely.