
In an increasingly connected world, the question of digital privacy, particularly concerning internet activity on shared networks, is paramount. As technological advancements continue to redefine what is possible in network management and data analysis, understanding the capabilities of a Wi-Fi owner to monitor online behavior becomes crucial for individuals navigating the digital landscape. This delves into the technical realities, innovative solutions, and evolving ethical considerations surrounding online privacy in shared network environments, situating the discussion firmly within the realm of Tech & Innovation.
Understanding Network Visibility: The Technical Landscape of Data Monitoring
The ability of a Wi-Fi owner to see what you search for hinges significantly on the specific technologies in use, the level of encryption employed, and the sophistication of their network monitoring tools. At its core, a Wi-Fi network acts as a conduit for all internet traffic originating from connected devices. The router, the central component of any Wi-Fi network, processes data packets as they travel between your device and the broader internet. This position grants the network owner a certain degree of visibility into the traffic flowing through their infrastructure.
Unencrypted Traffic and Packet Sniffing
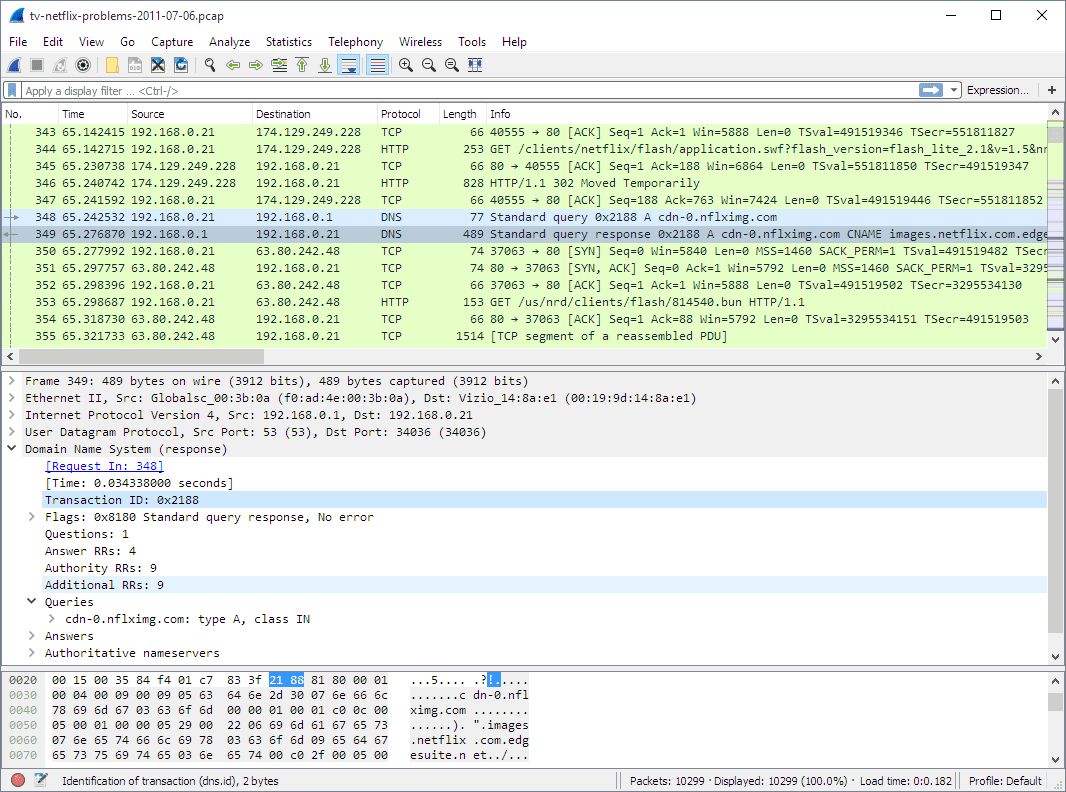
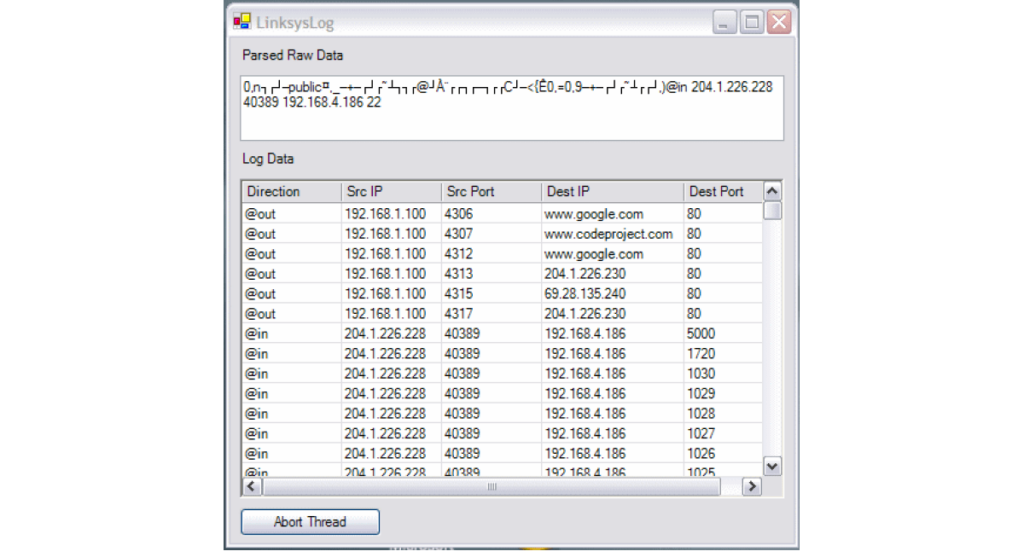
Historically, and in some less secure contexts, unencrypted internet traffic could be easily intercepted and read by anyone with access to the network and the right tools. Technologies like HTTP (Hypertext Transfer Protocol), used by many older or less secure websites, transmit data in plain text. If you were accessing an HTTP site on a Wi-Fi network, the owner, using a packet sniffing tool, could potentially view the full contents of your communication, including specific search queries, login credentials, and visited page content. This raw data capture allowed for a direct inspection of user activity. While the widespread adoption of HTTPS (HTTP Secure) has largely mitigated this risk for the content of individual web pages and searches, the principle of packet interception remains a foundational concept in network monitoring, with modern tools adapting to capture metadata even from encrypted streams.
DNS Queries and Website Visitation Logs
Even with HTTPS securing the content of your communications, the Domain Name System (DNS) queries made by your device often remain unencrypted. When you type a website address into your browser, your device sends a DNS request to translate that human-readable name (e.g., google.com) into an IP address that computers understand. These DNS requests typically go through the Wi-Fi router, and if the router is configured to log this information, the Wi-Fi owner can see a record of every website you attempted to visit. This provides a comprehensive history of your browsing activity, even if the specific content of those pages or individual search terms within an HTTPS session remain hidden. Many consumer-grade routers offer basic logging features, while more advanced network appliances or specialized monitoring software can provide detailed reports on DNS activity, including timestamps and frequency of visits.
Metadata and Connection Timestamps
Beyond explicit search queries or website content, a significant amount of metadata is generated by your online activity. This includes the IP addresses you connect to, the amount of data transferred, and the precise times of connection. Wi-Fi owners, especially in a corporate or institutional setting, frequently employ network monitoring solutions that track this metadata for bandwidth management, security auditing, and troubleshooting. While this does not reveal the content of your searches, it can paint a detailed picture of your online habits, identifying specific services used (e.g., streaming platforms, social media, VPN servers), the duration of engagement, and patterns of access. Innovative analytics tools can further process this metadata to infer user behavior and preferences, representing a sophisticated form of digital oversight even without direct content access.
Innovations in Privacy-Enhancing Technologies (PETs)
The push and pull between network visibility and individual privacy have spurred significant innovation in technologies designed to protect user data. These Privacy-Enhancing Technologies (PETs) empower users to reclaim control over their online footprint, even when operating on shared networks.
The Transformative Power of Virtual Private Networks (VPNs)
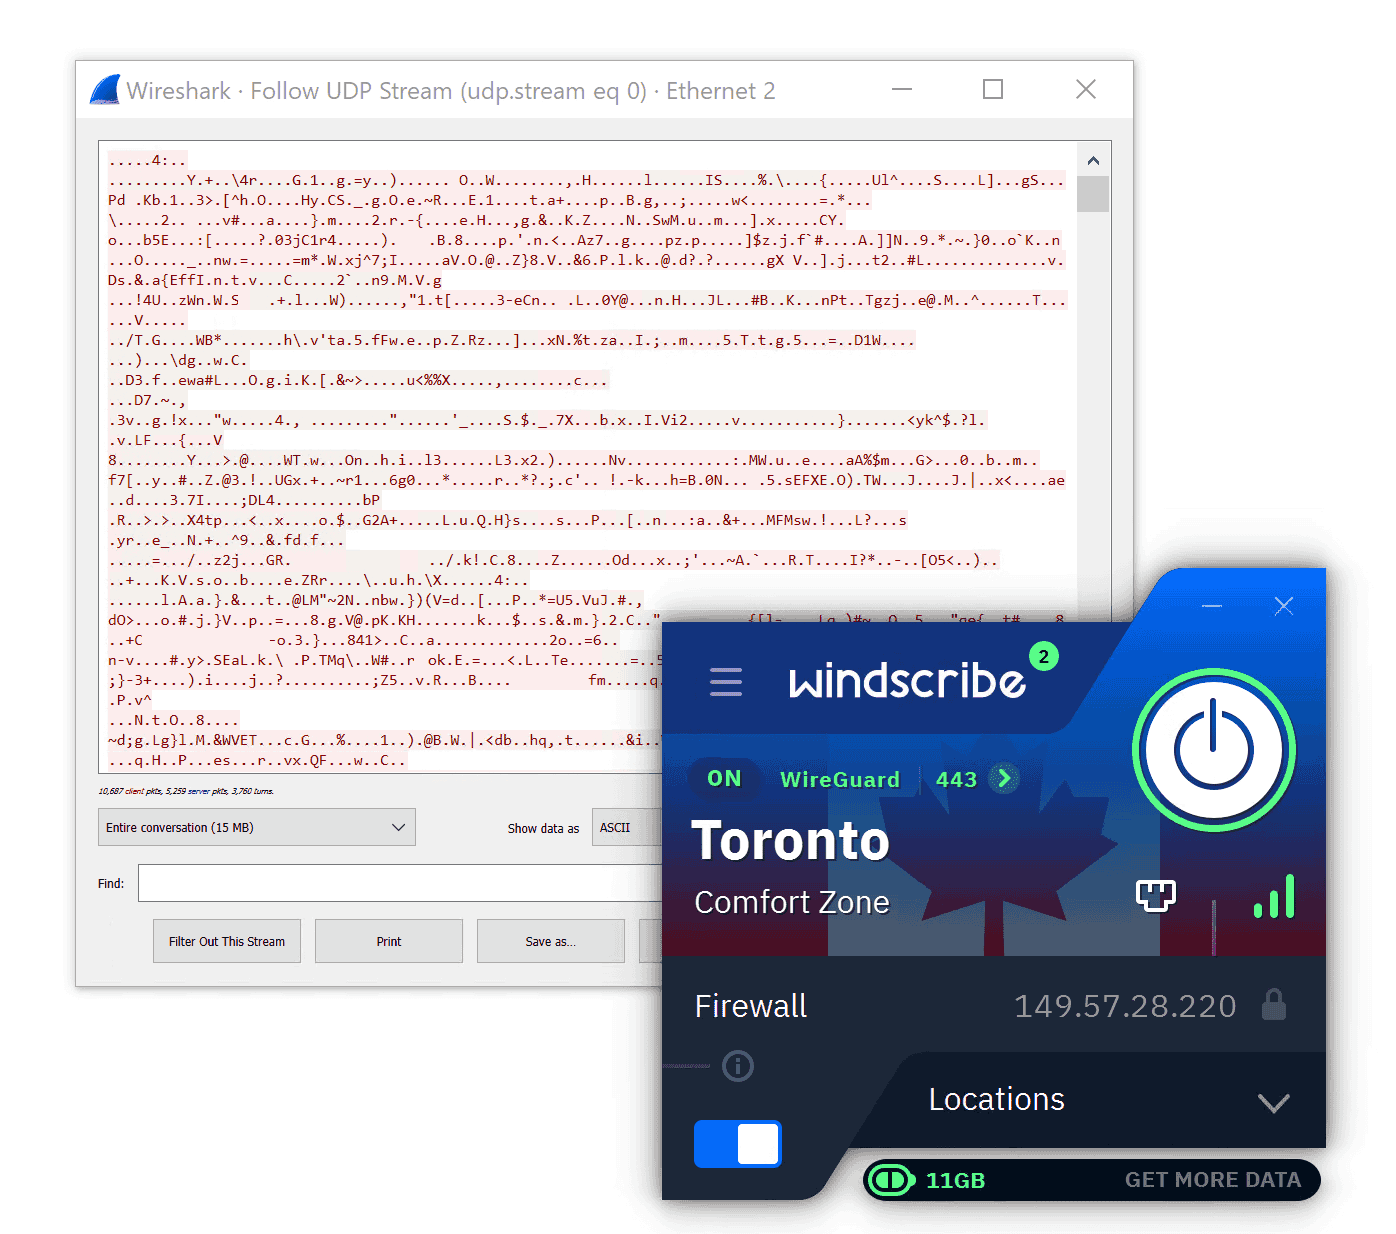
One of the most impactful innovations in personal digital privacy is the Virtual Private Network (VPN). A VPN creates an encrypted tunnel between your device and a server operated by the VPN provider. All your internet traffic, including DNS queries, passes through this encrypted tunnel. From the perspective of the Wi-Fi owner, all they can see is an encrypted connection to a single IP address—that of the VPN server. They cannot decipher the websites you visit, the searches you perform, or the content you access because all data within the tunnel is unintelligible. This technological solution effectively shifts the point of potential monitoring from the local Wi-Fi router to the VPN provider, making the choice of a trustworthy, no-logs VPN provider critical. The innovation lies in its ability to abstract and encrypt the entire connection, making local network surveillance largely ineffective against content and destination.
Secure DNS Protocols: DoH and DoT
Addressing the vulnerability of unencrypted DNS queries, the industry has developed and increasingly adopted Secure DNS protocols such as DNS over HTTPS (DoH) and DNS over TLS (DoT). These innovations encrypt your DNS requests, preventing local network observers (like the Wi-Fi owner) from seeing which websites you are trying to reach. Instead of sending plain text DNS queries, your device wraps them in an encrypted HTTPS or TLS session, similar to how secure website traffic is handled. When you configure your device or browser to use a DoH/DoT provider (e.g., Cloudflare, Google, Quad9), your DNS requests bypass the local router’s default DNS server and go directly to the secure resolver, encrypted. This significantly reduces the Wi-Fi owner’s ability to compile a list of visited websites based on DNS logs.
Anonymity Networks and Browser Technologies
Further pushing the boundaries of online anonymity are sophisticated networks like Tor (The Onion Router) and privacy-focused browser innovations. Tor routes your internet traffic through a series of relays operated by volunteers worldwide, encrypting it multiple times. Each relay only knows the previous and next hop, making it extremely difficult to trace the traffic back to its source or determine its destination. While slower due to its multi-layered encryption, Tor represents a significant innovation in achieving robust anonymity. Similarly, modern privacy-focused browsers come equipped with enhanced tracking protection, fingerprinting resistance, and integrated VPN or proxy services, leveraging innovative algorithms and configurations to minimize data leakage and resist surveillance attempts, even at the browser level.
The Evolving Ecosystem of Network Security and Data Encryption
The broader landscape of network security and data encryption is in constant flux, driven by the need to protect data in transit and at rest from increasingly sophisticated threats, including network monitoring. Innovations in this area directly impact the feasibility of Wi-Fi owners seeing user activity.
End-to-End Encryption and its Ramifications
End-to-end encryption (E2EE) is a paradigm-shifting innovation that ensures only the communicating users can read the messages, preventing even the service provider (or Wi-Fi owner) from accessing the content. Widely adopted by messaging apps like Signal, WhatsApp, and increasingly by email services, E2EE ensures that data is encrypted at the sender’s device and remains encrypted until it reaches the recipient’s device. For a Wi-Fi owner, this means that while they might see that an E2EE-enabled application is being used, the actual content of the communications—including searches made within the app’s interface—is completely opaque. This technological safeguard moves the locus of trust away from intermediaries, placing it squarely between the communicating parties.
WPA3 and Next-Generation Wi-Fi Security
The security protocols governing Wi-Fi networks themselves are also undergoing continuous innovation. Wi-Fi Protected Access 3 (WPA3) is the latest standard, succeeding WPA2. WPA3 introduces several key enhancements that bolster privacy and security on Wi-Fi networks. Crucially, it mandates “individualized data encryption” for all connections, even on open public networks. This means that each device establishes a unique, encrypted connection to the access point, making it significantly harder for other users on the same network (including the Wi-Fi owner, in certain scenarios of local traffic interception) to snoop on your traffic. The cryptographic strength and improved handshake protocols of WPA3 represent a substantial leap forward in securing the fundamental layer of Wi-Fi communication, embodying continuous innovation in network infrastructure.
Zero-Trust Architectures and Micro-segmentation
In enterprise and increasingly in advanced home networking environments, the adoption of “Zero-Trust” security architectures and micro-segmentation represents a significant philosophical and technological shift. Instead of assuming trust within a network, Zero-Trust models dictate that no user or device should be trusted by default, regardless of whether they are inside or outside the network perimeter. Every access attempt is authenticated and authorized. Micro-segmentation, a component of Zero-Trust, logically divides networks into smaller, isolated segments, with granular security policies applied to each. This approach means that even if a Wi-Fi owner has broad access to the overall network, they would face significant technological barriers to monitor traffic across different segments or between individual devices without explicit authorization and cryptographic keys, reflecting a sophisticated approach to data compartmentalization and access control.
Regulatory Frameworks and the Ethics of Digital Oversight
Beyond the technical capabilities and limitations, the discussion of Wi-Fi owners monitoring search activities is intricately linked with evolving legal and ethical frameworks. The interplay between technological innovation and public policy shapes what is permissible and expected in terms of digital privacy.
GDPR, CCPA, and Global Data Protection Norms
The emergence of comprehensive data protection regulations like the General Data Protection Regulation (GDPR) in Europe and the California Consumer Privacy Act (CCPA) in the United States highlights a global trend towards greater individual control over personal data. These regulations impose strict requirements on how personal data is collected, processed, and stored, compelling organizations (and by extension, network operators) to be transparent about their data practices and obtain user consent. While primarily aimed at businesses, the principles of data minimization and purpose limitation inherent in these laws influence the ethical considerations for any Wi-Fi owner considering comprehensive monitoring of user activity. The constant innovation in legal frameworks aims to keep pace with technological capabilities, defining acceptable boundaries for digital oversight.
The Fine Line Between Network Management and Surveillance
A critical ethical and practical dilemma lies in distinguishing between legitimate network management and intrusive surveillance. Wi-Fi owners, especially in professional or shared living environments, have valid reasons to monitor network activity: troubleshooting performance issues, preventing abuse, ensuring security against malware, or allocating bandwidth fairly. Technologies developed for these purposes, such as network analytics tools and intrusion detection systems, can inadvertently (or intentionally) provide insights into individual user behavior. The innovation challenge lies in developing tools that offer necessary network insights without compromising individual privacy, or in establishing clear policies that govern data collection and usage, striking a balance that respects both operational needs and user rights.
Corporate Policies and User Consent in Shared Networks
In environments like workplaces, schools, or public Wi-Fi hotspots, the Wi-Fi owner typically establishes clear acceptable use policies (AUPs) that users must agree to. These policies often outline the extent of network monitoring that may occur, specifying what data is collected and for what purpose. From an innovation perspective, the development of dynamic consent management platforms and transparent policy interfaces is crucial. These technologies aim to make complex policies understandable and allow users to actively manage their privacy settings, rather than passively accepting broad terms. The expectation is that technological solutions should facilitate clear communication and consent, aligning the owner’s capabilities with explicit user agreement.
Proactive Measures for Safeguarding Your Digital Footprint
Given the technological capabilities for monitoring and the ongoing innovations in privacy protection, individuals are empowered to take proactive steps to safeguard their digital footprint, particularly when using shared Wi-Fi networks.
Leveraging Secure Configurations
The first line of defense is often found in configuring devices and applications securely. Utilizing HTTPS Everywhere browser extensions ensures that you default to encrypted connections whenever possible. Enabling DoH or DoT in your browser or operating system directs your DNS queries through encrypted channels, obscuring your browsing history from local network snoopers. Furthermore, ensuring that your devices and applications are regularly updated with the latest security patches is paramount. These updates often include critical fixes for vulnerabilities that could otherwise be exploited for monitoring. Innovative software development practices continuously integrate these security enhancements, but user adoption is key.
Staying Informed on Security Patches and Updates
The landscape of cyber threats and privacy-enhancing technologies is constantly evolving. Staying informed about the latest security practices, software updates, and emerging privacy tools is a continuous process. Subscribing to reputable cybersecurity news sources, understanding the privacy implications of new technologies, and regularly reviewing the security settings of your devices and online accounts are essential. This proactive engagement allows individuals to adapt their privacy strategies in response to both new monitoring capabilities and new protective innovations. The digital arms race between monitoring and privacy means continuous vigilance and adoption of the latest technological safeguards are necessary.
The Future of Personal Privacy in a Connected World
The journey towards greater digital privacy is an ongoing one, marked by continuous technological innovation. From advances in homomorphic encryption (allowing computations on encrypted data without decrypting it first) to decentralized identity systems and the potential of quantum-resistant cryptography, the future holds promise for even more robust privacy-enhancing technologies. However, the balance between security, convenience, and privacy will always be a dynamic tension. Understanding the current technical realities of network visibility and leveraging available innovative tools are fundamental steps in protecting one’s online autonomy in an increasingly connected, and often transparent, digital world.