
In the rapidly evolving landscape of technology and innovation, particularly within the realms of drone operation and data management, understanding the nuances of secure communication is paramount. As unmanned aerial vehicles (UAVs) become increasingly sophisticated, capable of transmitting vast amounts of data, and integrating with complex cloud-based platforms, the security of these data streams is a critical concern. This is where the concept of SSL/TLS certificates, and specifically self-signed ones, comes into play. While often associated with web servers, their underlying principles and applications can extend to ensuring secure communication channels for drone operations, data logging, and remote control.
The Fundamentals of SSL/TLS Certificates
At its core, an SSL/TLS (Secure Sockets Layer/Transport Layer Security) certificate is a digital certificate that provides authentication and enables encrypted communication over a network. When you visit a website secured with SSL/TLS, your browser establishes a secure, encrypted connection with the web server. This is typically indicated by a padlock icon in your browser’s address bar and the use of “https://” in the URL.
The primary functions of an SSL/TLS certificate are:
- Authentication: It verifies the identity of the server (or, in some cases, the client) to the other party. This helps prevent “man-in-the-middle” attacks where an attacker intercepts communication between two parties, masquerading as one of them.
- Encryption: It encrypts the data exchanged between the client and the server, making it unreadable to anyone who might intercept it. This protects sensitive information such as login credentials, personal data, and proprietary operational details.
- Data Integrity: It ensures that the data transmitted has not been altered or tampered with during transit.
How Certificates Work
The trust in SSL/TLS certificates is established through a hierarchical system involving Certificate Authorities (CAs). CAs are trusted third-party organizations that issue and manage digital certificates. When a server requests a certificate, it submits a Certificate Signing Request (CSR) to a CA. The CA verifies the identity of the requester and, if validated, issues a certificate that binds the server’s public key to its identity. Your browser or client software has a pre-installed list of trusted CAs. When it receives a certificate, it checks if it was issued by a trusted CA and if the certificate is still valid.
The Role in Tech & Innovation
In the context of drones and advanced tech, secure communication is not limited to web interfaces. Consider a drone autonomously collecting data for mapping or remote sensing. This data might be transmitted in real-time to a ground station or uploaded to a cloud platform. Ensuring the integrity and confidentiality of this data is crucial. Similarly, remote control commands sent to a drone need to be secure to prevent unauthorized control. While commercial CAs are the standard for public-facing websites, there are scenarios where a self-signed certificate offers a viable alternative for internal or controlled environments.
Understanding Self-Signed SSL Certificates
A self-signed SSL certificate is a certificate that is signed by its own creator, rather than by a trusted Certificate Authority (CA). In essence, the issuer and the subject of the certificate are the same entity. This means that the certificate’s authenticity is not validated by an independent, trusted third party.
The Creation Process
Creating a self-signed certificate is a straightforward technical process, often involving command-line tools like OpenSSL. The process typically involves:
- Generating a Private Key: This is a secret key used for encryption and decryption.
- Generating a Public Key: This key is derived from the private key and is used for encryption.
- Creating a Certificate Signing Request (CSR): This contains information about the entity requesting the certificate (e.g., domain name, organization name).
- Signing the CSR with the Private Key: This action generates the self-signed certificate.
The resulting certificate contains the public key and identity information, but the signature is made by the private key corresponding to the public key within the certificate itself.
Key Characteristics and Differences
The fundamental difference between a self-signed certificate and one issued by a CA lies in the trust model.
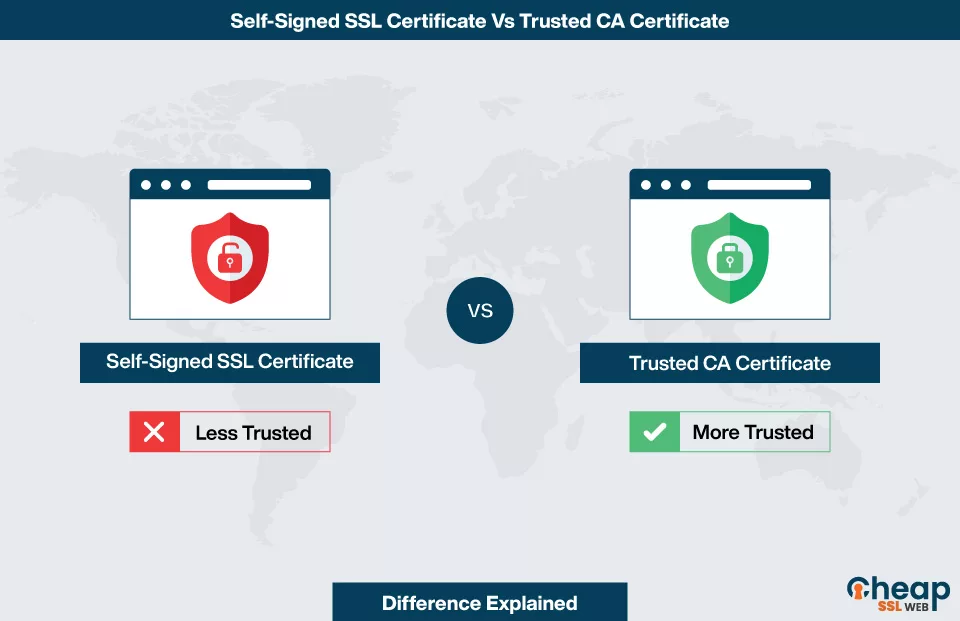
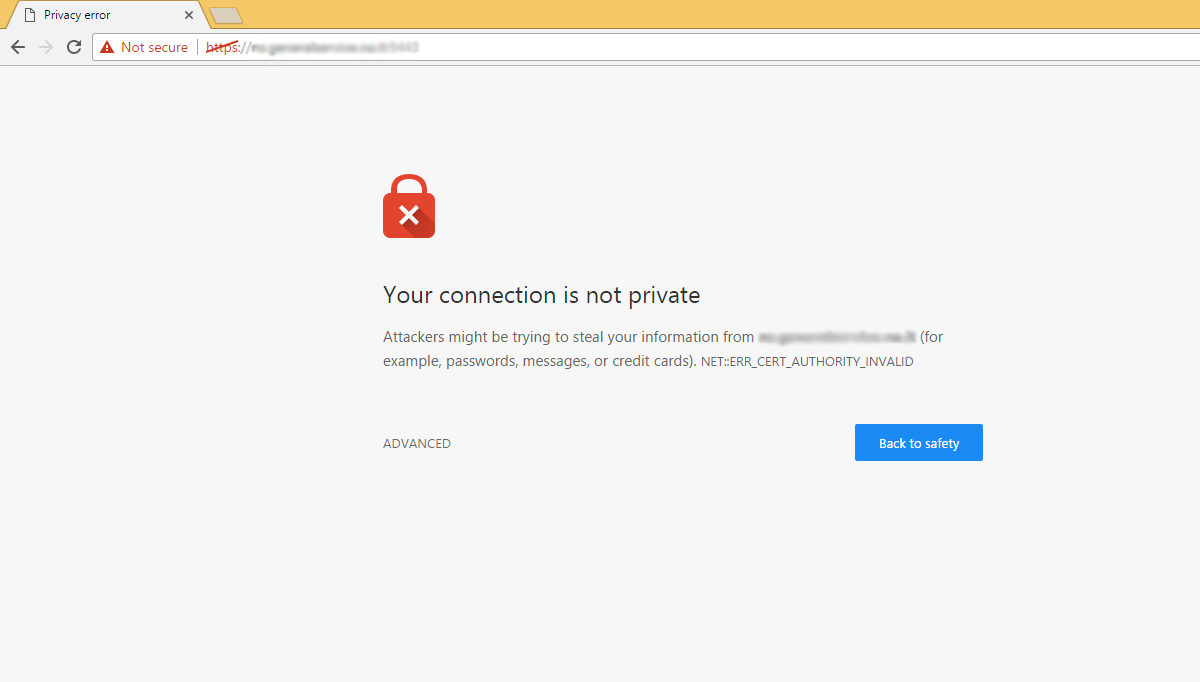
- Trust: Certificates from CAs are trusted by default by most browsers and operating systems because the CAs themselves are trusted. Self-signed certificates are not inherently trusted. Any client attempting to connect to a service secured by a self-signed certificate will typically receive a warning about an untrusted connection.
- Validation: CAs have rigorous validation processes to confirm the identity of the certificate applicant. Self-signed certificates bypass this external validation.
- Cost: Obtaining certificates from CAs can involve annual fees. Self-signed certificates are essentially free to generate.
- Use Cases: CA-issued certificates are essential for public-facing websites and services where broad, automatic trust is required. Self-signed certificates are best suited for internal networks, development environments, or specific controlled applications where trust can be manually established.
Security Implications
The primary security concern with self-signed certificates is the lack of third-party validation. An attacker could, in theory, create a self-signed certificate that appears legitimate to a specific, unsophisticated client, thereby impersonating a trusted server. For this reason, self-signed certificates should never be used for public-facing applications or to secure sensitive data exchanged over the public internet without an explicit, manual trust establishment process.
Applications of Self-Signed Certificates in Tech & Innovation
While not suitable for general public internet use, self-signed SSL certificates offer practical and cost-effective solutions for secure communication within controlled environments common in the tech and innovation sectors, especially concerning drone operations.
Development and Testing Environments
During the development and testing phases of drone software, communication protocols, or cloud integration platforms, developers often need to simulate secure connections. Setting up a full CA infrastructure for internal testing can be complex and costly. A self-signed certificate allows developers to quickly establish an HTTPS endpoint for their applications, enabling them to test encryption, authentication, and secure data transfer mechanisms without the overhead of external validation. This is particularly useful when developing APIs that drones might interact with, or for simulating secure ground control station communication.
Internal Networks and Private Cloud Deployments
For organizations that operate their own private cloud infrastructure or manage internal networks for drone fleet management, data storage, or operational control, self-signed certificates can be a practical choice. If all devices and users within this private network trust the self-signed certificate (e.g., by manually installing the certificate on all endpoints or configuring them to trust the issuing entity), then secure communication can be established. This is beneficial for:
- Drone Fleet Management Systems: Securely transmitting telemetry data, receiving flight plan updates, and managing remote commands within a corporate network.
- On-Premises Data Storage: Encrypting data uploaded from drones before it’s stored on local servers.
- Internal Communication Channels: Securing communication between different components of a drone ecosystem, such as sensors, flight controllers, and processing units.
Specific Device-to-Device Communication
In certain advanced drone applications, direct, secure communication between onboard components or between a drone and a dedicated, on-site processing unit might be required. For example, a drone equipped with advanced AI for real-time object detection might transmit its findings directly to a nearby edge computing device. If both devices are trusted within a confined operational area, a self-signed certificate can secure this point-to-point communication, ensuring the integrity of the analyzed data and the commands exchanged.
Bridging to Public Services with Manual Trust
While generally discouraged, there can be niche scenarios where a self-signed certificate is used as an intermediary to establish a secure connection that is then further secured. For instance, a drone might connect to an internal gateway using a self-signed certificate, and this gateway then establishes a standard, CA-signed SSL connection to a public cloud service. This approach can add an extra layer of internal security, though it complicates management and requires careful consideration of trust.
Managing Trust with Self-Signed Certificates
The key challenge and advantage of self-signed certificates lie in trust management. Since they are not automatically trusted, the burden of establishing trust falls on the administrator or the end-user.
Manual Trust Establishment
The most common method is to manually import the self-signed certificate into the trust store of the client devices or applications that need to communicate with the service. For example:
- On ground stations: The self-signed certificate of a private drone management server can be imported into the operating system’s or application’s certificate store.
- On drones: If the drone’s operating system or firmware allows it, the certificate can be added to its trusted root certificates.
This process ensures that the client device recognizes and trusts the certificate, thereby preventing security warnings and enabling encrypted communication.
Automated Trust Distribution
In larger deployments or more sophisticated systems, trust can be managed more programmatically.
- Configuration Management Tools: Tools like Ansible, Chef, or Puppet can be used to automate the distribution and installation of self-signed certificates across multiple devices within a network.
- Custom Software Integration: Applications designed to interact with drone systems can be built with the capability to securely retrieve and trust a specific self-signed certificate from a known source during their initial setup or configuration.
Considerations for Production Environments
While self-signed certificates are valuable for development, testing, and highly controlled internal environments, their use in critical production systems that interact with the public internet or handle extremely sensitive data should be approached with extreme caution. The potential for impersonation, even if reduced in a controlled environment, remains a risk.
For public-facing applications or when interoperability with unknown or untrusted entities is a requirement, obtaining certificates from reputable CAs is the industry standard and the most secure approach. The investment in a CA-issued certificate provides a robust framework of trust that is essential for widespread adoption and user confidence. However, for internal innovation, controlled data flows, and specialized drone operational technology where trust can be explicitly managed, self-signed certificates provide a flexible and economical pathway to securing communication channels.