
In the increasingly digital landscape of modern cyber security, understanding and combating threats requires a deep dive into the remnants left behind by malicious actors. This is where digital forensics emerges as a critical discipline. Far from being a niche area, digital forensics forms the bedrock of incident response and investigative efforts within cyber security, providing the tangible evidence needed to understand, attribute, and prevent future attacks.
The Foundational Pillars of Digital Forensics
At its core, digital forensics is the application of scientific investigation principles to identify, collect, preserve, analyze, and present digital evidence. In the context of cyber security, this translates to meticulously examining electronic devices and digital media to uncover traces of unauthorized access, data breaches, malware infections, or other cybercrimes. The goal is not just to identify the “what” of an incident, but also the “how,” “when,” “where,” and crucially, “who.”

Evidence Acquisition and Preservation: The First Response
The integrity of digital evidence is paramount. Any mishandling during acquisition can render it inadmissible in legal proceedings or compromise the investigation’s validity. The initial stages involve identifying potential sources of evidence, which can range from servers and workstations to mobile devices, network logs, and even cloud storage.
Chain of Custody: Maintaining Evidentiary Integrity
A fundamental principle in digital forensics is the chain of custody. This is a chronological documentation or paper trail that shows the seizure, custody, control, transfer, analysis, and disposition of evidence. Strict adherence to the chain of custody ensures that the evidence has not been tampered with, altered, or contaminated since it was collected. This meticulous record-keeping is essential for demonstrating the reliability and authenticity of the evidence presented.
Imaging and Write-Blocking: Capturing an Unaltered State
Before any analysis can begin, a forensically sound copy, or “image,” of the original digital media must be created. This is typically done using specialized hardware or software that ensures data is read from the original source without making any modifications. Write-blocking hardware is a crucial tool in this process, preventing any accidental writes to the source drive, thereby preserving its original state. This forensic image then becomes the primary object of analysis, leaving the original evidence untouched.
Data Analysis: Unraveling the Digital Narrative
Once the evidence is securely acquired and preserved, the intricate process of analysis begins. This phase involves sifting through vast amounts of data to find relevant clues, reconstruct events, and identify patterns indicative of malicious activity.
File System Analysis: The Blueprint of Data
Understanding the file system of a device is critical. Forensists examine file creation, modification, and access times, deleted files, and unallocated space. These seemingly innocuous details can reveal crucial information about when a system was compromised, what files were accessed or altered, and how data was exfiltrated. Techniques like file carving, which reconstructs fragmented files from raw data, are essential for recovering deleted or damaged information.
Memory Forensics: The Ephemeral Footprint
Volatile memory (RAM) contains a wealth of transient information that can be crucial for understanding an active compromise. This includes running processes, network connections, encryption keys, and even the command history of an attacker. Acquiring and analyzing memory dumps can provide immediate insights into an ongoing attack, allowing for rapid containment and remediation.
Network Forensics: Tracing the Digital Pathways
Network traffic logs, packet captures, and firewall records are vital for understanding how an attacker gained access, moved laterally within a network, and exfiltrated data. Network forensics involves analyzing this data to identify suspicious connections, malware communication patterns, and the origin and destination of data transfers.
Malware Analysis: Deconstructing the Digital Weapon
When malware is suspected, a dedicated analysis is performed to understand its functionality, propagation methods, and impact. This often involves static analysis (examining the code without execution) and dynamic analysis (running the malware in a controlled, isolated environment to observe its behavior). This deep understanding helps in developing detection signatures and remediation strategies.
The Role of Digital Forensics in Cyber Security Incident Response
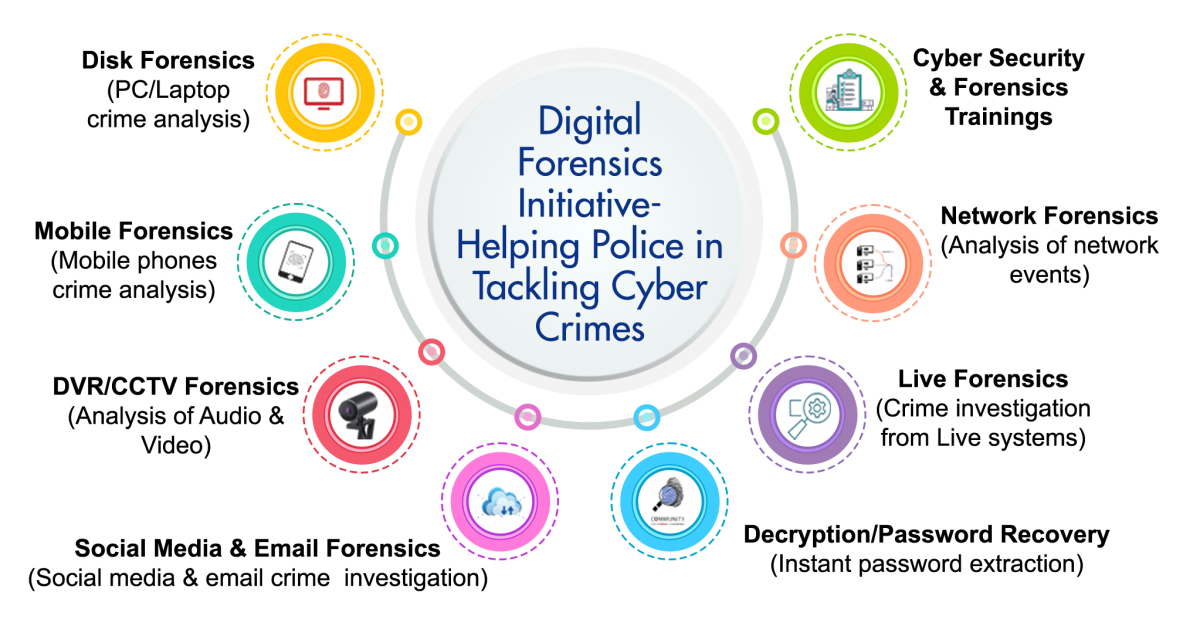
Digital forensics is not an isolated discipline; it is intrinsically woven into the fabric of effective cyber security incident response. When a security incident occurs, be it a data breach, ransomware attack, or insider threat, digital forensics provides the systematic approach to understanding the incident and guiding the response.
Incident Triage and Containment: Immediate Actions
In the immediate aftermath of an incident, digital forensics plays a role in identifying the scope and nature of the breach. This allows security teams to prioritize containment efforts, preventing further damage or data loss. Understanding the initial point of compromise through forensic analysis is crucial for effective isolation of affected systems.
Root Cause Analysis: Identifying the “Why”
Beyond simply containing an incident, digital forensics aims to identify the root cause. Was it a vulnerability in a software application? A phishing attack that succeeded? An unpatched system? Uncovering the root cause is essential for implementing long-term preventative measures and strengthening the overall security posture.
Post-Incident Recovery and Remediation: Rebuilding Trust
Once the incident is contained and the root cause understood, forensic findings inform the recovery process. This might involve restoring systems from clean backups, patching vulnerabilities, and implementing new security controls. The insights gained from the forensic investigation help ensure that the remediation efforts are comprehensive and address the underlying weaknesses exploited by the attacker.
Legal and Compliance Implications: Accountability and Evidence
In cases where legal action or regulatory compliance is a factor, digital forensics is indispensable. The evidence collected and analyzed by forensic experts can be used to identify perpetrators, support legal proceedings, and demonstrate compliance with data protection regulations. The rigor and scientific methodology employed by digital forensic investigators lend credibility to their findings in legal and regulatory contexts.
Advanced Techniques and Future Trends in Digital Forensics
The field of digital forensics is continuously evolving, driven by the ever-changing threat landscape and the exponential growth of data. New technologies and methodologies are constantly being developed to keep pace.
Cloud Forensics: Navigating the Digital Sky
The increasing adoption of cloud computing presents unique challenges for digital forensics. Investigating incidents that span cloud environments requires specialized tools and techniques to access and analyze data residing on third-party infrastructure. Understanding cloud provider logs, service configurations, and data residency becomes paramount.
Mobile Device Forensics: The Pocket-Sized Investigator
Smartphones and tablets are ubiquitous, making them prime targets for data theft and avenues for attack. Mobile device forensics involves extracting and analyzing data from these devices, including call logs, text messages, app data, location history, and deleted information, providing insights into user activity and potential compromise.
Internet of Things (IoT) Forensics: The Expanding Attack Surface
The proliferation of interconnected devices in the Internet of Things (IoT) creates a vast and often poorly secured attack surface. Forensic examination of IoT devices, from smart home appliances to industrial sensors, is becoming increasingly important for understanding how these devices are compromised and used as entry points into networks or for malicious purposes.
Artificial Intelligence and Machine Learning in Forensics: Enhancing Detection and Analysis
The application of AI and ML is beginning to revolutionize digital forensics. These technologies can automate repetitive tasks, identify subtle patterns in large datasets that might be missed by human analysts, and even predict potential areas of forensic interest. AI-powered tools can accelerate the analysis process and improve the accuracy of investigations.

The Human Element: Skills and Expertise
Despite the advancements in tools and technologies, the human element remains critical in digital forensics. Skilled forensic investigators possess a combination of technical expertise, analytical reasoning, and an understanding of attacker methodologies. Their ability to interpret complex data, draw logical conclusions, and present findings clearly is what makes digital forensics such a powerful tool in the arsenal of cyber security professionals.
In conclusion, digital forensics is an indispensable discipline within cyber security. It provides the scientific rigor and investigative prowess necessary to understand, respond to, and ultimately prevent cyber threats. As technology continues to advance and the complexity of cyber-attacks grows, the role of digital forensics will only become more vital in safeguarding our increasingly digital world.