
The Critical Role of VLANs in Advanced Drone Ecosystems
In the rapidly evolving landscape of drone technology and innovation, network infrastructure forms the backbone of operations, data management, and autonomous systems. From real-time telemetry streaming for high-precision autonomous flight systems to the secure transfer of massive remote sensing datasets, the integrity and isolation of network traffic are paramount. Virtual Local Area Networks (VLANs) are foundational in achieving this, allowing administrators to logically segment networks regardless of physical topology. For drone enterprises managing vast fleets, processing sensitive geospatial mapping data, or enabling beyond visual line of sight (BVLOS) operations, VLANs ensure that command and control signals are isolated from payload data, and administrative traffic is kept separate from guest access. This segmentation is vital not only for performance and compliance but, critically, for security.
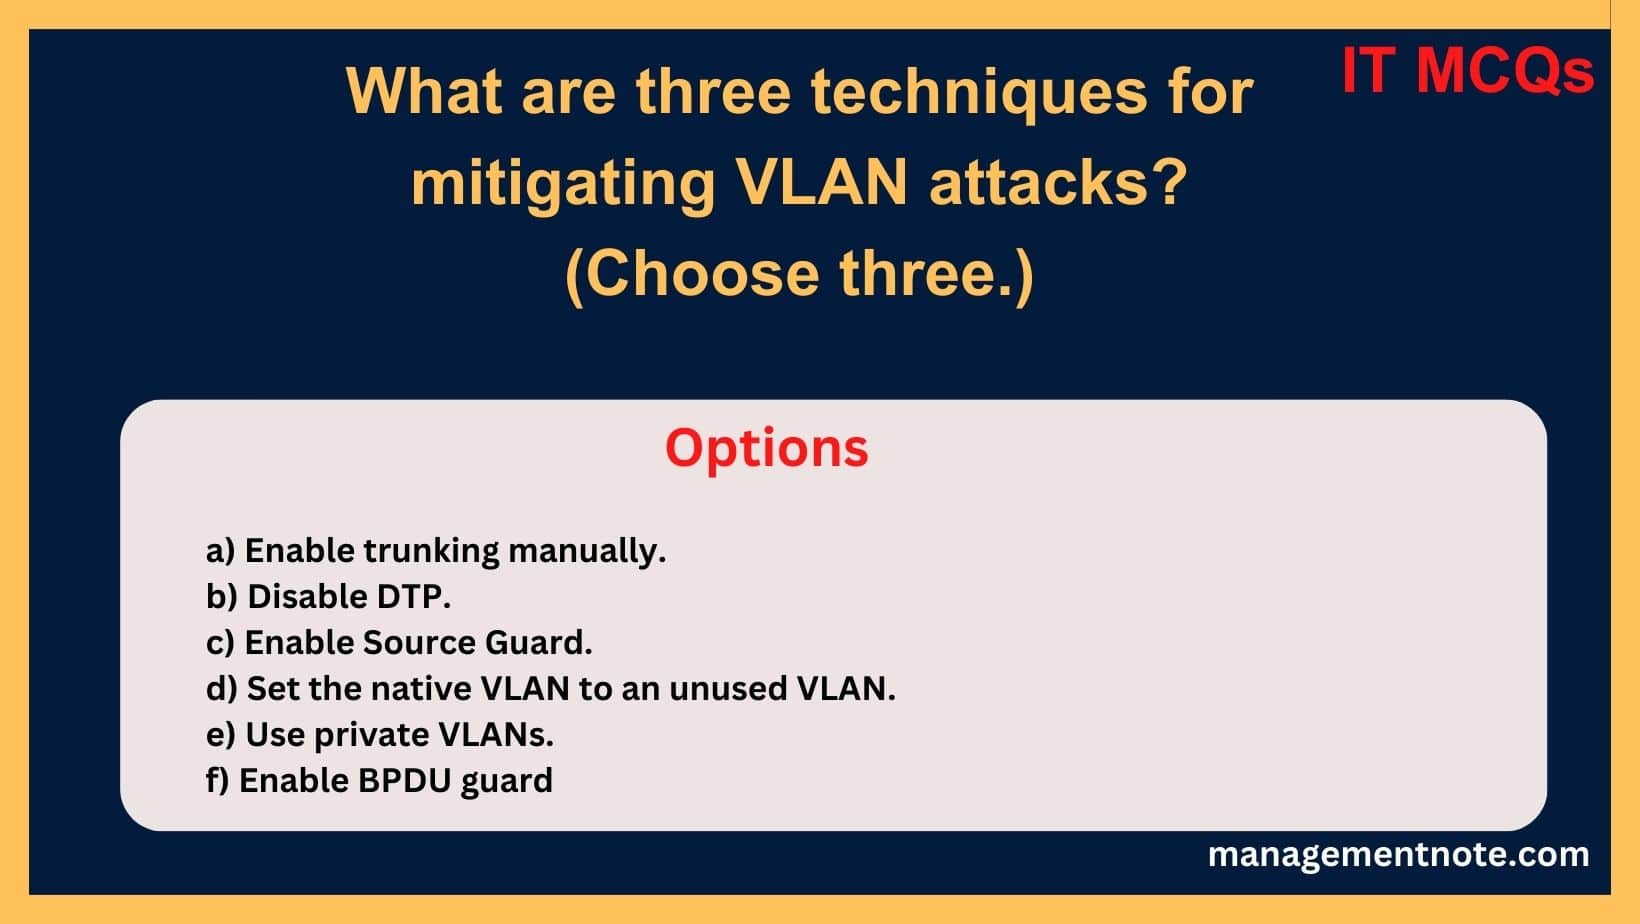
As drone applications become more sophisticated, integrating with AI-driven analytics, cloud-based processing for mapping algorithms, and complex ground control station architectures, the underlying network becomes an increasingly attractive target for malicious actors. VLAN attacks, which aim to bypass logical network segmentation, pose a significant threat. A successful VLAN attack could lead to unauthorized access to critical drone operational data, interference with flight commands, or the exfiltration of sensitive intellectual property derived from remote sensing missions. Therefore, understanding and implementing robust mitigation techniques is not just an IT concern but a strategic imperative for safeguarding the future of drone innovation.
Robust Segmentation via Port Security and Access Control Lists
One of the most effective foundational techniques for mitigating VLAN attacks in any sophisticated network, including those supporting advanced drone technology, involves a dual approach: strict port security combined with meticulously crafted Access Control Lists (ACLs). These mechanisms work in concert to ensure that network access points are secured and that traffic flowing within and between VLANs adheres to predefined security policies, directly protecting the sensitive data streams and command channels vital for autonomous flight and remote sensing.
Implementing Strict Port Security
Port security is a Layer 2 control feature implemented directly on network switches, offering a first line of defense against unauthorized devices attempting to connect to a specific VLAN. For drone ground control stations, data processing servers, or even charging stations that connect directly to the enterprise network, port security can be configured to allow only specific MAC addresses (the unique identifiers of network interfaces) to access a particular switch port. This means that if an attacker attempts to connect an unauthorized device to a port designated for a drone-specific VLAN, the switch can immediately detect the violation.
Administrators can configure various actions upon a security violation, such as:
- Protect: Drops packets from unauthorized sources without notification.
- Restrict: Drops packets from unauthorized sources and sends an SNMP trap or syslog message.
- Shutdown: Disables the port entirely, requiring manual intervention to re-enable it.
For drone operations, especially those handling sensitive data or real-time flight commands, the “shutdown” mode is often preferred, as it immediately neutralizes the threat by isolating the unauthorized device. Furthermore, the number of MAC addresses allowed per port can be limited, preventing an attacker from spoofing multiple MAC addresses to bypass security. This is particularly crucial for ports connected to servers hosting drone-derived data or mission planning software, where integrity is non-negotiable.
Deploying Granular Access Control Lists (ACLs)
While port security guards the ingress points, ACLs provide a more granular, Layer 3 and Layer 4 filtering capability that dictates what traffic is permitted to flow across VLAN boundaries or even within a single VLAN. ACLs are rules that can be applied to switch interfaces (both physical and VLAN interfaces) or router interfaces to permit or deny packets based on criteria such as source IP address, destination IP address, source port, destination port, and protocol type.
In a drone ecosystem, ACLs can be strategically deployed to:
- Restrict inter-VLAN communication: For instance, preventing a guest Wi-Fi VLAN from accessing the VLAN segment dedicated to drone command and control.
- Isolate critical systems: Ensuring that only specific IP addresses belonging to authorized ground control stations can communicate with drone data servers in a different VLAN.
- Filter specific protocols: Blocking non-essential protocols from being used on VLANs that carry sensitive telemetry or mapping data, reducing the attack surface.
- Enforce compliance: Ensuring that data flows adhere to regulatory requirements by restricting access to sensitive drone imagery or sensor data to authorized personnel or systems only.
By combining the physical layer security of port security with the logical filtering capabilities of ACLs, drone operators can create a robust, multi-layered defense that significantly reduces the risk of VLAN-based attacks, thereby securing critical technological assets and innovations.
Defending Against VLAN Hopping and Double Tagging Exploits
Beyond basic unauthorized access, sophisticated VLAN attacks often exploit inherent mechanisms designed for network flexibility. Two prominent examples are VLAN hopping and double tagging. Both aim to circumvent VLAN segmentation and gain unauthorized access to isolated network segments. Mitigating these requires specific, proactive configurations to secure the integrity of logical segmentation, which is paramount for the secure operation of autonomous drone systems and the protection of remote sensing data.
Preventing VLAN Hopping
VLAN hopping attacks typically fall into two categories: switch spoofing and double tagging (which we’ll cover separately). In a switch spoofing attack, an attacker’s device attempts to impersonate a network switch and negotiate a trunking protocol (like Cisco’s DTP – Dynamic Trunking Protocol) with a legitimate switch. If successful, the attacker’s device gains access to all VLANs traversing that trunk, effectively “hopping” into any VLAN segment.
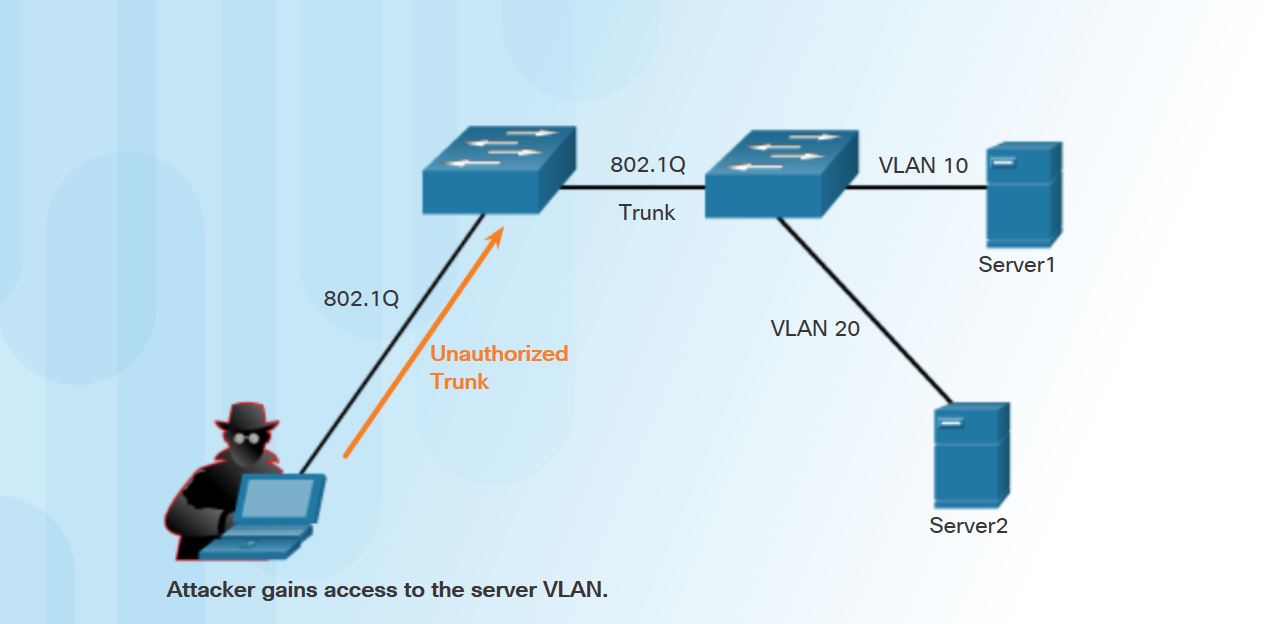
To prevent VLAN hopping via switch spoofing:
- Disable Dynamic Trunking Protocol (DTP): This is the most critical step. DTP should be explicitly disabled on all user-facing ports. Ports should be configured as either
accessports (belonging to a single VLAN) ortrunkports (carrying multiple VLANs) based on their intended function, but never left indynamic autoordynamic desirablemodes. For ports connecting to ground control stations or drone data storage, they should always be access ports. - Manually Configure Trunk Ports: Only ports genuinely intended to carry traffic for multiple VLANs (e.g., inter-switch links, connections to specific servers needing access to multiple segments) should be configured as trunk ports. Even then, best practice dictates specifying allowed VLANs on these trunks (
switchport trunk allowed vlan). This minimizes the exposure of all VLANs to every trunk. - Native VLAN Mismatch Detection: Ensure the native VLAN on trunk ports is explicitly defined and that it is not VLAN 1 (the default management VLAN) and is not used by any user traffic. Mismatched native VLANs can be exploited, so consistency and isolation of the native VLAN are key.
By eliminating the dynamic negotiation of trunk links, administrators effectively remove the primary vector for switch spoofing attacks, ensuring that drone operational VLANs remain isolated.
Countering Double Tagging Exploits
Double tagging (or VLAN stacking) is a more subtle VLAN hopping technique that relies on the way switches process VLAN tags. In this attack, a malicious actor crafts a frame with two VLAN tags: an outer tag pointing to the attacker’s native VLAN (which the first switch removes) and an inner tag pointing to the target VLAN. When the first switch receives the frame on an access port belonging to its native VLAN, it strips off the outer tag and forwards the frame. The second switch (or subsequent switches) then sees only the inner, malicious tag and forwards the frame to the target VLAN, bypassing the intended segmentation.
Mitigation strategies for double tagging include:
- Change the Native VLAN: As mentioned for VLAN hopping, never use VLAN 1 as the native VLAN. It should be an unused, arbitrary VLAN ID. This makes it harder for an attacker to craft the outer tag to match the native VLAN.
- Do Not Use the Native VLAN for User Traffic: The native VLAN should be completely isolated and not carry any user or management traffic. Its sole purpose should be for untagged frames on trunk links, and even then, untagged traffic should be minimized.
- Explicitly Tag All Frames on Trunk Ports: While the IEEE 802.1Q standard allows for untagged frames on the native VLAN, many network devices can be configured to tag all frames, including those belonging to the native VLAN. This eliminates the vulnerability that double tagging exploits by ensuring no frames are processed without a tag. This configuration might be vendor-specific but offers the strongest defense against this particular attack.
By meticulously configuring trunk ports, disabling dynamic negotiation, and isolating the native VLAN, organizations can significantly bolster the security of their drone-related network segments against these advanced VLAN manipulation techniques, safeguarding critical command, control, and data transfer operations.
Enhancing Isolation with Private VLANs (PVLANs)
While standard VLANs provide logical segmentation between groups of devices, Private VLANs (PVLANs) offer an even finer grain of isolation within a single primary VLAN. This advanced technique is particularly beneficial in environments where robust security and strict isolation are required between devices that are otherwise members of the same logical segment, such as for cloud-based drone service providers, multi-tenant ground control station infrastructures, or public access points related to drone operations. PVLANs significantly reduce the attack surface by preventing direct communication between specific devices, even if they share the same subnet and VLAN.
PVLAN Fundamentals
A Private VLAN structure consists of several components:
- Primary VLAN: This is the overarching VLAN that encapsulates one or more secondary VLANs. Devices in different secondary VLANs can only communicate with devices in the primary VLAN (e.g., a router or firewall) or with each other if they are in the promiscuous type of secondary VLAN.
- Secondary VLANs: These exist within the primary VLAN and provide the actual isolation. There are two types:
- Isolated VLANs: Ports assigned to an isolated VLAN can only communicate with promiscuous ports. They cannot communicate with other ports within the same isolated VLAN, nor with ports in other isolated or community VLANs. This is ideal for ensuring that individual drone assets, guest devices, or partner connections cannot directly interact with each other.
- Community VLANs: Ports within a community VLAN can communicate with each other and with promiscuous ports, but they cannot communicate with ports in other community VLANs or isolated VLANs. This allows for controlled collaboration between specific groups of devices (e.g., a team of drone pilots sharing resources while remaining isolated from another team).
A promiscuous port is a port that belongs to the primary VLAN and can communicate with all other ports within that primary VLAN (including all isolated and community secondary VLANs). Typically, router interfaces or firewall connections are configured as promiscuous ports to allow controlled traffic flow into and out of the PVLAN domain.
Isolated Port Implementations in Drone Technology
The application of PVLANs holds immense value for securing drone-related infrastructure:
- Multi-Tenant Drone-as-a-Service Platforms: A provider offering cloud-based drone flight planning, data processing, or simulation services to multiple clients could place each client’s specific virtual machines or network segments into separate isolated VLANs. Even if these clients appear to be on the same subnet, PVLANs would prevent client A from directly communicating with or attacking client B’s infrastructure, enhancing data sovereignty and security.
- Secure Public Access Points: If drone operators provide public Wi-Fi or kiosks for accessing limited drone data (e.g., flight schedules, public imagery), these devices can be placed in an isolated VLAN. This prevents users on these public access points from directly communicating with each other or with more sensitive internal drone operational networks, mitigating risks like peer-to-peer attacks or lateral movement.
- Ground Control Station Isolation: In large-scale operations where multiple ground control stations might be physically co-located but require stringent isolation (e.g., different mission types, different security clearances), PVLANs can ensure that one ground station’s components cannot directly interact with another’s, even if they are on the same switch and logical primary VLAN.
- IoT Device Security in Drone Ecosystems: With the proliferation of IoT sensors and devices contributing to drone data collection or environmental monitoring, PVLANs can isolate each device or small groups of devices. This containment prevents a compromised IoT sensor from directly attacking other devices on the network, limiting the blast radius of a potential breach.
By implementing Private VLANs, organizations can achieve a superior level of network segmentation that goes beyond traditional VLANs, offering an advanced layer of defense crucial for the secure and reliable operation of cutting-edge drone technology and the sensitive data it generates.

Building a Resilient Network for Future Drone Innovations
The advancements in drone technology—from autonomous flight choreography to sophisticated AI-driven remote sensing and real-time data analytics—place unprecedented demands on network infrastructure. The security of the underlying network, particularly the integrity of its VLAN segmentation, is not merely a supplementary concern but a fundamental requirement for the reliable and secure functioning of these innovations. Mitigating VLAN attacks through robust techniques like stringent port security, precise ACLs, diligent prevention of VLAN hopping and double tagging exploits, and the strategic deployment of Private VLANs is therefore essential.
These techniques, when implemented correctly, build a resilient network architecture capable of safeguarding critical drone operational data, ensuring the integrity of flight commands, and protecting proprietary insights derived from advanced mapping and sensing missions. A proactive and multi-layered approach to network security ensures that the logical isolation intended by VLANs cannot be circumvented, thereby preserving the security and performance benefits they offer. As drone technology continues to push boundaries, integrating deeper into critical infrastructure and becoming increasingly autonomous, the emphasis on robust, unassailable network segmentation will only grow. Investing in and meticulously maintaining these mitigation strategies forms the bedrock upon which future drone innovations can securely take flight, allowing for continued exploration, efficiency, and expansion in the aerial technology domain.