
The rapid evolution of drone technology has transformed industries ranging from logistics and agriculture to public safety and infrastructure inspection. As drones become more autonomous, interconnected, and capable of collecting vast amounts of sensitive data, the complexity of managing access to these sophisticated systems and their valuable outputs intensifies. Traditional access control mechanisms, which often rely on predefined roles, struggle to keep pace with the dynamic, nuanced requirements of modern drone operations. This is where Attribute-Based Access Control (ABAC) emerges as a pivotal advancement within the Tech & Innovation landscape, offering a flexible and scalable solution for securing the drone ecosystem.
The Evolving Landscape of Drone Technology and Security
Modern drone applications are no longer confined to simple recreational flights. They encompass complex missions involving multiple operators, diverse data types, autonomous decision-making, and interactions with various networked systems. Consider a fleet of drones conducting infrastructure inspections, simultaneously collecting high-resolution imagery, thermal data, and LiDAR scans. Different teams—inspectors, data analysts, regulatory bodies, and maintenance personnel—will require varying levels of access to the drones themselves, their flight capabilities, and the sensitive data they generate.
Traditional Role-Based Access Control (RBAC), while effective in many IT environments, often falls short in this intricate domain. RBAC assigns permissions based on a user’s role (e.g., “Pilot,” “Analyst”). However, the context of drone operations is rarely static; access might need to vary based on the specific drone model, its current location, the time of day, the criticality of the mission, or the certification level of the operator for a particular airspace. This granularity and dynamism are precisely what ABAC is designed to address, providing a framework for managing access that is both robust and adaptable.
Understanding Attribute-Based Access Control (ABAC)
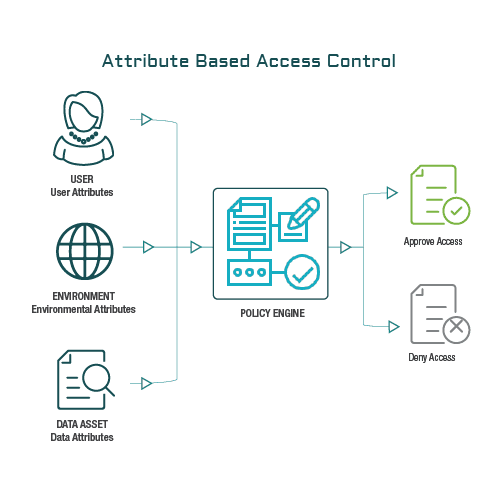
Attribute-Based Access Control is a logical access control model that grants or denies access to resources based on an evaluation of attributes associated with the subject (user), the object (resource), the action being requested, and the environment context. Unlike RBAC, which pre-defines permissions for roles, ABAC evaluates a set of attributes in real-time against a predefined policy to make an access decision.
Beyond Role-Based Access Control (RBAC)
RBAC defines permissions by assigning users to roles, and roles to permissions. For instance, a “Drone Pilot” role might have permission to “fly drone.” While simple, this approach can become unwieldy when the number of roles or the complexity of permissions grows. If access needs to be restricted only to pilots certified for heavy-lift drones, flying in specific geo-fenced areas, during daylight hours, for a particular client project, RBAC would require creating a multitude of highly specific roles, leading to “role explosion.” This complexity makes management difficult and prone to errors.
ABAC transcends these limitations by not relying on static roles. Instead, it uses a dynamic policy engine that evaluates attributes. This allows for far more granular and flexible control, adapting to the unique circumstances of each access request without the need for an ever-expanding list of roles.
Core Components of ABAC
Implementing an ABAC system involves several key components that work in concert to enforce access policies:
- Attributes: These are fundamental to ABAC. Attributes are characteristics or properties associated with various entities involved in an access request.
- Subject Attributes: Describe the entity requesting access (e.g., user ID, pilot license number, certification level, department, clearance level, location).
- Object Attributes: Describe the resource being accessed (e.g., drone serial number, drone model, data sensitivity, mission type, airspace classification, data owner).
- Action Attributes: Describe the operation being attempted (e.g., “fly,” “download data,” “configure settings,” “disarm”).
- Environment Attributes: Describe the context of the access request (e.g., time of day, date, geographical location of the drone or operator, weather conditions, network security posture).
- Policies: Policies are rules that combine attributes using logical expressions (e.g., AND, OR, NOT) to determine whether access should be granted or denied. A policy might look like: “Permit Subject.PilotLicense=’Commercial’ to Action=’Fly’ Object.DroneModel=’HeavyLift’ if Environment.GeoFence=’ApprovedIndustrialZone’ AND Environment.TimeOfDay=’DaylightHours’.”
- Policy Enforcement Point (PEP): This is the component that intercepts access requests and enforces the decision made by the Policy Decision Point. In a drone system, the PEP could be integrated into the ground control station software, the drone’s flight controller, or a cloud-based data storage system.
- Policy Decision Point (PDP): When a PEP receives an access request, it sends the relevant attributes to the PDP. The PDP evaluates these attributes against the stored policies and returns an “allow” or “deny” decision to the PEP.
- Policy Information Point (PIP): The PIP acts as a source for attribute values. It can pull attributes from various databases or identity management systems (e.g., a pilot’s certification database, a drone’s telemetry system, a weather service API).
ABAC in Action: Practical Applications for Drones
The flexibility of ABAC makes it uniquely suited for the intricate security demands of modern drone operations, particularly within the realms of Tech & Innovation.

Autonomous Flight and Mission Management
For autonomous drone fleets, ABAC can precisely control which operators, or even other authorized AI systems, can initiate, modify, or terminate specific flight plans. For example:
- A policy could stipulate that only pilots with “Level 3 Autonomous Operations Certification” can deploy a drone for “Beyond Visual Line of Sight (BVLOS)” missions using a specific “High-Payload Drone Model” in a “Pre-approved Corridor.”
- Access to emergency override commands for a swarm of delivery drones might be restricted to “Fleet Managers” located within the “Operations Center” during “Active Flight Times.”
- Different mission parameters—such as maximum altitude, speed, or specific Waypoint sequences—could be dynamically controlled based on the drone’s current “Battery Level,” “Weather Conditions,” and the “Assigned Mission Priority.”
Data Security and Remote Sensing
Drones are powerful data collection platforms, generating vast amounts of sensitive information from mapping and surveying to surveillance. Protecting this data from unauthorized access, viewing, or distribution is paramount.
- ABAC can ensure that “Thermal Imagery Data” collected from a “Confidential Client Project” is only accessible to “Project Team Members” with “Data Analyst Clearance” and only when they are connected from an “Approved Secure Network.”
- High-resolution “Agricultural Survey Data” might be viewable by “Farm Managers” but “Editable” only by “Agronomists” and only for data pertaining to their specific “Assigned Farm ID.”
- Access to “Personally Identifiable Information (PII)” captured during public safety operations could be strictly limited to “Law Enforcement Personnel” with a “Specific Case ID” and accessed only within “Audited Systems.”
Fleet Management and Compliance
Managing a large fleet of drones requires strict adherence to regulatory standards and operational protocols. ABAC simplifies this by embedding compliance directly into the access control logic.
- A policy could automatically prevent any “Unlicensed Drone Model” from being armed or flown in “Regulated Airspace” if the “Operator’s License Status” is “Expired.”
- Access to critical drone maintenance logs or firmware update capabilities might be restricted to “Certified Maintenance Technicians” and only for drones flagged with a “Maintenance Status = Due.”
- Geospatial attributes can enforce “No-Fly Zones” by denying any “Action=’Fly'” if the “Object.DroneLocation” intersects with a “Restricted Airspace Polygon” or an “Environment.TemporaryFlightRestriction” notice.
AI Integration and Collaborative Operations
As AI increasingly drives autonomous drone functions, securing the interaction between AI systems, human operators, and other networked entities becomes crucial.
- An AI “Obstacle Avoidance System” might be granted access to “Drone.SensorData.Lidar” but explicitly denied access to “Drone.ControlSystem.ManualOverride.”
- In collaborative missions involving multiple agencies (e.g., fire department and police), ABAC can dynamically adjust access to shared drone resources or real-time feeds based on the “Incident Commander’s Authorization” and the “Severity of the Incident.” For instance, only the fire department might be able to control drone movement over a fire, while both departments can view the live video feed, but access to recorded video might be restricted to specific personnel.
Advantages and Challenges of Implementing ABAC for Drones
The shift to ABAC for drone systems brings significant benefits but also introduces certain complexities.
Key Benefits
- Fine-Grained Control: Provides unparalleled precision in defining who can do what, with which drone, under what circumstances.
- Flexibility and Scalability: Easily adapts to new drone models, mission types, regulatory changes, or user roles without requiring extensive reconfigurations. Policies can be updated dynamically.
- Dynamic Policy Enforcement: Access decisions are made in real-time, leveraging current contextual information.
- Enhanced Security: Reduces the risk of unauthorized access by ensuring that permissions are always evaluated against the latest attributes and policies.
- Compliance Enablement: Simplifies adherence to complex regulations by baking compliance rules directly into the access control policies.
- Reduced Administrative Overhead: Over time, can decrease the effort needed for access management compared to complex RBAC deployments, especially in dynamic environments.

Potential Challenges
- Complexity of Policy Definition: Designing comprehensive and unambiguous ABAC policies requires careful planning and a deep understanding of attributes and their relationships. Poorly defined policies can lead to unintended access or denials.
- Attribute Management: Sourcing, maintaining, and synchronizing a large number of attributes from various systems (identity providers, drone telemetry, environmental sensors, regulatory databases) can be challenging.
- Performance Overhead: Real-time evaluation of complex policies can introduce latency, which is critical in time-sensitive drone operations. Optimized policy engines are crucial.
- Initial Setup Costs: The initial investment in developing or integrating ABAC infrastructure and defining policies can be substantial.
- Auditability: While ABAC provides detailed logging of access decisions, interpreting these logs for auditing purposes can be complex given the dynamic nature of policy evaluation.
As drone technology continues its trajectory towards greater autonomy, interconnectedness, and broader integration into critical infrastructure, the need for sophisticated security frameworks will only intensify. Attribute-Based Access Control represents a crucial leap forward in this domain, offering the flexibility, granularity, and scalability required to secure the dynamic and data-rich world of modern drone operations. By moving beyond static roles to dynamic attributes, ABAC empowers organizations to manage access with unprecedented precision, ensuring both operational efficiency and robust security for their advanced aerial assets.