
The Foundation of Authenticity in Digital Communications
In the intricate realm of digital security, where data integrity and authentication are paramount, a critical mechanism known as a Hash-based Message Authentication Code (HMAC) plays a vital role. While not directly a component of drone hardware or flight software in the way a GPS module or an obstacle avoidance sensor is, the principles behind HMAC are deeply relevant to the secure operation and data transmission of unmanned aerial vehicles (UAVs) and the broader field of flight technology. Understanding HMAC is crucial for appreciating the robust security measures that underpin modern connected systems, including those that control and communicate with drones.

At its core, an HMAC is a specific type of cryptographic checksum used to verify both the data integrity and the authenticity of a message. In simpler terms, it ensures that a message has not been tampered with during transit and that it genuinely originates from the claimed sender. This is achieved by combining a secret key with the message itself and then applying a cryptographic hash function. The resulting HMAC value is then appended to the message. When the recipient receives the message, they can perform the same HMAC calculation using the shared secret key and compare the result with the received HMAC. If they match, the message is considered authentic and unaltered.
The significance of HMAC extends far beyond simple error checking. Unlike a standard hash function, which can only verify integrity (whether the data has changed), HMAC incorporates a secret key, making it resistant to malicious modification. An attacker who intercepts a message and its HMAC cannot forge a new, valid HMAC for a modified message without knowing the secret key. This makes HMAC an indispensable tool for secure communication protocols, authentication schemes, and data validation, all of which are essential for the reliable and secure operation of flight technology, including drone systems.
Cryptographic Hashing: The Building Blocks of HMAC
Before delving deeper into HMAC, it’s important to grasp the concept of cryptographic hash functions. These functions are mathematical algorithms that take an input (any size of data) and produce a fixed-size string of characters, known as a hash value or digest. Key properties of cryptographic hash functions include:
- Deterministic: The same input will always produce the same output hash.
- Fast Computation: It’s quick to compute the hash value for any given message.
- Pre-image Resistance: It is computationally infeasible to find the original message given only its hash value. This is often referred to as “one-way” property.
- Second Pre-image Resistance: Given an original message and its hash, it is computationally infeasible to find a different message that produces the same hash.
- Collision Resistance: It is computationally infeasible to find two different messages that produce the same hash value.
Commonly used cryptographic hash functions include SHA-256 (Secure Hash Algorithm 256-bit), SHA-512, and MD5 (though MD5 is now considered cryptographically broken and should not be used for security-sensitive applications). These functions are the bedrock upon which HMAC is built, providing the underlying mechanism for generating unique “fingerprints” of data.
The HMAC Construction: Combining Secrecy with Hashing
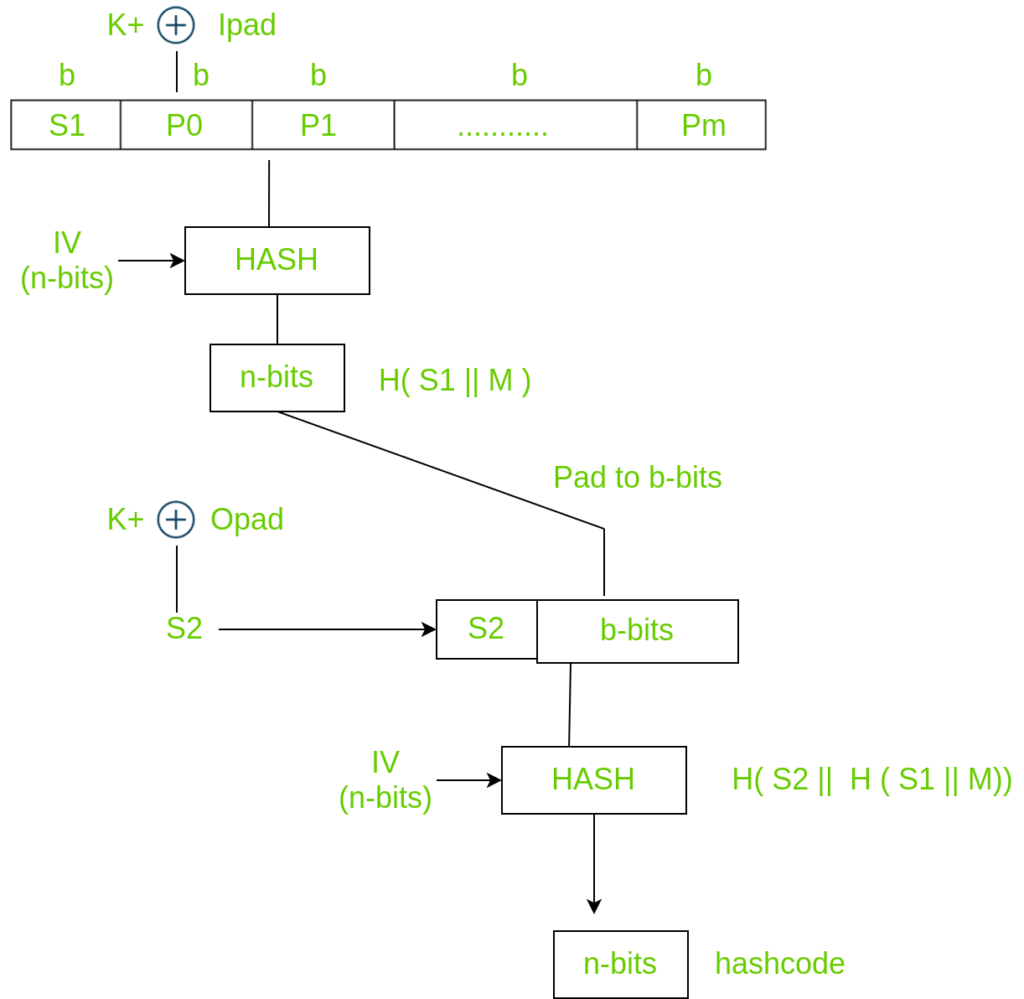
The HMAC construction, as defined in RFC 2104, is relatively straightforward yet remarkably effective. It involves two rounds of hashing. Let’s assume we are using a hash function H, a secret key K, and the message M.
The process involves:
- Key Preparation: The secret key
Kis processed. IfKis longer than the block size of the hash function, it is first hashed to produce a key of the appropriate size. IfKis shorter than the block size, it is padded with zeros to match the block size. - Inner Hash: The key
Kis XORed with a fixed inner padding string,ipad(0x36 repeated for the block size). This result is then concatenated with the messageM, and the hash functionHis applied to this combined input:H( (K XOR ipad) || M ). - Outer Hash: The key
Kis XORed with a fixed outer padding string,opad(0x5c repeated for the block size). This result is then concatenated with the output of the inner hash, and the hash functionHis applied again:H( (K XOR opad) || H( (K XOR ipad) || M ) ).
The final output of this outer hash is the HMAC value.
The use of two rounds of hashing with distinct padding values is a security measure. It prevents certain attacks that could be mounted against a single-round hash construction. For instance, if an attacker knew the hash function and the message, they could try to extend the hash by appending new data. The HMAC construction makes such “length extension attacks” significantly more difficult.
Why HMAC is Essential for Flight Technology and Drones
While you won’t find “HMAC module” listed as a standard component on a drone’s bill of materials, its principles are foundational to the secure operation of systems that control and communicate with drones. Consider the following scenarios:
Secure Command and Control (C2) Links
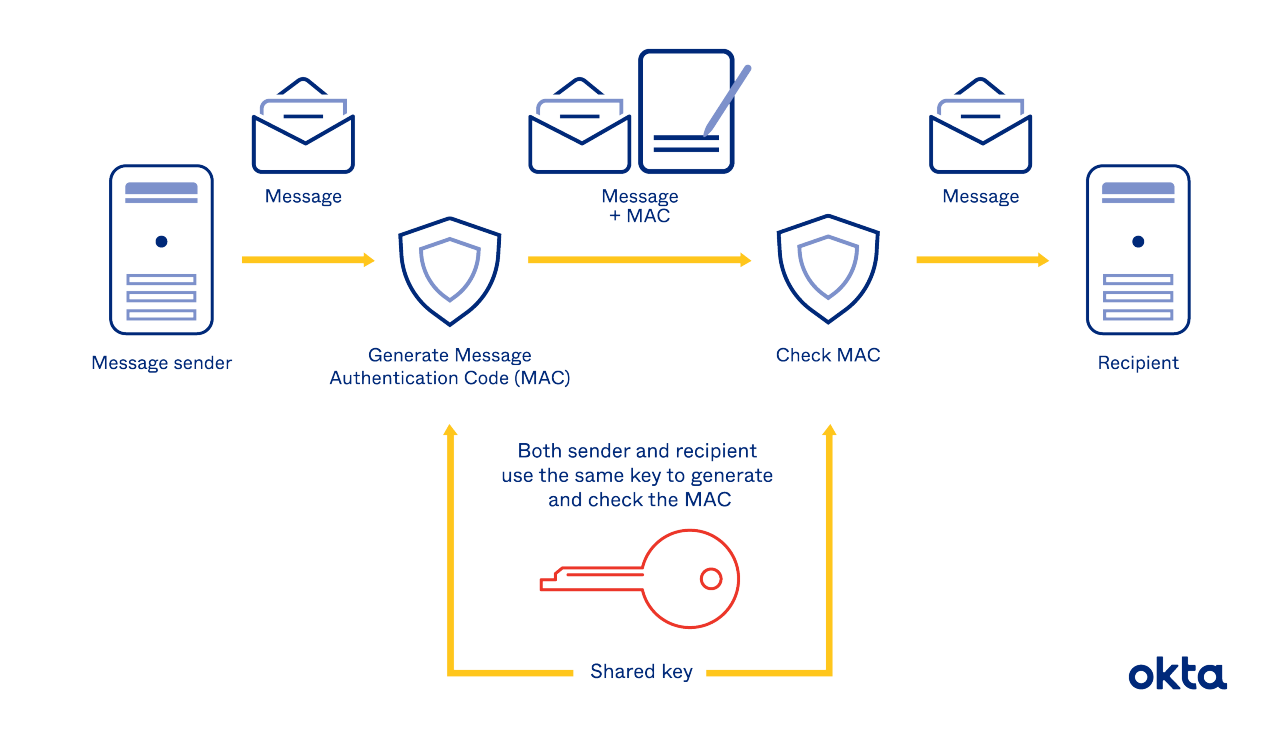
Drones, especially those used for commercial, industrial, or military purposes, require secure command and control (C2) links. Operators need to be absolutely certain that the commands they send – such as “takeoff,” “land,” “go to coordinates,” or “return to home” – are not intercepted, altered, or spoofed by malicious actors.
- Data Integrity: An HMAC can be used to ensure that a command intended for the drone arrives without modification. If a hacker tries to change a “land” command to something else, the HMAC verification on the drone will fail, and the command will be rejected.
- Authenticity: The HMAC, generated using a secret key shared between the ground station and the drone (or a central command center), verifies that the command truly originated from the authorized controller. This prevents an unauthorized party from sending spurious commands and potentially causing the drone to crash or act erratically.
Flight Data Logging and Telemetry
During a flight, drones generate vast amounts of telemetry data, including GPS coordinates, altitude, speed, battery status, sensor readings, and video streams. This data is often logged for post-flight analysis, regulatory compliance, or to feed into AI-driven flight control systems.
- Log Tampering Prevention: If sensitive flight data is transmitted or stored, an HMAC can be applied to ensure its integrity and authenticity. This is crucial if the data might be used in legal proceedings or for critical decision-making processes.
- Secure Firmware Updates: When a drone receives a firmware update, it’s imperative that the update is from a legitimate source and has not been corrupted. HMAC can be used to authenticate the source and verify the integrity of the firmware file before it’s installed on the drone’s control systems, preventing the installation of malicious software.
Communication with Ground Control Stations and Network Infrastructure
Modern flight technology often involves communication with sophisticated ground control stations (GCS), air traffic management systems, or cloud-based platforms. These communications need to be secured.
- API Authentication: When a drone’s data is accessed via an API, or when control commands are issued through a web interface, HMAC can be used to authenticate the request. The client application generates an HMAC of the request parameters using a shared secret, and the server verifies it.
- Secure Data Exchange: In distributed systems where multiple entities communicate with each other (e.g., a fleet of drones coordinating their flight paths), HMAC ensures that messages exchanged between them are genuine and have not been tampered with.
Securing GPS and Navigation Data
While GPS itself is a broadcast signal and not inherently secure against spoofing, the data processed from GPS receivers and other navigation sensors can be protected using HMAC. When this data is relayed or logged, an HMAC can be appended to guarantee its integrity. This is particularly important for autonomous navigation systems where falsified navigation data could lead to catastrophic failures.
HMAC vs. Other Security Mechanisms
It’s important to distinguish HMAC from other related security concepts:
- Symmetric Encryption: While symmetric encryption (like AES) scrambles data to make it unreadable without a key, it doesn’t inherently provide authentication. An encrypted message could still be tampered with, or an attacker could replay a message at a later time (replay attack). HMAC, on the other hand, is not about confidentiality but about authentication and integrity.
- Digital Signatures: Digital signatures typically use asymmetric cryptography (public/private key pairs) for authentication and non-repudiation. HMAC uses symmetric keys and is generally faster, making it more suitable for high-throughput applications where speed is critical and non-repudiation (the ability to prove someone sent a message) is not always the primary concern. In many drone C2 links, where a dedicated secure channel is established between a ground station and a specific drone, shared secret keys and HMAC are often more practical than complex public-key infrastructures.
- Simple Hashing (e.g., SHA-256): As mentioned, a standard hash function only verifies data integrity. If a message is sent with its SHA-256 hash, an attacker could potentially intercept the message, modify it, and then calculate a new SHA-256 hash for the modified message, making it appear legitimate to a naive verification process. HMAC’s inclusion of a secret key prevents this.
Implementing HMAC in Flight Technology Systems
Implementing HMAC in systems related to flight technology requires careful consideration:
- Key Management: The most critical aspect of any HMAC implementation is the secure management of the shared secret keys. These keys must be generated securely, stored safely, and distributed to authorized entities without compromise. For drone operations, this might involve pre-shared keys programmed onto both the drone and the GCS, or dynamically generated keys managed by a secure server.
- Choice of Hash Function: Selecting a strong, modern cryptographic hash function (e.g., SHA-256 or SHA-512) is essential. Older, weakened algorithms should be avoided.
- Protocol Design: HMAC should be integrated into the communication protocols used between the drone and its controllers, or between different components of a flight system. This ensures that every critical message is authenticated.
- Resource Constraints: Drones, especially smaller ones, may have limited processing power and battery life. While HMAC is generally efficient, the choice of hash function and the frequency of HMAC calculations should be balanced against these constraints.
Conclusion: The Unseen Guardian of Secure Flight
In the ever-expanding landscape of unmanned aerial vehicles and advanced flight technology, security is no longer an afterthought but a fundamental requirement. While HMAC might operate behind the scenes, its role in ensuring data authenticity and integrity is indispensable. It acts as an unseen guardian, protecting command links, securing flight data, and guaranteeing that the digital conversations powering our aerial adventures are trustworthy. As flight technology becomes more sophisticated and integrated into critical infrastructure, the understanding and application of robust authentication mechanisms like HMAC will only grow in importance, ensuring that these powerful tools can be used safely and reliably.