
Zero-day vulnerabilities, often referred to as “zero-days,” represent a critical and often terrifying aspect of cybersecurity. The term itself evokes a sense of immediate and unaddressed danger, and for good reason. In the realm of technology, and particularly within the sophisticated ecosystems that underpin modern digital infrastructure, a zero-day signifies a security flaw that is unknown to the vendor or developer responsible for the affected software, hardware, or system. This lack of awareness is precisely what makes them so potent.
The “zero” in zero-day refers to the number of days the vendor has had to fix the vulnerability. Once a zero-day exploit is discovered and weaponized, an attacker can leverage it before any patches or countermeasures are available. This effectively leaves systems exposed and vulnerable for an unpredictable period, creating a window of opportunity for malicious actors to compromise data, disrupt services, or gain unauthorized access.

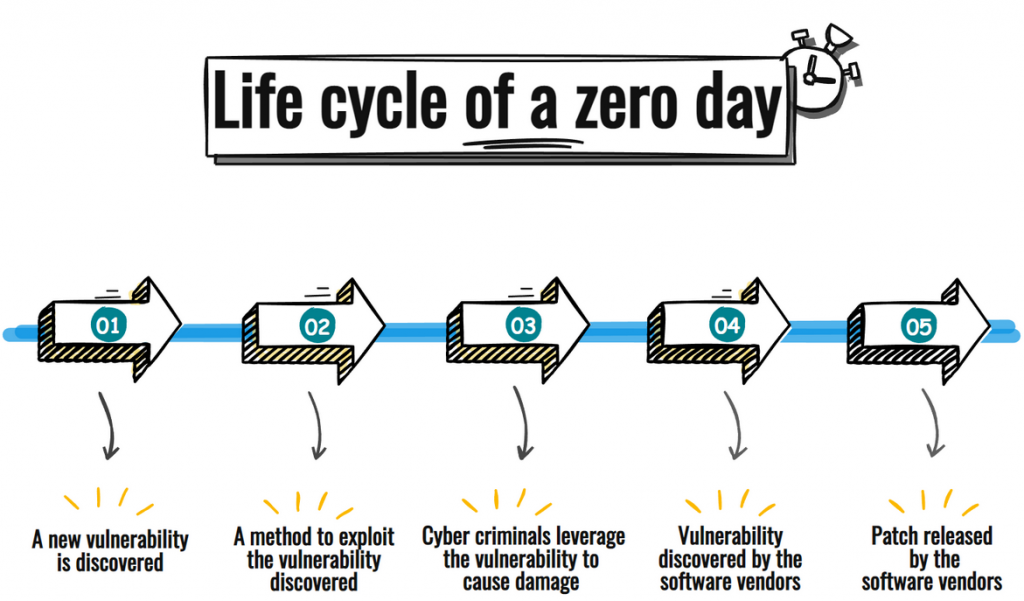
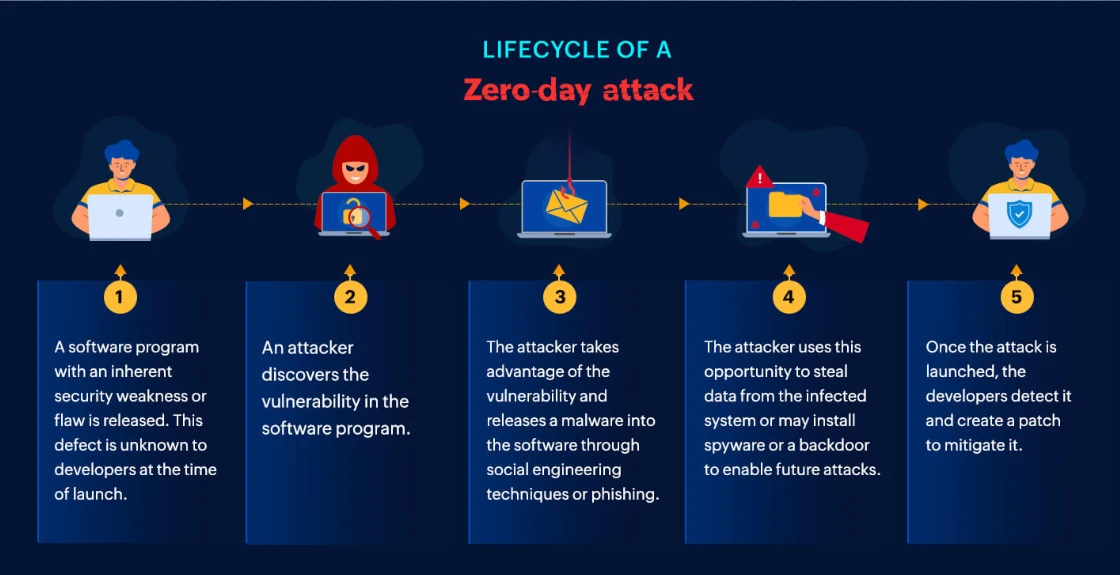
The lifecycle of a zero-day typically begins with its discovery. This can happen through various channels: meticulous security research by ethical hackers, accidental discovery by developers, or, most concerningly, through exploitation by malicious entities. Once a vulnerability is found, it can be kept secret for a variety of reasons – to be sold on the black market, used for espionage, or deployed in targeted attacks. When the first known “exploit” – a piece of code or a technique that leverages the vulnerability – appears in the wild, the clock starts ticking. The vendor, alerted to the problem either through the exploit’s activity or through responsible disclosure by researchers, now has “zero days” to prepare a fix.
The Anatomy of a Zero-Day Attack
Understanding how zero-day attacks unfold is crucial for appreciating their threat. The process generally involves several distinct phases, each building upon the last to achieve the attacker’s objective.
Discovery and Weaponization
The genesis of a zero-day lies in the identification of a previously unknown security weakness. This could be a coding error, a design flaw, or an oversight in the implementation of a security protocol. Unlike known vulnerabilities, which are documented in databases like CVE (Common Vulnerabilities and Exposures) and have associated patches, zero-days exist in the shadows.
Once discovered, the vulnerability is “weaponized.” This means that attackers develop specific tools, scripts, or methodologies to exploit it. This weaponization phase is critical because a raw vulnerability is often not directly usable for an attack; it requires a specific exploit to trigger its effect. The sophistication of this weaponization can vary greatly, from simple script kiddie exploits to highly advanced, custom-built attack vectors.
Exploitation and Initial Compromise
The exploitation phase is where the weaponized zero-day is deployed against its target. This can occur through a multitude of vectors, depending on the nature of the vulnerability and the intended target. Common methods include:
- Malicious Websites and Downloads: Users may be tricked into visiting a compromised website that automatically attempts to exploit the zero-day in their browser or other software. Alternatively, they might download a seemingly legitimate file that contains the exploit.
- Email Attachments and Phishing: Phishing emails are a perennial favorite for delivering malware. A zero-day exploit can be embedded in an attachment (like a PDF or document) or a link within an email, waiting to be triggered when the user opens it or clicks the link.
- Network Exploits: Some zero-days can be exploited remotely over a network, targeting vulnerable services or applications running on servers or individual devices without any user interaction. This is particularly dangerous for large-scale, indiscriminate attacks.
- Supply Chain Attacks: In this more sophisticated approach, attackers compromise a trusted software vendor or service provider. When legitimate software updates or products are distributed, they contain the zero-day exploit, infecting all downstream users.
The initial compromise often involves gaining a foothold within the target system. This could mean executing arbitrary code, gaining elevated privileges, or establishing a persistent presence.
Post-Exploitation and Objective Achievement
Once the initial compromise is successful, attackers move to the post-exploitation phase. Their objectives here vary widely:
- Data Exfiltration: Stealing sensitive information, such as personal data, financial records, intellectual property, or classified government secrets.
- Lateral Movement: Using the compromised system as a stepping stone to move deeper into the network, seeking out more valuable targets or critical infrastructure.
- Establishing Persistence: Ensuring they maintain access to the system even if it’s rebooted or certain defenses are put in place. This might involve installing backdoors or rootkits.
- Disruption of Services: Causing denial-of-service (DoS) or distributed denial-of-service (DDoS) attacks to cripple operations.
- Espionage: Conducting surveillance, monitoring communications, or gathering intelligence over an extended period.
- Ransomware Deployment: Encrypting data and demanding a ransom for its decryption.
The impact of a zero-day attack can range from minor inconvenience to catastrophic financial loss, reputational damage, and even national security breaches.
The High Stakes of Zero-Day Exploits
The value of zero-day exploits is immense, driven by their efficacy and the scarcity of defenses. This has created a complex and often ethically ambiguous market for these vulnerabilities.
The Zero-Day Marketplace
A significant part of the zero-day ecosystem involves their commercialization. Governments, intelligence agencies, and cybersecurity firms often purchase zero-day exploits for defensive purposes (to understand threats and develop countermeasures) or for offensive operations (espionage, cyber warfare). This legitimate market, while often shrouded in secrecy, coexists with a clandestine black market where exploits are sold to criminal organizations and state-sponsored hacking groups.
The price of a zero-day can vary dramatically, influenced by factors such as:
- Target Software/Hardware: Exploits targeting widely used and critical systems (like operating systems, popular browsers, or enterprise software) command higher prices.
- Severity of the Vulnerability: How much damage can the exploit cause? Can it lead to full system compromise or data theft?
- Reliability and Stability: A consistently working exploit is more valuable than one that is prone to failure.
- Discovery Method: Exploits discovered through sophisticated reverse engineering or novel research may fetch higher prices.
Some estimates place the cost of high-value zero-days in the millions of dollars, making them a lucrative commodity for those who can find and exploit them.
Ethical Considerations and Responsible Disclosure
The discovery of a zero-day presents a significant ethical dilemma for researchers. They face a choice:
- Responsible Disclosure: Informing the vendor about the vulnerability and providing them with a reasonable timeframe to develop and deploy a patch before making the vulnerability public. This is the preferred approach from a public safety perspective.
- Selling to Third Parties: Disclosing the vulnerability to governments, intelligence agencies, or private companies in exchange for payment.
- Keeping it Secret: Holding onto the vulnerability for personal use or future exploitation.
- Public Disclosure (Zero-Day Exploit): Releasing details or the exploit code publicly, which immediately puts users at risk.
Organizations like the Electronic Frontier Foundation (EFF) and the Carnegie Endowment for International Peace have been vocal advocates for responsible disclosure practices, emphasizing the need to balance security researchers’ rights with the public’s right to secure systems. The debate over the ethics of the zero-day market is ongoing, with proponents arguing for its role in national defense and cybersecurity research, while critics highlight the potential for abuse and the increased risk to ordinary users.
Defending Against the Unknown
Given that zero-days, by definition, lack readily available fixes, traditional signature-based detection methods are often ineffective. Defending against them requires a more proactive and layered approach.
Proactive Security Measures
Several strategies can bolster defenses against zero-day threats:
- Vulnerability Management and Patching: While zero-days bypass immediate patching, a robust patch management program for known vulnerabilities is essential. The less surface area of known weaknesses you have, the harder it is for attackers to find and exploit the unknown ones.
- Behavioral Analysis and Anomaly Detection: Instead of looking for known malicious code, these systems monitor system behavior for deviations from normal patterns. If a piece of software starts performing unusual actions (e.g., accessing sensitive system files, initiating network connections it shouldn’t), it can trigger an alert, even if the underlying exploit is unknown.
- Endpoint Detection and Response (EDR): EDR solutions provide advanced threat detection, investigation, and response capabilities for endpoints (laptops, servers, etc.). They continuously monitor endpoint activity, collect data, and use techniques like threat hunting and behavioral analysis to identify and neutralize threats, including zero-days.
- Network Segmentation and Least Privilege: Isolating critical systems and limiting user and application privileges can contain the damage if a zero-day exploit successfully compromises one part of the network.
- Application Sandboxing: Running applications in isolated environments (sandboxes) can prevent them from affecting the rest of the system if they are compromised by a zero-day exploit.
- Security Awareness Training: Educating users about phishing, social engineering, and safe browsing habits remains a vital defense, as many zero-day exploits rely on human error to be delivered.
- Threat Intelligence: Subscribing to and acting upon threat intelligence feeds can provide early warnings about emerging attack trends and potential zero-day threats being discussed or seen in the wild, even before a specific exploit is identified.
The Role of the Vendor and the Security Community
Ultimately, the most effective defense against zero-days is the development and deployment of patches by the software or hardware vendor. This highlights the critical importance of timely disclosure, rapid development, and efficient distribution of security updates. The security community, through bug bounty programs, responsible disclosure initiatives, and collaborative research, plays an indispensable role in identifying these vulnerabilities and pushing vendors to address them.
The constant cat-and-mouse game between attackers and defenders means that zero-days will likely remain a persistent and evolving threat. A comprehensive and adaptive security posture, combining technical controls with human vigilance and a commitment to prompt vulnerability remediation, is the most robust strategy for mitigating their impact.