
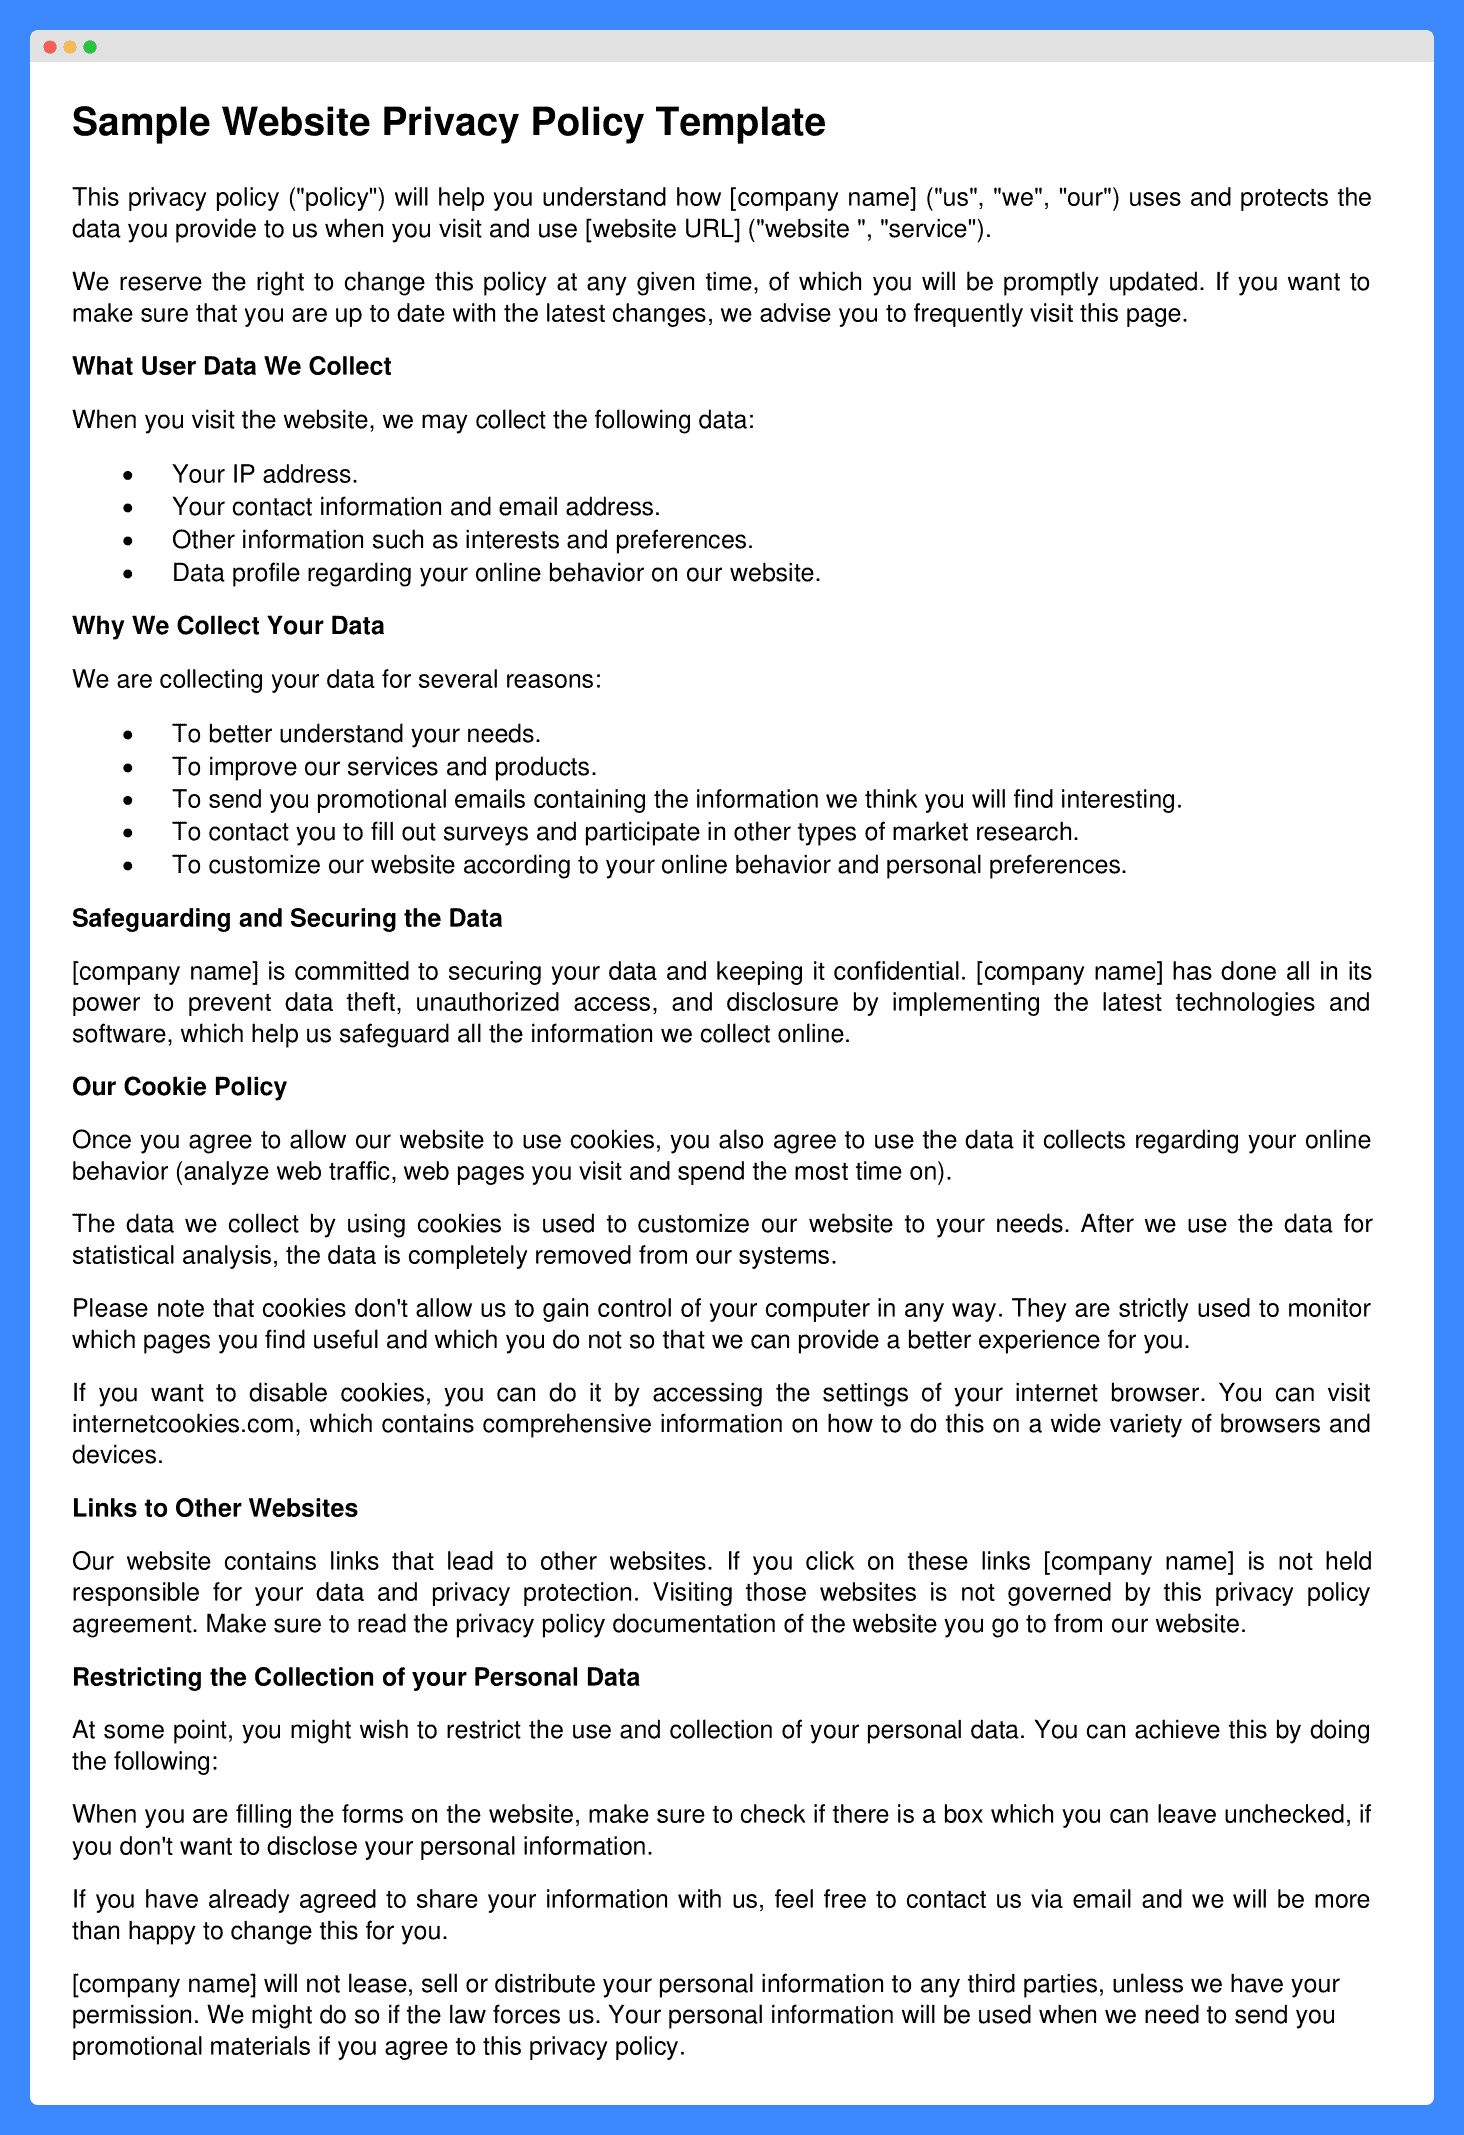
A website privacy policy is a fundamental legal document outlining how an organization collects, uses, stores, shares, and protects the personal data of its website visitors and users. In an increasingly data-driven world, particularly within the advanced realms of Tech & Innovation like AI follow mode, autonomous flight, mapping, and remote sensing, a comprehensive and transparent privacy policy is not merely a legal obligation but a cornerstone of trust, ethical operation, and sustained business success. For companies at the forefront of drone technology, where vast amounts of sensitive operational and personal data are generated and processed, understanding and meticulously crafting this policy is paramount. It serves as a public commitment to data stewardship, detailing the lifecycle of information from collection to eventual deletion, and empowering users with knowledge about their digital rights.
The Imperative of Privacy Policies in the Tech & Innovation Landscape
In the rapidly evolving Tech & Innovation sector, especially for entities pioneering drone-based solutions, data is both the fuel and the product. Systems leveraging AI for autonomous flight, sophisticated mapping algorithms, and advanced remote sensing capabilities rely on continuous data input and processing. This intricate relationship between technology and data elevates the privacy policy from a mere compliance formality to a strategic asset, critical for navigating complex data ecosystems and building enduring user trust.
Data Ecosystems in Advanced Drone Technologies
The development and deployment of advanced drone technologies inherently involve the creation and handling of diverse data sets. AI follow mode systems capture visual and positional data to track subjects. Autonomous flight platforms log extensive telemetry, flight paths, sensor readings, and environmental data for navigation and performance optimization. Mapping and remote sensing services process geospatial information, often including high-resolution imagery, LiDAR scans, and thermal data, which can sometimes inadvertently capture personally identifiable information (PII) or sensitive details about private property.
A robust privacy policy clarifies how this complex web of operational data (e.g., flight logs, sensor outputs, object identification data) intertwines with user data (e.g., account details, subscription information, communication logs). It addresses the nuances of data aggregation, anonymization practices, and the differentiation between data essential for service delivery and data utilized for system improvement. Without such clarity, drone tech companies risk legal challenges, reputational damage, and a fundamental breakdown in the confidence of their clients and end-users regarding the secure and ethical handling of their information.
Building User Trust in Data-Intensive Applications
In an era marked by heightened awareness of data breaches and privacy infringements, transparency is a non-negotiable currency. For businesses innovating with AI, autonomous systems, and remote sensing, a clearly articulated privacy policy serves as a vital assurance mechanism. It communicates to clients, drone operators, and the public that their flight mission parameters, collected sensor data, and personal account information are managed with integrity, security, and respect for privacy rights.
Consider a professional utilizing a drone for agricultural mapping or infrastructure inspection. Their data might include specific farm layouts, crop health metrics, or critical infrastructure vulnerabilities. These are highly sensitive datasets, and the company providing the drone service must clearly define how this information is protected, who has access, and under what circumstances it might be processed or shared. A strong, transparent privacy policy fosters confidence, encouraging wider adoption of these transformative technologies. Conversely, any perceived ambiguity or lack of transparency can erode trust, impede market penetration, and hinder the growth of innovative drone services that rely heavily on data exchange.
Core Elements of a Drone Tech Company’s Privacy Policy
A comprehensive privacy policy for a company operating in the Tech & Innovation sphere, particularly with drone technologies, must meticulously detail several key aspects of data handling. These elements collectively paint a clear picture of an organization’s commitment to data privacy and regulatory compliance.
Defining Data Collection Practices
The foundation of any privacy policy lies in an explicit articulation of what data is collected. For drone tech companies, this extends beyond standard website analytics to encompass data generated directly by their advanced systems:
- Personal Identifiable Information (PII): This includes direct identifiers like names, email addresses, phone numbers, payment information (for platform subscriptions, hardware purchases), and user credentials.
- Operational Data: Unique to drone tech, this covers flight telemetry (altitude, speed, heading), mission parameters (flight plans, no-fly zones), sensor data (high-resolution imagery, video streams, LiDAR point clouds, thermal readings), GPS coordinates of flight operations, and object detection logs.
- Usage Data: Information about how users interact with the company’s website, software platforms, and mobile applications. This includes feature usage, session duration, device information (IP addresses, browser type, operating system), and error logs crucial for system improvement.
- Third-Party Data: Data received from partners or third-party integrations (e.g., weather services, ground control software, cloud storage providers) that contribute to the drone’s operational environment or service delivery.
The policy must also specify how this data is collected—through direct user input, automated processes (cookies, web beacons, embedded trackers), API integrations with drone hardware or software, and passive data capture during drone operations.
Purpose and Utilization of Collected Data
Equally critical is a clear explanation of why the collected data is used. For drone tech, the purposes are diverse and often deeply integrated with the functionality of the innovations themselves:
- Service Delivery: To facilitate autonomous missions, execute predefined flight paths, provide real-time mapping solutions, enable AI-powered object recognition, and deliver requested remote sensing outputs.
- Product Improvement and Innovation: Data is invaluable for refining AI algorithms, enhancing the precision of autonomous navigation systems, improving flight stability, developing new features (e.g., more sophisticated follow modes), and optimizing the user experience across platforms. This often involves anonymized or aggregated data for training machine learning models.
- Security, Safety, and Compliance: To detect unauthorized access, prevent fraud, ensure adherence to aviation regulations (e.g., logging flight data for auditing), investigate incidents or accidents, and monitor system health.
- Communication and Support: To send service updates, provide technical support, respond to inquiries, and, with explicit consent, offer marketing communications about new products or features.
- Legal and Regulatory Obligations: To comply with applicable laws, government requests, and enforce terms of service.
Data Sharing, Disclosure, and Third-Party Relationships
Transparency about data sharing practices is paramount. A privacy policy must detail under what circumstances and with whom user and operational data might be shared:
- Service Providers: Sharing data with trusted third-party vendors for essential operational functions, such as cloud hosting (e.g., AWS, Azure, Google Cloud for data storage and processing), payment processors, analytics platforms, and logistics partners (for hardware distribution).
- Business Partners: Collaboration on joint ventures, large-scale mapping projects, or data aggregation initiatives. Such sharing should typically involve strict data processing agreements and, wherever possible, utilize anonymized or aggregated data.
- Legal Obligations: Disclosing data when mandated by law, government authorities, or court orders, such as during investigations into drone-related incidents or for national security purposes.
- Business Transfers: In the event of a merger, acquisition, or asset sale, data may be transferred to the acquiring entity, with appropriate safeguards and user notification.
The policy should also address international data transfers, clarifying how data belonging to users in one jurisdiction (e.g., EU citizens) is handled when processed or stored in another country, emphasizing adherence to relevant cross-border data transfer mechanisms.
Navigating the Complex Regulatory Landscape for Drone Tech Data
The global nature of technology, coupled with the unique operational aspects of drone technology, subjects companies in this sector to a multifaceted regulatory environment. A robust privacy policy must demonstrate an understanding of and commitment to compliance with both general data protection laws and specific industry standards.
Global Privacy Frameworks (GDPR, CCPA, etc.)
Drone tech companies, particularly those with a global footprint or those serving international clients, must contend with a patchwork of stringent data privacy regulations:
- General Data Protection Regulation (GDPR): As a comprehensive law protecting EU citizens’ data, GDPR has extraterritorial reach. Any drone tech company processing data from individuals in the EU (even if the company isn’t based there) must comply. This entails strict requirements for lawful basis for processing, explicit consent, data subject rights (e.g., right to access, rectification, erasure, portability), data protection impact assessments (DPIAs) for high-risk processing, and mandatory breach notifications.
- California Consumer Privacy Act (CCPA) / California Privacy Rights Act (CPRA): Similar to GDPR, these US state laws grant California residents specific rights regarding their personal information, including rights to know, delete, and opt-out of sales or sharing.
- Other National and State Laws: Numerous countries (e.g., Canada’s PIPEDA, Brazil’s LGPD, Australia’s Privacy Act) and US states are implementing their own data privacy regulations. A comprehensive privacy policy must reflect an awareness of these diverse requirements and outline how the company seeks to align with them, potentially by adopting the highest common denominator of protection.
Navigating these frameworks requires careful legal counsel and a commitment to continuous compliance, particularly as new regulations emerge and existing ones evolve.
Sector-Specific Regulations and Industry Standards
Beyond general privacy laws, drone operations introduce unique regulatory layers, often involving aviation authorities and industry bodies:
- Aviation Regulations: Agencies like the FAA (US) or EASA (Europe) mandate specific data logging and retention requirements for safety, auditing, and incident investigation purposes. A drone tech company’s privacy policy needs to acknowledge how these requirements intersect with individual privacy rights, particularly concerning the retention of flight data.
- Ethical AI Guidelines: As AI becomes more integral to autonomous drones, guidelines on ethical AI development (e.g., fairness, accountability, transparency, bias mitigation) are emerging. While not strictly privacy laws, adherence to these principles often necessitates robust data governance and privacy by design, which should be reflected in the policy’s underlying philosophy.
- Industry Best Practices and Certifications: Adopting international standards like ISO 27001 (Information Security Management) or SOC 2 (Service Organization Control 2) demonstrates a commitment to robust data security and privacy practices. While not always legally mandated, these certifications can enhance credibility and trust, particularly when dealing with sensitive client data or government contracts.
The privacy policy should implicitly or explicitly acknowledge these sector-specific nuances, demonstrating a holistic approach to data governance that spans legal, operational, and ethical dimensions.
Fostering Ethical Innovation and Competitive Advantage through Privacy
Beyond mere compliance, a well-crafted privacy policy serves as a powerful instrument for ethical innovation and a significant competitive differentiator in the dynamic Tech & Innovation sector, especially for drone-based solutions.
Ethical AI and Data Stewardship
The development of AI for autonomous flight, mapping, and remote sensing carries significant ethical implications, particularly regarding data. Misuse of data, whether through biased training datasets leading to discriminatory AI outcomes or unauthorized surveillance capabilities, can severely damage public trust and provoke regulatory backlash. A robust privacy policy reflects a company’s commitment to responsible AI development and ethical data stewardship. It signals that the organization prioritizes user rights and societal welfare alongside technological advancement. By clearly outlining data minimization, anonymization, and secure processing practices, a company demonstrates its dedication to ensuring that its innovations in mapping precision, autonomous capabilities, and remote sensing benefit society without infringing on individual privacy or societal norms. This ethical stance is crucial for sustainable growth and for securing the social license required for widespread adoption of cutting-edge drone technologies.
Competitive Edge and Brand Reputation
In a fiercely competitive market, a transparent and comprehensive privacy policy can be a powerful differentiator. Companies that demonstrably prioritize user privacy and proactively communicate their data practices are more likely to attract and retain customers, partners, and top-tier talent. Clients seeking drone services for sensitive applications—such as infrastructure inspection, environmental monitoring, or precision agriculture—will gravitate towards providers who offer clear assurances regarding data security and privacy. A strong privacy posture builds brand reputation, positioning the company as a trustworthy and responsible innovator.
Conversely, privacy missteps, data breaches, or a lack of transparency can lead to severe reputational damage, significant financial penalties from regulatory bodies, and a considerable loss of market share. For startups and established innovators in the drone tech space, where public perception and regulatory scrutiny are high, protecting customer data and upholding privacy standards are not just legal requirements but essential components of a long-term business strategy.
Continuous Adaptation and Future-Proofing
The landscape of technology, innovation, and data privacy is in constant flux. Drone technology itself is rapidly evolving, with advancements in edge AI, swarm intelligence, more sophisticated sensors, and new use cases emerging regularly. Simultaneously, data privacy regulations are becoming more stringent and globally interconnected. Therefore, a privacy policy cannot be a static document. It must be a living instrument, subject to regular review, adaptation, and updates to reflect technological advancements, new data processing activities, and changes in the legal and regulatory environment. This proactive and iterative approach ensures ongoing compliance, reinforces ethical data practices, and builds a resilient foundation for sustainable, responsible growth in the fast-paced world of Tech & Innovation.