
Understanding Rootkits in the Modern Tech Landscape
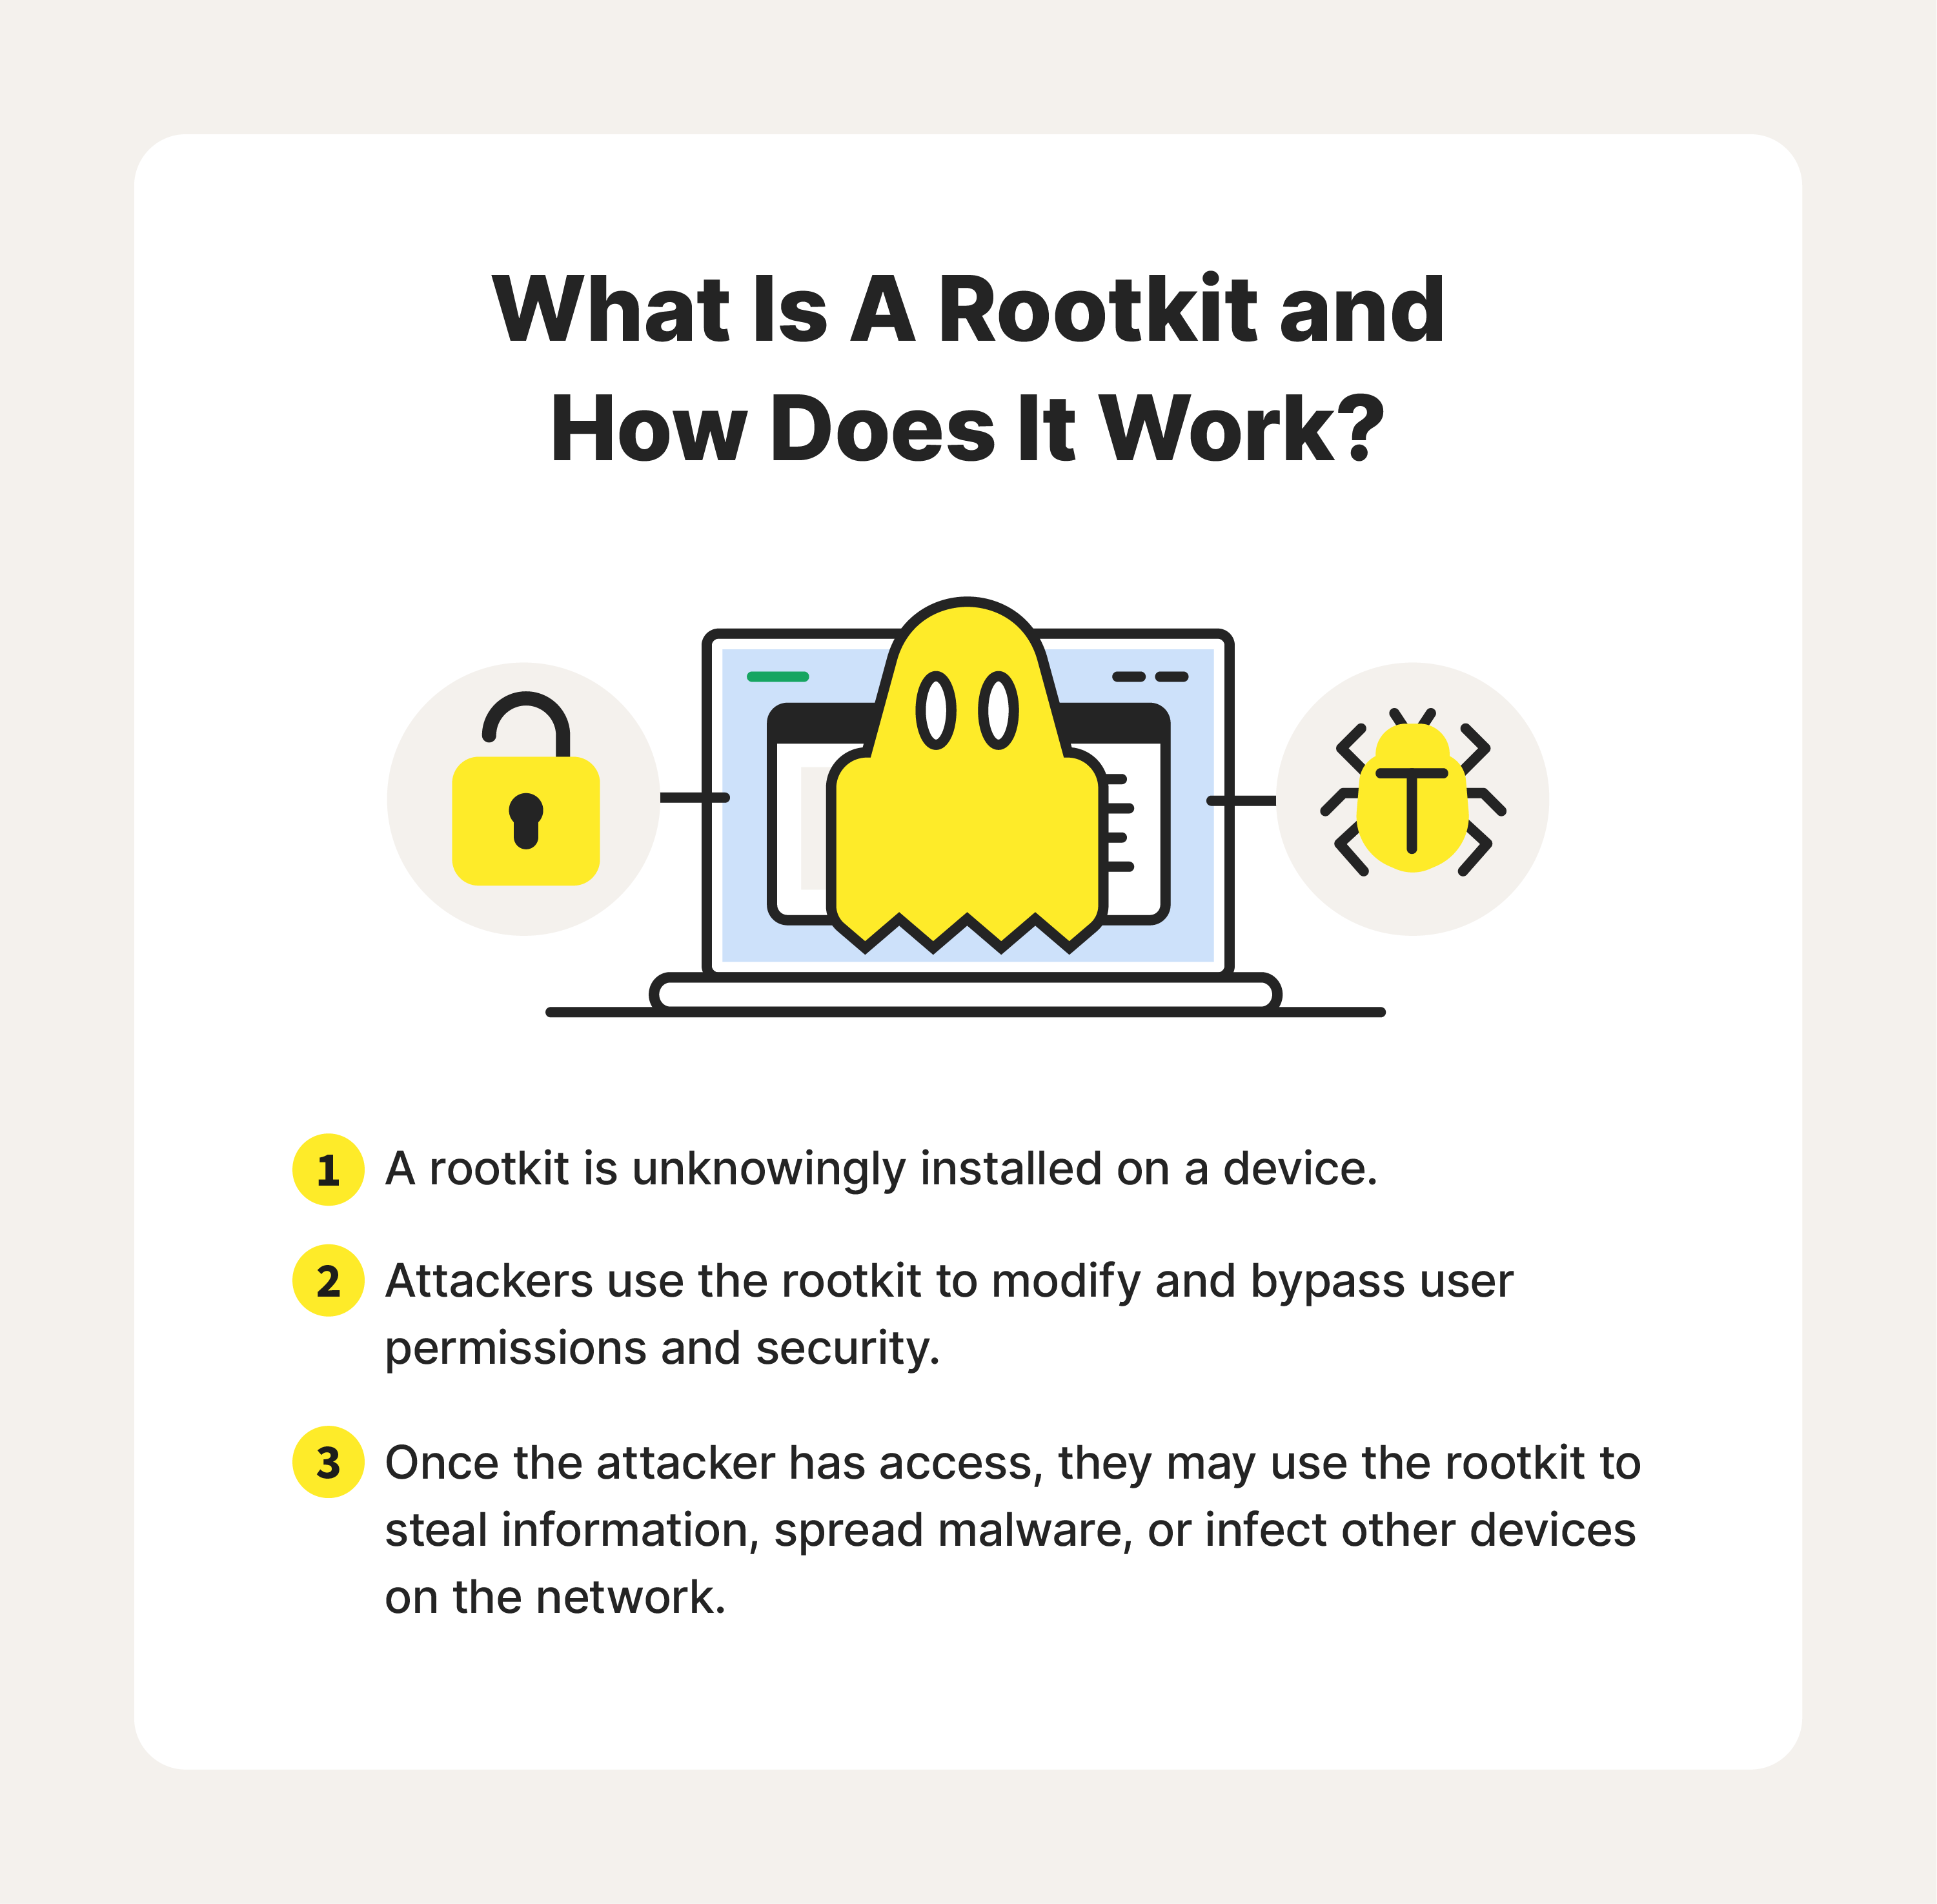
A rootkit, at its core, is a collection of clandestine computer programs designed to enable continuous, privileged access to a computer while actively hiding its presence from administrators and security software. The term “root” refers to the highest level of access on Unix-like operating systems, while “kit” denotes the collection of tools. Historically, rootkits have been a persistent threat in traditional computing environments, allowing malicious actors to maintain control over compromised systems, exfiltrate data, and launch further attacks with impunity. They achieve this by manipulating operating system functions, often at a very low level, to intercept or modify system calls, thereby presenting a ‘clean’ view of the system to security tools while their malicious processes run unimpeded in the background. Their stealth and persistence make them particularly insidious, posing a significant challenge for detection and removal. While their origins lie in desktop and server environments, the principles and dangers of rootkits are increasingly relevant as technology evolves and permeates new domains, including the rapidly expanding field of drone technology.
The Evolving Threat to Advanced Drone Systems
The modern drone is far more than just a flying camera; it is a sophisticated, interconnected computing platform. Equipped with powerful processors, intricate operating systems, advanced sensors, and often leveraging artificial intelligence for navigation and data processing, drones represent a new frontier for technological innovation. Consequently, they also represent an attractive target for advanced persistent threats, including rootkits. The unique operational profile of drones – often remote, wirelessly connected, and performing critical functions – makes them particularly vulnerable and, simultaneously, makes a successful rootkit compromise profoundly impactful.
A rootkit could potentially target various layers within a drone’s architecture. At the firmware level, malicious code could be injected into the flight controller, Electronic Speed Controllers (ESCs), or sensor modules. This allows an attacker to manipulate core flight dynamics, sensor readings, or power delivery systems without detection by higher-level software. Onboard computers, especially those managing AI processing for tasks like “AI Follow Mode” or “Autonomous Flight,” run their own operating systems and are susceptible to OS-level rootkits. Such a compromise could alter navigation algorithms, falsify sensor inputs, or completely hijack autonomous decision-making processes. Even ground control stations (GCS) and the communication links between the drone and operator are potential vectors. A compromised GCS could push malicious updates to the drone, or a rootkit on the GCS itself could intercept and modify telemetry or command signals. The allure for malicious actors ranges from intellectual property theft (e.g., proprietary mapping algorithms, remote sensing data) to weaponization or large-scale disruption of critical infrastructure managed by drones.
Vectors of Infection in Drone Technology
The pathways through which rootkits could infiltrate drone systems are manifold, mirroring some traditional IT attack vectors while also introducing drone-specific vulnerabilities.
- Supply Chain Attacks: One of the most insidious methods involves injecting malicious code, potentially a rootkit, into a drone’s hardware or software during its manufacturing process or through third-party components. If a sub-component, such as a camera module, a GPS receiver, or even a specific processing chip, comes pre-infected, the rootkit could establish a foothold before the drone even reaches its end-user. This type of attack is incredibly difficult to detect, as the compromise occurs prior to deployment and often operates at a very low system level, making it challenging for standard security scans.
- Exploitation of Software and Firmware Vulnerabilities: Like any complex software, drone operating systems, flight control firmware, and associated applications can contain bugs or security flaws. Zero-day exploits, or even known vulnerabilities that remain unpatched, can be leveraged by attackers to gain initial access, then deploy a rootkit to establish persistent control and hide their presence. Unsecured update mechanisms for firmware are particularly dangerous, allowing an attacker to push a malicious update disguised as legitimate, thereby implanting a rootkit.
- Compromised Ground Control Stations (GCS) and Connected Devices: The GCS, often a laptop or tablet running specialized software, is the primary interface for drone operation. If a GCS is compromised by a rootkit through conventional means (e.g., phishing, malware downloads), it can serve as a bridge to infect the connected drone. Malicious software on the GCS could intercept data, modify commands sent to the drone, or even directly upload rootkit components to the drone’s onboard systems during data transfer or updates. Similarly, any connected peripherals or network infrastructure that interacts with the drone or GCS could serve as an indirect vector.
- Malicious Payloads Disguised as Legitimate Updates or Apps: With the increasing sophistication of drone software and the availability of app stores for drone control, malicious actors can create seemingly legitimate applications or firmware updates that contain hidden rootkit components. Users, eager to enhance their drone’s capabilities or apply security patches, might unknowingly install these compromised packages, granting the rootkit deep system access.

The Impact of Rootkit Compromise on Drone Operations and Innovation
The successful deployment of a rootkit on a drone system carries far-reaching consequences, impacting everything from data integrity and operational safety to the very trust placed in autonomous technologies.
- Data Exfiltration: Drones are invaluable tools for data collection, from high-resolution “Mapping” and “Remote Sensing” imagery to sensitive infrastructure inspection data, agricultural metrics, and even surveillance feeds. A rootkit can stealthily capture and transmit this critical information to unauthorized parties, leading to intellectual property theft, espionage, or privacy breaches.
- Malicious Control and Hijacking: Perhaps the most alarming impact is the potential for an attacker to gain complete, hidden control over a drone. A rootkit could allow an adversary to alter flight paths, disable safety protocols, manipulate “Autonomous Flight” algorithms, or even weaponize the drone. Imagine a drone programmed for package delivery suddenly rerouted, or an industrial inspection drone causing damage instead of detecting it. The ability to covertly command a drone poses severe risks to public safety, national security, and critical infrastructure.
- Denial of Service (DoS) and Disruption: Beyond direct control, a rootkit can be used to render a drone inoperable. By corrupting essential system files, disabling key components, or creating persistent system instability, an attacker can effectively ground a drone, disrupting critical missions such as search and rescue, disaster response, or commercial logistics. This can result in significant financial losses, operational delays, and potentially life-threatening situations.
- Reputational Damage and Trust Erosion: For manufacturers, operators, and the broader drone industry, a rootkit compromise can be catastrophic. Publicized security breaches erode consumer confidence, damage brand reputation, and can lead to stringent regulatory backlash. The development of advanced features like “AI Follow Mode” and broader acceptance of autonomous systems hinge heavily on trust in their security and reliability. Any major rootkit incident could significantly set back the adoption and innovation in these areas.
Implications for Specific Drone Applications
The consequences vary depending on the drone’s application:
- Commercial Drones: Package delivery drones could be hijacked for theft, inspection drones could be used to sabotage infrastructure, and agricultural drones could spread incorrect data, leading to crop failures.
- Military/Defense Drones: Compromised reconnaissance drones could feed false intelligence, and attack drones could be turned against friendly forces or civilians, with devastating geopolitical implications.
- Public Safety Drones: Drones used by law enforcement or emergency services could have their surveillance feeds intercepted, or be disabled during critical search and rescue operations, jeopardizing human lives.

Innovating Defenses: Countermeasures and Future Security for Drones
The fight against rootkits in drone technology is a critical aspect of “Tech & Innovation.” As attackers develop more sophisticated methods, so too must the defense mechanisms evolve. A multi-layered approach to security, integrating both hardware and software solutions, is essential to protect these increasingly vital assets.
- Secure Boot and Firmware Verification: Implementing secure boot processes ensures that only cryptographically signed and verified firmware can load onto a drone’s flight controller and other critical components. This prevents unauthorized or malicious code, including rootkits, from being injected and executed during startup. Each stage of the boot process must verify the integrity of the next, creating a chain of trust.
- Hardware-level Security: Embedding Trusted Platform Modules (TPMs) or Hardware Security Modules (HSMs) directly into drone hardware can provide a secure root of trust. These dedicated cryptographic processors can securely store keys, verify system integrity, and perform cryptographic operations, making it significantly harder for rootkits to compromise the underlying system’s authenticity and integrity.
- Advanced Anomaly Detection: Leveraging “AI Follow Mode” and other forms of artificial intelligence not just for flight, but for security, is a promising avenue. Machine learning algorithms can be trained to recognize deviations from normal drone behavior – unusual power consumption, unexpected sensor readings, abnormal communication patterns, or sudden changes in flight parameters. These anomalies could indicate the presence of a rootkit attempting to manipulate the drone covertly.
- Regular Security Audits and Penetration Testing: Proactive and continuous security assessments are crucial. Independent security researchers and ethical hackers can be employed to search for vulnerabilities in drone hardware, firmware, software, and communication protocols. Regular penetration testing helps identify weak points before malicious actors can exploit them, ensuring that the defense mechanisms remain robust against evolving threats.
- Supply Chain Security: Mitigating the risk of rootkits introduced during manufacturing requires rigorous vetting of all components and software used in drone production. This involves working with trusted suppliers, implementing strict quality control, and performing regular audits of the supply chain to ensure the integrity of every part of the drone system. Transparency and accountability throughout the development lifecycle are paramount.
- Secure Communication Protocols: All communication between the drone, its ground control station, and any cloud services must be robustly encrypted and authenticated. Secure protocols prevent eavesdropping, data tampering, and command injection, making it more difficult for a rootkit to communicate with its command and control server or for an attacker to hijack the drone via insecure links.
- Sandboxing and Isolation: Critical drone functions, such as flight control, navigation, and payload management, can be isolated within sandboxed environments. This limits the potential damage a rootkit can inflict, even if it manages to compromise one part of the system. By segmenting the drone’s operating environment, a rootkit in one area cannot easily propagate to others, enhancing overall system resilience.
The battle against rootkits in drone technology underscores a broader theme in “Tech & Innovation”: the perpetual arms race between those who seek to exploit vulnerabilities and those who build robust, secure systems. As drones become more integrated into daily life and critical operations, investing in advanced security countermeasures against threats like rootkits is not merely an option, but a fundamental necessity for ensuring their safe, reliable, and trustworthy operation.