
The digital landscape is a vibrant ecosystem of constant innovation, from advanced AI algorithms to autonomous systems that redefine industries. However, this rapid technological advancement is often shadowed by evolving cyber threats. Among the most potent and insidious tools in an attacker’s arsenal is the web shell – a malicious script that provides remote access and control over a web server. Understanding web shells is critical not just for general cybersecurity, but especially for securing the innovative platforms that are shaping the future, including the sophisticated web infrastructure behind drone operations and other emerging technologies.
Understanding the Threat: The Mechanics of a Web Shell
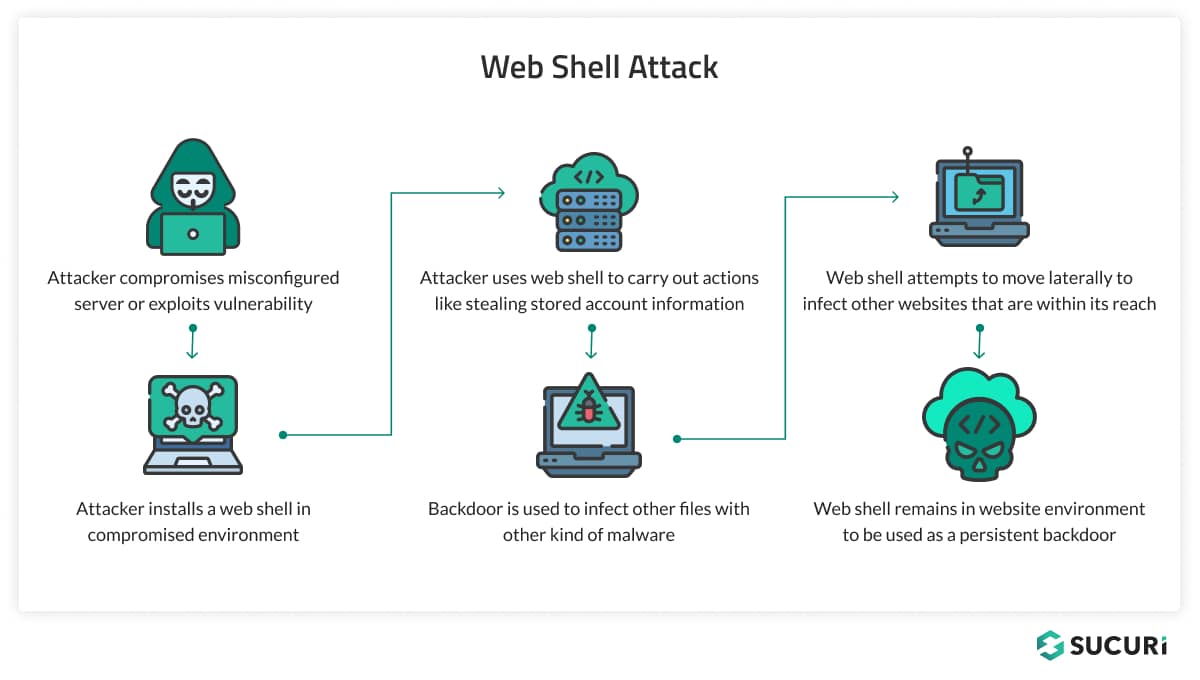
At its core, a web shell is a piece of code, often written in common web scripting languages like PHP, ASP, JSP, or Python, designed to be uploaded to a compromised web server. Once successfully deployed, it grants the attacker a persistent backdoor and a command-line interface to the server, all accessible through a standard web browser. This seemingly innocuous script transforms a legitimate web server into a potent tool for reconnaissance, data exfiltration, system manipulation, and further network penetration.
Definition and Purpose
A web shell’s primary purpose is to provide remote control. Unlike other forms of malware that might require direct executables or complex infection chains, a web shell leverages the server’s existing web services. This means an attacker can manage files, execute system commands, browse directories, and even interact with databases directly from a web interface. The simplicity and potency of this access make web shells highly attractive to malicious actors ranging from opportunistic defacers to state-sponsored advanced persistent threat (APT) groups. The ultimate goal can vary from website defacement to intellectual property theft, or using the compromised server as a pivot point for attacking other systems within the network.
How a Web Shell Gains Foothold
The successful deployment of a web shell typically relies on exploiting a vulnerability in a web application or server configuration. Common vectors include:
- File Upload Vulnerabilities: Many web applications allow users to upload files (e.g., profile pictures, documents). If these applications do not properly validate file types, sizes, or content, an attacker can upload a malicious script disguised as a legitimate file. For instance, renaming a PHP script to “image.php.jpg” might bypass basic extension checks.
- Remote File Inclusion (RFI) and Local File Inclusion (LFI): These vulnerabilities allow an attacker to include remote or local files into the web application. If an RFI vulnerability exists, an attacker can point the application to a web shell hosted on their own server, causing the vulnerable application to download and execute it. LFI can sometimes be leveraged to include log files or other system files containing attacker-controlled data, which then gets interpreted as code.
- SQL Injection (SQLi): In some database configurations, particularly those using MySQL with
outfilepermissions, an attacker can use SQL injection to write a web shell directly to the web server’s filesystem through a database query. - Vulnerable Content Management Systems (CMS) and Plugins: Popular CMS platforms like WordPress, Joomla, or Drupal, along with their numerous plugins and themes, are frequently targeted. Outdated versions or known vulnerabilities in these systems provide easy entry points for attackers to upload or inject web shells.
- Weak Credentials or Configuration Flaws: Default administrative credentials, easily guessable passwords, or misconfigurations that expose sensitive directories can also provide attackers with the initial access needed to place a web shell.
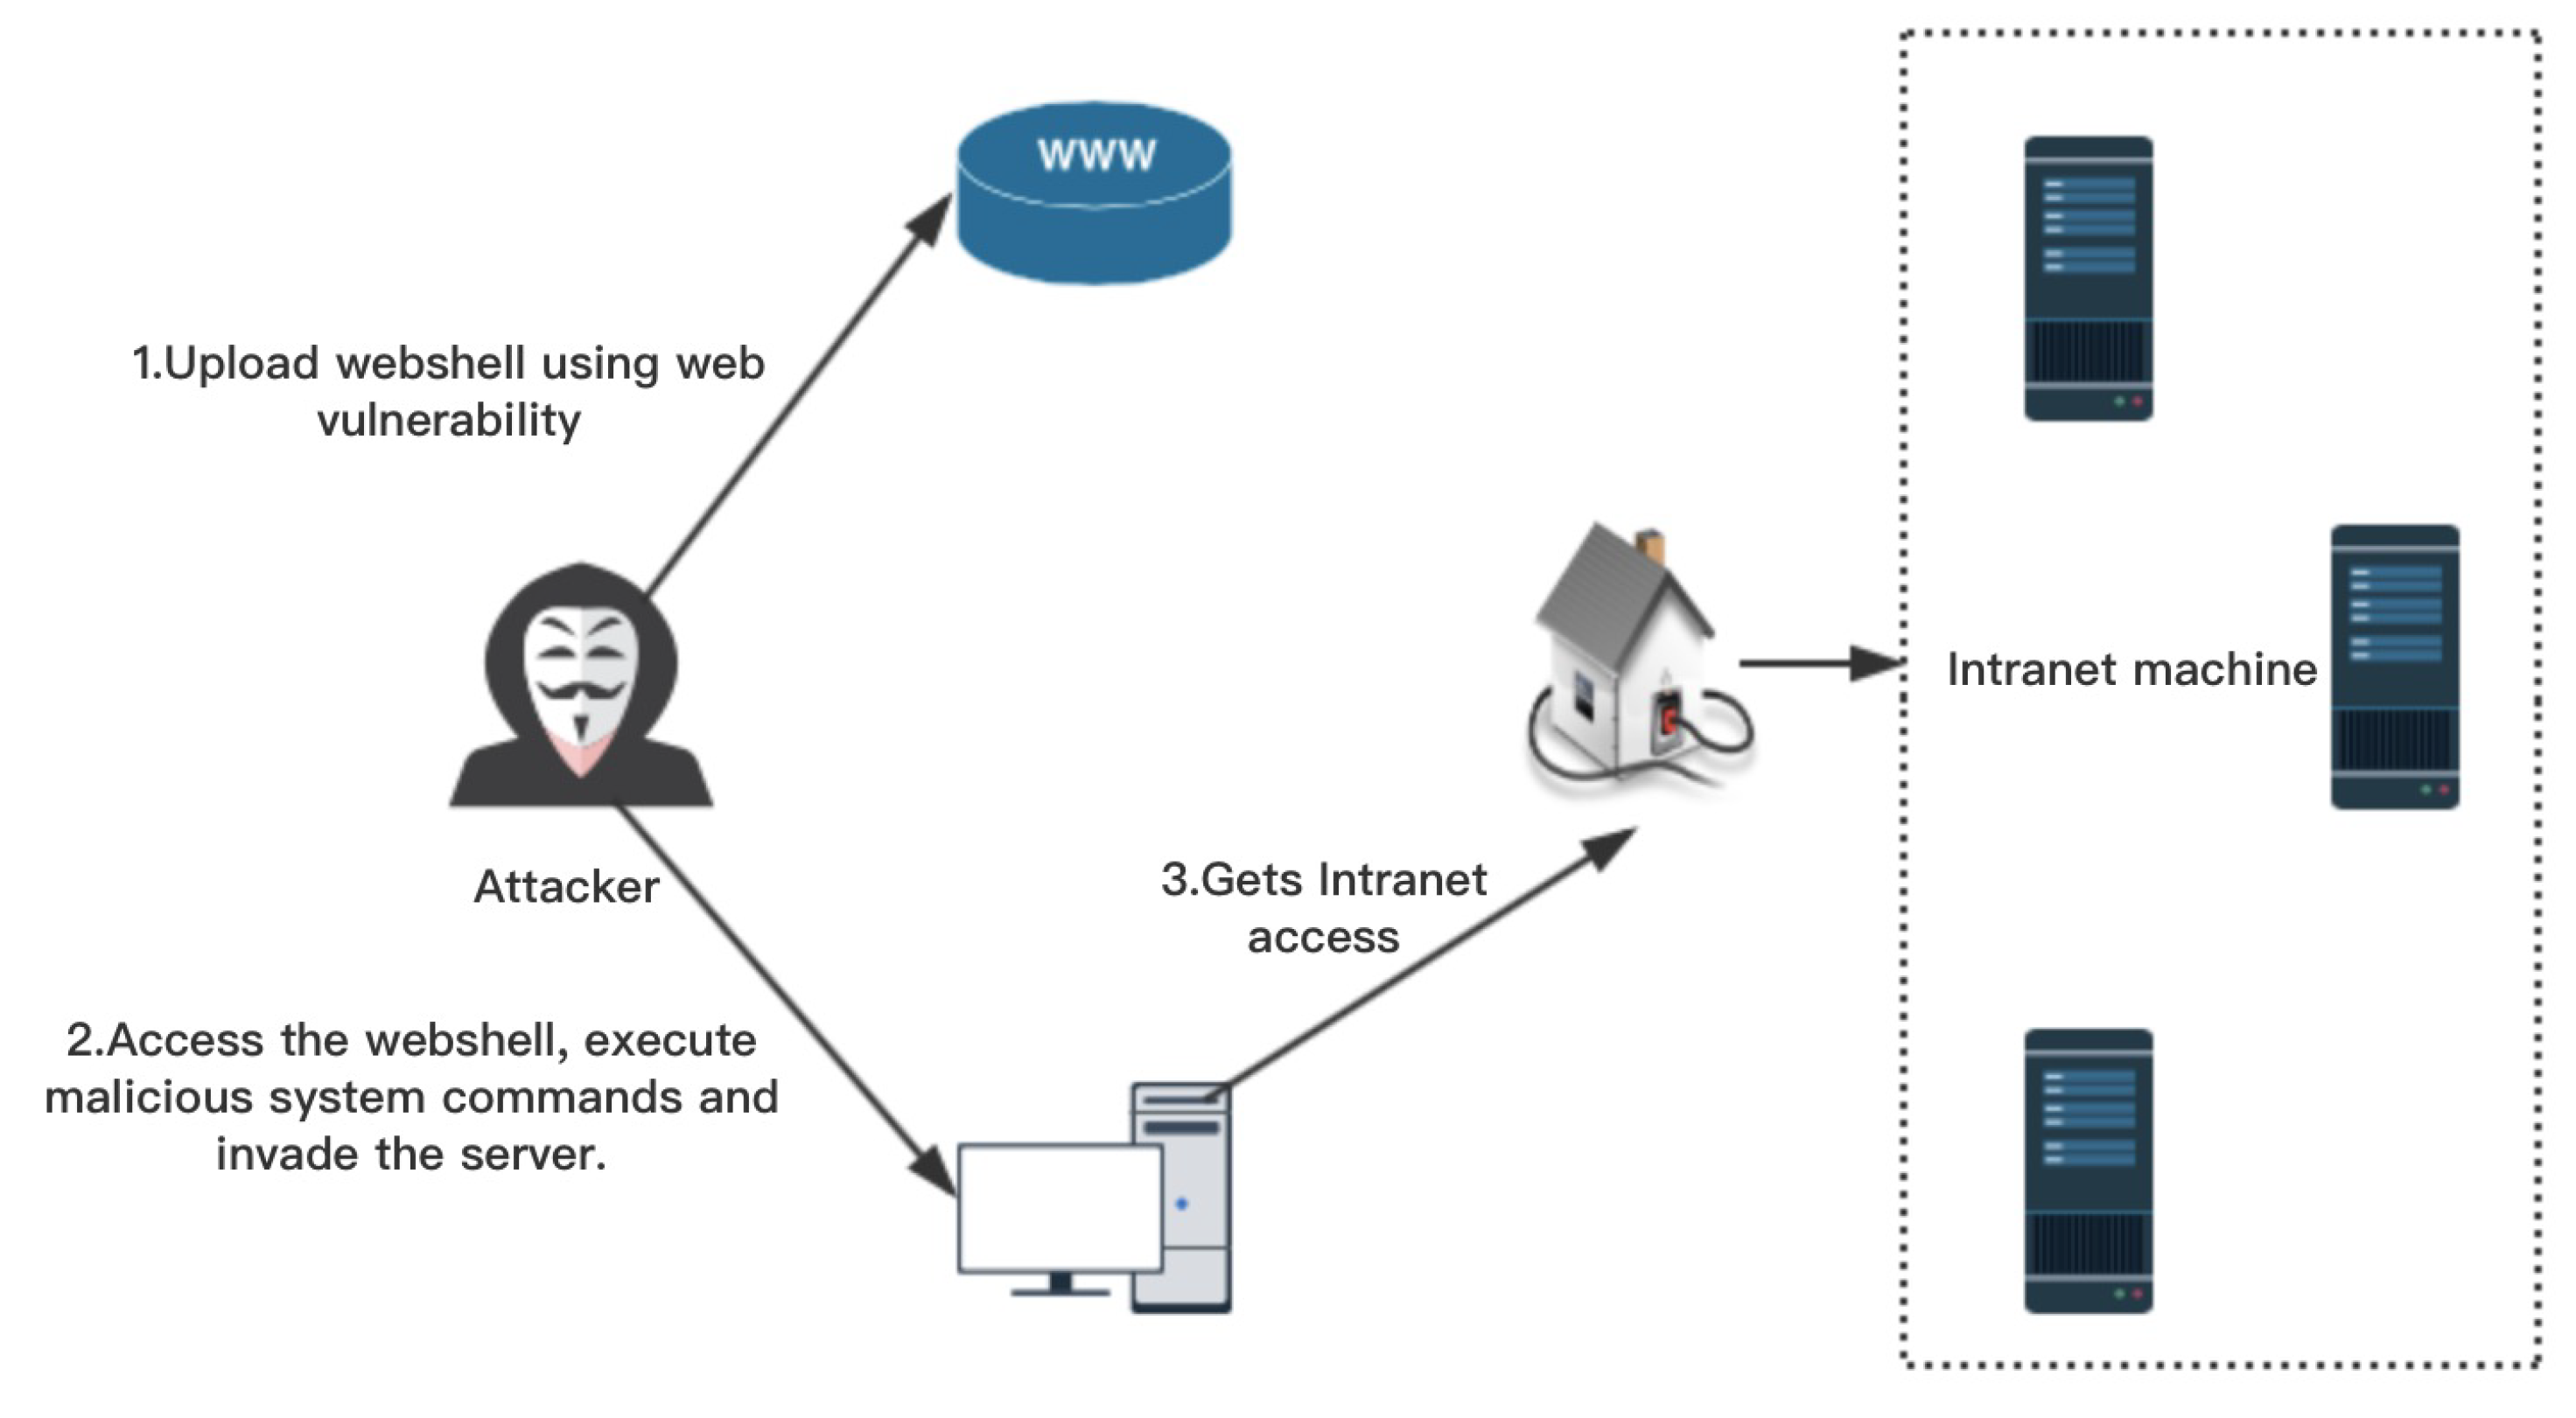
Once the web shell is uploaded, the attacker navigates to its URL using a web browser, triggering the script and establishing a persistent backdoor.
Capabilities and Control
The functionality of a web shell can range from basic file browsing and command execution to sophisticated interfaces offering database interaction, network scanning, and even self-deletion capabilities. A well-crafted web shell might include features such as:
- File Management: Uploading, downloading, editing, deleting, and renaming files on the server.
- Command Execution: Running arbitrary operating system commands (e.g.,
ls,pwd,netstat) with the privileges of the web server process. - Database Interaction: Directly querying and manipulating databases if the web server has access.
- Network Pivoting: Using the compromised server as a jump point to scan and attack other internal systems.
- Privilege Escalation: Attempting to gain higher privileges on the compromised server.
- Information Gathering: Collecting system information, user accounts, and configuration details.
The attacker effectively gains a powerful, web-based remote administration tool, often without requiring any specialized client software beyond a standard browser.
Web Shells in the Context of Tech & Innovation Security
The “Tech & Innovation” sector, encompassing areas like AI Follow Mode in drones, autonomous flight systems, sophisticated mapping solutions, and remote sensing technologies, often relies on complex, interconnected web applications and cloud infrastructure. This makes these cutting-edge innovations particularly susceptible to threats like web shells, which can undermine trust, compromise sensitive data, and even disrupt critical operations.
The Broader Landscape of Cyber Threats to Emerging Tech
Emerging technologies are inherently complex, often integrating various hardware, software, and network components. This complexity creates a larger attack surface. AI systems might process vast amounts of proprietary data, autonomous vehicles require robust, real-time communication, and remote sensing platforms collect invaluable intellectual property. A compromise in any part of this ecosystem can have cascading effects. Web shells, by providing deep access to foundational web servers, represent a direct threat to the integrity and confidentiality of the data and processes underpinning these innovations. The very nature of innovation involves rapid development and deployment, which can sometimes lead to security oversights if not carefully managed.
Specific Risks to Drone-Related Systems and Innovation
Consider the intricate web of applications and services that support modern drone technology:
- Drone Fleet Management Platforms: These web-based systems allow operators to plan missions, monitor drone telemetry, manage maintenance schedules, and track flight logs for entire fleets. A web shell on such a server could allow an attacker to alter flight plans, access sensitive operational data, or even inject malicious commands that could affect drone behavior.
- Aerial Mapping and Data Processing Platforms: After a drone collects vast amounts of imagery or sensor data, this data is often uploaded to cloud-based platforms for processing, stitching, and analysis. Compromising these servers via a web shell could lead to the theft of valuable mapping data, proprietary algorithms, or even the manipulation of generated maps, leading to incorrect spatial intelligence.
- Ground Control Station (GCS) Web Interfaces: While many GCS applications are desktop-based, some offer web interfaces for remote access or supplementary features. A web shell could potentially provide an attacker with a foothold into the system controlling drone operations, posing a significant risk to flight safety and mission integrity.
- Cloud-Based Flight Planning and Regulatory Compliance Systems: Innovators often develop web applications to streamline flight planning, ensure regulatory compliance, and obtain necessary airspace authorizations. A web shell could expose sensitive flight plans, user credentials, or allow an attacker to tamper with compliance records.
- Drone Data Repositories and IP Storage: Companies developing new drone technologies often store their proprietary designs, software code, research data, and business strategies on internal web servers or cloud storage accessible via web applications. A web shell could facilitate the exfiltration of this invaluable intellectual property, undermining years of research and development.
The compromise of such systems through a web shell poses not just a data breach risk, but a potential threat to operational safety, commercial viability, and national security in the context of critical infrastructure or defense applications.

Impact on Development and Deployment
The consequences of a web shell attack extend beyond immediate data loss. For innovative companies, it can mean:
- Disruption of Research and Development: Attackers could delete or corrupt vital project files, roll back codebases, or render development servers unusable, halting progress.
- Intellectual Property Theft: The blueprints for next-generation drone designs, proprietary AI algorithms, and unique sensor data processing techniques could be stolen and sold to competitors or hostile entities.
- Data Integrity Concerns: Manipulated data can lead to erroneous analyses, flawed product development, or incorrect decisions based on compromised information. For drone mapping, this could mean inaccurate terrain models or infrastructure inspections.
- Operational Safety Risks: In the most severe cases, compromised systems related to autonomous flight or real-time control could lead to malfunctions, crashes, or unauthorized drone operations.
- Reputational Damage and Financial Loss: A significant breach can erode customer trust, lead to regulatory fines, and incur substantial costs for incident response and remediation.
Detecting and Mitigating Web Shell Threats
Protecting the innovative systems driving advancements in drone technology and beyond requires a multi-layered security approach to prevent, detect, and respond to web shell threats effectively.
Proactive Defenses
Prevention is always better than cure. Organizations must integrate security into the entire lifecycle of their web applications and infrastructure.
- Secure Coding Practices: Developers must be educated on common web vulnerabilities and implement secure coding guidelines. This includes rigorous input validation, output encoding, and using secure APIs.
- Regular Patch Management: All web servers, CMS platforms, plugins, and underlying operating systems must be kept up-to-date with the latest security patches. Many web shells exploit known vulnerabilities for which patches are already available.
- Web Application Firewalls (WAFs): A WAF can provide an essential layer of defense by filtering and monitoring HTTP traffic between a web application and the Internet. It can detect and block many web shell upload attempts and command execution patterns.
- Principle of Least Privilege: Web server processes should run with the minimum necessary permissions to perform their function. This limits the damage a web shell can inflict if successfully deployed. File upload directories should not have execute permissions.
- Strong Authentication and Access Control: Implement multi-factor authentication (MFA) for all administrative interfaces and critical systems. Strict access controls should ensure that only authorized personnel can access sensitive directories or configuration files.
Detection Strategies
Even with the best preventative measures, some web shells may slip through. Robust detection mechanisms are crucial.
- File Integrity Monitoring (FIM): Continuously monitor critical web server directories for unauthorized file changes, additions, or deletions. FIM tools can alert administrators to the presence of new, suspicious files that might be web shells.
- Anomaly Detection and Behavioral Analysis: Security Information and Event Management (SIEM) systems can analyze logs for unusual activity, such as a web server process executing commands it normally wouldn’t, or excessive outbound network connections from a web application.
- Log Analysis: Regularly review web server access logs, error logs, and application logs for suspicious requests. Look for unusual file accesses, requests to unknown scripts, or HTTP POST requests containing large amounts of data to suspicious endpoints.
- Endpoint Detection and Response (EDR): EDR solutions on the server can monitor processes, file system events, and network connections for indicators of compromise that suggest a web shell is active.
- Regular Security Audits and Penetration Testing: Proactively seek out vulnerabilities in web applications and configurations before attackers do. These assessments can often uncover potential web shell deployment vectors.
Incident Response and Recovery
If a web shell is detected, a swift and well-defined incident response plan is paramount to minimize damage.
- Containment: Immediately isolate the compromised server or application to prevent further damage or lateral movement by the attacker.
- Eradication: Identify and remove all traces of the web shell, including any backdoor accounts, configuration changes, or additional malicious files dropped by the attacker. This often requires a complete rebuild from known-good backups.
- Recovery: Restore the affected systems from clean backups, ensuring all vulnerabilities exploited by the attacker have been patched and secured.
- Post-Incident Analysis: Conduct a thorough root cause analysis to understand how the web shell was deployed and implement measures to prevent future occurrences.
The Evolving Challenge
The threat of web shells is not static. Attackers continually refine their techniques to create more advanced and evasive variants.
Advanced Web Shells
Modern web shells can employ sophisticated tactics to evade detection:
- Evasive Techniques: Obfuscation, encryption, and polymorphism are used to disguise the web shell’s code, making it harder for signature-based detection systems to identify.
- Polymorphic Shells: These change their code each time they are accessed, further hindering signature detection.
- Memory-Only Shells: Some advanced web shells exist only in the server’s memory, leaving no traces on the disk, making them incredibly difficult to detect and remove. These are typically injected via in-memory exploits.
- Custom Communication Channels: Beyond standard HTTP, web shells might use DNS tunneling or other covert channels for command and control, complicating network-based detection.
Securing the Future of Connected Technologies
For the “Tech & Innovation” sector, especially in areas as sensitive and critical as drone technology, the fight against web shells and other cyber threats demands continuous vigilance and an integrated security mindset. Security must be an inherent part of the design and development process for all new applications and platforms. From the initial conceptualization of an AI-powered autonomous drone system to the deployment of its cloud-based management portal, security considerations must be embedded at every stage.
Investing in secure development practices, robust infrastructure hardening, advanced threat intelligence, and continuous monitoring is not merely a cost but a fundamental investment in the resilience and success of future innovations. Only by proactively addressing these pervasive threats can we truly unlock the full potential of groundbreaking technologies without compromising their integrity or the safety of their operations.